

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
cve — Reproducible example demonstrating CVE-2024-26308 vulnerability detection during Docker builds, with Maven dependency tree analysis and remediation guidance for Apache Commons Compress. | Kitploit
Tools/GitHubGitHub/crazycatmyopic/cve
Container SecurityVulnerability AnalysisCode AnalysisSupply Chain SecurityLearning & Education
GitHubcrazycatmyopic/cve

cve

Reproducible example demonstrating CVE-2024-26308 vulnerability detection during Docker builds, with Maven dependency tree analysis and remediation guidance for Apache Commons Compress.

View Repository
402 years agoNot yet reviewed
Share

CVE


Problem statement: Stackoverflow

I'm trying to build by project in Docker, So i'm using Docker Desktop to build my project, when i build the image i get this as one of my vulnerabilities

CVE-2024-26308
CWE-770
7.5
H
Allocation of Resources Without Limits or Throttling vulnerability in Apache Commons Compress. This issue affects Apache Commons Compress: from 1.21 before 1.26. Users are recommended to upgrade to version 1.26, which fixes the issue.
CVSS Score:	7.5
CVSS Vector:	CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:N/A:H
Affected range:	>=1.21,<1.26.0
Fix version:	1.26.0
Publish date:	2024-02-19

I would like to fix this, but when i read the bug it say it's due to org.apache.commons, but i don't have it in my dependency, i try running mvn help:effective-pom and mvn dependency:tree -Dverbose and i still did not find it. What could be the cause of it and how can i fix it?


Requirement

  • Java 17
  • maven
  • Docker Desktop

RUN

command to run

 docker build --target run -t build_run .
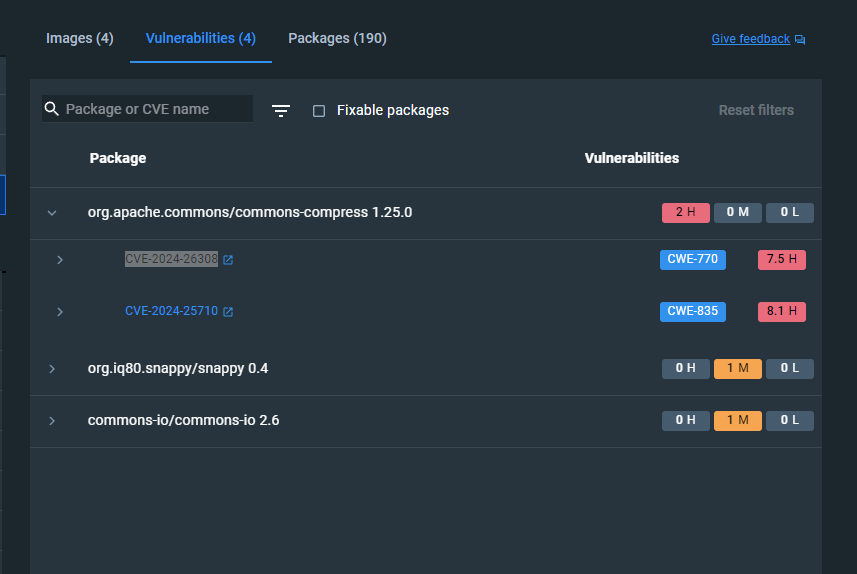
Snapshot

snapsho

Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    524
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    478
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    357
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    317
  • 5

    estorides

    grisuno/estorides

    Aggregates 99+ free OSINT sources in parallel, resolves entities into a knowledge graph, and exports STIX 2.1, MISP, or GraphML with LLM-assisted analysis.

    305
  • 6

    opencti

    opencti-platform/opencti

    Open Cyber Threat Intelligence Platform

    275

Explore all tools

Browse our collection of tools

View all tools →






