

owasp-ctf-in-a-box
 owasp/owasp-ctf-in-a-box
Self-hosted OWASP CTF kit: one box, one free GitHub org, no cloud dependencies
container-securityctfdevsecops+6
13
owasp/owasp-ctf-in-a-boxSelf-hosted OWASP CTF kit: one box, one free GitHub org, no cloud dependencies
 node9-ai/node9-proxy
IAM for your AI agents. Set what Claude Code, Codex, Gemini, Cursor and any MCP server are allowed to do, review risky actions before they run, and…
 msaad00/agent-bom
Open security scanner and self-hosted control plane for AI, MCP, and cloud. One evidence model — run scans in your environment, centralize findings,…
 prismorsec/prismor
Self-hosted runtime control plane for AI agents. Observe or HITL approve or Block rogue tool calls before it executes: secret leaks, prompt…
 usmannasir/cyberpanel
Cyber Panel - The hosting control panel for OpenLiteSpeed
 spiffe/spire
Workload identity platform that attests running services, issues SPIFFE IDs/SVIDs, and enables mTLS and JWT authentication for Kubernetes,…
 open-policy-agent/opa
Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…
 ed1s0nz/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 openziti/ziti
Zero-trust networking platform that makes services invisible with cryptographic identity, policy-based access, and end-to-end encryption. Replaces…
 jumpserver/jumpserver
JumpServer is an open-source Privileged Access Management (PAM) platform that provides DevOps and IT teams with on-demand and secure access to SSH,…
 nvidia/openshell
Sandboxed runtime for autonomous AI agents with declarative YAML policies enforcing filesystem, network, and process constraints, plus endpoint-bound…
 sigstore/cosign
Code signing and transparency for containers and binaries
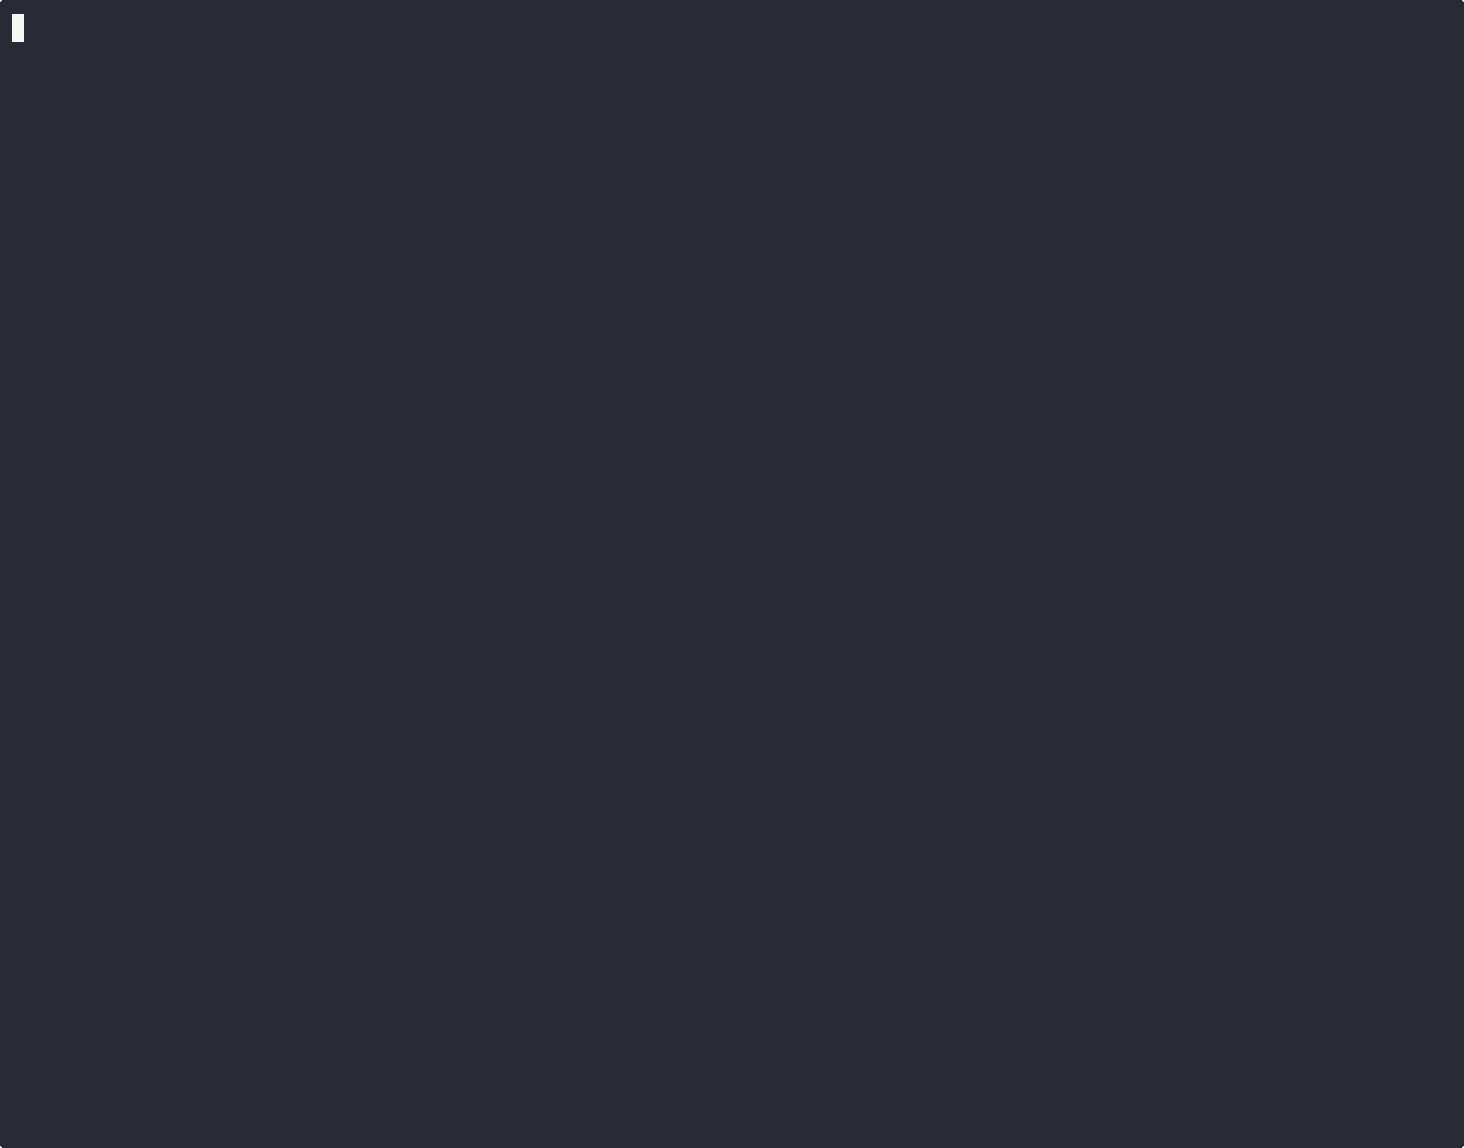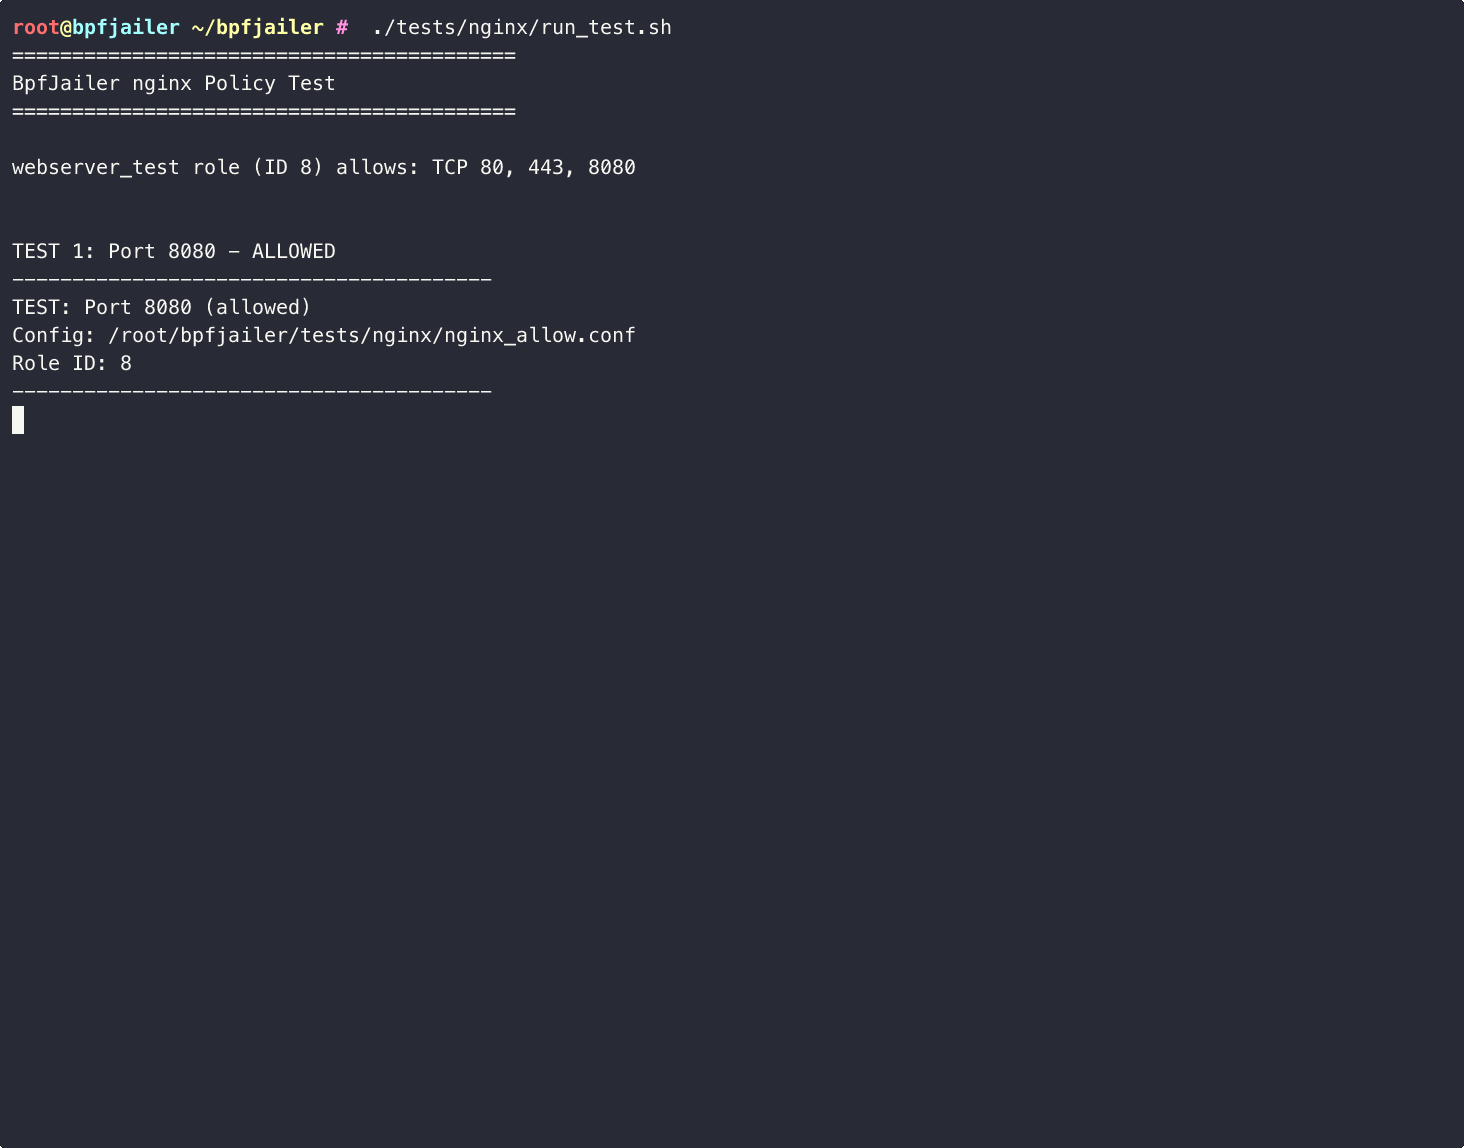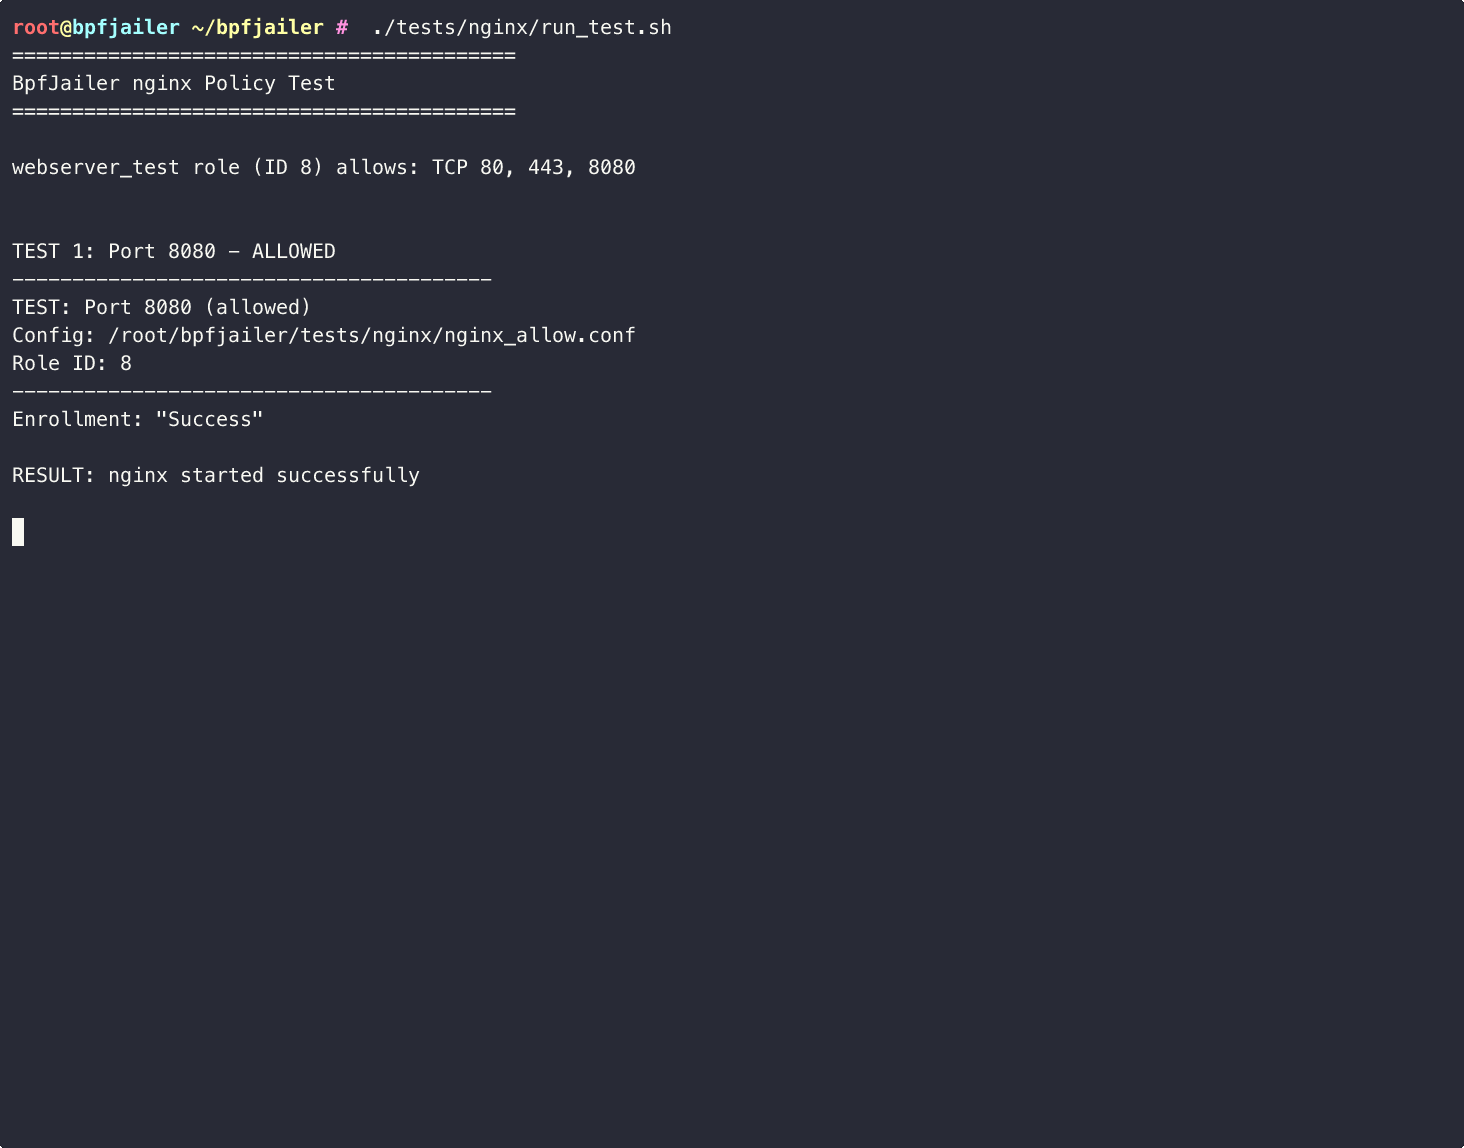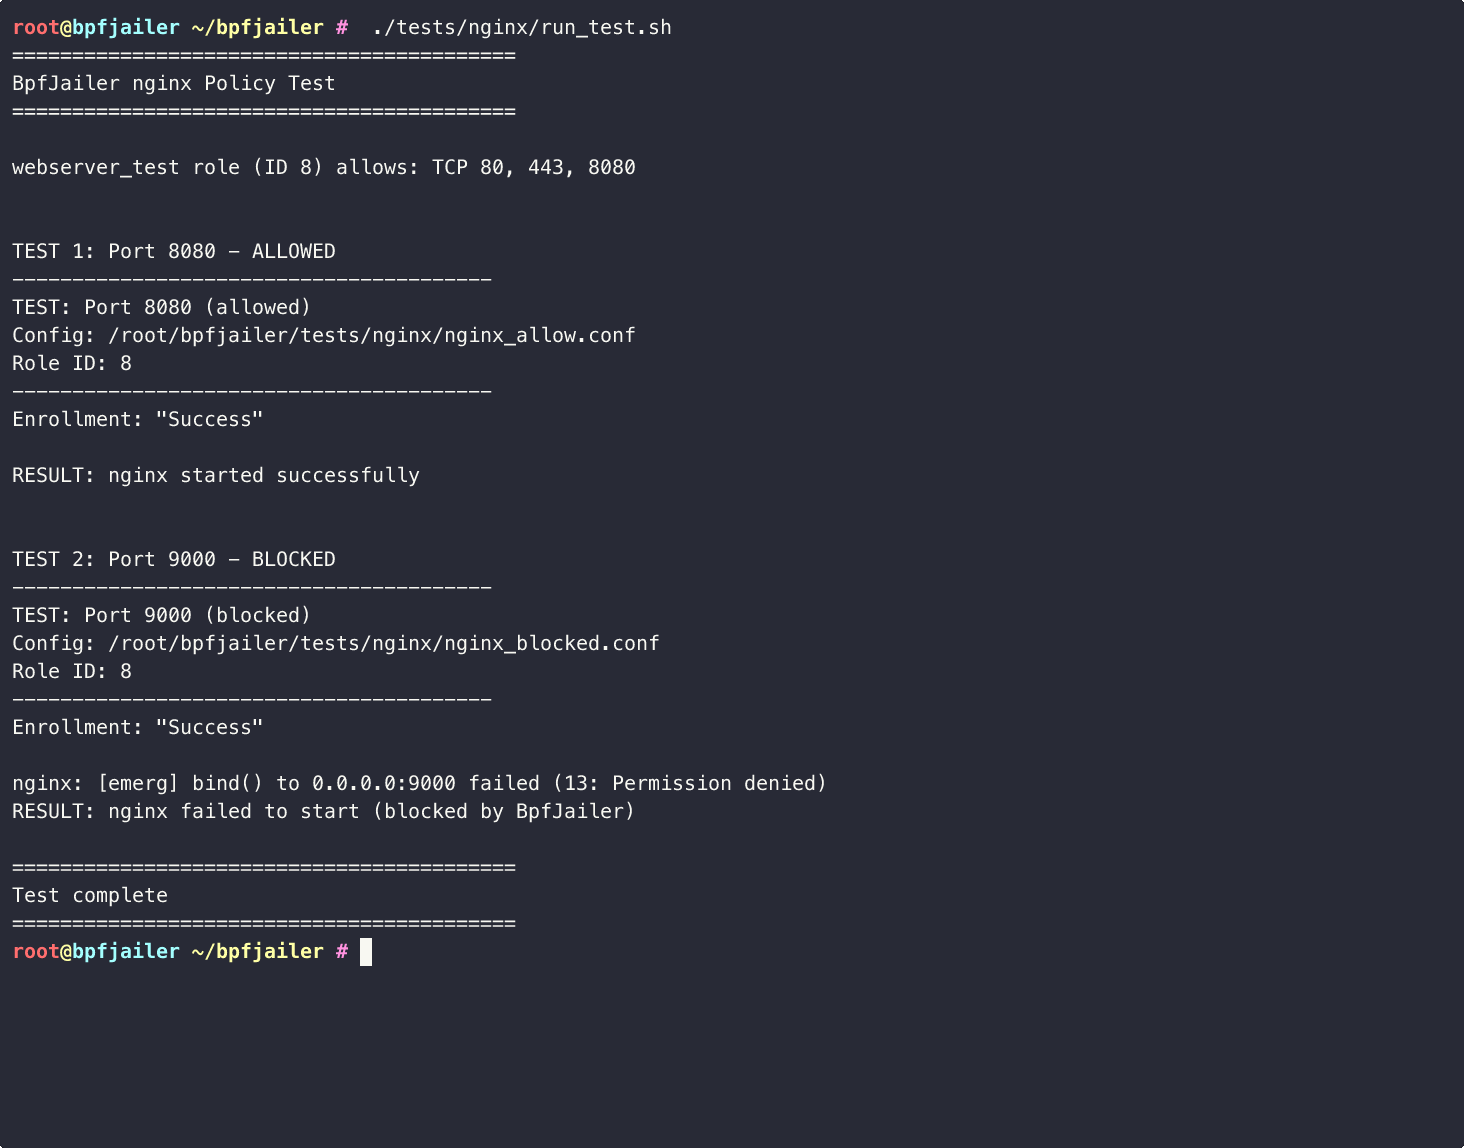 gen0sec/jailer
Jailer is an eBPF-based process jailing system that provides mandatory access control (MAC) for Linux. It tracks processes using BPF task_storage…
 moltis-org/moltis
A secure persistent personal agent server in Rust. One binary, sandboxed execution, multi-provider LLMs, voice, memory, Telegram, WhatsApp, Discord,…
 open-policy-agent/gatekeeper
Kubernetes policy engine with OPA-based admission control, mutation, and audit for enforcing security and compliance configurations.
 runewardd/runeward
Governed execution cells for AI agents.
 aipentest/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 canyonroad/agentsh
Execution-Layer Security (ELS) for AI agents — policy-enforced shell with audit.