CVE-2025-9074-PoC
A vulnerability has been identified in Docker Desktop. A remote attacker could exploit this vulnerability to trigger security restriction bypass on…

A vulnerability has been identified in Docker Desktop. A remote attacker could exploit this vulnerability to trigger security restriction bypass on…

Proof-of-concept demonstrating container escape on Amazon EKS by exploiting Dirty Frag (CVE-2026-43284) kernel page-cache corruption via shared image…

POE code for CVE-2017-1000112 adapted to both funtion on a specific VM and Escape a Docker

Reproduction of CVE-2017-5123 kernel vulnerability allowing local privilege escalation via waitid syscall memory write, demonstrated with Docker…

Proof-of-concept exploit for CVE-2019-5736, a runc container escape that overwrites the host runc binary to achieve root code execution on the host.

Kubesploit is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in Golang, focused on containerized environments.

A Linux Host-based Intrusion Detection System based on eBPF.

PoC: fully unprivileged container escape to node-level code execution on Kubernetes via CVE-2026-31431 page-cache corruption + shared image layers.…

Master the art of cloud exploitation. A specialized resource for offensive security researchers and red teamers focused on weaponizing…

Proof-of-concept exploit for CVE-2025-9074 demonstrating container-to-host file write via exposed Docker Engine API on Windows. For authorized…

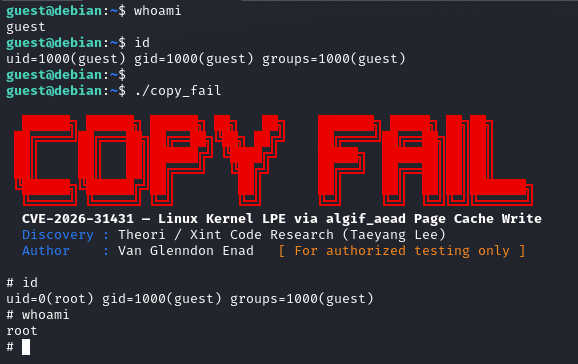
Proof-of-concept exploit for CVE-2026-31431, a Linux kernel local privilege escalation via AF_ALG page cache write, achieving root on major…

Exploits CVE-2026-41567 Docker escape using trojanized xz/unpigz binaries to gain a root shell on the host from inside a container.

A 16-year-old bug in the Linux kernel lets a rented VM break out and attack the host it runs on. Intel and AMD alike. Januscape is a use-after-free…

Proof of concept exploit for CVE-2025-9074 - Unauthenticated Docker Engine API container escape affecting Docker Desktop < 4.44.3 on Windows and…

POC shows how to leak postgresql stuff cause hugefile sub-system. Based on https://x.com/spendergrsec/status/1993794163880718700?s=20

Proof-of-concept demonstrating container escape on Kubernetes via CVE-2026-31431 kernel page-cache corruption, achieving node-level code execution…

PoC exploit for CVE-2025-9074 demonstrating a full Docker Desktop container escape on Windows and macOS via an unauthenticated internal Docker Engine…

Golang rewrite of the Copy Fail (CVE-2026-31431) local privilege escalation exploit, corrupting page cache to gain root on Linux systems.