
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
Tools/GitHubGitHub/bridgeralderson/cve-2025-9074-poc
Privilege EscalationVulnerability AnalysisExploitationPenetration TestingRed TeamingContainer Escape
GitHubbridgeralderson/cve-2025-9074-poc

CVE-2025-9074-PoC

A vulnerability has been identified in Docker Desktop. A remote attacker could exploit this vulnerability to trigger security restriction bypass on the targeted system.

Share
View Repository
5053911 months agoReviewed by Kitploit

Docker API Unauthenticated RCE (CVE-2025-9074)

A critical CVE-2025-9074 vulnerability in Docker Desktop enables locally running Linux containers to connect to the Docker Engine API through the default subnet (192.168.65.7:2375). The issue persists regardless of Enhanced Container Isolation (ECI) or TCP exposure settings. Proof of Concept exploit code is publicly available for CVE-2025-9074. The vulnerability may allow unauthorized access to user files on the host system. Hence, the risk level is rated as High Risk.

A standalone Bash script to exploit exposed Docker APIs (typically port 2375) without authentication. This tool automates container breakout via volume mounting, allowing for arbitrary command execution on the host system with root/admin privileges.

Features

  • Universal OS Support: Automatically detects the target OS (Linux vs. Windows/Docker Desktop) and adjusts the mount point accordingly (/:/host_root or /mnt/host/c:/host_root).
  • Air-Gap Friendly: Enumerates and uses existing images on the target system. Does not require internet access on the target to pull new images.
  • Auto-Cleanup: Forcefully removes the container after command execution to minimize footprint.
  • Zero Dependencies: Written in pure Bash using standard curl, grep, and sed. No jq or external binaries required.

Usage

chmod +x exploit.sh
./exploit.sh <TARGET_IP> <COMMAND> [PORT]
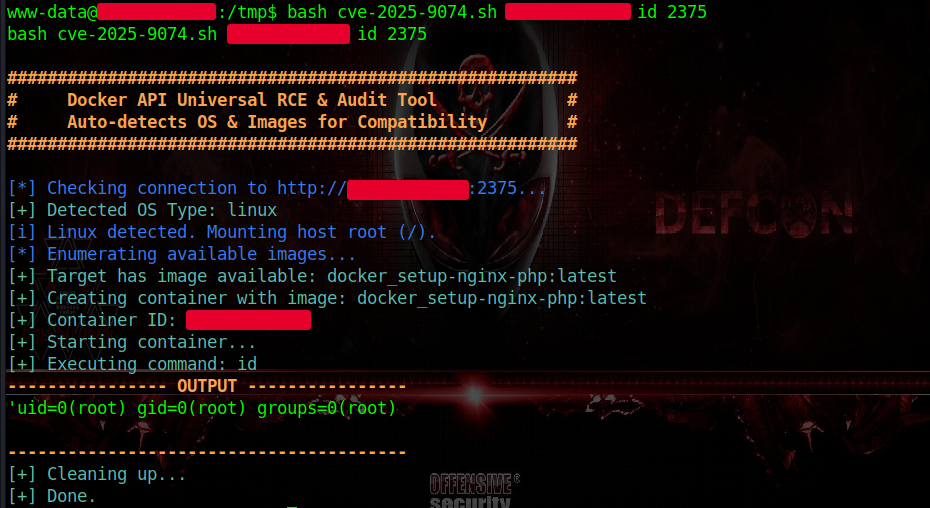
Proof Of Concept

image
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    755
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    510
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    415
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    343
  • 5

    antifox

    antifox-ai/antifox

    AI multi-agent autonomous penetration testing platform that runs recon, attack-surface discovery, exploitation validation and evidence-backed report delivery.

    259
  • 6

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    258

Explore all tools

Browse our collection of tools

View all tools →






