

CVE-2022-0492-Checker
 sofianehamlaoui/cve-2022-0492-checker
A script to check if a container environment is vulnerable to container escapes via CVE-2022-0492
cloud-securitycontainer-escapecontainer-security+3
13
sofianehamlaoui/cve-2022-0492-checkerA script to check if a container environment is vulnerable to container escapes via CVE-2022-0492
 jpts/cve-2025-23266-poc
Proof-of-concept exploit for CVE-2025-23266 (NVIDIAScape) targeting NVIDIA AI container runtime. Demonstrates container escape via GPU driver…
 shaoshi17/cve-2025-9074-docker-exploit
一个功能强大的 Docker 远程 API 漏洞利用工具,用于 CVE-2025-9074 漏洞的安全研究和测试。
 t1erno/cve-2022-0492-docker-breakout-checker-and-poc
Docker Breakout Checker and PoC via CAP_SYS_ADMIN and via user namespaces (CVE-2022-0492)
 r0binak/cve-2024-0132
CVE-2024-0132 – Fully Weaponized NVIDIA Container Toolkit Exploit
 cdxiaodong/cve-2024-21626
Proof-of-concept exploit for CVE-2024-21626 runc container breakout via leaked file descriptors and process.cwd manipulation, enabling host…
 ssst0n3/poc-cve-2024-0132
Proof-of-concept exploit for CVE-2024-0132 enabling container escape via NVIDIA container toolkit, allowing host filesystem access and Docker daemon…
 666asd/cve-2024-23653
Proof-of-concept demonstrating CVE-2024-23653, a BuildKit container escape via a malicious Dockerfile frontend, using buildctl to inspect process…
 ssst0n3/kata-cve-2020-2023-poc
Proof-of-concept exploit for Kata Containers container escape (CVE-2020-2023) using mknod to modify guest filesystem and overwrite system binaries…
 zhangguanzhang/cve-2024-21626
Proof-of-concept exploit for CVE-2024-21626, a runc container escape vulnerability allowing host file system access via crafted working directory in…
 yandex-cloud-examples/yc-mk8s-sctphantom-mitigation
DaemonSet для митигации уязвимости CVE-2026-64564 (SCTPhantom)
 hans362/cve-2026-31431-copy-fail-container-escape
Container escape on any docker container with healthcheck enabled via CVE-2026-31431
 wuzuowei/copy-fail-cve-2026-31431
Exploit for CVE-2026-31431, a Linux kernel authencesn vulnerability enabling local privilege escalation to root and container escape via AF_ALG and…
 medaz-sploit/cve-2025-9074-docker-desktop-api-escape-poc
Proof-of-concept exploit for CVE-2025-9074 enabling Docker Desktop API escape via raw HTTP requests. Provides an emulated interactive shell inside a…
 pucagit/cve-2025-9074
PoC exploit for CVE-2025-9074 demonstrating a full Docker Desktop container escape on Windows and macOS via an unauthenticated internal Docker Engine…
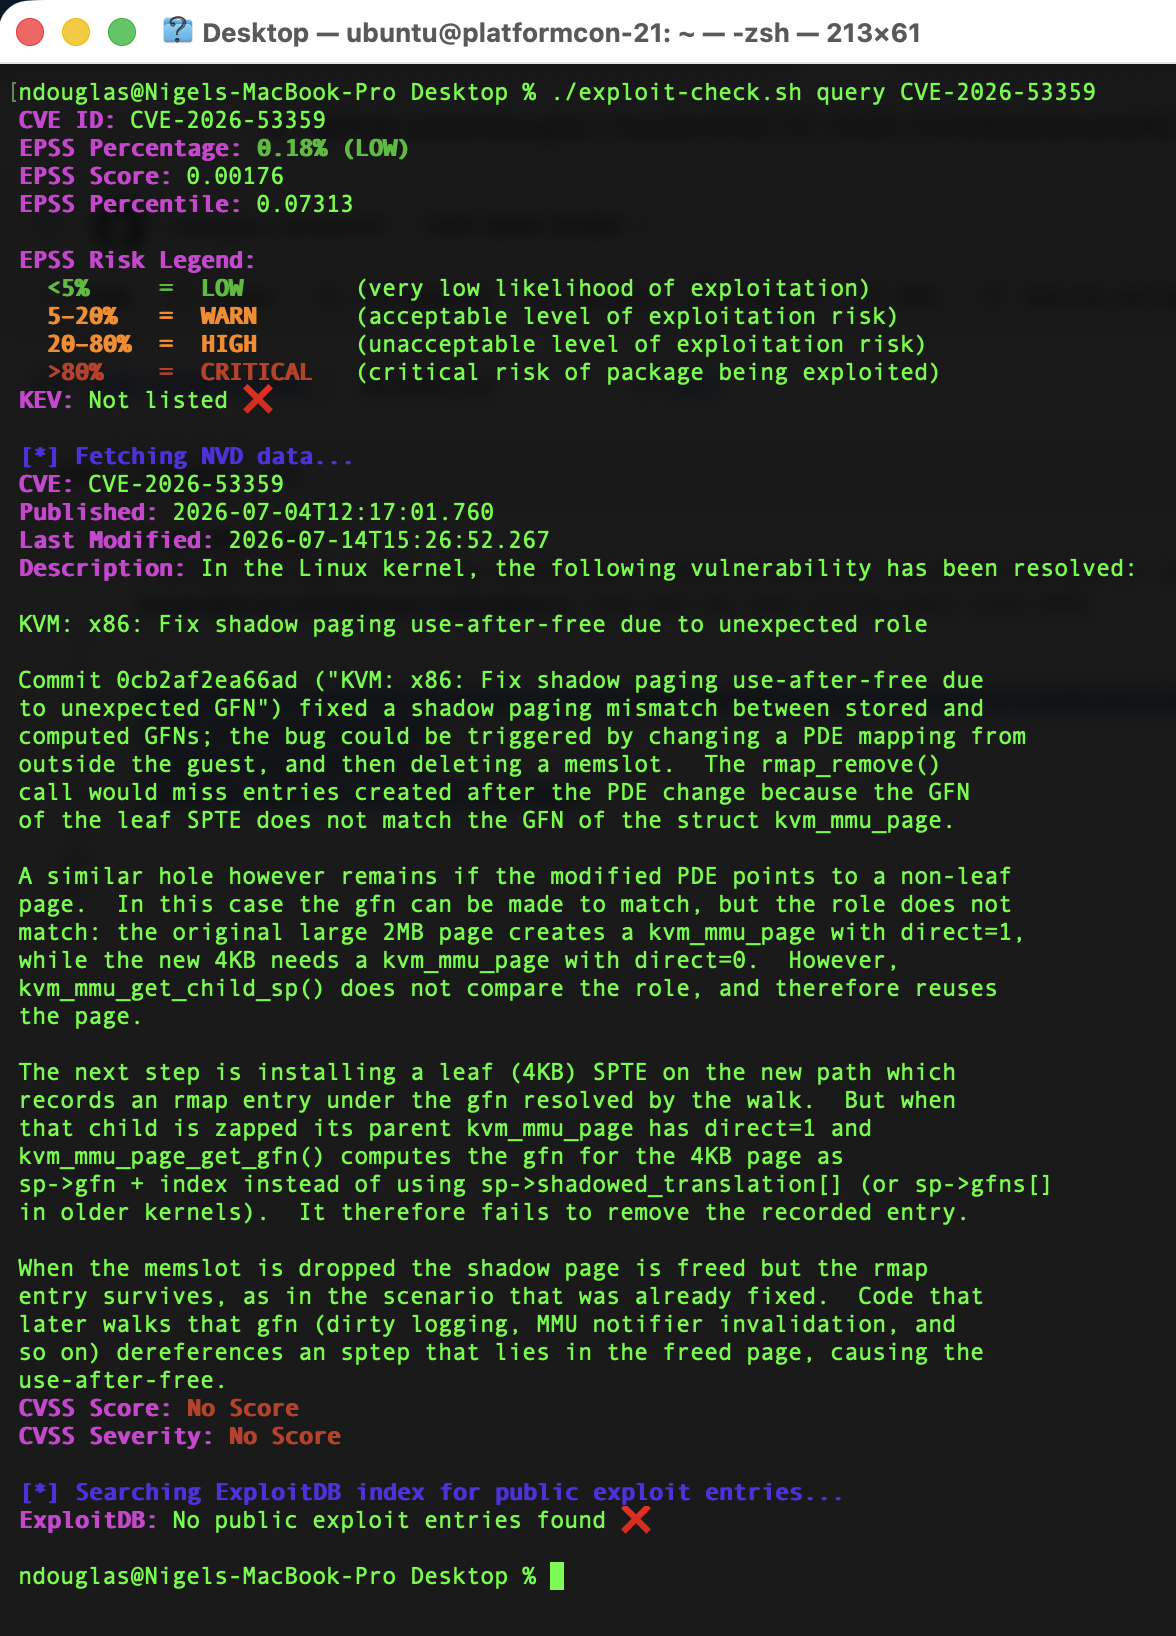 ndouglas-cloudsmith/cve-2026-53359
A 16-year-old bug in the Linux kernel lets a rented VM break out and attack the host it runs on. Intel and AMD alike. Januscape is a use-after-free…
 r0binak/cve-2025-23266
CVE-2025-23266 – Fully Weaponized NVIDIA Container Toolkit Exploit
 flojboj/cve-2024-21626
Working exploit for CVE-2024-21626, a runC/Docker container escape via working directory symlink attack, enabling host filesystem access.