kafka-keycloak-oauth

Apache Kafka 4.1.0 (KRaft) with Keycloak OAuth2 authentication using Strimzi - bypasses CVE-2025-27817 URL allowlist restriction

Apache Kafka 4.1.0 (KRaft) with Keycloak OAuth2 authentication using Strimzi - bypasses CVE-2025-27817 URL allowlist restriction

Ansible playbook to verify target Linux hosts using the official Red Hat Log4j detector script RHSB-2021-009 for Log4Shell (CVE-2021-44228).

System Vulnerability Checklist & Network Security Hardening project featuring reconnaissance, vsFTPd backdoor analysis (CVE-2011-2523), and active…

A web version of the bash scripts wrote for Check Point CVE-2026-50751 and CVE-2026-50752. This uses a local server to scan and make changes using…

Scenario-based training exercise for IT administrators: identify, approve, and deploy critical patches for financial systems under a 48-hour SLA…

Multi-VM virtual network lab with GRE tunneling, nftables firewall, Active Directory, BIND9 DNS, and Docker services. Includes vulnerability…

Junior Backend Candidate Exercise: Packaging the dasel CLI (v3.3.1) with Melange, fixing CVE-2026-33320, and building a minimal container image using…

Automated, reproducible network security testing framework using Ansible and BATS to verify DNS, host availability, open ports, and TLS configuration…

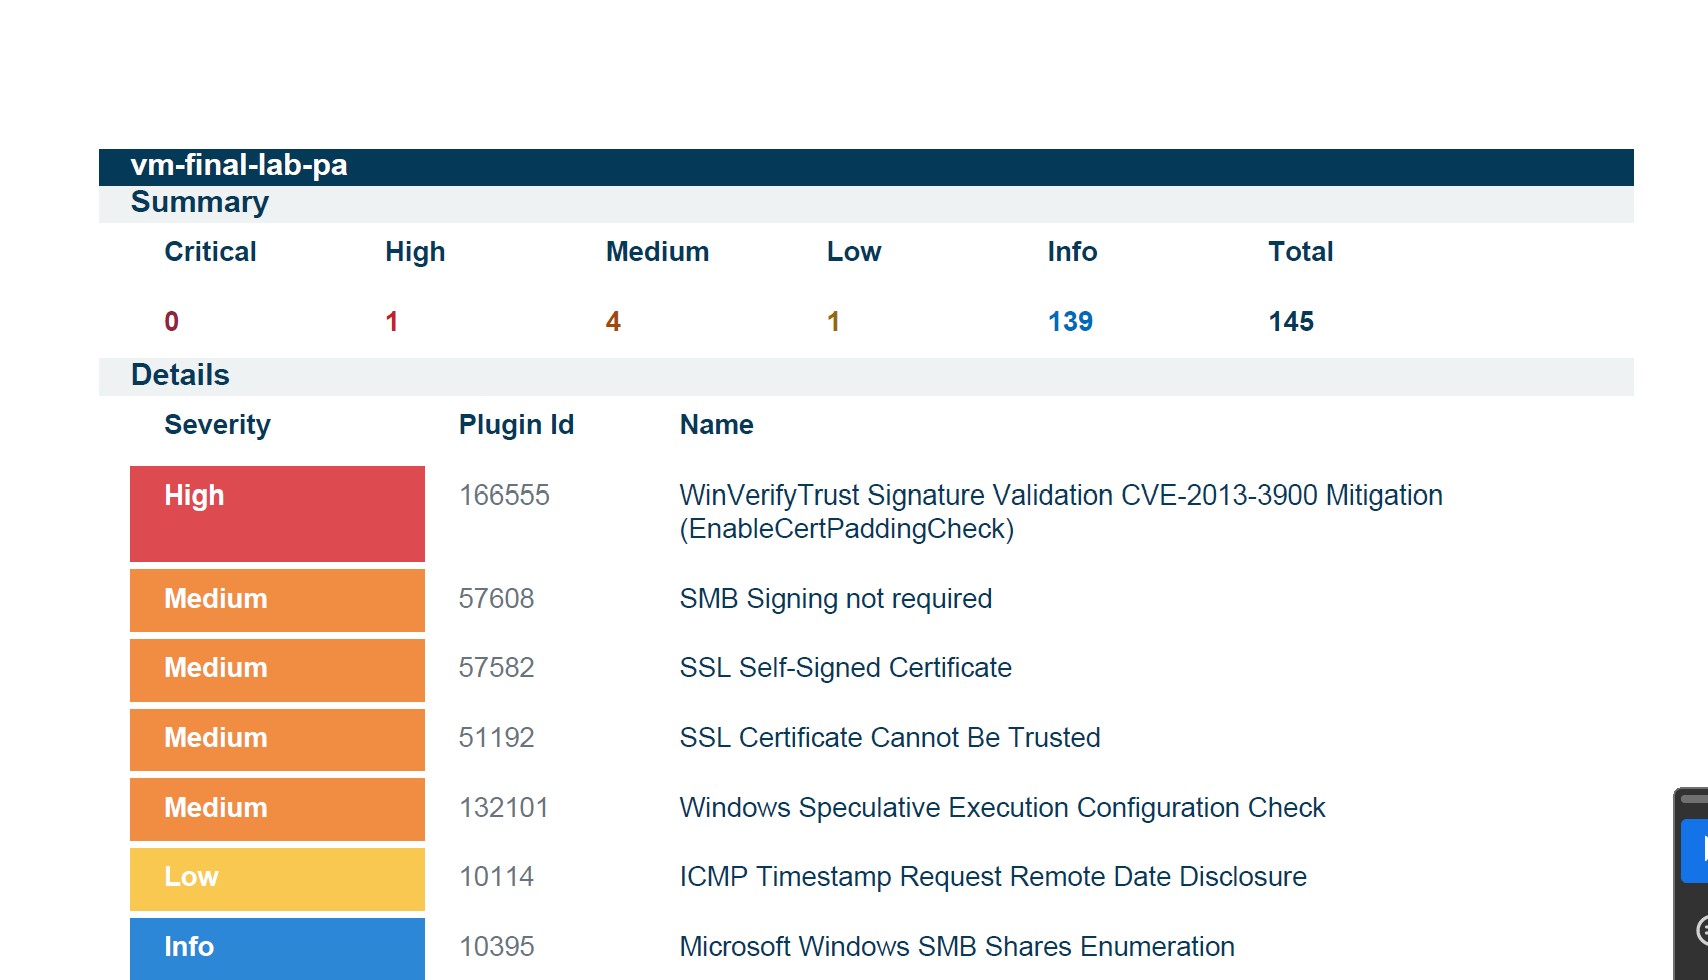
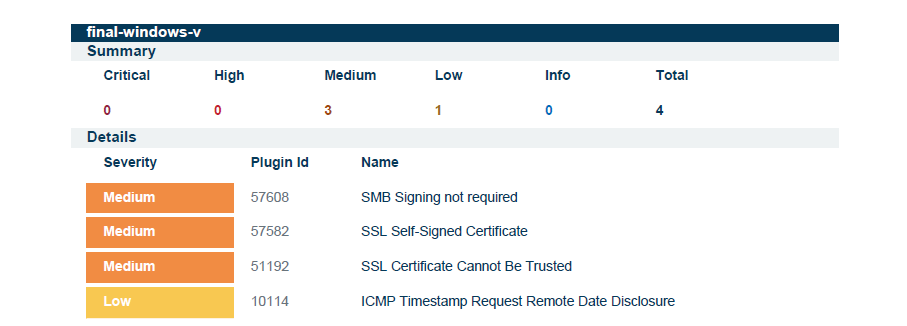
End-to-end remediation of CVE-2013-3900 using PowerShell and Tenable. Demonstrates vulnerability identification, registry hardening, and automated…

Step-by-step remediation report for CVE-2013-3900 on Windows Server 2019 Azure VM, using Tenable/Nessus credentialed scans and registry hardening to…

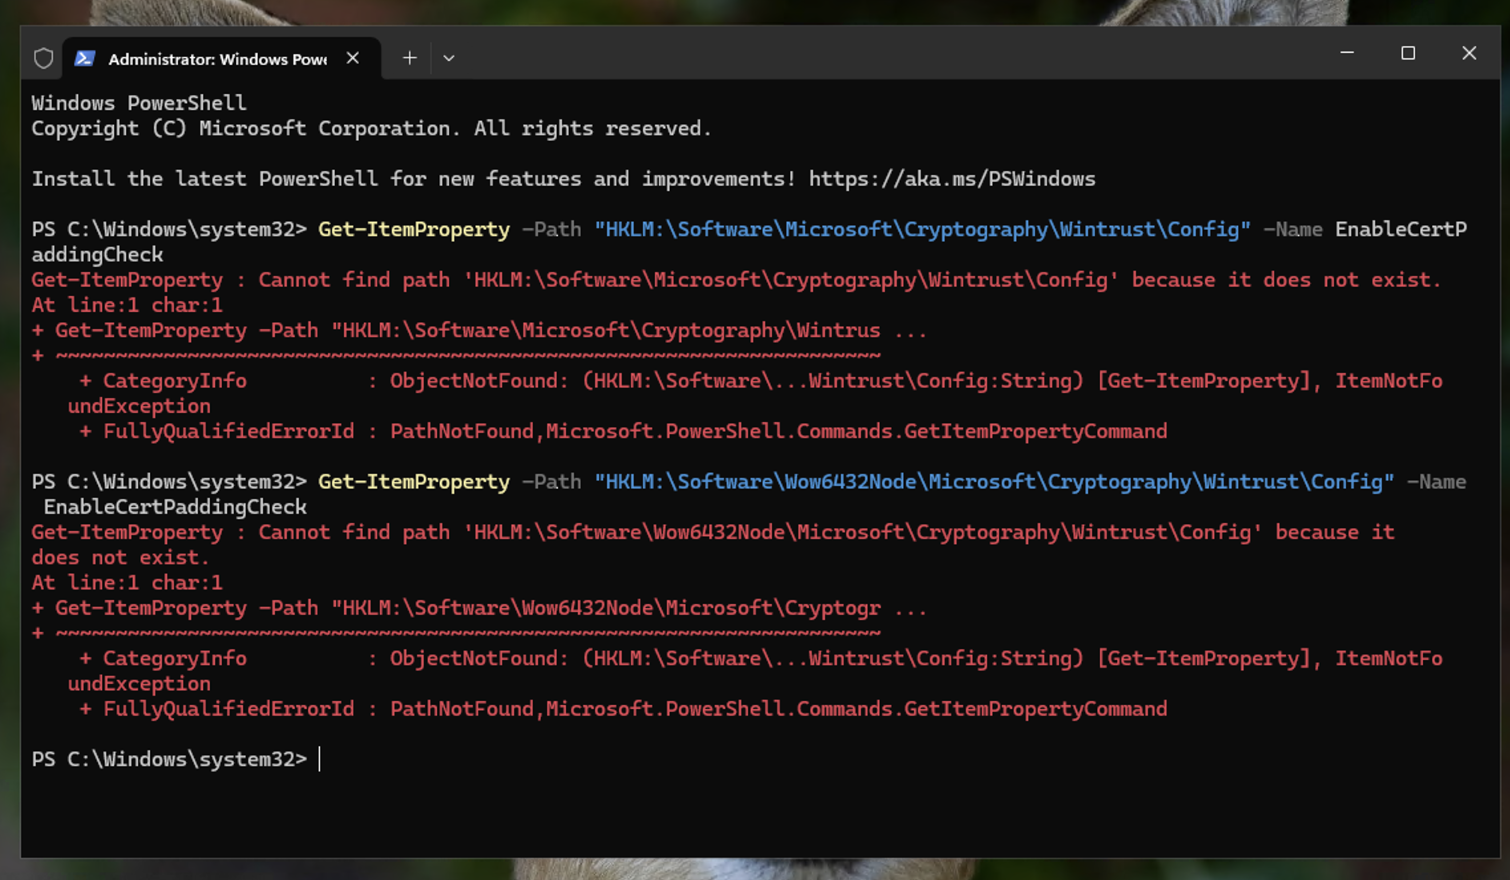
PowerShell remediation for CVE-2013-3900 (WinVerifyTrust) / Tenable Plugin 166555 using EnableCertPaddingCheck.

Scans Git repositories for hardcoded secrets, keys, and passwords using Gitleaks, integrating security into Bitbucket Pipelines with Code Insights…

Scans Infrastructure as Code files for security misconfigurations and vulnerabilities using KICS, with Bitbucket Code Insights reporting.

Hands-on lab on detecting and mitigating web app threats using OWASP ZAP, Burp Suite, and ModSecurity WAF (with OWASP CRS). Case study: Spring4Shell…

Demo to remediate CVE-2023-20198 using forward networks and tines

C++ utility that checks Windows OS version and detects whether the patch for CVE-2018-1010 is installed using systeminfo and wmic commands.

Ansible playbook automating CVE-2016-5195 (Dirty COW) mitigation on CentOS/Scientific Linux using SystemTap kernel module generation.

A small powershell script to disable print spooler service using desired state configuration