

wazuh
 wazuh/wazuh
Open-source XDR and SIEM platform for threat detection, log analysis, file integrity monitoring, vulnerability assessment, and compliance management…
anomaly-detectionanti-botcloud-security+12
17.2k1 day ago
wazuh/wazuhOpen-source XDR and SIEM platform for threat detection, log analysis, file integrity monitoring, vulnerability assessment, and compliance management…
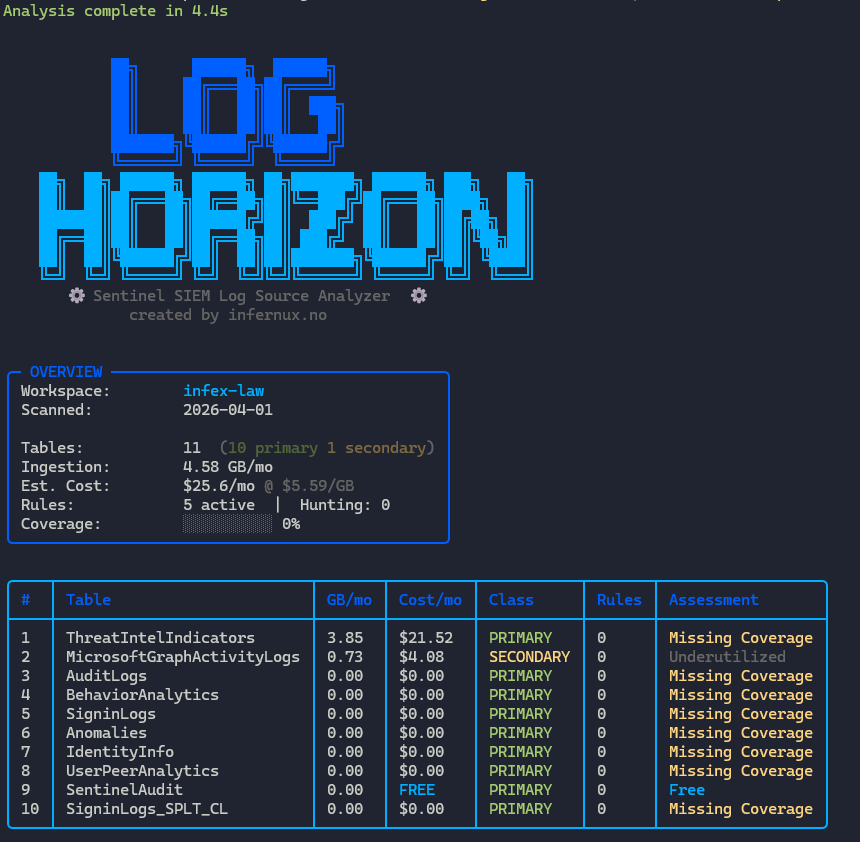 lnfernux/log-horizon
Microsoft Sentinel SIEM Log Source Analyzer
 duggytuxy/syswarden
Host-local Linux security orchestrator enforcing nftables policy with HIDS/HIPS telemetry, bounded threat-intelligence feeds, out-of-band WAAP log…
 yamato-security/wela
Audits Windows event log settings against best-practice guidelines and Sigma-rule detectability, with automated configuration for DFIR readiness.
 jithinkrishnanrs/cve-2026-67401-cpanel-emailtrack-sqli
Read-only IOC scanner and mitigation toolkit for cPanel & WHM EmailTrack SQL injection (CVE-2026-67401). Performs version fingerprinting, file…
 siberanka/rdp-guard
Monitors Windows Security logs for failed RDP attempts and automatically blocks abusive IPs via Windows Firewall, with configurable thresholds and…
 t0tooro/cve-2025-24054-lab
Blue-team lab: detecting & mitigating CVE-2025-24054 (Windows NTLM hash disclosure) with Sysmon, Wazuh SIEM, and Group Policy
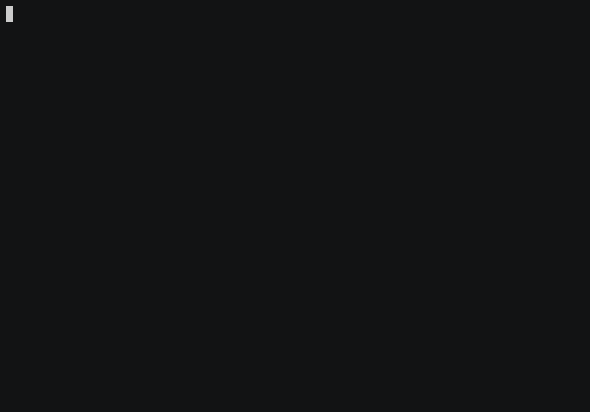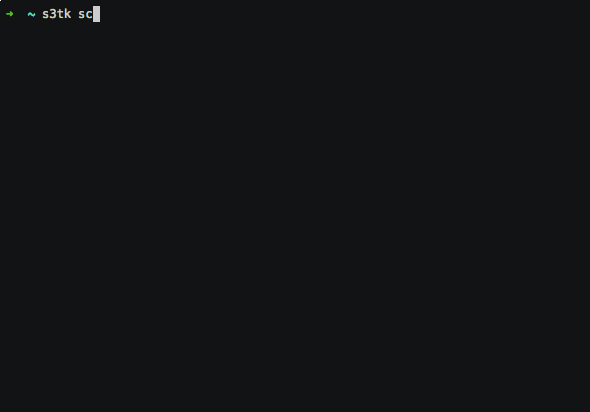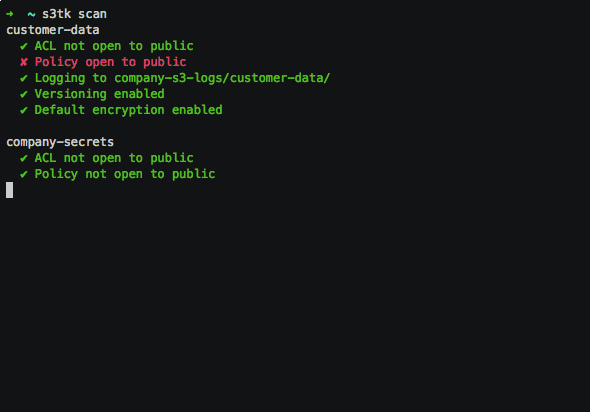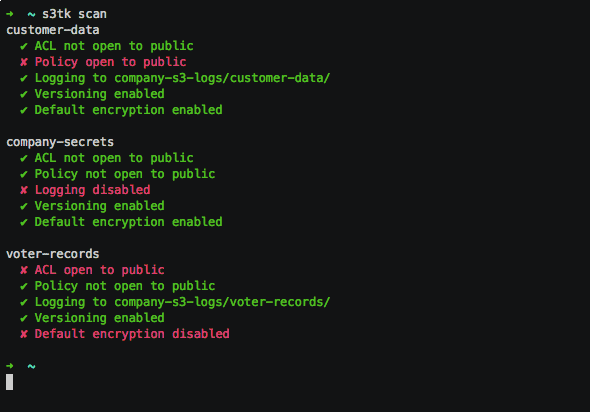 ankane/s3tk
A security toolkit for Amazon S3
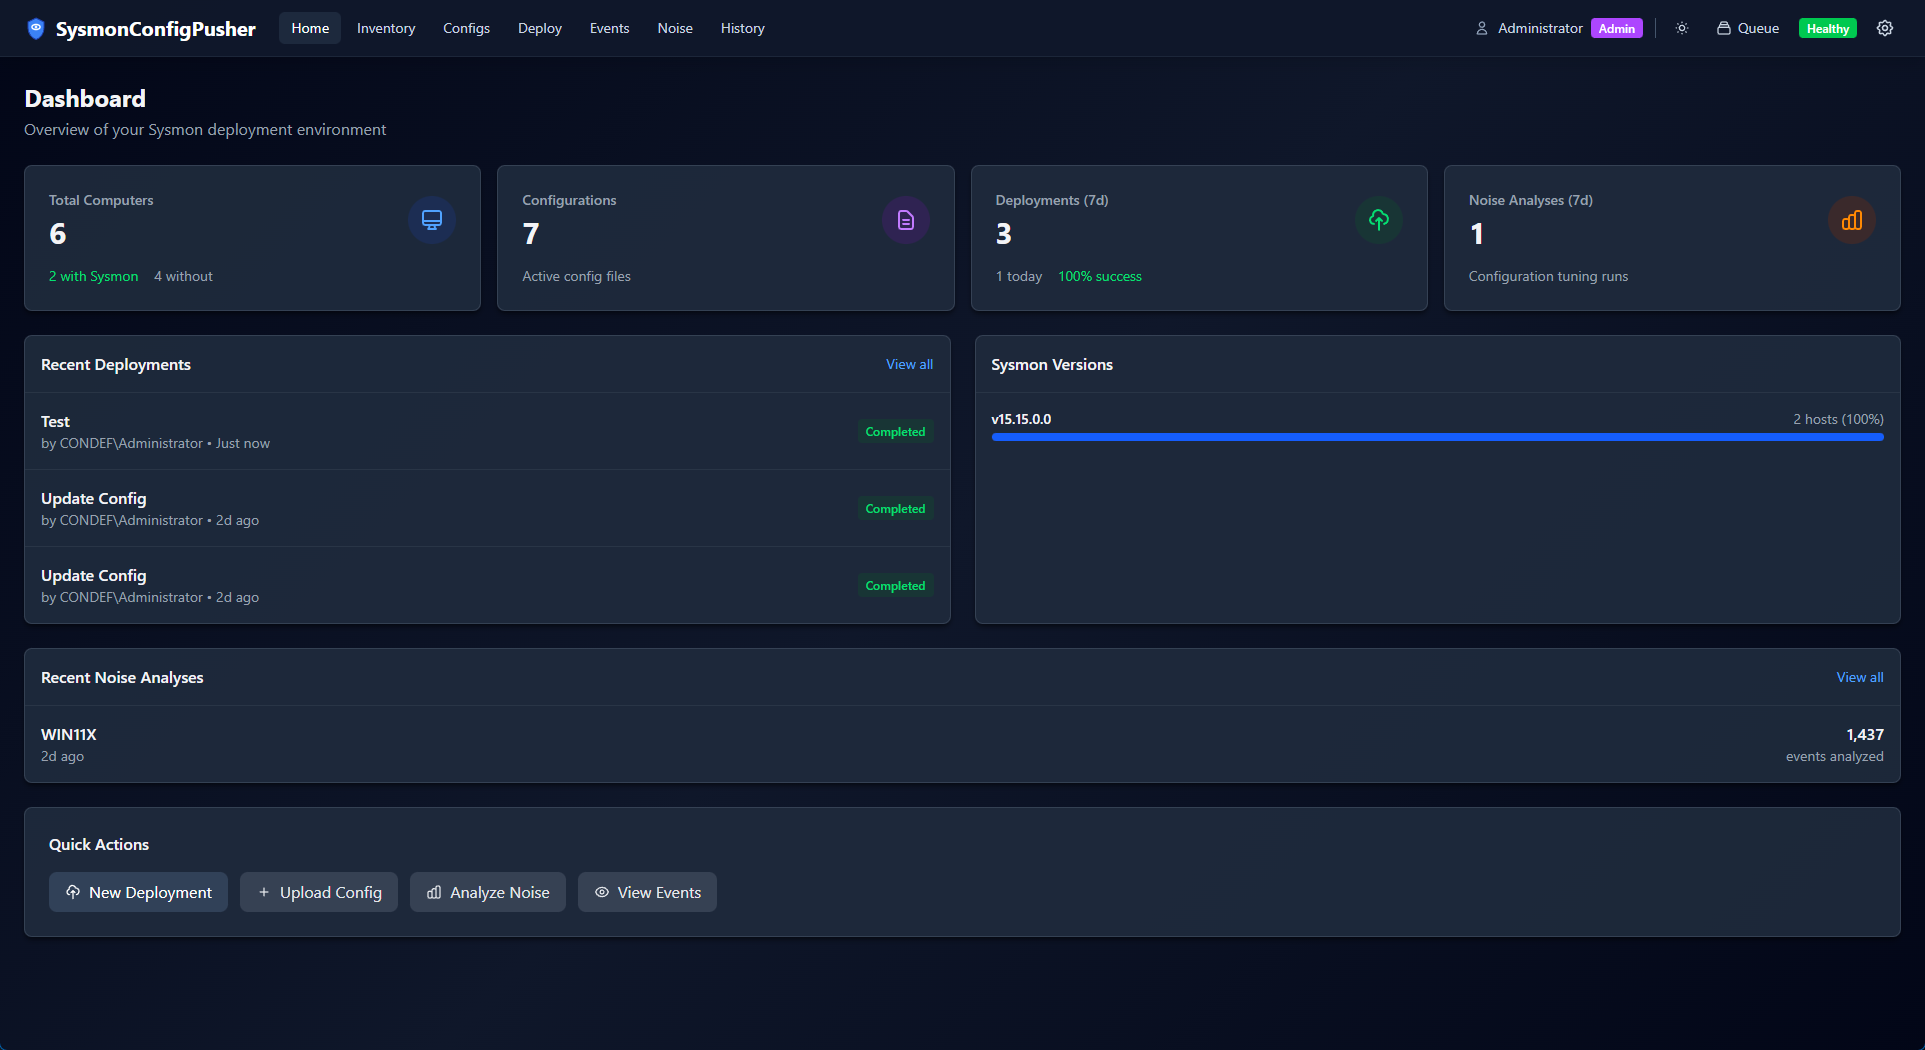 antonlovesdnb/sysmonconfigpusher2
Web-based tool for managing and deploying Sysmon configurations across Windows endpoints via agentless (WMI/SMB) or agent-based methods, with remote…
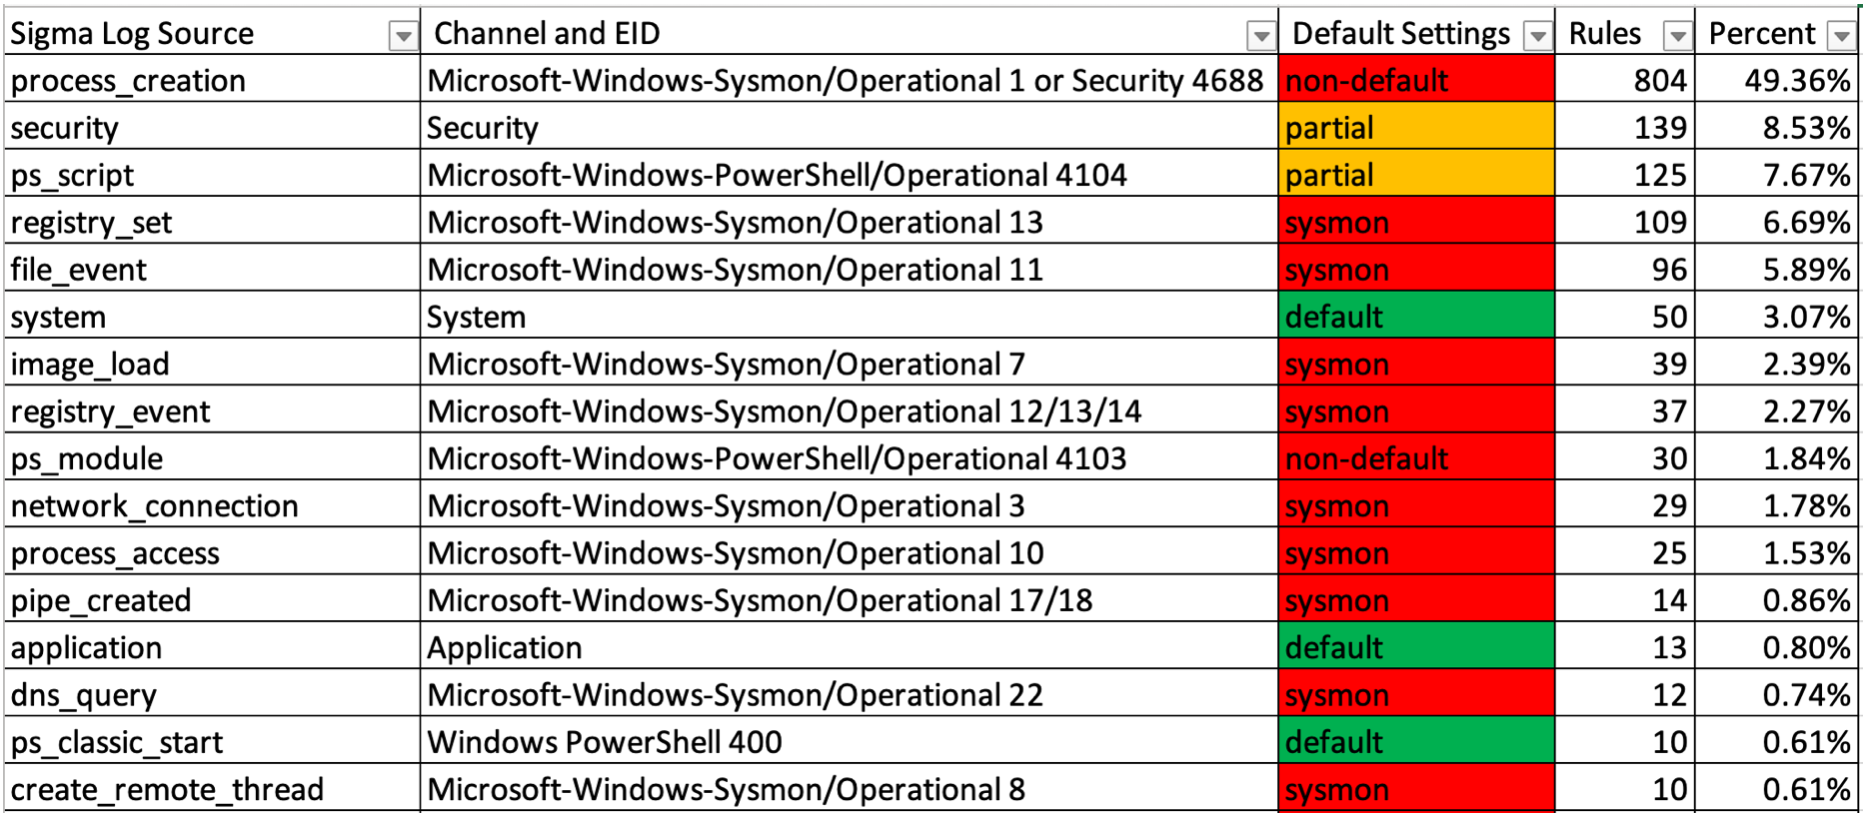 yamato-security/enablewindowslogsettings
Documentation and scripts to properly enable Windows event logs.
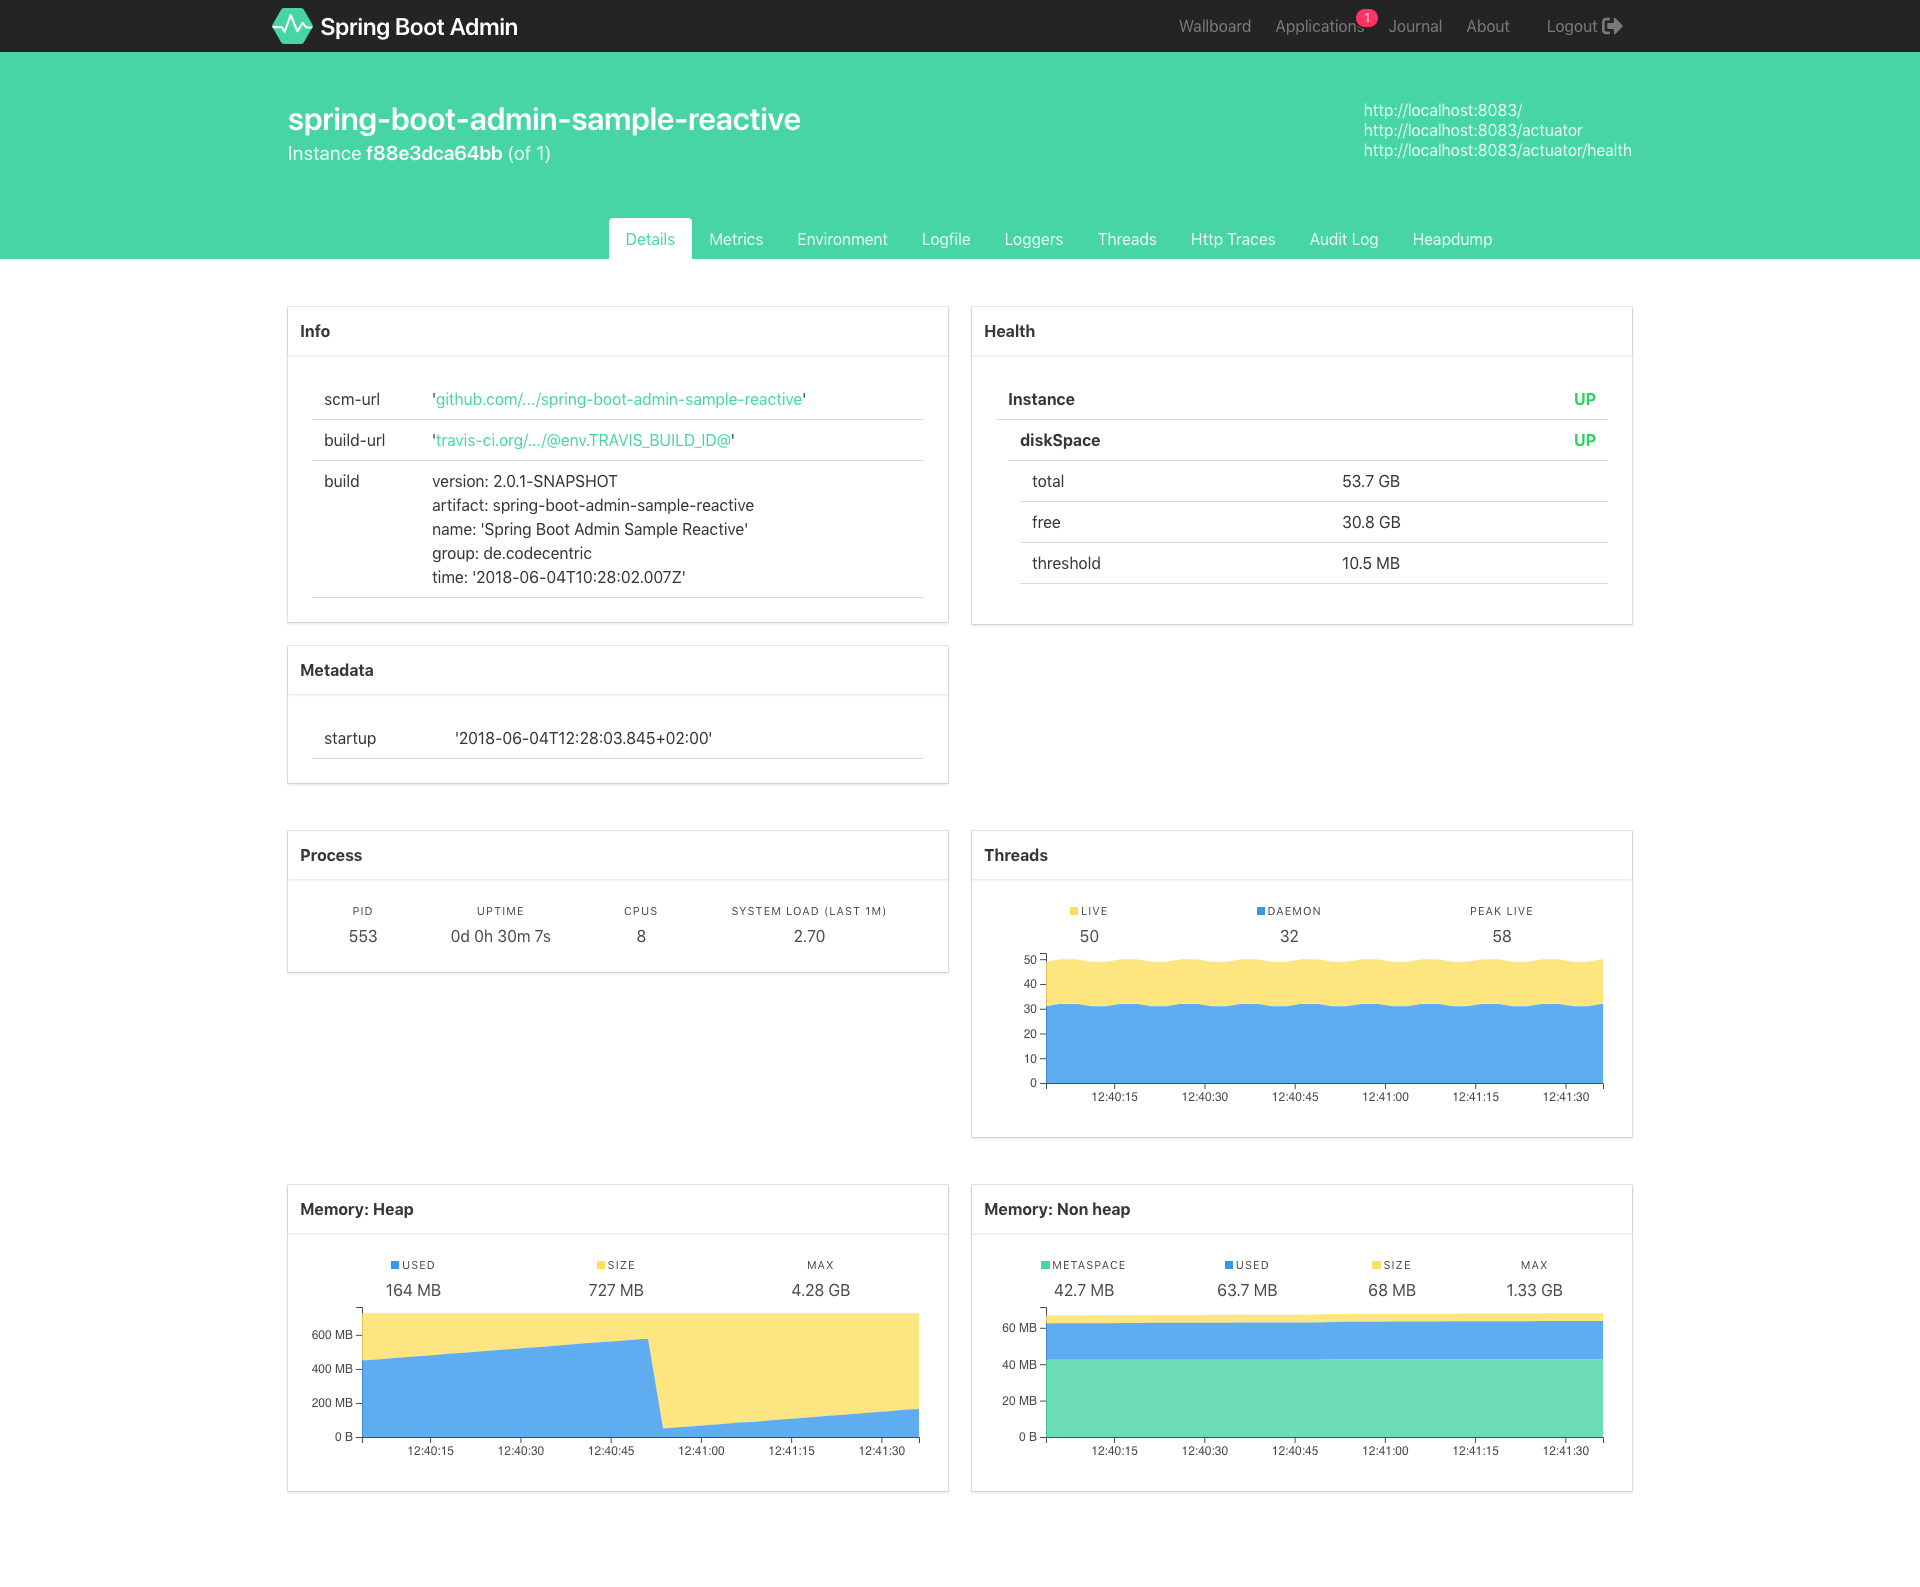 shoucheng3/codecentric__spring-boot-admin_cve-2022-46166_2-6-9
Admin interface for monitoring Spring Boot applications with health checks, metrics, log management, JMX interaction, and thread dump viewing.
 zenzue/cve-2025-50154
PowerShell toolkit to audit, harden, and hunt for insecure NTLM/SMB usage, addressing CVE-2025-50154 credential leak risks with event log analysis…
 githubfoam/nxlog-ubuntu-githubactions
CI pipeline for building nxlog-ce on Ubuntu with CVE-2020-35488 vulnerability detection, enabling automated log collection and security auditing in…
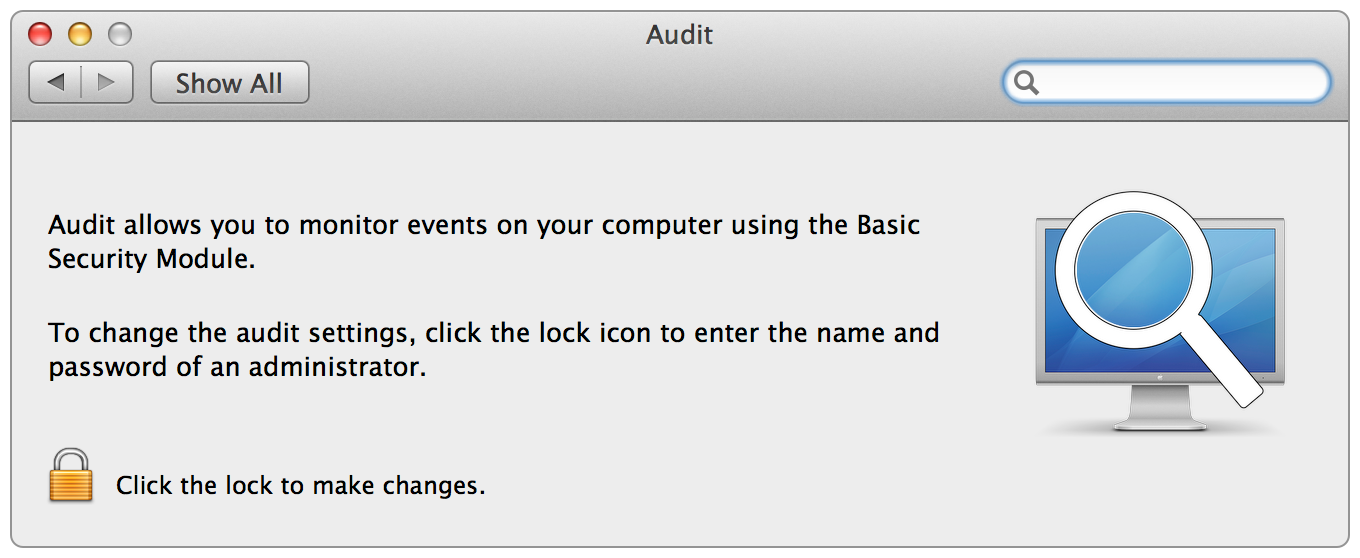 twocanoes/audit
Audit Preference Pane and Log Reader for OS X