 ankane/s3tk
A security toolkit for Amazon S3

A security toolkit for Amazon S3
🍊 Battle-tested at Instacart
Run:
pip install s3tk
You can use the AWS CLI or AWS Vault to set up your AWS credentials:
pip install awscli
aws configure
See IAM policies needed for each command.
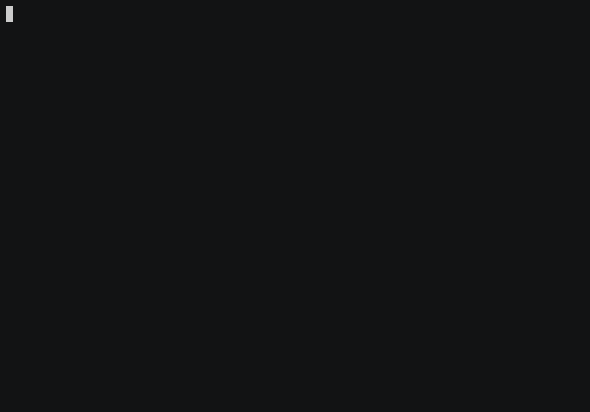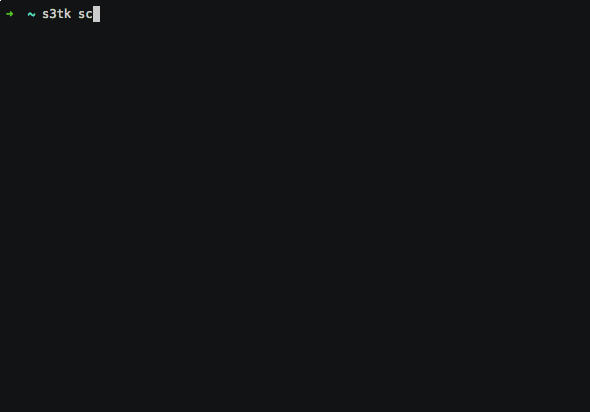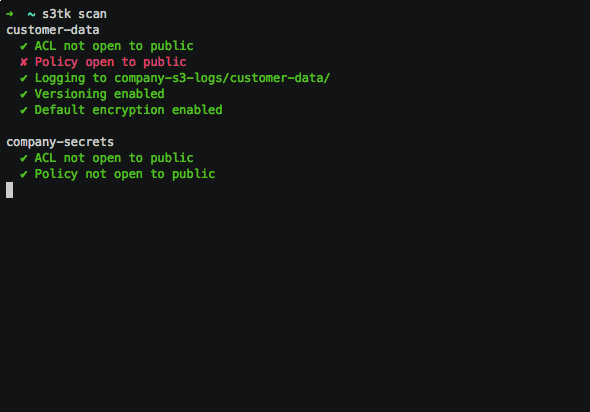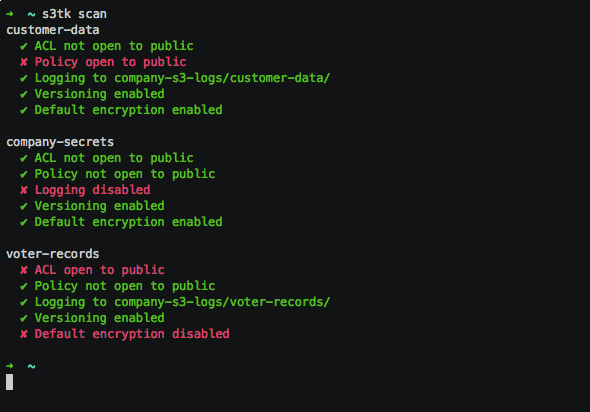
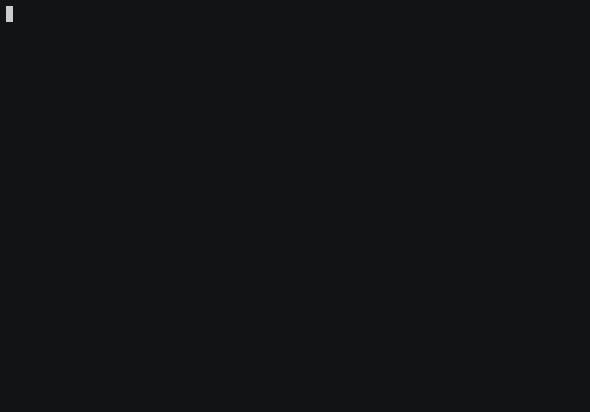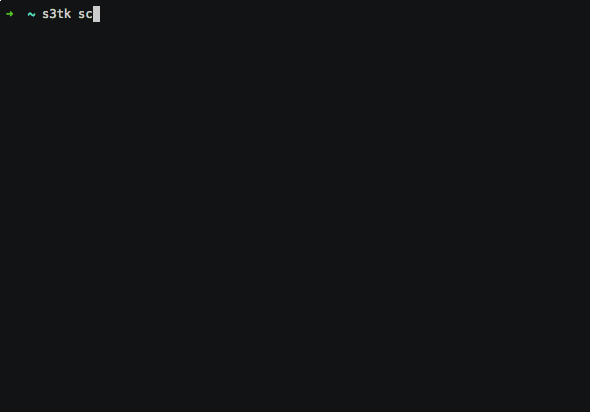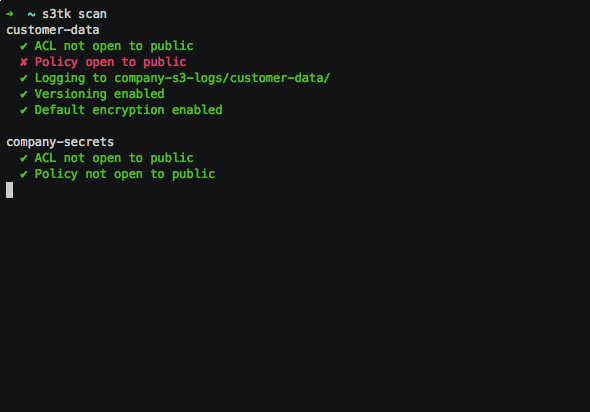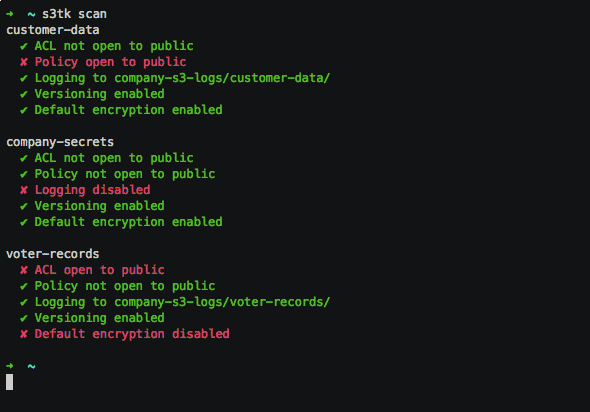
Scan your buckets for:
s3tk scan
Only run on specific buckets
s3tk scan my-bucket my-bucket-2
Also works with wildcards
s3tk scan "my-bucket*"
Confirm correct log bucket(s) and prefix
s3tk scan --log-bucket my-s3-logs --log-bucket other-region-logs --log-prefix "{bucket}/"
Check CloudTrail object-level logging [experimental]
s3tk scan --object-level-logging
Skip logging, versioning, or default encryption
s3tk scan --skip-logging --skip-versioning --skip-default-encryption
Get email notifications of failures (via SNS)
s3tk scan --sns-topic arn:aws:sns:...
List bucket policies
s3tk list-policy
Only run on specific buckets
s3tk list-policy my-bucket my-bucket-2
Show named statements
s3tk list-policy --named
Note: This replaces the previous policy
Only private uploads
s3tk set-policy my-bucket --no-object-acl
Delete policy
s3tk delete-policy my-bucket
Block public access on specific buckets
s3tk block-public-access my-bucket my-bucket-2
Use the --dry-run flag to test
Enable logging on all buckets
s3tk enable-logging --log-bucket my-s3-logs
Only on specific buckets
s3tk enable-logging my-bucket my-bucket-2 --log-bucket my-s3-logs
Set log prefix ({bucket}/ by default)
s3tk enable-logging --log-bucket my-s3-logs --log-prefix "logs/{bucket}/"
Use the --dry-run flag to test
A few notes about logging:
Enable versioning on all buckets
s3tk enable-versioning
Only on specific buckets
s3tk enable-versioning my-bucket my-bucket-2
Use the --dry-run flag to test
Enable default encryption on all buckets
s3tk enable-default-encryption
Only on specific buckets
s3tk enable-default-encryption my-bucket my-bucket-2
This does not encrypt existing objects - use the encrypt command for this
Use the --dry-run flag to test
Scan ACL on all objects in a bucket
s3tk scan-object-acl my-bucket
Only certain objects
s3tk scan-object-acl my-bucket --only "*.pdf"
Except certain objects
s3tk scan-object-acl my-bucket --except "*.jpg"
Reset ACL on all objects in a bucket
s3tk reset-object-acl my-bucket
This makes all objects private. See bucket policies for how to enforce going forward.
Use the --dry-run flag to test
Specify certain objects the same way as scan-object-acl
Encrypt all objects in a bucket with server-side encryption
s3tk encrypt my-bucket
Use S3-managed keys by default. For KMS-managed keys, use:
s3tk encrypt my-bucket --kms-key-id arn:aws:kms:...
For customer-provided keys, use:
s3tk encrypt my-bucket --customer-key secret-key
Use the --dry-run flag to test
Specify certain objects the same way as scan-object-acl
Note: Objects will lose any custom ACL
Delete all unencrypted versions of objects in a bucket
s3tk delete-unencrypted-versions my-bucket
For safety, this will not delete any current versions of objects
Use the --dry-run flag to test
Specify certain objects the same way as scan-object-acl
Scan Route 53 for buckets to make sure you own them
s3tk scan-dns
Otherwise, you may be susceptible to subdomain takeover
Credentials can be specified in ~/.aws/credentials or with environment variables. See this guide for an explanation of environment variables.
You can specify a profile to use with:
AWS_PROFILE=your-profile s3tk
Here are the permissions needed for each command. Only include statements you need.
