

wapiti
 wapiti-scanner/wapiti
Web vulnerability scanner written in Python3
api-security-testingconfiguration-auditingcrawler+11
wapiti-scanner/wapitiWeb vulnerability scanner written in Python3
 owasp/trisuella-aidlca-framework
Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…
 owasp/openshield
Open source CSPM for Azure - scan for misconfigurations and quantum-unsafe cryptography, map findings to CIS/NIST/ISO27001/SOC2, and fix them with…
 owasp/software-component-verification-standard
Software Component Verification Standard (SCVS)
 asamassekou10/ship-safe
The independent security agent for AI-written software. Finds issues, investigates whether they are real, and shows you the evidence. Deterministic…
 zappaboy/vuln-scanner
Vulnerability Assessment Scanner with Report Generation
 cspf-founder/api-scanner-docker
Automated API security testing tool that scans REST and SOAP APIs for vulnerabilities using OpenAPI/Swagger specs and WSDL files. Deploys a full …
 cropnet/ni8mare
Comprehensive vulnerability detection tool for n8n workflow automation instances. Detects the critical CVE-2026-21858 vulnerability (CVSS 10.0)…
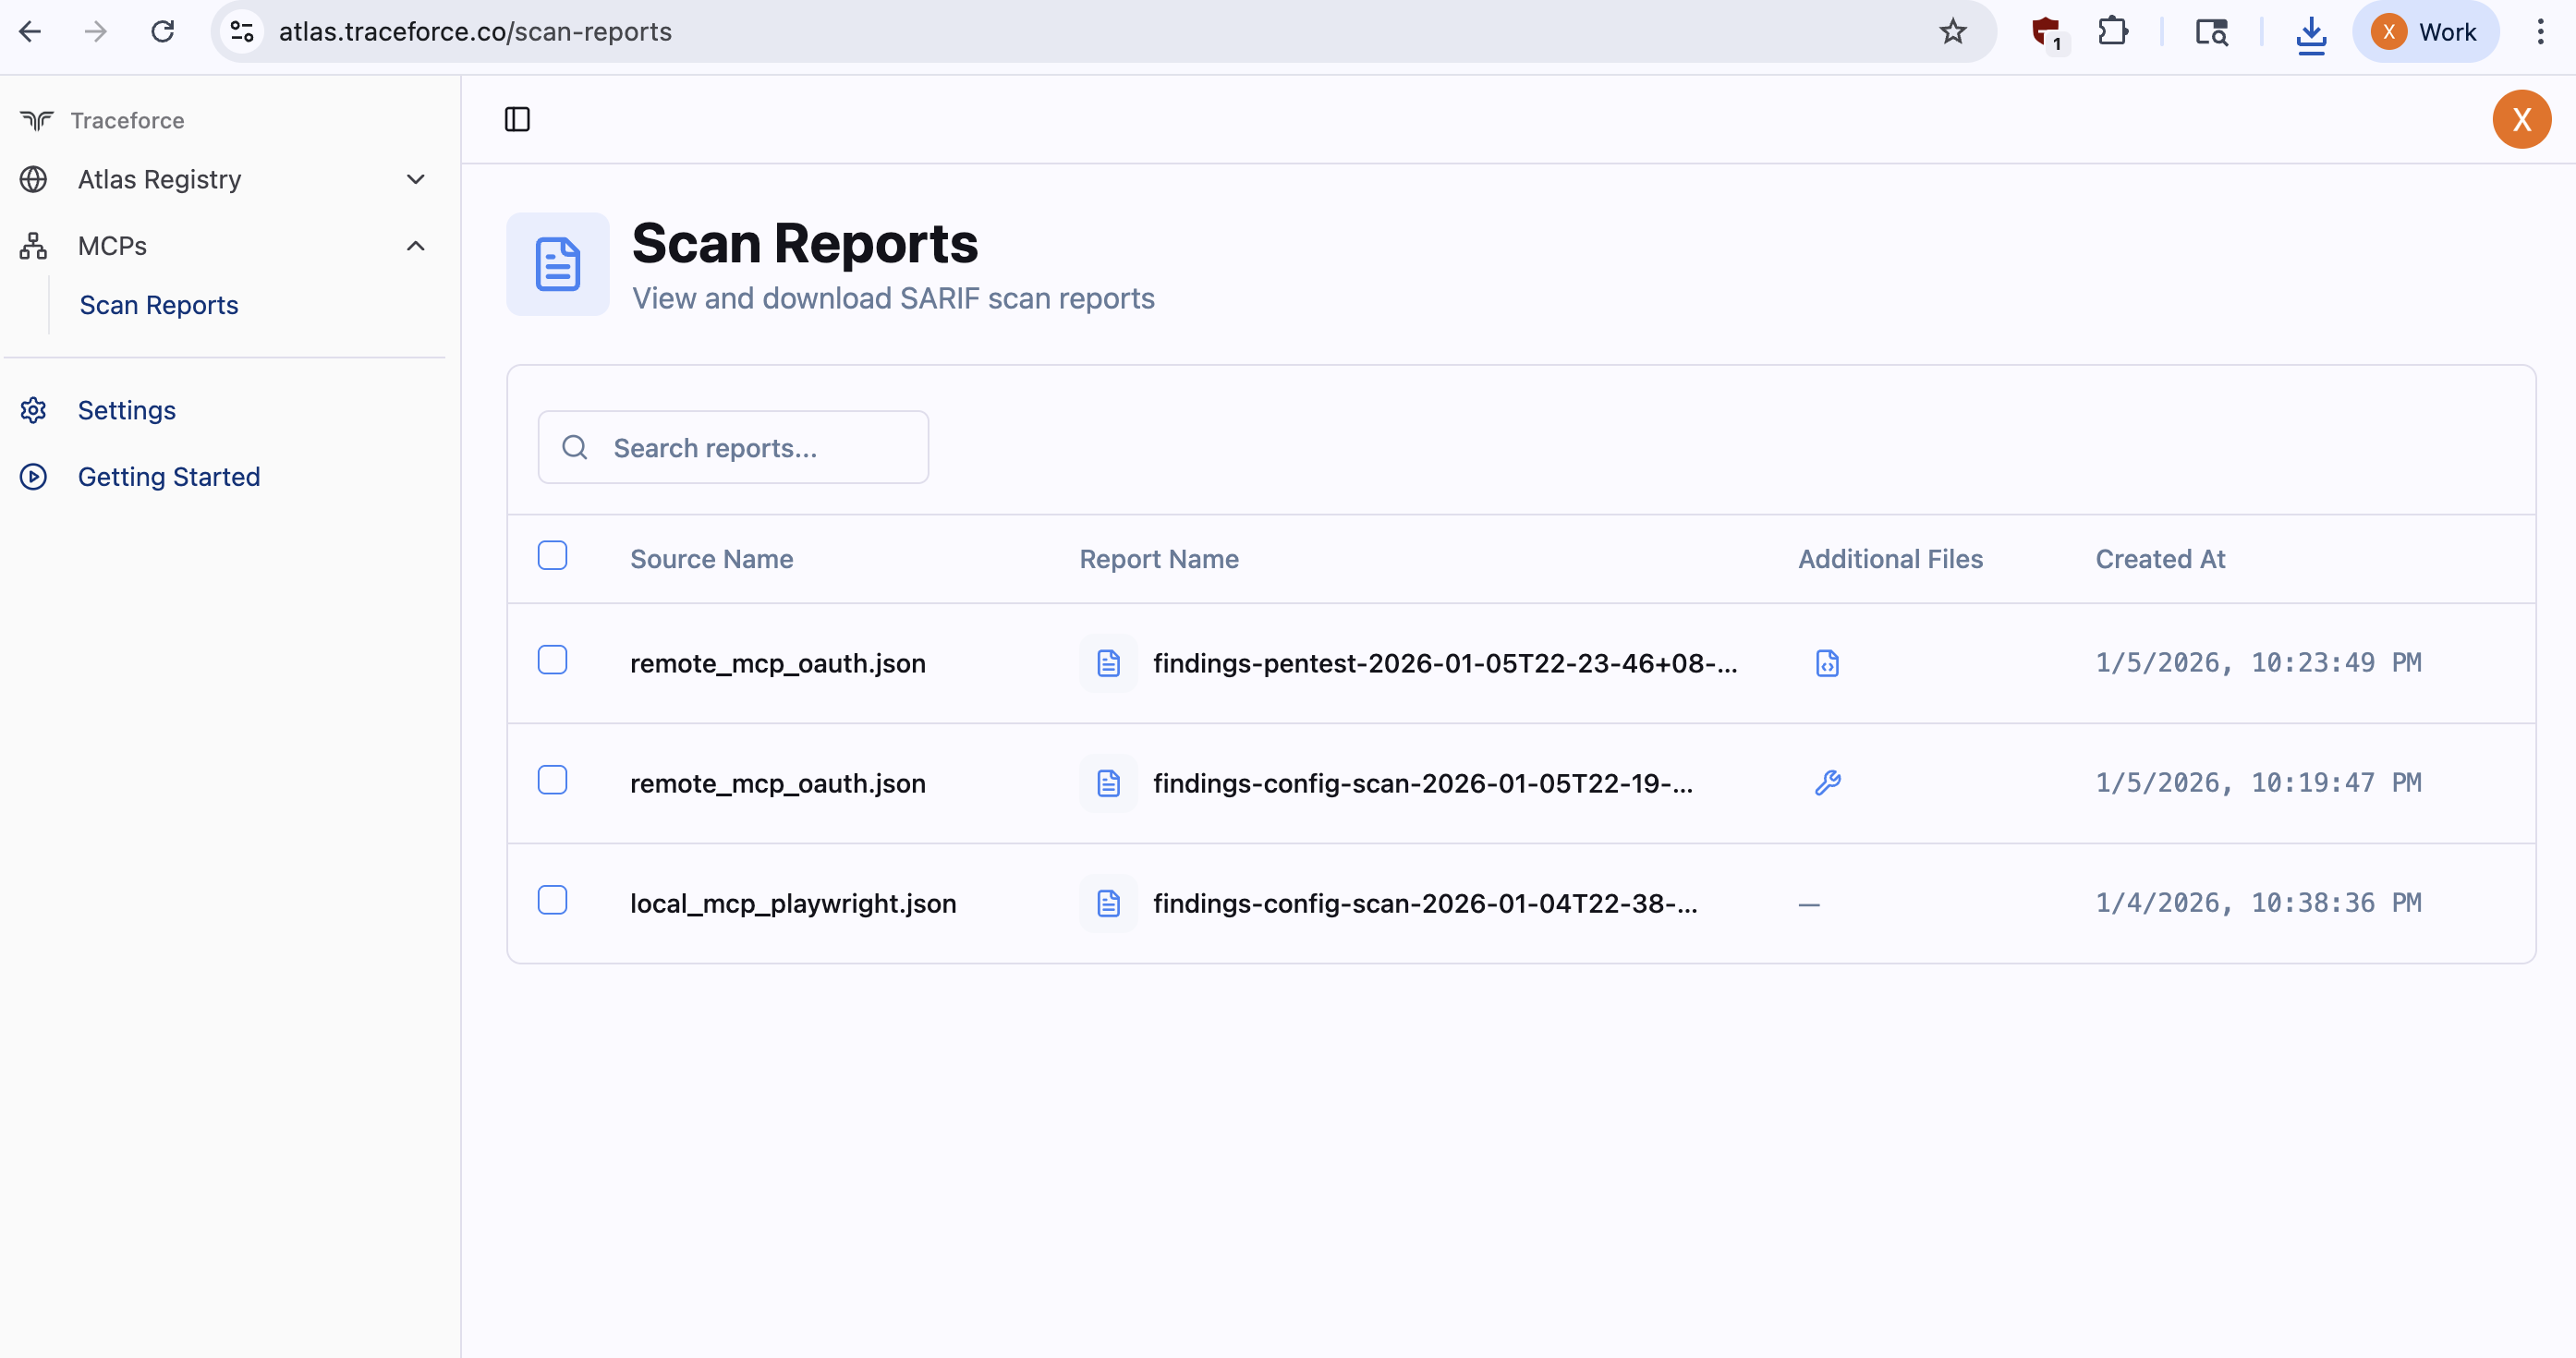 traceforce/mcp-xray
Unified security scanner for MCP servers with config, pentest, and repo-scan modes. Generates SARIF reports for CI/CD integration, detects secrets,…
 owasp/packman
A documentation and tracking project with the goal of making package management systems more secure.
 owasp/docker-security
Getting a handle on container security
 havoc10-sw/detect_polyfill_cve-2024-38537-
Here's a Python script that checks if the polyfill.io domain is present in the Content Security Policy (CSP) header of a given web application.
 brunoh6/web-threat-mitigation
Hands-on lab on detecting and mitigating web app threats using OWASP ZAP, Burp Suite, and ModSecurity WAF (with OWASP CRS). Case study: Spring4Shell…
 owasp/sedated
SEDATED® Project (Sensitive Enterprise Data Analyzer To Eliminate Disclosure)
 owasp/open-sammy
Web-based tool for assessing and tracking software security maturity using the OWASP SAMM and DSOMM models, with Docker support and automated mailing.
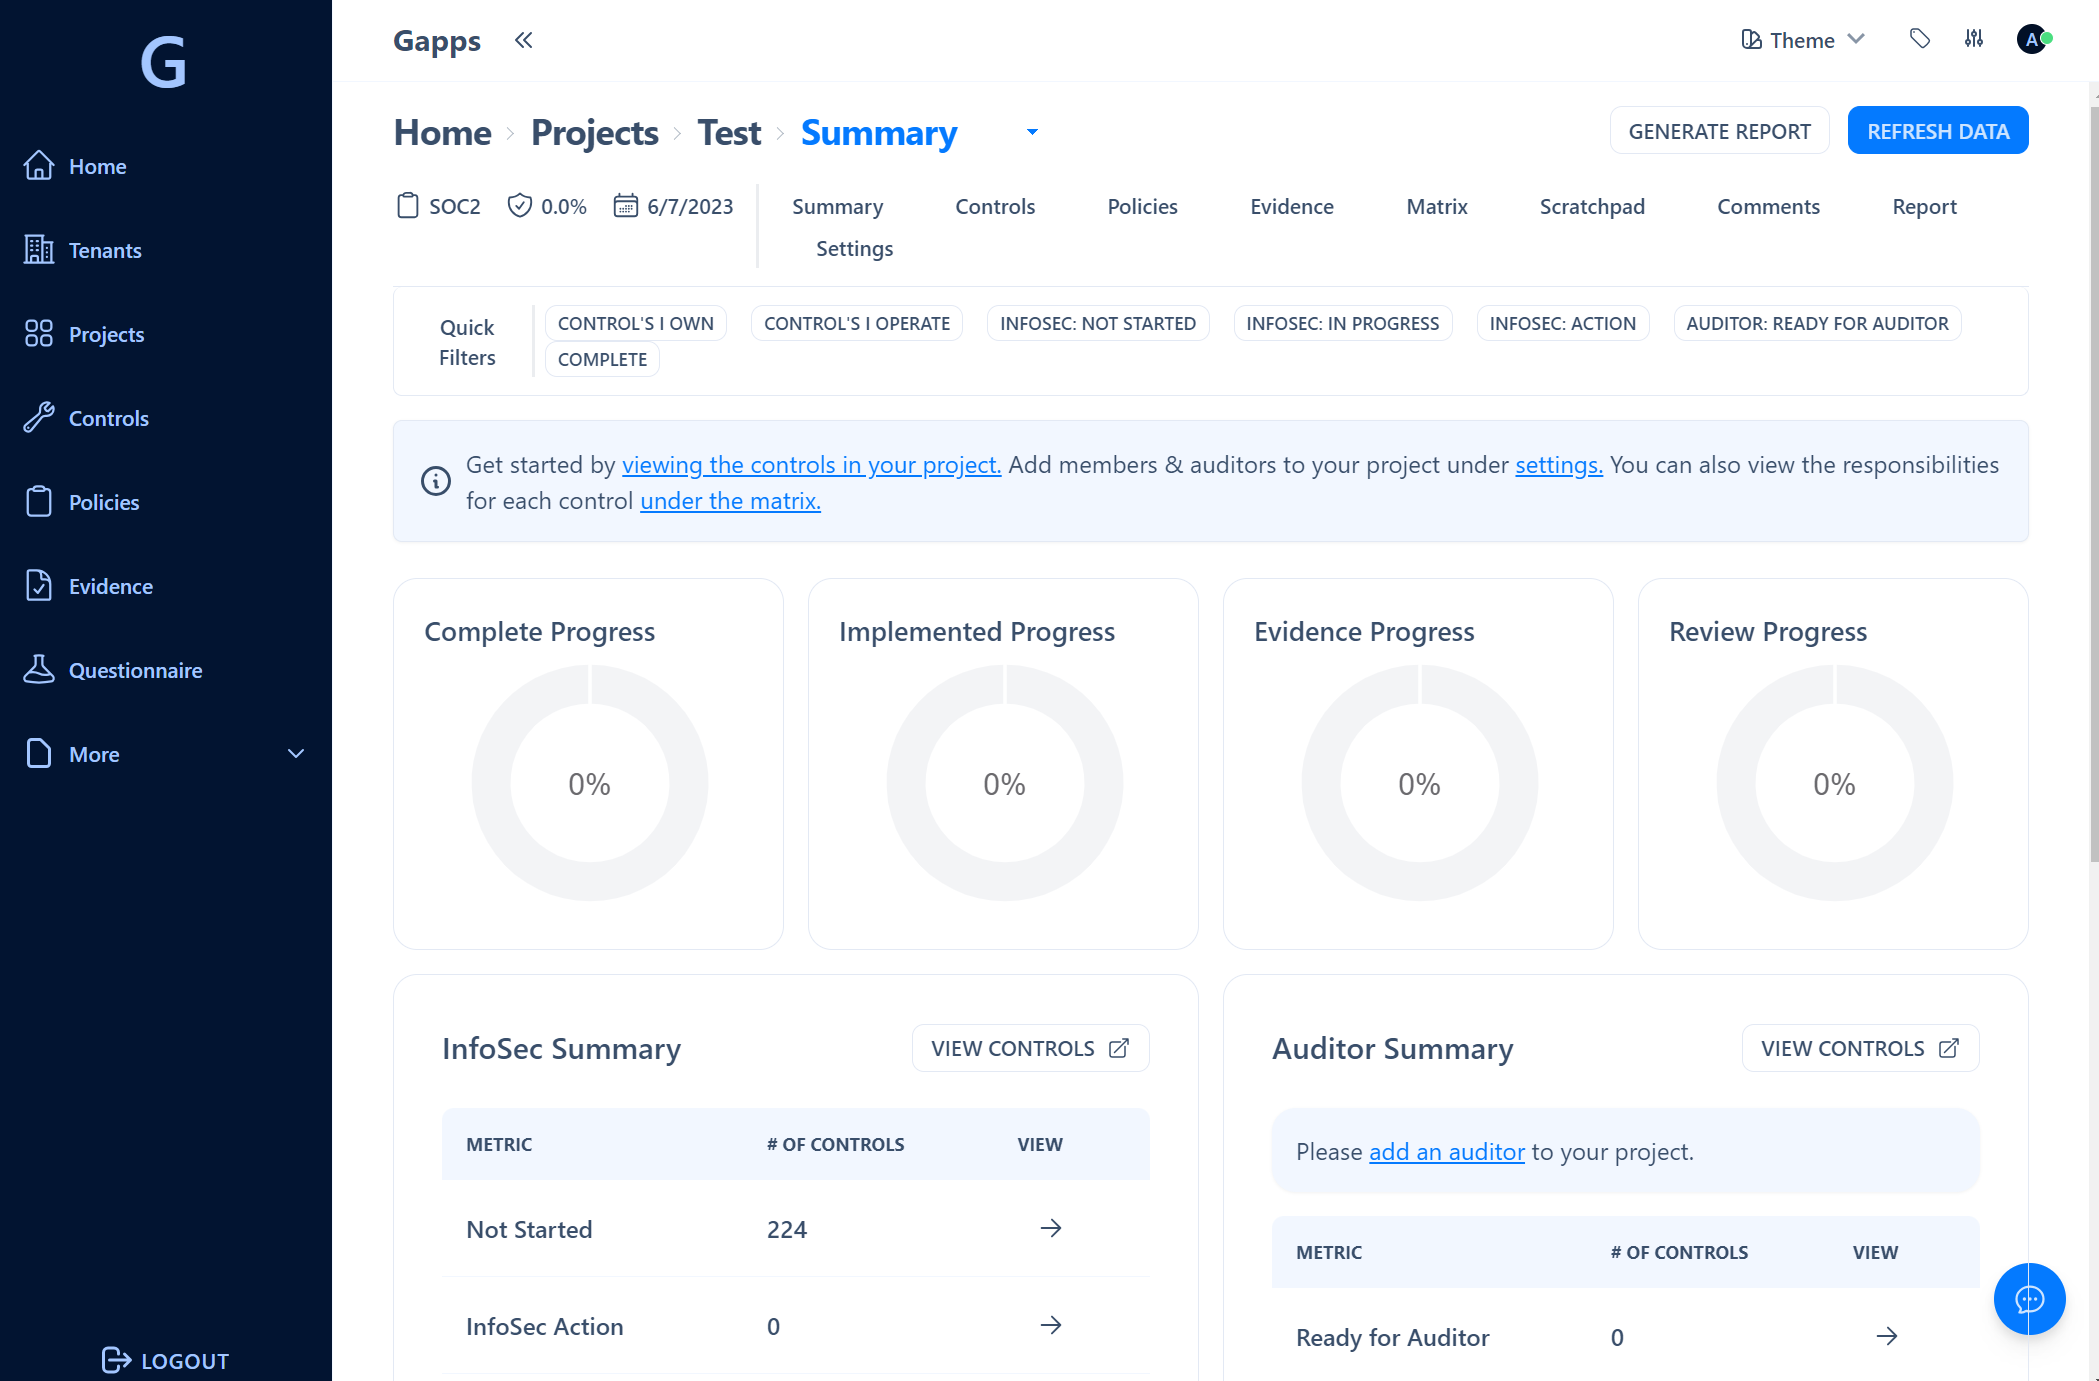 bmarsh9/gapps
Security compliance platform - SOC2, CMMC, ASVS, ISO27001, HIPAA, NIST CSF, NIST 800-53, CSC CIS 18, PCI DSS, SSF tracking
 owasp/kubelight
OWASP Kubernetes security and compliance tool [WIP]
 owasp/sapkiln
OWASP SAPKiln is a graphical user interface (GUI) tool designed to facilitate securing and auditing SAP systems effectively.