
CVE-2025-55182
 rix4uni/cve-2025-55182
A command-line tool for detecting CVE-2025-55182 and CVE-2025-66478 in Next.js applications using React Server Components.
command-and-controlexploitationinformation-gathering+4
6
rix4uni/cve-2025-55182A command-line tool for detecting CVE-2025-55182 and CVE-2025-66478 in Next.js applications using React Server Components.
 zamdevio/r2s
Advanced security testing tool for CVE-2025-55182 vulnerability assessment in Next.js applications. Features interactive shell, batch scanning, WAF…
 splunk/melting-cobalt
A Cobalt Strike Scanner that retrieves detected Team Server beacons into a JSON object
 nccgroup/steppingstones
Web-based red team activity logging, reporting, and situational awareness tool with Cobalt Strike and BloodHound integration.
 thundergunexpress/badministration
Offensive tool for exploiting management applications (SolarWinds Orion, McAfee ePO) via non-technical vulnerabilities. Enables client enumeration,…
 quantum-sicarius/cve-2024-49369
Exploit tool for CVE-2024-49369 in Icinga, enabling subnet scanning, agent takeover via JSON-RPC impersonation, arbitrary command execution, and…
 imbas007/cve-2025-25257
Python-based exploit tool for CVE-2025-25257 in FortiWeb. Automates SQL injection detection, webshell upload, and remote command execution on…
 m8sec/activereign
A Network Enumeration and Attack Toolset for Windows Active Directory Environments.

 yukibtc/redknife
A Swiss Army knife for offensive security.
 ad0nis/ntlm_relay_gat
Automates NTLM relay exploitation using ntlmrelayx.py for SMB share enumeration, shell execution, secrets dumping, and MSSQL command execution via…
 marten4n6/evilosx
An evil RAT (Remote Administration Tool) for macOS / OS X.
 st3rven/fronthunter
FrontHunter is a tool for testing large lists of domains to identify candidates for domain fronting.
 gmh5225/mcp-god-mode
Did you ever just want it to do everything? 148 POWERFUL Infosec/Admin tools on a single MCP server.
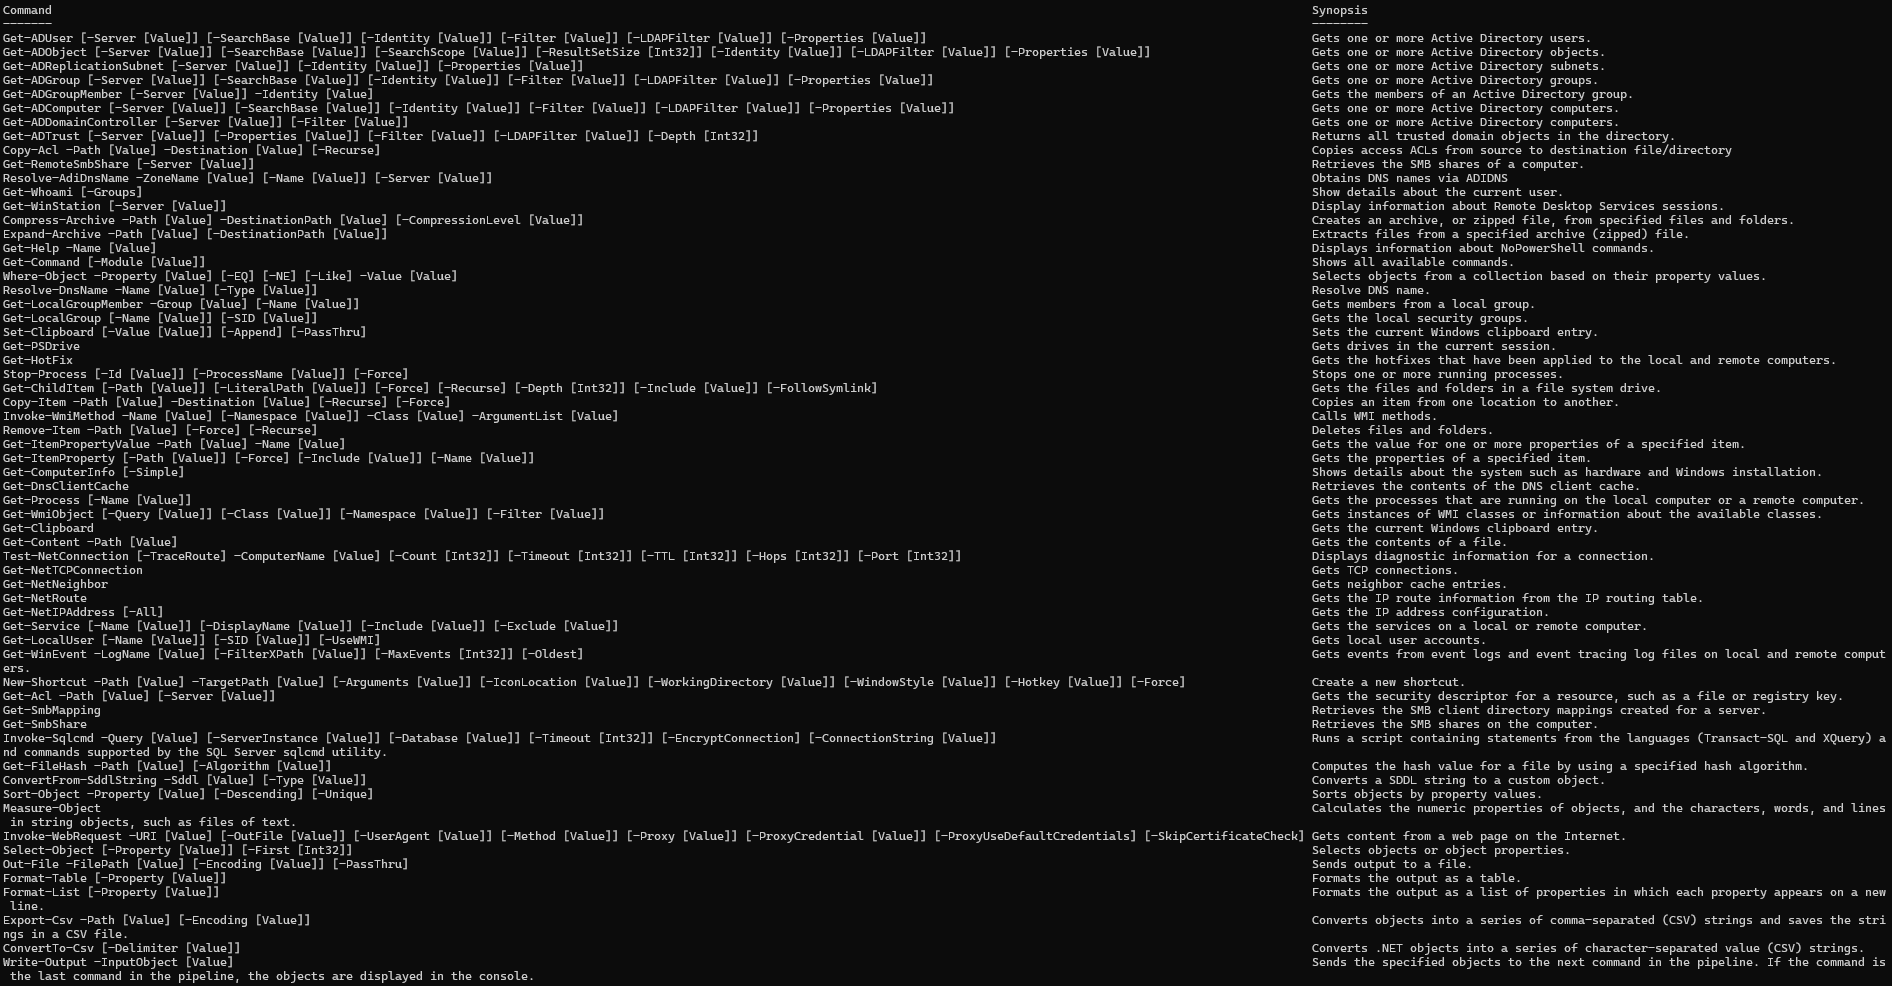 bitsadmin/nopowershell
PowerShell rebuilt in C# for Red Teaming purposes
 redsiege/wmimplant
This is a PowerShell based tool that is designed to act like a RAT. Its interface is that of a shell where any command that is supported is…
 lucasjacks0n/eggshell
iOS/macOS/Linux Remote Administration Tool
 thelsa/f5-bigip-rce-cve-2020-5902
F5 BIG-IP RCE CVE-2020-5902 automatic check tool
 exdev994/cve-2026-4631-cockpit-rce
Unauthenticated Remote Code Execution via SSH Command-Line Argument Injection Cockpit versions 327 – 359 | CVSS 9.8 Critical | CWE-78