
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
86 results
blue-pigeon preview

blue-pigeon

GitHubbluepigeonproject/blue-pigeon

Blue Pigeon is a Bluetooth-based data exfiltration and proxy tool to enable communication between a remote Command and Control (C2) server and a…
android-securitybluetooth-securitycommand-and-control+4
57
5 years ago
GeckoDroid preview

GeckoDroid

GitHubblacksnufkin/geckodroid

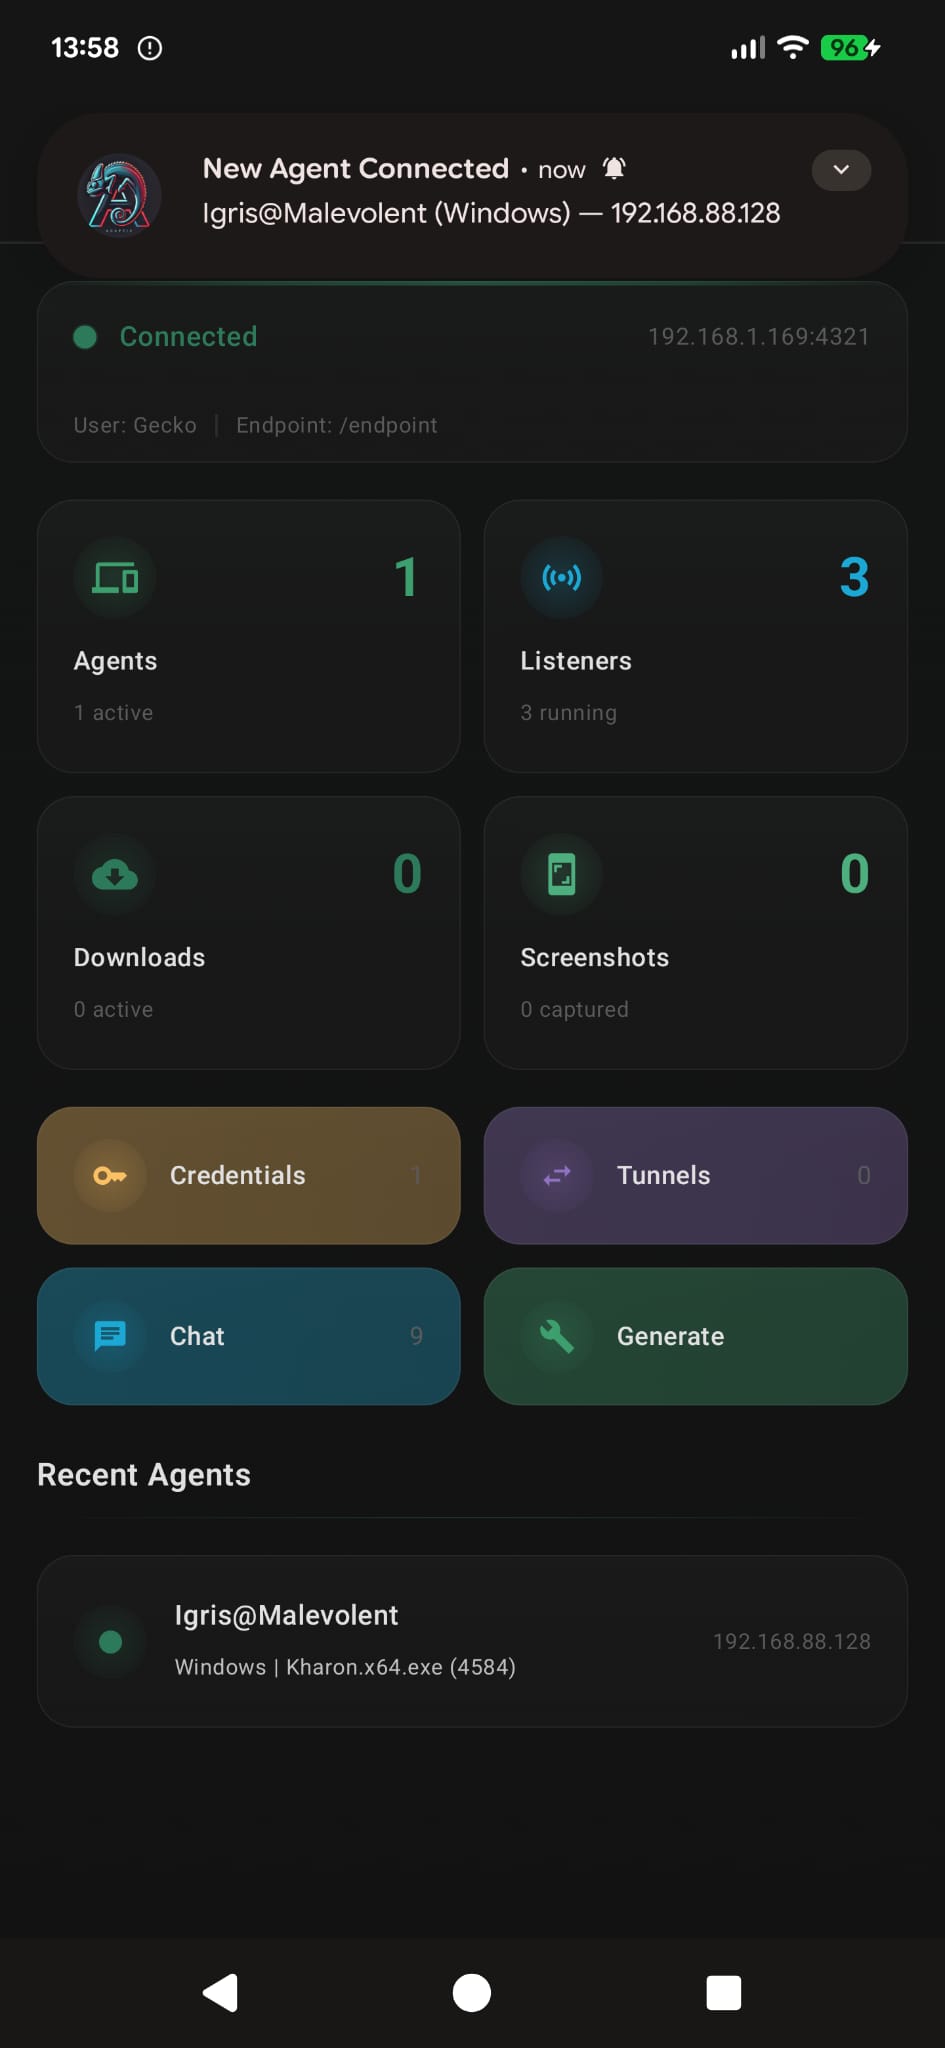
Android client for Adaptix C2 framework enabling remote agent management, interactive command shells, listener control, payload generation, and…

android-securitycommand-and-controlmobile-security+4
396 months ago
PureRAT-msbuild.exe--C2-Extraction--Net-Evasion-Analysis preview

PureRAT-msbuild.exe--C2-Extraction--Net-Evasion-Analysis

GitHubkaandemir993/purerat-msbuild.exe--c2-extraction--net-evasion-analysis

Reverse engineering analysis of PureRAT RAT abusing msbuild.exe, extracting C2 infrastructure, .NET evasion APIs, file system manipulation, and…
binary-analysiscommand-and-controldefensive-tools+6
1610 days ago
Chimera preview

Chimera

GitHubcipher-attack/chimera

Payload injector and HID emulator for Android like Hak5 and rubber ducky

android-securitybluetooth-securitycommand-and-control+4
253 months ago
PHPStudy-Backdoor preview

PHPStudy-Backdoor

GitHubjas502n/phpstudy-backdoor

phpstudy dll backdoor for v2016 and v2018
command-and-controlmalware-analysispayload-development+4
197 years ago
Lumma-Stealer-dllhost-Hollowing-C2-Domains-Payload-Extraction-Analysis preview

Lumma-Stealer-dllhost-Hollowing-C2-Domains-Payload-Extraction-Analysis

GitHubkaandemir993/lumma-stealer-dllhost-hollowing-c2-domains-payload-extraction-analysis

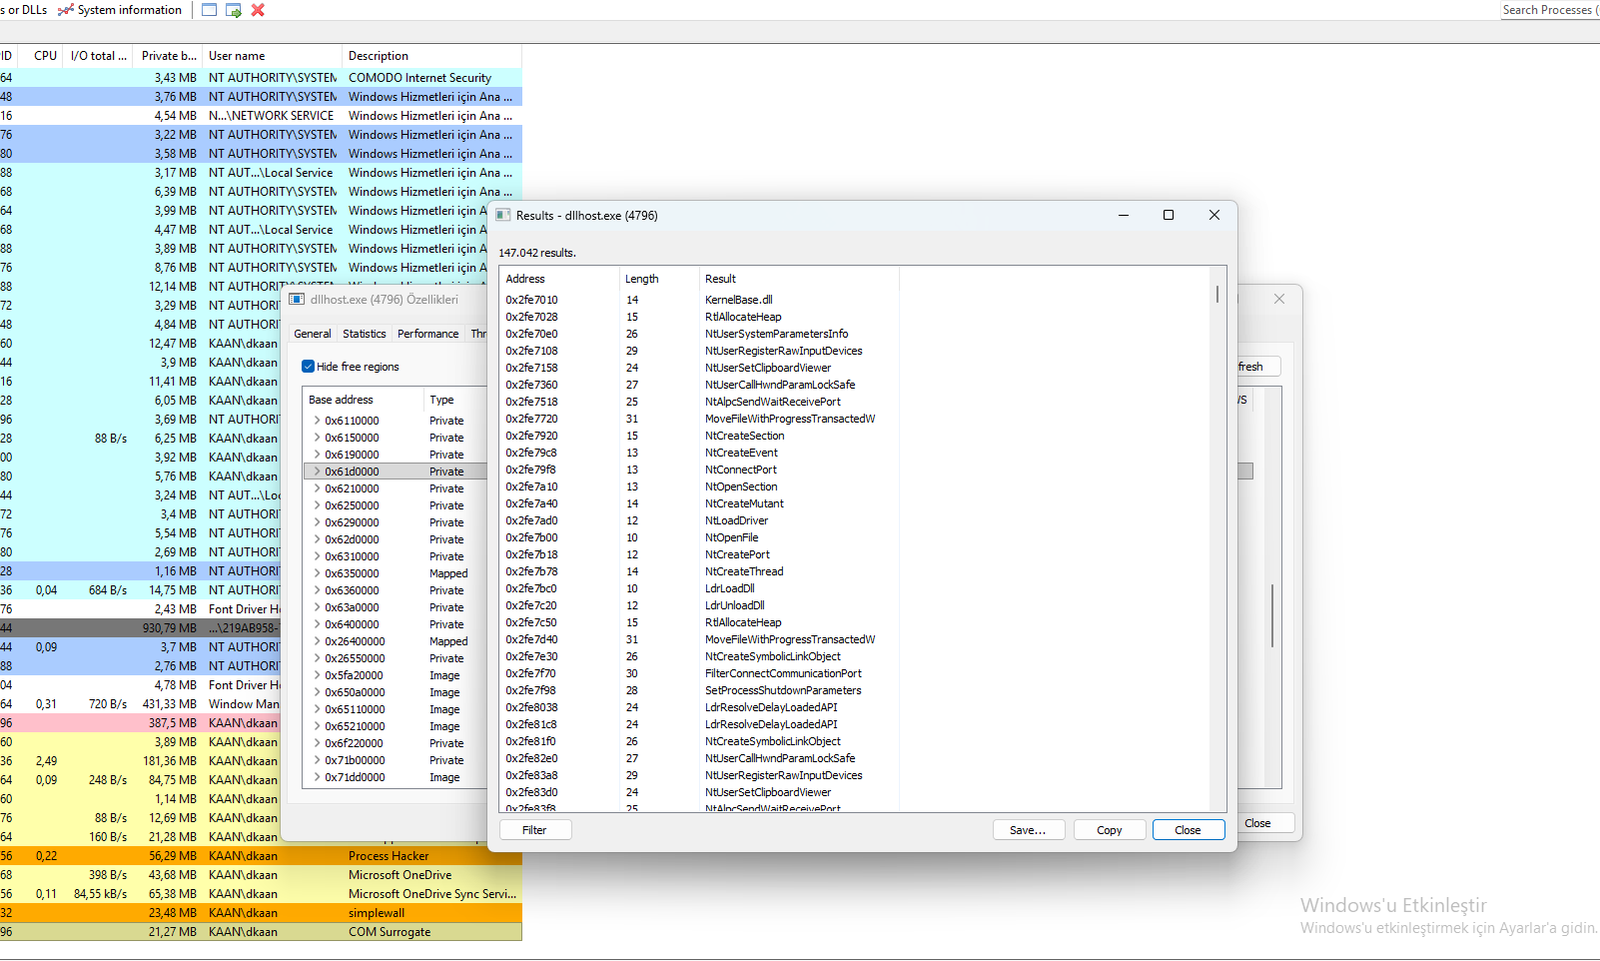
In-depth reverse engineering analysis of Lumma Stealer, an info-stealer using process hollowing, Native API calls, and C2 communication. Includes…

binary-analysiscommand-and-controldata-exfiltration+4
111 month ago
OpenShell preview

OpenShell

GitHubiss4cf0ng/openshell

Lightweight Go-based reverse shell management server with a web GUI for interactive shell sessions, session management, and multi-tab terminal…
command-and-controlpenetration-testingred-teaming+3
266 months ago
Tourmaline preview

Tourmaline

GitHubv-pun215/tourmaline

Reverse engineering notes, deobfuscated source, IOCs, and YARA rules for the Tourmaline ClickFix Python RAT, covering its DNS tunnel and blockchain…
command-and-controlcryptographydigital-forensics+7
1020 days ago
Salat-Stealer-Telegram-Proxy-Decoy-C2-Analysis preview

Salat-Stealer-Telegram-Proxy-Decoy-C2-Analysis

GitHubkaandemir993/salat-stealer-telegram-proxy-decoy-c2-analysis

"Reverse engineering analysis of Salat Stealer, a Go-based info-stealer that uses a Telegram proxy decoy, C2 communication, and encrypted memory…

binary-analysiscommand-and-controleducation+6
52 months ago
linux-root-kit preview

linux-root-kit

GitHubic3-512/linux-root-kit

End-to-end simulation of a Python dependency confusion attack, sudo privilege escalation (CVE-2025-32463), and rootkit-based persistence - with full…

command-and-controldigital-forensicseducation+8
101 year ago
StealC-Stealer-RuntimeBroker-Hollowing-C2-Extraction-Payload-Extraction-Analysis preview

StealC-Stealer-RuntimeBroker-Hollowing-C2-Extraction-Payload-Extraction-Analysis

GitHubkaandemir993/stealc-stealer-runtimebroker-hollowing-c2-extraction-payload-extraction-analysis

Reverse engineering analysis of StealC Stealer, an info-stealer that uses RuntimeBroker.exe hollowing, C2 infrastructure, and payload extraction.…
command-and-controldata-exfiltrationdigital-forensics+7
317 days ago
Dropper-GCleaner-C2-Infrastructure-Kernel-Driver-PowerShell-Conhost-Payload-Analysis preview

Dropper-GCleaner-C2-Infrastructure-Kernel-Driver-PowerShell-Conhost-Payload-Analysis

GitHubkaandemir993/dropper-gcleaner-c2-infrastructure-kernel-driver-powershell-conhost-payload-analysis

Reverse engineering analysis of Dropper GCleaner, a malware that uses a resilient C2 infrastructure, kernel driver loading, PowerShell/Conhost…
binary-analysiscommand-and-controldata-exfiltration+6
51 month ago
AcrStealer-Custom-Protocol-Credential-Theft-Payload-Extraction-Analysis preview

AcrStealer-Custom-Protocol-Credential-Theft-Payload-Extraction-Analysis

GitHubkaandemir993/acrstealer-custom-protocol-credential-theft-payload-extraction-analysis

Reverse engineering analysis of AcrStealer, a sophisticated info-stealer that uses custom protocols, browser credential theft, and payload…
binary-analysiscommand-and-controldata-exfiltration+2
31 month ago
silverboxcc preview

silverboxcc

GitHubbizdak/silverboxcc

Reverse engineered android malware, and this is a C&C server for it
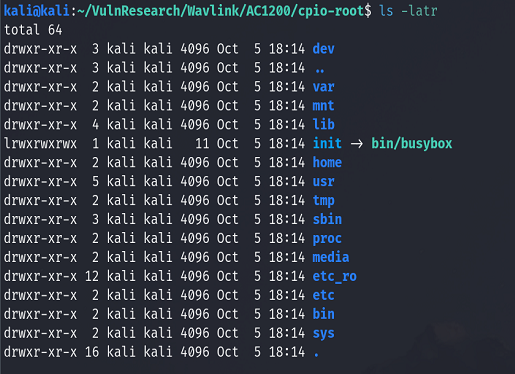
android-securitycommand-and-controlmalware-analysis+3
28 years ago
CVE-2024-48705 preview

CVE-2024-48705

GitHubl41kaa/cve-2024-48705

Wavlink AC1200 with firmware versions M32A3_V1410_230602 and M32A3_V1410_240222 are vulnerable to a post-authentication command injection while…
binary-analysiscommand-and-controlembedded-systems-security+7
21 year ago
RedLine-Stealer-C2-Defender-Bypass-Payload-Analysis preview

RedLine-Stealer-C2-Defender-Bypass-Payload-Analysis

GitHubkaandemir993/redline-stealer-c2-defender-bypass-payload-analysis

"Reverse engineering analysis of RedLine Stealer, a .NET-based info-stealer that uses C2 domains (198.46.86.63, tempuri.org), Windows Defender…
command-and-controldata-exfiltrationmalware-analysis+4
11 month ago
CVE-2021-4045 preview

CVE-2021-4045

GitHubkaleth4/cve-2021-4045

Command injection exploit for TP-Link Tapo C200 camera (CVE-2021-4045) providing root shell access via UART and reverse-engineered uhttpd binary…
command-and-controlembedded-systems-securityexploitation+6
3 months ago
Log4Shell-CVE-2021-44228 preview

Log4Shell-CVE-2021-44228

GitHubdrhaitham/log4shell-cve-2021-44228

Hands-on lab for exploiting and understanding Log4Shell (CVE-2021-44228) using Docker, Kali Linux, Burp Suite and log4j-shell-poc. For teaching and…

command-and-controleducationexploitation+7
9 months ago
Previous12345Next