metasploit-framework

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…

Original CVEs, exploit PoCs, and security advisories with detailed vulnerability chains, privilege escalation, and container escape techniques for…

Authenticated command injection PoC for D-Link R95/BE9500 DHMAPI SetTimeSettings, achieving root RCE via NTPServer backtick injection, with full…

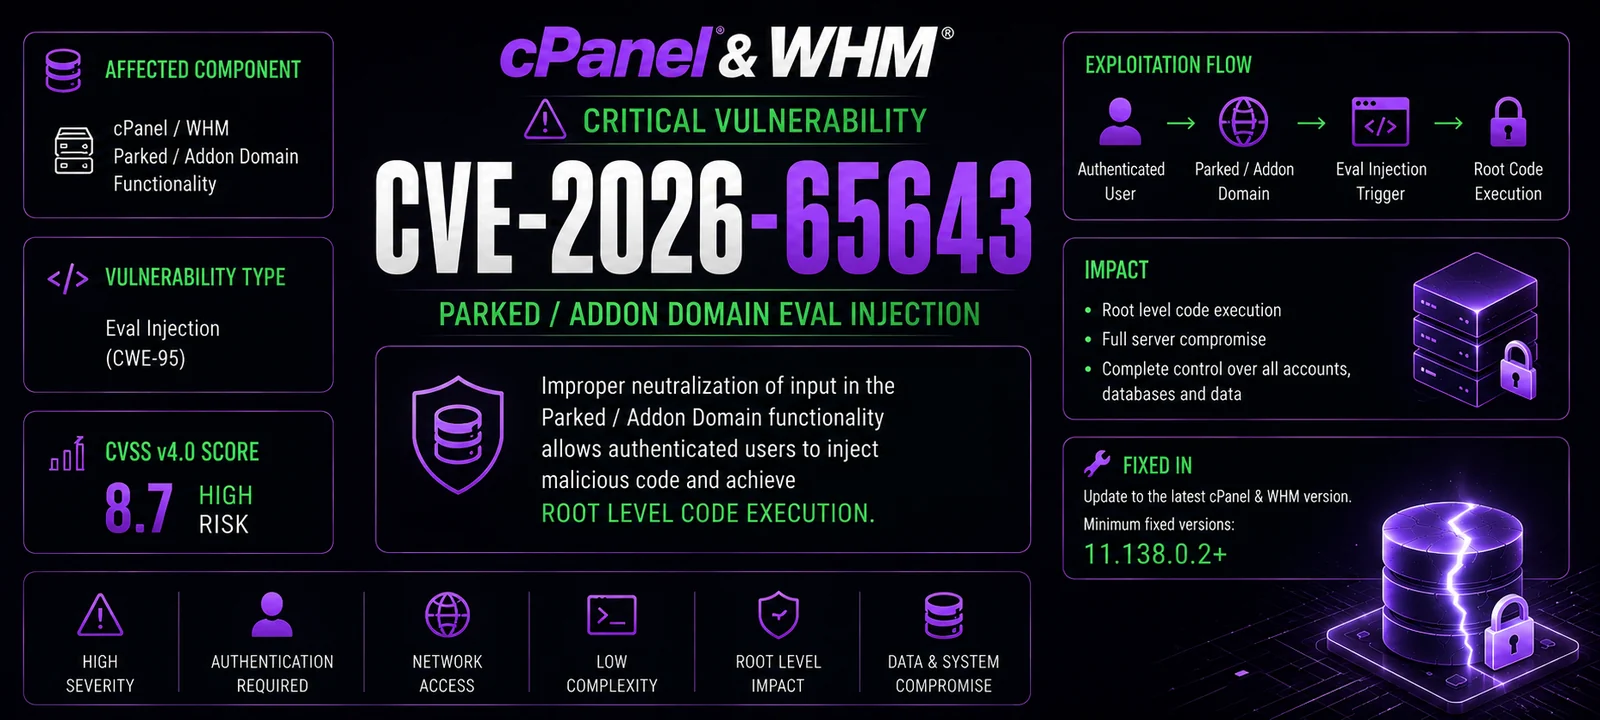
Red/Blue team toolkit for CVE-2026-65643, a cPanel domain parking RCE. Includes exploit with reverse shell, webshell, persistence, and mass scanning,…

CVE-2025-62593 — Ray Unauthenticated RCE Exploit is an unauthenticated remote code execution vulnerability in the Ray distributed AI compute engine.

Python PoC exploiting CVE-2026-19586, an unauthenticated command injection in TP-Link Omada SSL VPN that executes arbitrary commands as root via…

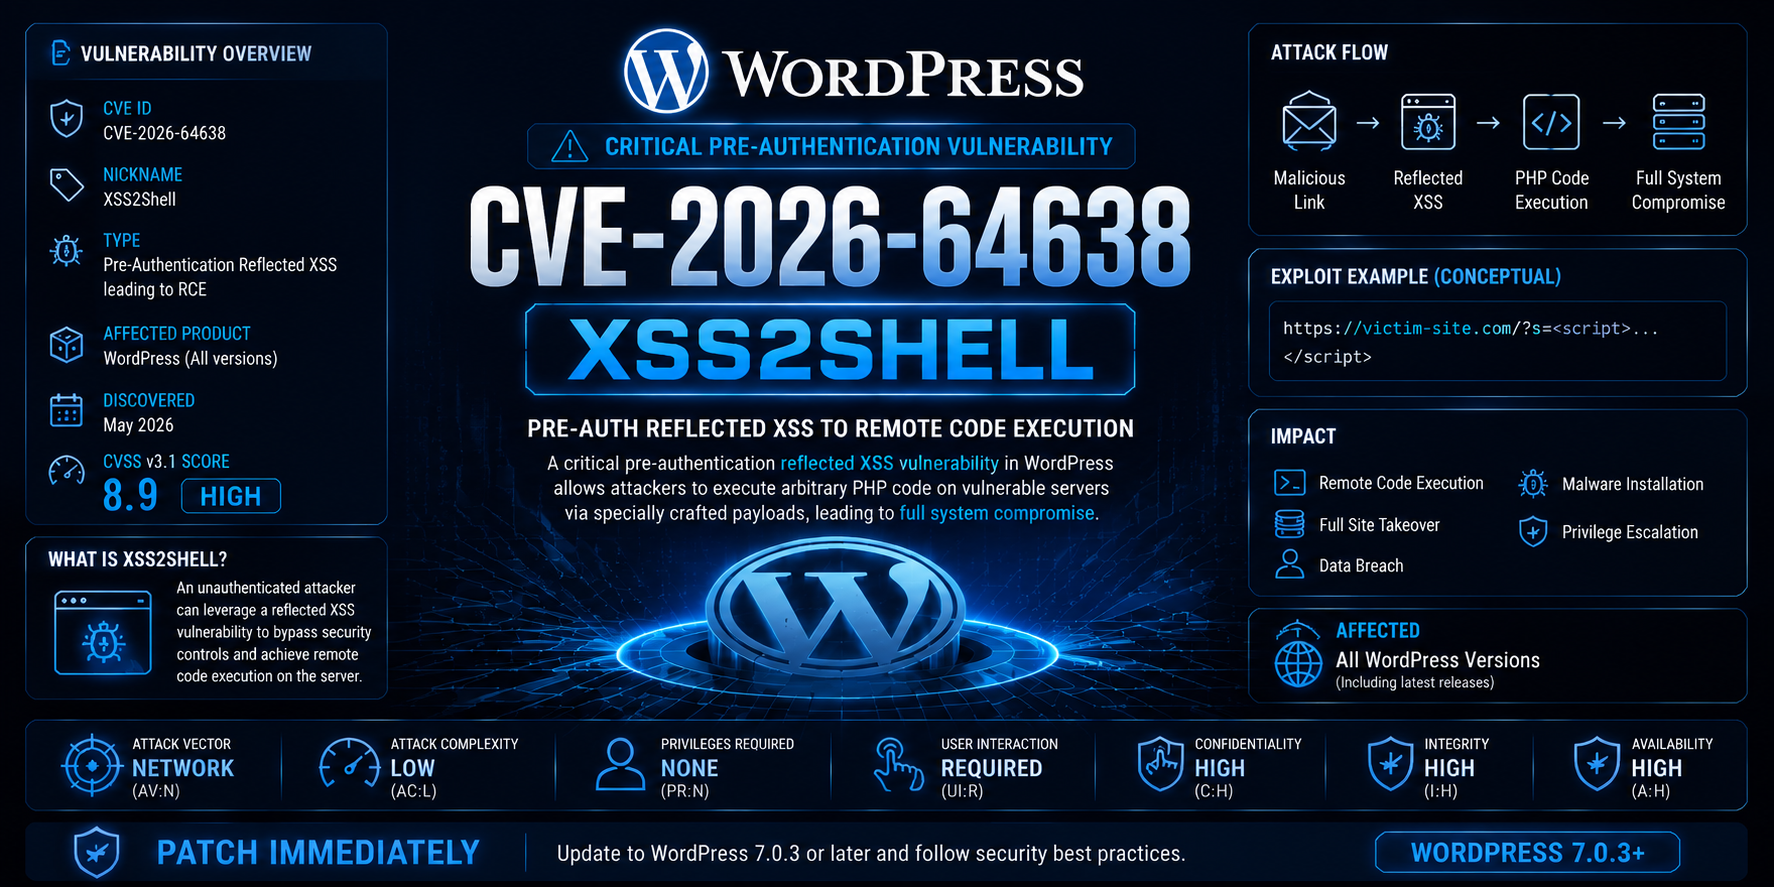
🛡️ CVE-2026-64638 - WordPress Security Assessment Suite (CVSS 8.9) | WordPress 4.7.0-7.0.2 pentest toolkit. Includes vulnerability assessment &…

In the realm of cybersecurity, accurately identifying and characterizing web servers is crucial for threat detection, vulnerability assessment, and…

Reproduction of cve-2024-3400-panos_rce_reproduction

CVE-2024-25600 - Unauthenticated RCE exploit for WordPress Bricks Builder Theme. Advanced exploitation framework with interactive shell, reverse…

A bash scanner for detecting CVE-2025-55182 vulnerability in Next.js applications. And a PoC nodejs script

Recreating Shellshock (CVE-2014-6271) - the bash vulnerability that endangered millions of servers. Automated exploitation toolkit + Burp Suite…

A proof-of-concept exploit for CVE-2026-23744 - MCPJam Inspector Remote Code Execution (RCE) vulnerability. This tool demonstrates the security flaw…

Proof-of-concept exploit for CVE-2026-9277, a command injection vulnerability in shell-quote library. Performs recursive JSON traversal with…

Technical advisory and proof-of-concept for CVE-2024-13985, a critical unauthenticated remote code execution vulnerability in Dahua EIMS via command…

Control Web Panel (CWP) vulnerability scenario related to CVE-2026-57517

Proof of Concept: CVE-2026-24061 is a critical authentication bypass vulnerability in GNU inetutils-telnetd allowing unauthenticated remote attackers…

Cacti Unauthenticated Command Injection