

ultrasploiter
 vqkro/ultrasploiter
A single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…
command-and-controlexploitationexploit-frameworks+9
vqkro/ultrasploiterA single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…

 grisuno/lazyown
Red team framework and multi-operator C2 platform with AI agents, malleable implants, rootkits, phishing engine, and 741 CLI commands covering the…
 dagowda/notrdp
Havoc C2 plugin that creates a hidden Windows desktop, streams it to a browser viewer, and injects mouse/keyboard input for covert remote control.
 hackspeak/cve-2026-93958
Authenticated command injection PoC for D-Link R95/BE9500 DHMAPI SetTimeSettings, achieving root RCE via NTPServer backtick injection, with full…
 28zaaky/khaos-c2
KHAOS is a modern C2 framework that routes agent traffic through cloud services already trusted by enterprise networks.
 abraxas/veneficus
Super elite end-to-end implant 0day. Full kill-chain. Exploit, escalate, pivot, poison, persistence.
 abraxas/veneficus-implant-public
Spicy malware 0day. Full kill-chain malware: exploit, pivot, c2, persistence. Rust converted to pseudo-code - if you're smart you can build it…
 ahmed-tarek22752/rce-cve-2017-0199-detection-analysis
This repository contains a full blue-team malware analysis of a real malicious DOCX exploiting CVE-2017-0199. The lab includes sandbox execution,…
 kaandemir993/acrstealer-custom-protocol-credential-theft-payload-extraction-analysis
Reverse engineering analysis of AcrStealer, a sophisticated info-stealer that uses custom protocols, browser credential theft, and payload…
 kaandemir993/dropper-gcleaner-c2-infrastructure-kernel-driver-powershell-conhost-payload-analysis
Reverse engineering analysis of Dropper GCleaner, a malware that uses a resilient C2 infrastructure, kernel driver loading, PowerShell/Conhost…
 icex0/wp2shell-poc
wp2shell (CVE-2026-63030 & CVE-2026-60137) - full RCE chain
 j4ck3lsyn-gen2/cve-2026-13768
Azure IoT Hub where exposure of an owner-level Shared Access Key enables unauthenticated remote code execution (RCE) against connected IoT devices.…
 ethicalhackinglabs/metasploitable2-exploitation-metasploit
Full Metasploit exploitation walkthrough against Metasploitable2 — vsftpd backdoor, Samba CVE-2007-2447, UnrealIRCd backdoor, Netcat exfiltration,…
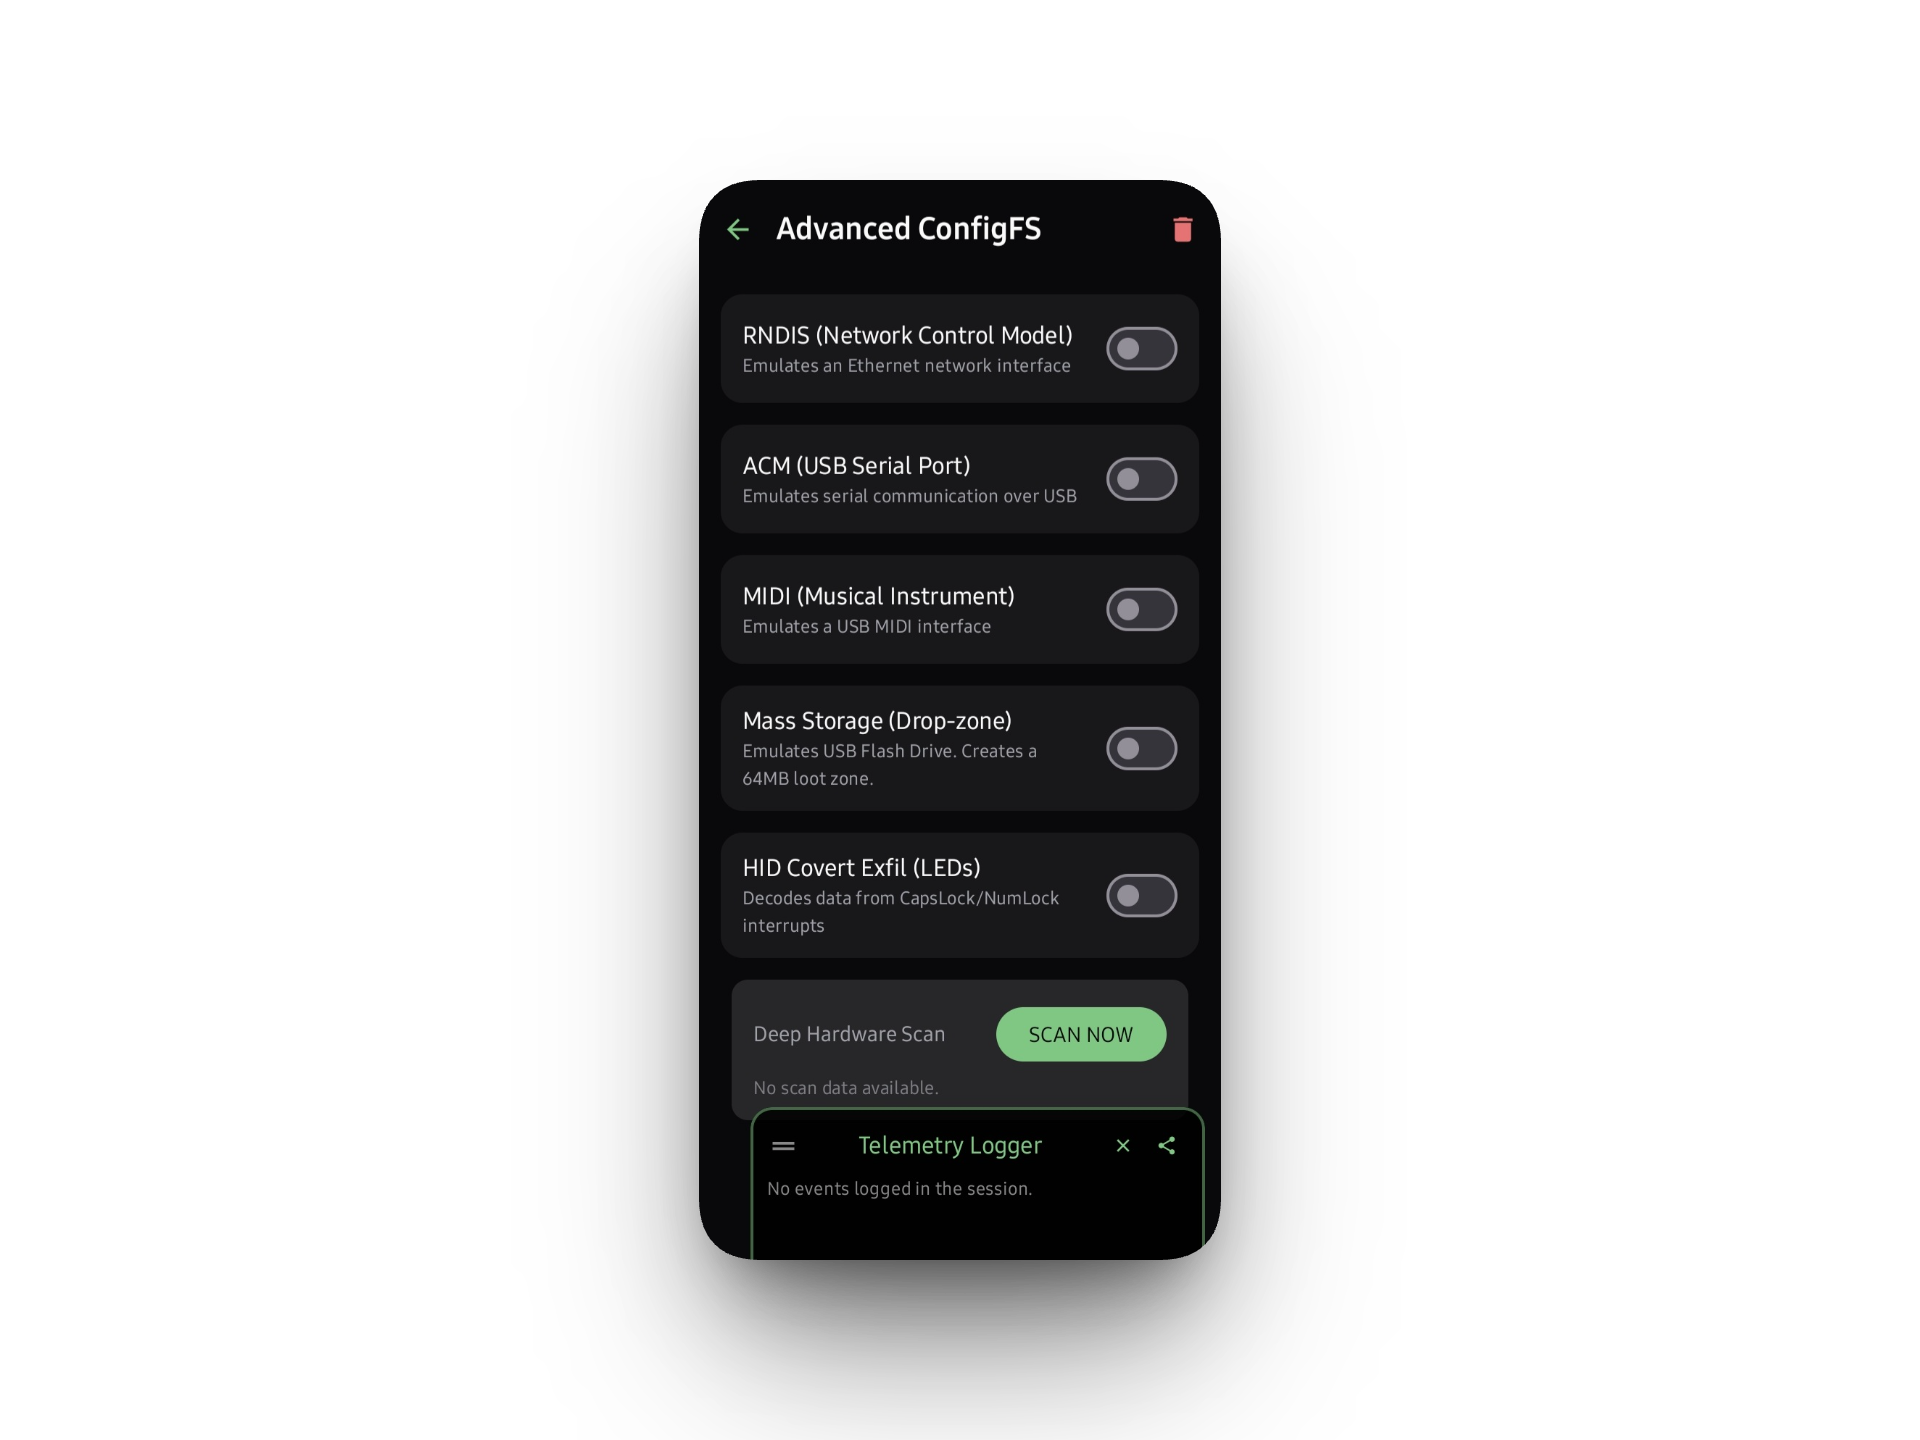 cipher-attack/chimera
Payload injector and HID emulator for Android like Hak5 and rubber ducky
 czabatta/thm-tempest
TryHackMe SOC Level 1 — Follina CVE-2022-30190, Nim C2, Chisel, PrintSpoofer, backdoor accounts
 0xblackash/cve-2026-10520
CVE-2026-10520
 anxs3c/cve-2026-24061-gnu-inetutils-telnetd
GNU-InetUtils-telnetd-Authentication-Bypass-Vulnerability
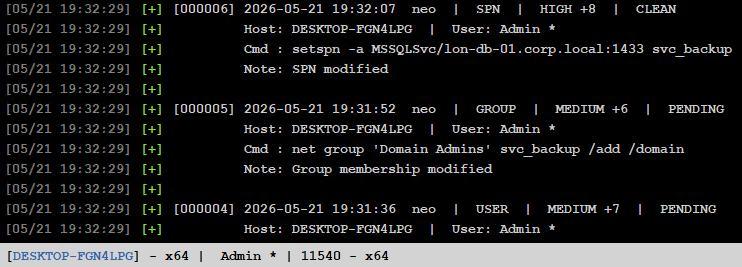 shellkraft/ledger
An aggressor script that tracks operational changes made during a red team engagement. Gives you a full audit trail of what was changed and what…