

Archived
Heroinn
 b23r0/heroinn
A cross platform C2/post-exploitation framework.
command-and-controlpayload-developmentpenetration-testing-frameworks+4
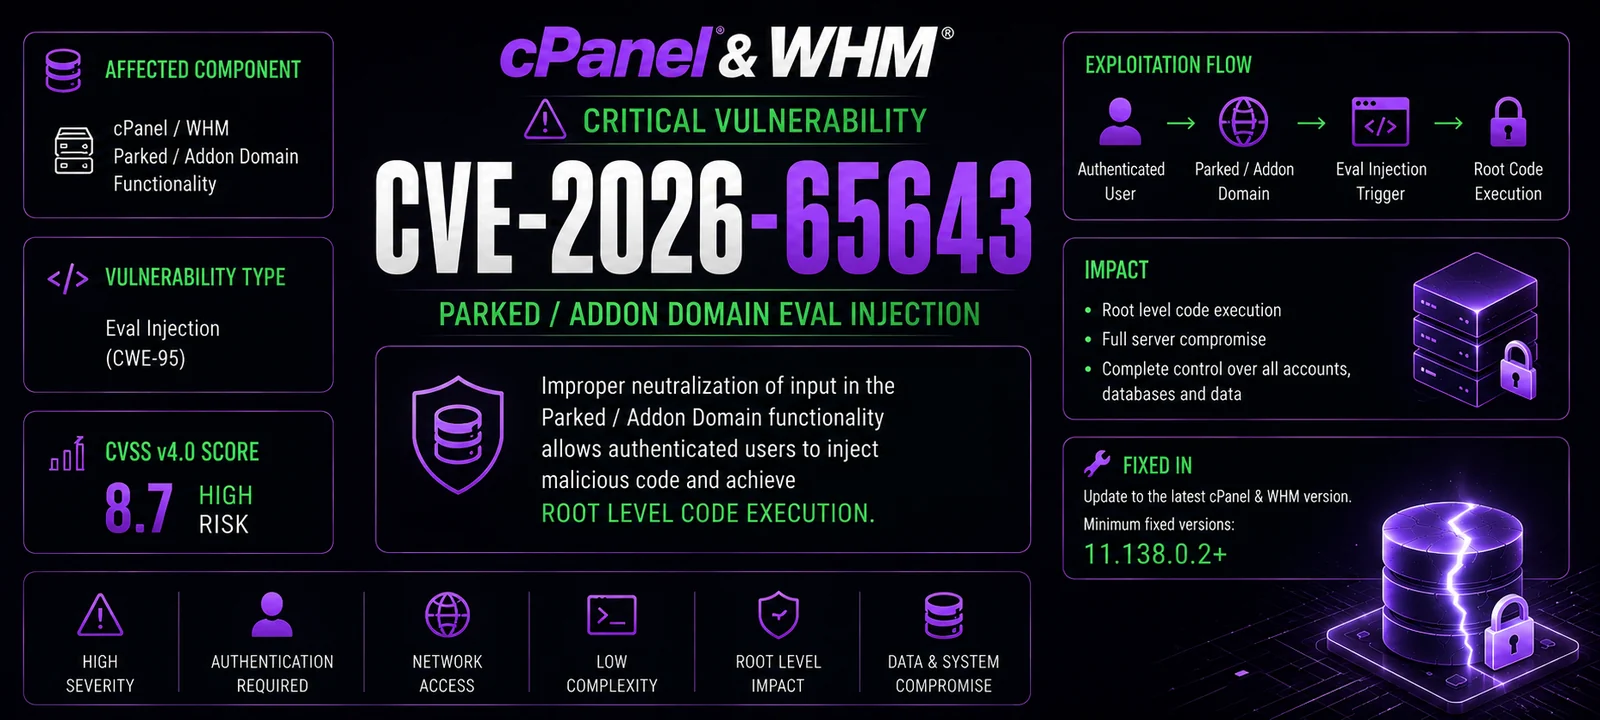 tc4dy/cve-2026-65643-poc-toolkit
Red/Blue team toolkit for CVE-2026-65643, a cPanel domain parking RCE. Includes exploit with reverse shell, webshell, persistence, and mass scanning,…
 e4zyy/project-cve-2026-33017
CVE-2026-33017 - Langflow Unauthenticated RCE Exploit
 jasonbernier/cve-2025-5781
Proof-of-concept exploit for CVE-2025-57819 in FreePBX: SQL injection in the AJAX API to execute arbitrary PHP, create a persistent webshell, and…
 codextf2/screenshotbof
An alternative screenshot capability for Cobalt Strike that uses WinAPI and does not perform a fork & run. Screenshot downloaded in memory.
 mcipekci/wp2shell
Pre-auth RCE PoC for WordPress core — chains CVE-2026-63030 (REST /batch/v1 route-confusion desync) with CVE-2026-60137 (author__not_in SQLi) into an…
 toxy4ny/copy-fail
Copy Fail - CVE-2026-31431 - Hardened C implementation for redteam and authorized penetration testing operations. ⚠️ Legal Notice: This tool is…
 idov31/nidhogg
Windows rootkit for Intel x64 with 25+ features, demonstrating rootkit techniques compatible with all Windows 10 and Windows 11 versions.
 gagaltotal/cve-2026-48908-sp-page-builder-joomla
CVE-2026-48908 - SP Page Builder Joomla Unauthenticated RCE
 layer-6/cve-2026-5027-langflow
Multi-CVE exploit tool for pre-auth remote code execution on Ivanti Sentry and FortiSandbox. Features interactive shell, webshell deployment,…
 yuvrajshad/freepbx-cve-2025-57819
Unauthenticated SQL Injection to Remote Code Execution in FreePBX — CVE-2025-57819
 tihanyin/pssw100avb
A list of useful Powershell scripts with 100% AV bypass (At the time of publication).
 nccgroup/async-pico-hub
Async PICO Hub is a work-in-progress framework to extend Cobalt Strike with custom event monitoring and in-process Asynchronous BOFs
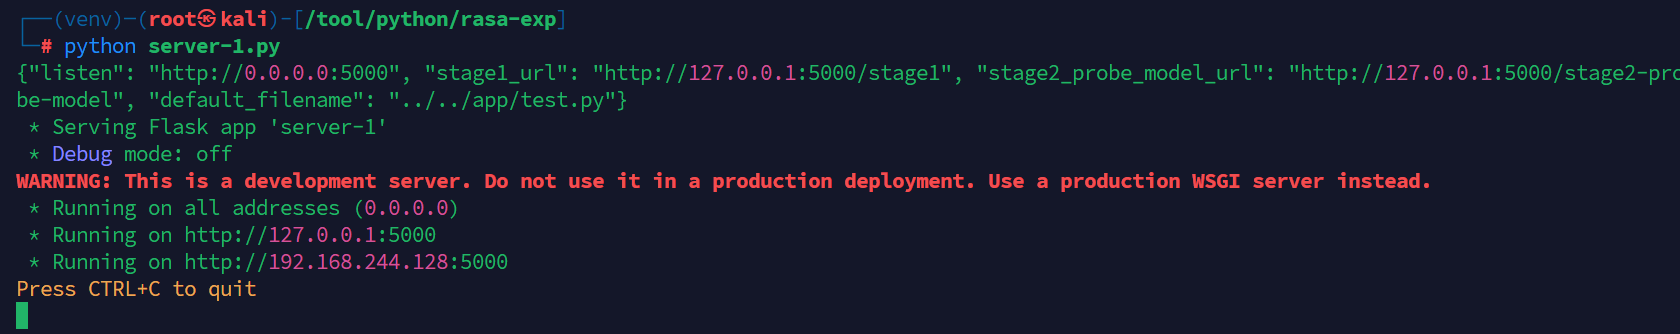 lierbushiwo/rasa-cve-exp
CVE-2024-49375、CVE-2021-42556、CVE-2021-41127
 joshuavanderpoll/cve-2026-44262
Unauthenticated RCE in dedoc/scramble — PoC, Nmap NSE & Nuclei template.
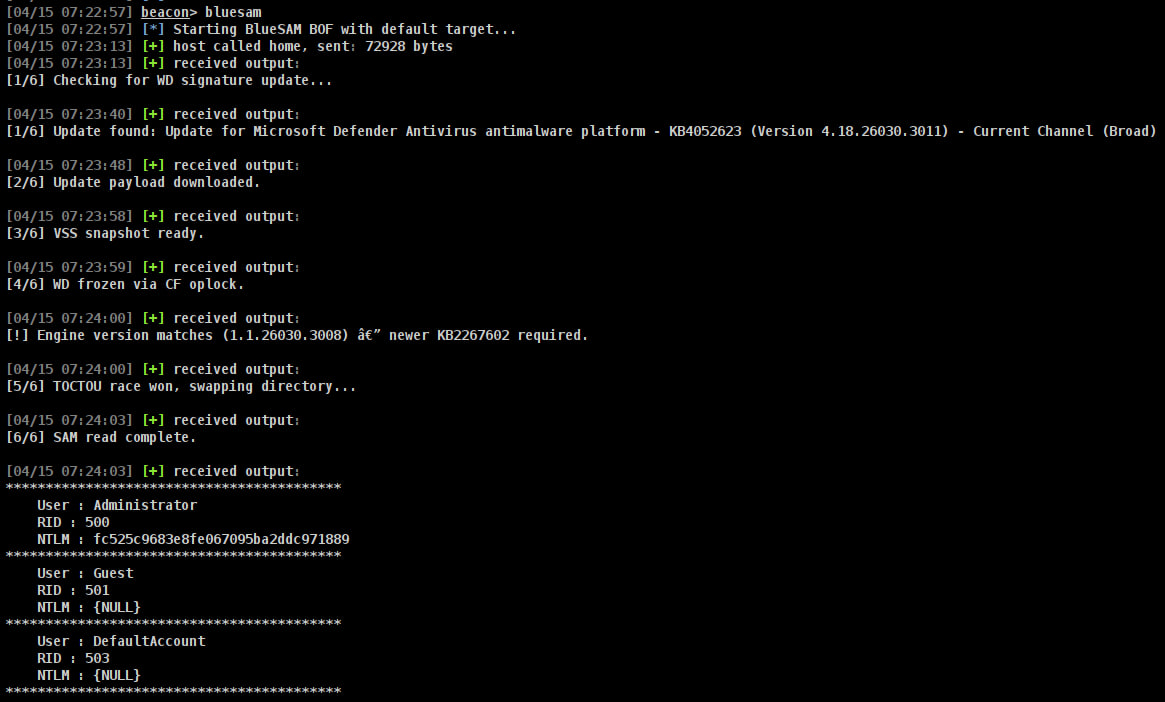 incursi0n/bluesam
A Cobalt Strike Beacon Object File that exploits the BlueHammer vulnerability that to obtain a copy of the SAM database.
 kasem545/cve-2025-54123-poc
CVE-2025-54123 Hoverfly Authenticated Middleware Command Injection RCE
 dazzyddos/lsawhisper-bof
A Beacon Object File (BOF) that talks directly to Windows authentication packages through the LSA untrusted/trusted client interface, without…