
SteppingStones
 nccgroup/steppingstones
Web-based red team activity logging, reporting, and situational awareness tool with Cobalt Strike and BloodHound integration.
command-and-controlinformation-gatheringpenetration-testing+3
244
nccgroup/steppingstonesWeb-based red team activity logging, reporting, and situational awareness tool with Cobalt Strike and BloodHound integration.
 trustedsec/unicorn
Unicorn is a simple tool for using a PowerShell downgrade attack and inject shellcode straight into memory. Based on Matthew Graeber's powershell…
 onyks-os/transparenttorproxy
A Linux CLI utility that transparently routes all system traffic through the Tor network using nftables. It enables rapid IP rotation and easy…
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 adaptix-framework/adaptixc2
AdaptixC2 is a highly modular advanced redteam toolkit
 yasouxken/cve-2026-41940-poc
Python PoC exploiting CVE-2026-41940, a cPanel & WHM authentication bypass enabling unauthenticated root-level WHM access, with scanning and…
 yasserbdj96/hiphp
PHP-based backdoor tool for remote website control via HTTP/HTTPS. Enables file management, command execution, and Tor connectivity with…
 davidcarliez/mythic_telegram_profile
Mythic C2 profile that tunnels Athena and Apollo agent traffic through Telegram bot-to-bot messages, bridging encrypted payloads to Mythic via its…
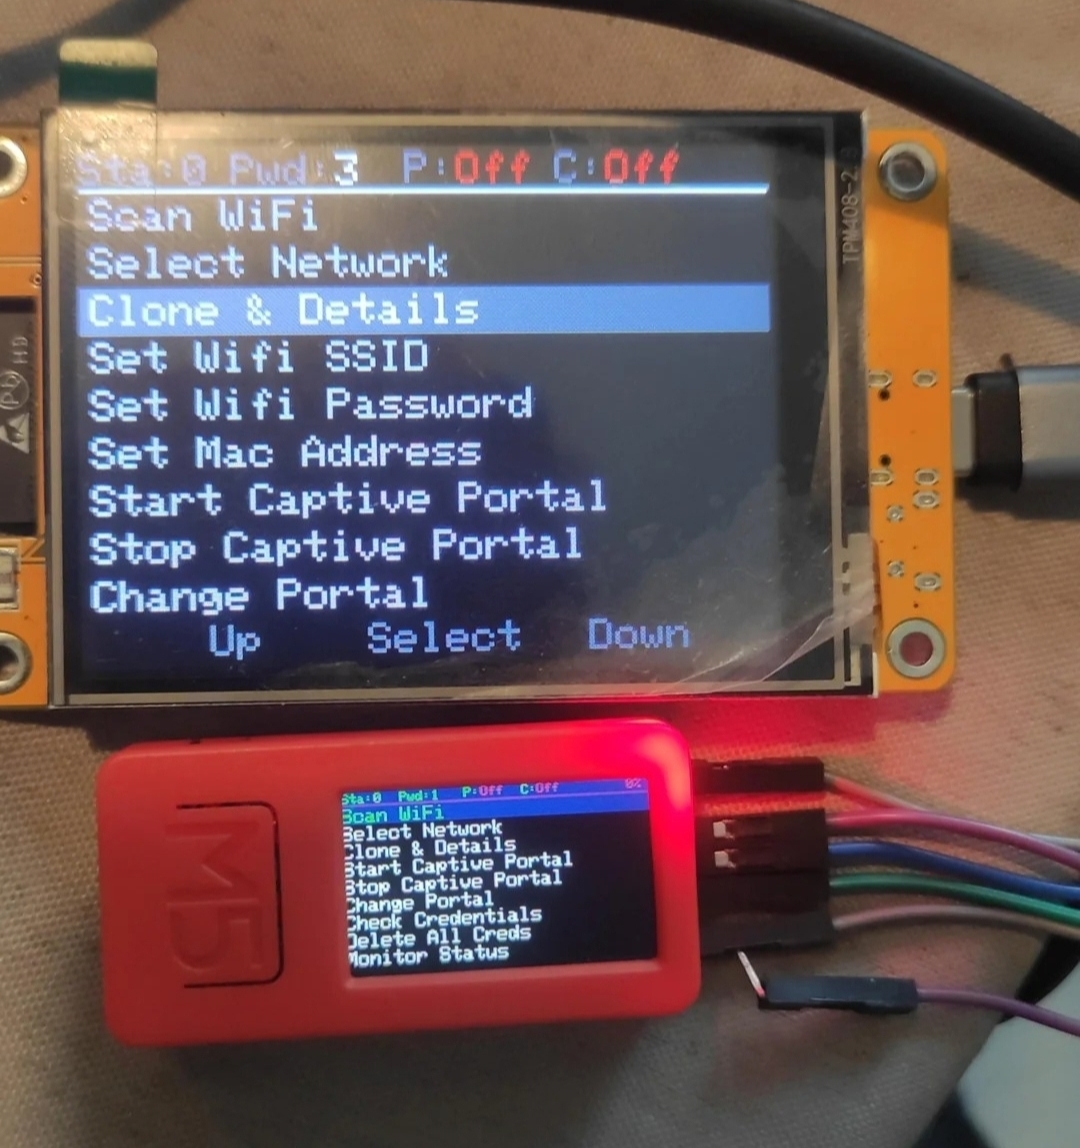 7h30th3r0n3/evil-m5project
Multi-purpose WiFi penetration testing toolkit for M5Stack devices. Performs network scanning, evil-twin attacks, deauthentication, captive portal…
 ctdal/cve-2026-41940-poc
Exploits CVE-2026-41940, a cPanel/WHM authentication bypass, to gain root WHM access and run post-exploitation commands, account listing, and…
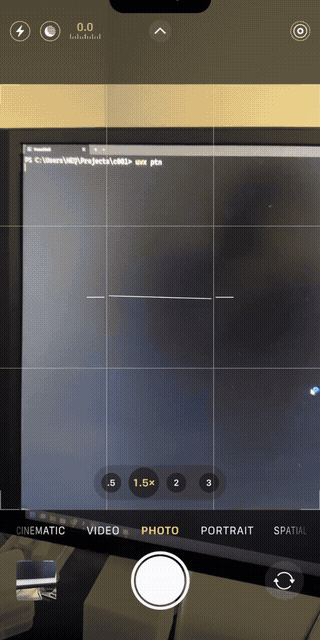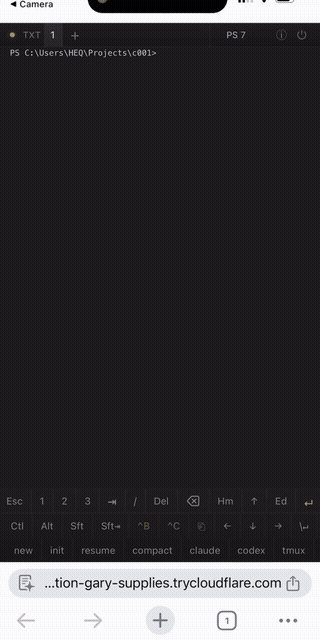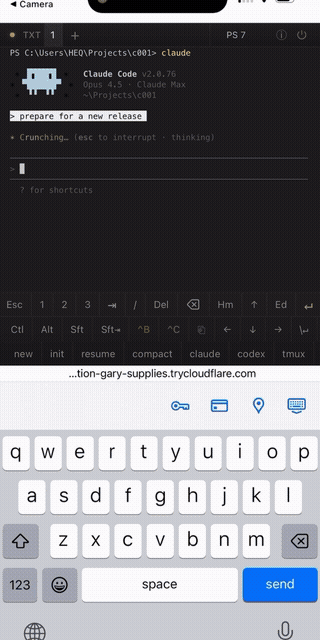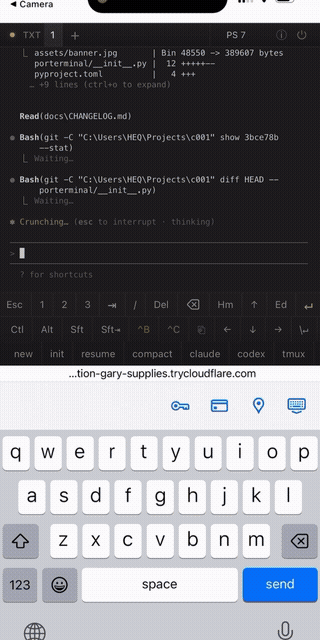 lyehe/porterminal
Quick n' dirty web/mcp terminal tunneling your phone & pc
 here_forawhile/terminalphone
Encrypted push-to-talk voice and text communication over Tor hidden services with end-to-end encryption, configurable ciphers, relay mode for group…
 studiomeyer-io/mcp-server-attestation
Layer-2 supply-chain hardening for MCP servers — Ed25519-signed tool manifests, runtime spawn-attestation, default-deny argument sanitizer. Defends…
 whispergate/msteams
Mythic C2 profile that tunnels agent traffic through Microsoft Teams channels using the Microsoft Graph API, with AES256 encryption, jitter, kill…
 dirkjanm/askwam
Ask the Web Account Manager (WAM) for Entra ID tokens
 voidsecsoftwares/voidsyscall
Cross-platform syscall-powered implant & C2 — direct syscalls (Win), raw syscalls (Linux), HTTPS/DNS/ICMP channels. No winapi layer.
 lame-projects/stratum-c2
Cloud dead-drop C2 framework — RSA-4096 + AES-256-GCM, 5 cloud providers, Rust-only agents, P2P mesh, persistence engine, credential harvesting
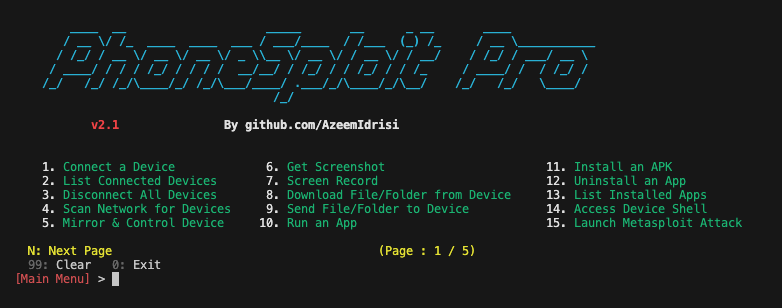 azeemidrisi/phonesploit-pro
An all-in-one hacking tool to remotely take over Android devices.