

AdStrike
 capture0x/adstrike
AI-powered modular Active Directory red-team framework for authorized penetration testing, AD enumeration, attack-path analysis, Kerberos/ADCS…
ai-securitycommand-and-controlexploitation+7
396
capture0x/adstrikeAI-powered modular Active Directory red-team framework for authorized penetration testing, AD enumeration, attack-path analysis, Kerberos/ADCS…
 kr0no/bloodhound-shell
An interactive command-line shell for BloodHound API.

 yukibtc/redknife
A Swiss Army knife for offensive security.
 karmanya03/overthrone
All-Rust Active Directory exploitation framework: LDAP/SMB/Kerberos enumeration, attack-graph pathfinding, Kerberoasting, NTLM relay, ticket forging,…
 vqkro/ultrasploiter
A single binary that folds a port scanner, the full Exploit-DB index (47k entries) and runnable exploit modules into one tool. Written in Rust, runs…
 gmh5225/github-gato
GitHub Self-Hosted Runner Enumeration and Attack Tool
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
 imbas007/poc_cve-2026-41940
Proof-of-concept exploit for CVE-2026-41940 targeting cPanel, enabling account enumeration, command execution, and interactive shell access on…
 rohmatariow/cve-2026-22812-exploit
Exploitation toolkit for CVE-2026-22812 (OpenCode unauthenticated RCE) providing interactive shell, arbitrary command execution, file…
 rvrsh3ll/bof_collection
Various Cobalt Strike BOFs
 rasta-mouse/ppenum
Simple BOF to read the protection level of a process
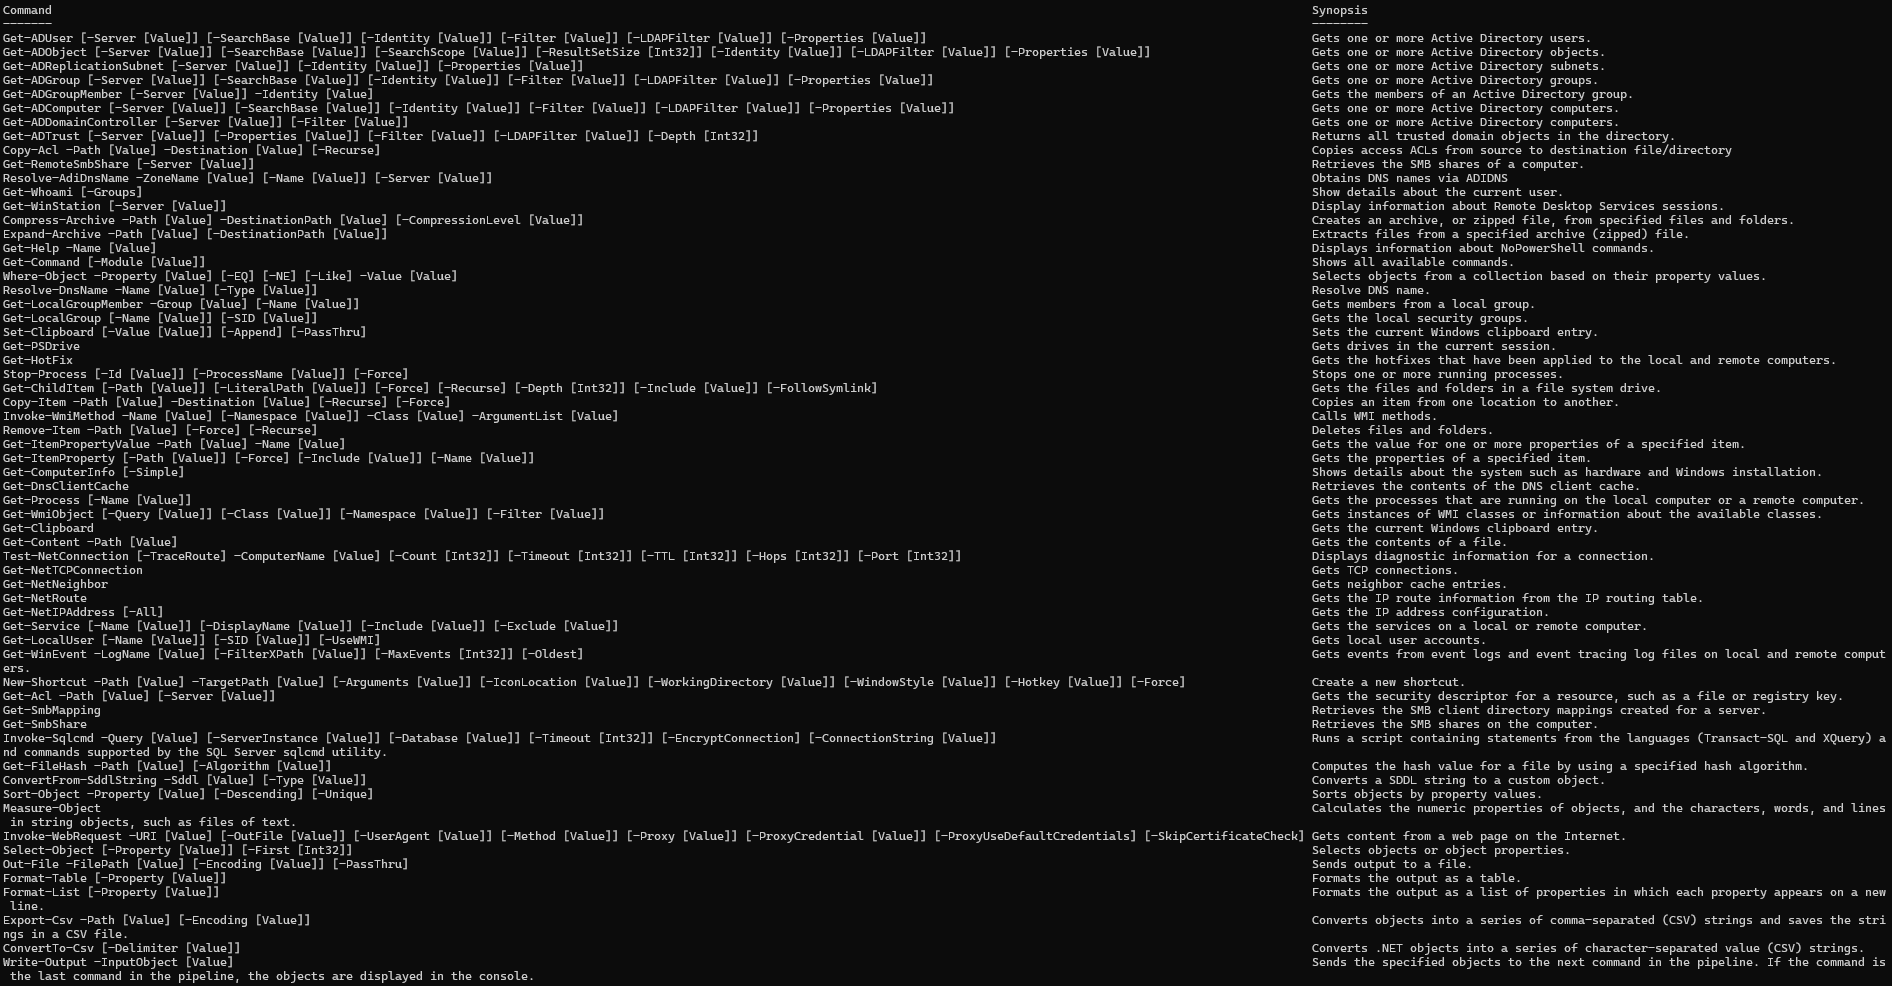 bitsadmin/nopowershell
PowerShell rebuilt in C# for Red Teaming purposes
 mayyhem/maestro
Abusing Azure services over C2
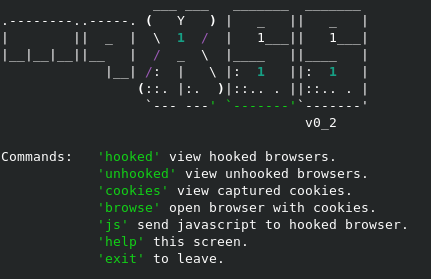 grampae/mqxss
Hooked browser communication over MQTT
 nccgroup/steppingstones
Web-based red team activity logging, reporting, and situational awareness tool with Cobalt Strike and BloodHound integration.
 razureink/fucker
Penetration testing framework with AI-driven decision engine
 blue0x1/nimux
Pure-Nim network enumeration and remote execution toolkit for authorized security assessments. Supports SMB, LDAP, Kerberos, WinRM, database clients,…
 malwaretech/phasehack
Phase C&C Blind SQL Injection