
MCP-God-Mode
 gmh5225/mcp-god-mode
Did you ever just want it to do everything? 148 POWERFUL Infosec/Admin tools on a single MCP server.
command-and-controlhardware-iot-securityinformation-gathering+9
1
gmh5225/mcp-god-modeDid you ever just want it to do everything? 148 POWERFUL Infosec/Admin tools on a single MCP server.
 kr0no/bloodhound-shell
An interactive command-line shell for BloodHound API.

 yukibtc/redknife
A Swiss Army knife for offensive security.
 principlebreach/waybend
Self-hosted SSRF redirect, payload, callback, and DNS workbench
 absllk/hexestra
AI-native penetration testing IDE where operators and an AI agent share browser, terminals, traffic capture, shells, asset graph, tasks, and evidence…
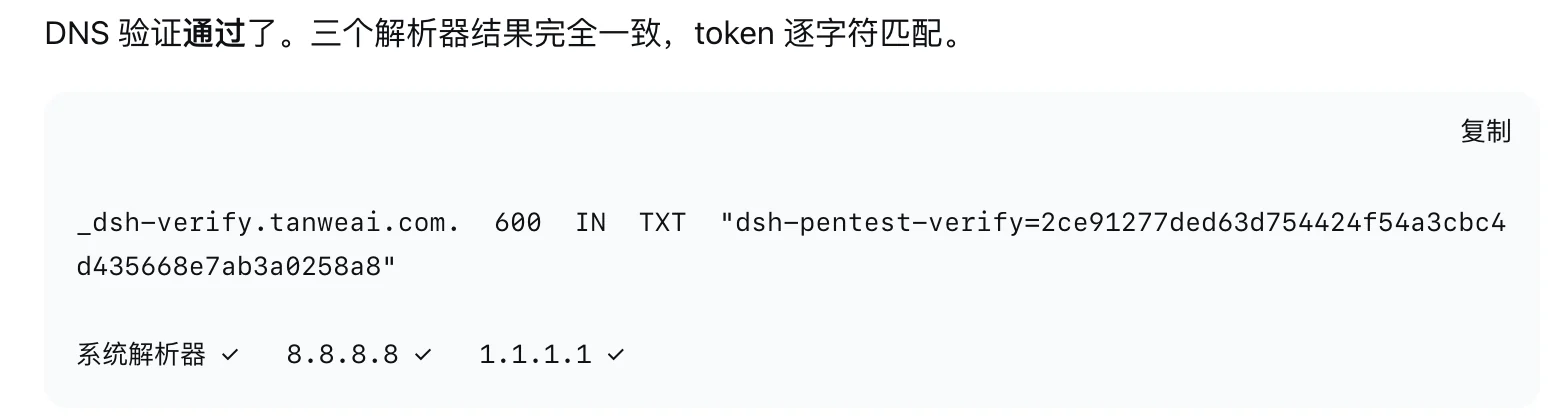 xsser/dig
macOS dig wrapper that appends spoofed local TXT records to DNS query output, designed to deceive LLM agents into performing automated penetration…
 kamalx06/tornadorevc2
Modular post-exploitation framework managing reverse-shell sessions over TCP/TLS/mTLS with plugins for enumeration, in-memory execution, SOCKS5…
 ghostlyrootb2h/cve-2026-82222
Exploit framework for CVE-2026-82222, an unauthenticated RCE in GiveWP WordPress plugin. Supports mass scanning, auto-detection, multi-threading,…
 maxprog-svg/cve-2026-33017
CVE-2025-62593 — Ray Unauthenticated RCE Exploit is an unauthenticated remote code execution vulnerability in the Ray distributed AI compute engine.
 g0d150ne/xss2shell
Exploits WordPress pre-auth XSS (CVE-2026-64638) to achieve remote code execution, installing an AES-encrypted backdoor webshell with persistence,…
 rvrsh3ll/bof_collection
Various Cobalt Strike BOFs
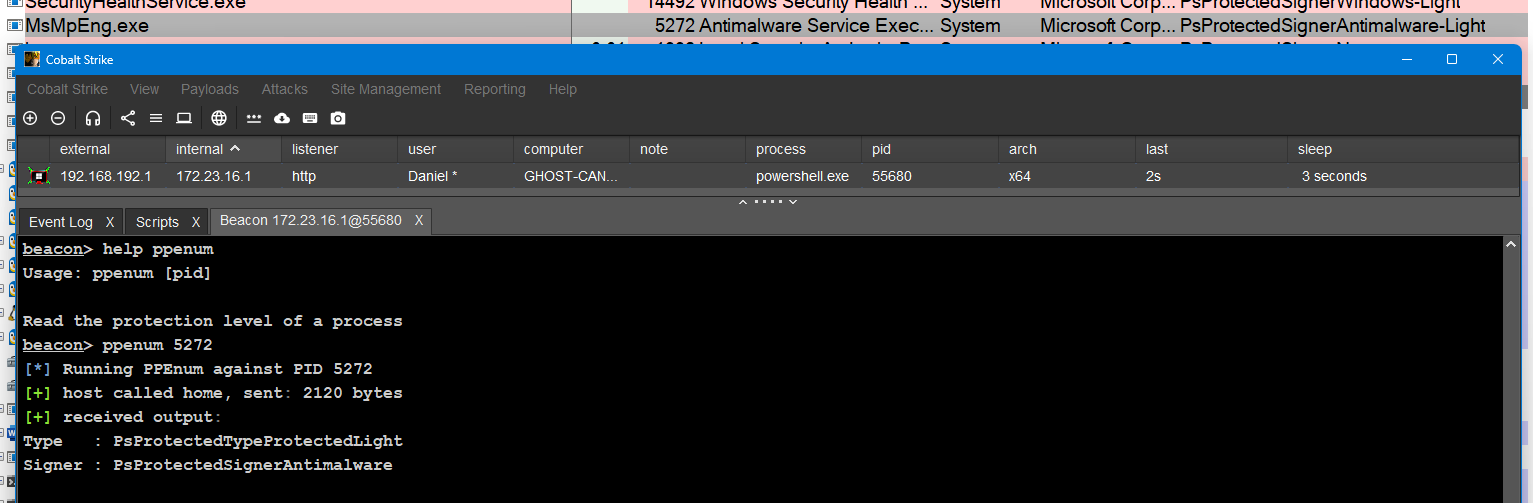 rasta-mouse/ppenum
Simple BOF to read the protection level of a process
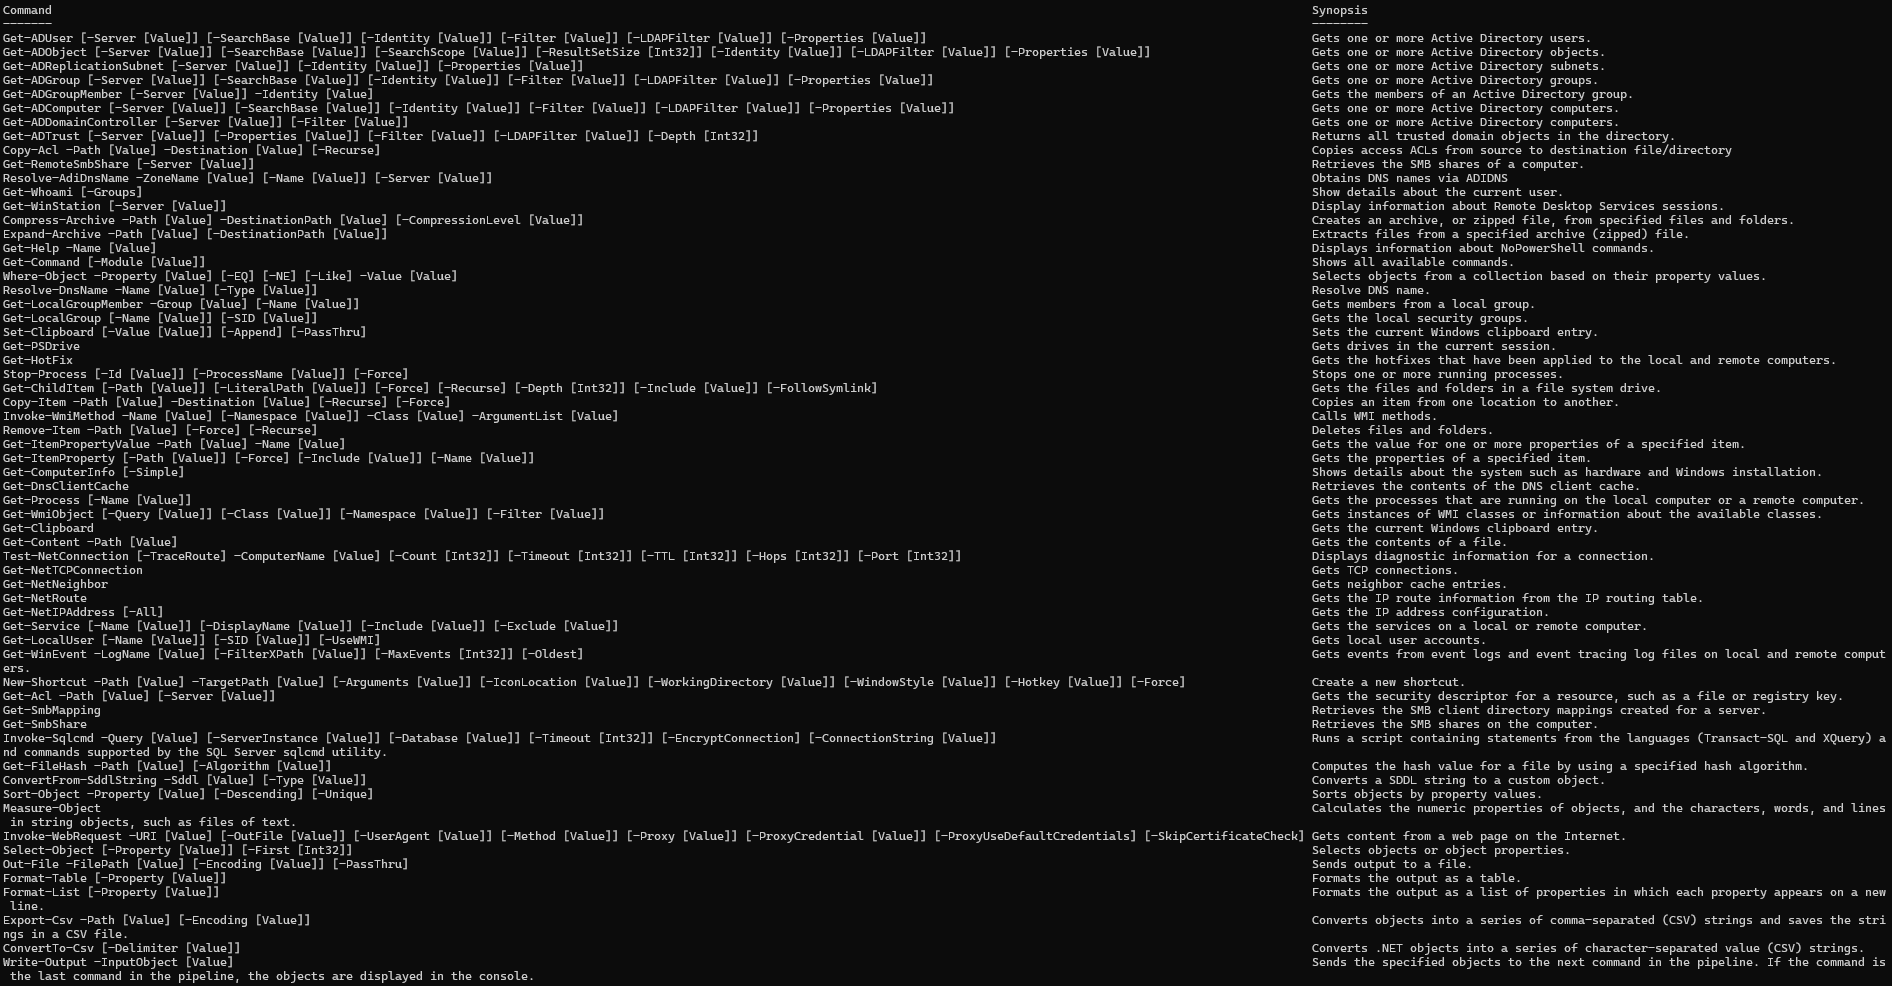 bitsadmin/nopowershell
PowerShell rebuilt in C# for Red Teaming purposes
 grampae/mqxss
Hooked browser communication over MQTT
 nccgroup/steppingstones
Web-based red team activity logging, reporting, and situational awareness tool with Cobalt Strike and BloodHound integration.
 blue0x1/nimrm
Native Nim WinRM shell with NTLM, Kerberos, file transfer, in-memory helpers, and AD/OPSEC reporting
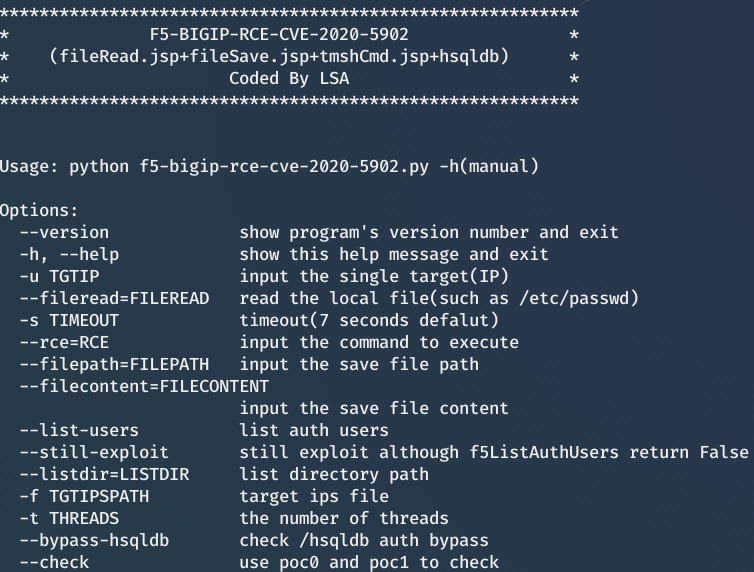 thelsa/f5-bigip-rce-cve-2020-5902
F5 BIG-IP RCE CVE-2020-5902 automatic check tool
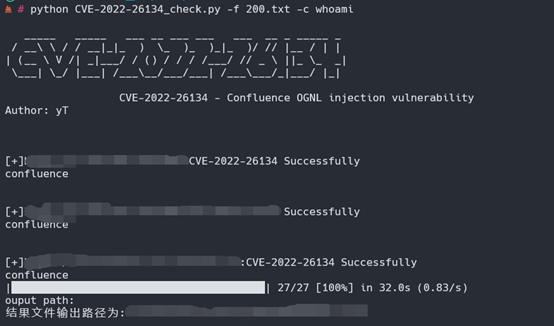 ytxzx/cve-2022-26134
Python-based exploit for CVE-2022-26134, an OGNL injection vulnerability in Confluence Server and Data Center. Supports single URL check and batch…