
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
48 results
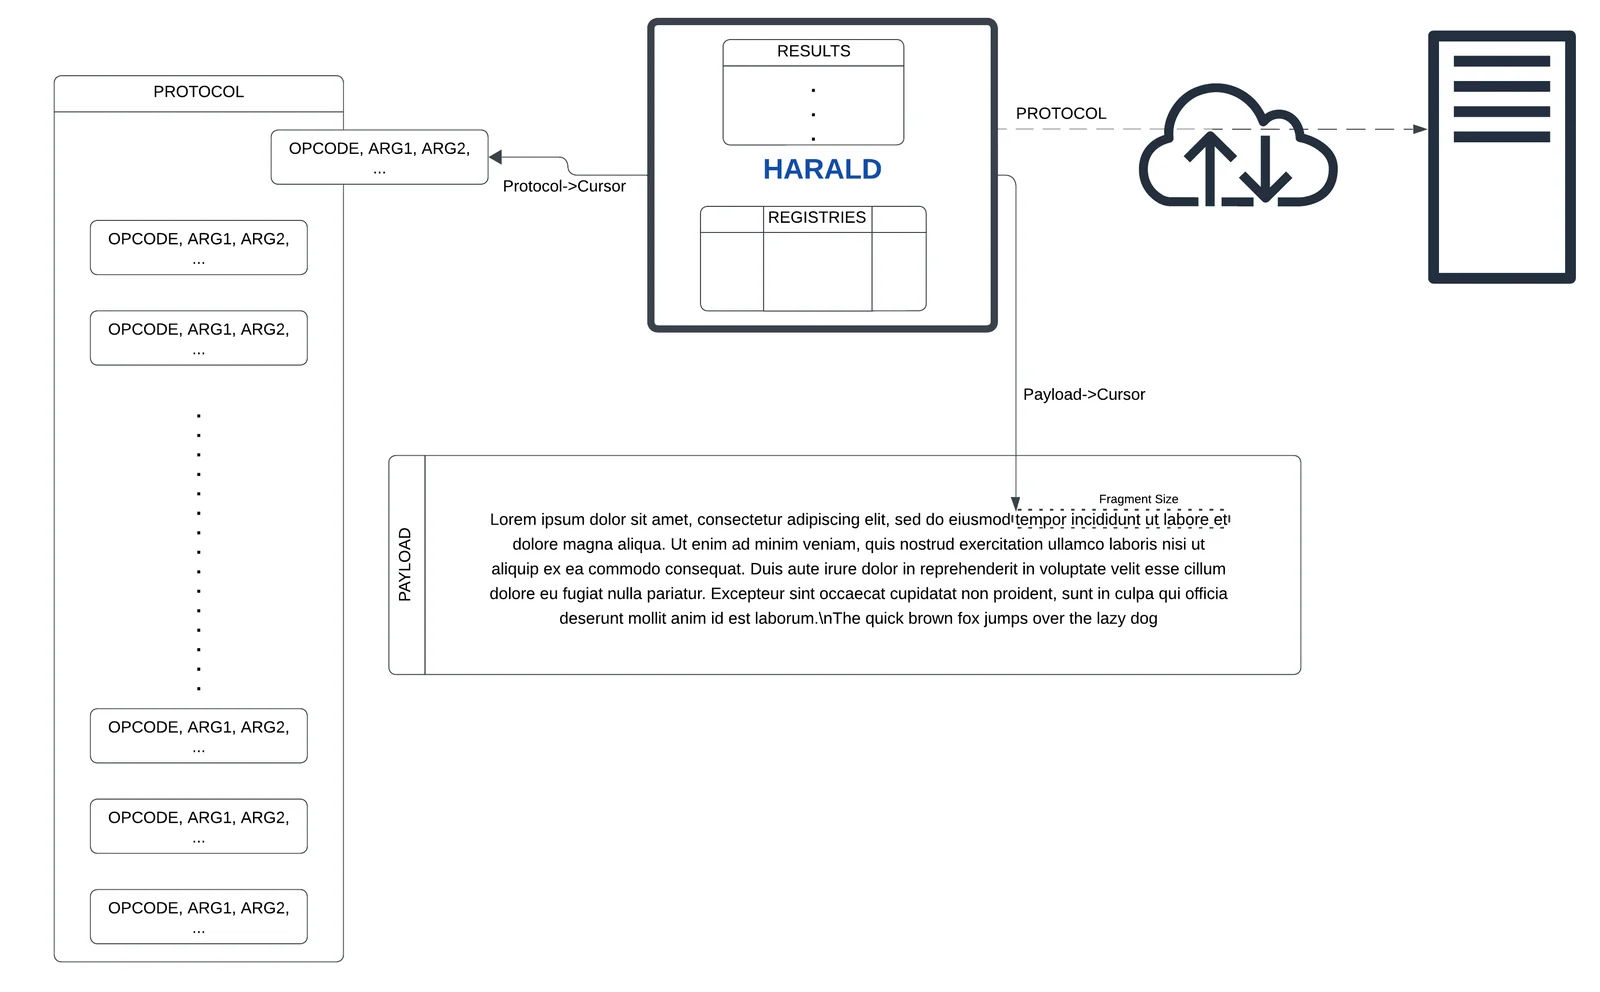
Harald preview

Harald

GitHubgmh5225/harald

An in-memory minimal CPU for agnostic on-the-fly protocols creation
command-and-controlexploitationids-ips-evasion+6
1 year ago
Dji_ble_vuln preview

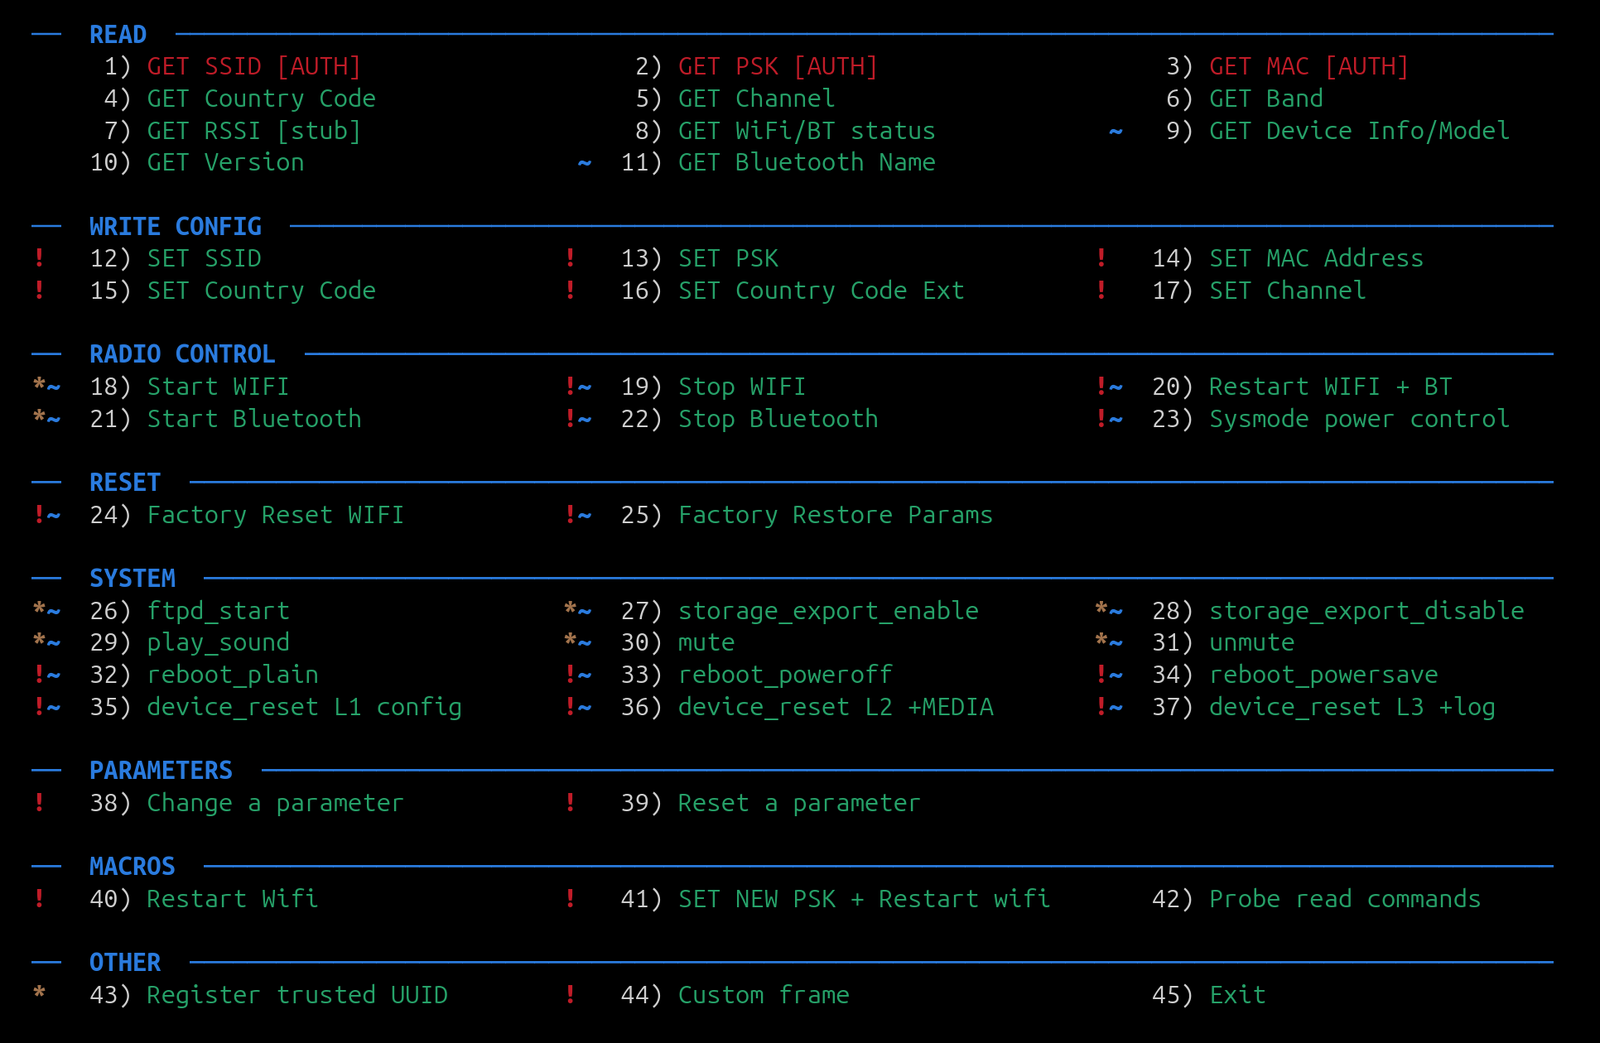
Dji_ble_vuln

GitHubfeedbeef/dji_ble_vuln

DJI Drone DUML Command Injection over Bluetooth — Proof of Concept for CVE-2026-78306
bluetooth-securitycommand-and-controlembedded-systems-security+6
1 month ago
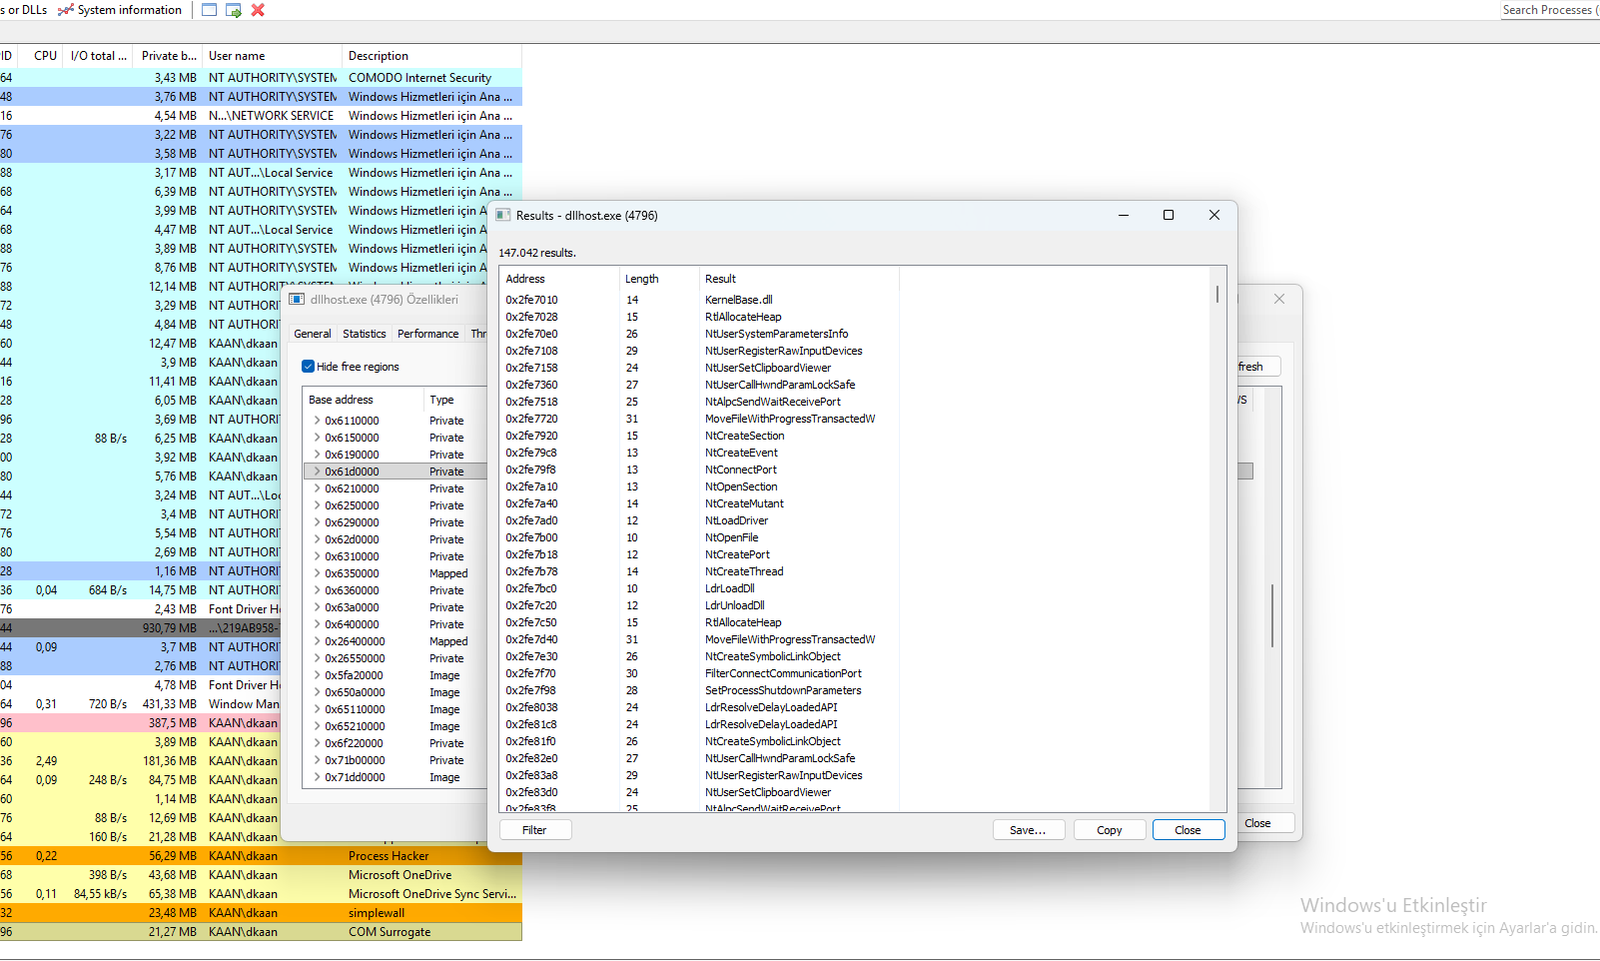
Lumma-Stealer-dllhost-Hollowing-C2-Domains-Payload-Extraction-Analysis preview

Lumma-Stealer-dllhost-Hollowing-C2-Domains-Payload-Extraction-Analysis

GitHubkaandemir993/lumma-stealer-dllhost-hollowing-c2-domains-payload-extraction-analysis

In-depth reverse engineering analysis of Lumma Stealer, an info-stealer using process hollowing, Native API calls, and C2 communication. Includes…

binary-analysiscommand-and-controldata-exfiltration+4
121 month ago
RedLine-Stealer-C2-Defender-Bypass-Payload-Analysis preview

RedLine-Stealer-C2-Defender-Bypass-Payload-Analysis

GitHubkaandemir993/redline-stealer-c2-defender-bypass-payload-analysis

"Reverse engineering analysis of RedLine Stealer, a .NET-based info-stealer that uses C2 domains (198.46.86.63, tempuri.org), Windows Defender…

command-and-controldata-exfiltrationmalware-analysis+4
12 months ago
Empire preview

Empire

GitHubbc-security/empire

Empire is a post-exploitation and adversary emulation framework that is used to aid Red Teams and Penetration Testers.
adversarial-attackcommand-and-controldata-exfiltration+16
5.3k1 month ago
RPC-Backdoor preview

RPC-Backdoor

GitHubeladshamir/rpc-backdoor

A basic emulation of an "RPC Backdoor"
command-and-controllateral-movementpost-exploitation+3
2424 years ago
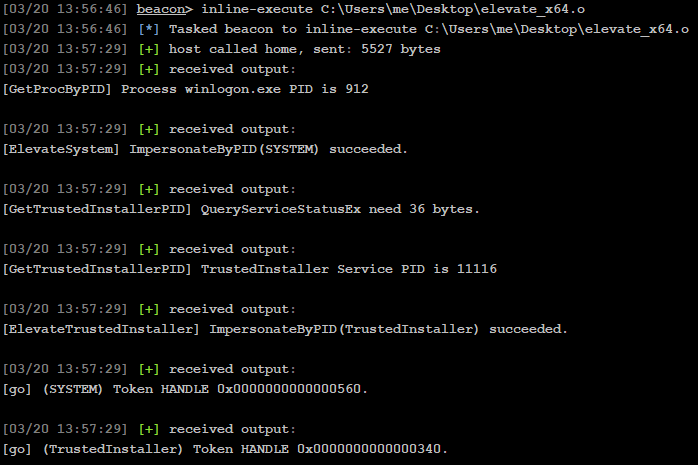
Elevate-System-Trusted-BOF preview

Elevate-System-Trusted-BOF

GitHubmr-un1k0d3r/elevate-system-trusted-bof

Cobalt Strike Beacon Object File that elevates an active beacon to SYSTEM and grants TrustedInstaller privileges through SetThreadToken token…
command-and-controlpayload-developmentpost-exploitation+2
1813 years ago
Mystikal preview

Mystikal

GitHubd00mfist/mystikal

macOS Initial Access Payload Generator
adversarial-attackcommand-and-controlpayload-development+4
3302 years ago
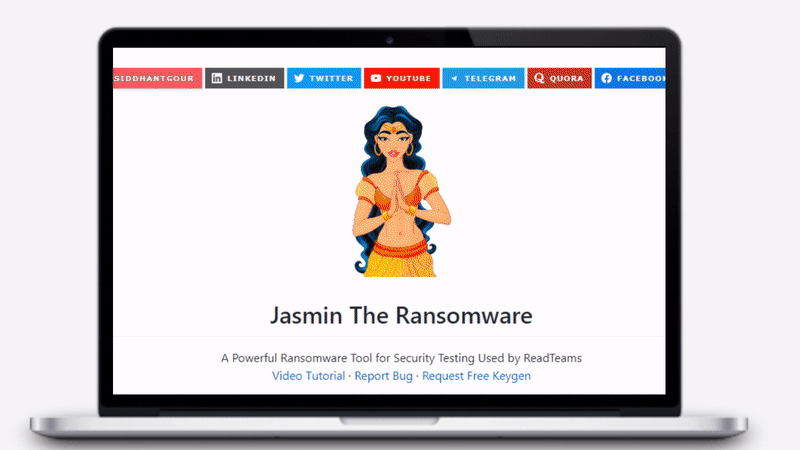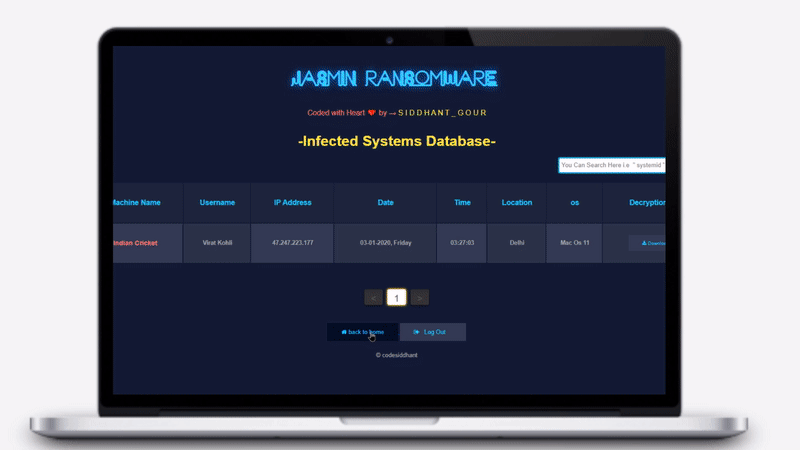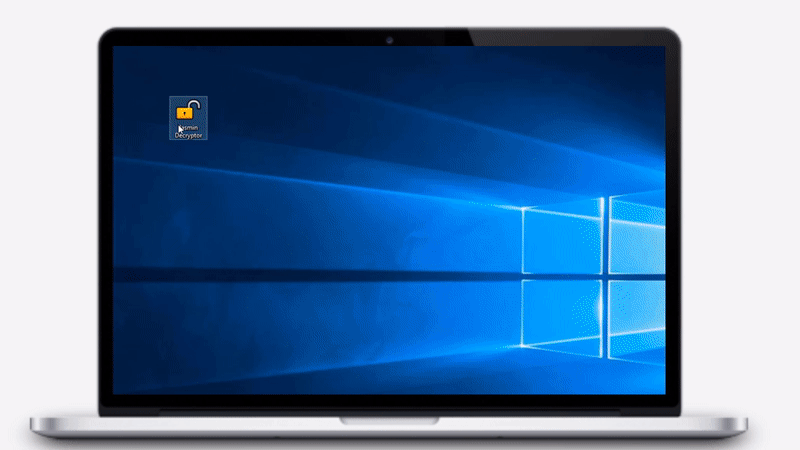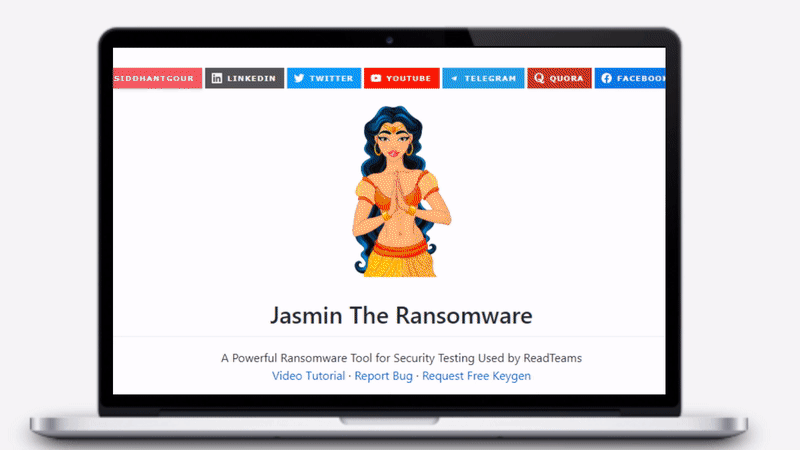
Jasmin-Ransomware preview

Jasmin-Ransomware

GitHubcodesiddhant/jasmin-ransomware

Jasmin Ransomware is an advanced red team tool (WannaCry Clone) used for simulating real ransomware attacks. Jasmin helps security researchers to…
command-and-controlencryption-decryption-toolsexploitation+5
2895 years ago
Java-Servlets-Shell preview

Java-Servlets-Shell

GitHubmbadanoiu/java-servlets-shell

JSP-less Java Servlets Backdoor inspired by https://www.redteam-pentesting.de/files/redteam-jboss.tar.gz
command-and-controlexploitationpenetration-testing+3
11 year ago
CVE-2026-32238_RemoteCodeExecutionOpenEMR8.0.0 preview

CVE-2026-32238_RemoteCodeExecutionOpenEMR8.0.0

GitHubchrissub08/cve-2026-32238_remotecodeexecutionopenemr8.0.0

Remote code execution vulnerability in OpenEMR <8.0.0.2.
command-and-controlexploitationpayload-development+3
7 months ago
Hale preview

Hale

GitHubpjlantz/hale

Botnet command & control monitor
command-and-controlincident-responseinformation-gathering+5
2024 years ago
AndroidClient preview

AndroidClient

GitHubrev-code/androidclient

Android remote administration client
android-securitycommand-and-controlmobile-security+3
118 years ago
BlockchainC2 preview

BlockchainC2

GitHubxpn/blockchainc2

A POC C2 server and agent to explore just if/how the Ethereum blockchain can be used for C2
command-and-controlexploitationpayload-development+2
797 years ago
ChromeAlone preview

ChromeAlone

GitHubpraetorian-inc/chromealone

A tool to transform Chromium browsers into a C2 Implant
command-and-controlpayload-developmentpersistence-mechanisms+6
6121 year ago
doublepulsar-c2-traffic-decryptor preview

doublepulsar-c2-traffic-decryptor

GitHubwithsecurelabs/doublepulsar-c2-traffic-decryptor

A python2 script for processing a PCAP file to decrypt C2 traffic sent to DOUBLEPULSAR implant
command-and-controlencryption-decryption-toolsexploitation+3
2259 years ago
Sudo-Vulnerability-Exploit-CVE-2019-14287 preview

Sudo-Vulnerability-Exploit-CVE-2019-14287

GitHubhasintha-98/sudo-vulnerability-exploit-cve-2019-14287

Exploit for CVE-2019-14287, a sudo vulnerability allowing privilege escalation via user ID -1 on Linux systems. Enables arbitrary command execution…
command-and-controlexploitationpenetration-testing+3
5 years ago
Log4Shell-CVE-2021-44228-PoC preview

Log4Shell-CVE-2021-44228-PoC

GitHubpierpaolosestito-dev/log4shell-cve-2021-44228-poc

CVE 2021-44228 Proof-of-Concept. Log4Shell is an attack against Servers that uses vulnerable versions of Log4J.

command-and-controlexploitationpayload-development+3
13 years ago
Previous123Next