

hexvero
 maximilianfeix/hexvero
Know what changed inside your Electron release: diff two builds for IPC, preload, windows, fuses and hosts, with file:line. CLI, CI gate, MCP server.
ai-securityandroid-securitybinary-analysis+9
10
maximilianfeix/hexveroKnow what changed inside your Electron release: diff two builds for IPC, preload, windows, fuses and hosts, with file:line. CLI, CI gate, MCP server.
 superandroidanalyzer/super
Secure, Unified, Powerful and Extensible Rust Android Analyzer
 androbugs/androbugs_framework
AndroBugs Framework is an efficient Android vulnerability scanner that helps developers or hackers find potential security vulnerabilities in Android…
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 dnspyex/dnspy
Unofficial revival of the well known .NET debugger and assembly editor, dnSpy
 pascal-lab/tai-e
An easy-to-learn/use static analysis framework for Java and Android
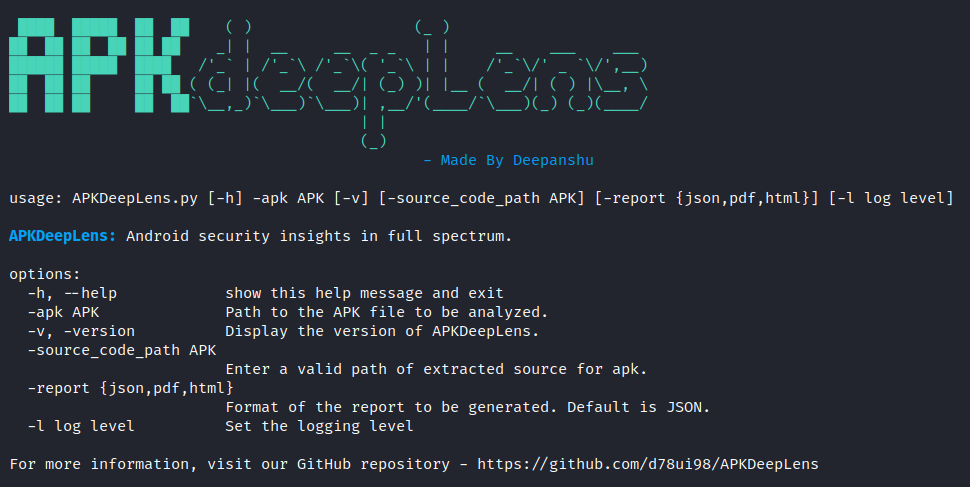 d78ui98/apkdeeplens
Android security insights in full spectrum.
 fadi002/de4py
The ultimate AI-powered toolkit for python reverse engineering
 ejfkdev/ddc
Android DEX → Java decompiler in Rust — quality-first: javac-verified output, exact semantic-preserving simplification (cure), full apps in seconds,…
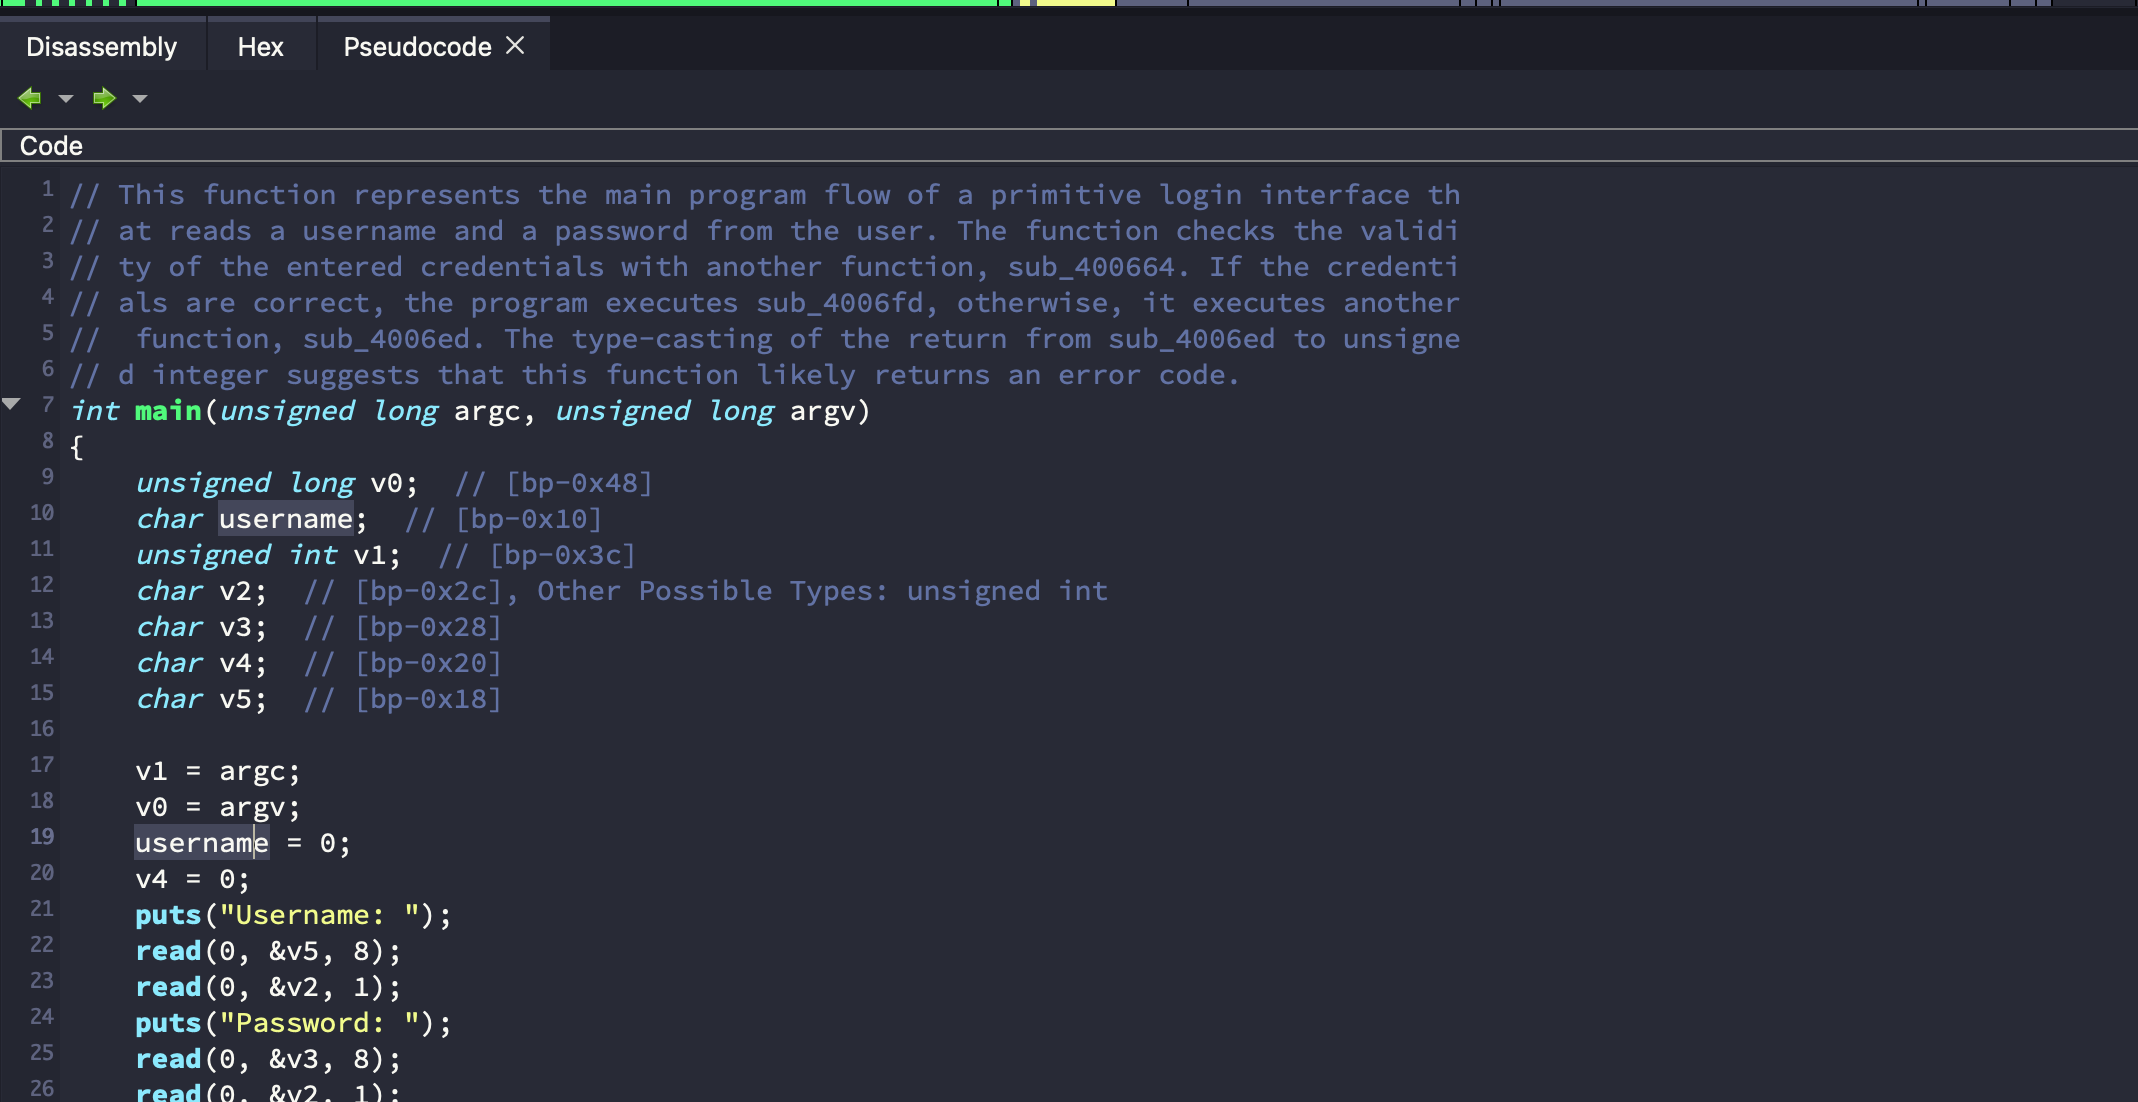 mahaloz/daila
A decompiler-agnostic plugin for interacting with AI in your decompiler. GPT, Claude, and local models supported!
 symbioticsec/hermes-decomp
A powerful decompiler that lets you reverse-engineer React Native mobile apps by converting their compiled Hermes bytecode (.hbc) files back into…
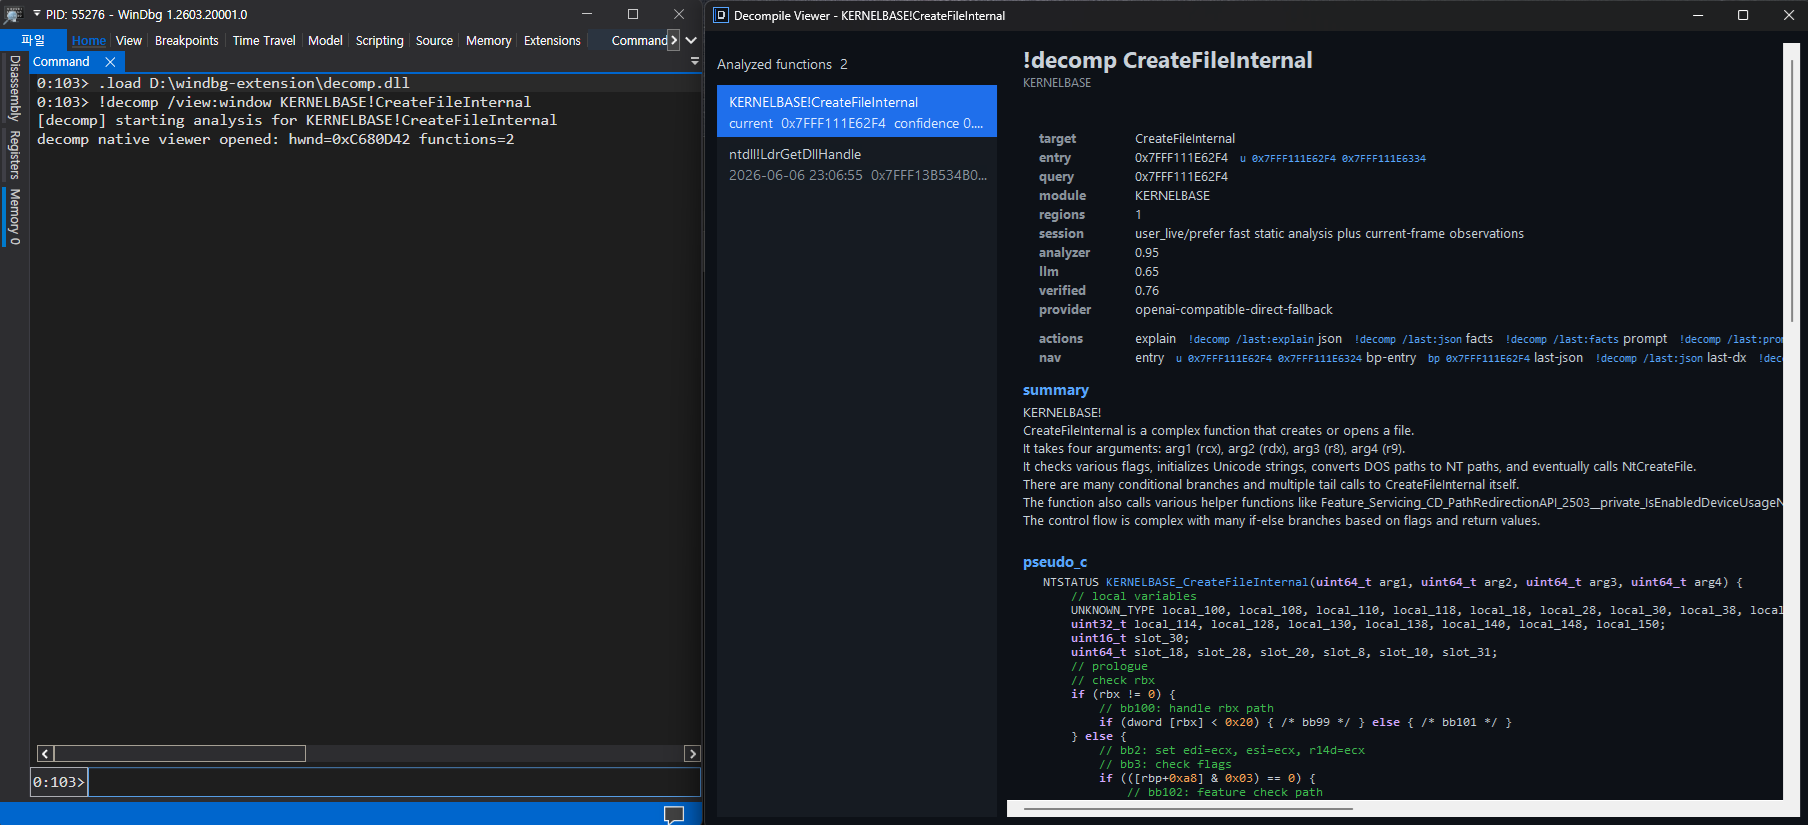 kernullist/windbg-decompile-ext
WinDbg x64 extension that disassembles live functions and uses an LLM to produce verified pseudocode.
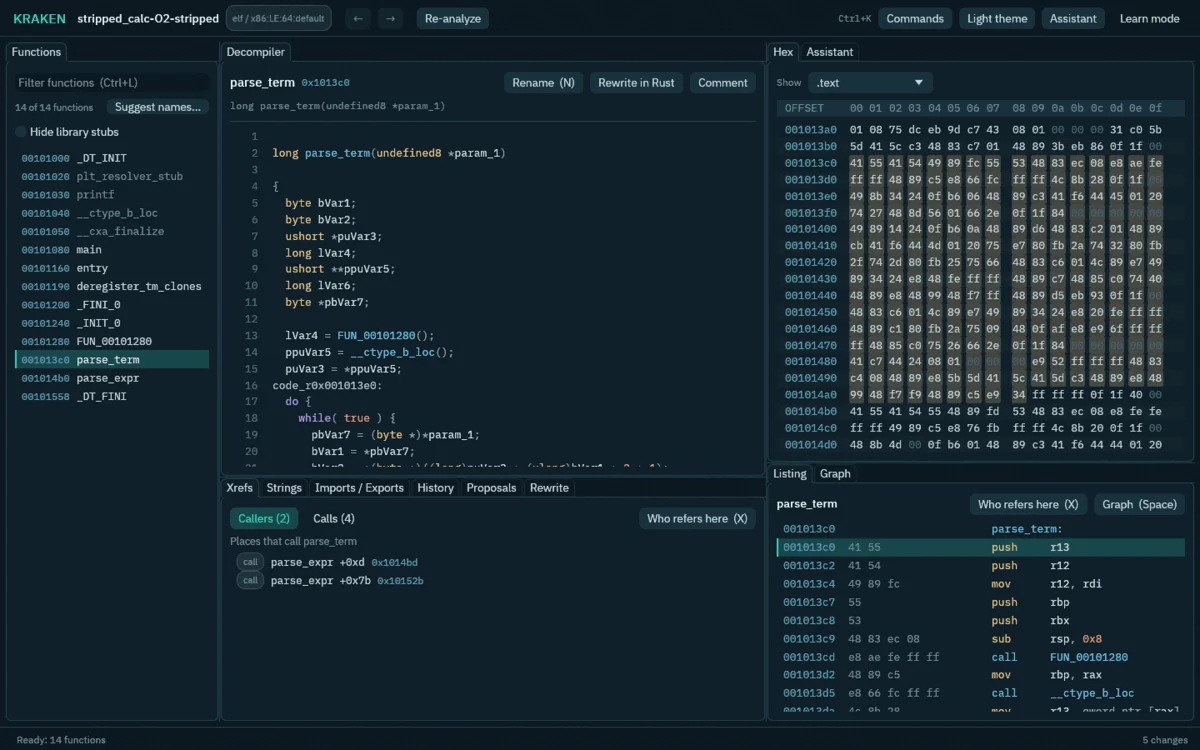 adam-atlassoftware/kraken
Reverse-engineering workbench built on Ghidra's decompiler with a native Java-free engine, AI-assisted function analysis, byte patching, sandboxed…
 martyx00/vulnfanatic-ng
BianryNinja plugin for identifying vulnerabilities in decompiled binaries with both programmatic scans and LLM support.
 gmh5225/gmh5225
LLVM-based security research toolchain: NeverC, a C23 cross-compiler, and NeverD, a binary analysis and decompilation engine that lifts PE, ELF,…