
PolinRider
 opensourcemalware/polinrider
Technical dossier on the DPRK-linked PolinRider supply-chain attack, documenting obfuscated JS payload injection, git history manipulation, C2…
code-analysiscurated-resourceseducation+8
99
opensourcemalware/polinriderTechnical dossier on the DPRK-linked PolinRider supply-chain attack, documenting obfuscated JS payload injection, git history manipulation, C2…
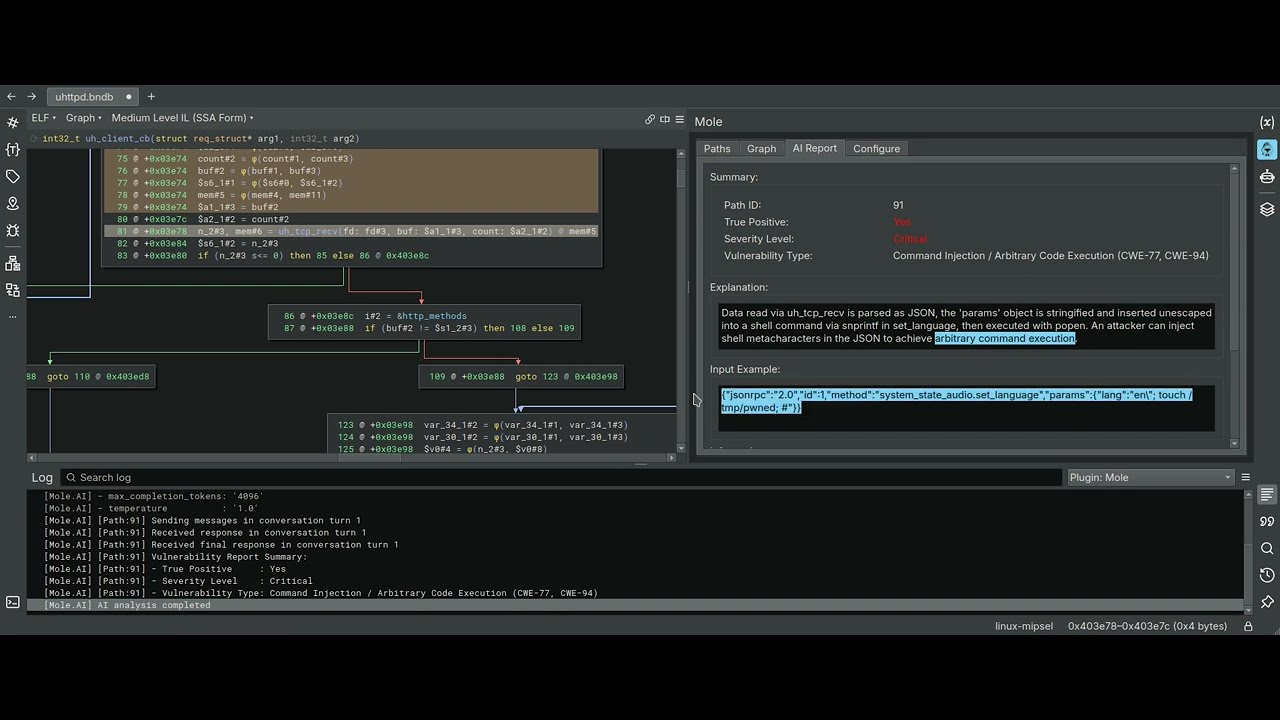 cyber-defence-campus/mole
A Binary Ninja plugin using backward slicing of variables as a driver for static taint analysis
 trailofbits/ruzzy
A coverage-guided fuzzer for pure Ruby code and Ruby C extensions
 airbus-cert/vbsparkle
VBScript & VBA source-to-source deobfuscator with partial-evaluation
 josue87/wp_hunter
Static analysis of wordpress plugins
 polaris64/web_exploit_detector
The Web Exploit Detector is a Node.js application used to detect possible infections, malicious code and suspicious files in web hosting environments
 lunixbochs/revsync
realtime cross-tool collaborative reverse engineering
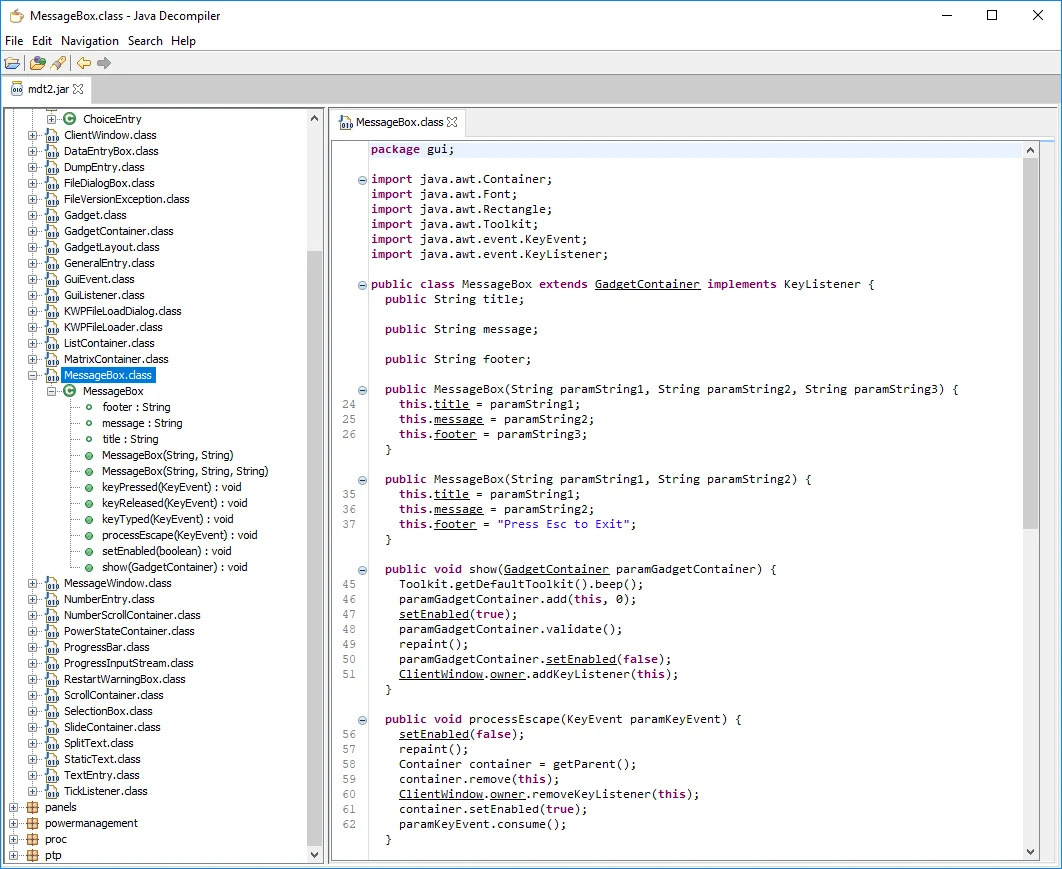 pelock/jobfuscator
Obfuscates Java source code to protect against reverse engineering, decompilation, and IP theft. Renames variables/methods, encrypts strings, and…
 momenbasel/malware-check
Static and dynamic analysis tool for detecting malicious code, suspicious binaries, and privacy violations
 silverplate3/my-cves
CVE's I found. technical writeups, expolitation examples and fuzzing sessions walkthroughs
 ejfkdev/jscd
Reverse bytenode .jsc (V8 code cache) to JavaScript — static, pure Rust, no patched V8/Node. Node 8→26 / V8 5.8–14.6; 25k .jsc tested, 0 fail.
 mahmoudimus/static_asm
Header-only C++2x compile-time assembler for x86/x86-64 instruction encoding
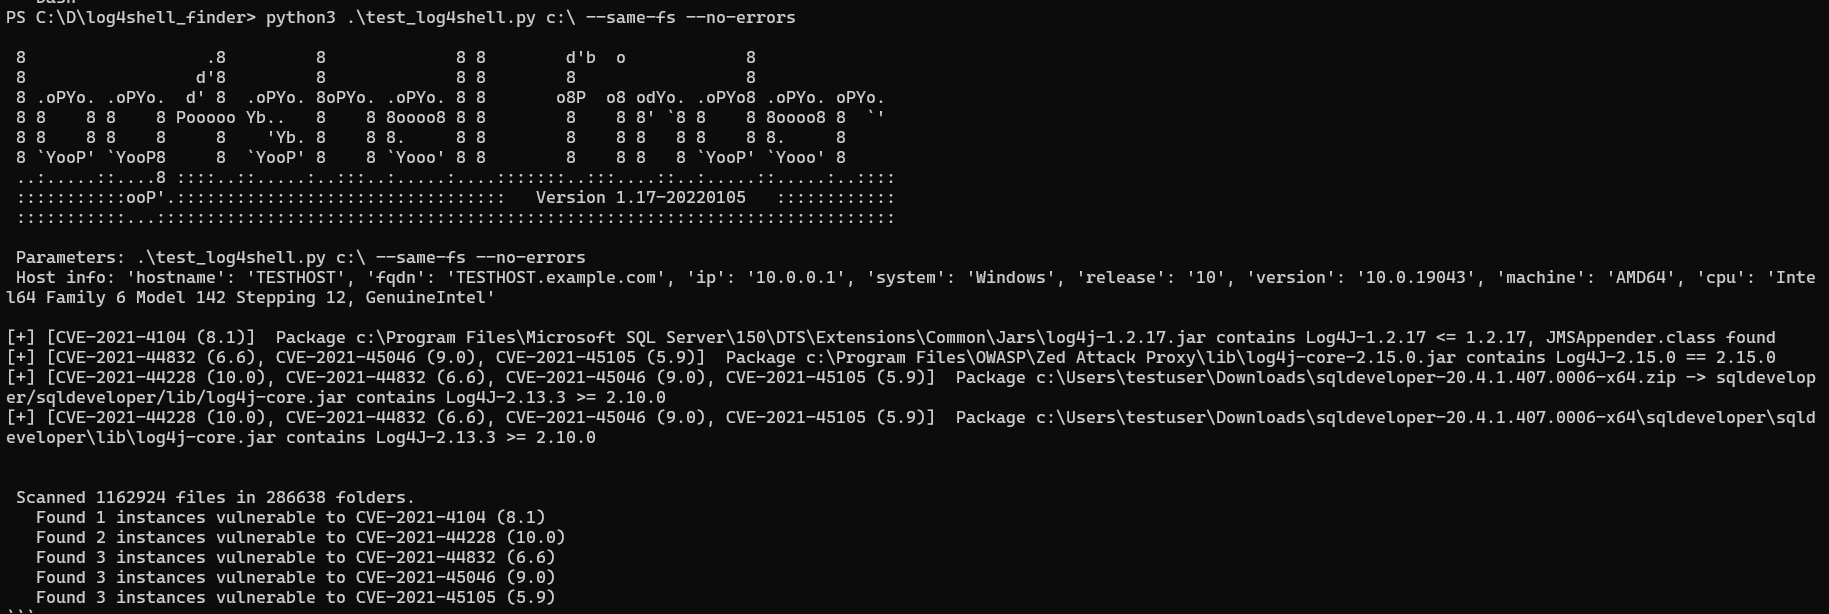 hynekpetrak/log4shell-finder
Fastest filesystem scanner for log4shell (CVE-2021-44228, CVE-2021-45046) and other vulnerable (CVE-2017-5645, CVE-2019-17571, CVE-2022-23305,…
 neargle/go-get-rce-cve-2018-6574-poc
CVE-2018-6574 POC : golang 'go get' remote command execution during source code build
 owasp/vulnreach
Runtime-aware SCA — proves which CVEs are actually reachable, not just installed.
 xv4l3x/hermit
Inspects, decompiles and structurally patches Hermes bytecode (HBC) from React Native apps, with a GDB-style REPL, CFG, decompiler and re-serializing…
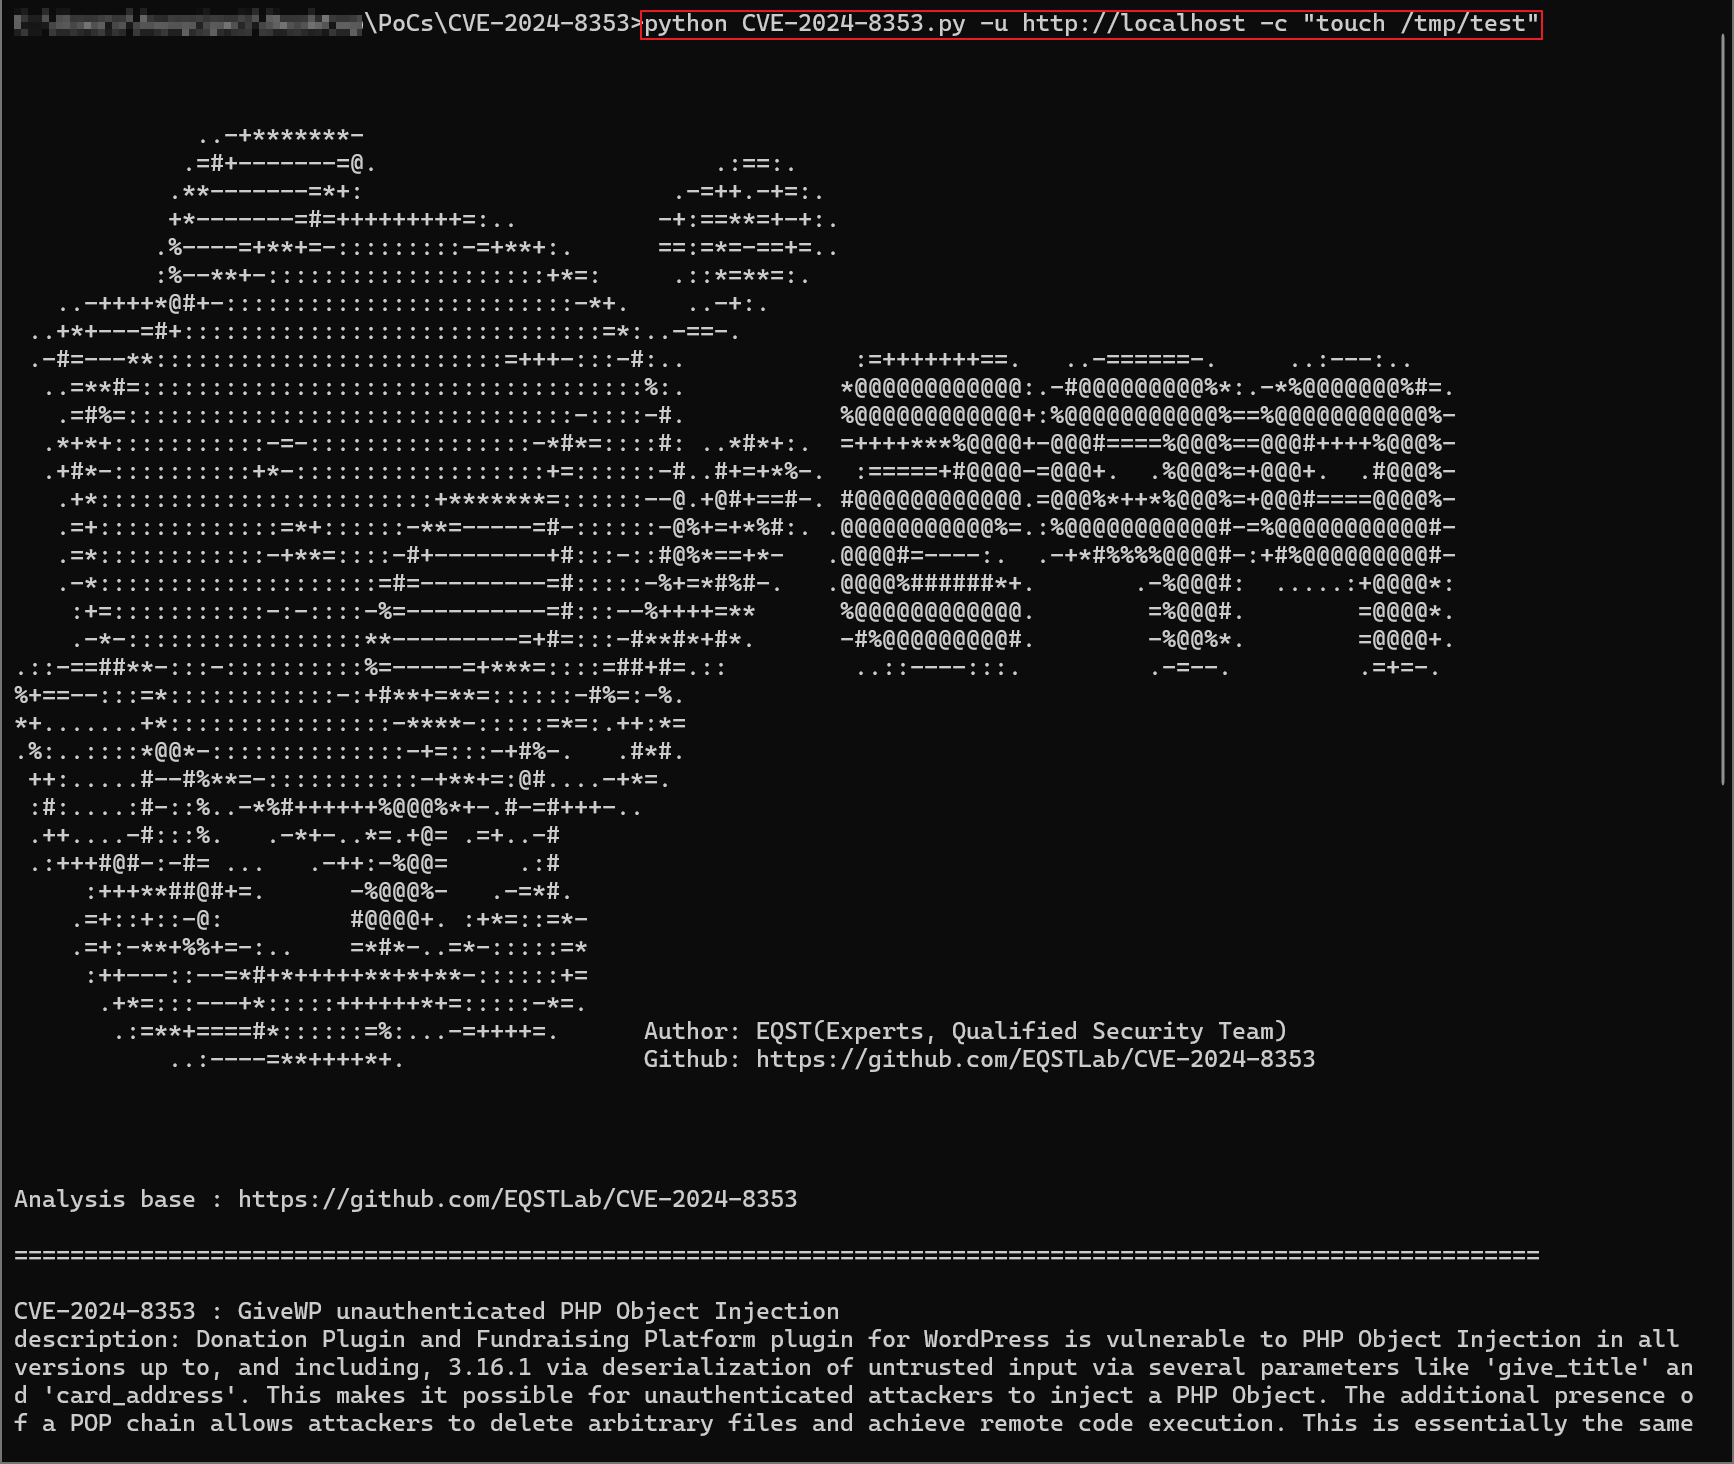 eqstlab/cve-2024-8353
GiveWP PHP Object Injection exploit
 vulnz/sast
Free offline SAST engine for CI/CD: AST and cross-file taint analysis, secret detection with live validation, SCA/CVE, IaC misconfiguration, and…