
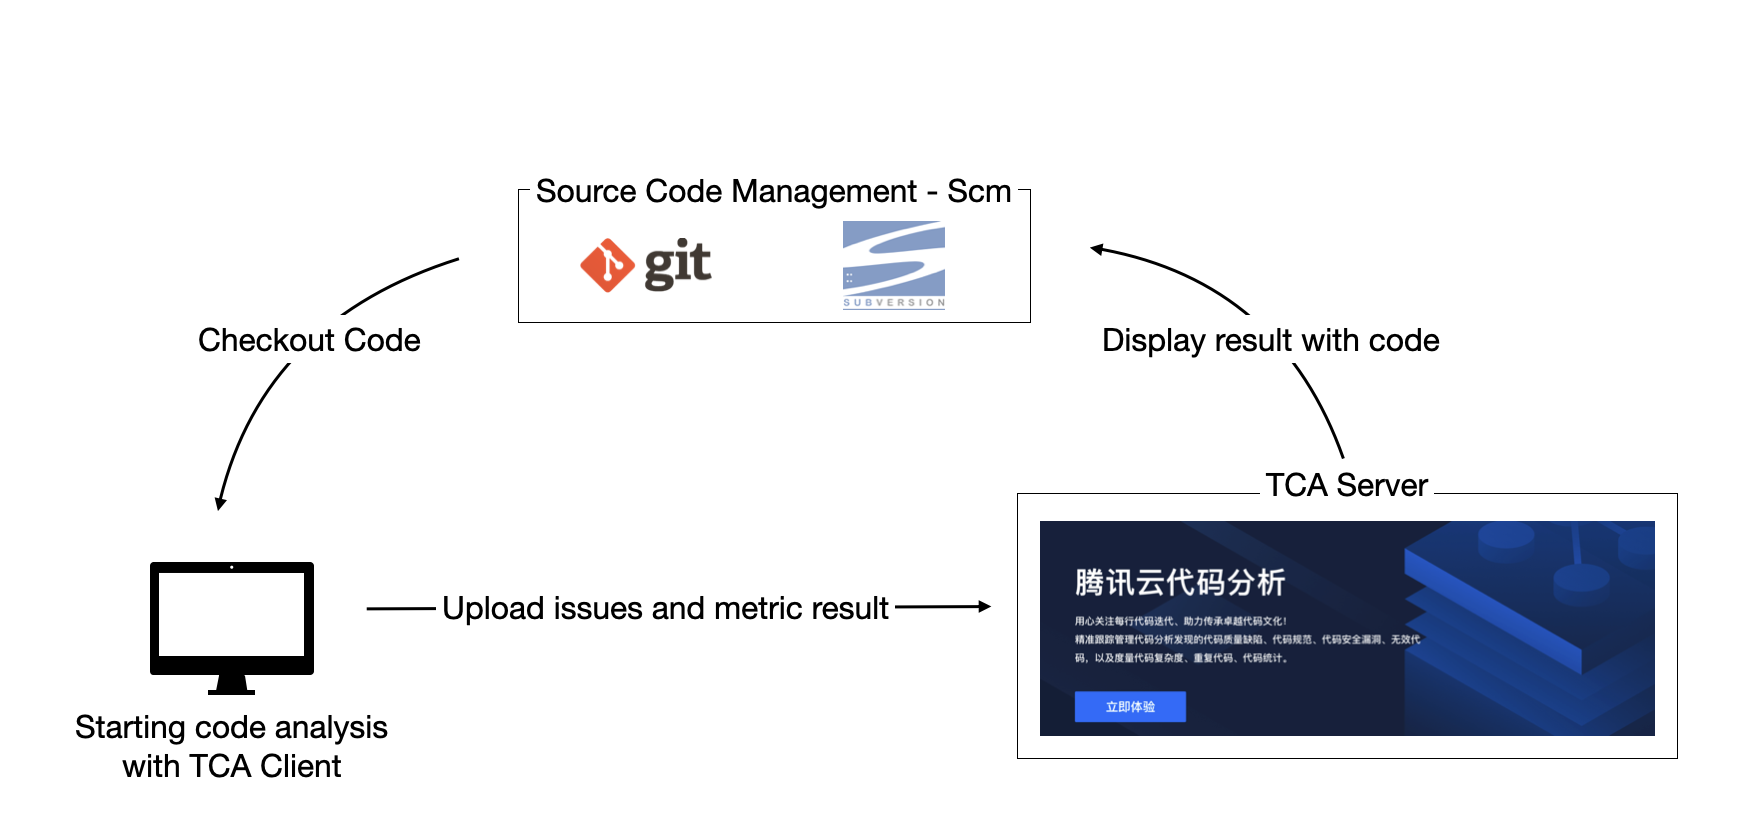
CodeAnalysis
 tencent/codeanalysis
Enterprise-grade static code analysis platform with multi-language support, security vulnerability detection, code quality metrics, and DevOps…
code-analysisdevsecopseducation+3
1.8k
tencent/codeanalysisEnterprise-grade static code analysis platform with multi-language support, security vulnerability detection, code quality metrics, and DevOps…
 p3nt4/powershdll
Run PowerShell with rundll32. Bypass software restrictions.
 zupit/horusec
Horusec is an open source tool that improves identification of vulnerabilities in your project with just one command.
 nealbridges/vulnhunter
Agentic AI security scanner that reasons like an attacker over source code, confirms exploitable flaws with executable PoCs, and drives test-first…
 praetorian-inc/titus
High-performance secrets scanner. CLI, Go library, Burp Suite extension, and Chrome extension. 487 detection rules with live credential validation.
 owasp/owasp-java-encoder
The OWASP Java Encoder is a Java 1.5+ simple-to-use drop-in high-performance encoder class with no dependencies and little baggage. This project will…
 silentchainai/silentchain
AI-powered vulnerability scanner extension for Burp Suite with multi-provider support (Ollama, OpenAI, Claude, Gemini)
 whgojp/javaseclab
Comprehensive Java vulnerability lab with vulnerable and fixed code, attack scenarios, source/sink audit notes, and secure coding guidance for…
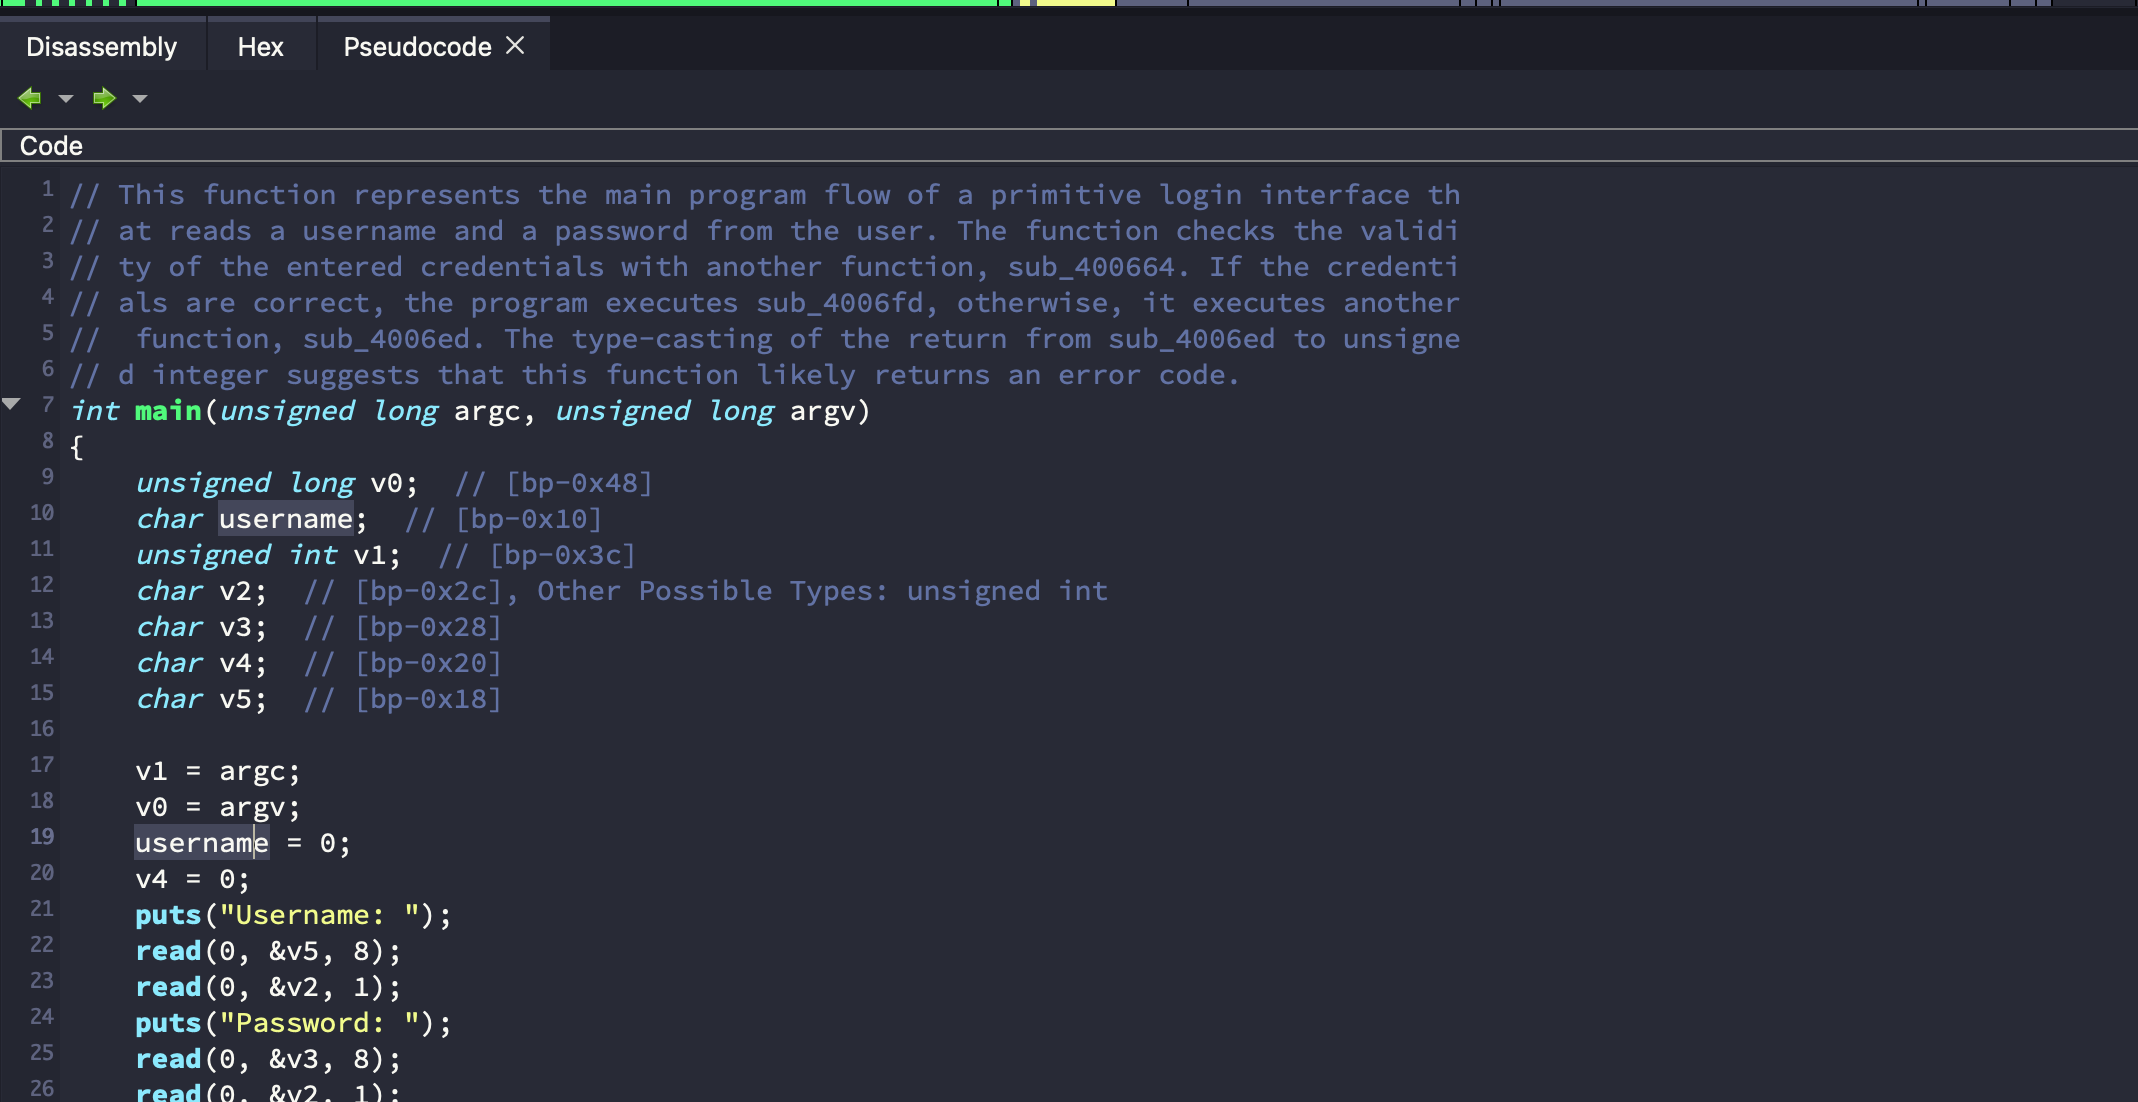 mahaloz/daila
A decompiler-agnostic plugin for interacting with AI in your decompiler. GPT, Claude, and local models supported!
 elastic/supply-chain-monitor
Automated supply chain security monitor that polls PyPI and npm registries, diffs new releases against predecessors, and uses LLM analysis to detect…
 githubsecuritylab/seclab-taskflow-agent
MCP-enabled multi-agent framework for declarative YAML-driven agentic workflows, used for AI-assisted code auditing, vulnerability triage, and…
 agent-field/sec-af
AI-native code security auditor on AgentField that proves exploitability with verdicts, traces, and actionable evidence.
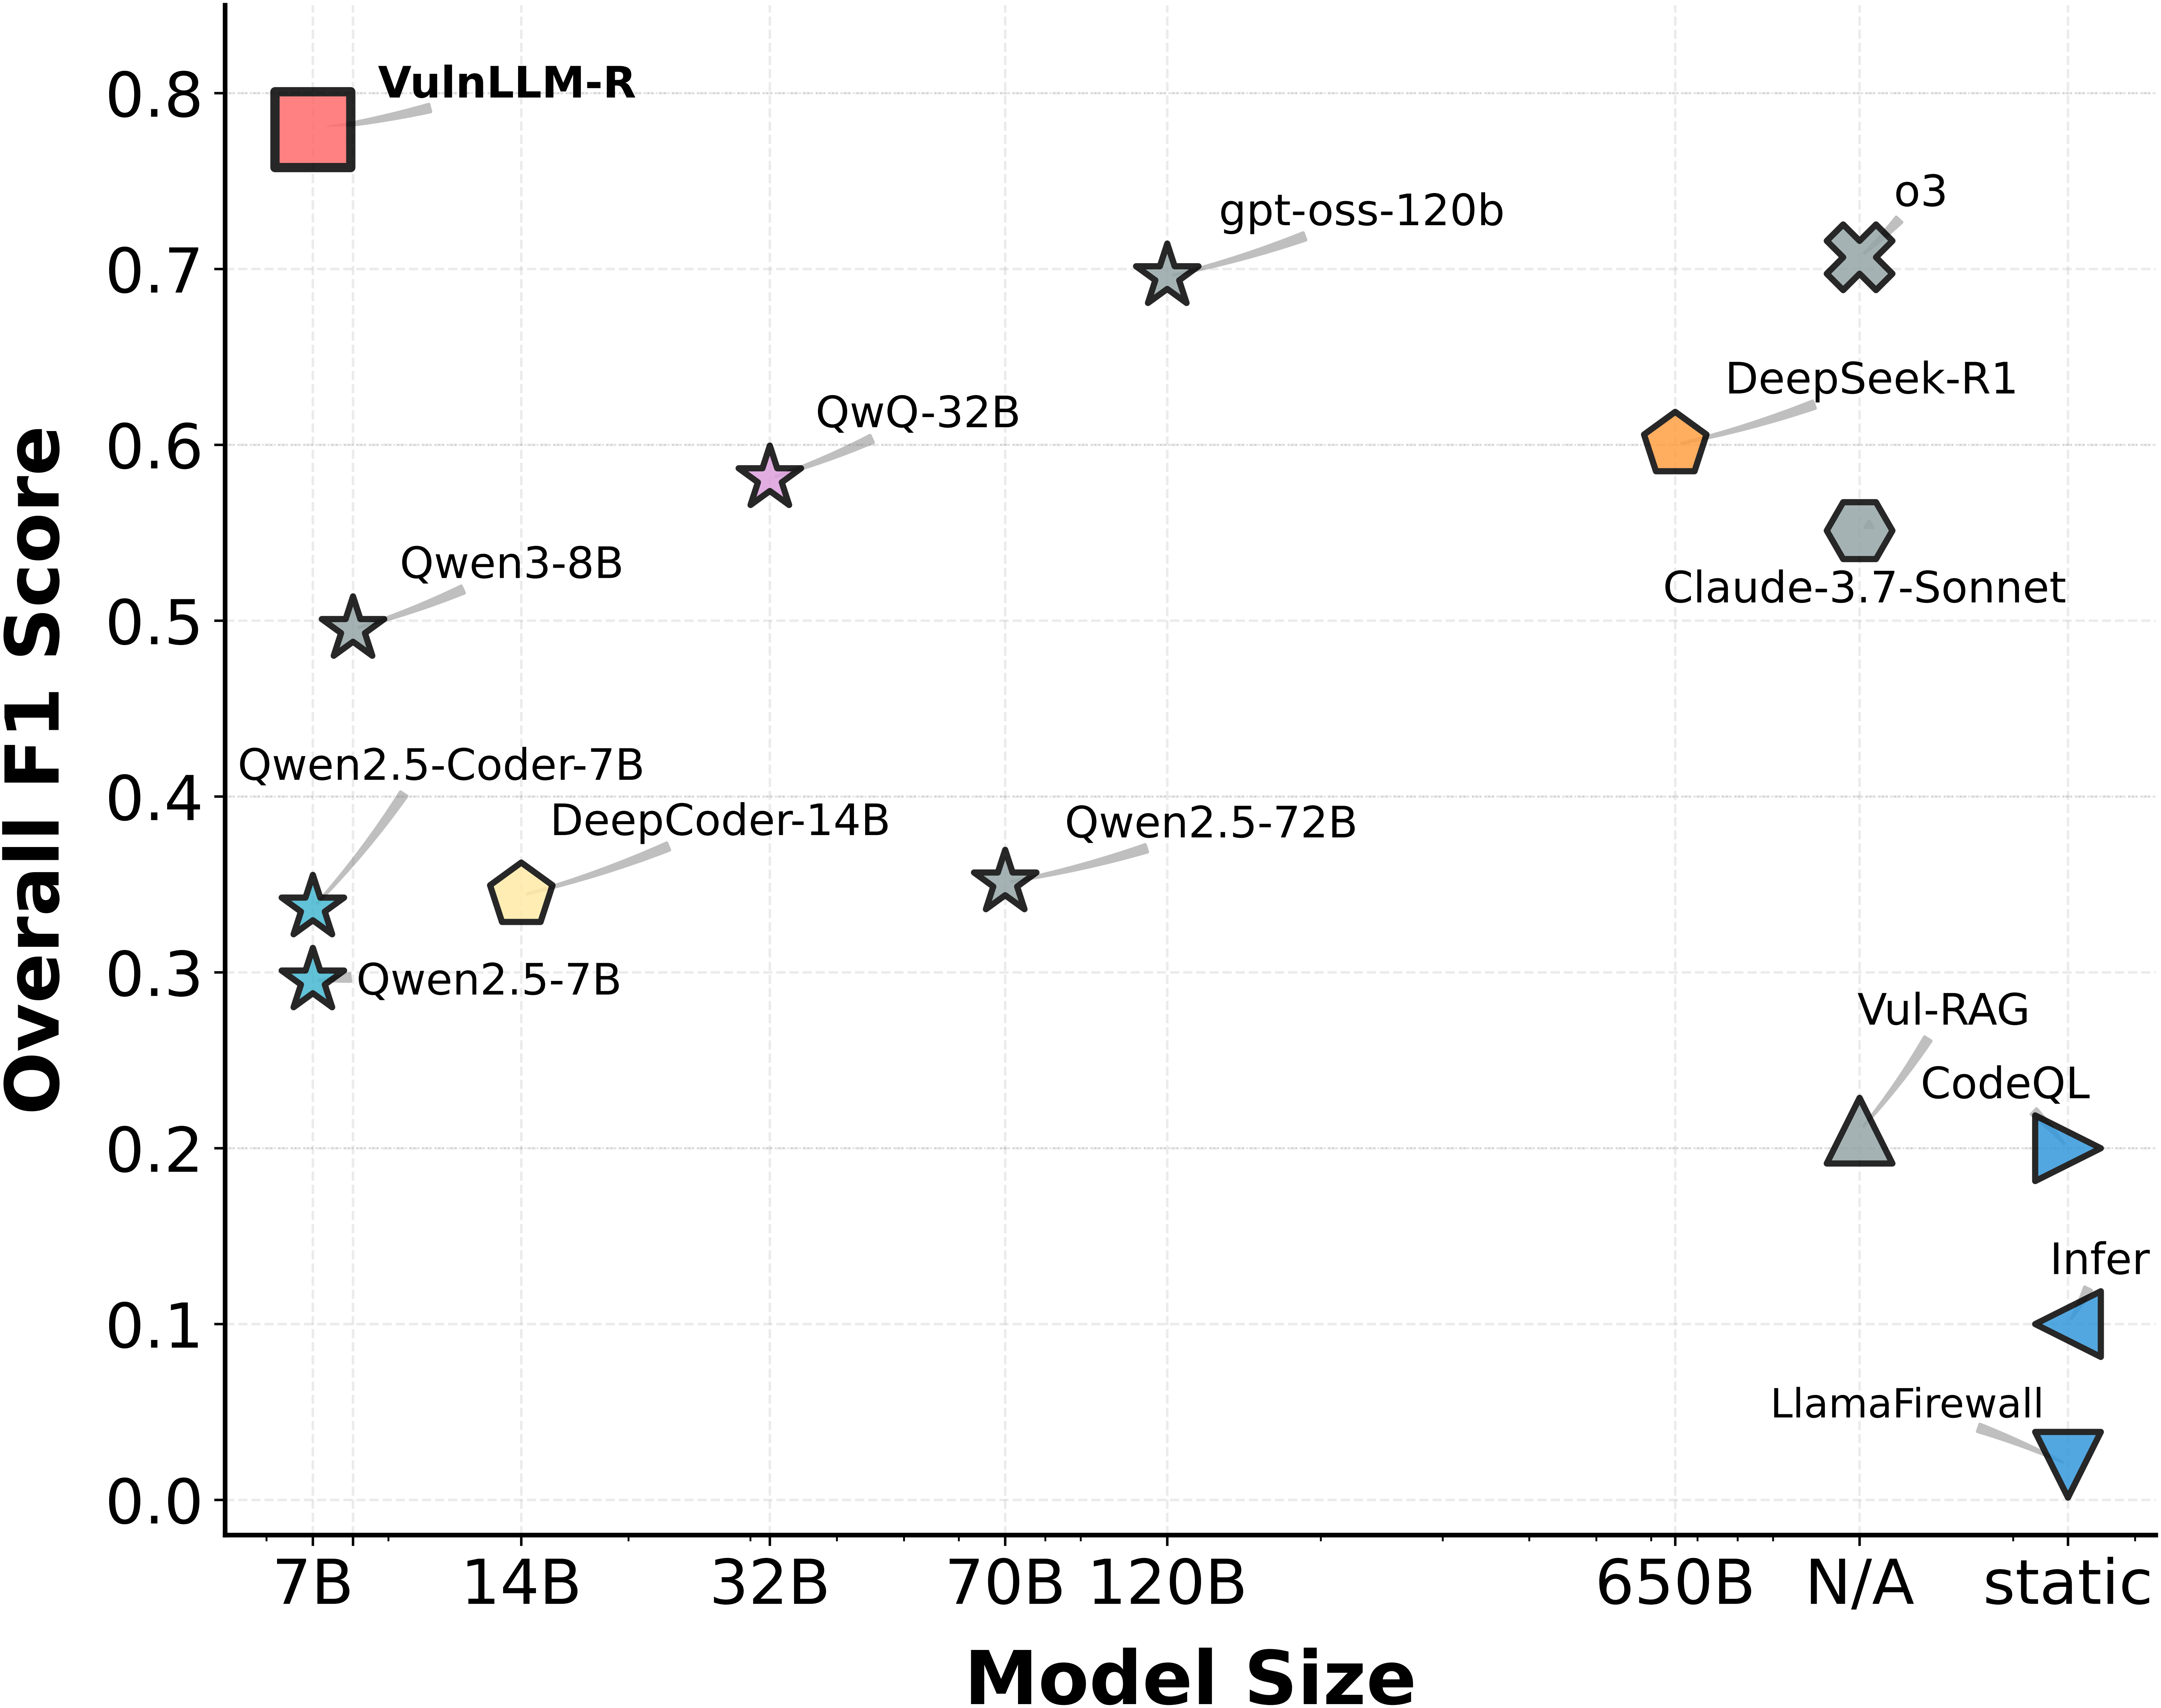 ucsb-mlsec/vulnllm-r
Specialized reasoning LLM for source-code vulnerability detection in C/C++ and Python, with dataset construction, SFT/DPO training, and…
 corgea/sighthound
Tree-sitter based static vulnerability scanner with pattern matching and taint-flow analysis for multi-language source code. Outputs findings as…
 ewenquim/entropy
CLI tool that scans codebases for high-entropy lines to detect potential secrets, with customizable file extension and top-N filtering.
 trailofbits/test-fuzz
Rust macros and Cargo subcommand to automate fuzzing with afl.rs, including corpus generation and harness implementation, integrated with Rust's…
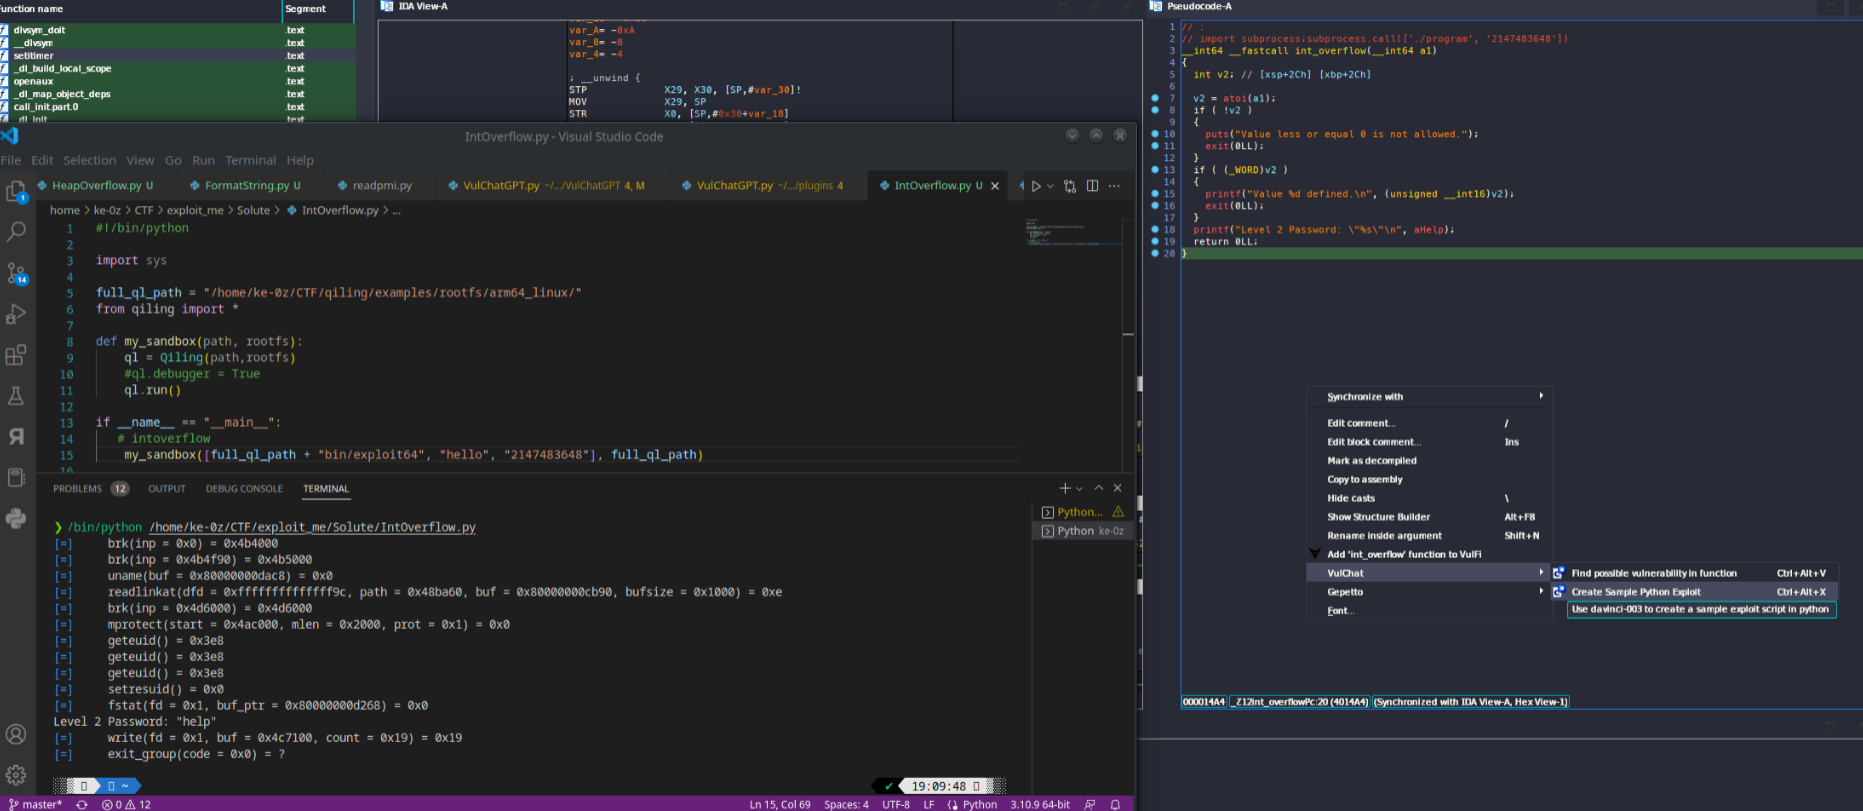 ke0z/binaivulhunter
Use IDA PRO HexRays decompiler with OpenAI(ChatGPT) to find possible vulnerabilities in binaries
 awslabs/threat-modeling-mcp-server
MCP server for structured STRIDE-based threat modeling with automatic code validation, business context analysis, and comprehensive report generation…