

ASC
 mg1937/asc
Fast Android APK decompiler front-end that queries compiled DEX artifacts directly, extracting classes and cross-references in milliseconds without…
android-securitybinary-analysiscode-analysis+6
2.3k
mg1937/ascFast Android APK decompiler front-end that queries compiled DEX artifacts directly, extracting classes and cross-references in milliseconds without…
 corelight/quipu
A desktop workbench for writing, validating, compiling, and testing YARA rules.
 projectdiscovery/nuclei-templates
Community curated list of templates for the nuclei engine to find security vulnerabilities.
 praetorian-inc/trajan
A multi-platform CI/CD vulnerability detection and attack automation tool for identifying security weaknesses in pipeline configurations.
 trailofbits/skills
Trail of Bits Claude Code skills for security research, vulnerability detection, and audit workflows
 trufflesecurity/trufflehog
Find, verify, and analyze leaked credentials
 frida/frida
Main repo for hosting release binaries
 nuguardai/nuguard
opensource repo for validating agentic AI applications: redteam, behavior, supply-chain, static analysis
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 phpstan/phpstan
PHP Static Analysis Tool - discover bugs in your code without running it!
 cure53/dompurify
DOMPurify - a DOM-only, super-fast, uber-tolerant XSS sanitizer for HTML, MathML and SVG. DOMPurify works with a secure default, but offers a lot of…
 owasp/cheatsheetseries
The OWASP Cheat Sheet Series was created to provide a concise collection of high value information on specific application security topics.
 owasp/aisvs
The AI Security Verification Standard (AISVS) focuses on providing developers, architects, and security professionals with a structured checklist to…
 usestrix/strix
Open-source AI penetration testing tool to find and fix your app’s vulnerabilities.
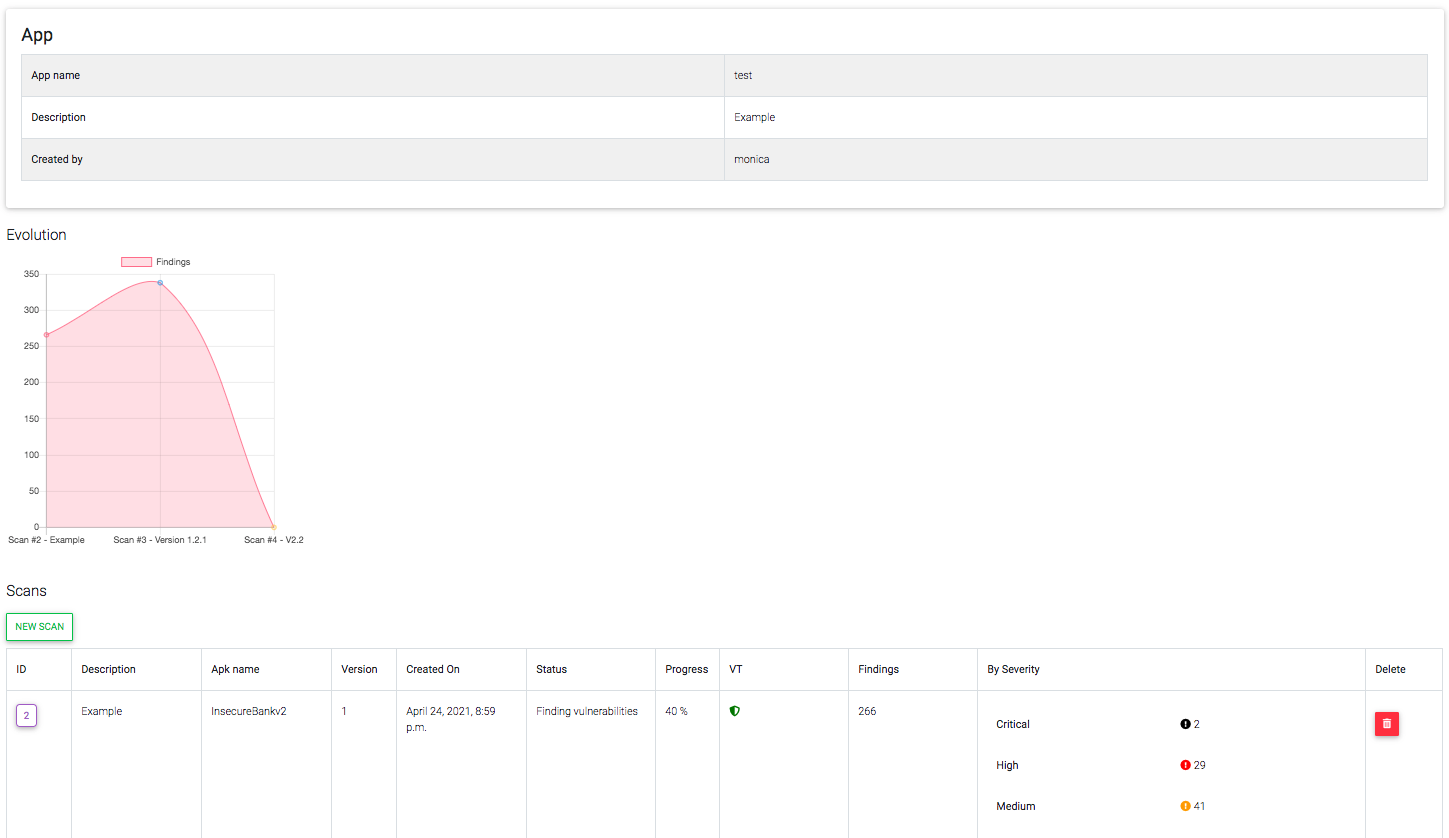 mpast/mobileaudit
Django application that performs SAST and Malware Analysis for Android APKs
 facebook/mariana-trench
A security focused static analysis tool for Android and Java applications.
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
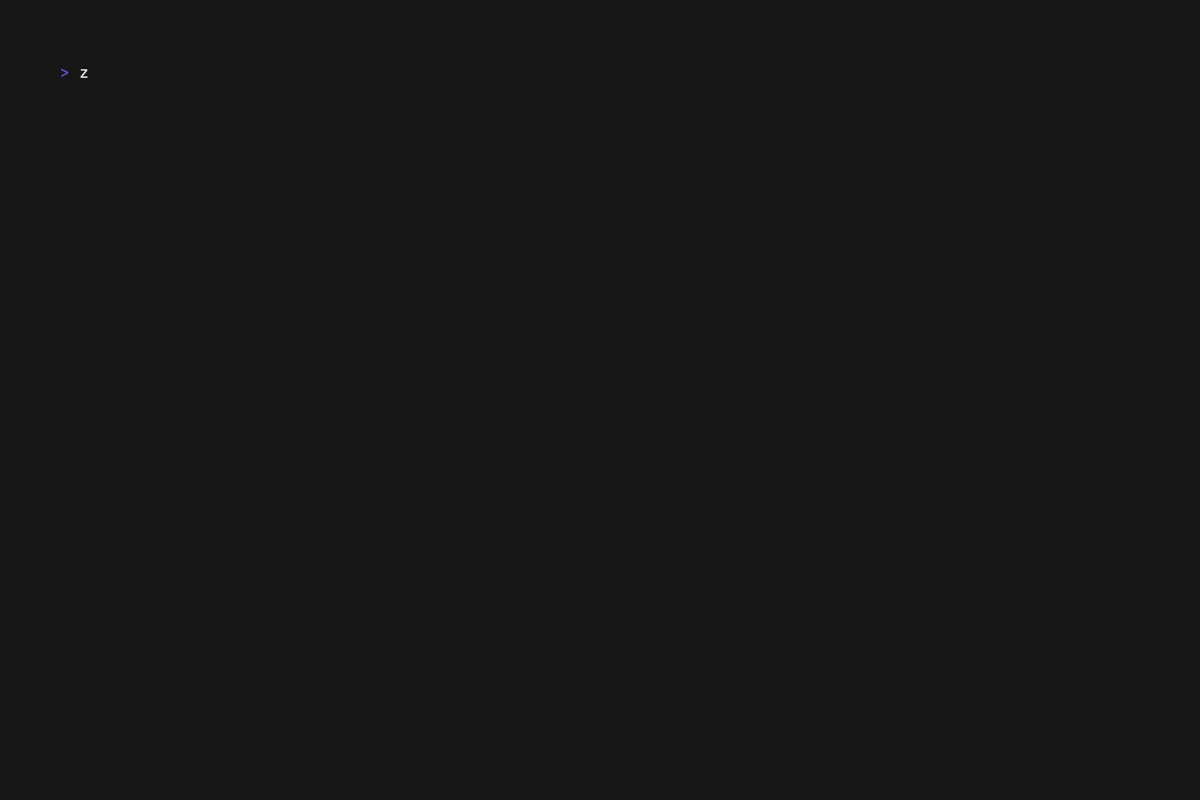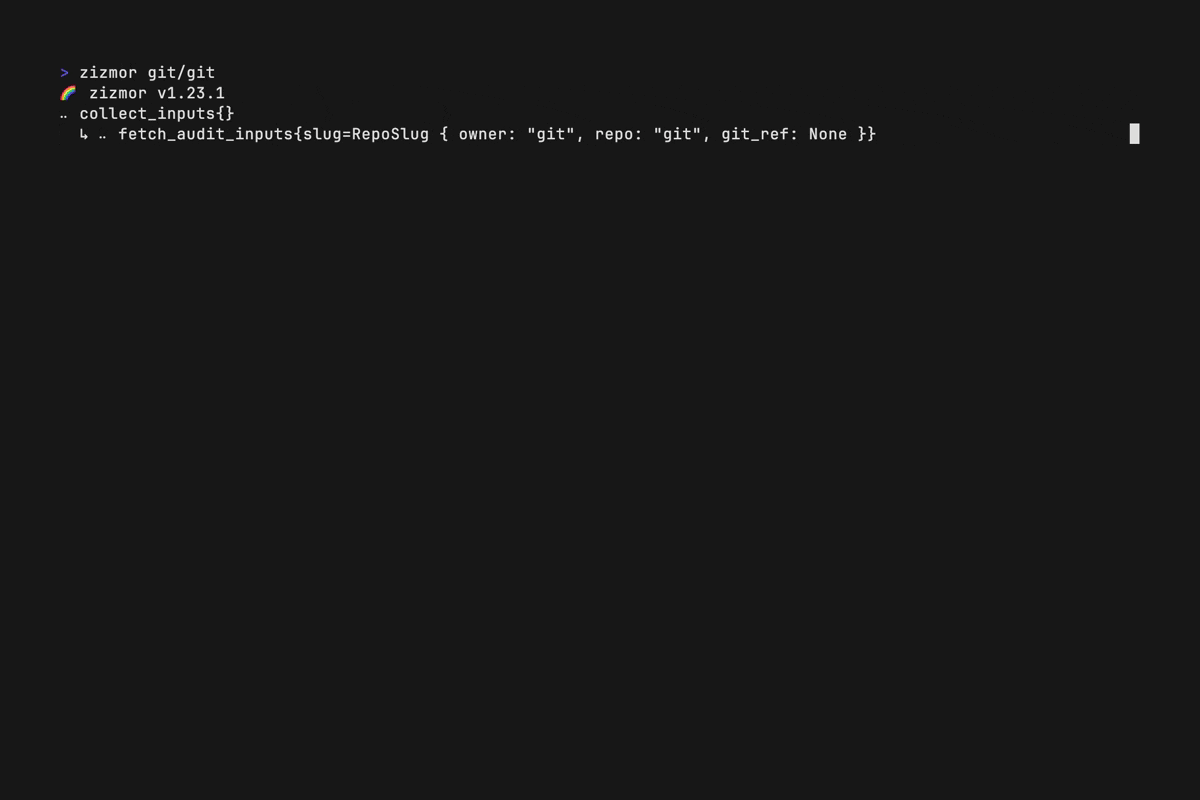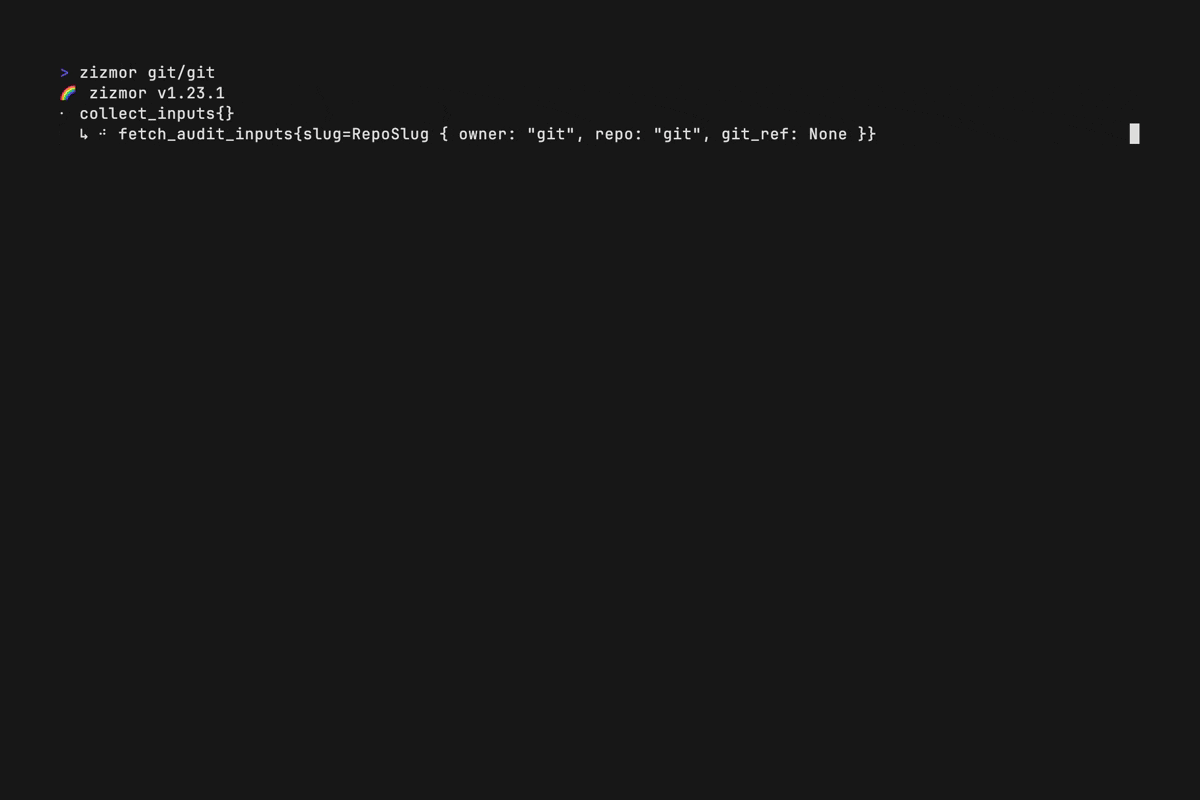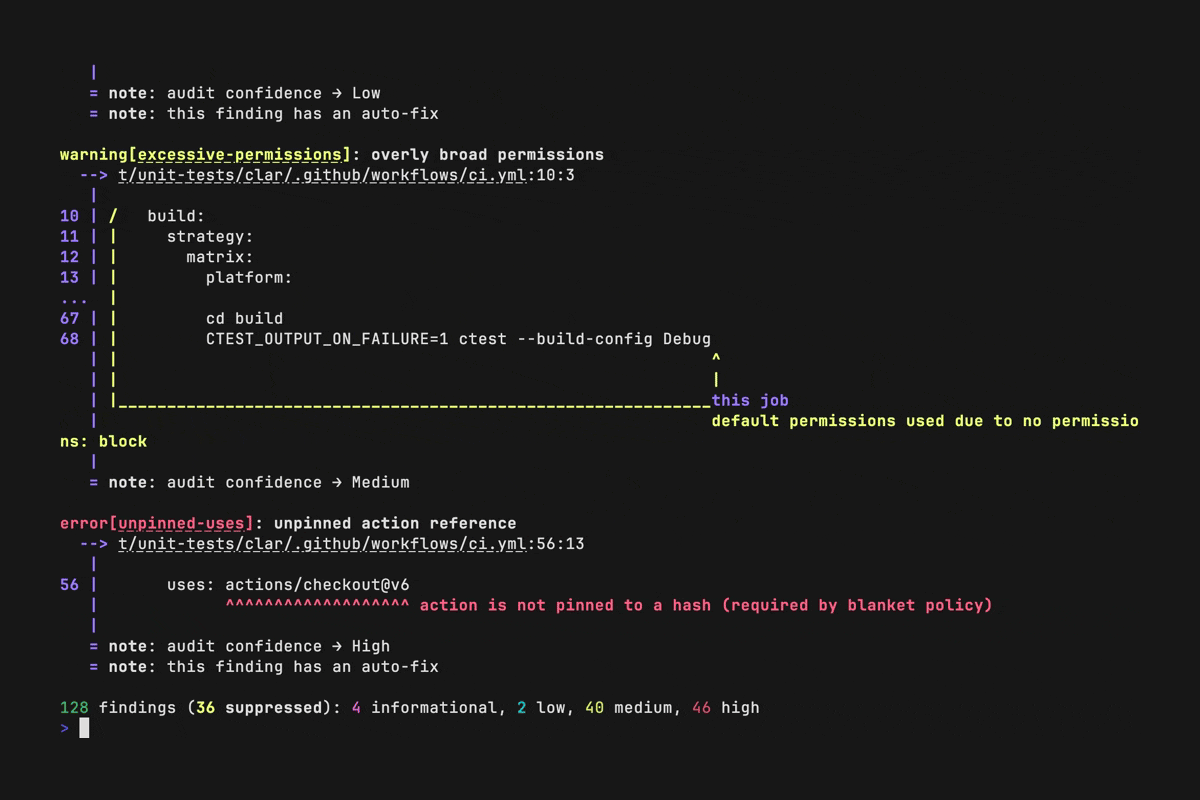 zizmorcore/zizmor
Static analysis tool for CI/CD systems that detects and fixes security issues in GitHub Actions, Dependabot, and pre-commit configurations, including…