

sast-scan-action
 offensive360/sast-scan-action
GitHub Action for Offensive360 SAST scans and SARIF results. See the open-source program for eligibility and setup.
api-security-testingcloud-securitycode-analysis+4
offensive360/sast-scan-actionGitHub Action for Offensive360 SAST scans and SARIF results. See the open-source program for eligibility and setup.
 offensive360/mcp-server
MCP server that runs SAST scans on local codebases and returns findings with severity and fixes, enabling AI assistants to perform security analysis…
 tomnomnom/gf
A wrapper around grep, to help you grep for things
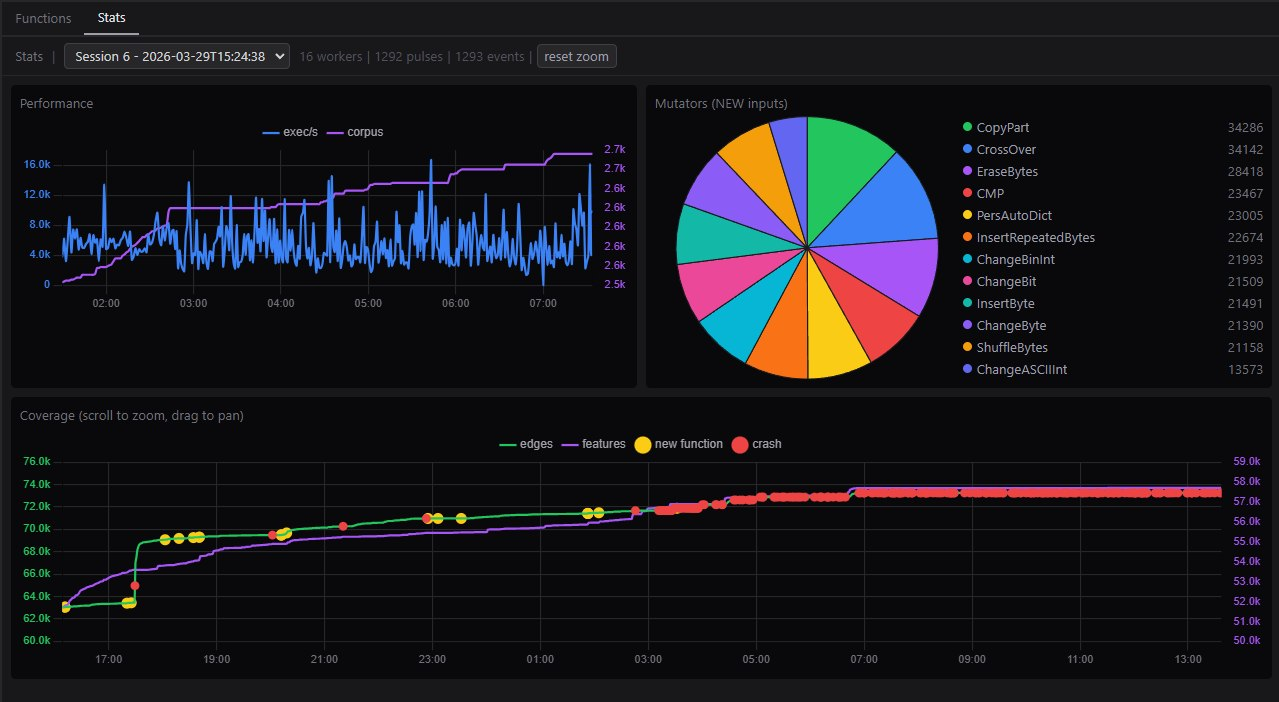 0xbigshaq/apatchy
Fuzzing Framework for Modules in Apache HTTPD Server
 skysliently/cve-2022-22947-pb-ai
一个由AI生成的漏洞验证应用
 cerberusmrxi/cve-2026-44680-mikroorm-sql-injection-exploit-framework
PoC tool for CVE-2026-44680 affecting MikroORM ≤7.0.13. Exploits JSON path injection to extract database contents via UNION-based attacks. Features…
 csinexus/mcpshield
Drop-in fix for the unpatched MCP STDIO command-injection flaw (CVE-2026-30623 family)
 owasp/agent-security-regression-harness
Executable security regression testing for agentic applications and MCP-integrated systems.
 trailofbits/slither-mcp
MCP server for Slither static analysis of Solidity smart contracts
 silentchainai/silentchain
AI-powered vulnerability scanner extension for Burp Suite with multi-provider support (Ollama, OpenAI, Claude, Gemini)
 shoucheng3/x-stream__xstream_cve-2021-21345_1-4-15
Java XML serialization library with a focus on CVE-2021-21345 exploit analysis and deserialization vulnerability testing for web applications.
 ananay/wp2shell-lab
Validation target: minimal WordPress core slice reproducing the wp2shell (CVE-2026-63030 + CVE-2026-60137) REST-to-SQLi chain
 usestrix/strix
Open-source AI penetration testing tool to find and fix your app’s vulnerabilities.
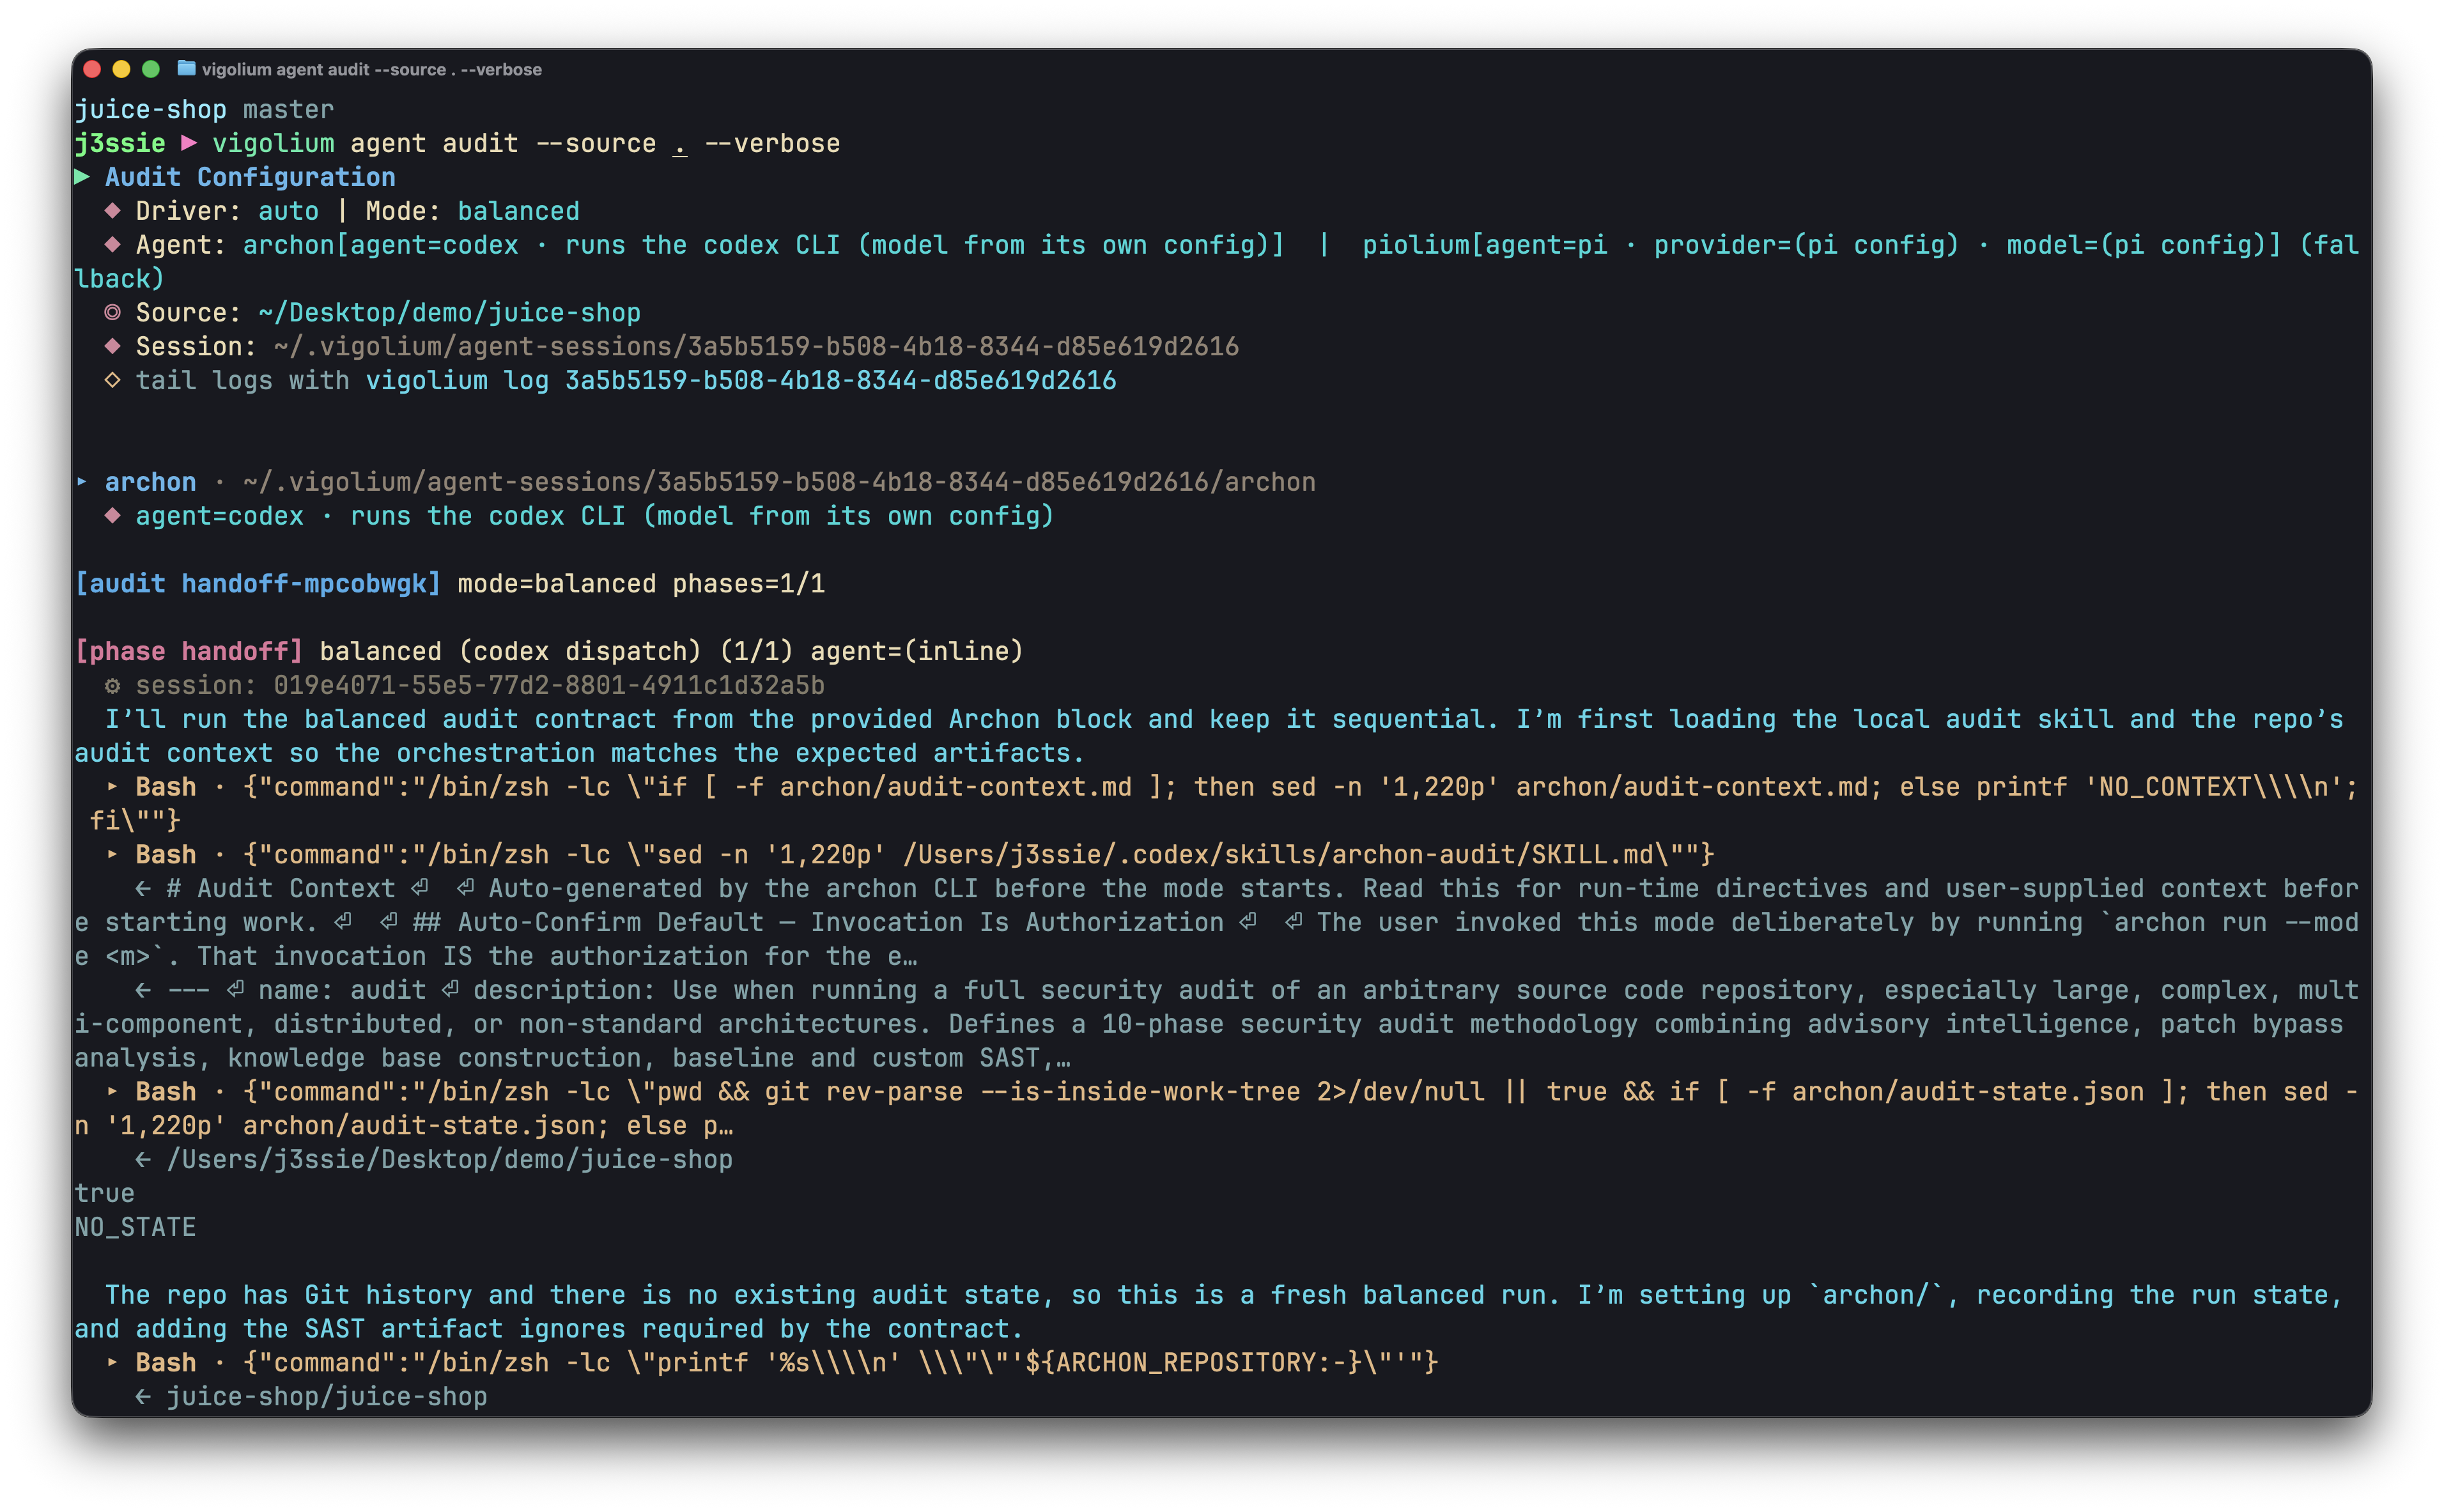 vigolium/vigolium
Vigolium - High-fidelity vulnerability scanner fusing agentic AI with native speed, modularity, and precision
 nuguardai/nuguard
opensource repo for validating agentic AI applications: redteam, behavior, supply-chain, static analysis
 cloudflare/security-audit-skill
A coding-agent skill for multi-phase security audits with independently verified, machine-readable findings
 jpiechowka/jenkins-cve-2016-0792
Exploit for Jenkins serialization vulnerability - CVE-2016-0792
 hupe1980/cve-2021-3129
Laravel debug mode - Remote Code Execution (RCE)