

MFASweep
 dafthack/mfasweep
A tool for checking if MFA is enabled on multiple Microsoft Services
authenticationcloud-securitypenetration-testing+2
dafthack/mfasweepA tool for checking if MFA is enabled on multiple Microsoft Services
 microsoft/onefuzz
A self-hosted Fuzzing-As-A-Service platform
 invictus-ir/alfa
Automated forensic analysis tool for Google Workspace audit logs. Acquires all log types, maps events to MITRE ATT&CK Cloud Framework, and identifies…
 fleetdm/fleet
Open-source platform to secure and manage endpoints via MDM, patch management, software deployment, and osquery-powered visibility with compliance…
 openclarity/openclarity
OpenClarity is an open source platform built to enhance security and observability of cloud native applications and infrastructure
 tylermontneyacc/updatewindowsre-cve-2022-41099
Script to update Windows Recovery Environment to patch against CVE-2022-41099
 microsoft/restler-fuzzer
RESTler is the first stateful REST API fuzzing tool for automatically testing cloud services through their REST APIs and finding security and…
 wattocyber/detection-defense-library
Detection-engineering reference mapping Windows, cloud, container, identity, and ICS attack classes to Sigma rules, trust-boundary models, BYOVD…
 cyberjez/pqc-scanner
The PQC Network Scanner is a quantum‑focused network assessment tool that scans TLS/SSL certificates across enterprise environments to identify…
 zephrfish/azureattackkit
Collection of Azure Tools to Pull down for Attacking an Environment + quick tips and other useful information
 dawnsmithcyber/azure-vulnerability-remediation-project
End-to-end vulnerability management lifecycle on Azure Windows Server 2025. Features OS patching and network-level compensating controls (NSG) to…
 mrk336/from-foothold-to-domain-admin-weaponizing-cve-2025-54918-in-real-world-devops
Simulated exploitation and mitigation of CVE-2025-54918 (Windows NTLM flaw). Includes detection scripts, Ansible patching, and CI/CD hardening.…
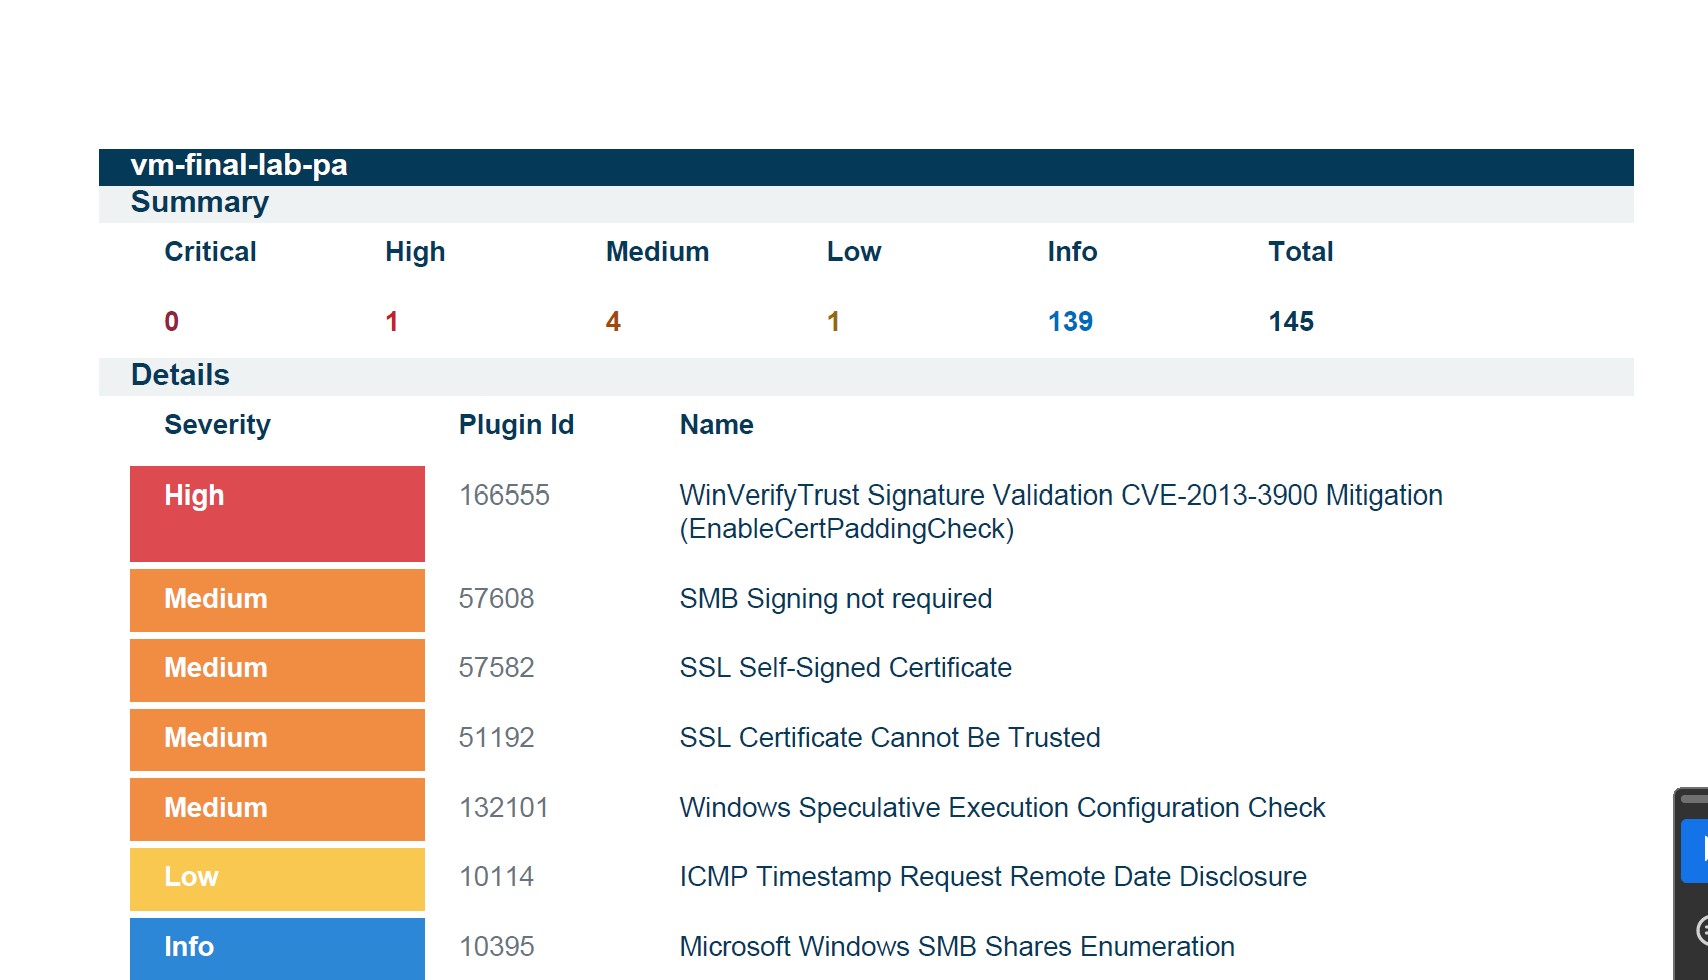 pkblanks/remediating-cve-2013-3900-enablecertpaddingcheck-
Step-by-step remediation report for CVE-2013-3900 on Windows Server 2019 Azure VM, using Tenable/Nessus credentialed scans and registry hardening to…
 mondoohq/installer
Linux, macOS and Windows Install scripts for cnquery & cnspec
 iknowjason/purplecloud
A little tool to play with Azure Identity - Azure and Entra ID lab creation tool. Blog: https://medium.com/@iknowjason/sentinel-for-purple-teaming-1…
 ptechamanja/cve-2025-9074-docker-desktop-container-escape
Proof of concept exploit for CVE-2025-9074 - Unauthenticated Docker Engine API container escape affecting Docker Desktop < 4.44.3 on Windows and…
 pucagit/cve-2025-9074
PoC exploit for CVE-2025-9074 demonstrating a full Docker Desktop container escape on Windows and macOS via an unauthenticated internal Docker Engine…
 cloudpassage/mangy-beast
CloudPassage Halo policy for detecting vulnerability to CVE-2014-3566 (AKA POODLE)