

grove
 hashicorp-forge/grove
A Software as a Service (SaaS) log collection framework.
api-securitycloud-securitydefensive-tools+3
186
hashicorp-forge/groveA Software as a Service (SaaS) log collection framework.
 kstenerud/yoloai
Your agent is a security risk, so treat it like one. yoloAI does AI agent sandboxing right.
 h4wkst3r/adokit
Modular attack toolkit exploiting Azure DevOps REST API for reconnaissance, privilege escalation, and persistence using stolen cookies or PATs.
 wiz-sec-public/cloud-middleware-dataset
Curated dataset of cloud middleware agents installed by AWS, Azure, and GCP, documenting past vulnerabilities, privileges, and attack-surface risks…
 tenable/cnappgoat
CNAPPgoat is an open source project designed to modularly provision vulnerable-by-design components in cloud environments.
 megamansec/gixy-next
Gixy-Next: NGINX Configuration Security Scanner & Performance Checker
 owasp/iot-security-verification-standard-isvs
OWASP IoT Security Verification Standard (ISVS)
 luemmelsec/apex
Azure Post Exploitation Framework
 owasp/openshield
Open source CSPM for Azure - scan for misconfigurations and quantum-unsafe cryptography, map findings to CIS/NIST/ISO27001/SOC2, and fix them with…
 synacktiv/mindmaps
Azure mindmap for penetration tests
 owasp/serverless-top-10-project
OWASP Serverless Top 10
 treebuilder/aad-sso-enum-brute-spray
POC of SecureWorks' recent Azure Active Directory password brute-forcing vuln
 v4bel/zapscape
PoC exploit for CVE-2026-64561, a KVM/x86 shadow MMU use-after-free enabling guest-to-host escape with kernel root code execution on the host.
 specterops/githound
BloodHound OpenGraph collector for GitHub that maps organization structure, permissions, and cross-cloud attack paths into a navigable graph for…
 cybermaggedon/cyberprobe
Capturing, analysing and responding to cyber attacks
 op7ic/blueteam.lab
Blue Team detection lab created with Terraform and Ansible in Azure.
 cyberark/skywrapper
SkyWrapper helps to discover suspicious creation forms and uses of temporary tokens in AWS
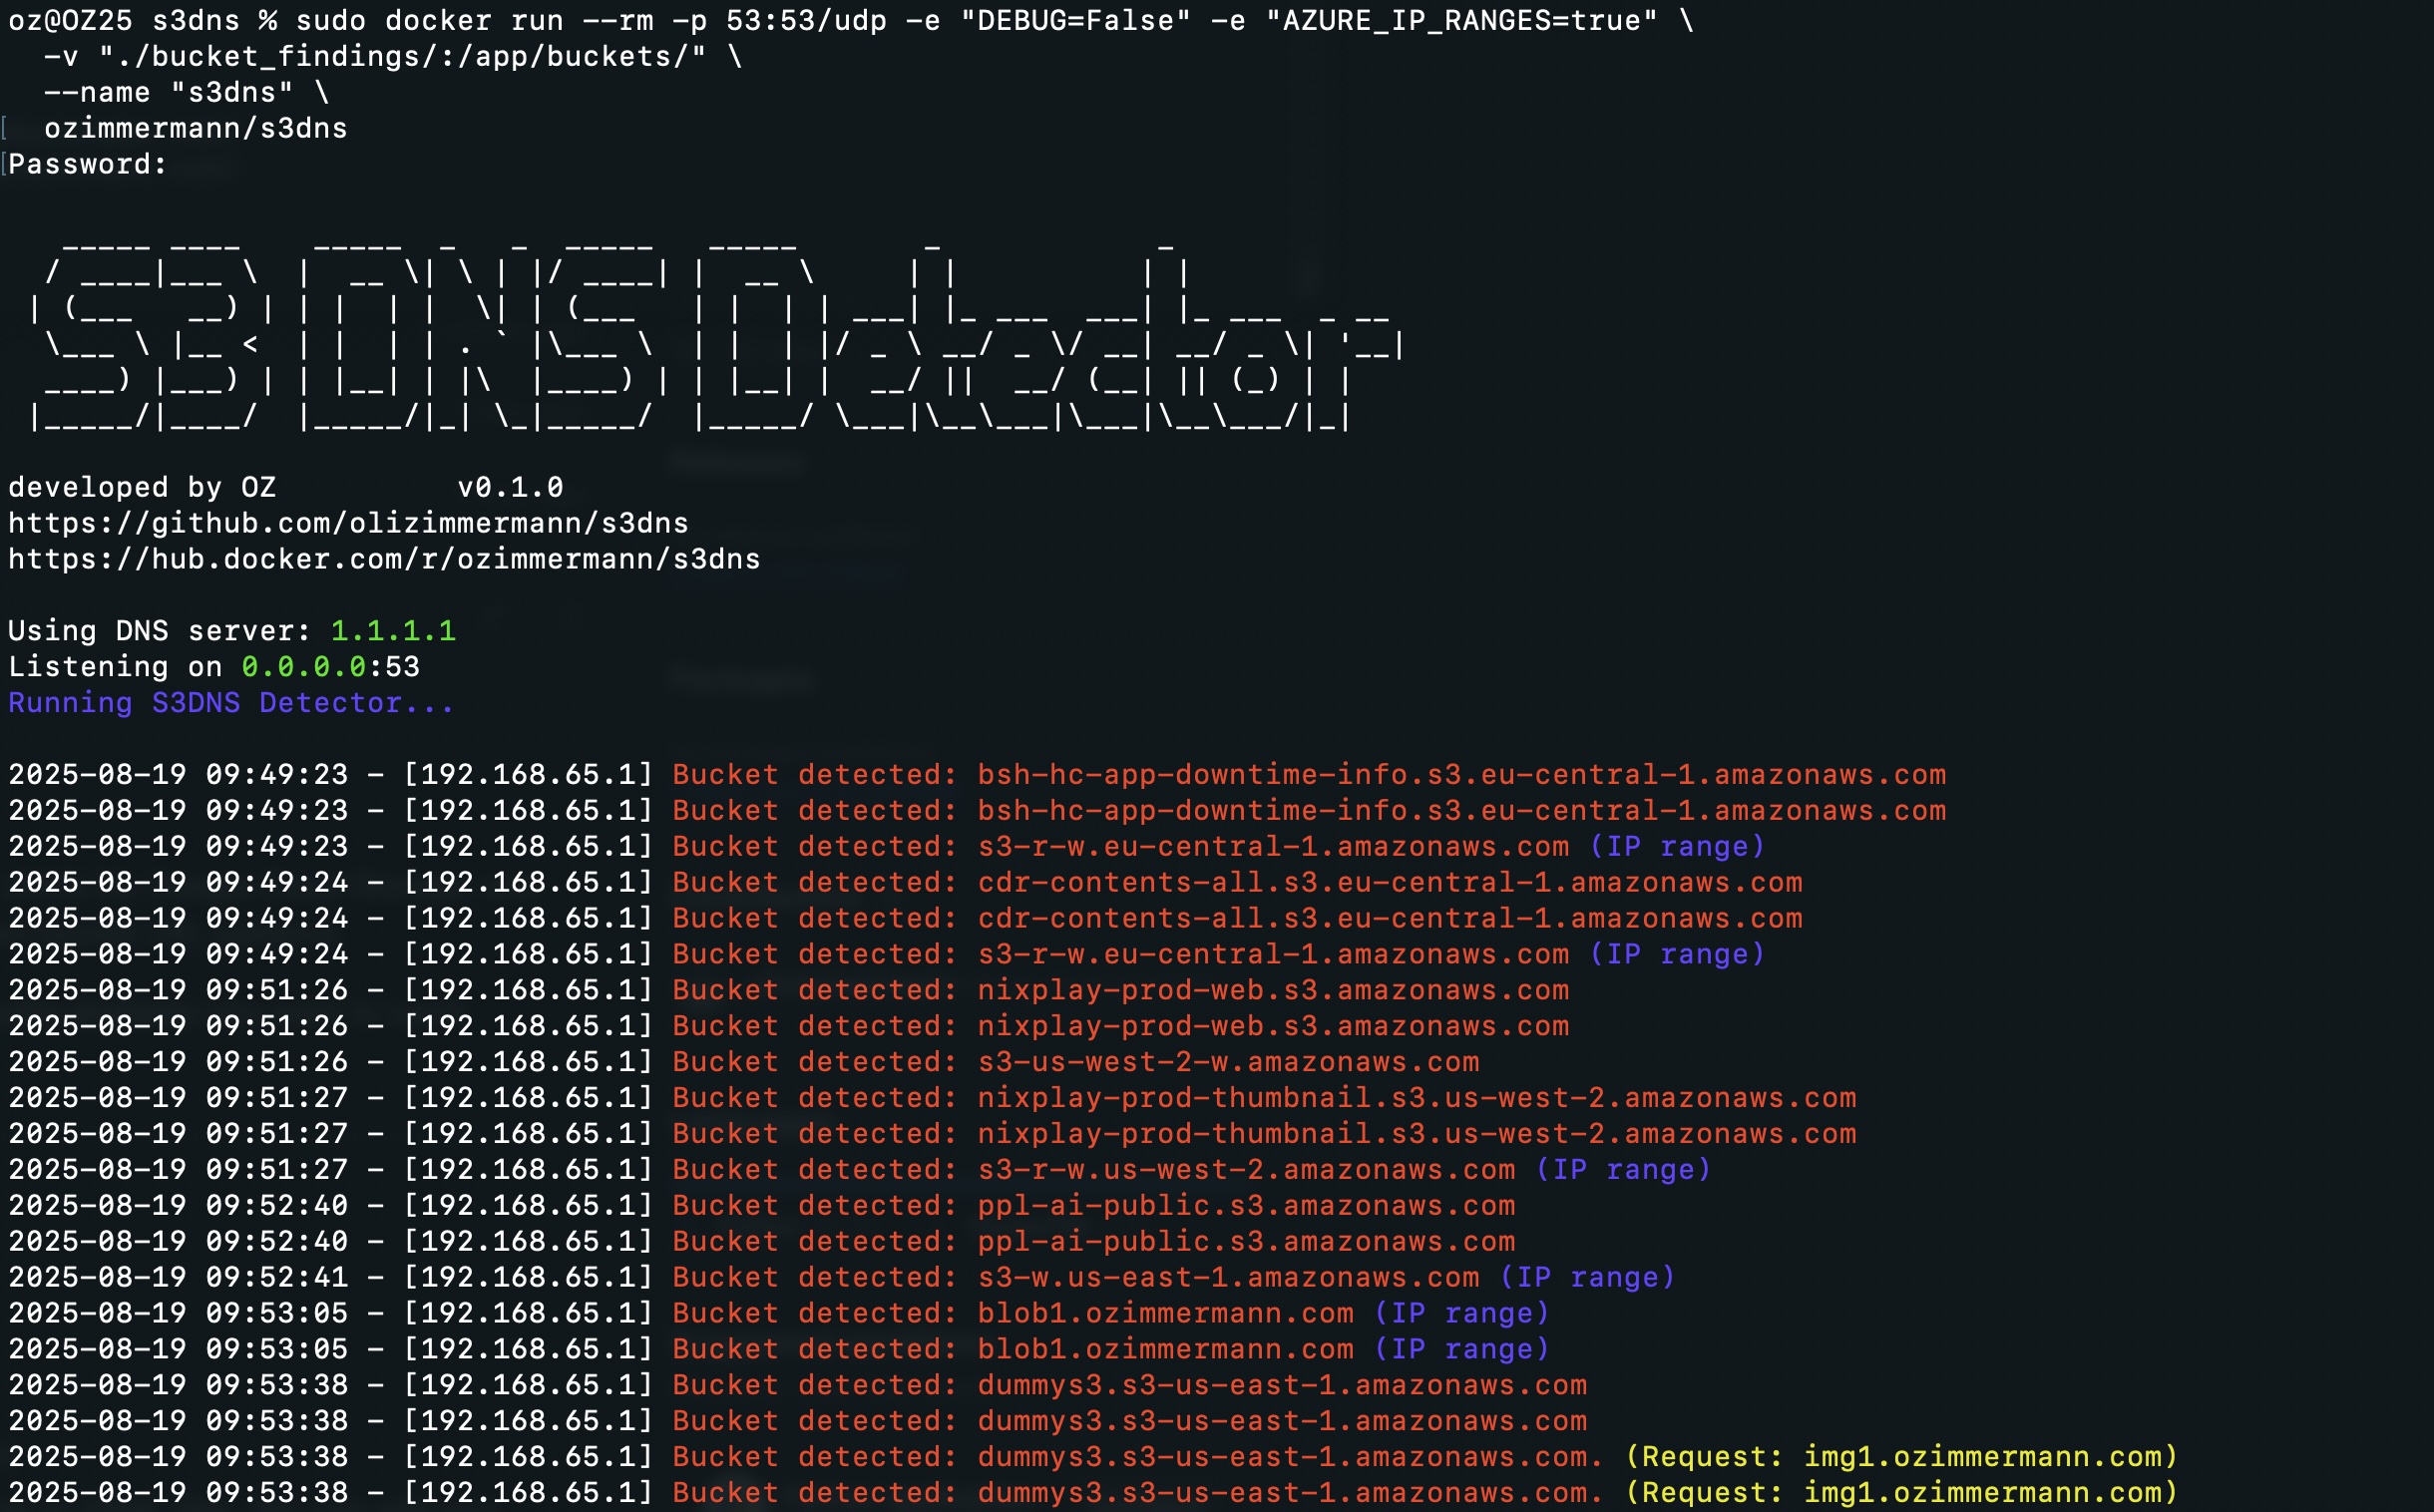 olizimmermann/s3dns
Passive DNS server that detects exposed cloud storage buckets (AWS S3, GCP, Azure) by resolving DNS requests, tracing CNAME chains, and flagging…