
pacu
 rhinosecuritylabs/pacu
The AWS exploitation framework, designed for testing the security of Amazon Web Services environments.
cloud-infrastructure-securitycloud-securitydata-exfiltration+7
5.3k
rhinosecuritylabs/pacuThe AWS exploitation framework, designed for testing the security of Amazon Web Services environments.
 pry0cc/axiom
The dynamic infrastructure framework for everybody! Distribute the workload of many different scanning tools with ease, including nmap, ffuf,…
 dirkjanm/roadtools
A collection of Azure AD/Entra tools for offensive and defensive security purposes
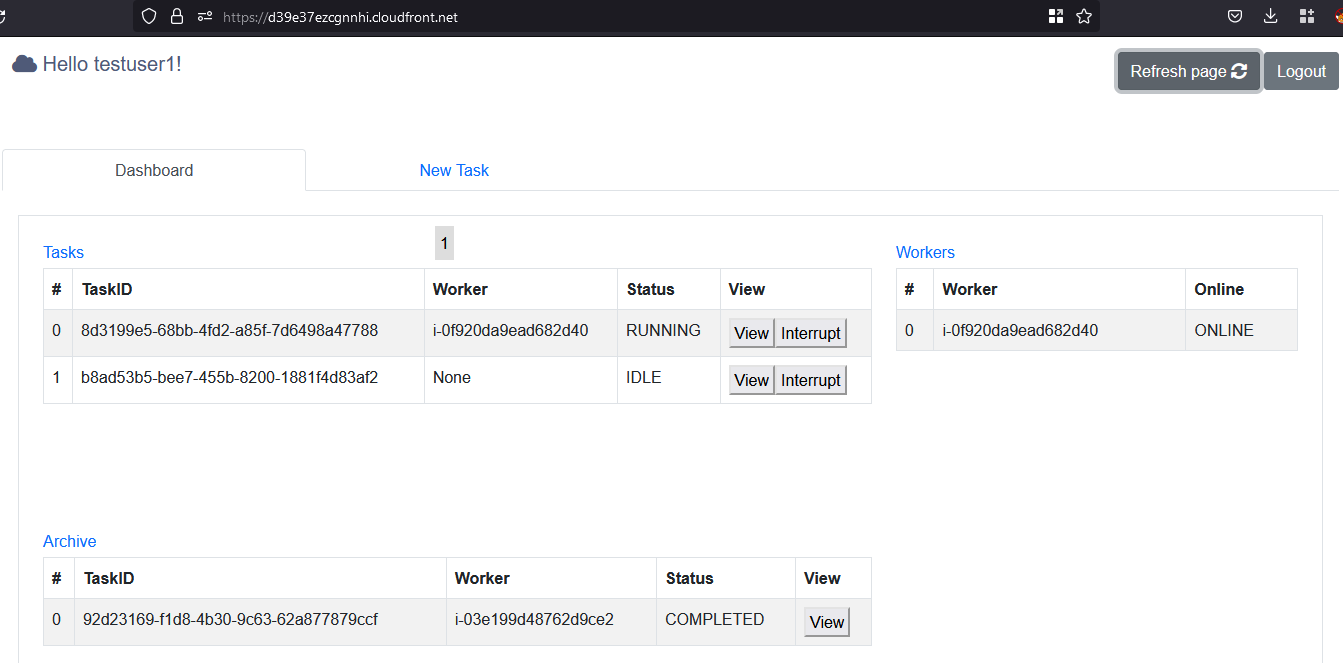 nccgroup/cowcloud
Serverless AWS solution for distributing recon and vulnerability scanning workloads. Submit tasks via web UI; EC2 workers execute custom Python…
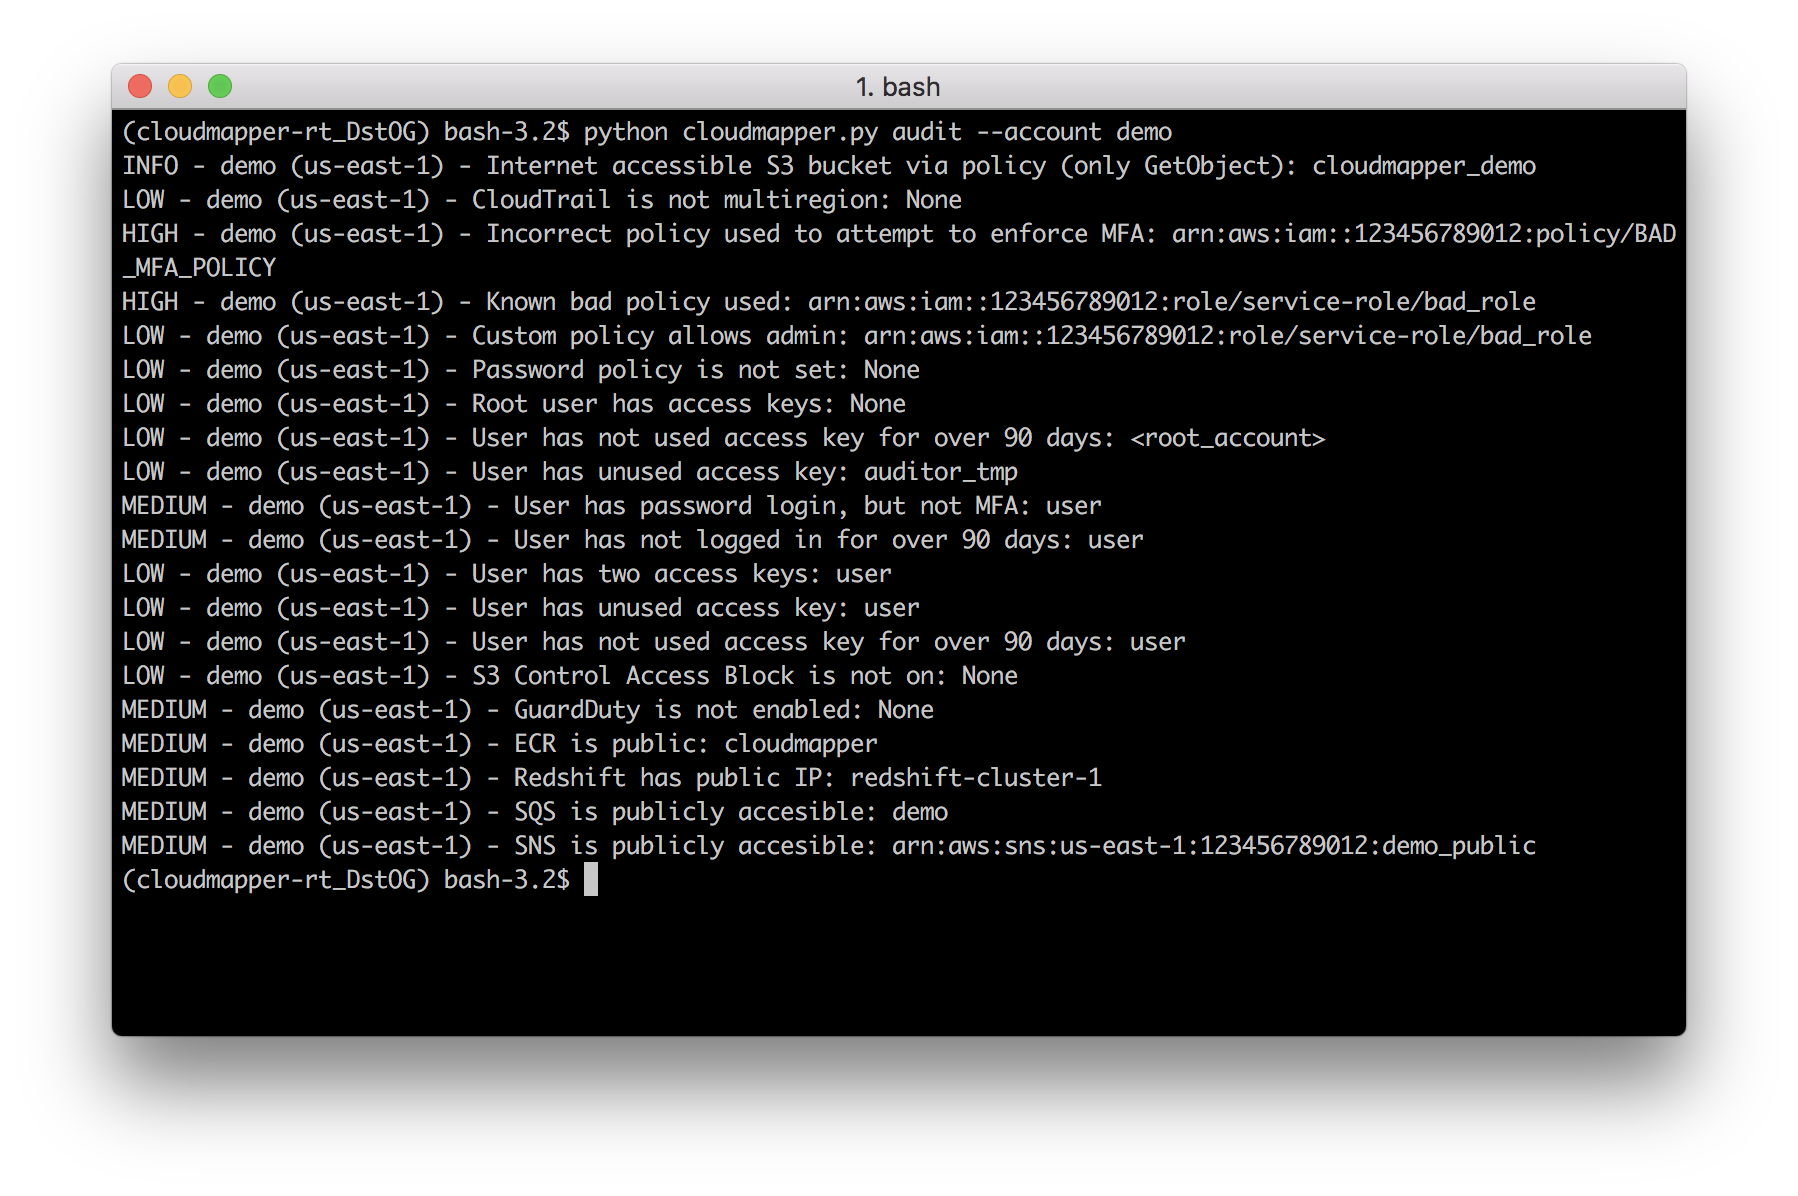 duo-labs/cloudmapper
CloudMapper helps you analyze your Amazon Web Services (AWS) environments.
 appsecco/spaces-finder
A tool to hunt for publicly accessible DigitalOcean Spaces
 kubeshark/kubeshark
eBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…
 hacktricks-wiki/hacktricks-cloud
Community-driven knowledge base for pentesting cloud environments and CI/CD pipelines: attack techniques, enumeration, privilege escalation, and…
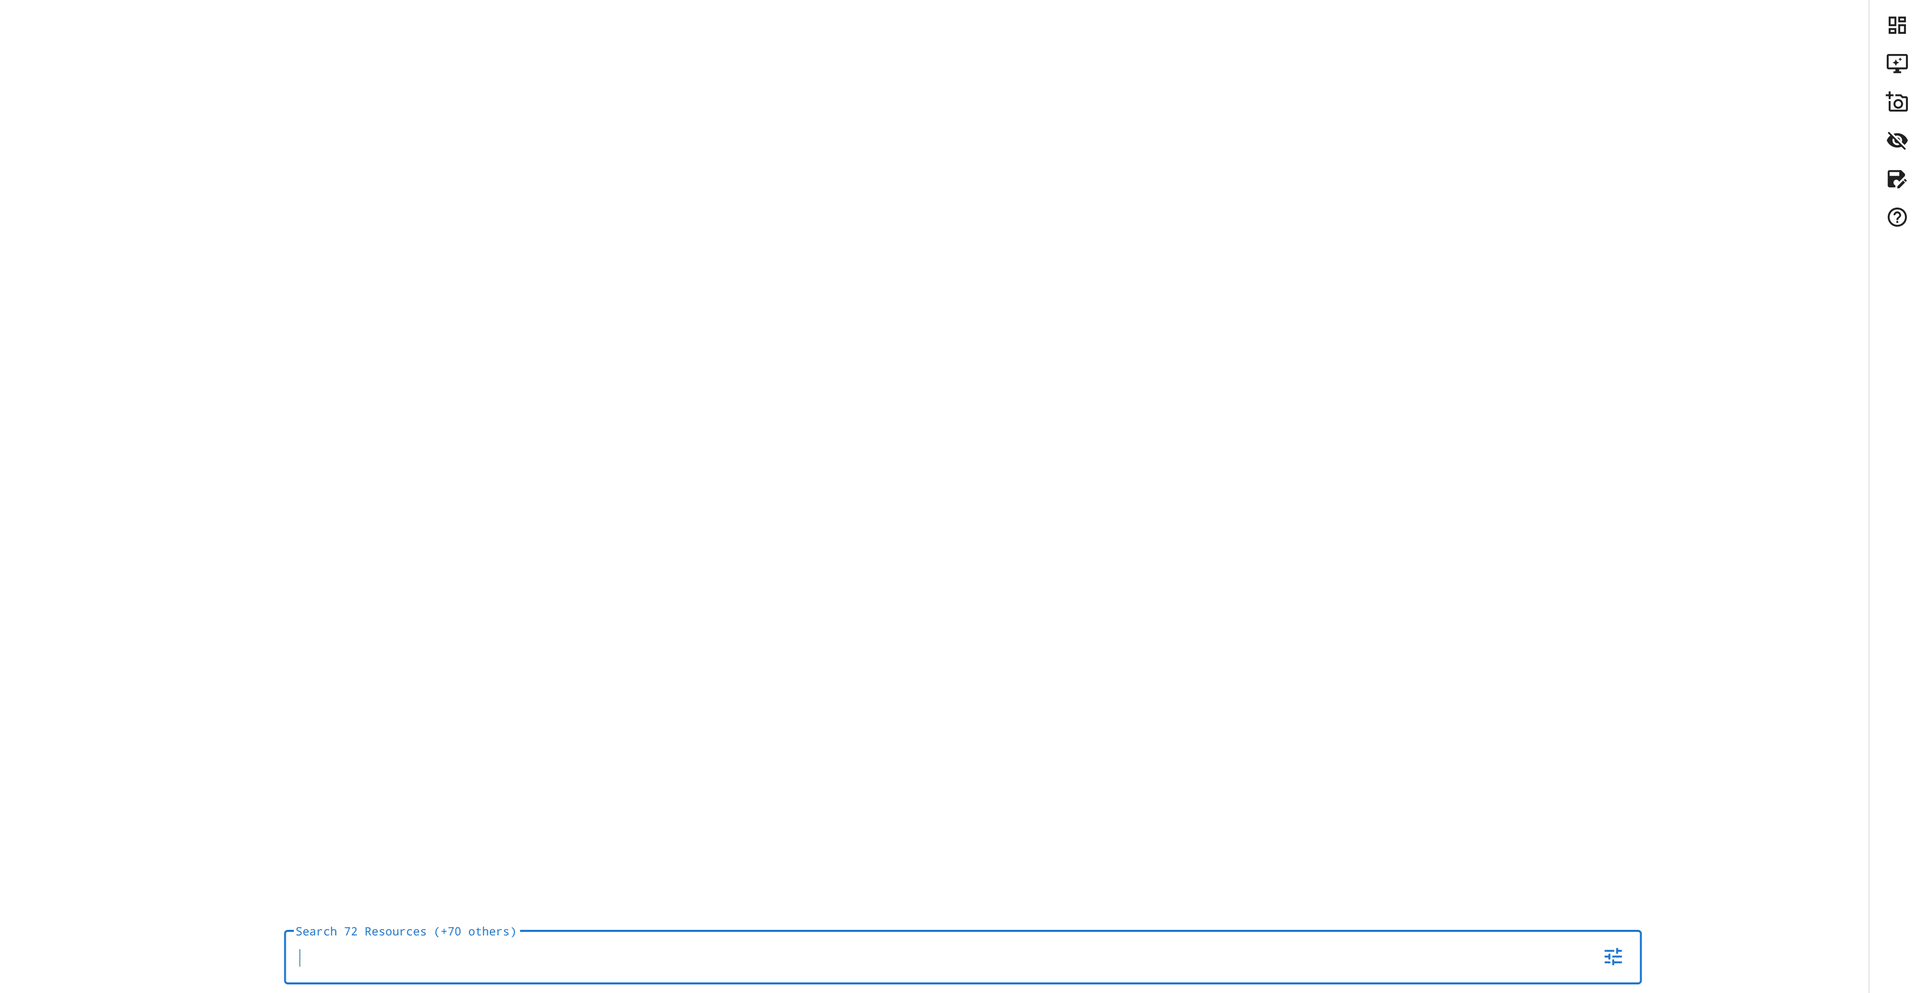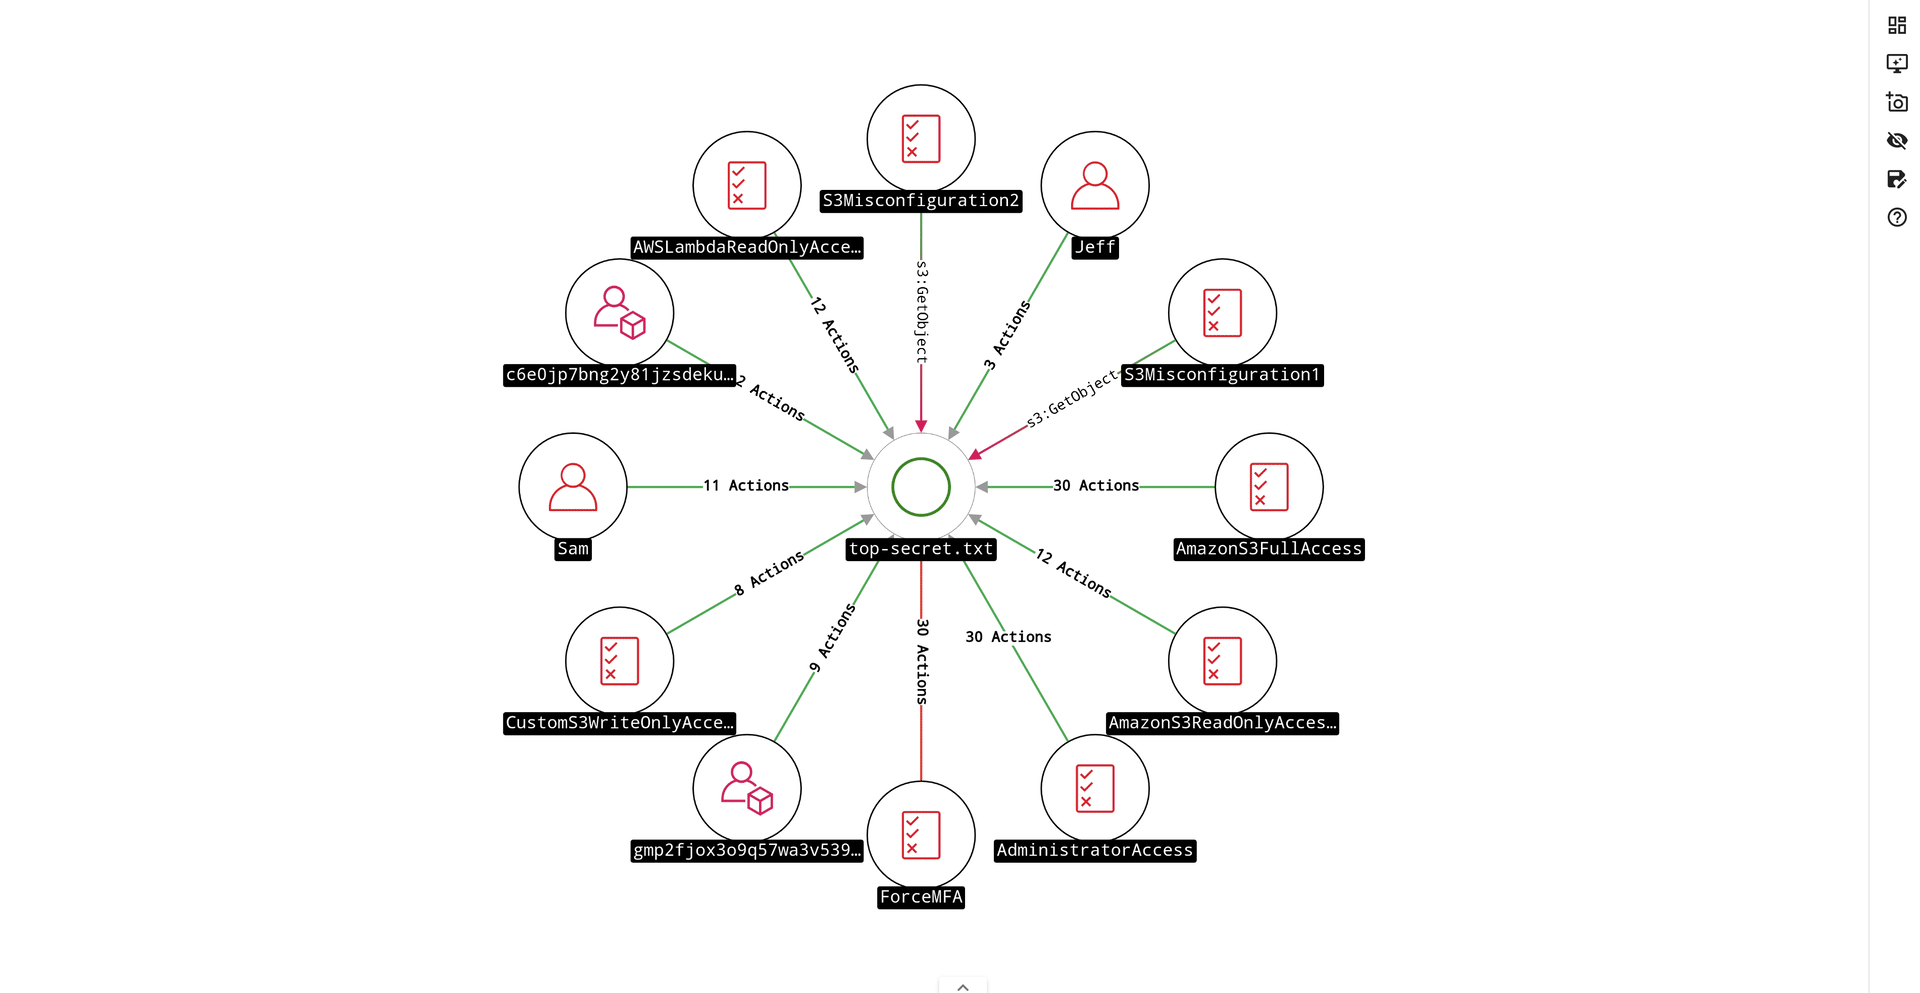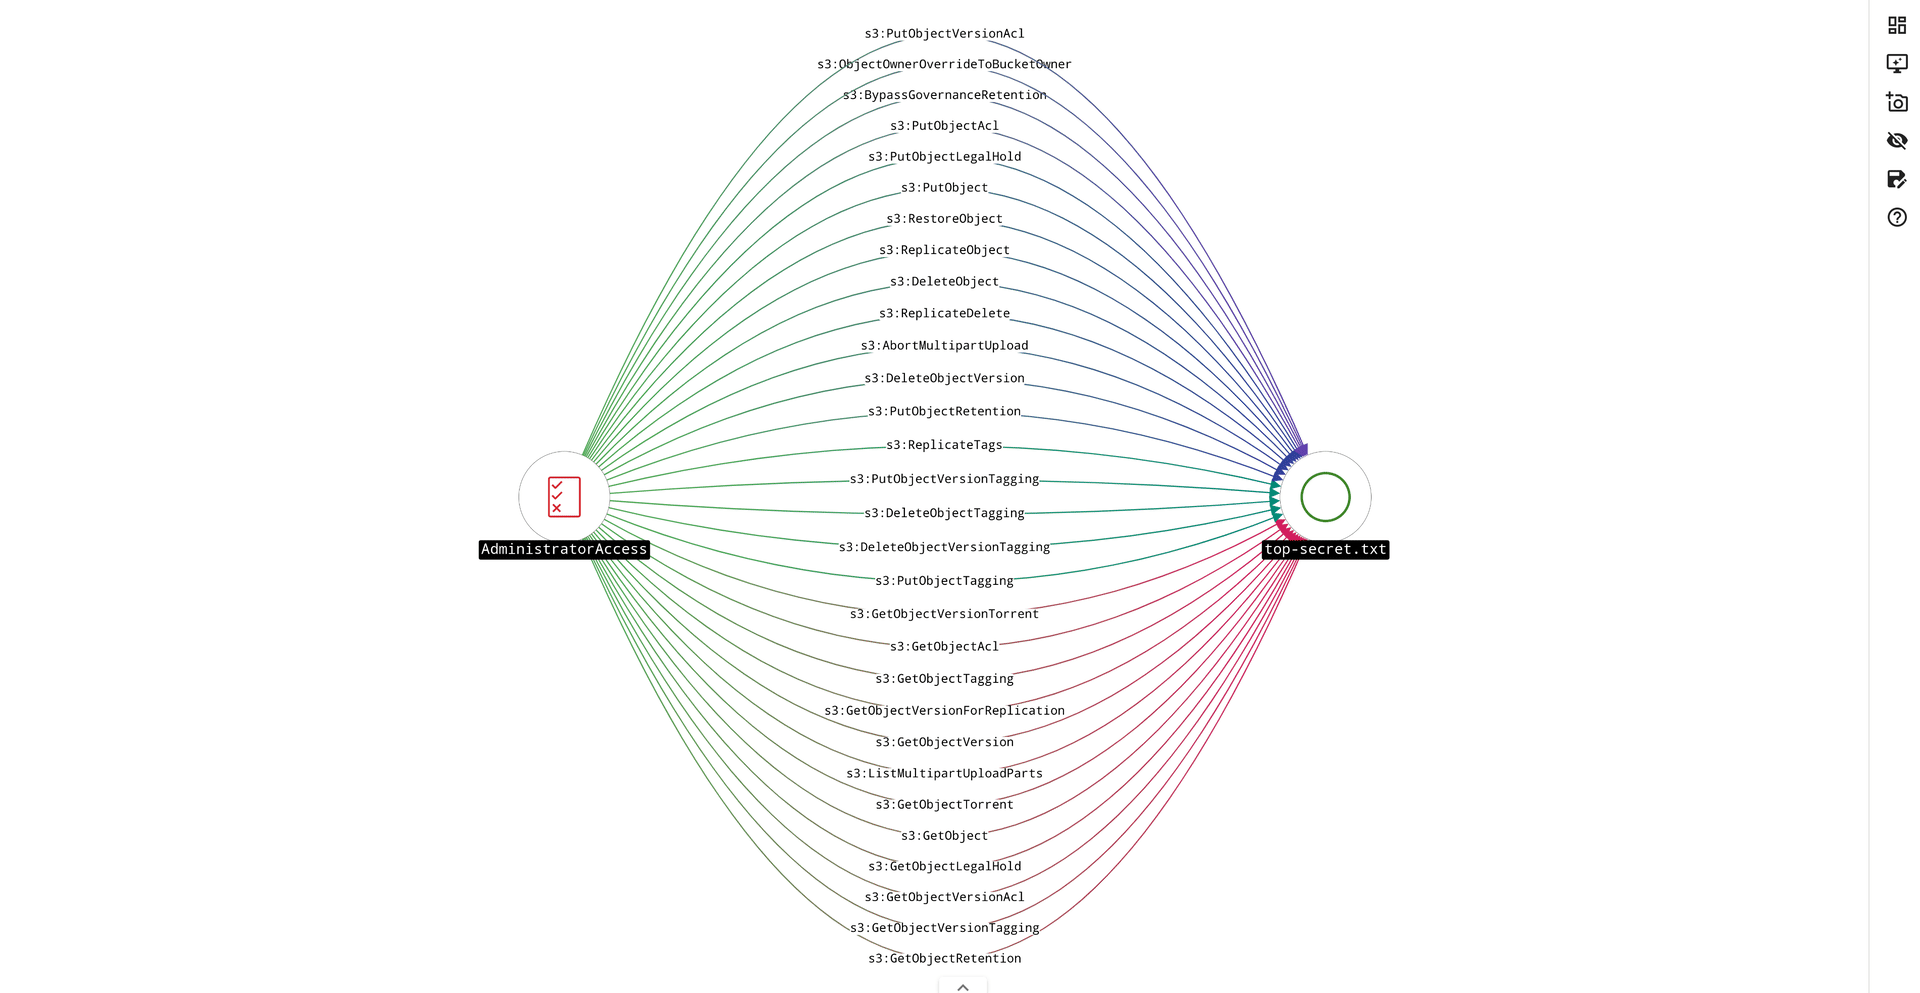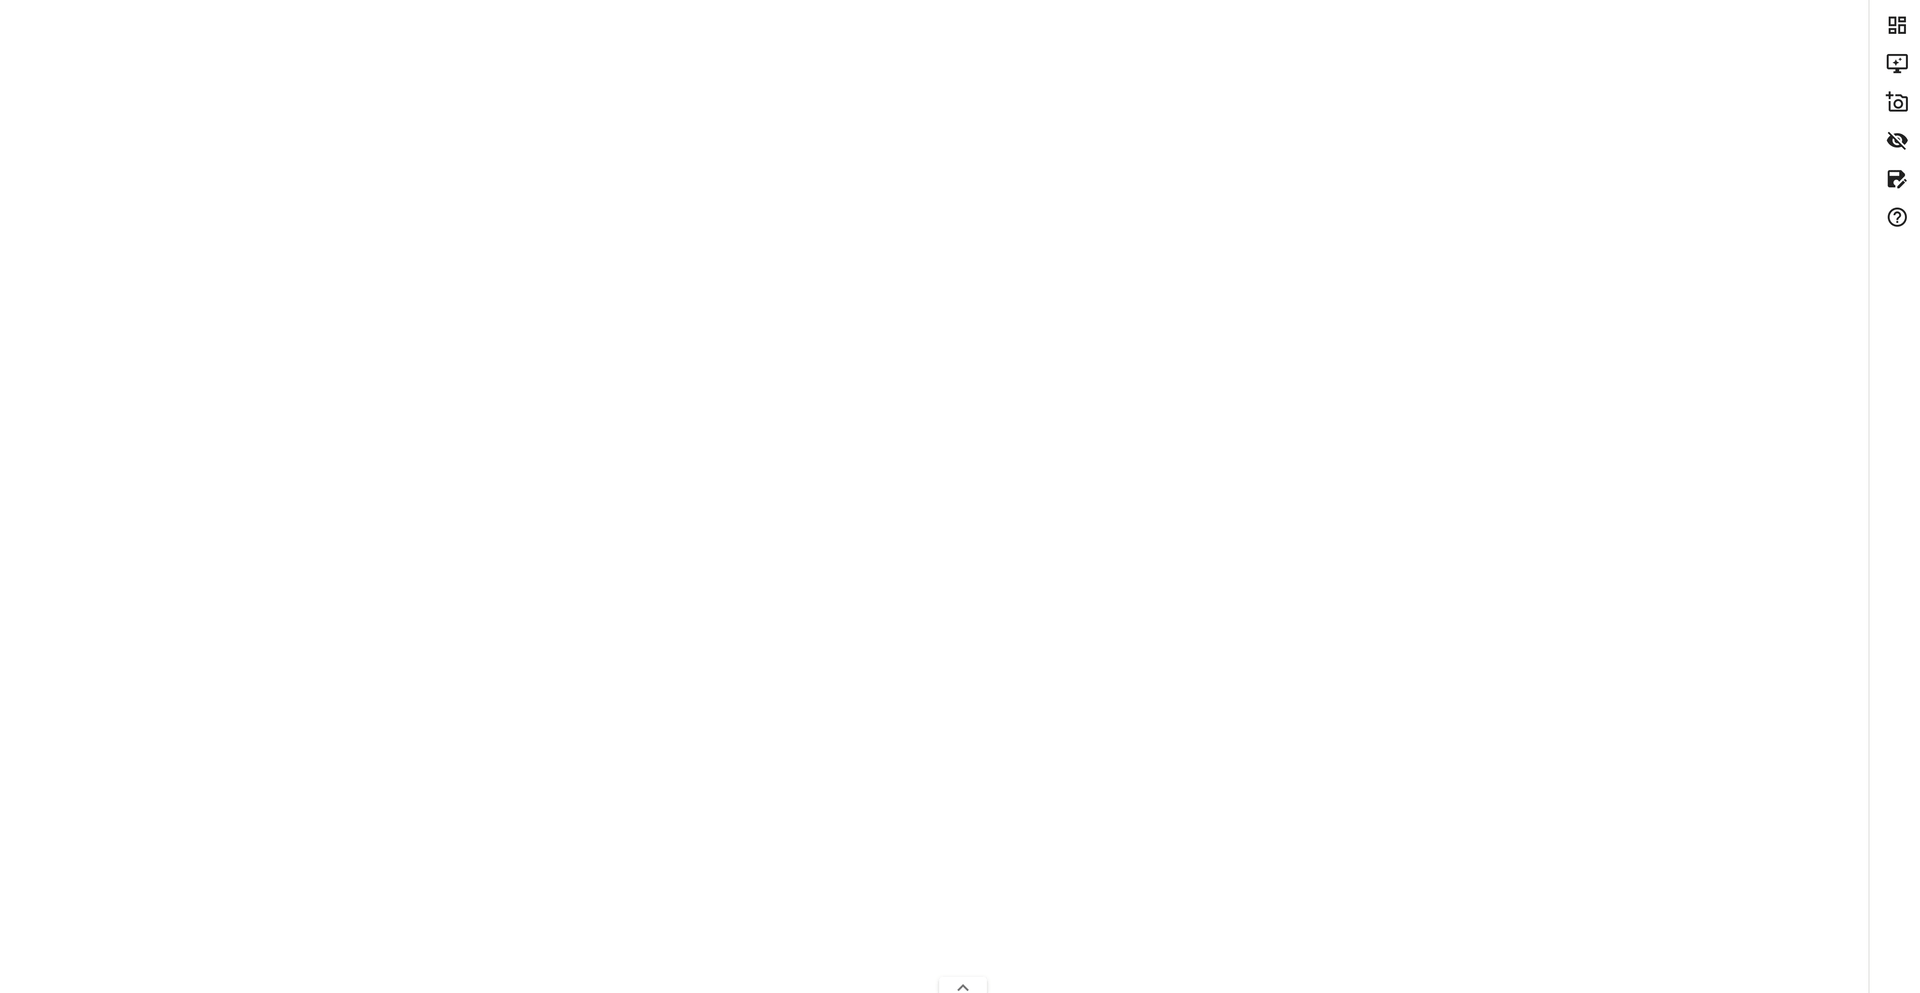 reverseclabs/awspx
A graph-based tool for visualizing effective access and resource relationships in AWS environments.
 azuread/azureadassessment
Tooling for assessing an Azure AD tenant state and configuration
 redhuntlabs/bucketloot
BucketLoot is an automated S3-compatible bucket inspector that can help users extract assets, flag secret exposures and even search for custom…
 expl0itabl3/check_mdi
Python script to enumerate valid Microsoft 365 domains, retrieve tenant name, and check for an MDI instance.
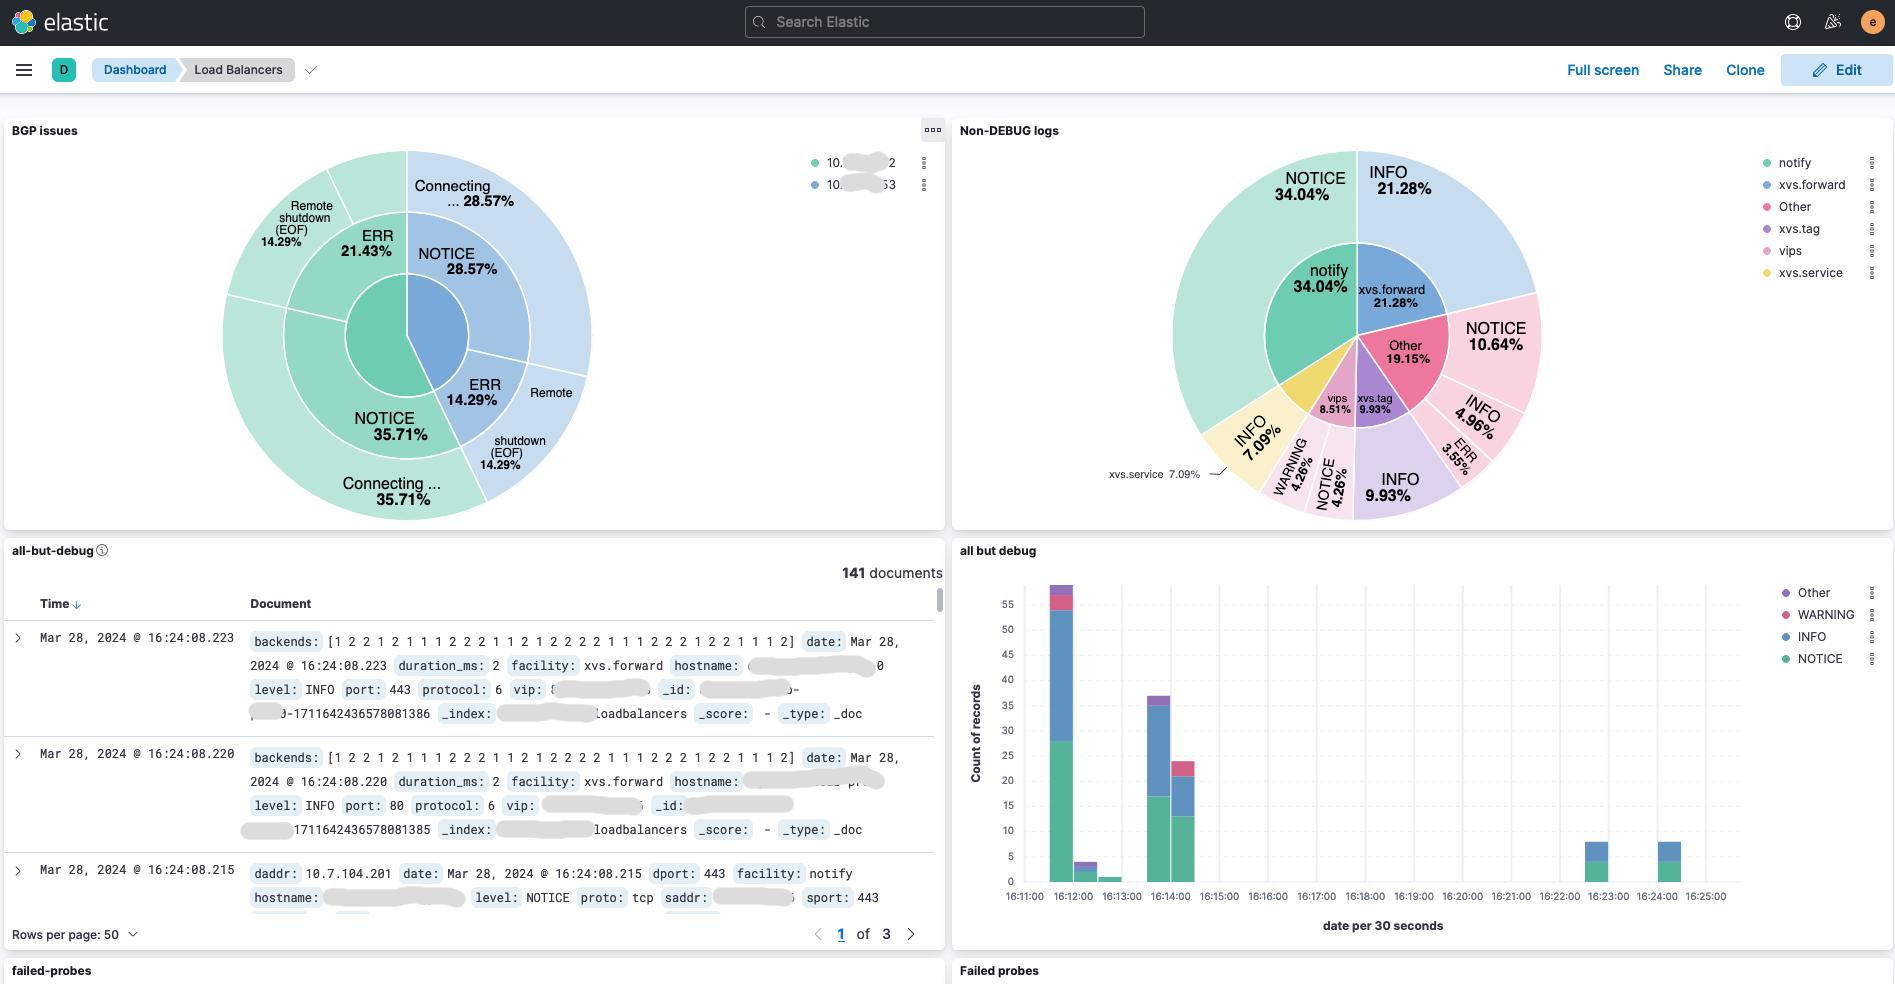 davidcoles/vc5
A horizontally scalable Direct Server Return layer 4 load balancer for Linux using XDP/eBPF
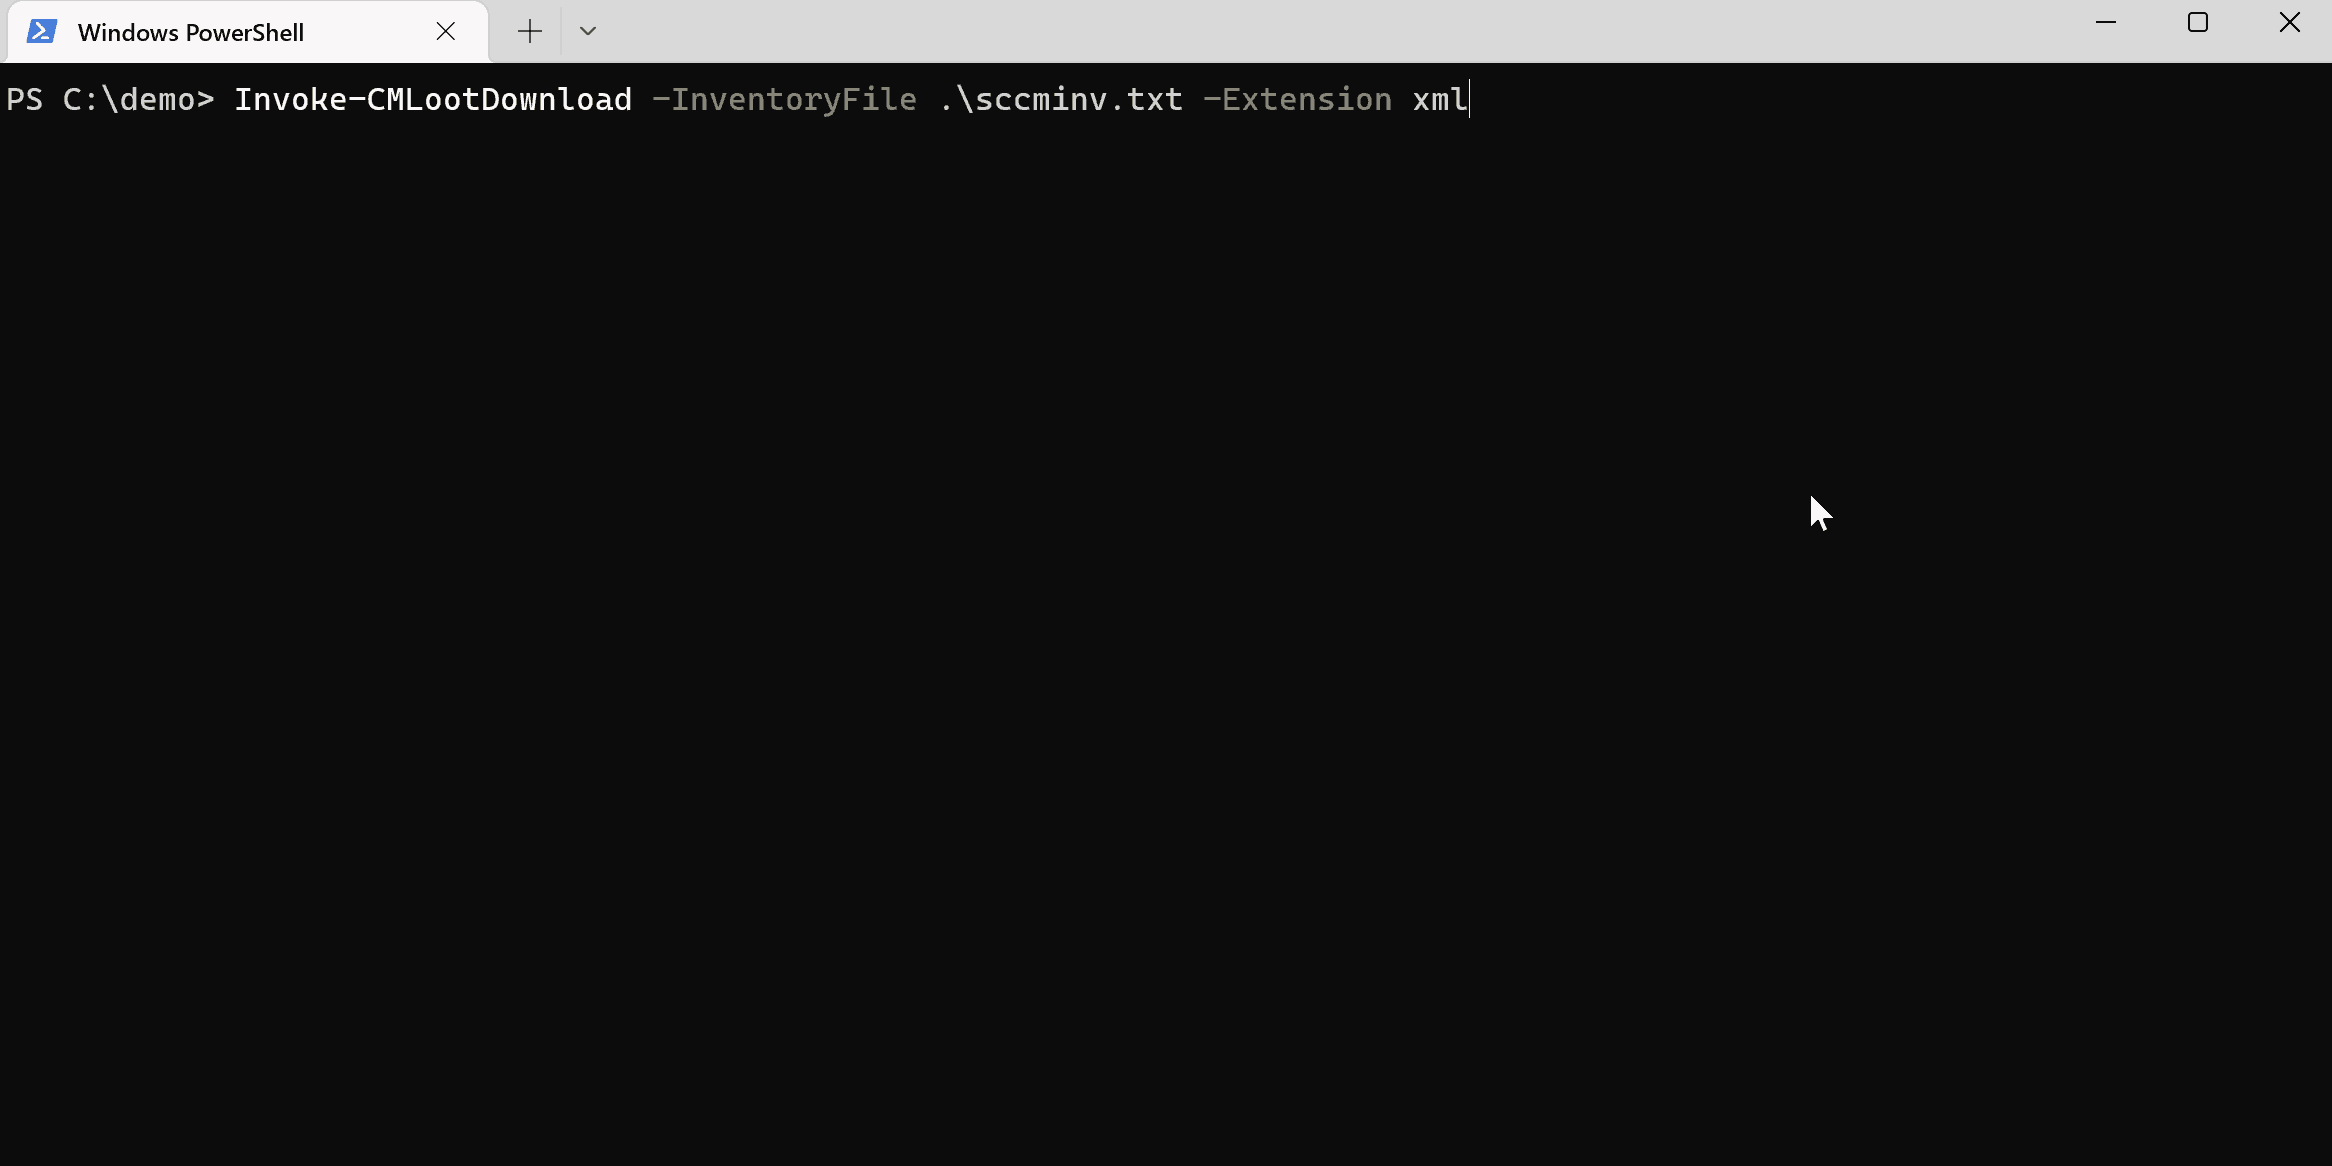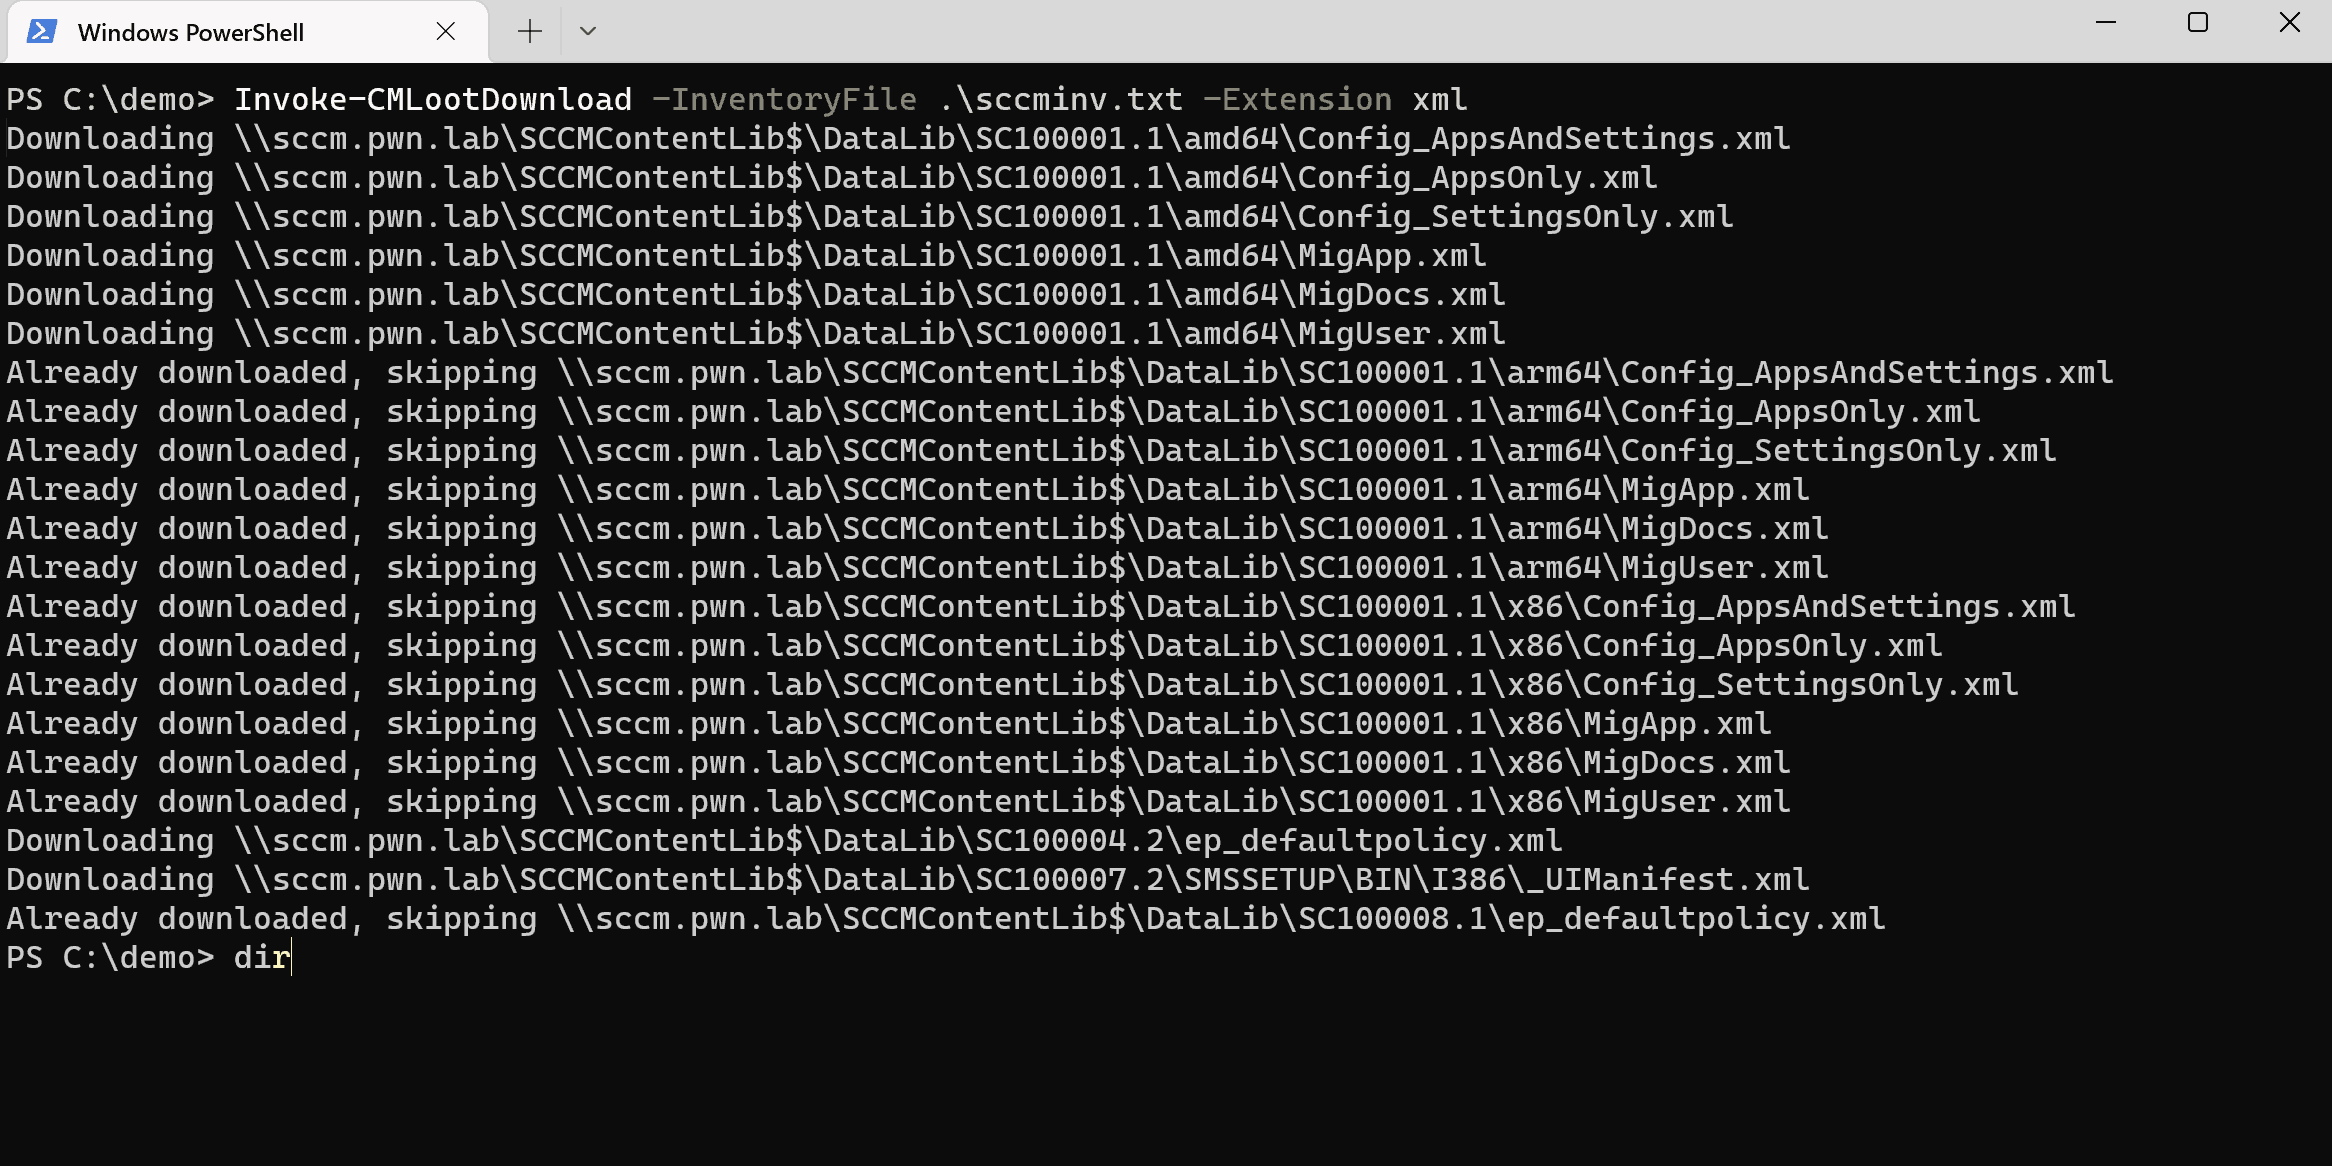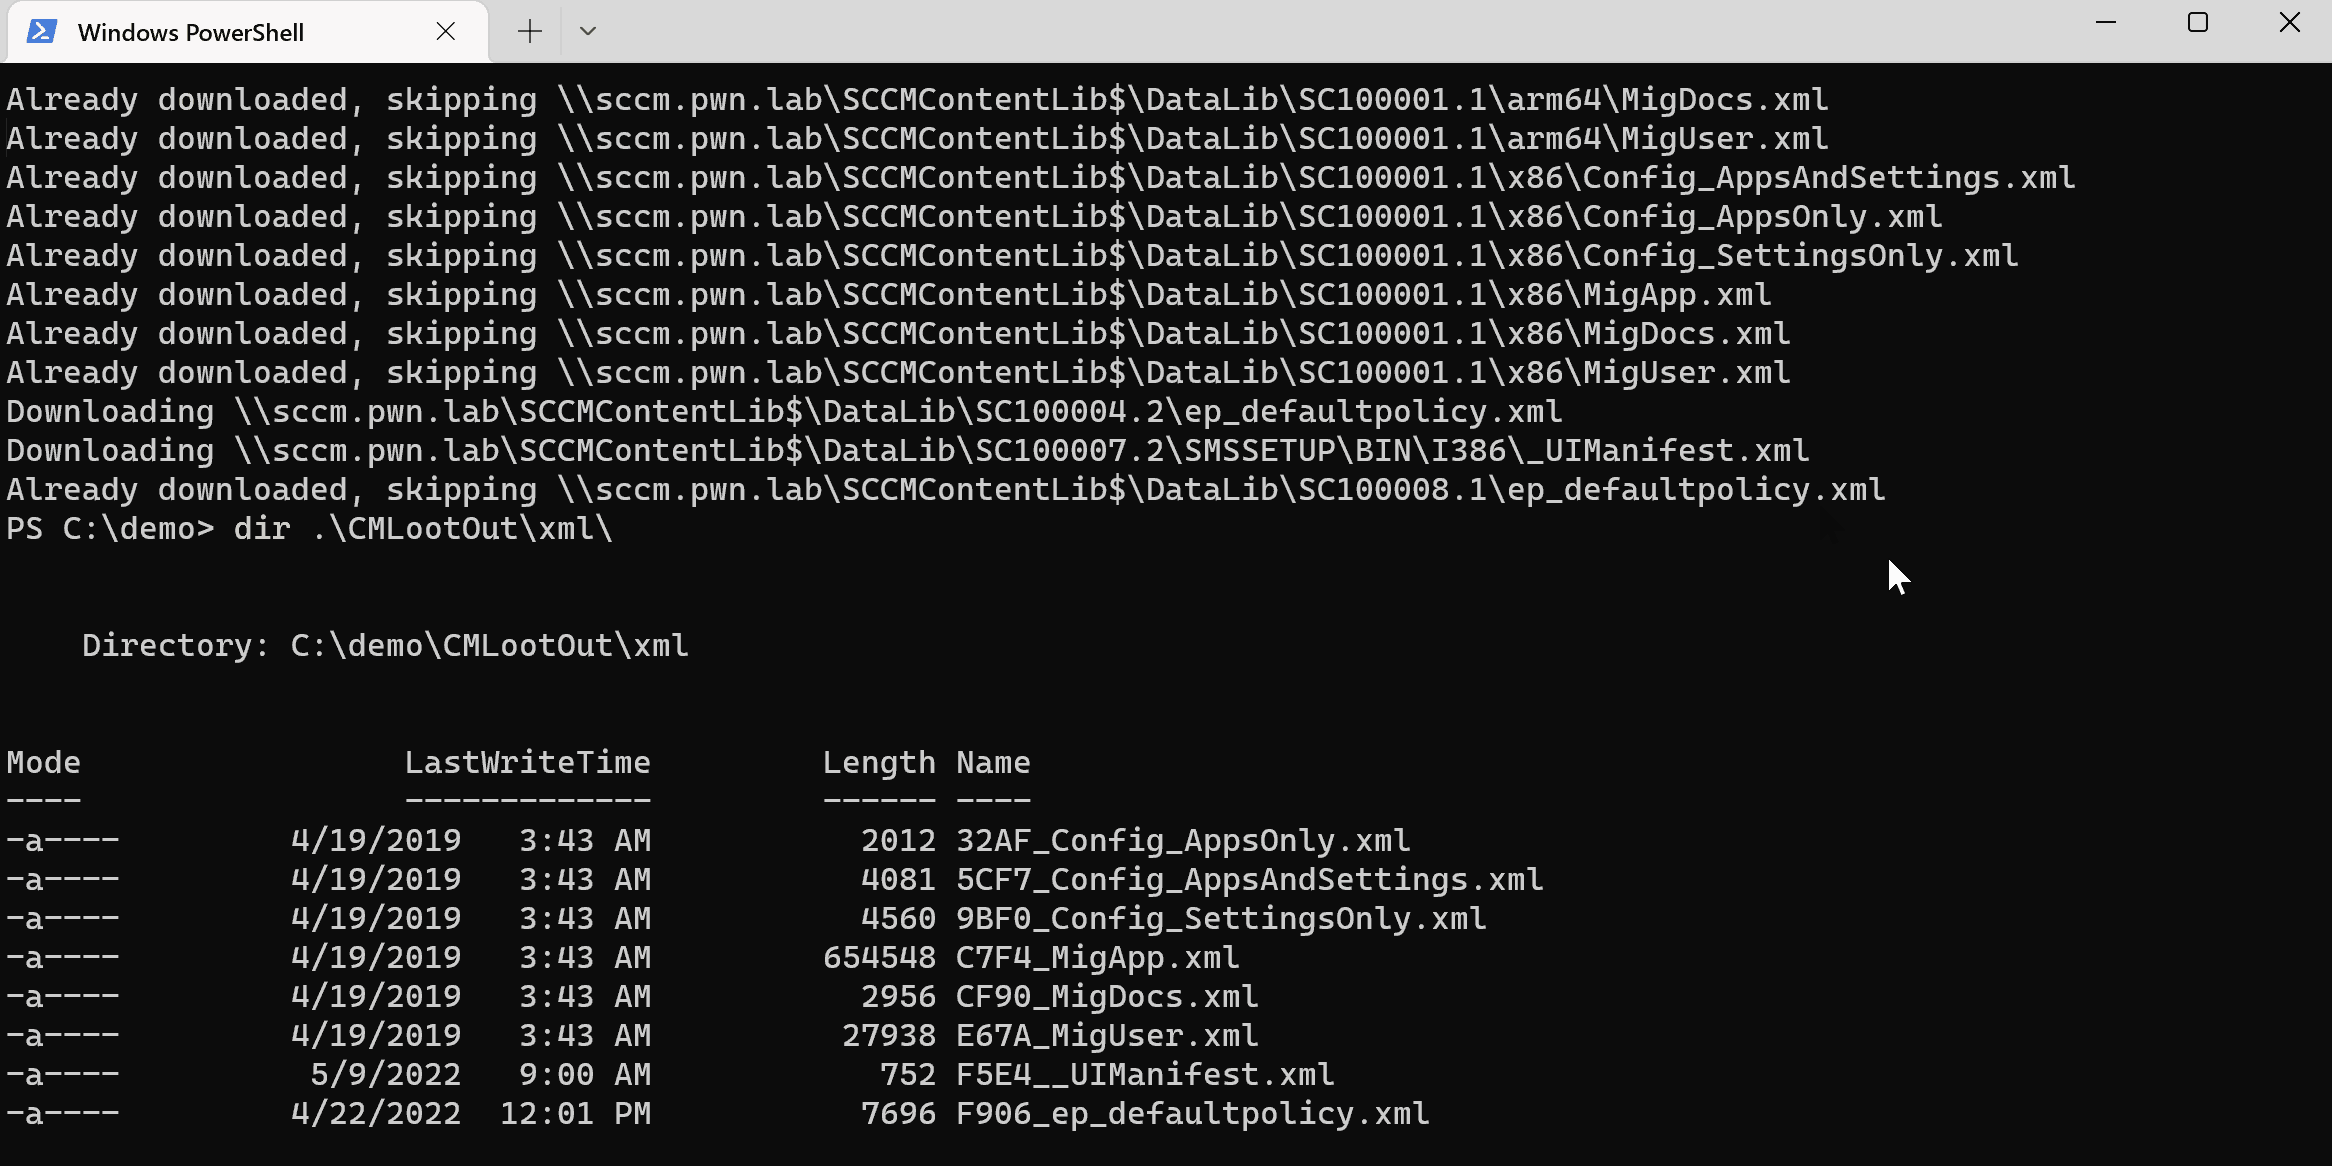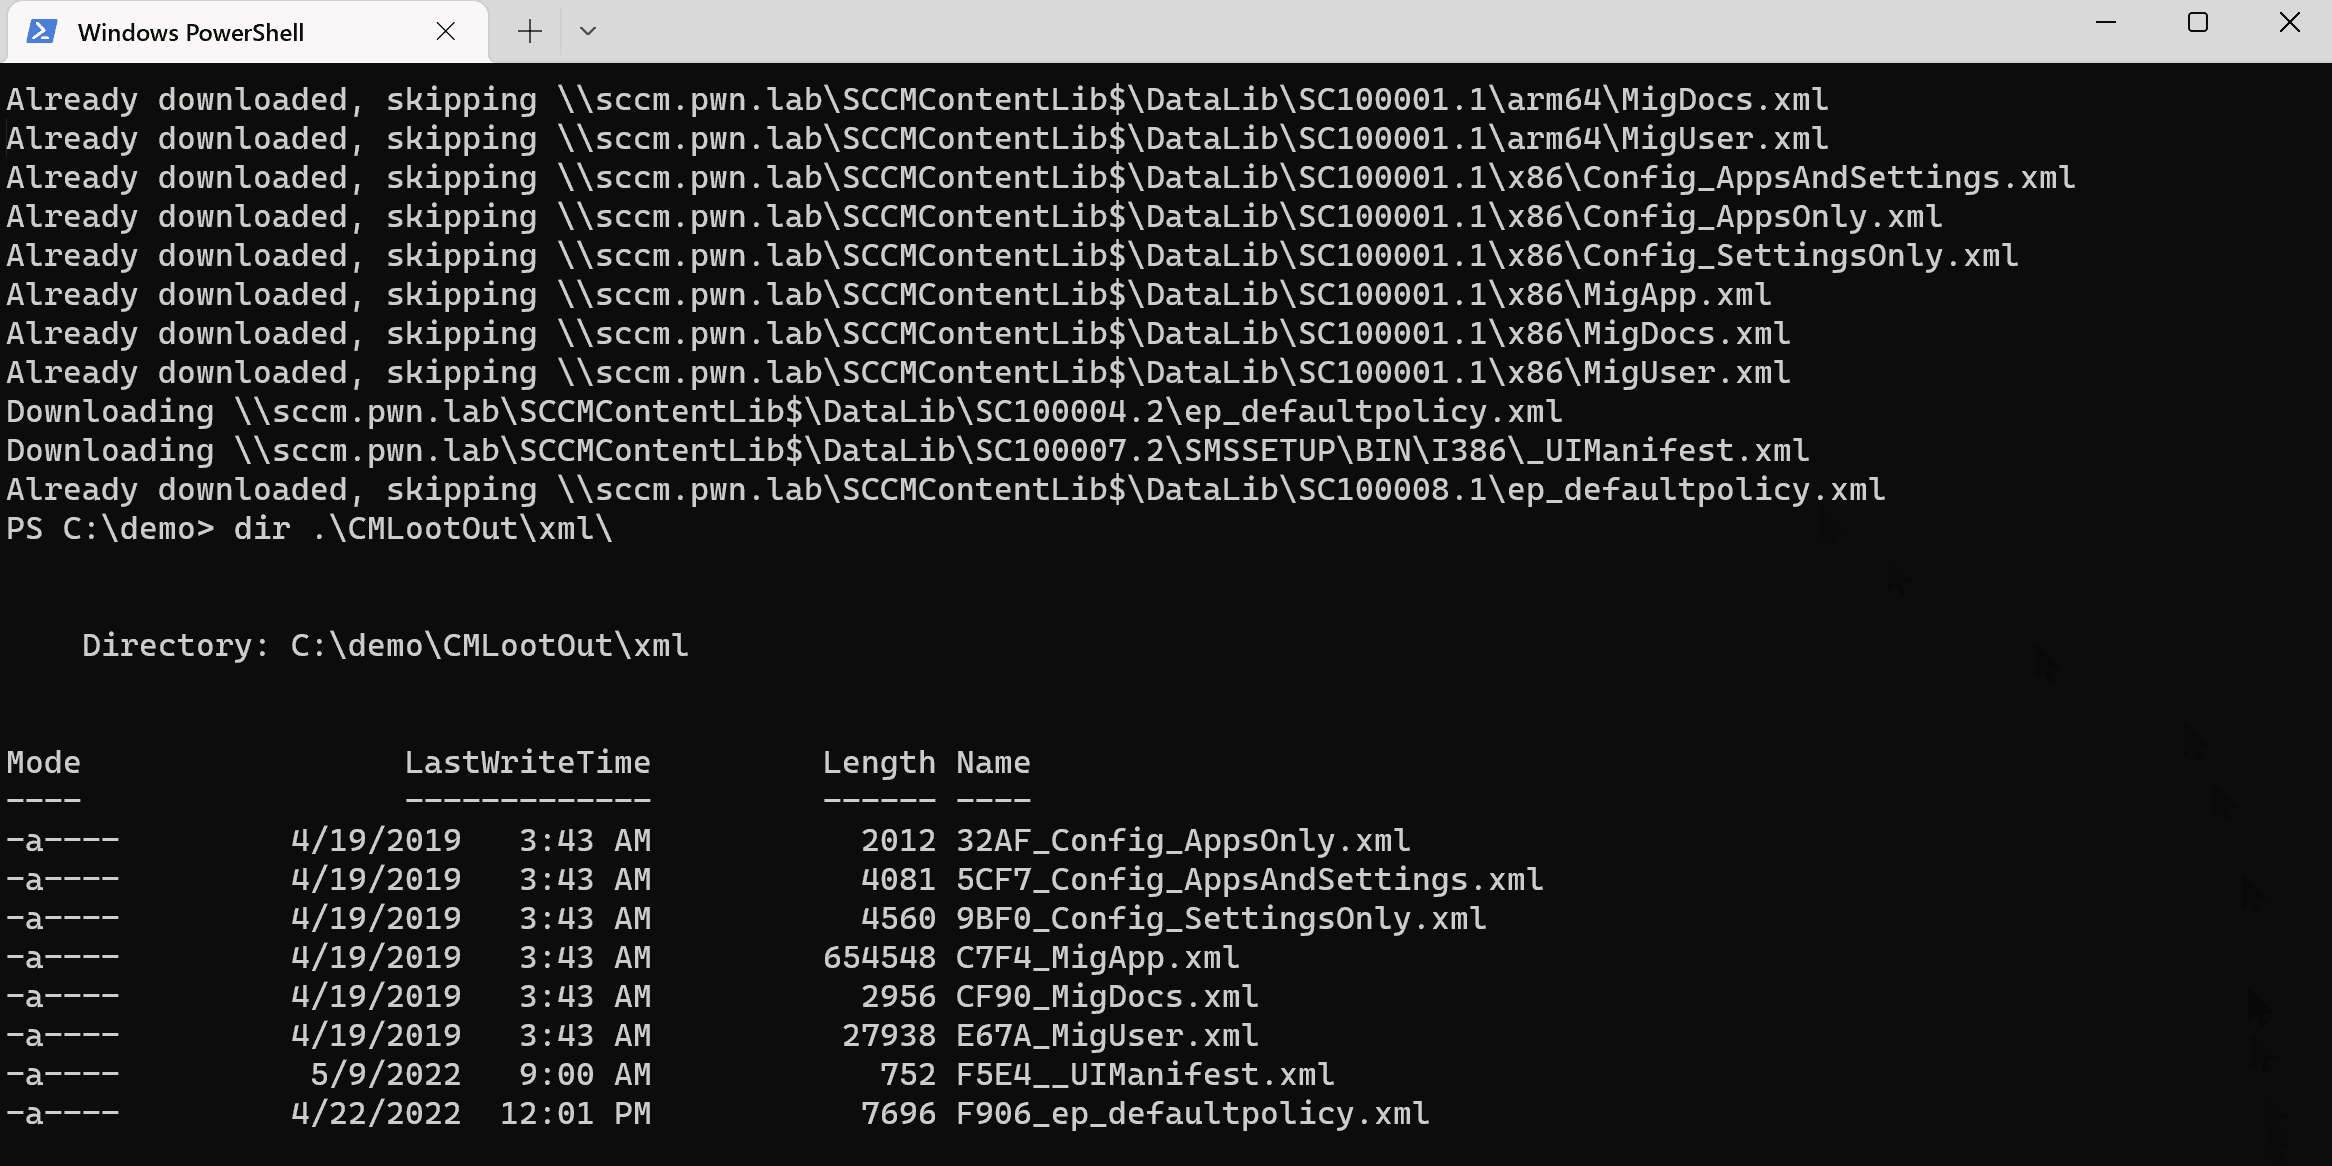 1njected/cmloot
Find interesting files stored on (System Center) Configuration Manager (SCCM/CM) SMB shares
 danthegoodman1/netfence
Like Envoy xDS, but for eBPF filters
 c0axx/canaryhunter
Canary Hunter aims to be a quick PowerShell script to check for Common Canaries in various formats generated for free on canarytokens.org
 0xbharath/slurp-old
A tool to enumerate S3 buckets manually or via certstream
 rootsecdev/secretsstalker
Read-only Entra ID app-credential assessment: enumerates Graph permissions, Azure RBAC, and reachable cloud data, then maps findings to…