
 reverseclabs/awspx
A graph-based tool for visualizing effective access and resource relationships in AWS environments.


auspex [ˈau̯s.pɛks] noun: An augur of ancient Rome, especially one who interpreted omens derived from the observation of birds.


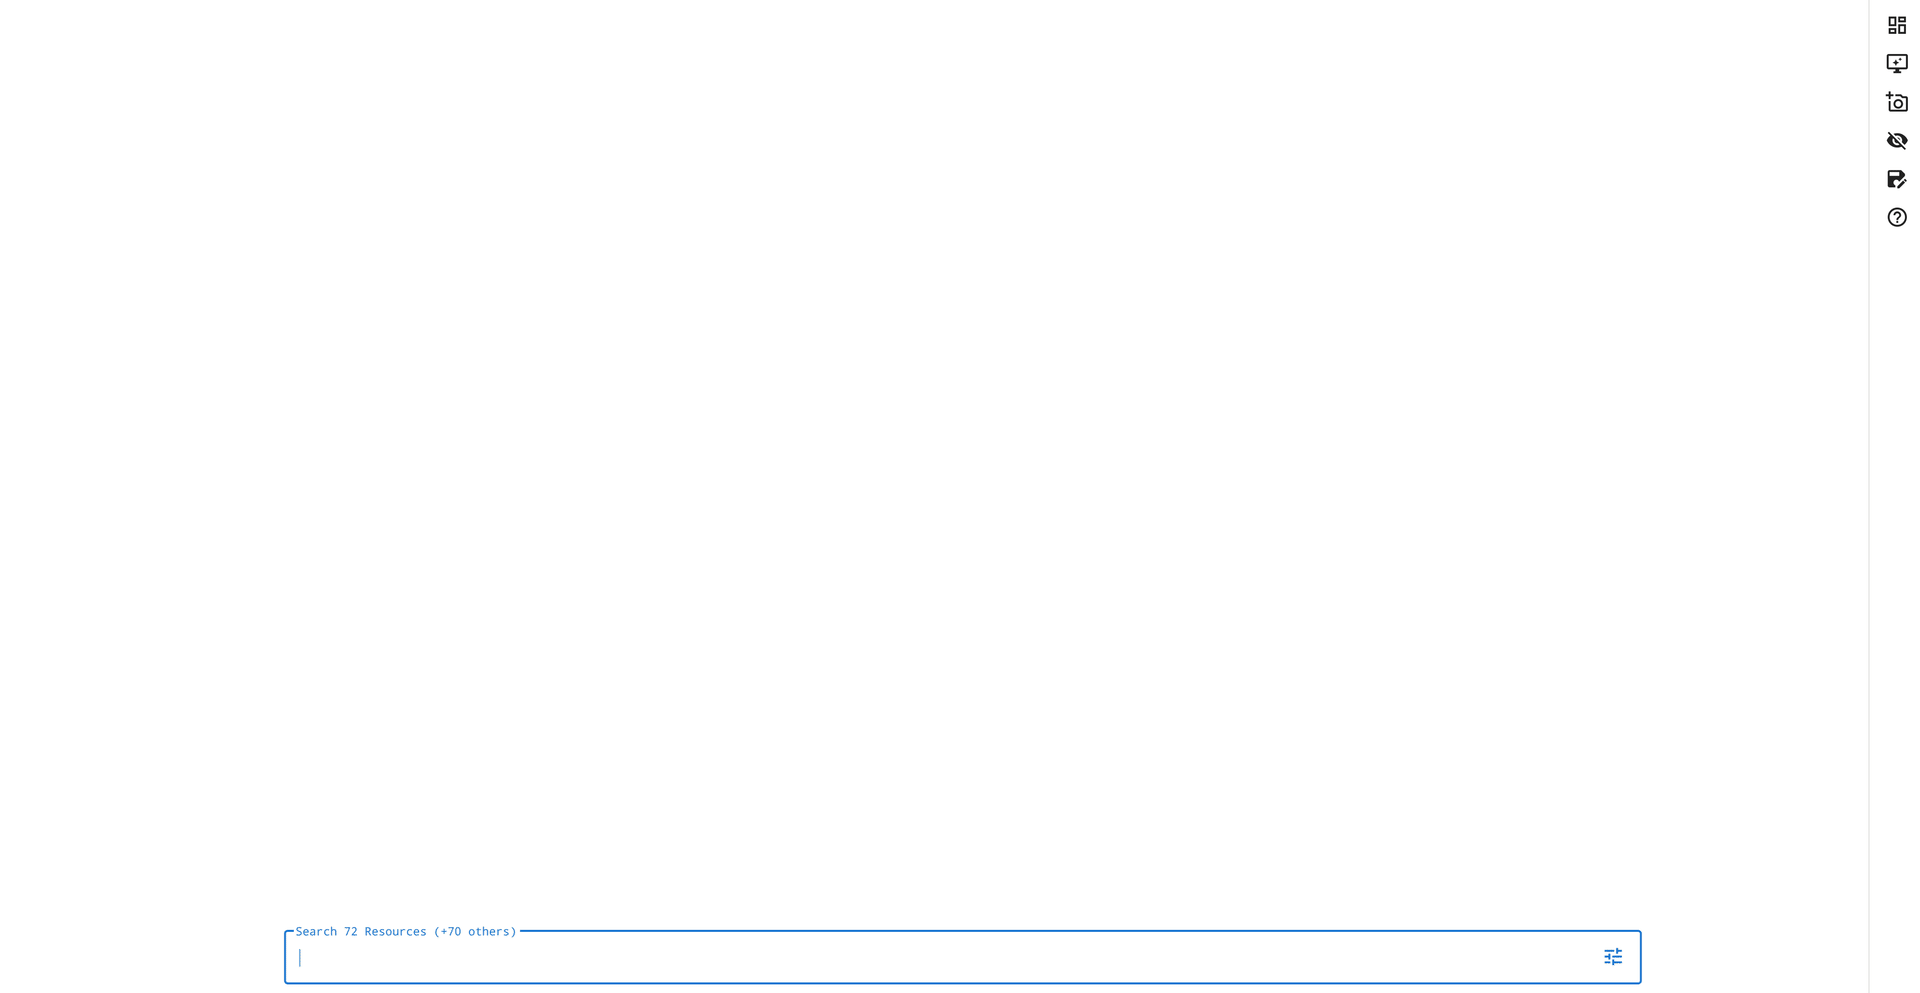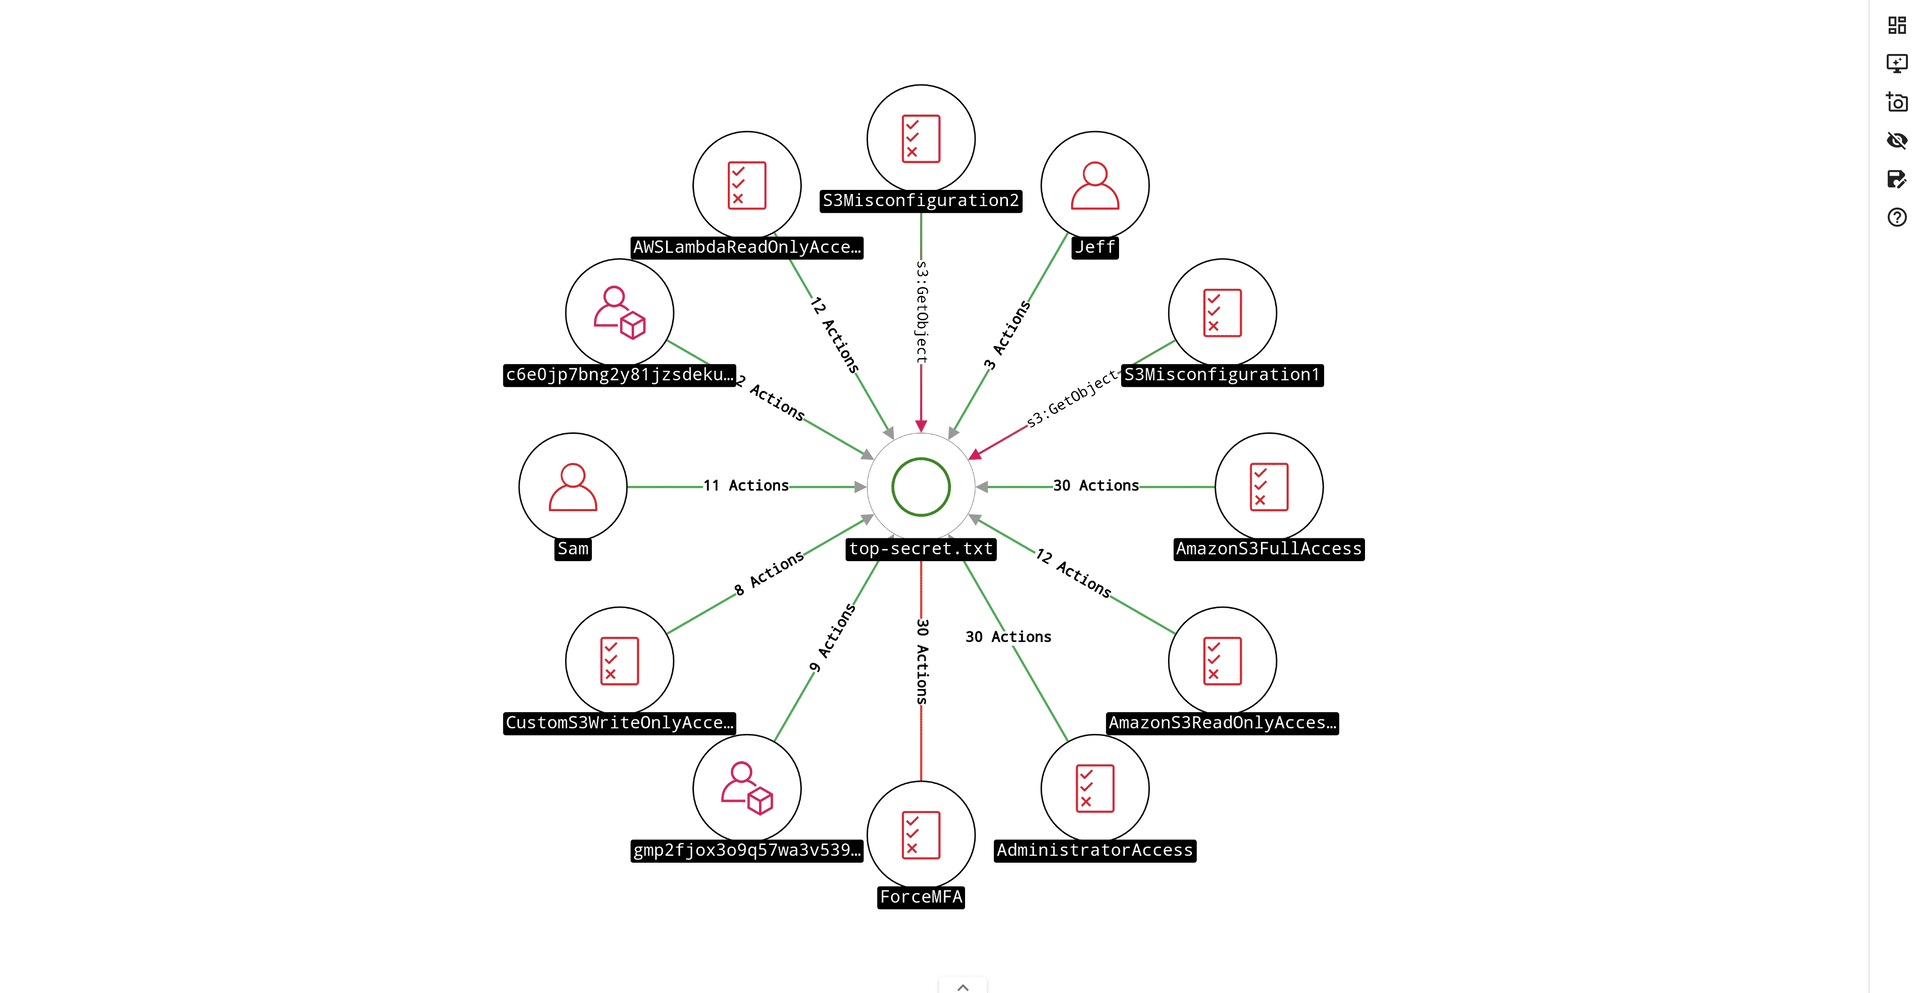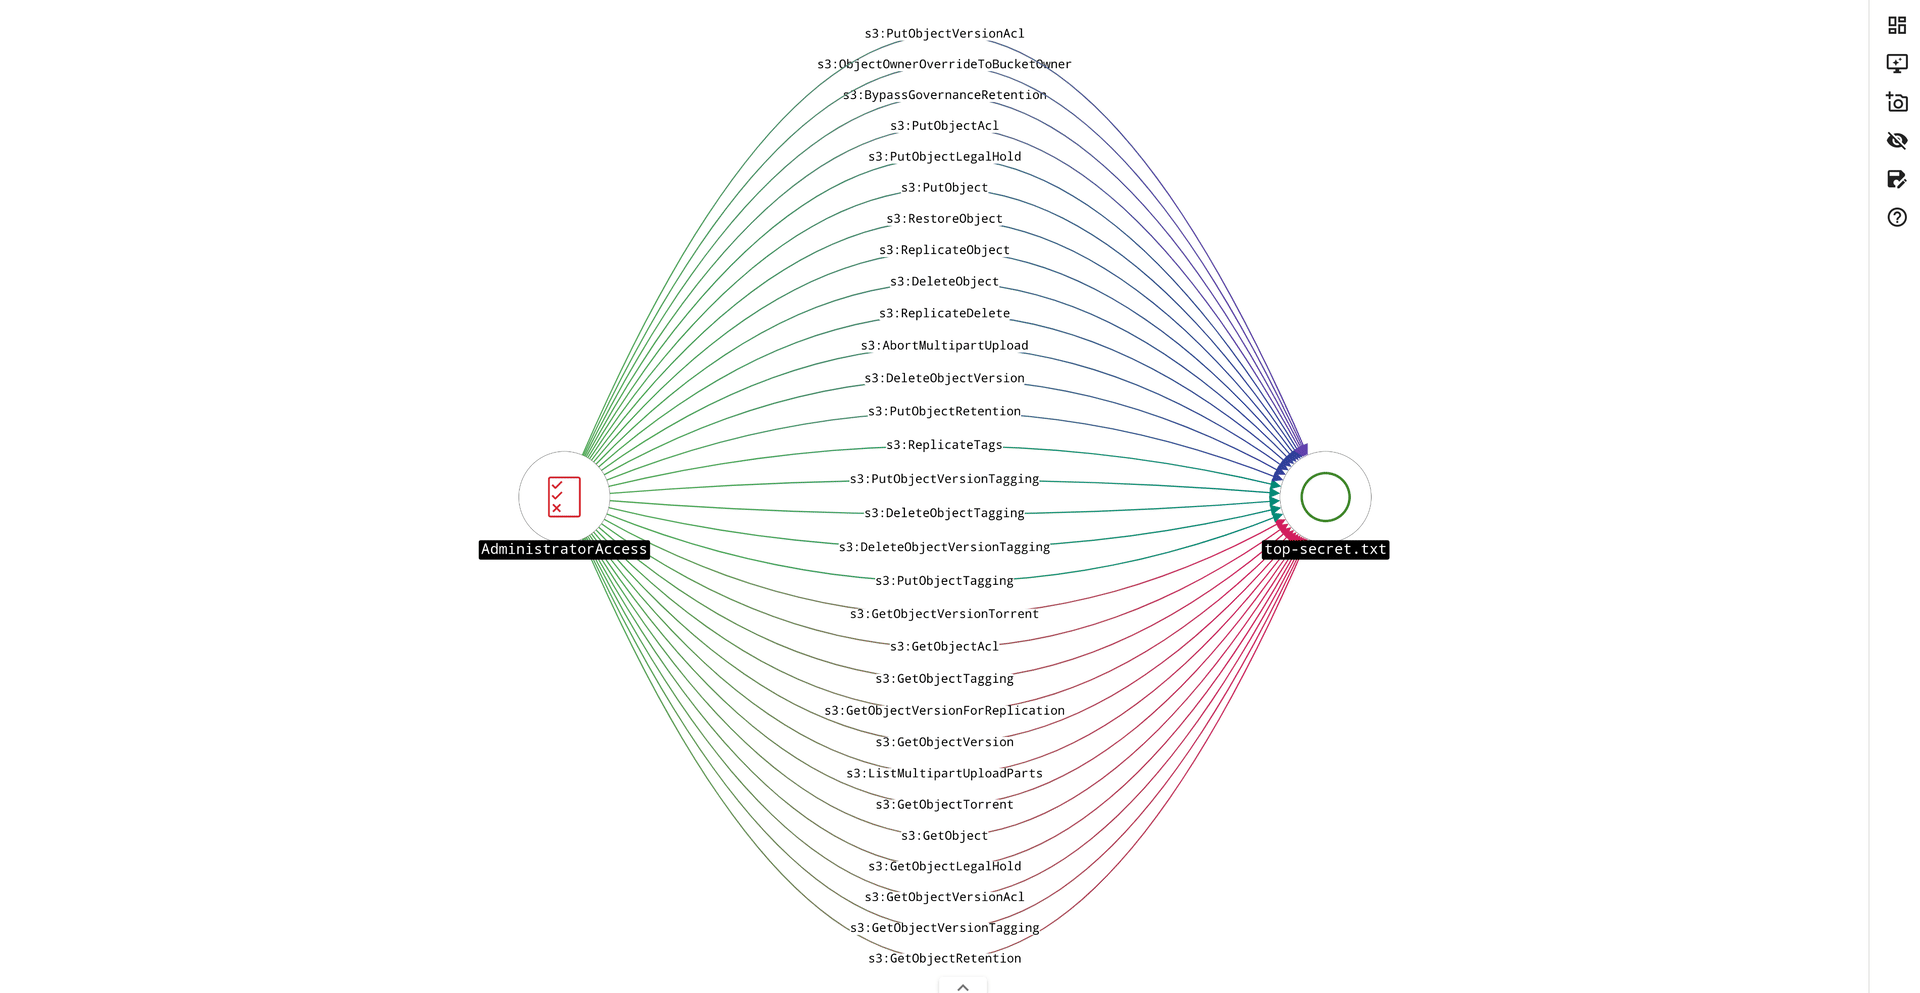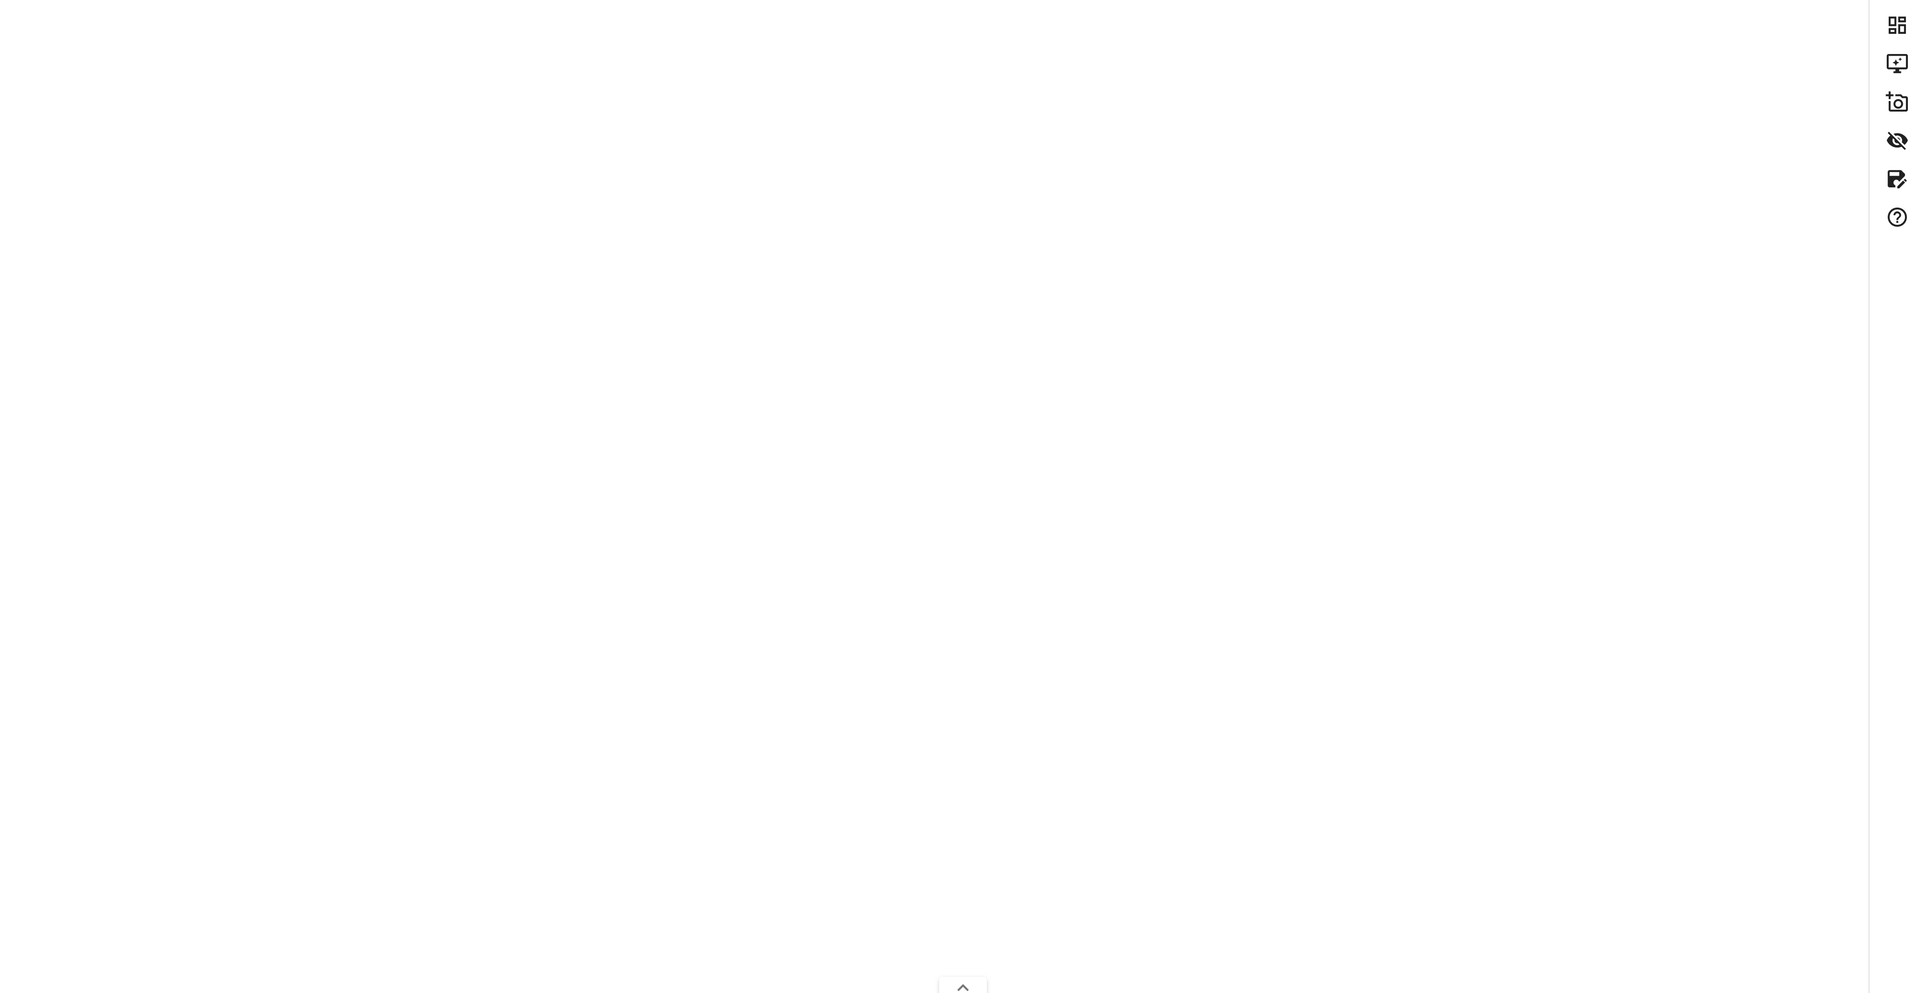
awspx is a graph-based tool for visualizing effective access and resource relationships within AWS. It resolves policy information to determine what actions affect which resources, while taking into account how these actions may be combined to produce attack paths. Unlike tools like Bloodhound, awspx requires permissions to function — it is not expected to be useful in cases where these privileges have not been granted.
For more information, checkout the awspx Wiki
For detailed installation instructions, usage, and answers to frequently asked questions, see sections: Setup; Data Collection and Exploration; and FAQs, respectively.
awspx can be installed on either Linux or macOS. In each case Docker is required.
git clone https://github.com/FSecureLABS/awspx.git
INSTALL scriptcd awspx && ./INSTALL
awspx consists of two main components: the ingestor, which collects AWS account data; and the web interface, which allows you to explore it.
Run the ingestor against an account of your choosing. You will be prompted for credentials.
awspx ingest
OR optionally forgo this step and load the sample dataset instead.
awspx db --load-zip sample.zip
awspx attacks
Browse to the web interface — http://localhost by default — and explore this environment.
This project is in its early days and there's still plenty that can be done. Whether its submitting a fix, identifying bugs, suggesting enhancements, creating or updating documentation, refactoring smell code, or even extending this list — all contributions help and are more than welcome. Please feel free to use your judgement and do whatever you think would benefit the community most.
See Contributing for more information.
awspx is a graph-based tool for visualizing effective access and resource relationships within AWS. (C) 2018-2020 F-SECURE.
This program is free software: you can redistribute it and/or modify it under the terms of the GNU General Public License as published by the Free Software Foundation, either version 3 of the License, or (at your option) any later version.
This program is distributed in the hope that it will be useful, but WITHOUT ANY WARRANTY; without even the implied warranty of MERCHANTABILITY or FITNESS FOR A PARTICULAR PURPOSE. See the GNU General Public License for more details.
You should have received a copy of the GNU General Public License along with this program. If not, see https://www.gnu.org/licenses/.







