Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories
slurp-old — A tool to enumerate S3 buckets manually or via certstream | Kitploit
Tools/GitHubGitHub/0xbharath/slurp-old
Cloud Infrastructure SecurityOSINT (Open Source Intelligence)ReconnaissanceInformation GatheringPenetration TestingCloud Security
GitHub0xbharath/slurp-old

slurp-old

A tool to enumerate S3 buckets manually or via certstream

View Repository
8319278 years agoReviewed by Kitploit
Share

slurp

Enumerates S3 buckets manually or via certstream

Overview

  • First of all, credit to https://github.com/eth0izzle/bucket-stream for the certstream idea.
  • Also, credit to all the vendor packages that made this tool possible.
  • Not responsible for how you use this tool.

Modes

Certstream

certstream

Domain

domain

Keywords

keyword

Features

  • Written in Go:
    • It's faster than python.
    • No dependency hell and version locks (ie python 3 and requirements.txt, etc); easier to deploy, static binary, etc.
    • Better concurrency.
  • Punycode support for internationalized domains (S3 doesn't allow internationalized buckets; so this app just notifies and skips (certstream) or exits (domain mode)).
  • Domain mode so that you can test individual domains.
  • New Keywords mode so that you can attempt enumeration based on keywords. Why is this useful? Sometimes organizations have shorthand names that they go by. If you wanted to test that shorthand name you could not do so previously; now you can by using this mode of enumeration.
  • New Supports a list of domains now.
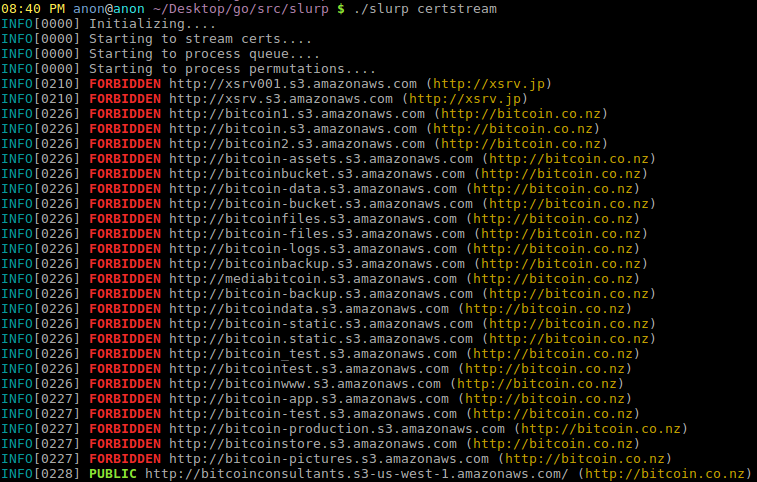
  • Certstream mode so that you can enumerate s3 buckets in real time.
  • Colorized output for visual grep.
  • Currently generates over 1200 permutations per domain and keyword.
  • Strong copyleft license.

Usage

  • slurp domain <-t|--target> google.com will enumerate the S3 domains for a specific target.
  • slurp keyword <-t|--target> linux,golang,python will enumerate S3 buckets based on those 3 key words.
  • slurp certstream will follow certstream and enumerate S3 buckets from each domain.
  • permutations.json stores the permutations that are used by the program; they are in JSON format and loaded during execution this is required; it assumes a specific format per permutation: anything_you_want.%s; the ending .%s is required otherwise the AWS S3 URL will not be attached to it, and therefore no results will come from S3 enumeration. If you need flexible permutations then see PermutateDomain function.

Installation

  • Download from Releases section, or build yourself with go build or build.sh.
    • Make sure you clone to $GOPATH/src or you will get build errors!

License

  • AGPLv3
Download Tool

Most Popular

View all →

Discover the most used tools by our community.

  • 1

    OsintHunter

    letox4/osinthunter

    🎯 The ultimate OSINT toolkit: investigation graph, confidence scoring, alias families, map, timeline and reports. 49 modules, 400+ sites, no API keys required.

    524
  • 2

    ghostlock-app

    yukonga/ghostlock-app

    GhostLock One-Tap Execution App (CVE-2026-43499)

    478
  • 3

    ARTEX

    baarai/artex

    LLM multi-agent autonomous penetration testing platform with planner/worker agents, asset and exploration graphs, MITM traffic recording, and vulnerability retesting.

    357
  • 4

    redforge

    cybersecurity91/redforge

    Browser-side red team toolkit with 102 offline tools for recon, payload generation, credential attacks, crypto, encoding and engagement reporting.

    317
  • 5

    estorides

    grisuno/estorides

    Aggregates 99+ free OSINT sources in parallel, resolves entities into a knowledge graph, and exports STIX 2.1, MISP, or GraphML with LLM-assisted analysis.

    305
  • 6

    opencti

    opencti-platform/opencti

    Open Cyber Threat Intelligence Platform

    275

Explore all tools

Browse our collection of tools

View all tools →