
om-research
 alkersan/om-research
Documenting Osmo Mobile BLE protocol
packet-sniffing-analysisbluetooth-securityreverse-engineering+3
178 months ago
alkersan/om-researchDocumenting Osmo Mobile BLE protocol
 roostercoopllc/flipper-mcp
AI-powered MCP server for Flipper Zero. Control SubGHz, NFC, RFID, IR, BLE, GPIO, and more over WiFi using Claude or any MCP client.
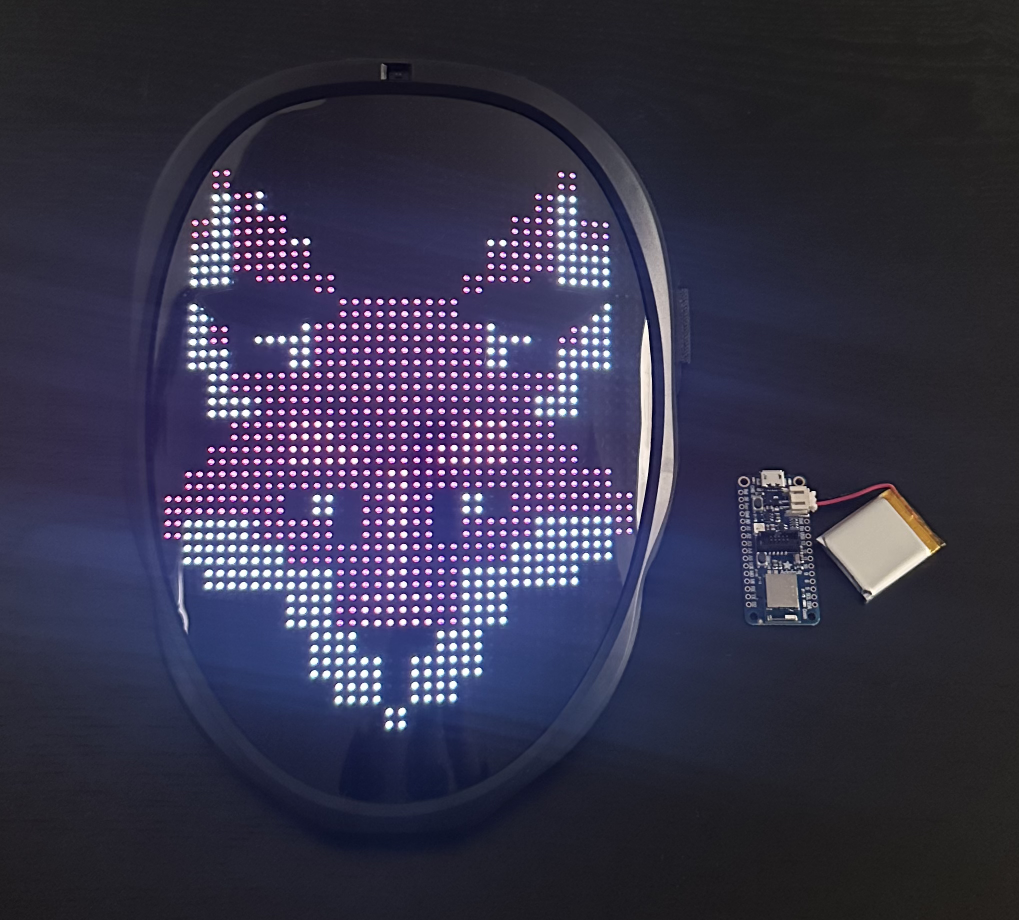 bishopfox/shining-mask
BLE-based tool that automatically discovers and exploits Shining LED Masks by uploading a custom image without user interaction, proving security…
 f4r3sx0/ios-bluetooth-ethernet-exploit
iOS Bluetooth PAN vulnerability that opens USB port 62078 and displays Ethernet icon without any adapter (€0). Apple sells a €89.95 adapter for the…
 joshuapassos/cmf-watch-pro-2-ble-protocol
Reverse-engineered BLE protocol for the CMF Watch Pro 2, documenting GATT layout, AES-128-CBC encrypted command frames, authentication handshake, and…
 esperto-input/esperto-wiimote
Advanced Wiimote remapping software
 eternityforest/lazymesh
Proof of concept IoT/Ham Radio mesh network with global routing over the internet
 elevenpaths/devicepairedtool
Tool for testing and auditing Bluetooth device pairing security, identifying vulnerabilities in wireless pairing protocols and hardware IoT…
 adrihd/shiningappmask-reverseengineering
Reverse Engineering of the Shining App Mask
 veteranop/trackem
Passive Device Tracker (Android)TrackEm Mobile is a real-time, passive Wi-Fi + Bluetooth LE probe-request scanner designed for OSINT, red-team ops,…
 toxy4ny/rinhit
Collects macOS and iOS artifacts to build timelines of network activity, cross-device identity, and physical location correlation for reconnaissance…
 steampunk424/cve-2025-36911-wisper_pair_target_finder
This is not an exploit for CVE-2025-36911!!! This is a detector for finding potentially vulnerable devices! Only use on your own devices! I am not…
 spiritualmachines/buds-audit
No-dongle, no-root Bluetooth security assessment tool for wireless earbuds affected by the Airoha SDK vulnerability chain (CVE-2025-20700/20701/20702)
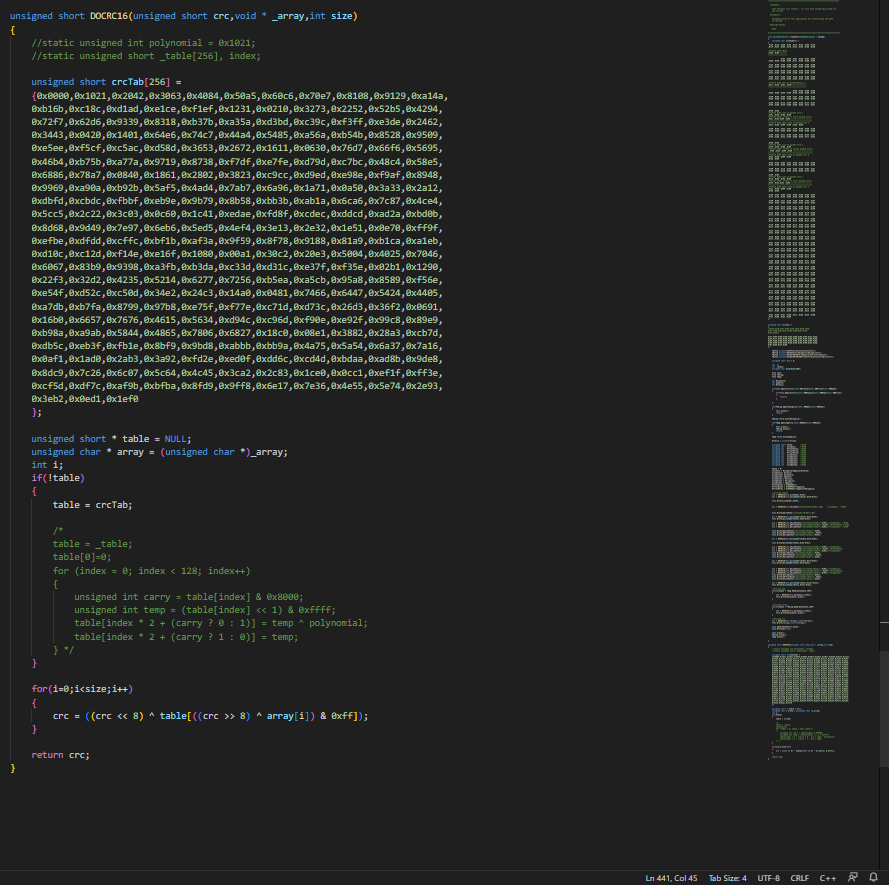 spiralbl0ck/cabir_analysis
cabin partial analysis
 mjancek/bluebornedetection
Simple detection tool for Blueborne vulnerability found on Android devices --- CVE-2017-0781.
 damiansuess/learn.bluejam
Learn what is BlueJam CVE-2017-0781
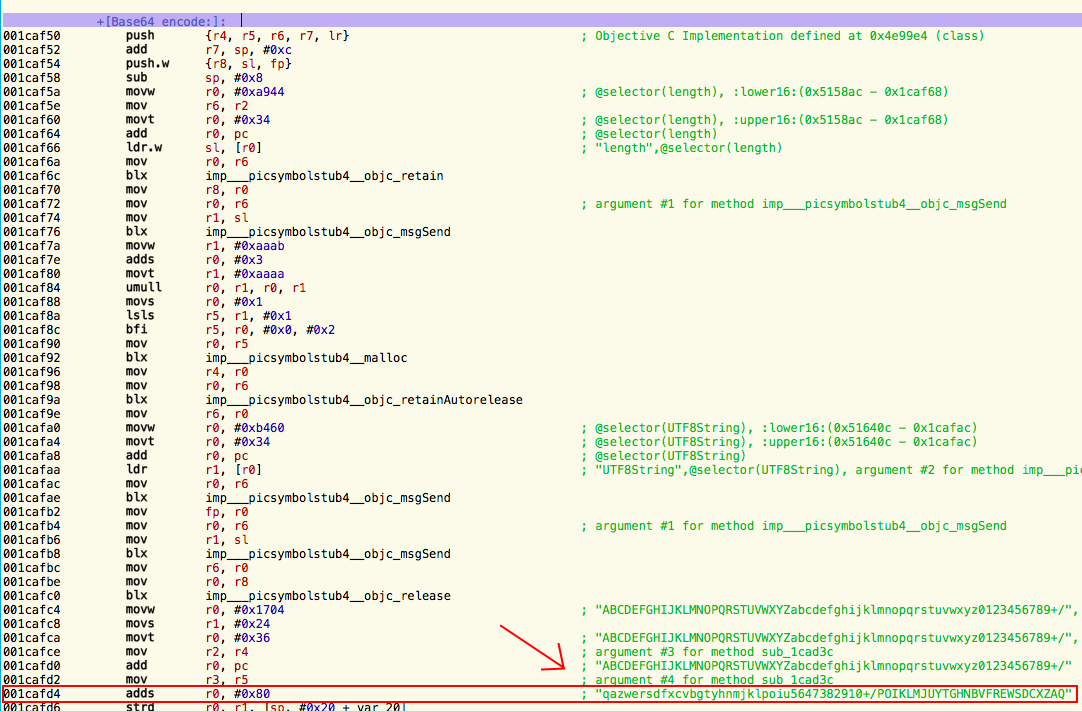 jasondoyle/komfy-switch-wifi-password-disclosure
Proof-of-concept and writeup showing how to retrieve Wi-Fi SSID/password from a D-Link Komfy smart switch over BLE by reversing the iOS app’s custom…
 jclarkcom/ble_proxy
BLE-based HTTP proxy system routing browser traffic through an iOS device. Supports HTTP/HTTPS, data compression, and mock mode for testing without…