
AndroidAuto
 mretallack/androidauto
Open-source Android Auto phone-side implementation with protocol reverse engineering, TLS mutual authentication, H.264 video projection, touch input…
android-securitybluetooth-securityeducation+4
8
mretallack/androidautoOpen-source Android Auto phone-side implementation with protocol reverse engineering, TLS mutual authentication, H.264 video projection, touch input…
 librepods-org/librepods
AirPods liberated from Apple's ecosystem.
 joshuapassos/cmf-watch-pro-2-ble-protocol
Reverse-engineered BLE protocol for the CMF Watch Pro 2, documenting GATT layout, AES-128-CBC encrypted command frames, authentication handshake, and…
 alkersan/om-research
Documenting Osmo Mobile BLE protocol
 kalibb/cve-2020-0022
Zero-click Bluetooth RCE exploit for Android 8-9 (CVE-2020-0022) with heap spraying, address leaking, and JOP chain execution for remote code…
 adrihd/shiningappmask-reverseengineering
Reverse Engineering of the Shining App Mask
 sastraadiwiguna-purpleeliteteaming/cve-2025-13834-a-bluetooth-rfcomm-out-of-bounds-read-vulnerability-in-modern-wireless-devices
CVE-2025-13834 Technical Summary Vulnerability Type: Memory Disclosure / Out-of-Bounds (OOB) Read (CWE-125). CVSS Score: 7.5–8.1 (High/Critical). …
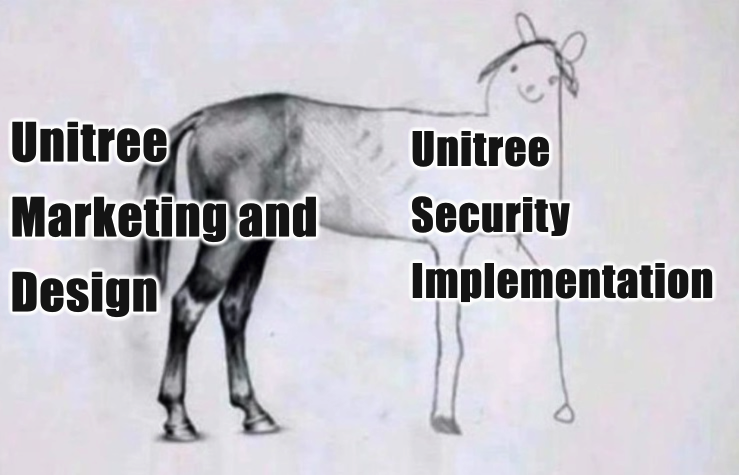 bin4ry/unipwn
BLE exploit framework for Unitree robots: command injection via hardcoded AES keys enables remote takeover, payload injection, and wormable…
 themmokhtar/cve-2020-0022
A fully public exploit of the CVE-2020-0022 BlueFrag Android RCE Vulnerability (tested on Pixel 3 XL)
 spiralbl0ck/cabir_analysis
cabin partial analysis
 seemoo-lab/toothpicker
Coverage-guided in-process fuzzer for iOS Bluetooth daemon (bluetoothd) using FRIDA, with over-the-air fuzzing for MagicPairing protocol and crash…
 sysnets/atfuzzer
Grammar-guided evolutionary fuzzer for dynamic analysis of AT command interfaces on Android smartphones via Bluetooth and USB, uncovering DoS,…
 polo35/cve-2020-0022
CVE-2020-0022 vulnerability exploitation on Bouygues BBox Miami (Android TV 8.0 - ARM32 Cortex A9)
 seemoo-lab/fitness-app
BLE-based Fitbit research tool for authentication replay, encrypted activity dump decryption, memory/firmware extraction, and custom firmware…
 x3ero0/android712-blueborne
Android Blueborne RCE CVE-2017-0781
 alfa100001/-cve-2017-0785-blueborne-poc
CVE-2017-0785 BlueBorne PoC
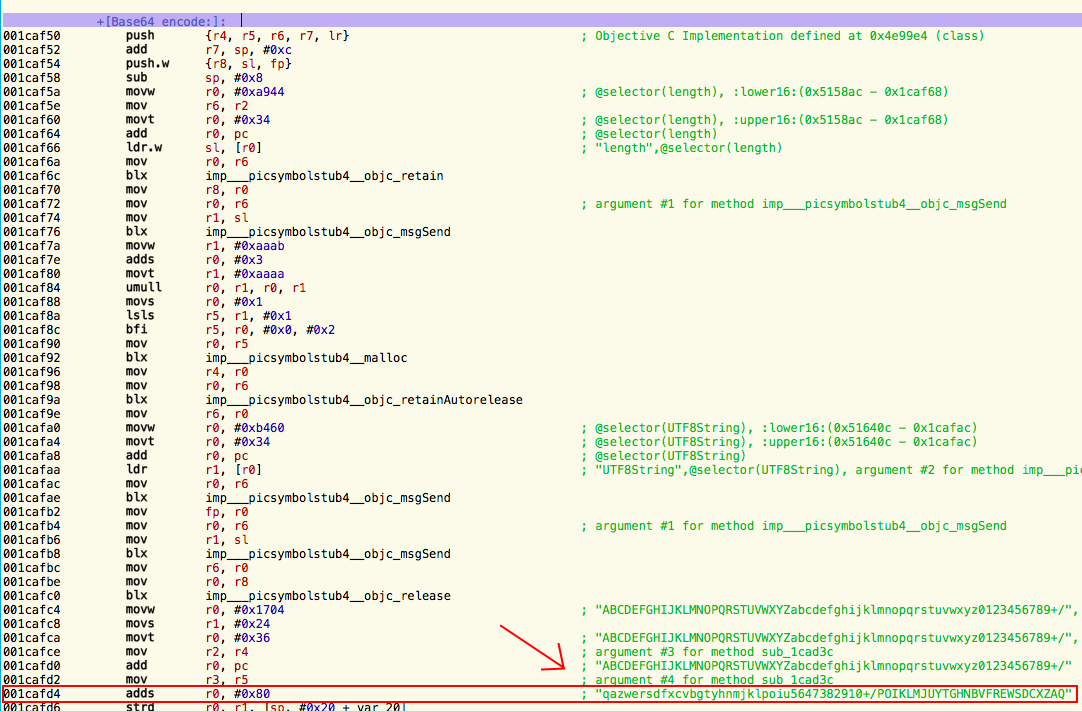 jasondoyle/komfy-switch-wifi-password-disclosure
Proof-of-concept and writeup showing how to retrieve Wi-Fi SSID/password from a D-Link Komfy smart switch over BLE by reversing the iOS app’s custom…