
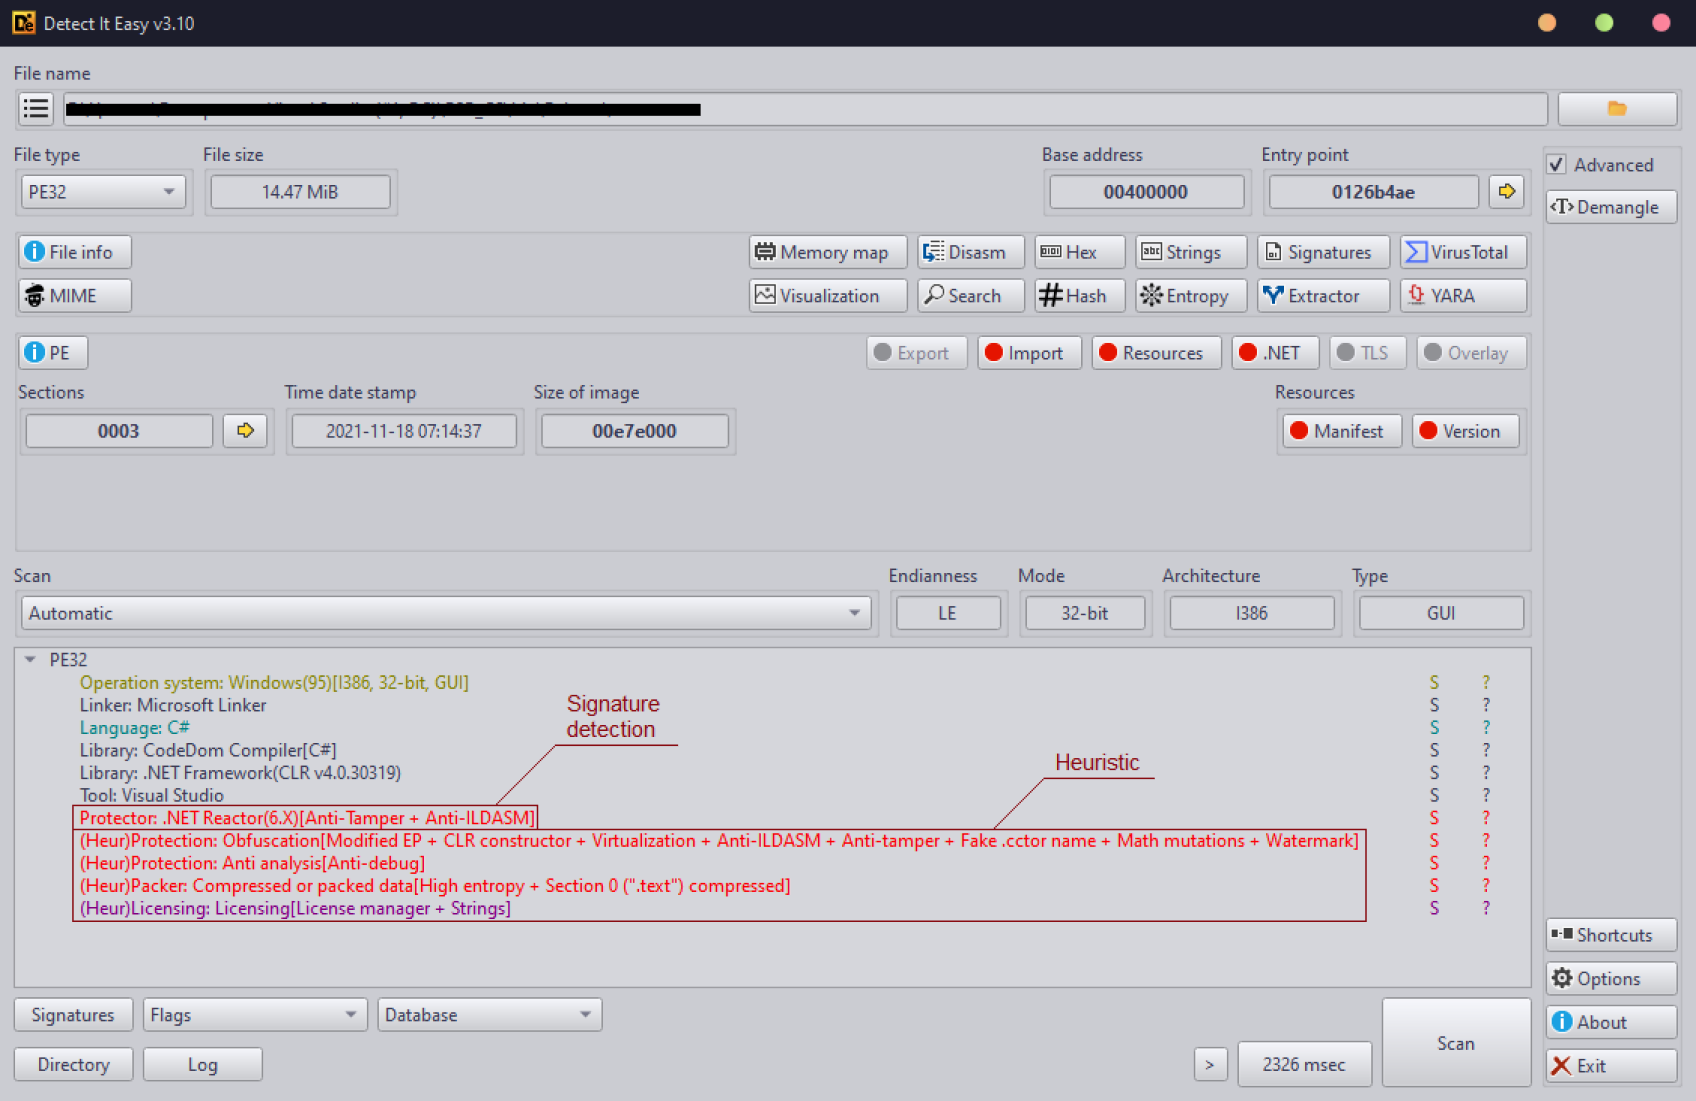
Detect-It-Easy
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
ai-assisted-reversingbinary-analysisbinary-exploitation+10
11.5k
horsicq/detect-it-easyProgram for determining types of files for Windows, Linux and MacOS.
 bcoles/kasld
KASLD derandomizes the Linux kernel's virtual and physical memory layout from a local process, using whatever its vantage — privilege, configuration,…
 csrxamfi/cve-2026-65330
Perl proof-of-concept exploit demonstrating a use-after-free in the NECP trie, with a heap spray option for triggering the kernel memory corruption.
 winterknife/evenstar
Intel 64/Windows low-level experiments
 aarif450/zapscape
Guest-to-host KVM/x86 escape exploiting CVE-2026-64561, delivering a full PoC chain and analysis for security researchers.
 learningdisordercapital35/cve_2025_24257----not-mine
Demonstrate CVE-2025-24257 with a public PoC for IOGPUFamily kernel heap OOB read/write and panic analysis
 rkrakesh524/oob_entry
oob_entry tfp0 kernel exploit for armv7 iOS (iOS 3.0–10.3.4), using CVE-2023-32434. We will publish a write-up detailing the methods in the coming…
 bikini/exploitarium
Curated archive of public proof-of-concept exploits and vulnerability research writeups covering web, binary, and network security, with a focus on…
 tracyliving606/regpwn
Exploit Windows local privilege escalation on clients and servers using tested code for CVE-2026-24291 across multiple Windows versions
 nomnomheapnom/cve-2024-27815
Proof-of-concept trigger for CVE-2024-27815, an XNU kernel heap buffer overflow in sbconcat_mbufs() reachable via AF_UNIX datagram sockets, causing…
 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
 deaurity/ghost-hoock
GhostLock stripped to one primitive: SELinux off on Galaxy A17 (BZA5) via futex PI UAF (CVE-2026-43499). No root, no cred patch, no rwforge.
 kurtulusakyuz/ionstack_s21
Exploit chain research targeting CVE-2026-43499 on Samsung Galaxy S21
 theendofabbys/pedit-cow
Linux kernel privilege escalation exploit for CVE-2026-46331, abusing the traffic control pedit subsystem to corrupt the page cache and execute SUID…
 capstone-engine/capstone
Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 youssefnoob003/sindrikit
A foundational C library for building operationally credible offensive capabilities