

Chimay-Red
 bignerd95/chimay-red
Working POC of Mikrotik exploit from Vault 7 CIA Leaks
binary-exploitationembedded-systems-securityexploitation+8
6684 years ago
bignerd95/chimay-redWorking POC of Mikrotik exploit from Vault 7 CIA Leaks
 67-6f-64/antioreans-codedevirtualizer
IDA 6.8 plugin that devirtualizes Themida's FISH virtual machine (2.2.5.0-2.2.7.0), restoring native code from protected binaries for reverse…
 valium007/cve-2026-56129
Proof-of-concept exploiting the Toshiba qiomem.sys driver to achieve arbitrary physical memory read/write from ring 3, with a companion writeup.
 0vercl0k/kepaboo
Neutralize KEPServerEX anti-debugging techniques
 structio-labs/n0xis
AI-first reverse-engineering toolkit: static analysis, SSA decompiler, live memory, provenance. Source-available (PolyForm Noncommercial).
 racoten/reflectivepluginloader
Minimal Windows x64 reflective PE mapper that loads DLLs from memory without LoadLibrary, resolves exports, and dispatches calls through a…
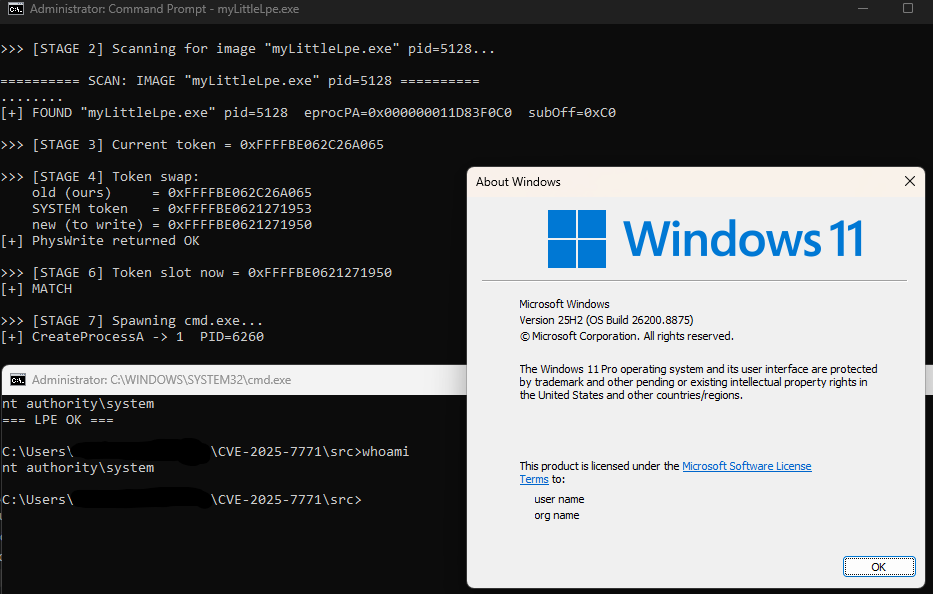 yulisec/cve-2025-7771
Full exploit chain for CVE-2025-7771 in ThrottleStop.sys, abusing unvalidated physical memory R/W IOCTLs to escalate from administrator to SYSTEM on…
 minime794/dirtyfrag
Linux kernel exploit chain (CVE-2026-43284 and CVE-2026-43500) that achieves root via xfrm-ESP and RxRPC page-cache write vulnerabilities.
 0xblackash/cve-2026-74469
Research repository for CVE-2026-74469 (DiagSpill), a Linux kernel SCTP peer transport counter overflow causing an out-of-bounds write, with PoC,…
 vportal/cve-2022-22715
Exploit code for CVE-2022-22715 (Windows Dirty Pipe), a sandbox escape and privilege escalation via named pipe TOKEN object corruption, with a linked…
 0xcyberstan/cve-2026-59346-poc
PoC for CVE-2026-59346 - 32-bit integer overflow in VMware's VMXNET3 TSO segmentation path, guest-to-host crash.
 gmh5225/dsark64
BYOVD proof-of-concept abusing the WHQL-signed DsArk64.sys driver for ring-0 process termination and kernel read/write via encrypted IOCTLs and…
 sneakynachos/cve-2026-87491-and-cve-2026-85046-the-bagel-fell-off-the-counter
Chrome 152 V8 exploit chaining CVE-2026-85046 and CVE-2026-87491 to corrupt the heap, forge Wasm metadata, and execute native code from the renderer.
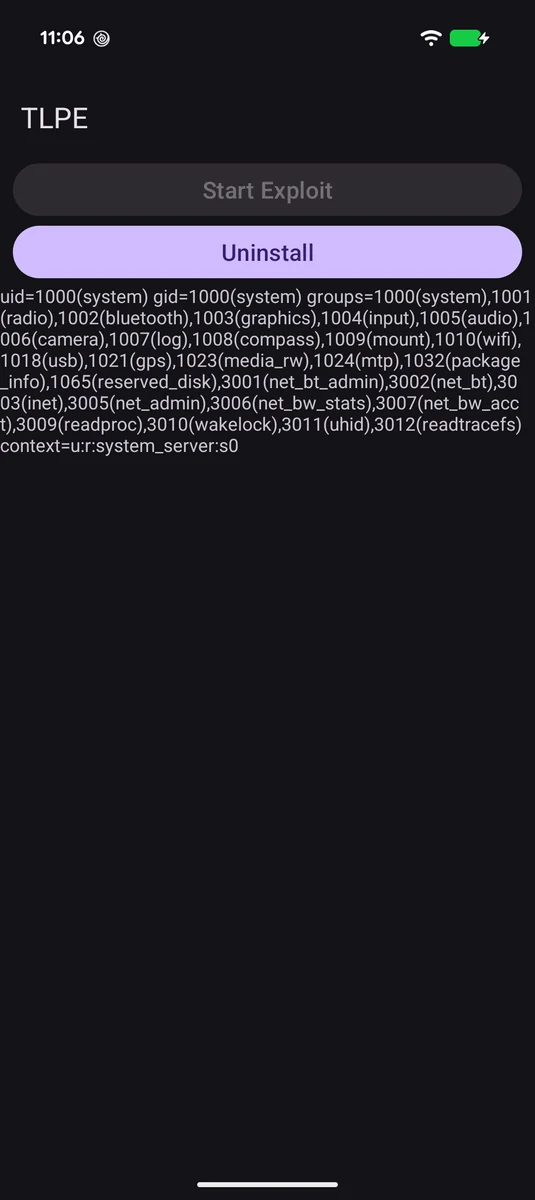 supersonic/tlpe
CVE-2026-49881, using insecure context creation in Android 17's Telecom service to execute arbitrary code as UID 1000 system_server from an…
 diegslva/cve-2010-4221-lab
From patch to RCE: hand-built exploit for CVE-2010-4221 (ProFTPD TELNET IAC stack overflow), with the full failure-driven journey documented
 dorlow/hazel-cve-2026-43499
Firmware-specific temporary root exploit for Toshiba/Amazon Fire TV (hazel) using CVE-2026-43499. Implements ARM32 futex-PI UAF, kernel address leak,…
 catforgor/cve-2026-51585
rt26cx21x64.sys exploit (Realtek PCIe GbE/2.5GbE/5GbE family)
 franklinf25/cve-2026-31431
Analyzes CVE-2026-31431, a Linux kernel AF_ALG AEAD vulnerability, providing a safe detector, in-lab LPE exploit, and QEMU-based A/B kernel lab for…