

radare2
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
ai-assisted-reversingandroid-securitybinary-analysis+16
24.5k
radareorg/radare2UNIX-like reverse engineering framework and command-line toolset
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 radareorg/iaito
Qt-based graphical interface for the radare2 reverse engineering framework, providing disassembly, binary analysis, debugging, patching and forensics…
 nbs32k/localstranger
PoC for WinNotify, demonstrated through a driver mapper, and local privilege escalation.
 lkeld/cve-2026-43499-poc
Weaponized proof-of-concept for CVE-2026-43499 (GhostLock), a Linux kernel rtmutex bug enabling local privilege escalation. Includes per-distribution…
 capstone-engine/capstone
Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…
 mfthomps/labtainers
Labtainers: A Docker-based cyber lab framework
 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.
 idov31/silverseal
Linux post-exploitation framework with a UEFI bootkit that persistently and stealthily loads a Rust-based kernel module rootkit on modern Linux…
 keystone-engine/keystone
Multi-architecture assembler framework that converts assembly source into machine code for Arm, x86, MIPS, PowerPC, RISC-V, and more, with a…
 angr/angr
A powerful and user-friendly binary analysis platform!
 impost0r/rie
Kernel exploit for CVE-2026-43724 targeting Apple macOS/iOS systems. Provides proof-of-concept code for the disclosed vulnerability.
 apkc/cve-2024-26229-bof
BOF implementations of CVE-2024-26229 for Cobalt Strike and BruteRatel
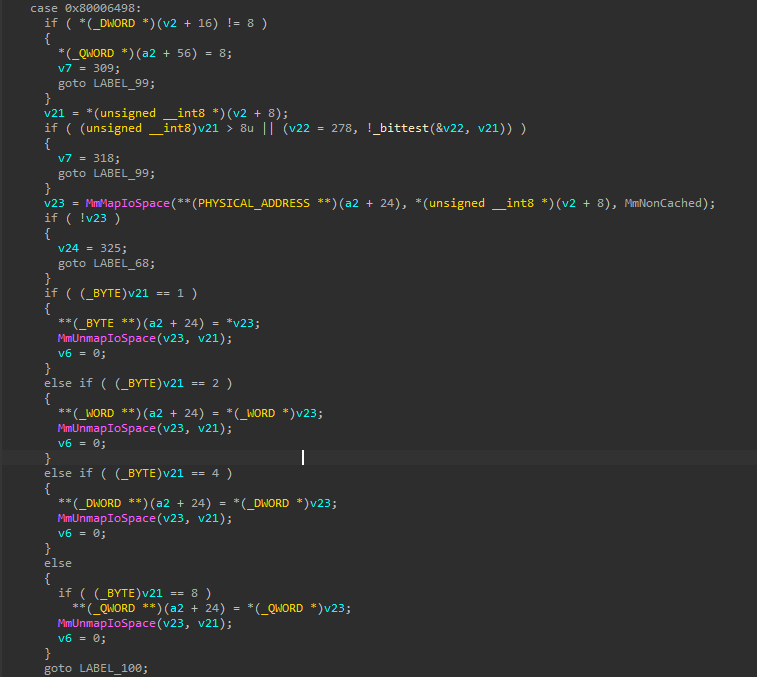 demoo1337/throttlestop
CVE-2025-7771 ThrottleStop.sys privilege escalation exploit - unrestricted IOCTL access to physical memory via MmMapIoSpace
 gallopsled/pwntools
CTF framework and exploit development library
 sashs/ropper
Display information about files in different file formats and find gadgets to build rop chains for different architectures (x86/x86_64, ARM/ARM64,…
 turtlearm/cve-2023-0179-poc
Exploit for CVE-2023-0179, a stack buffer overflow in the Linux nftables subsystem, enabling unprivileged local privilege escalation to root via…
 unicorn-engine/unicorn
Unicorn CPU emulator framework (ARM, AArch64, M68K, Mips, Sparc, PowerPC, RiscV, S390x, TriCore, X86)