
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
1147 results
sandfly-entropyscan preview

sandfly-entropyscan

GitHubsandflysecurity/sandfly-entropyscan

Entropy scanner for Linux to detect packed or encrypted binaries related to malware. Finds malicious files and Linux processes and gives output with…

binary-analysisforensicsincident-response+1
171

2 years ago
Detect-It-Easy preview

Detect-It-Easy

GitHubhorsicq/detect-it-easy

Program for determining types of files for Windows, Linux and MacOS.

ai-assisted-reversingbinary-analysisbinary-exploitation+10
11.8k22h 13m ago
Furtex preview

Furtex

GitHubmatheuzsecurity/furtex

Post-exploitation and evasion research toolkit for Linux.

binary-analysiscommand-and-controlexploitation+6
2933 months ago
Brovan preview

Brovan

GitHubadvdebug/brovan

User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…

binary-analysisdebuggersdynamic-analysis-sandboxing+3
16819h 8m ago
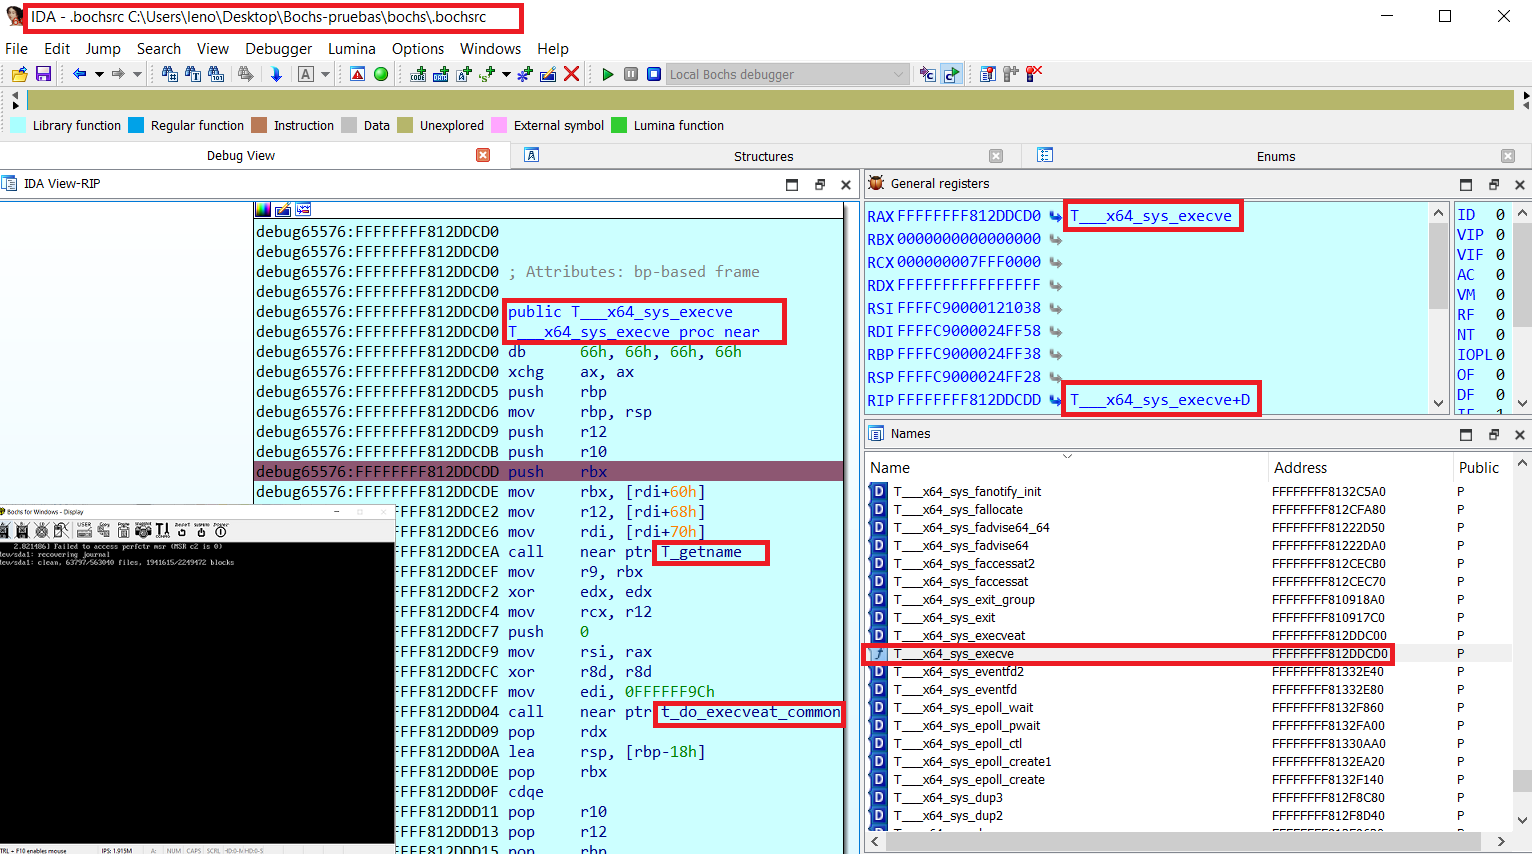
bochs_linux_kernel_debugging preview

bochs_linux_kernel_debugging

GitHubtherealdreg/bochs_linux_kernel_debugging

Tools for Linux kernel debugging on Bochs (including symbols, native Bochs debugger and IDA PRO)

binary-analysisdebuggerseducation+1
333 years ago
tiny_tracer preview

tiny_tracer

GitHubhasherezade/tiny_tracer

Intel Pin-based tracer for API calls, syscalls, and instructions with anti-debug evasion, used for malware analysis and reverse engineering of packed…

api-securitybinary-analysisdynamic-analysis-sandboxing+2
1.7k4 months ago
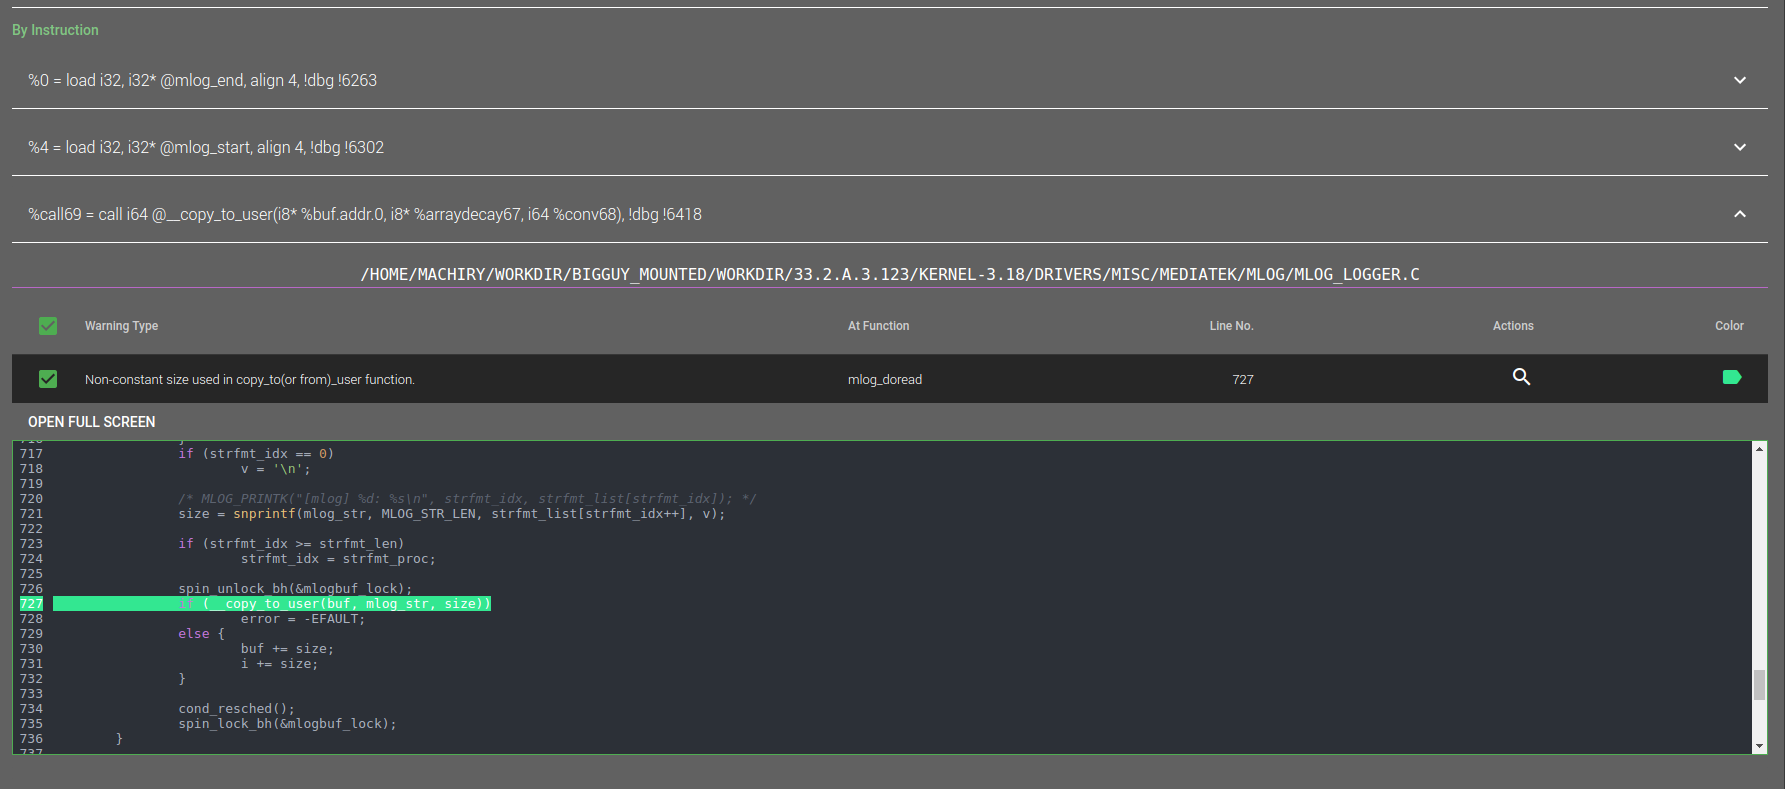
dr_checker preview

dr_checker

GitHubucsb-seclab/dr_checker

DR.CHECKER : A Soundy Vulnerability Detection Tool for Linux Kernel Drivers

binary-analysisfuzzingstatic-analysis+2
3394 years ago
mwemu preview

mwemu

GitHubmwemuorg/mwemu

Pure Rust x86 hardware emulator and Windows process simulator for malware analysis, shellcode emulation, and payload unpacking. Supports 32/64-bit PE…

binary-analysisexploit-frameworksmalware-analysis+2
3192 days ago
attesor preview

attesor

GitHubinokinoki/attesor

AI-powered reverse-engineering of Rosetta (2 for Linux). Disclaimer: due to the user agreement, I will not touch the code. All is done by AI, so…

ai-assisted-reversingbinary-analysiseducation+3
872 months ago
Soviet preview

Soviet

GitHubmephistolist/soviet

A Runtime Crypter in C for Linux ELF binaries.

anti-botbinary-analysisencryption-decryption-tools+6
368 months ago
linux-kernel-debugger preview

linux-kernel-debugger

GitHubgmh5225/linux-kernel-debugger

Kernel hardware debugger module for dumping rootkit operations and inspecting kernel-level activity for malware analysis and reverse engineering.

binary-analysisdebuggersdynamic-analysis-sandboxing+3
4 years ago
snoop preview

snoop

GitHubpandaadir05/snoop

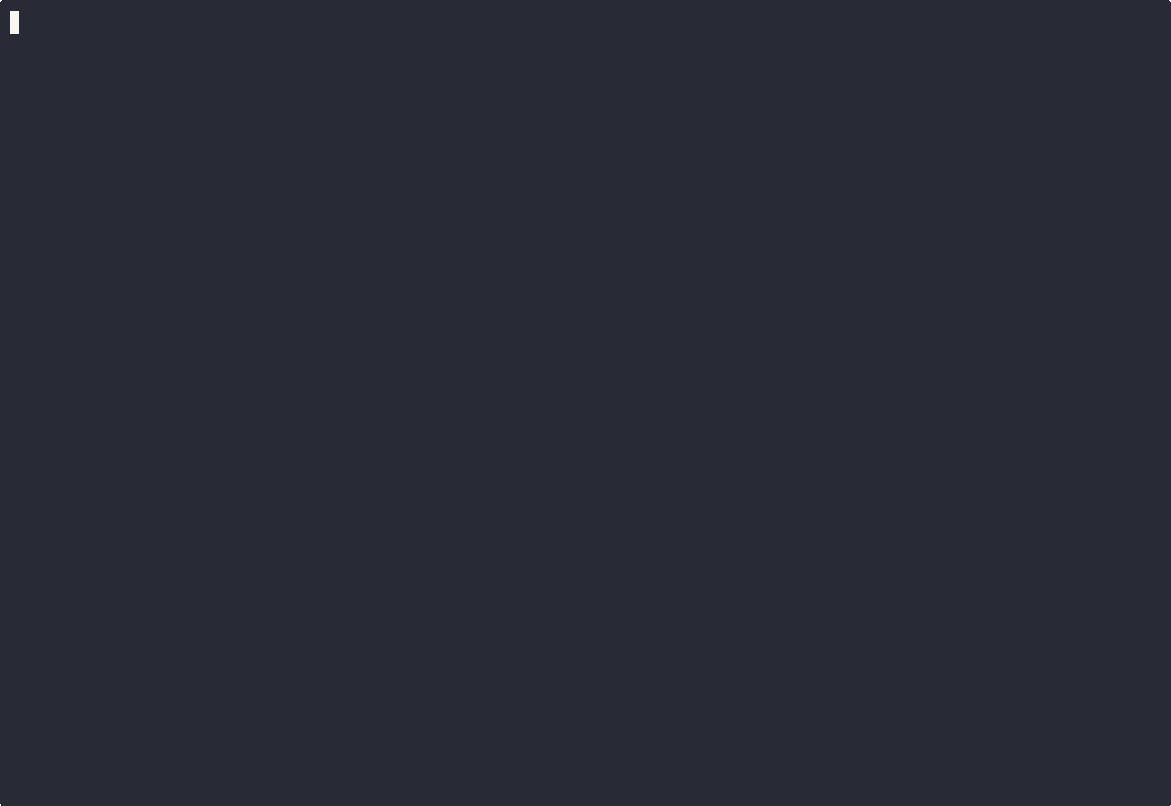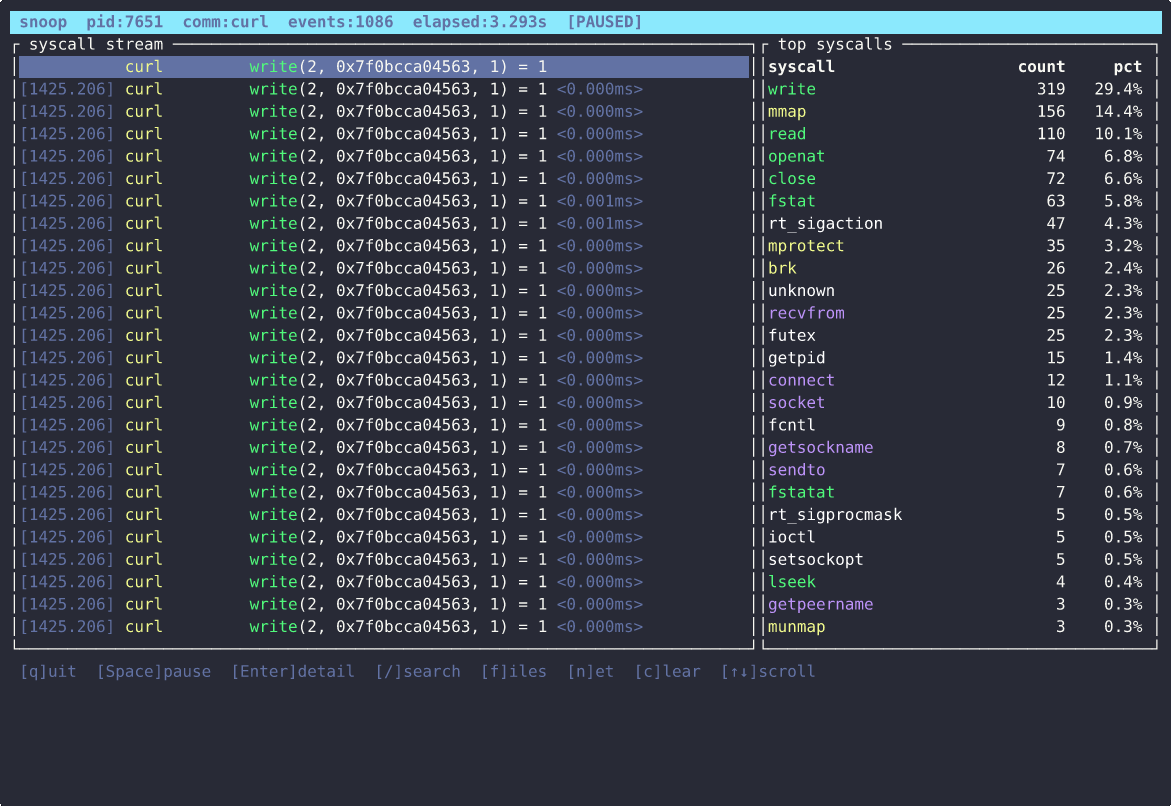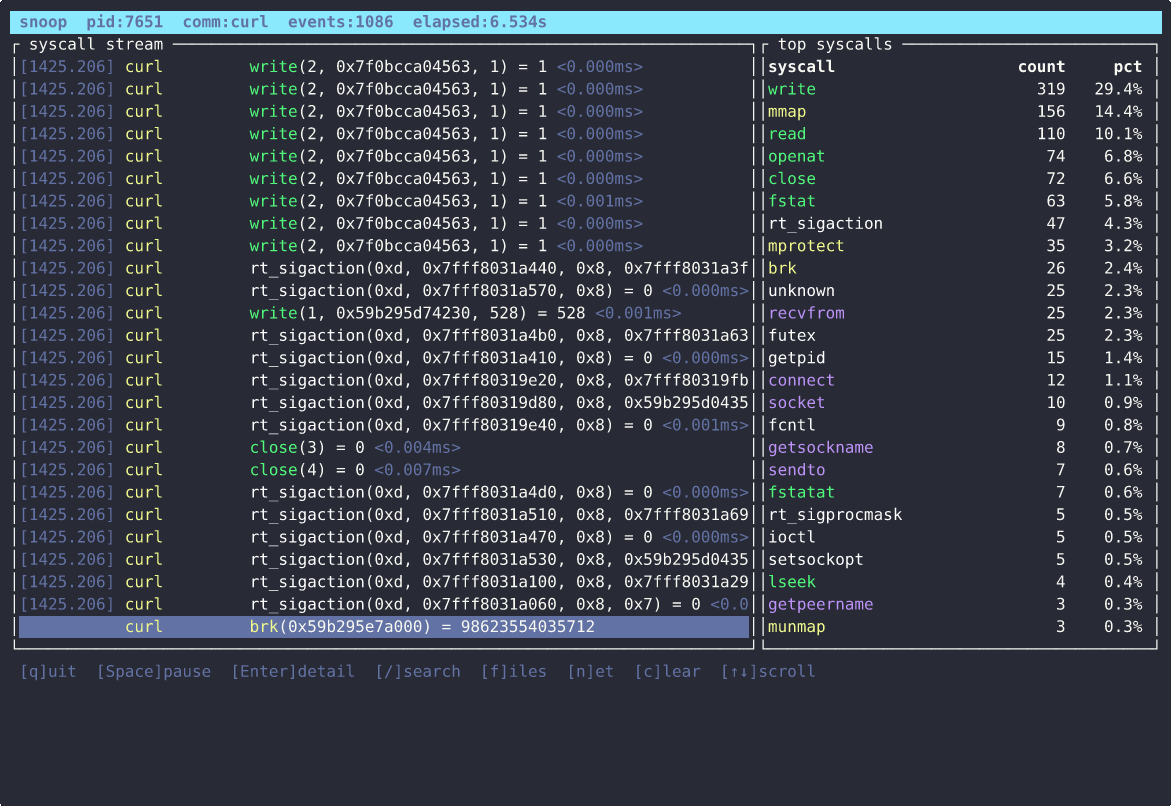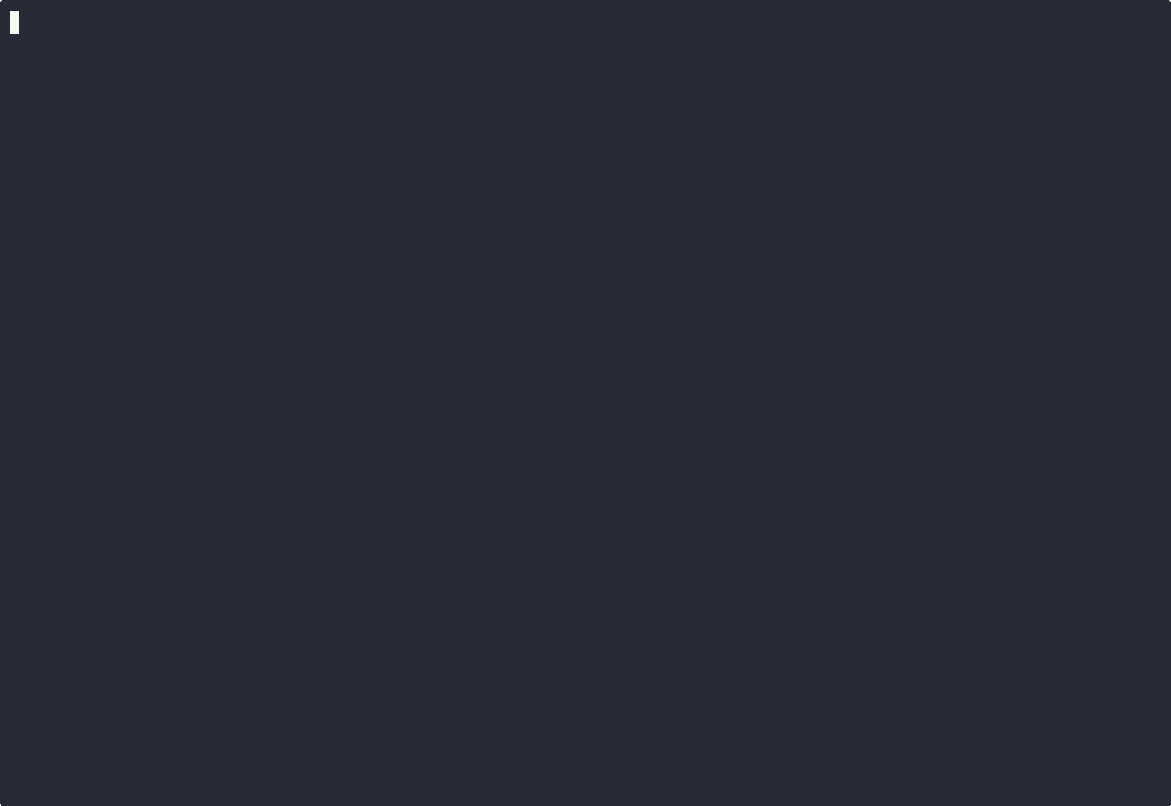
A modern syscall tracer built on eBPF. Think strace, but with a real TUI, smart filters, TLS decryption, and output that's actually readable.

binary-analysisdebuggersdynamic-analysis-sandboxing+7
2246 months ago
ComfyEngine preview

ComfyEngine

GitHubkashithecomfy/comfyengine

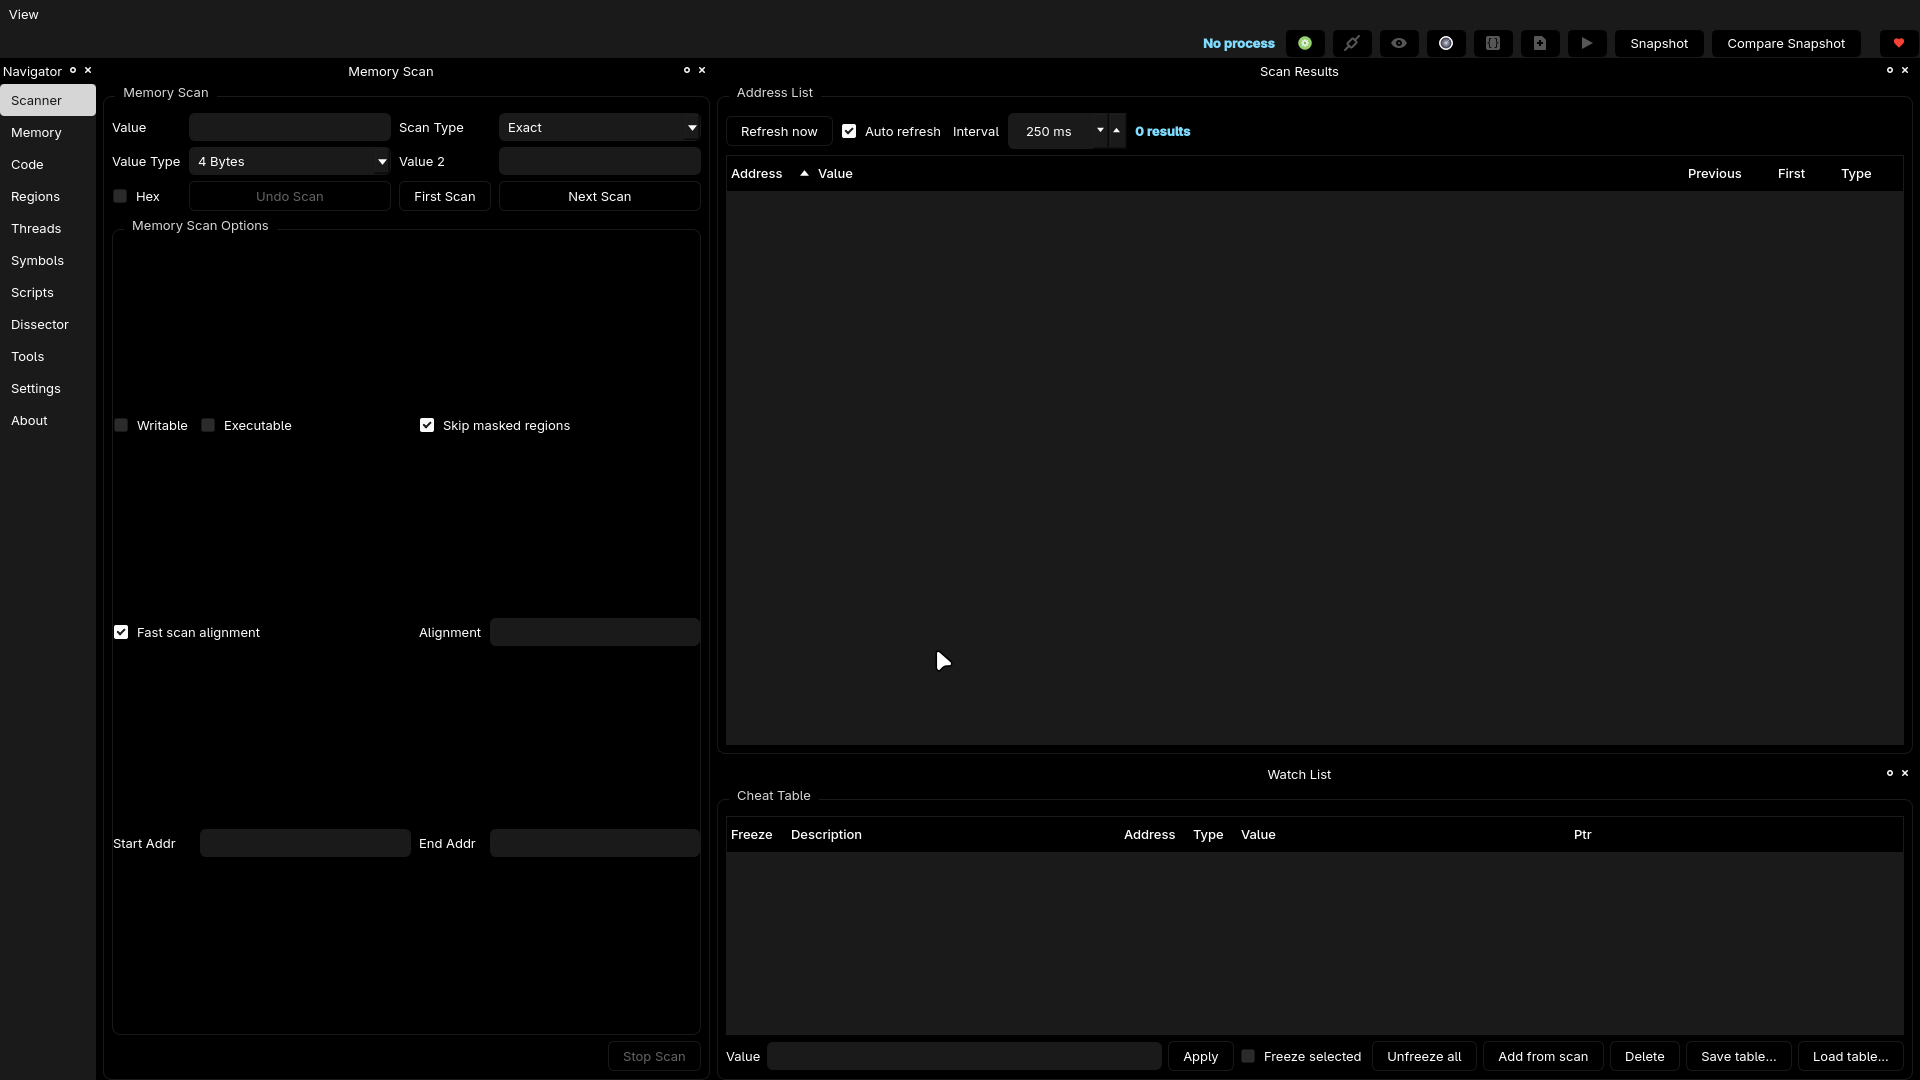
ComfyEngine is a memory exploration toolkit built for people who need to monitor, patch, and script a running process.

binary-analysisdebuggersdynamic-code-analysis+5
6110 months ago
PETriage preview

PETriage

GitHubuky007/petriage

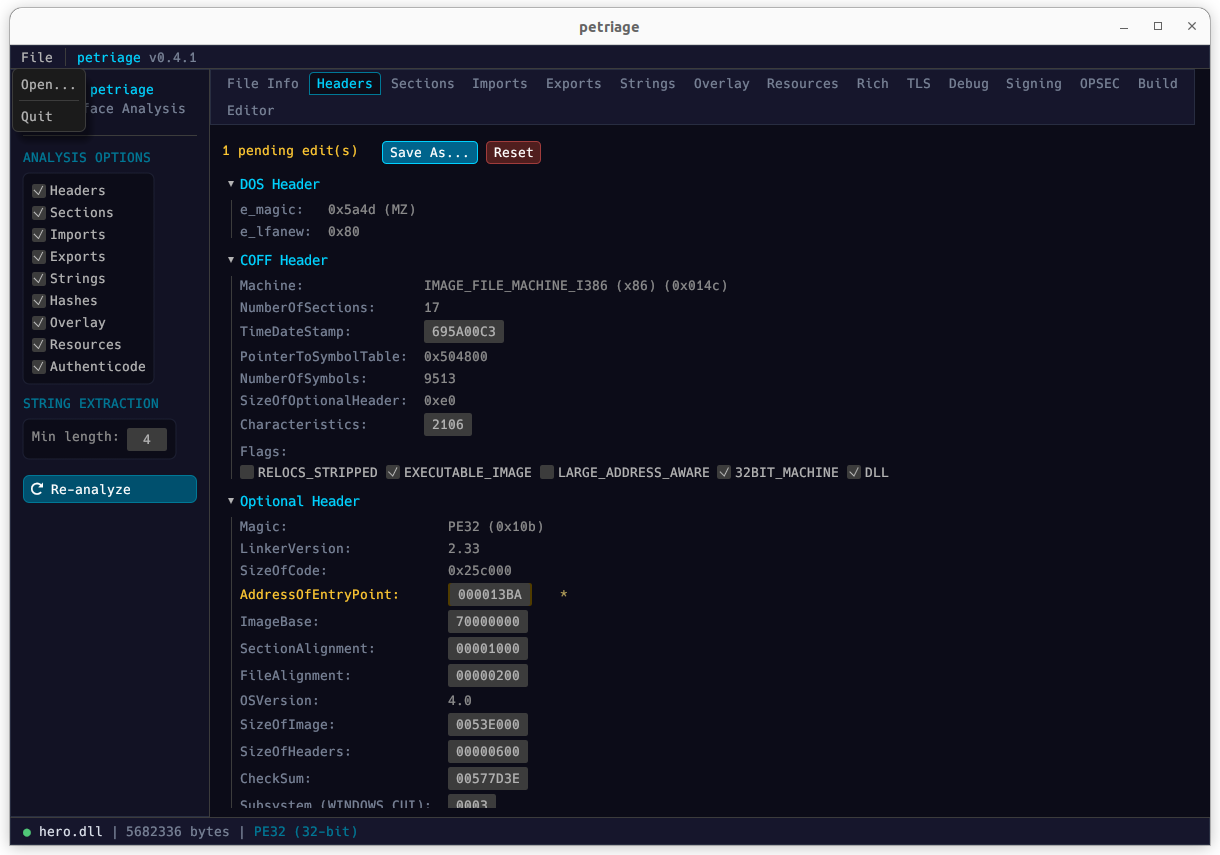
PETriage: A symbol-unified PE file reader for triage, built for multi-platform and multi-interface use.

anomaly-detectionbinary-analysisdigital-forensics+5
132 months ago
N0xis preview

N0xis

GitHubstructio-labs/n0xis

Reverse-engineering toolkit: disassembler, SSA decompiler, C++ class recovery and live-process analysis for PE and ELF. Scriptable CLI, every answer…

ai-assisted-reversingbinary-analysisbinary-exploitation+7
33 days ago
linux-4.1.15_CVE-2022-45934 preview

linux-4.1.15_CVE-2022-45934

GitHubsatheesh575555/linux-4.1.15_cve-2022-45934

Linux kernel 4.1.15 source code with a focus on CVE-2022-45934, providing a reference for vulnerability analysis and exploitation research.

binary-analysisdebuggersexploitation+2
3 years ago
seer preview

seer

GitHubepasveer/seer

Seer - a gui frontend to gdb

binary-analysisdebuggersdynamic-analysis-sandboxing+3
3.5k2 days ago
dwarf2json preview

dwarf2json

GitHubvolatilityfoundation/dwarf2json

convert ELF/DWARF symbol and type information into vol3's intermediate JSON

binary-analysisdigital-forensicsmemory-forensics+2
1592 years ago
Previous12…64Next