
MCPDebugger
 fatmike-gh/mcpdebugger
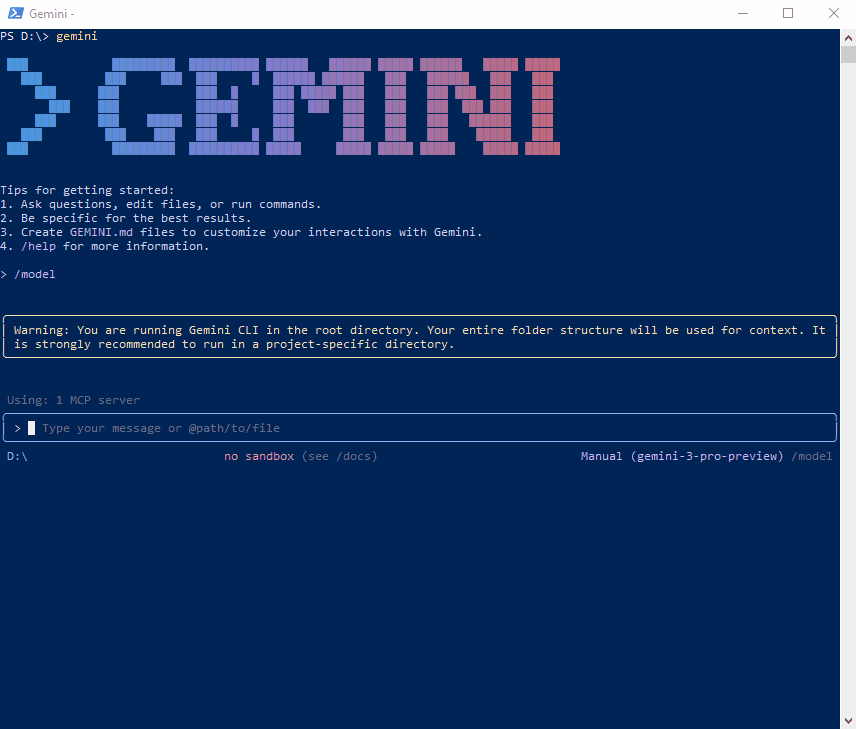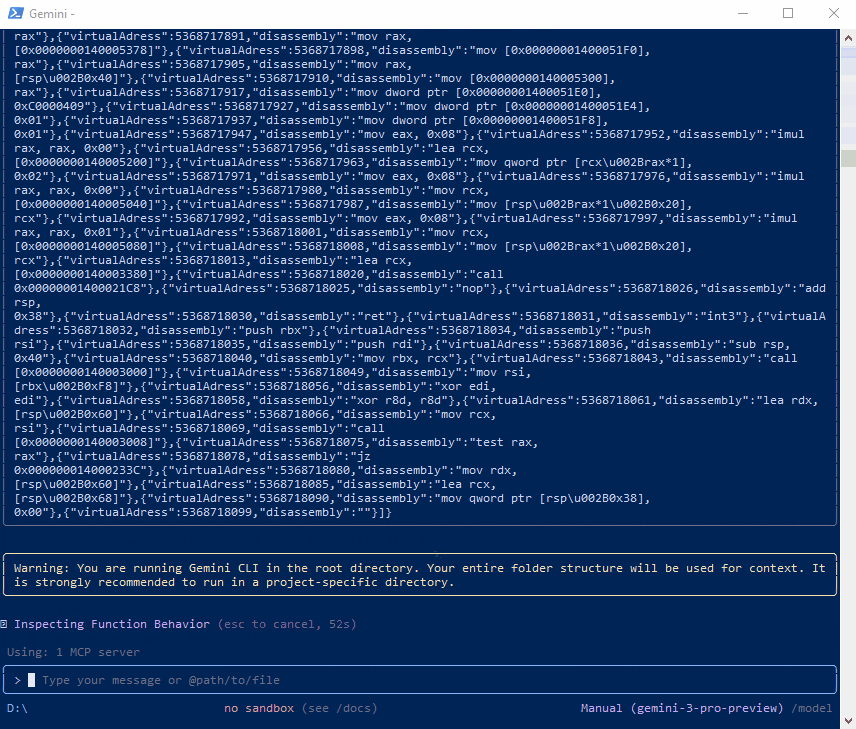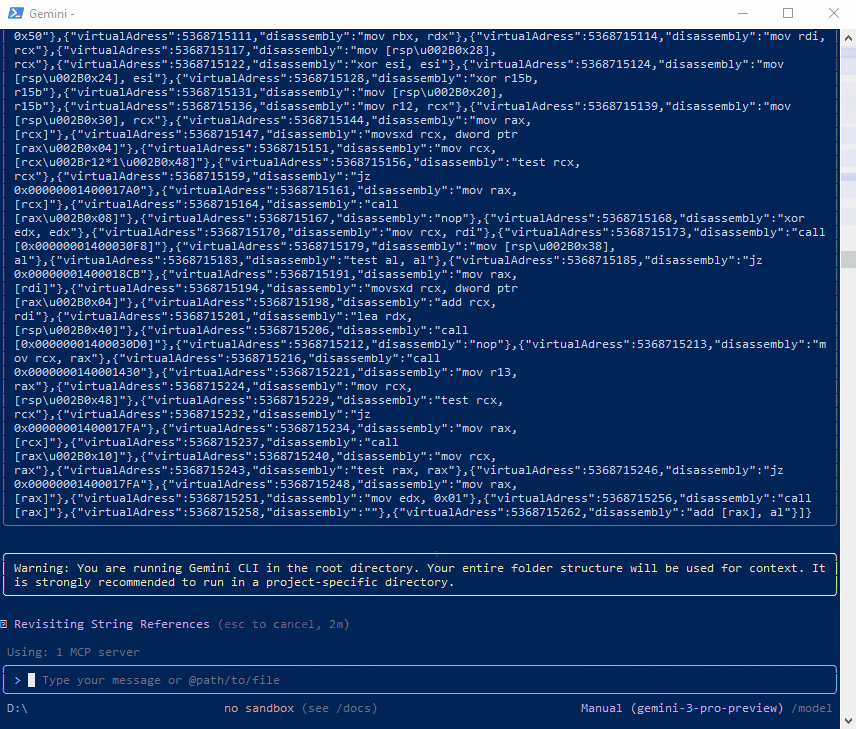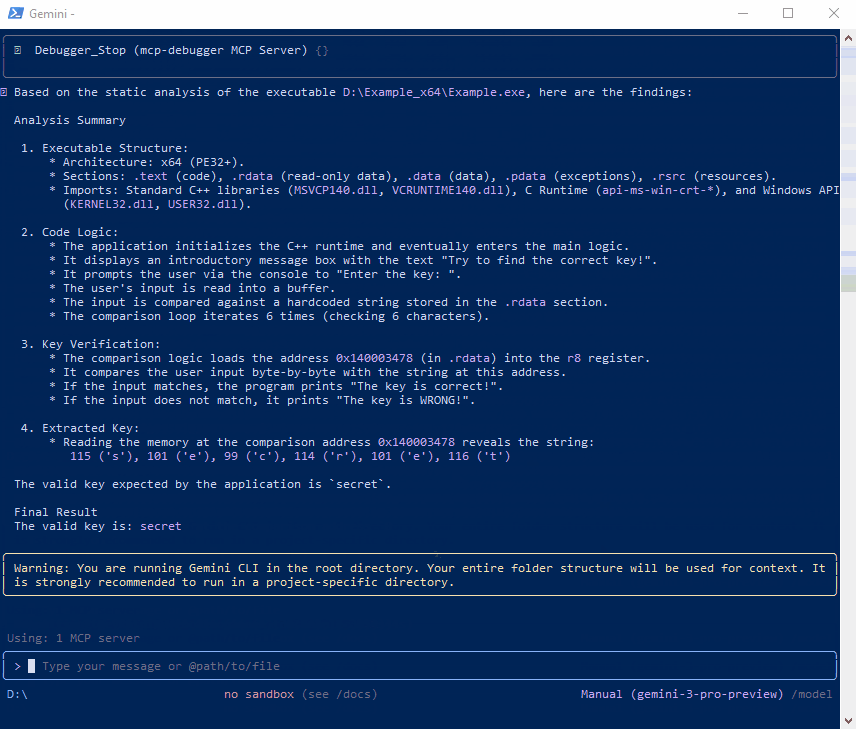
A MCP Debugger Server for Windows executables (x86 and x64). Exposes debugger functionality as MCP Tools for static / dynamic analysis of the…
ai-assisted-reversingbinary-analysisdebuggers+4
13
fatmike-gh/mcpdebuggerA MCP Debugger Server for Windows executables (x86 and x64). Exposes debugger functionality as MCP Tools for static / dynamic analysis of the…
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 darthton/blackbone
Windows memory hacking library
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
 mrexodia/dumpulator
An easy-to-use library for emulating memory dumps. Useful for malware analysis (config extraction, unpacking) and dynamic analysis in general…
 ohjeongwook/shellcodeemulator
Shellcode emulator written with Unicorn Framework With Process Dump Emulation Environment
 advdebug/brovan
User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…
 amossys/memitm
Tool to make in memory man in the middle
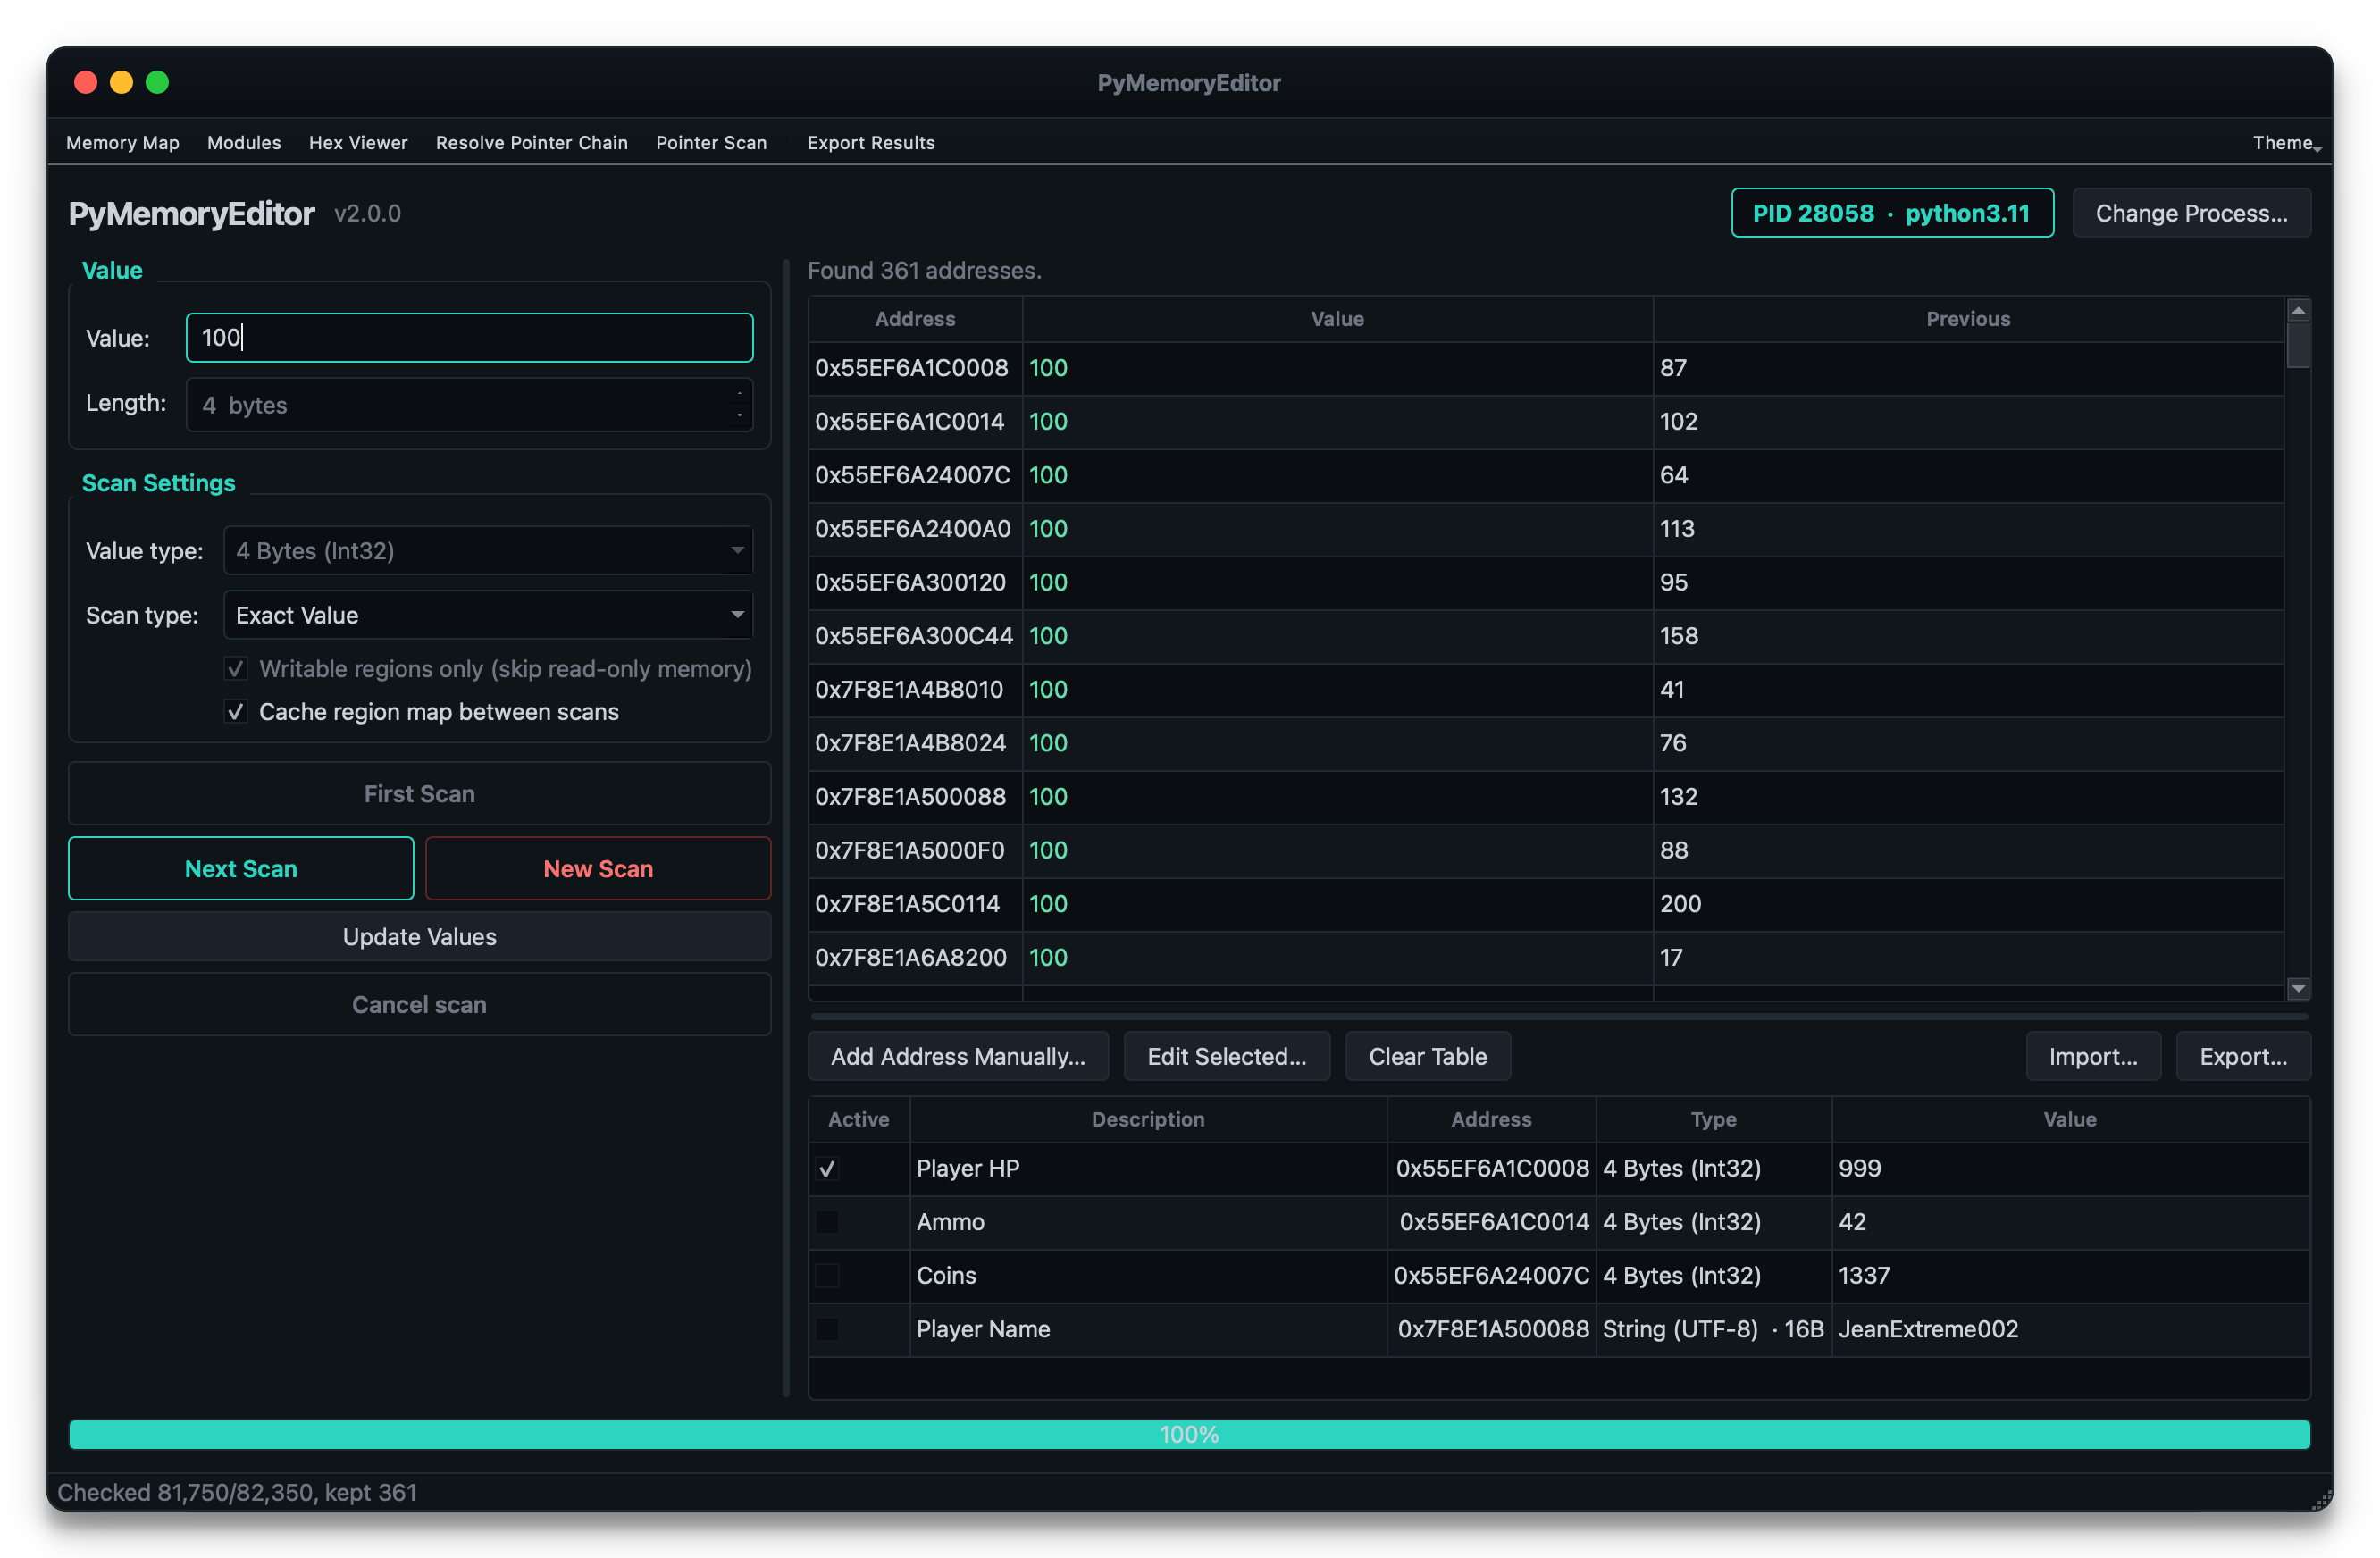 jeanextreme002/pymemoryeditor
A pure-Python library that lets you inspect, modify and search the memory of any running process in a few lines of Python :snake: .
 nickcano/xenoscan
Open source memory scanner written in C++
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
 ngwg/ceasta
disassembler, decompiler and debugger in one, with a built-in mcp server: point an ai at a binary and it can debug it, not just read it. ida-style…
 gaasedelen/patching
An Interactive Binary Patching Plugin for IDA Pro
 epi052/osed-scripts
bespoke tooling for offensive security's Windows Usermode Exploit Dev course (OSED)
 rizinorg/cutter
Free and Open Source Reverse Engineering Platform powered by rizin
 danigargu/heap-viewer
IDA Pro plugin to examine the glibc heap, focused on exploit development
 winterknife/evenstar
Intel 64/Windows low-level experiments