
CVE-2022-4510
 electr0sm0g/cve-2022-4510
Exploit for CVE-2022-4510 enabling remote command execution in Binwalk firmware analysis tool. Provides proof-of-concept code for security testing…
binary-analysisexploitationfirmware-analysis+2
9
electr0sm0g/cve-2022-4510Exploit for CVE-2022-4510 enabling remote command execution in Binwalk firmware analysis tool. Provides proof-of-concept code for security testing…

 ospg/binwalk
Firmware Analysis Tool
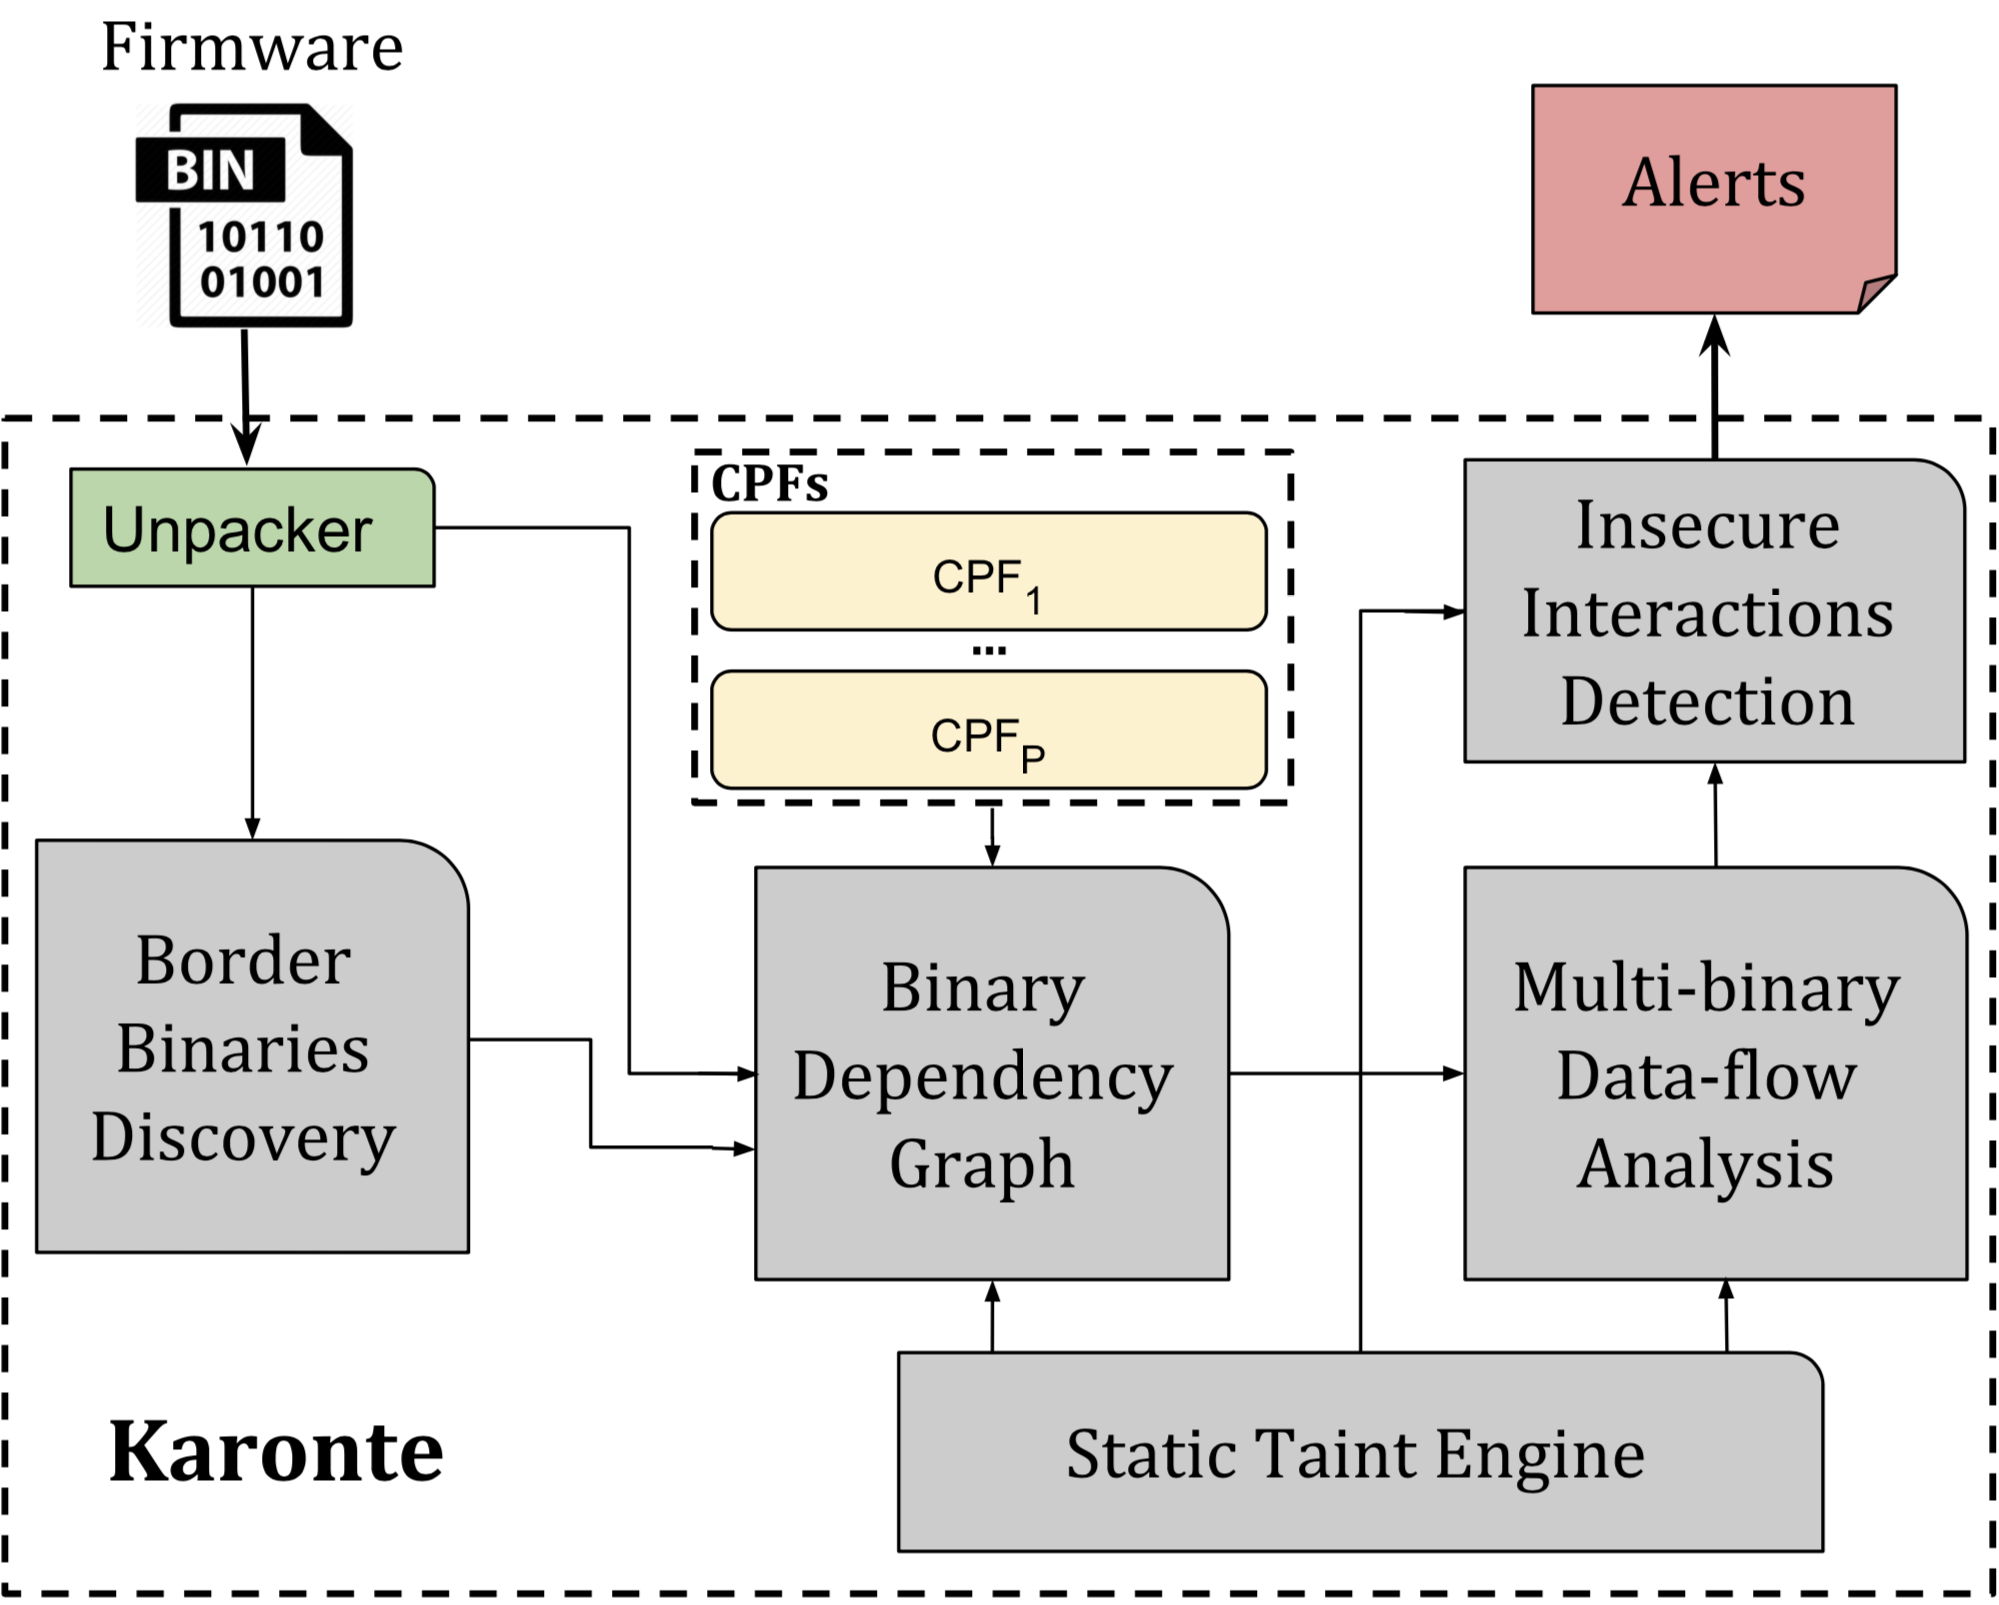 ucsb-seclab/karonte
Karonte is a static analysis tool to detect multi-binary vulnerabilities in embedded firmware
 yeggor/uefi_retool
A tool for UEFI firmware reverse engineering
 marin-m/vmlinux-to-elf
A tool to recover a fully analyzable .ELF from a raw kernel, through extracting the kernel symbol table (kallsyms)
 pagalaxylab/unifuzzer
A fuzzing tool for closed-source binaries based on Unicorn and LibFuzzer
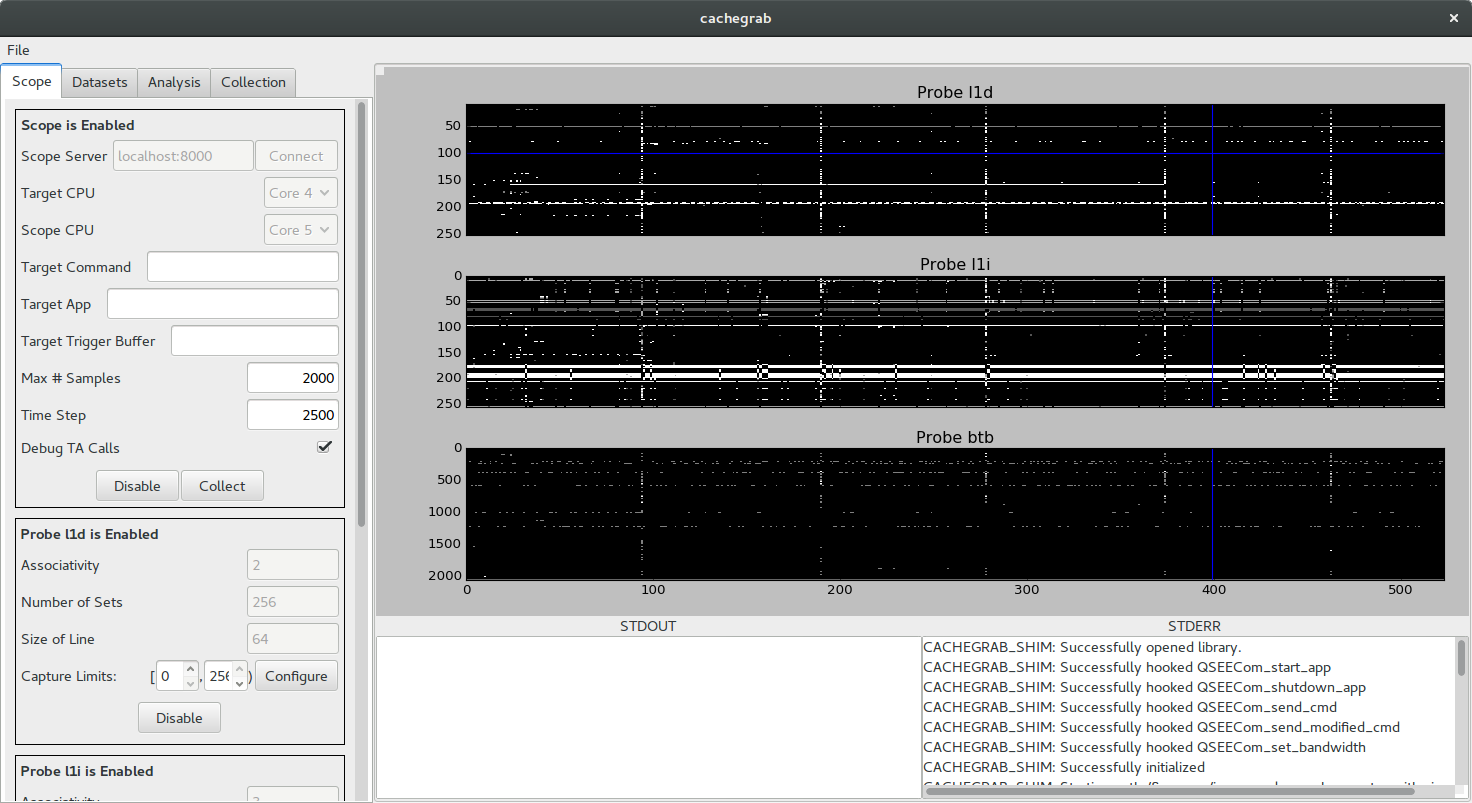 nccgroup/cachegrab
a tool designed to help perform and visualize trace-driven cache attacks against software in the secure world of TrustZone-enabled ARMv8 cores
 infobyte/draytek-arsenal
Reverse Engineering and Observability toolkit for Draytek firewalls
 jatinkapilaq1/intel-me-research
Talk to your Intel Management Engine directly — zero-dependency Python tool. Finds memory leaks, partition manifest, live MKHI probing. First public…
 finngineering/apxutil
A tool to manipulate Schneider Electric PLC archive files
 nikitapbst/cve-2019-6260
Low-level hardware debugging and security assessment tool for ASPEED BMC AHB interfaces. Probes PCIe, LPC, and UART interfaces to read/write…
 nccgroup/edidfuzzer
EDID (Enhanced Display Identification Data) Fuzzer
 ret5et/watchguard_webui_unpacker
Watchguard Sysa-dl file format
 rehints/efixplorer
IDA plugin and loader for UEFI firmware analysis and reverse engineering automation
 al3xtjames/ghidra-firmware-utils
Ghidra extension for PC firmware reverse engineering, providing loaders for PCI option ROMs, Intel Flash Descriptor, coreboot CBFS, and UEFI firmware…
 dsecurity/efiseek
Ghidra plugin that automates UEFI firmware analysis by identifying known GUIDs, protocols, SMI handlers, and interrupt functions, with headless…
 quarkslab/binbloom
Raw binary firmware analysis software