
CVE-2026-20805-PoC
 uzair-baig0900/cve-2026-20805-poc
The PoC of information disclosure in Microsoft Desktop Windows Management.
binary-analysisexploitationinformation-gathering+2
2
uzair-baig0900/cve-2026-20805-pocThe PoC of information disclosure in Microsoft Desktop Windows Management.
 csirttrizna/cve-2024-55587
Proof-of-concept exploit for CVE-2024-55587 in libarchive, demonstrating unsafe extraction via malicious ZIP files.
 sita-technologies/cve-2025-39247
HikCentral Professional - Pre-Auth License ActiveCode Leak
 idanshechter/cve-2017-13208-scanner
Python script using r2pipe to detect CVE-2017-13208 in Android libnetutils.so by checking for missing dhcp_size validation via static binary analysis.
 vorkampfer/pwnkit_safety_check
PwnKit (CVE-2021-4034) Safe Checker This tool performs read-only checks and does not attempt exploitation.
 13m0n4de/pngcheck-vulns
A repository of proof-of-concept files demonstrating disclosed and patched vulnerabilities in pngcheck (2.4.0 - 3.0.1), including CVE-2020-27818,…
 20urc3/sekiryu
Comprehensive toolkit for Ghidra headless.
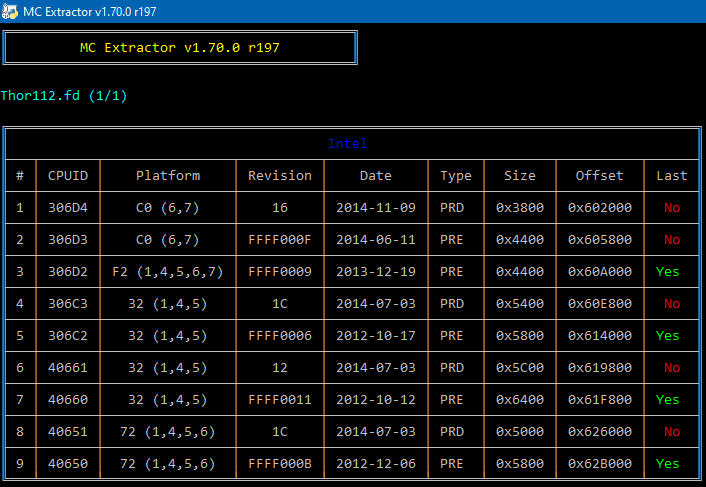 platomav/mcextractor
Intel, AMD, VIA & Freescale Microcode Extraction Tool
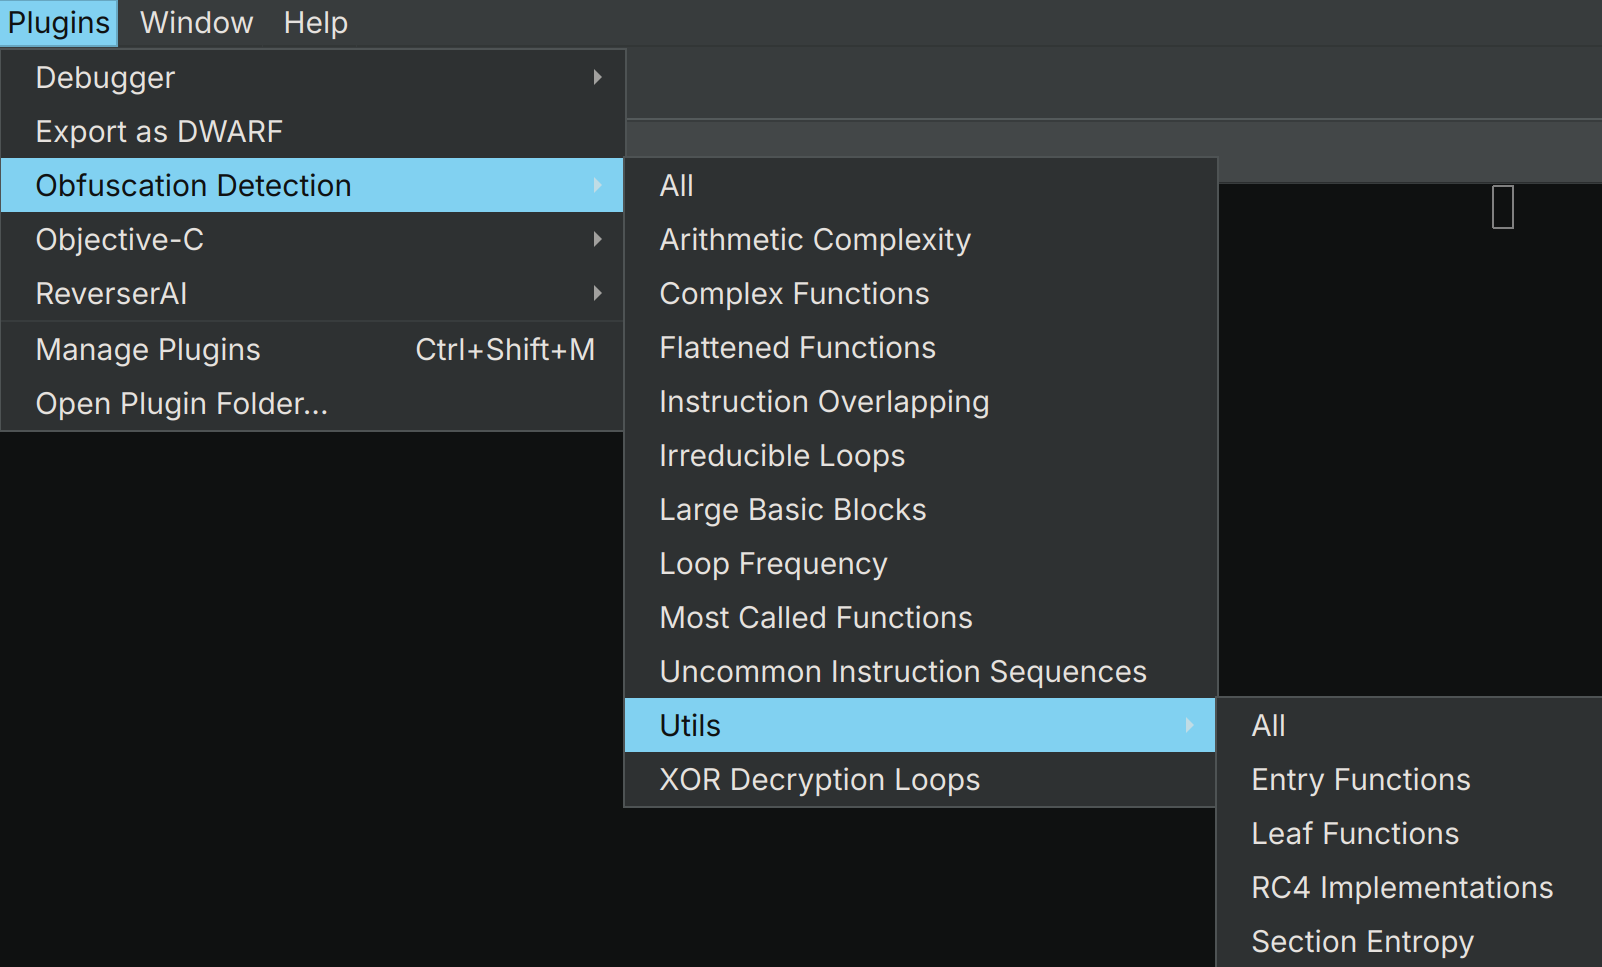 mrphrazer/obfuscation_detection
Binary Ninja plugin to identify obfuscated code and other interesting code constructs
 cmu-sei/kaiju
CERT Kaiju is a binary analysis framework extension for the Ghidra software reverse engineering suite. This repository is a "mirror" -- please file…
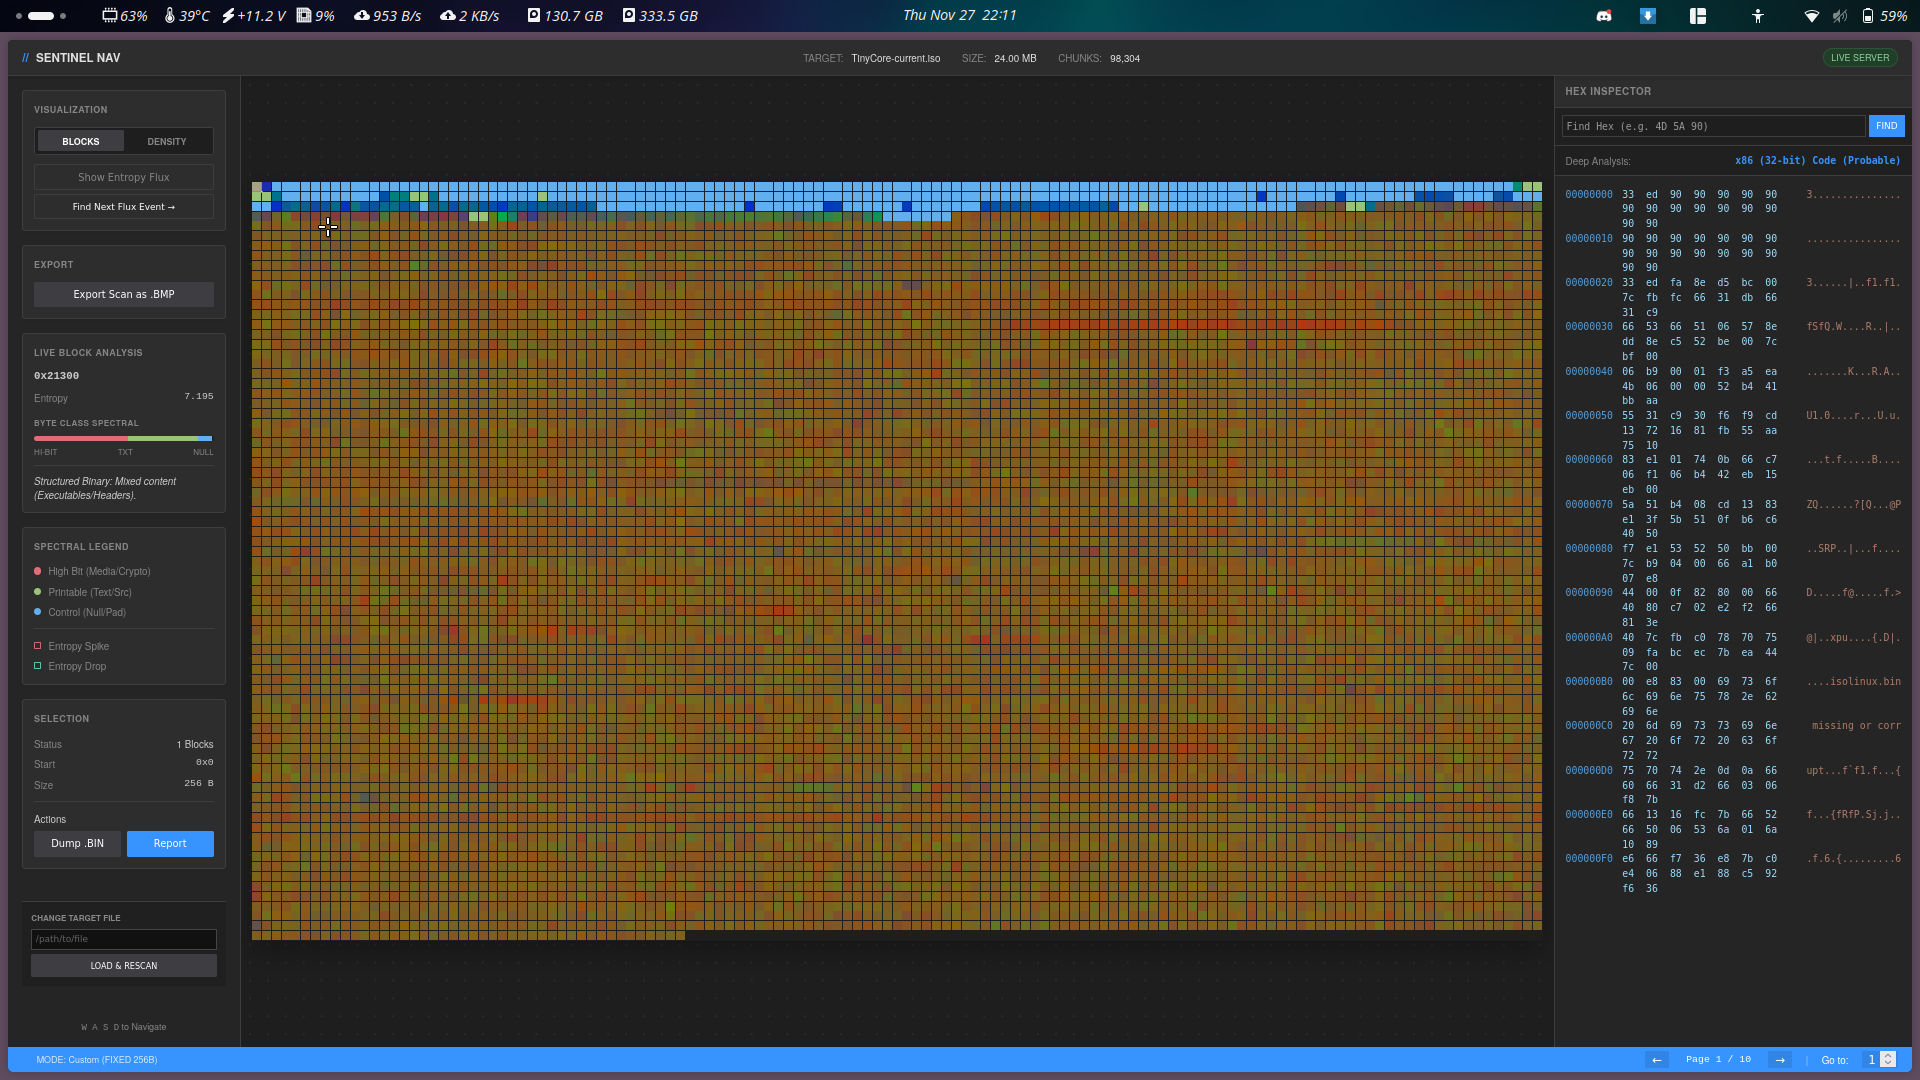 smolfiddle/sentinelnav
SentinelNav: zero-dependency, pure Python binary visualization and forensics tool.
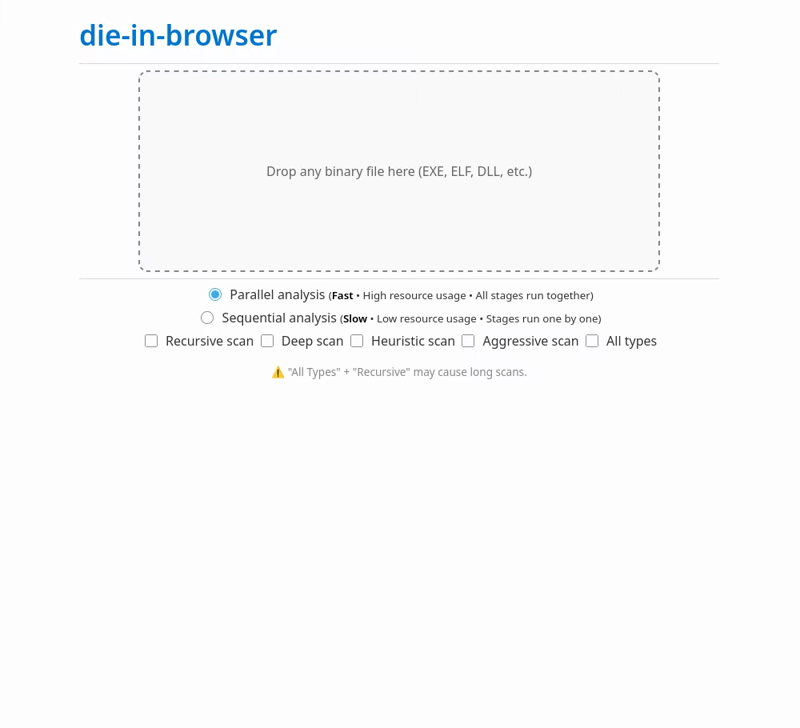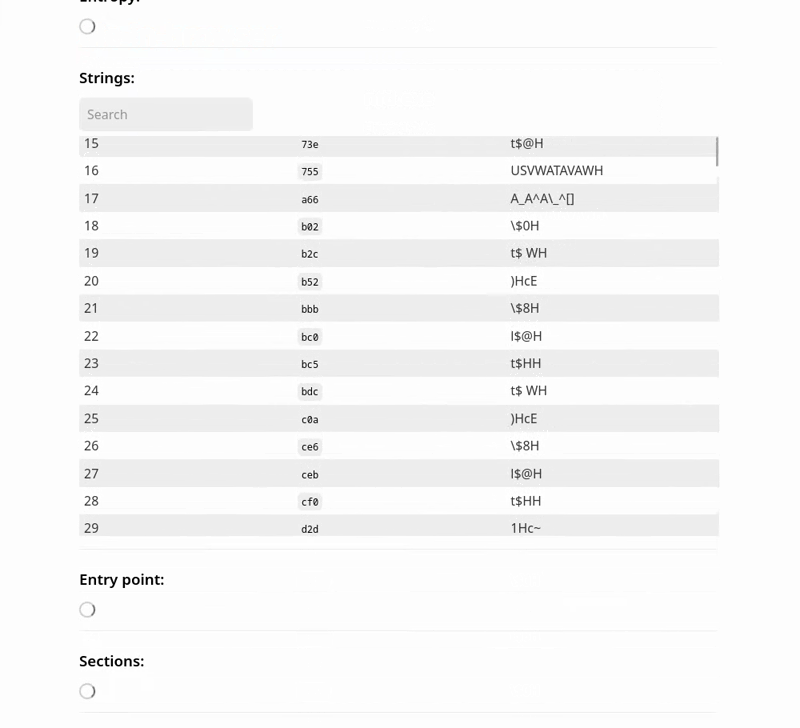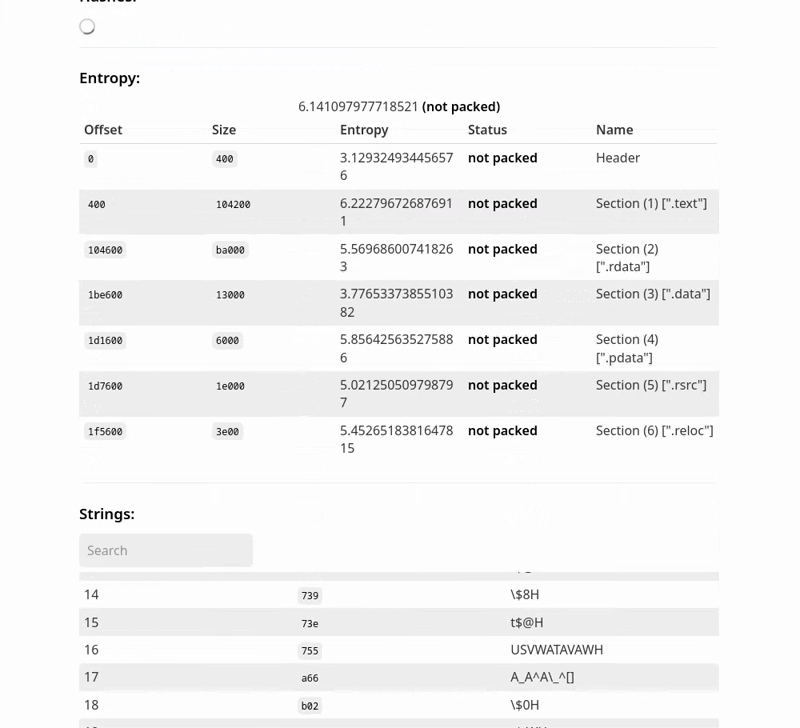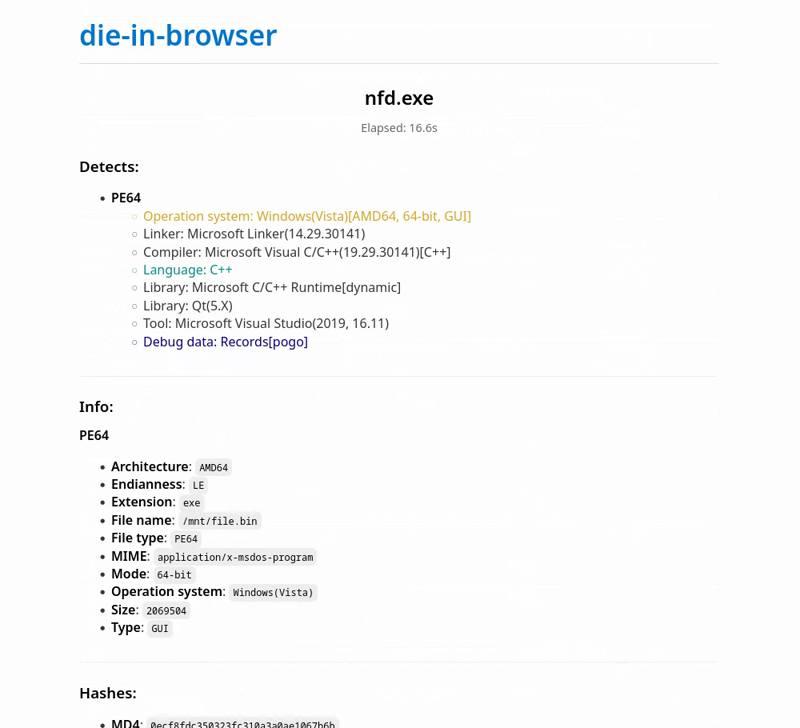 xoreaxlmbdx/die-in-browser
Static binary analysis with Detect It Easy — 100% in your browser, no uploads.
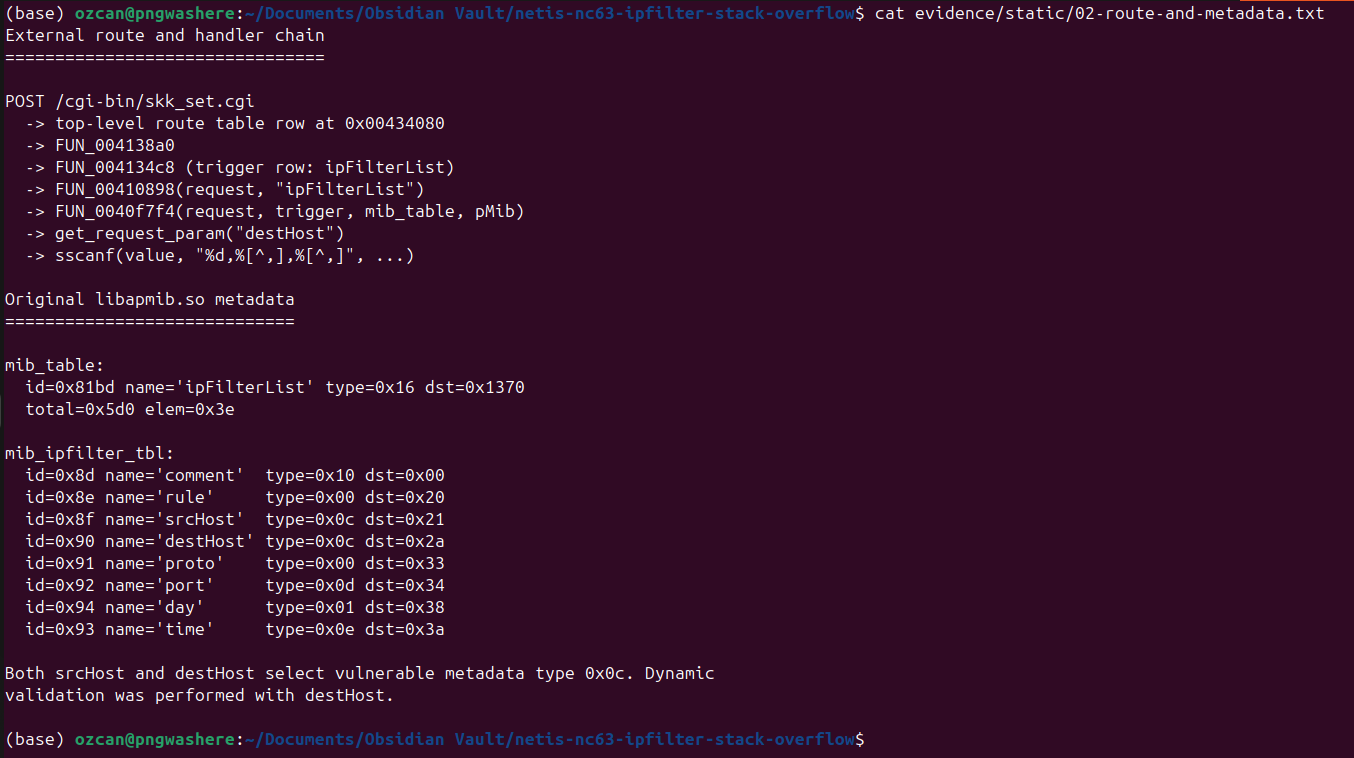 ozcanpng/cve-2026-76071
Original research and PoC for a pre-auth stack buffer overflow via unbounded sscanf scanset in the Netis NC63 ipFilterList handler
 tobss8/gigabyte-h510m-k-v2-bios-smm-reverse-engineering-cve-2025-7026-7027-7028-7029-research
Static reverse-engineering of a GIGABYTE H510M K V2 (`H510MKV2.F3`) BIOS image: full UEFI firmware-volume extraction analysis of the PI-spec SMM Core…