
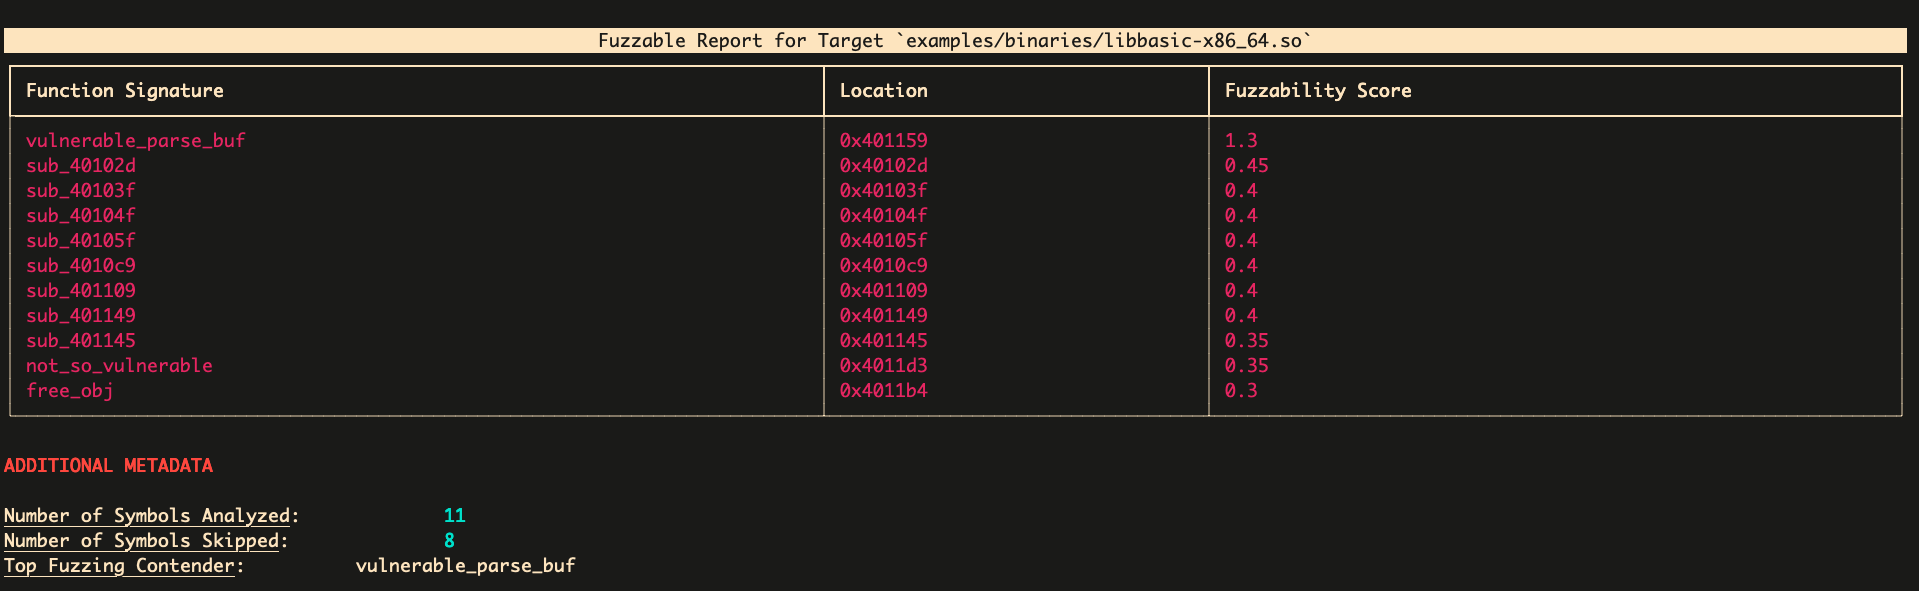
fuzzable
 ex0dus-0x/fuzzable
Static analysis framework that identifies fuzzable function targets in source code and binaries, generates harness templates, and integrates with…
binary-analysisfuzzingreverse-engineering+2
549
ex0dus-0x/fuzzableStatic analysis framework that identifies fuzzable function targets in source code and binaries, generates harness templates, and integrates with…
 cerbersec/ares
Project Ares is a Proof of Concept (PoC) loader written in C/C++ based on the Transacted Hollowing technique
 allthingsida/idasql
Vibe Reverse Engineer with IDA SQL: An interface for IDA in SQL via live virtual tables
 antonin-deniau/cave_miner
Search for code cave in all binaries
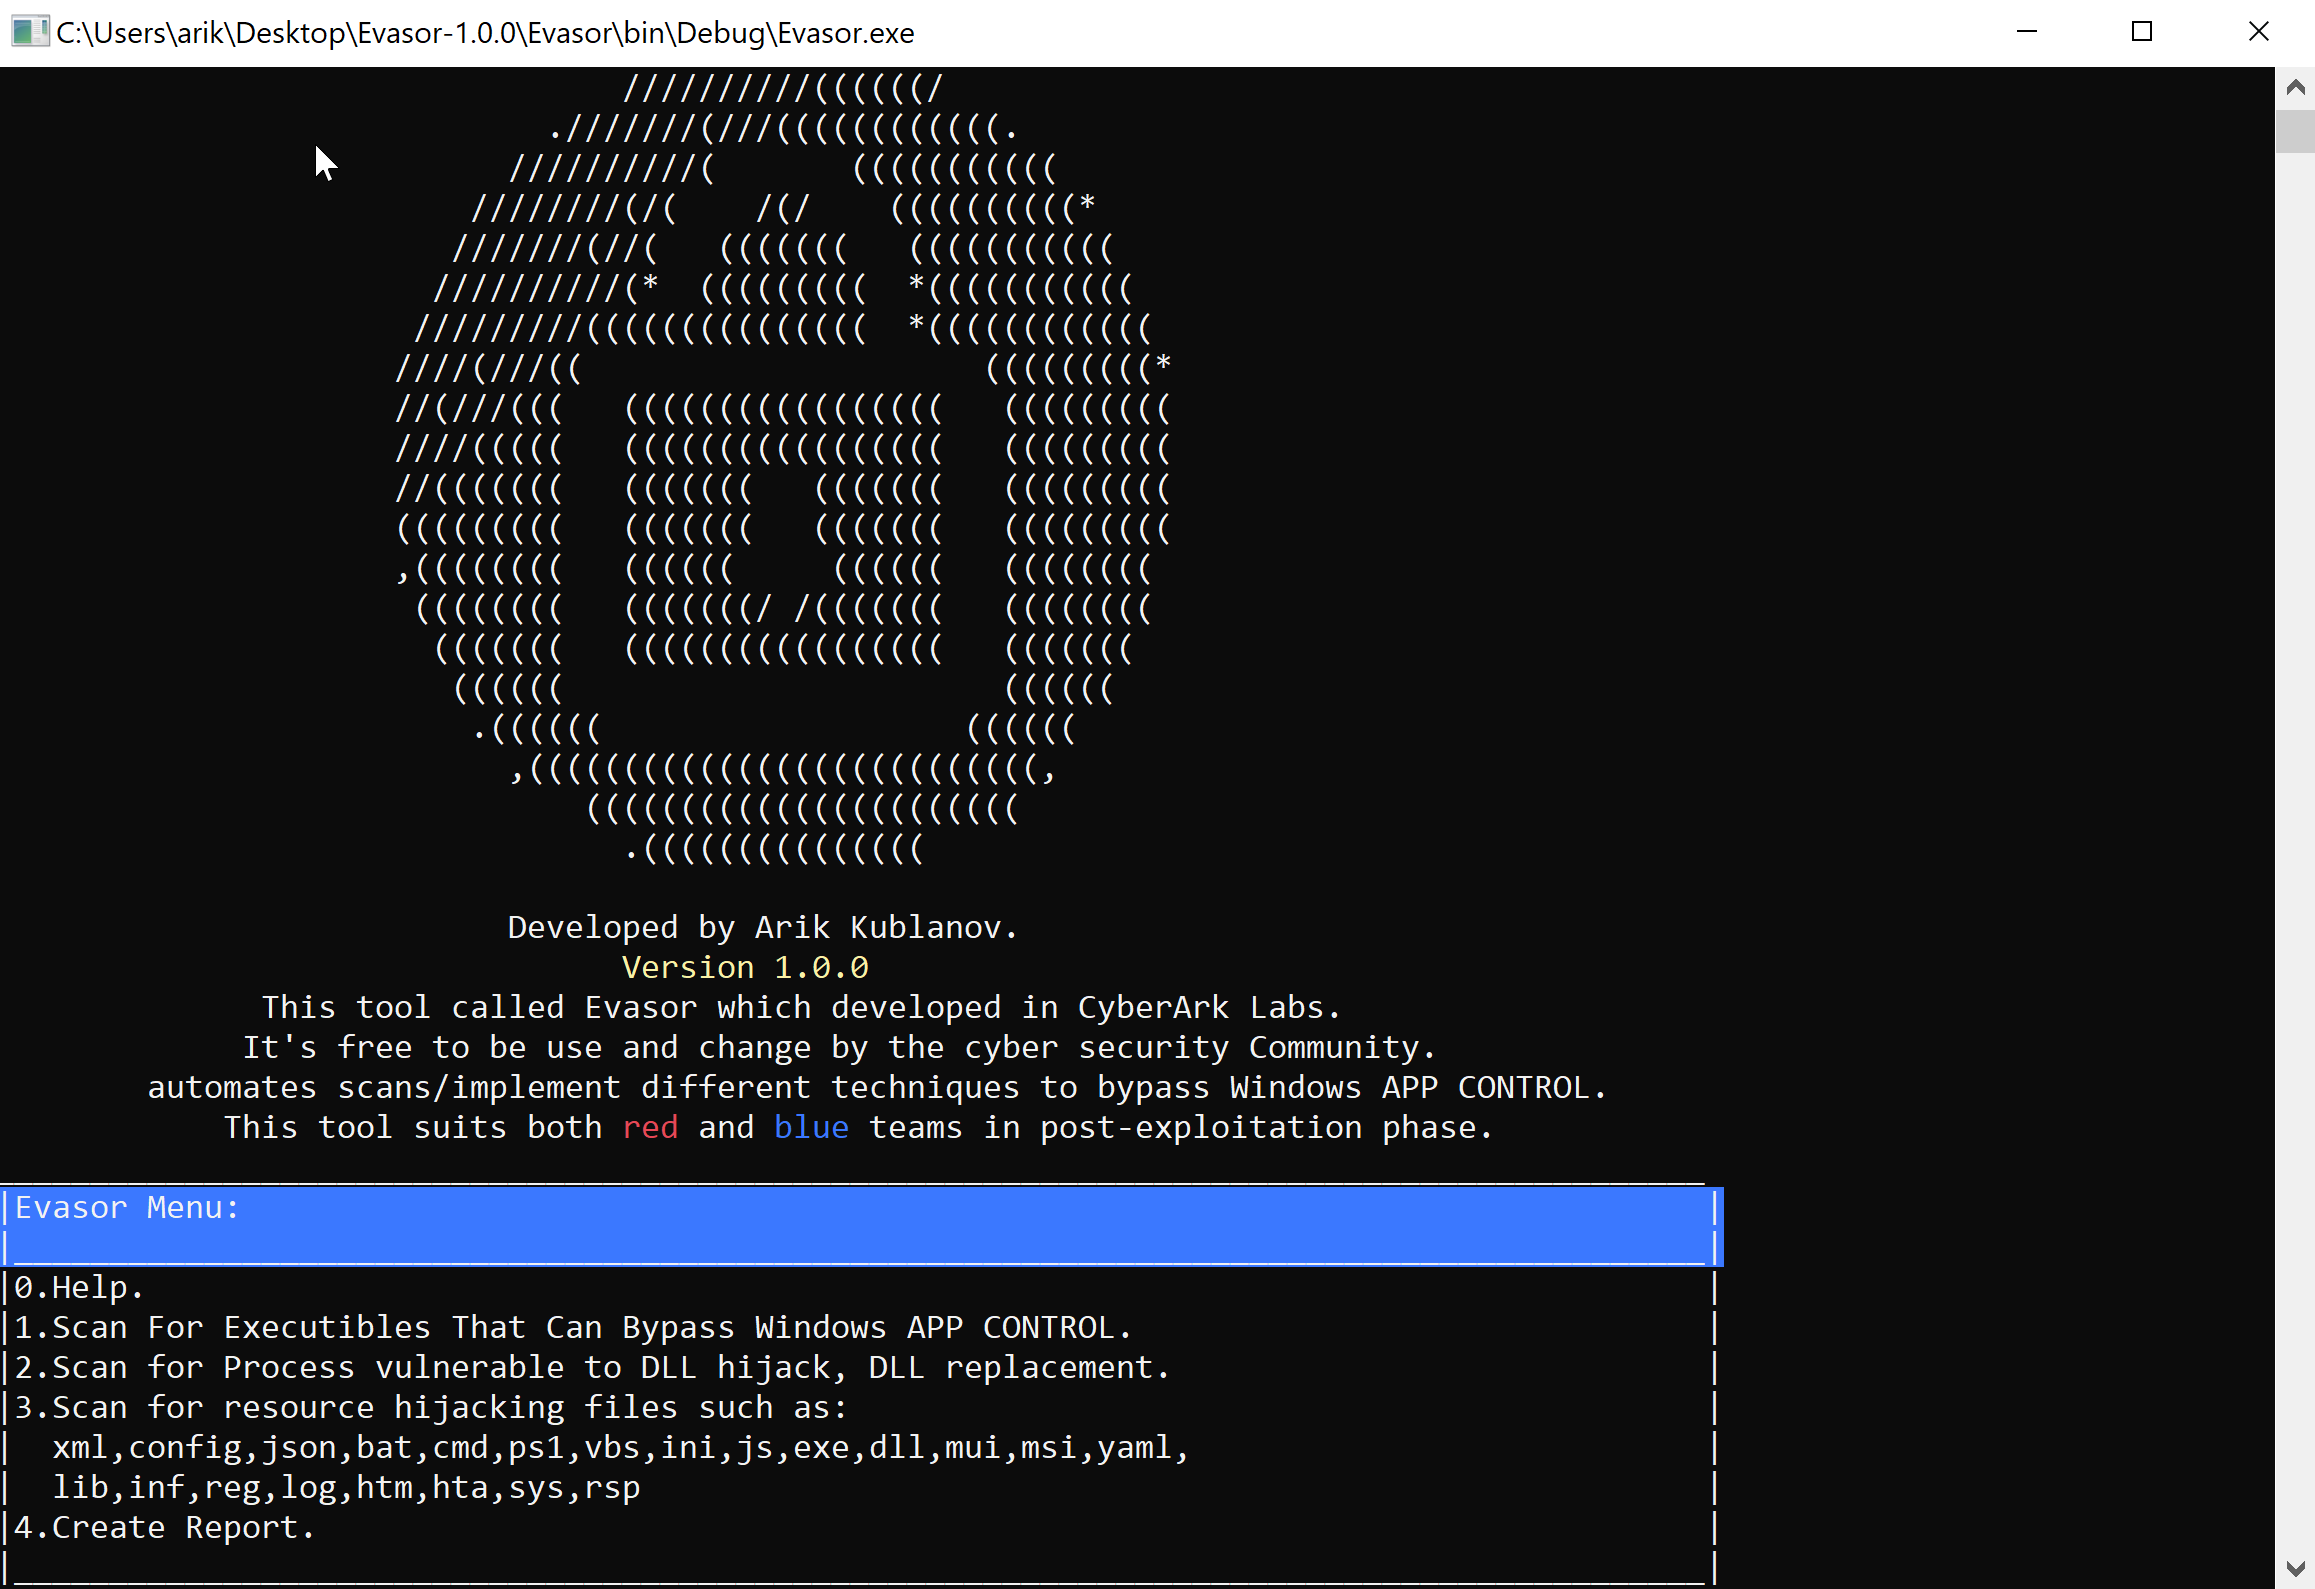 cyberark/evasor
A tool to be used in post exploitation phase for blue and red teams to bypass APPLICATIONCONTROL policies
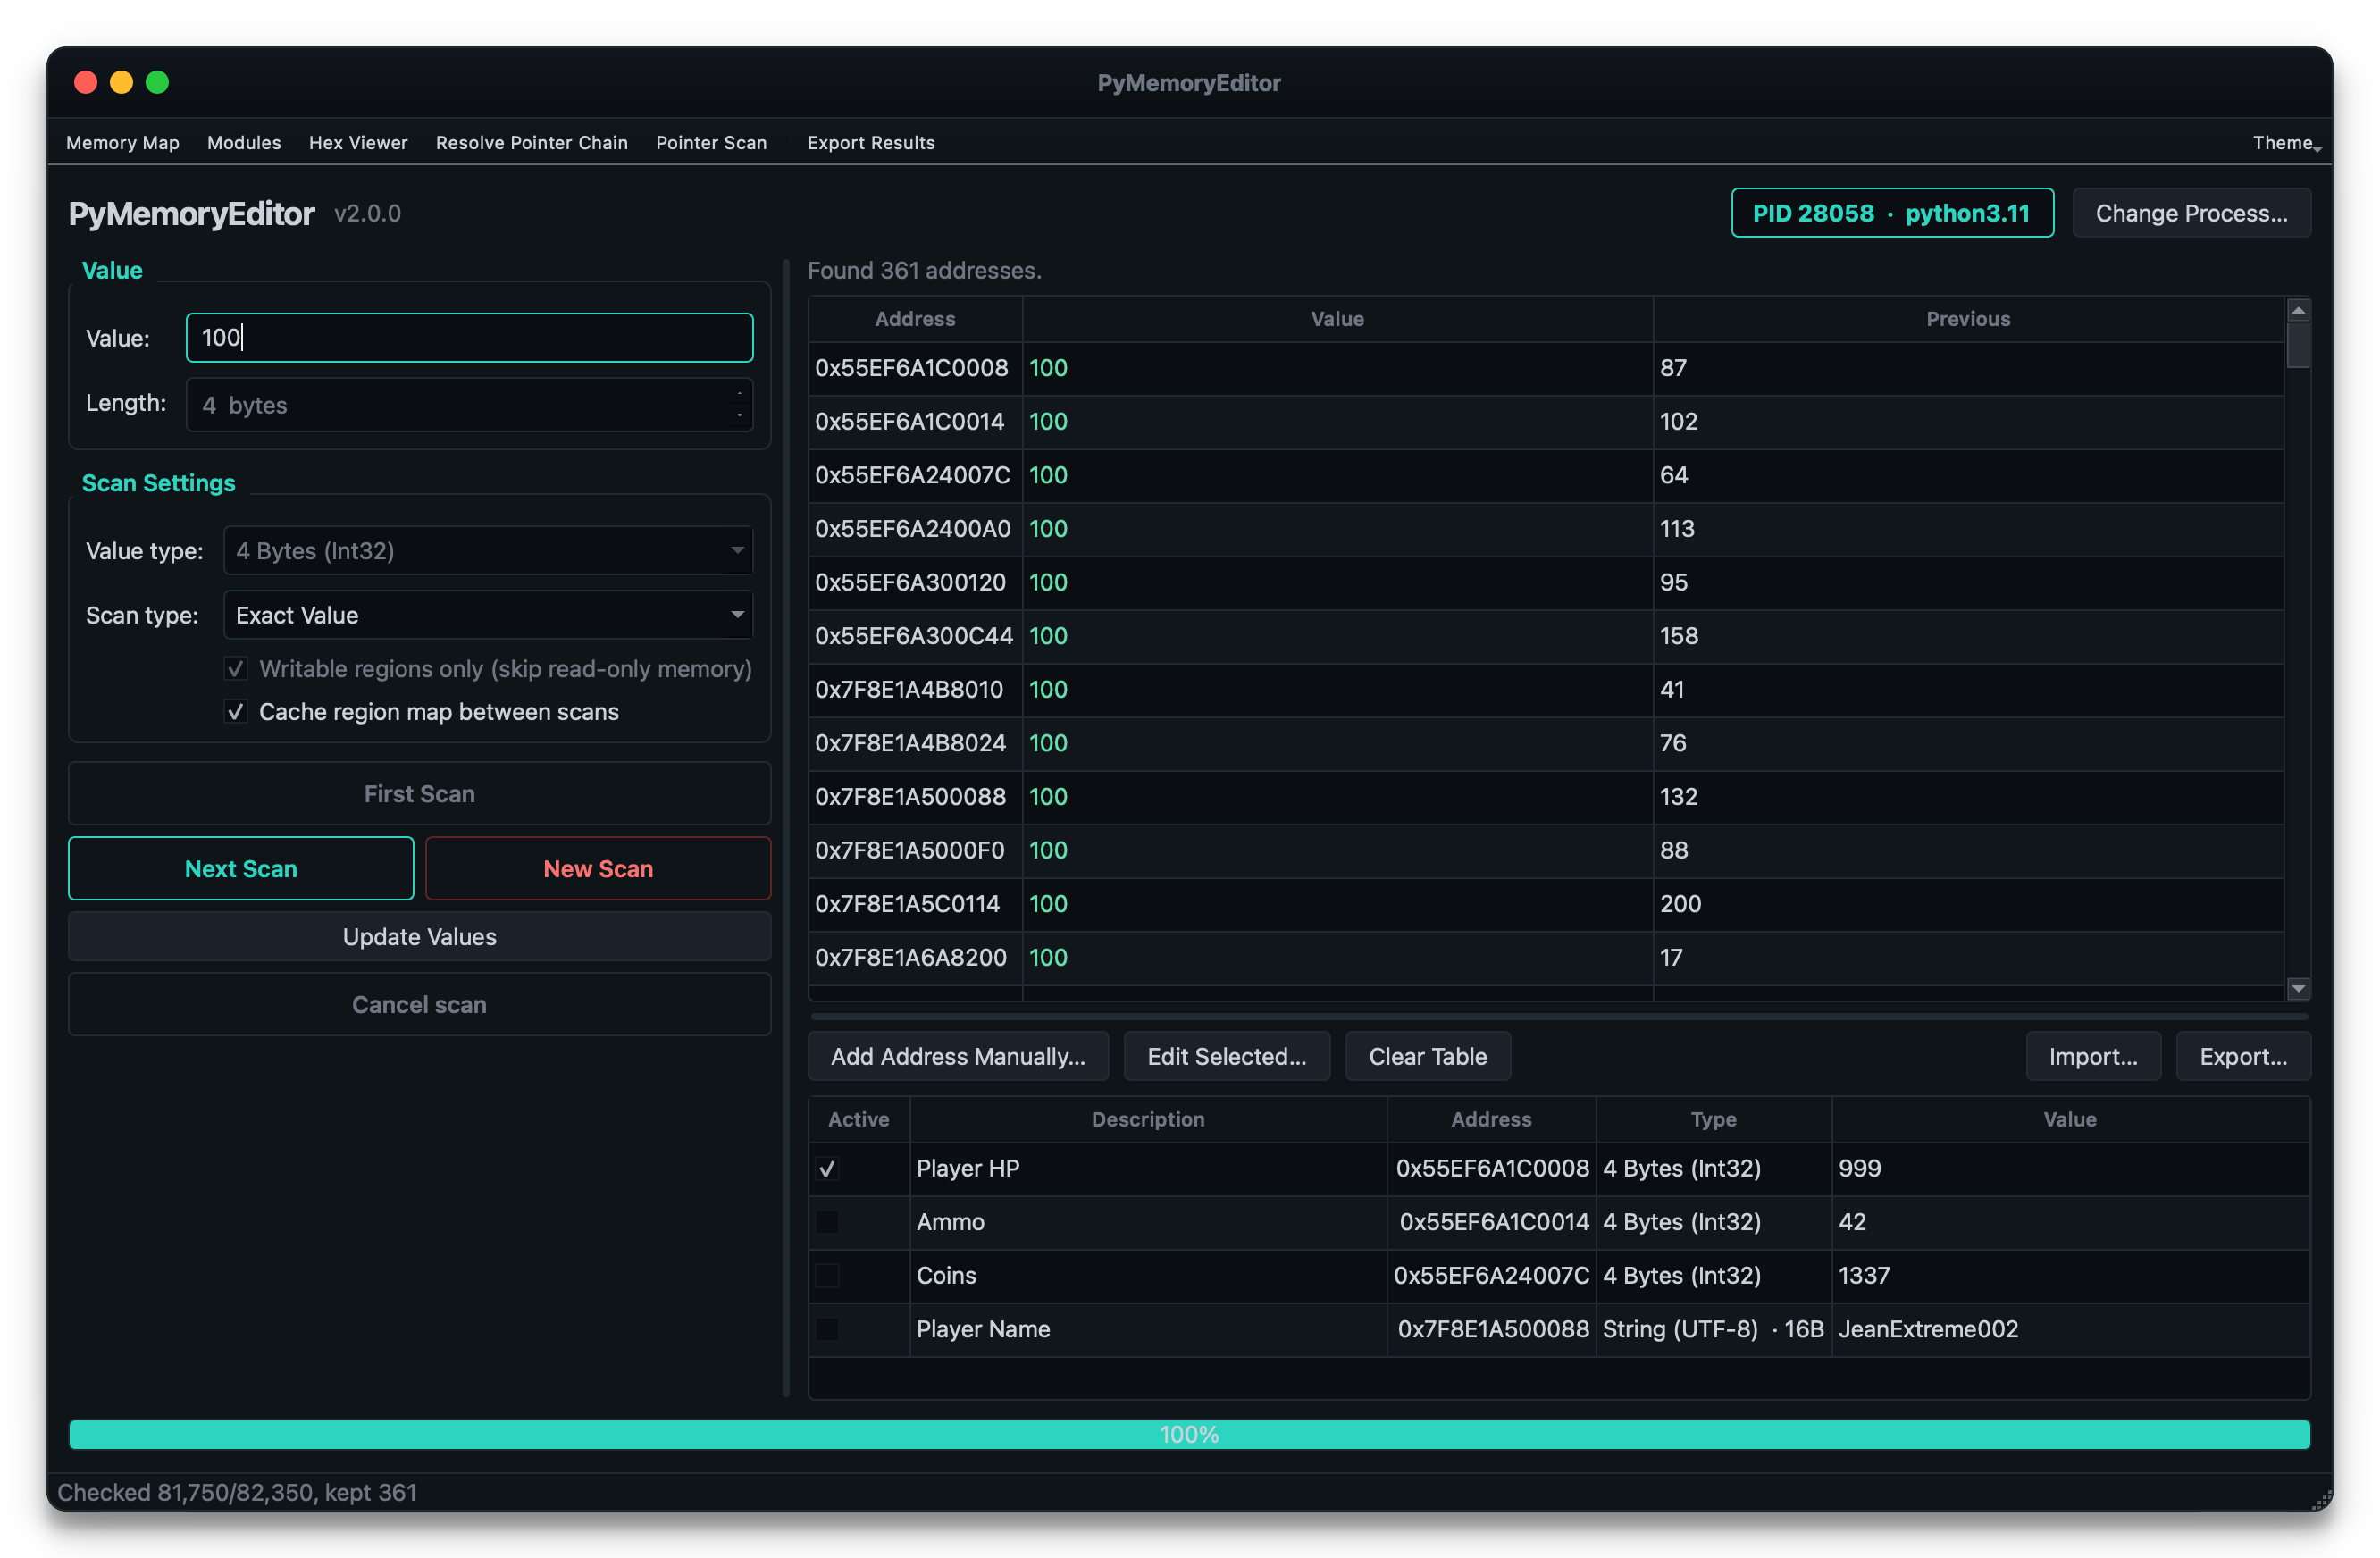 jeanextreme002/pymemoryeditor
A pure-Python library that lets you inspect, modify and search the memory of any running process in a few lines of Python :snake: .
 mistymntncop/cve-2023-4863
Proof-of-concept for CVE-2023-4863, a heap buffer overflow in WebP image decoding. Demonstrates the code_lengths trigger mechanism discovered by…
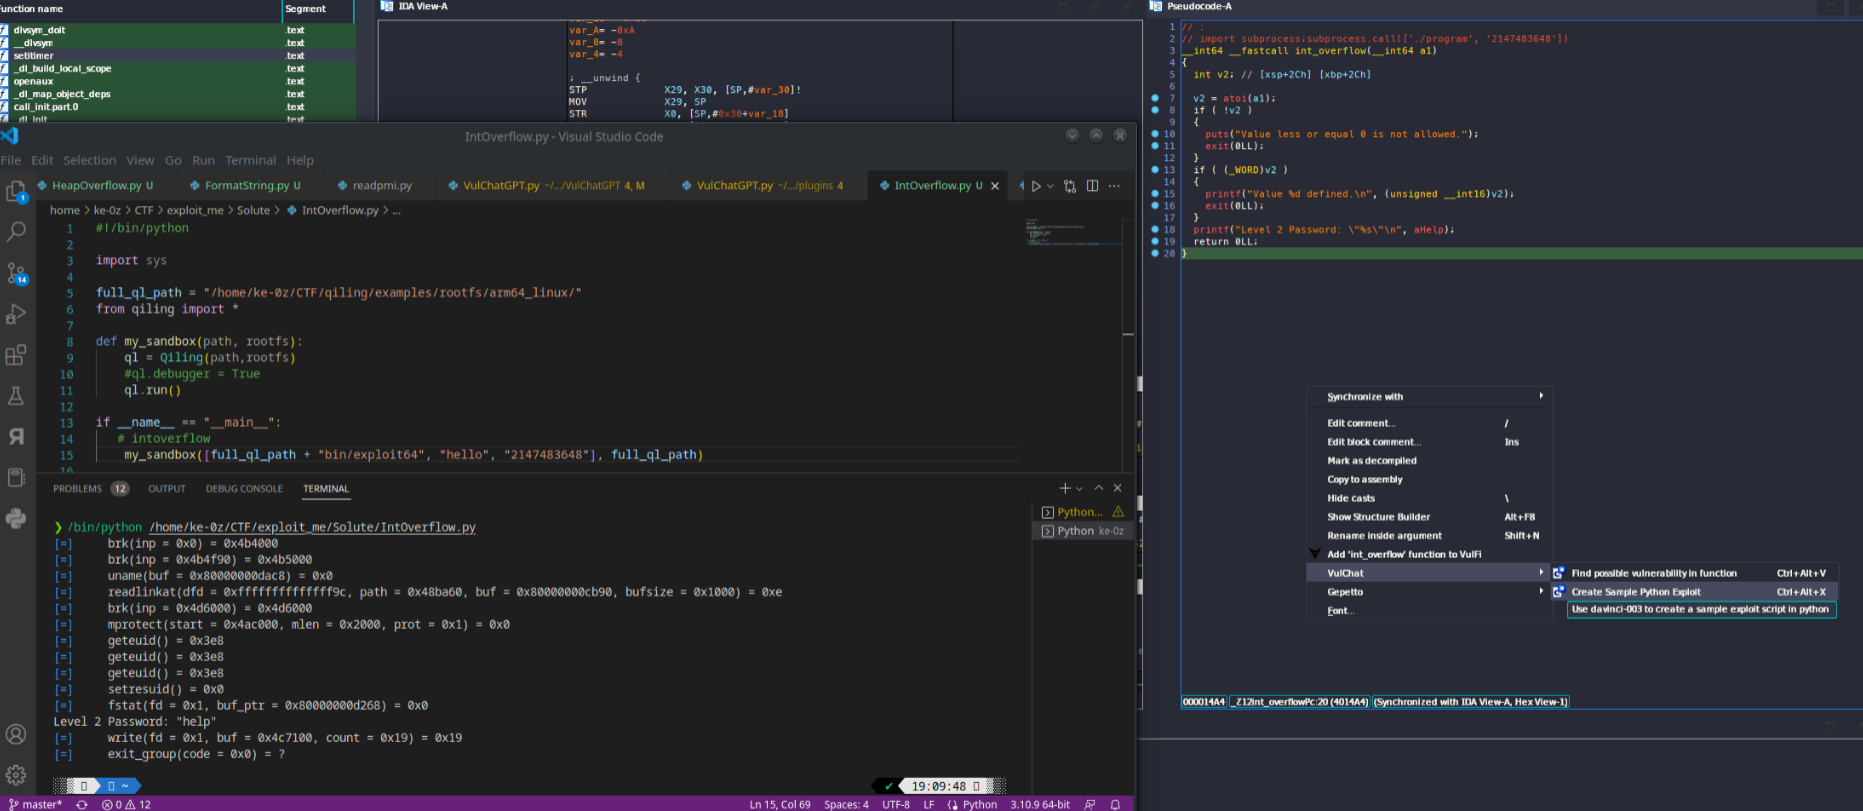 ke0z/binaivulhunter
Use IDA PRO HexRays decompiler with OpenAI(ChatGPT) to find possible vulnerabilities in binaries
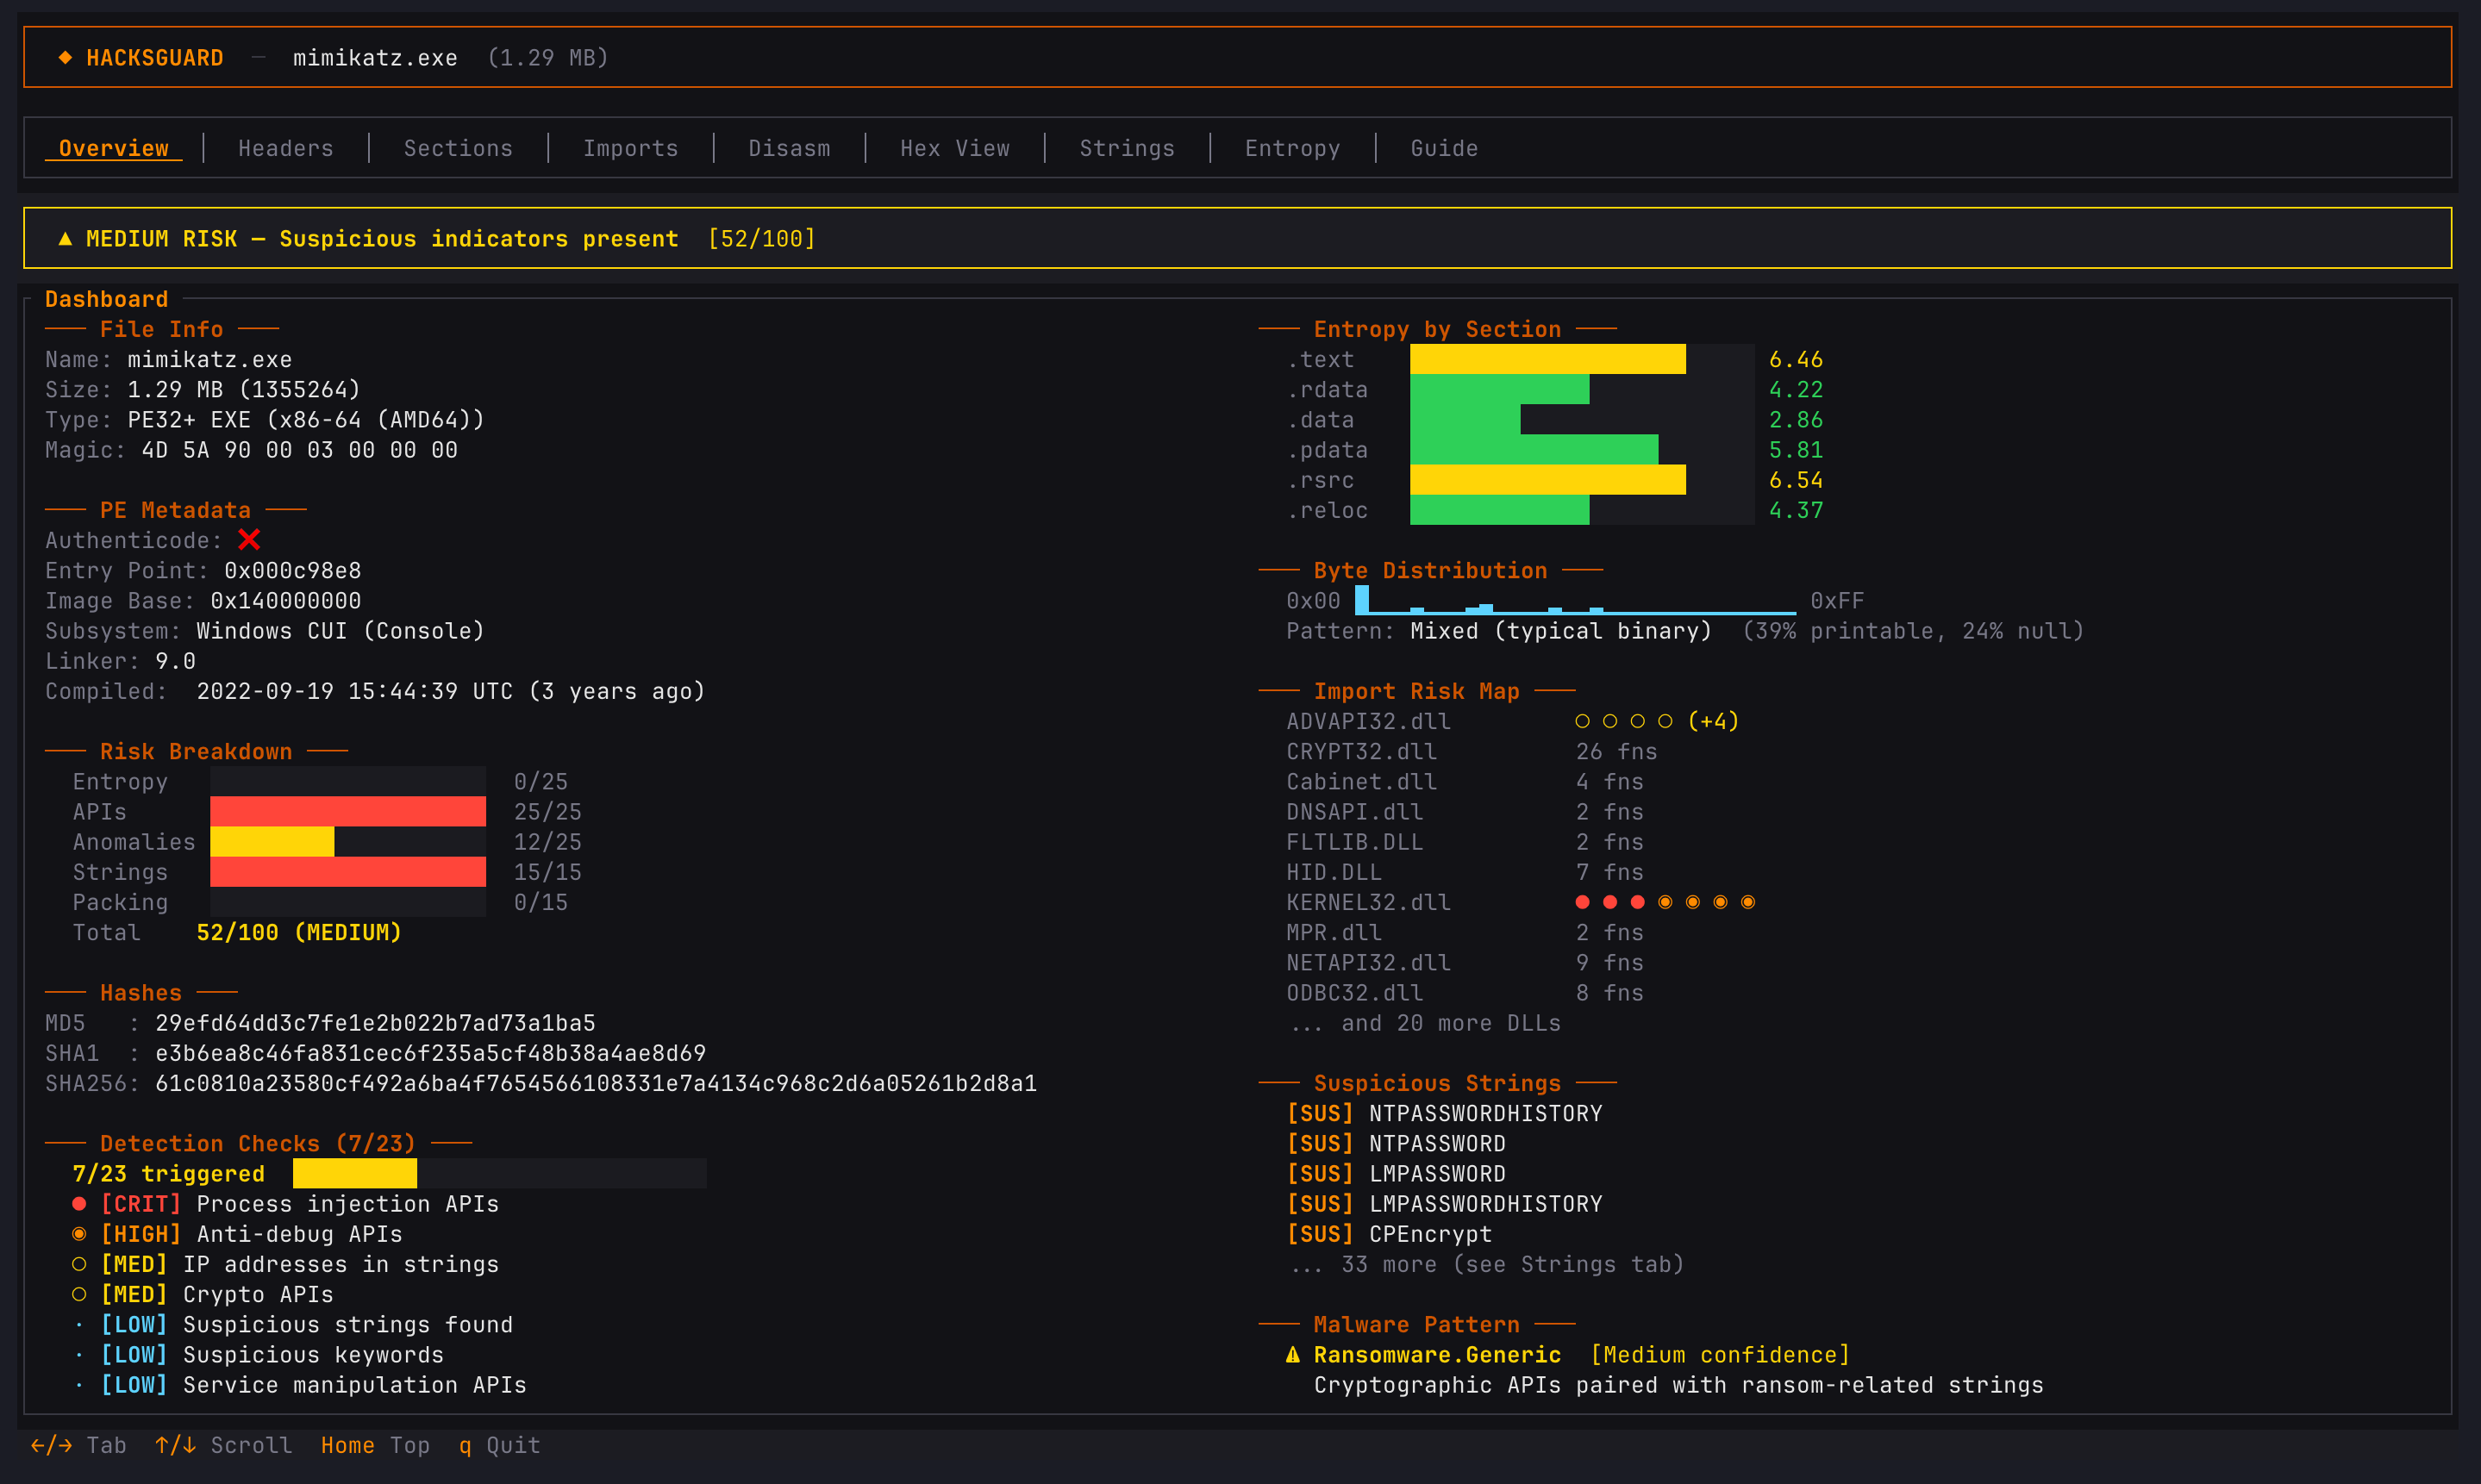 rhacknarok/hacksguard
A blazingly fast, multi-threaded TUI malware analysis tool built in Rust. Features deep PE parsing, YARA scanning, and heuristic risk scoring.
 colmmacc/cve-2022-3602
Technical deep-dive and anti-POC for CVE-2022-3602, a punycode buffer overflow in OpenSSL 3.0.x, with reproduction scripts, stack analysis, and…
 binarly-io/fwhunt
The Binarly Firmware Hunt (FwHunt) rule format was designed to scan for known vulnerabilities in UEFI firmware.
 battelle/repsych
Psychological warfare in reverse engineering
 seemoo-lab/polypyus
Binary-only firmware historian that learns to locate functions in raw binaries by extracting known functions from similar binaries, enabling fast…
 amossys/memitm
Tool to make in memory man in the middle
 advdebug/brovan
User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…
 zznop/sploit
Go package that aids in binary analysis and exploitation
 galoisinc/mate
Interactive program analysis suite using Code Property Graphs to hunt for bugs in C and C++ code, unifying application-specific and low-level…
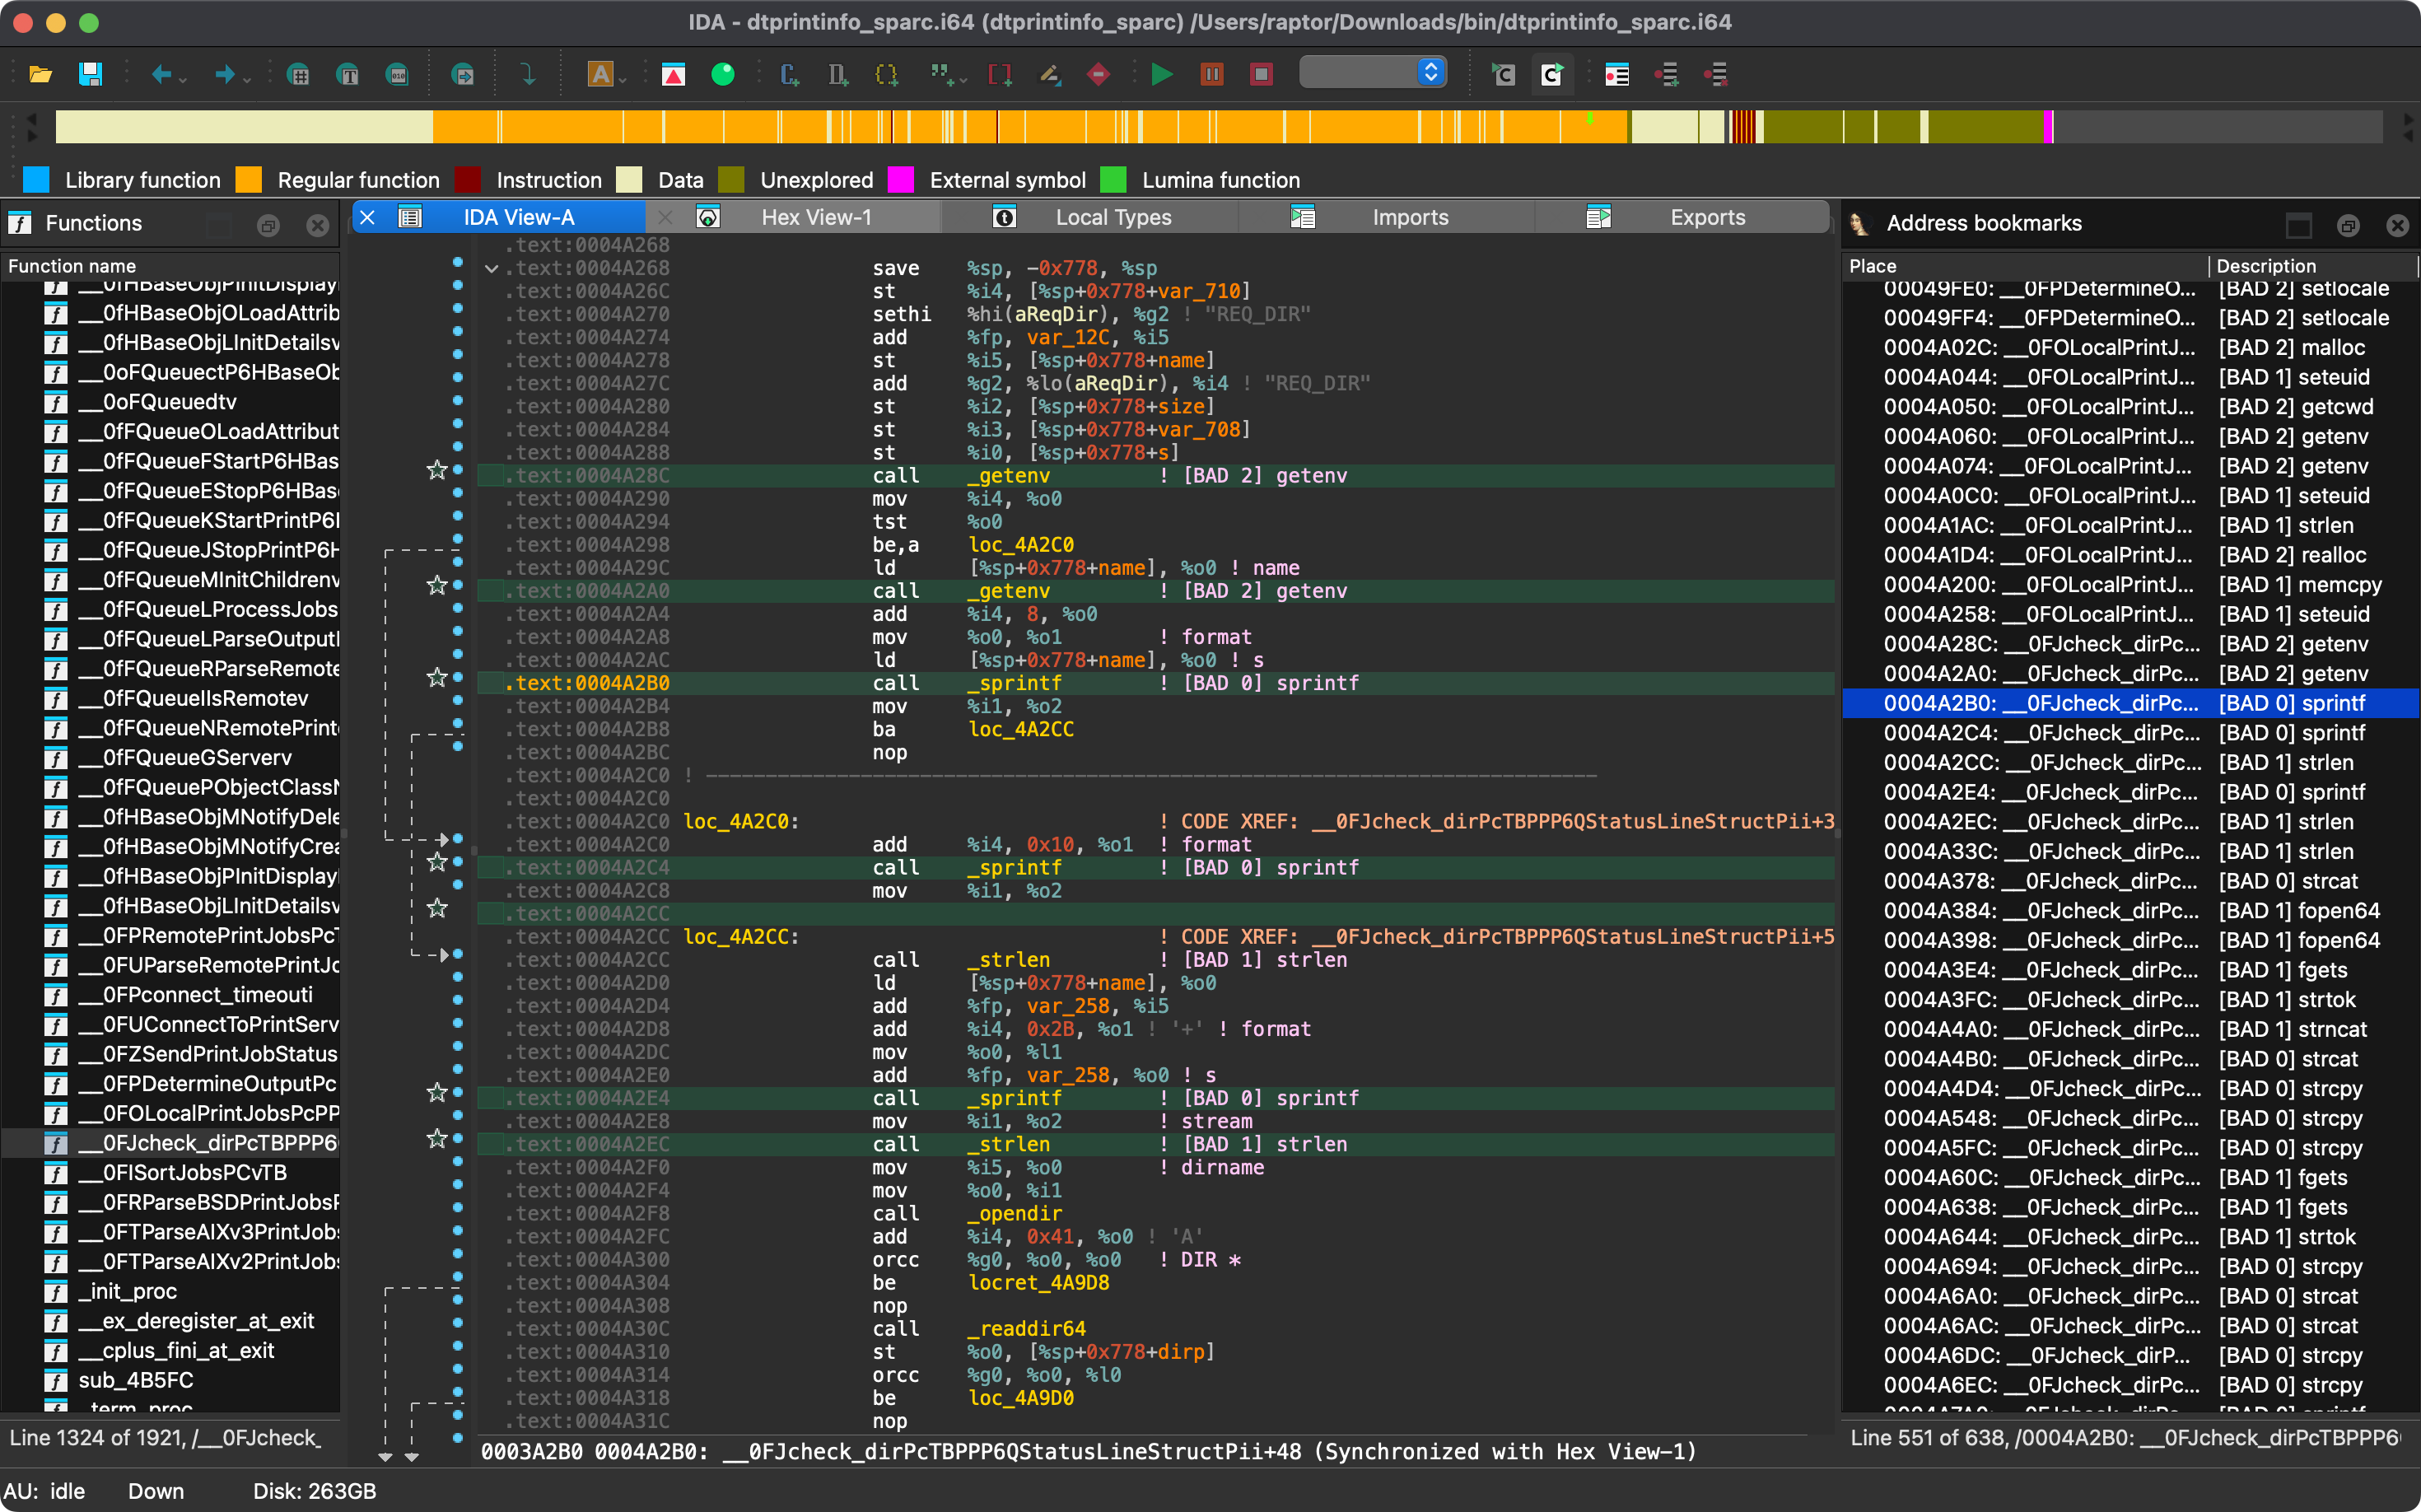 0xdea/rhabdomancer
Vulnerability research assistant that locates calls to potentially insecure API functions in a binary file.