

CyberStrikeAI
 ed1s0nz/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
ai-securitybinary-analysiscloud-security+9
7.2k
ed1s0nz/cyberstrikeaiThe system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 aipentest/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 dnspyex/dnspy
Unofficial revival of the well known .NET debugger and assembly editor, dnSpy
 unicorn-engine/unicorn
Unicorn CPU emulator framework (ARM, AArch64, M68K, Mips, Sparc, PowerPC, RiscV, S390x, TriCore, X86)
 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.
 lauriewired/ghidramcp
MCP Server for Ghidra

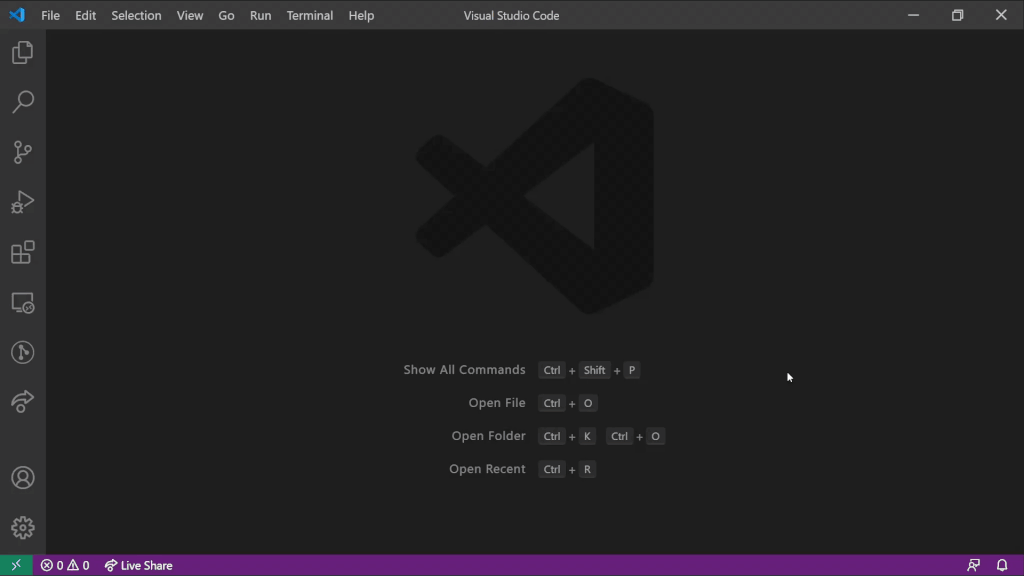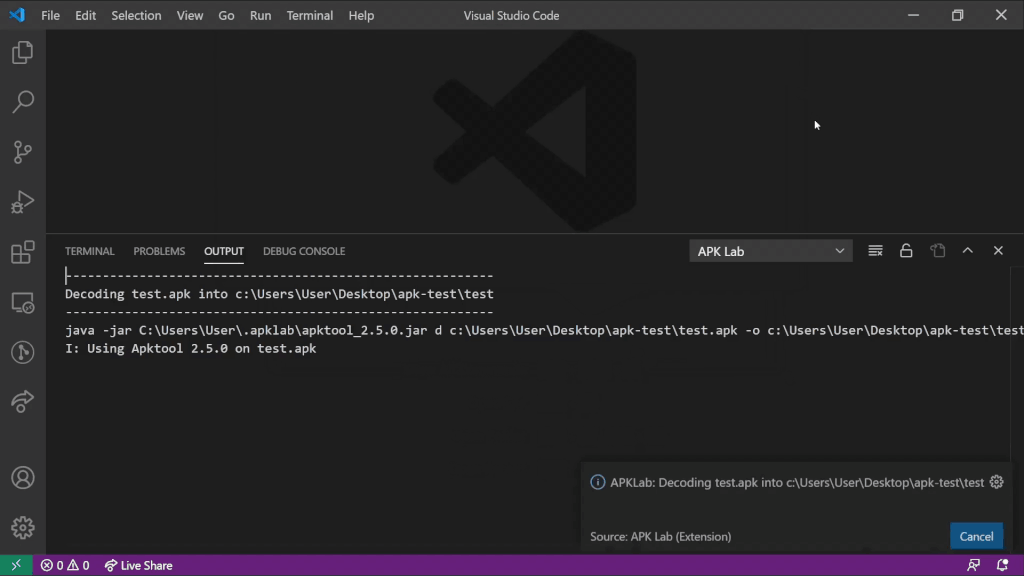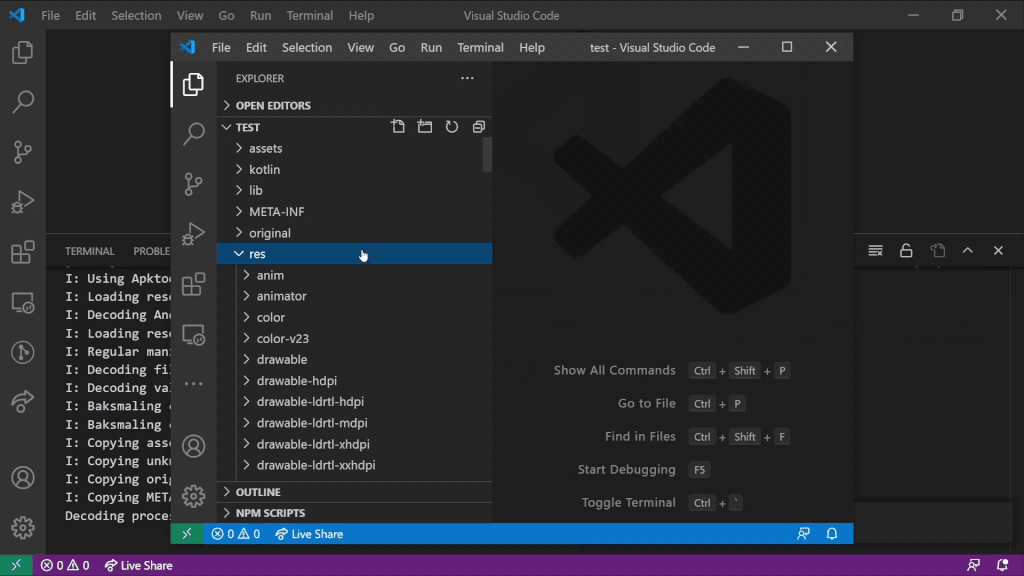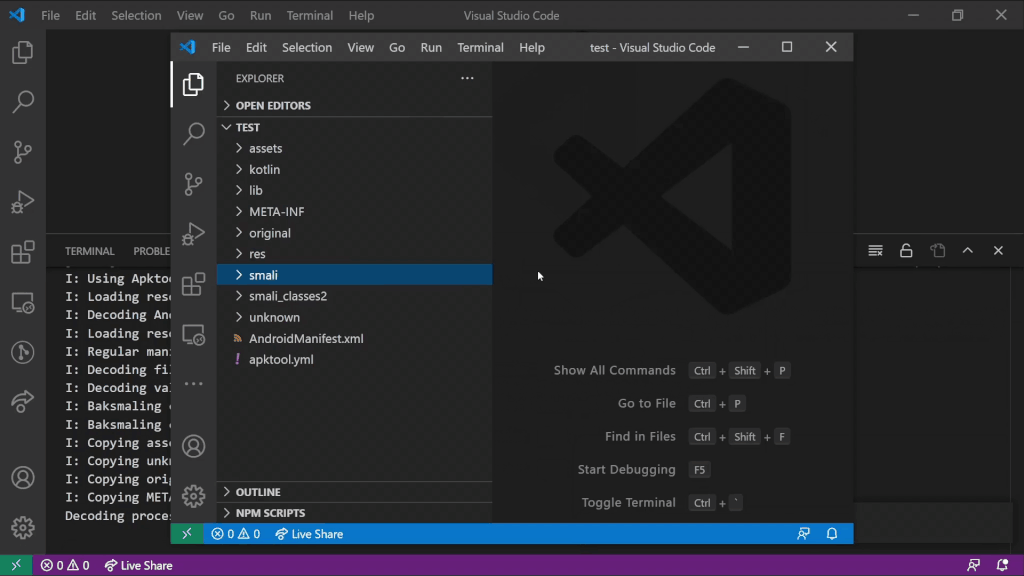 apklab/apklab
Android Reverse-Engineering Workbench for VS Code
 trustedsec/coffloader
Run Beacon Object Files (BOFs) outside Cobalt Strike by parsing 64-bit COFF object files, with Beacon-compatible argument generation and helper…
 endgameinc/xori
Xori is an automation-ready disassembly and static analysis library for PE32, 32+ and shellcode
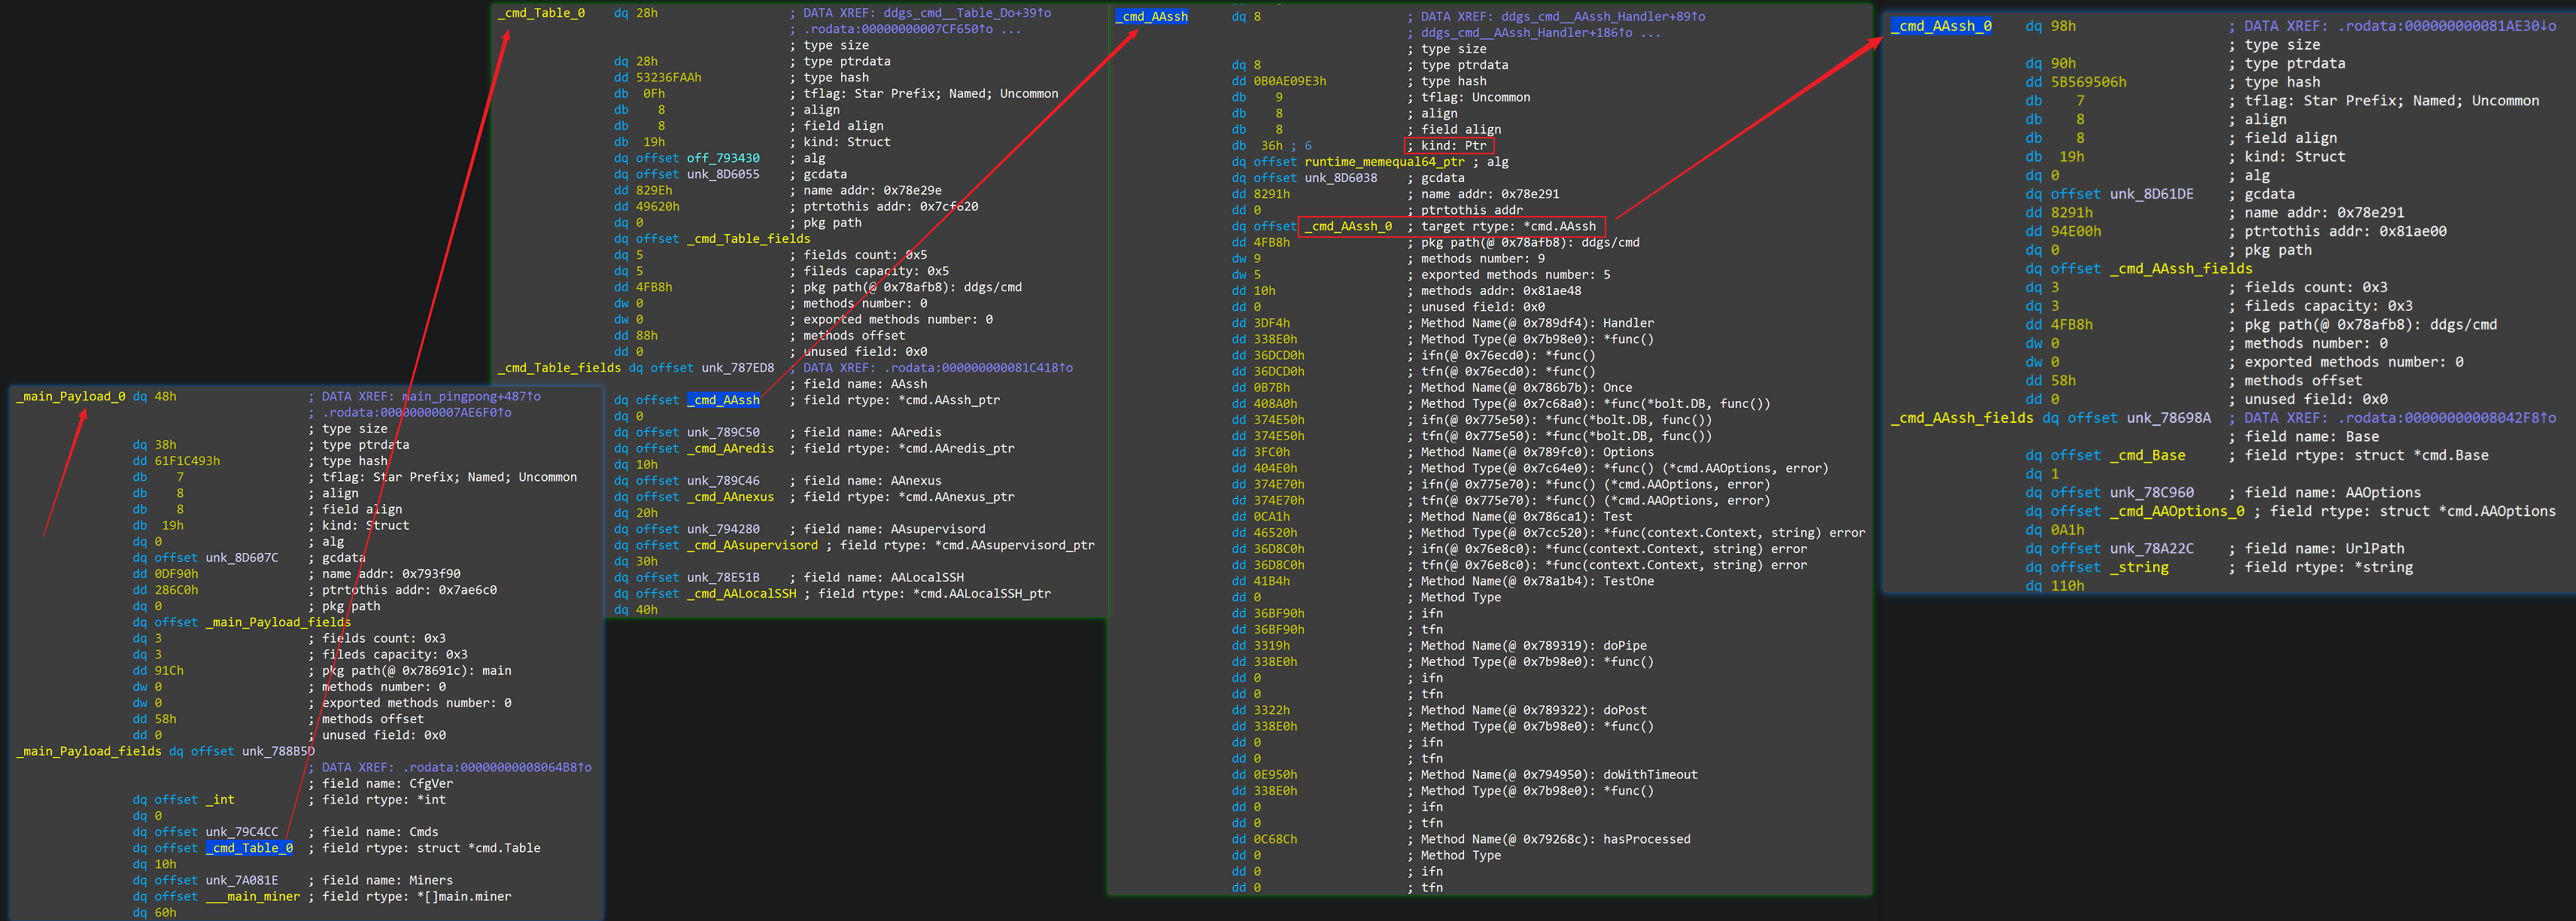 0xjiayu/go_parser
Yet Another Golang binary parser for IDAPro
 jfmaes/lazysign
Create fake certs for binaries using windows binaries and the power of bat files
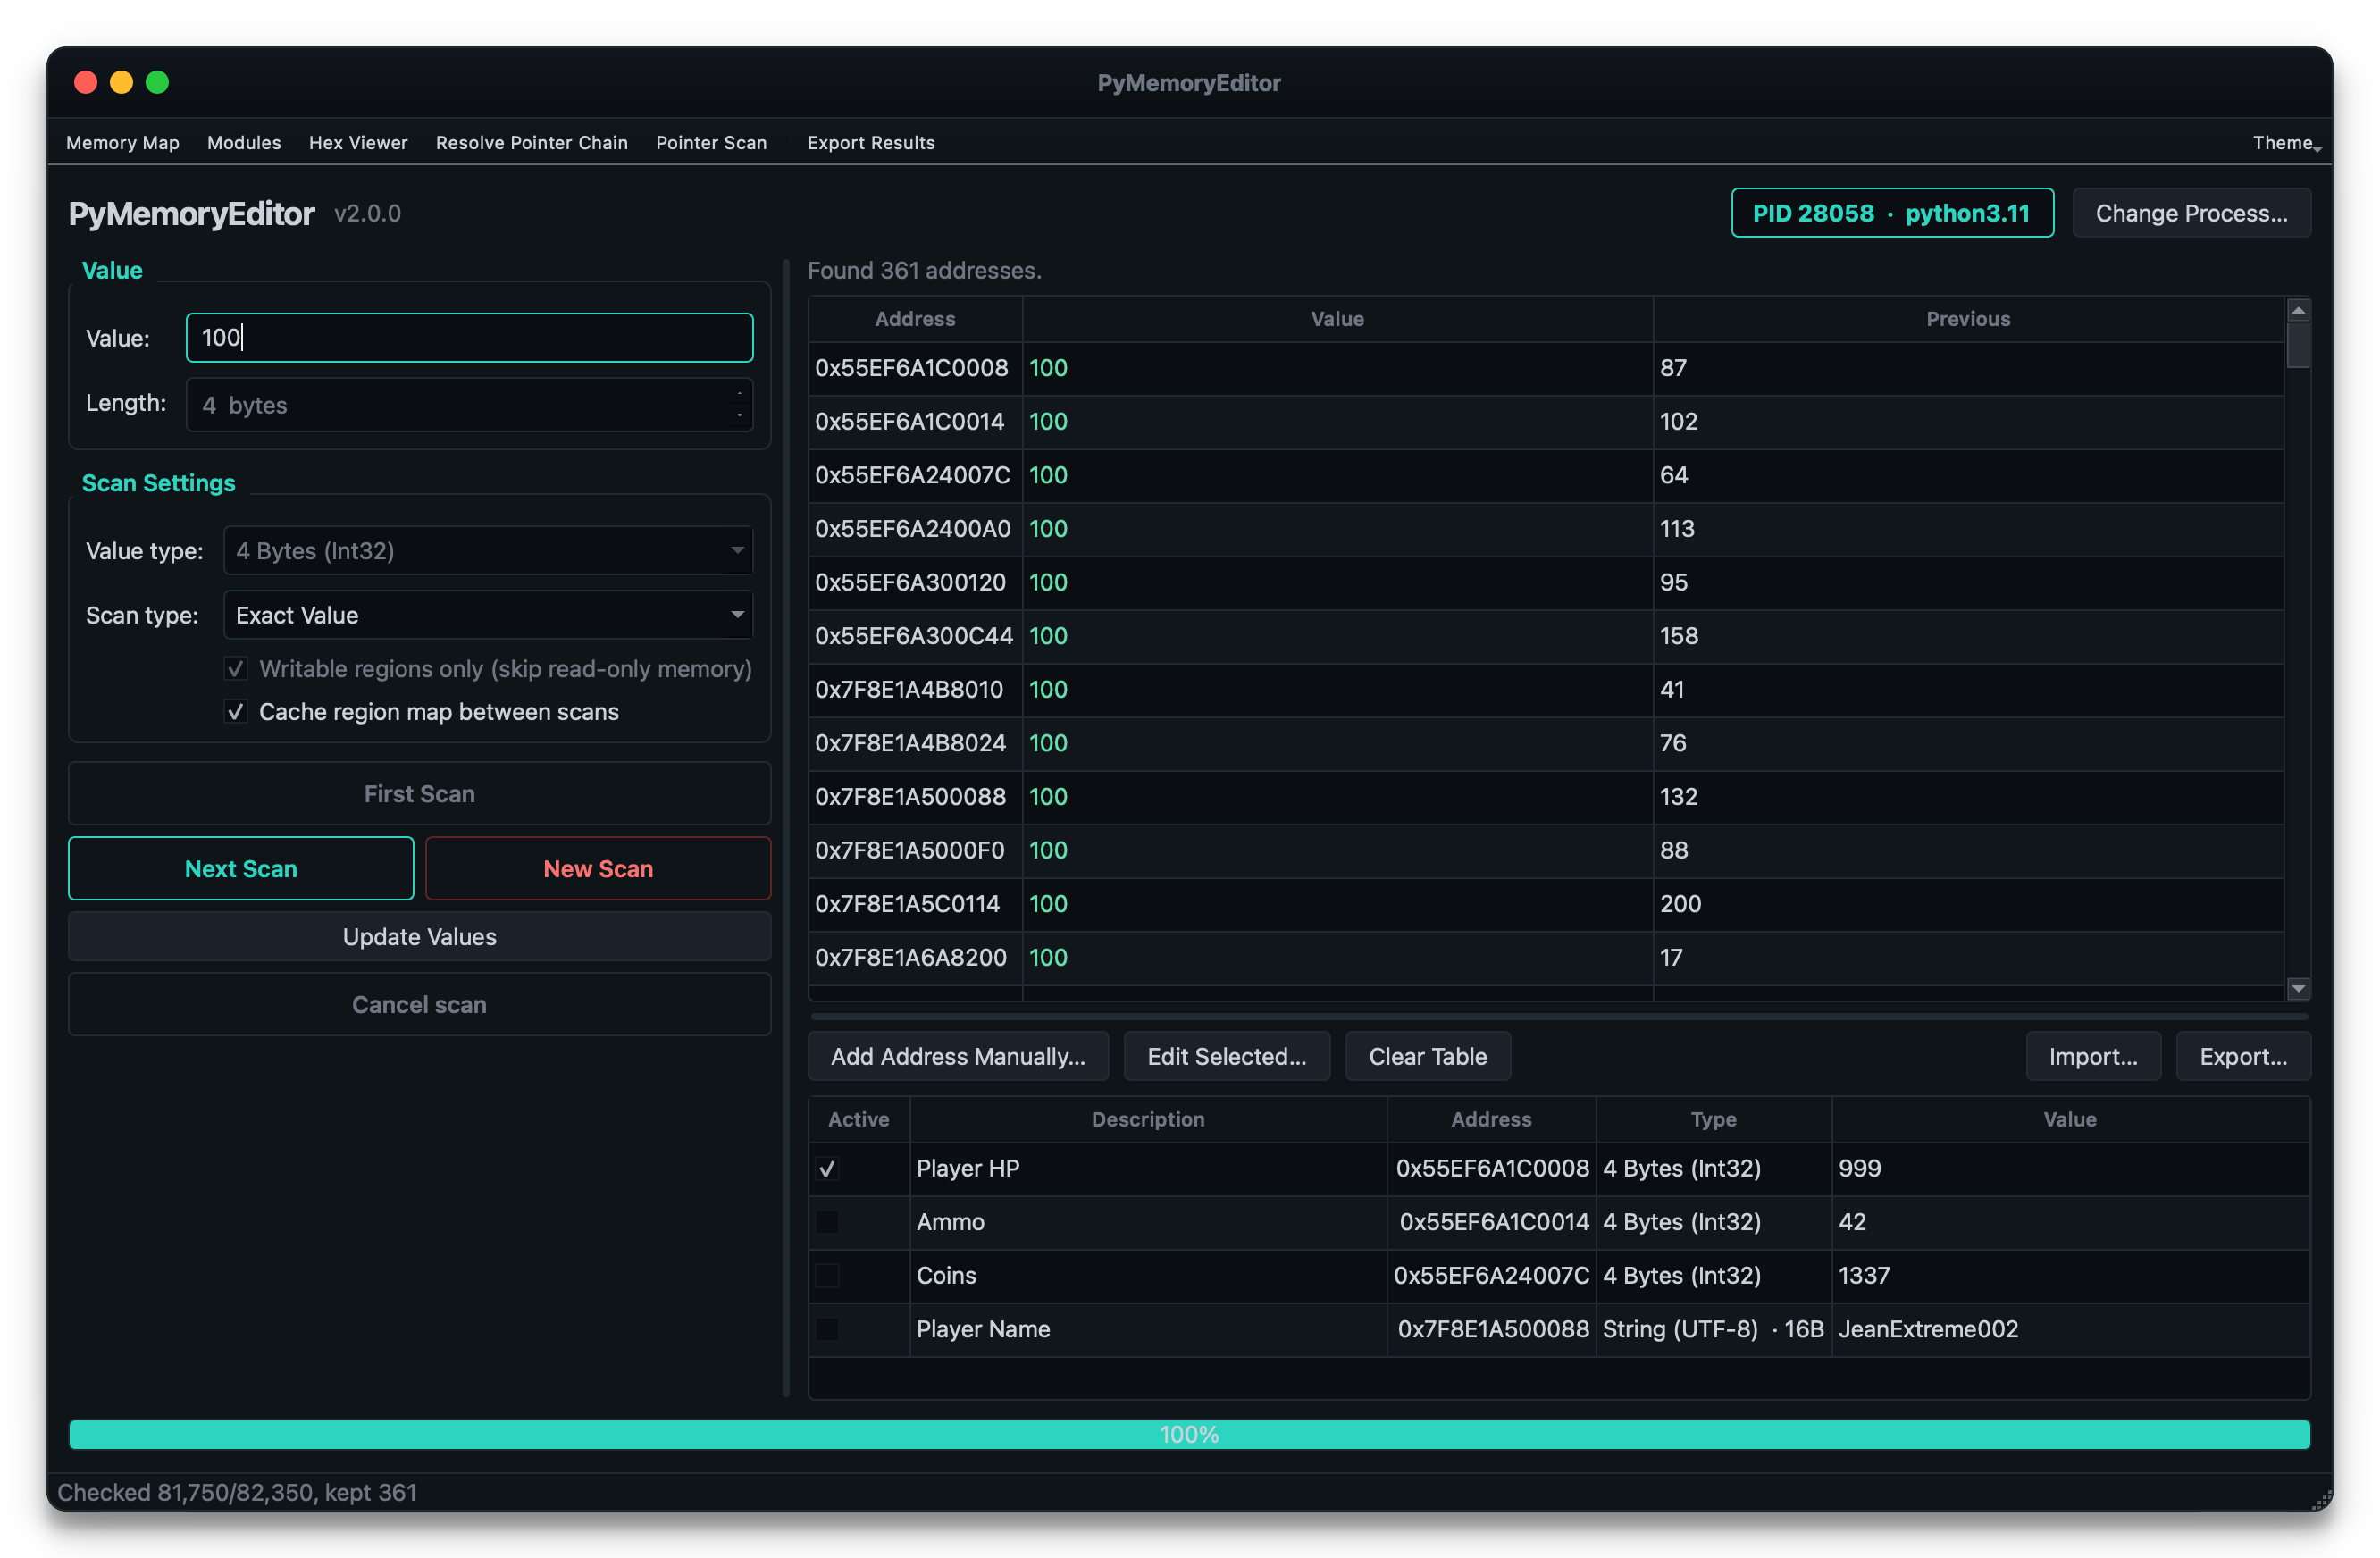 jeanextreme002/pymemoryeditor
A pure-Python library that lets you inspect, modify and search the memory of any running process in a few lines of Python :snake: .
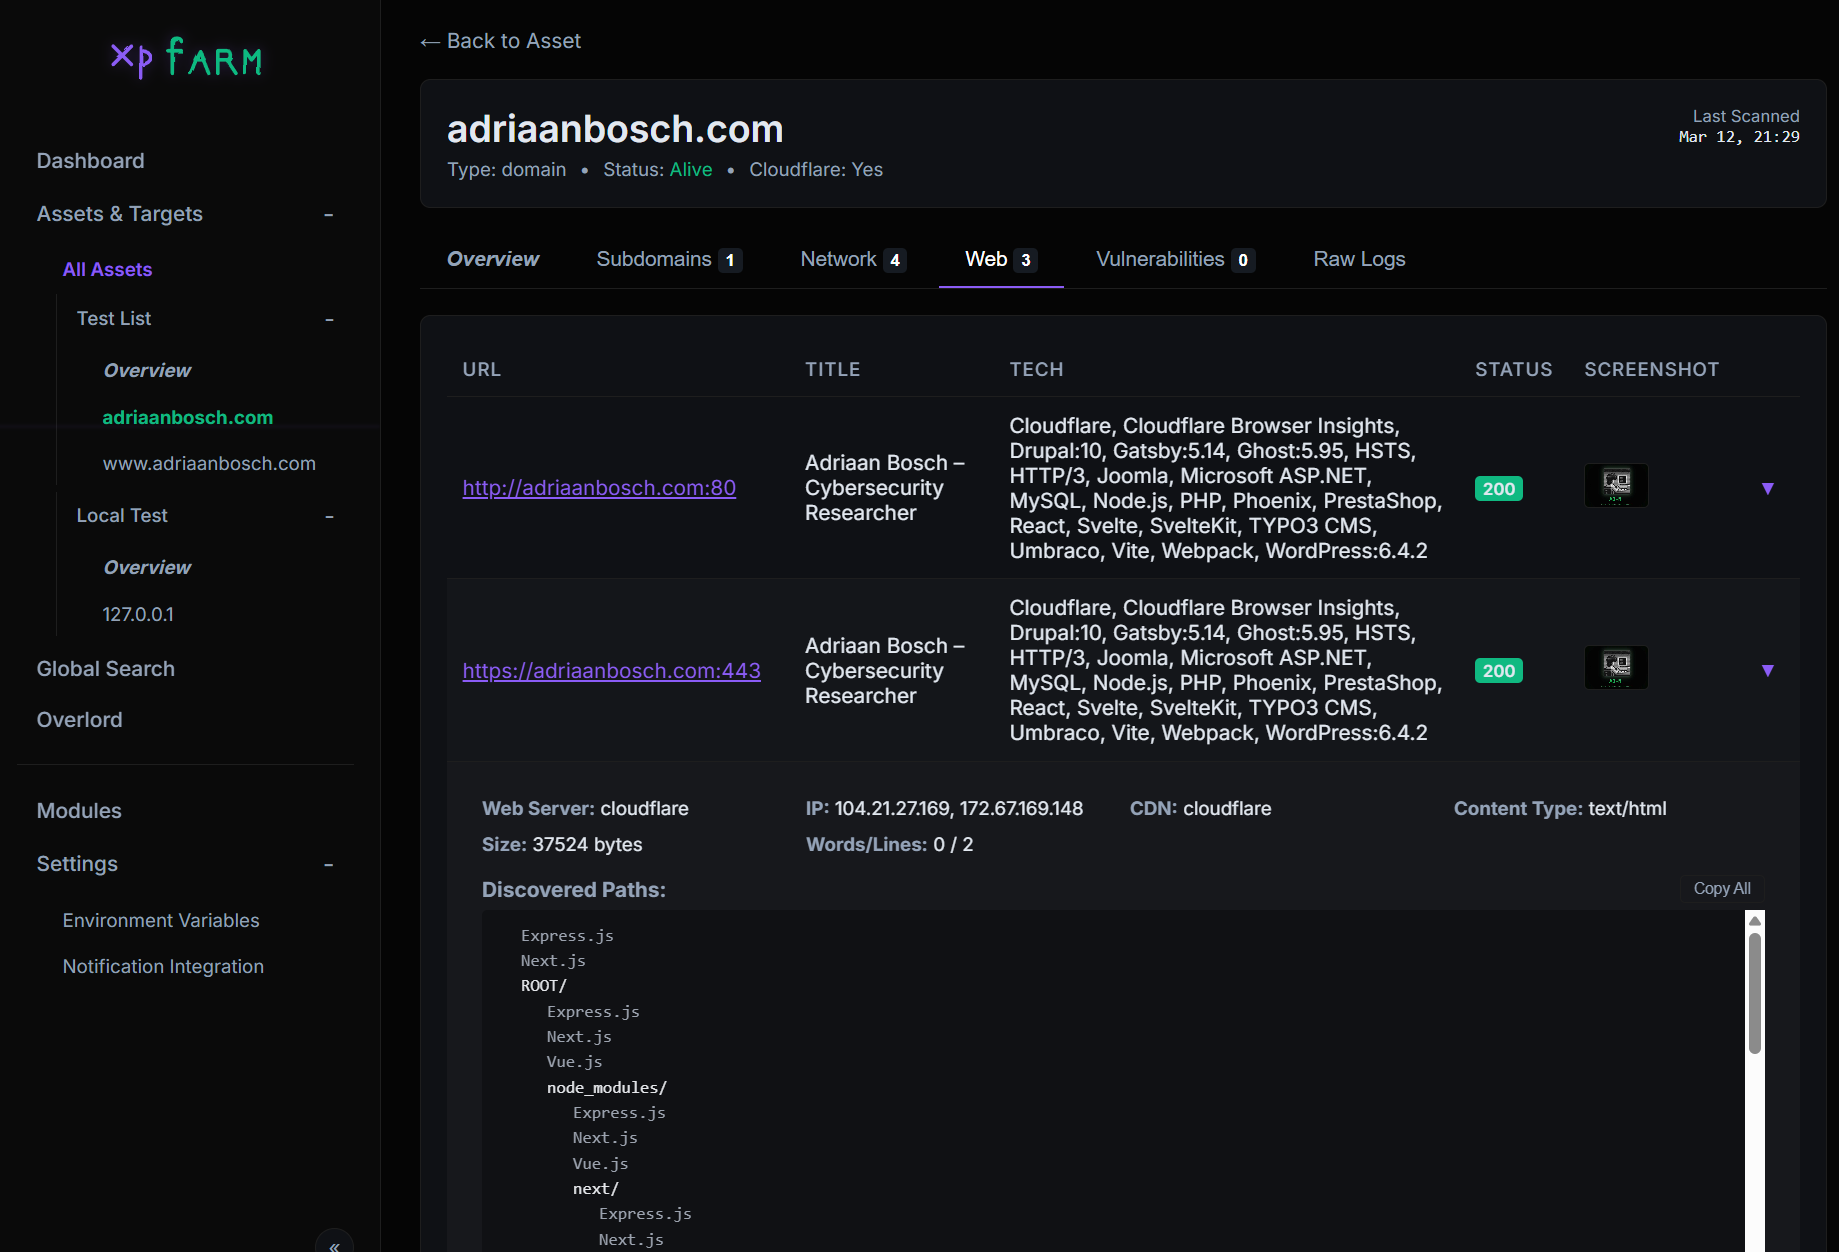 canuk40/xpfarm
Automated bug bounty & recon framework — wraps Subfinder, Naabu, Httpx, Nuclei, Nmap, CVEMap, Gowitness, Katana & more behind a unified web UI
 1-3-7/disrobe
Rust CLI suite that statically decompiles, deobfuscates, and unpacks native code, bytecode, scripts, firmware, and app packages across 15+ ecosystems…
 peterhackz/zyrox
Zyrox: LLVM based, compile-time obfuscator plugin.
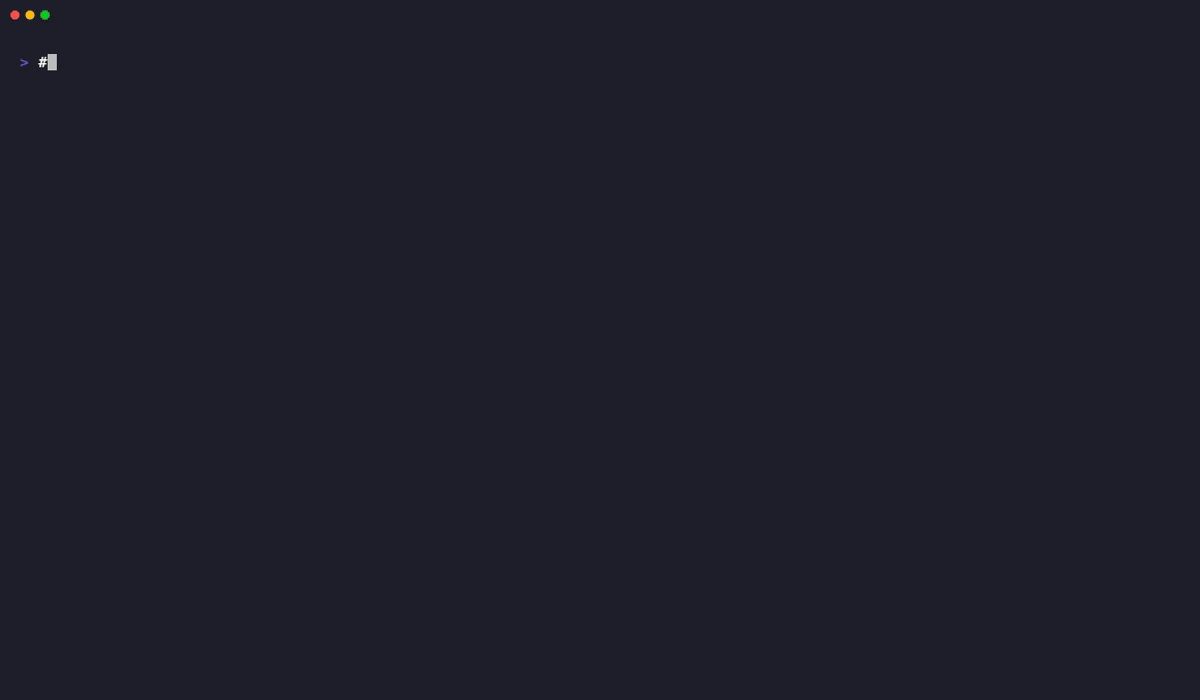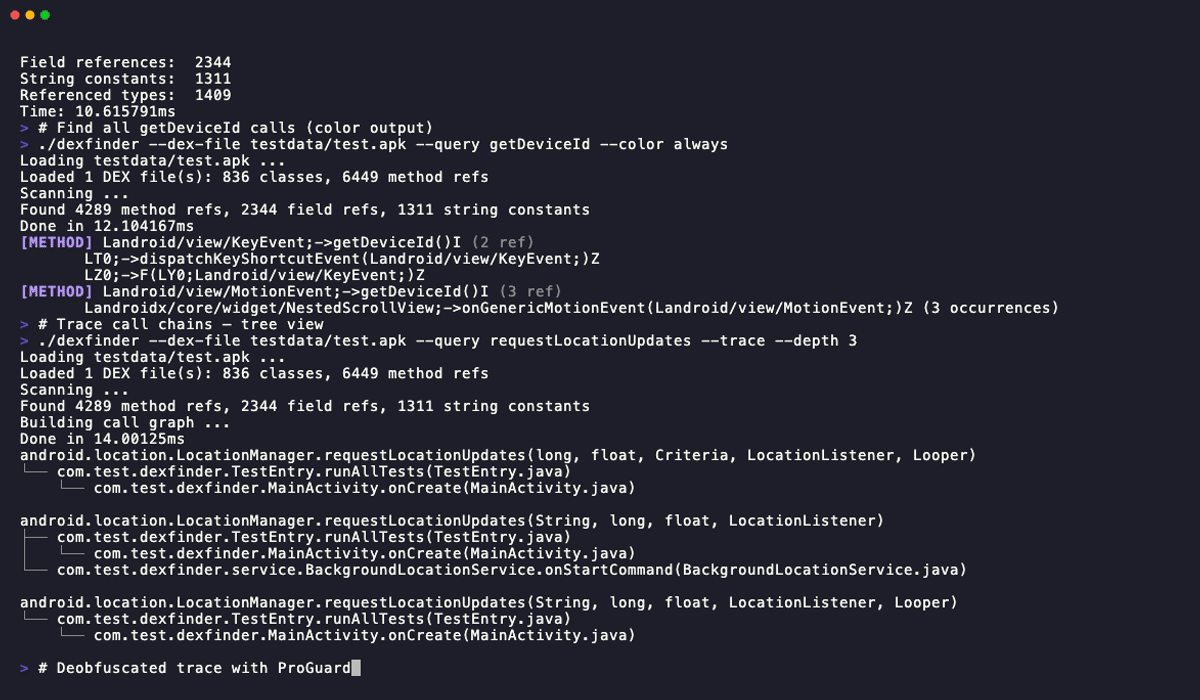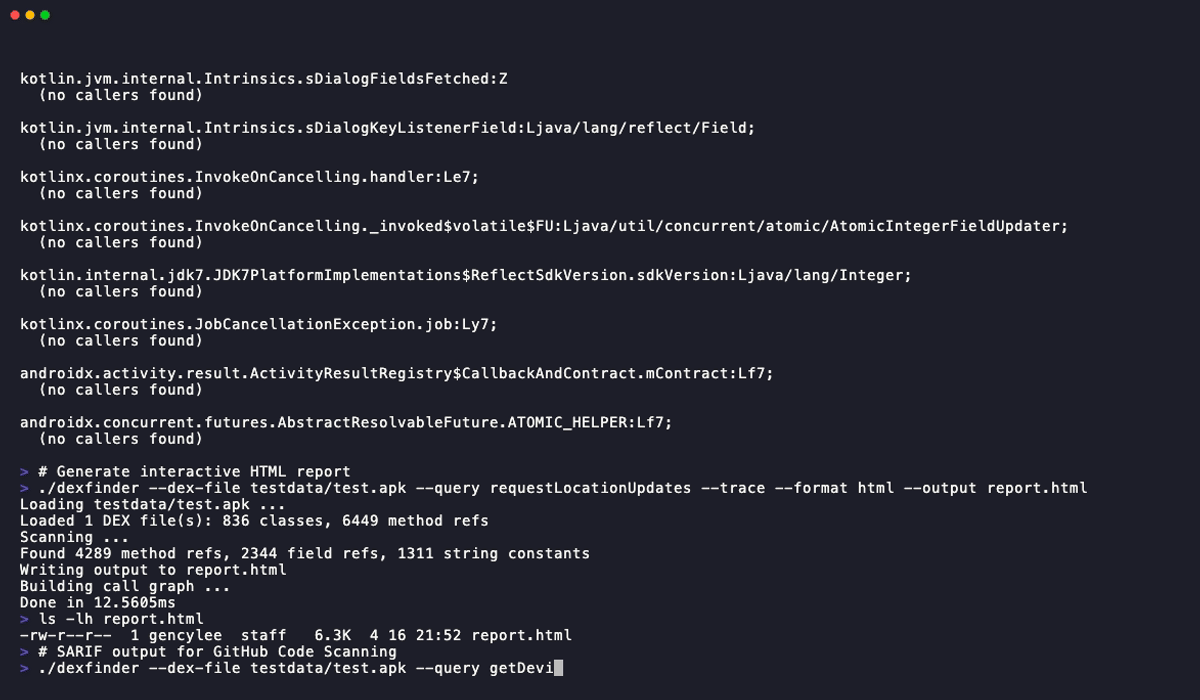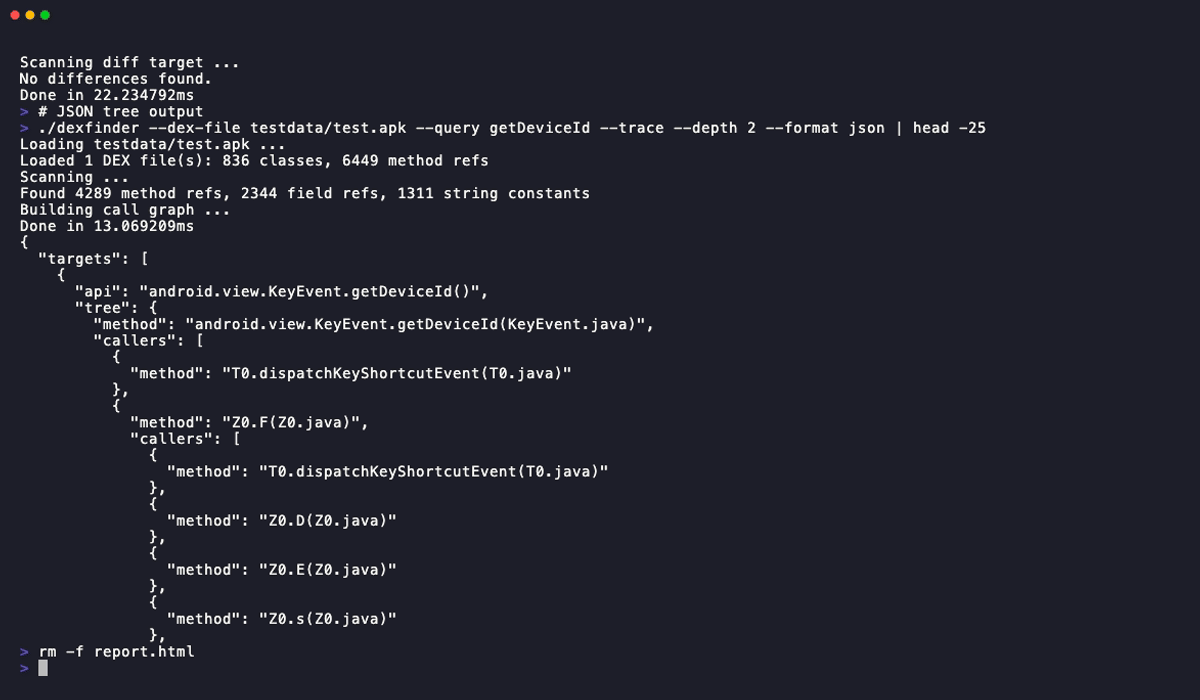 junelegency/dexfinder
Cross-platform APK/DEX method finder with call chain tracing, ProGuard deobfuscation, and hidden API detection