

Detect-It-Easy
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
ai-assisted-reversingbinary-analysisbinary-exploitation+10
11.6k
horsicq/detect-it-easyProgram for determining types of files for Windows, Linux and MacOS.
 wtsxdev/reverse-engineering
List of awesome reverse engineering resources
 fuzzysecurity/powershell-suite
My musings with PowerShell
 rehints/hexrayscodexplorer
Hex-Rays Decompiler plugin for better code navigation
 matterpreter/offensivecsharp
Collection of Offensive C# Tooling
 airbus-seclab/bincat
Binary code static analyser, with IDA integration. Performs value and taint analysis, type reconstruction, use-after-free and double-free detection
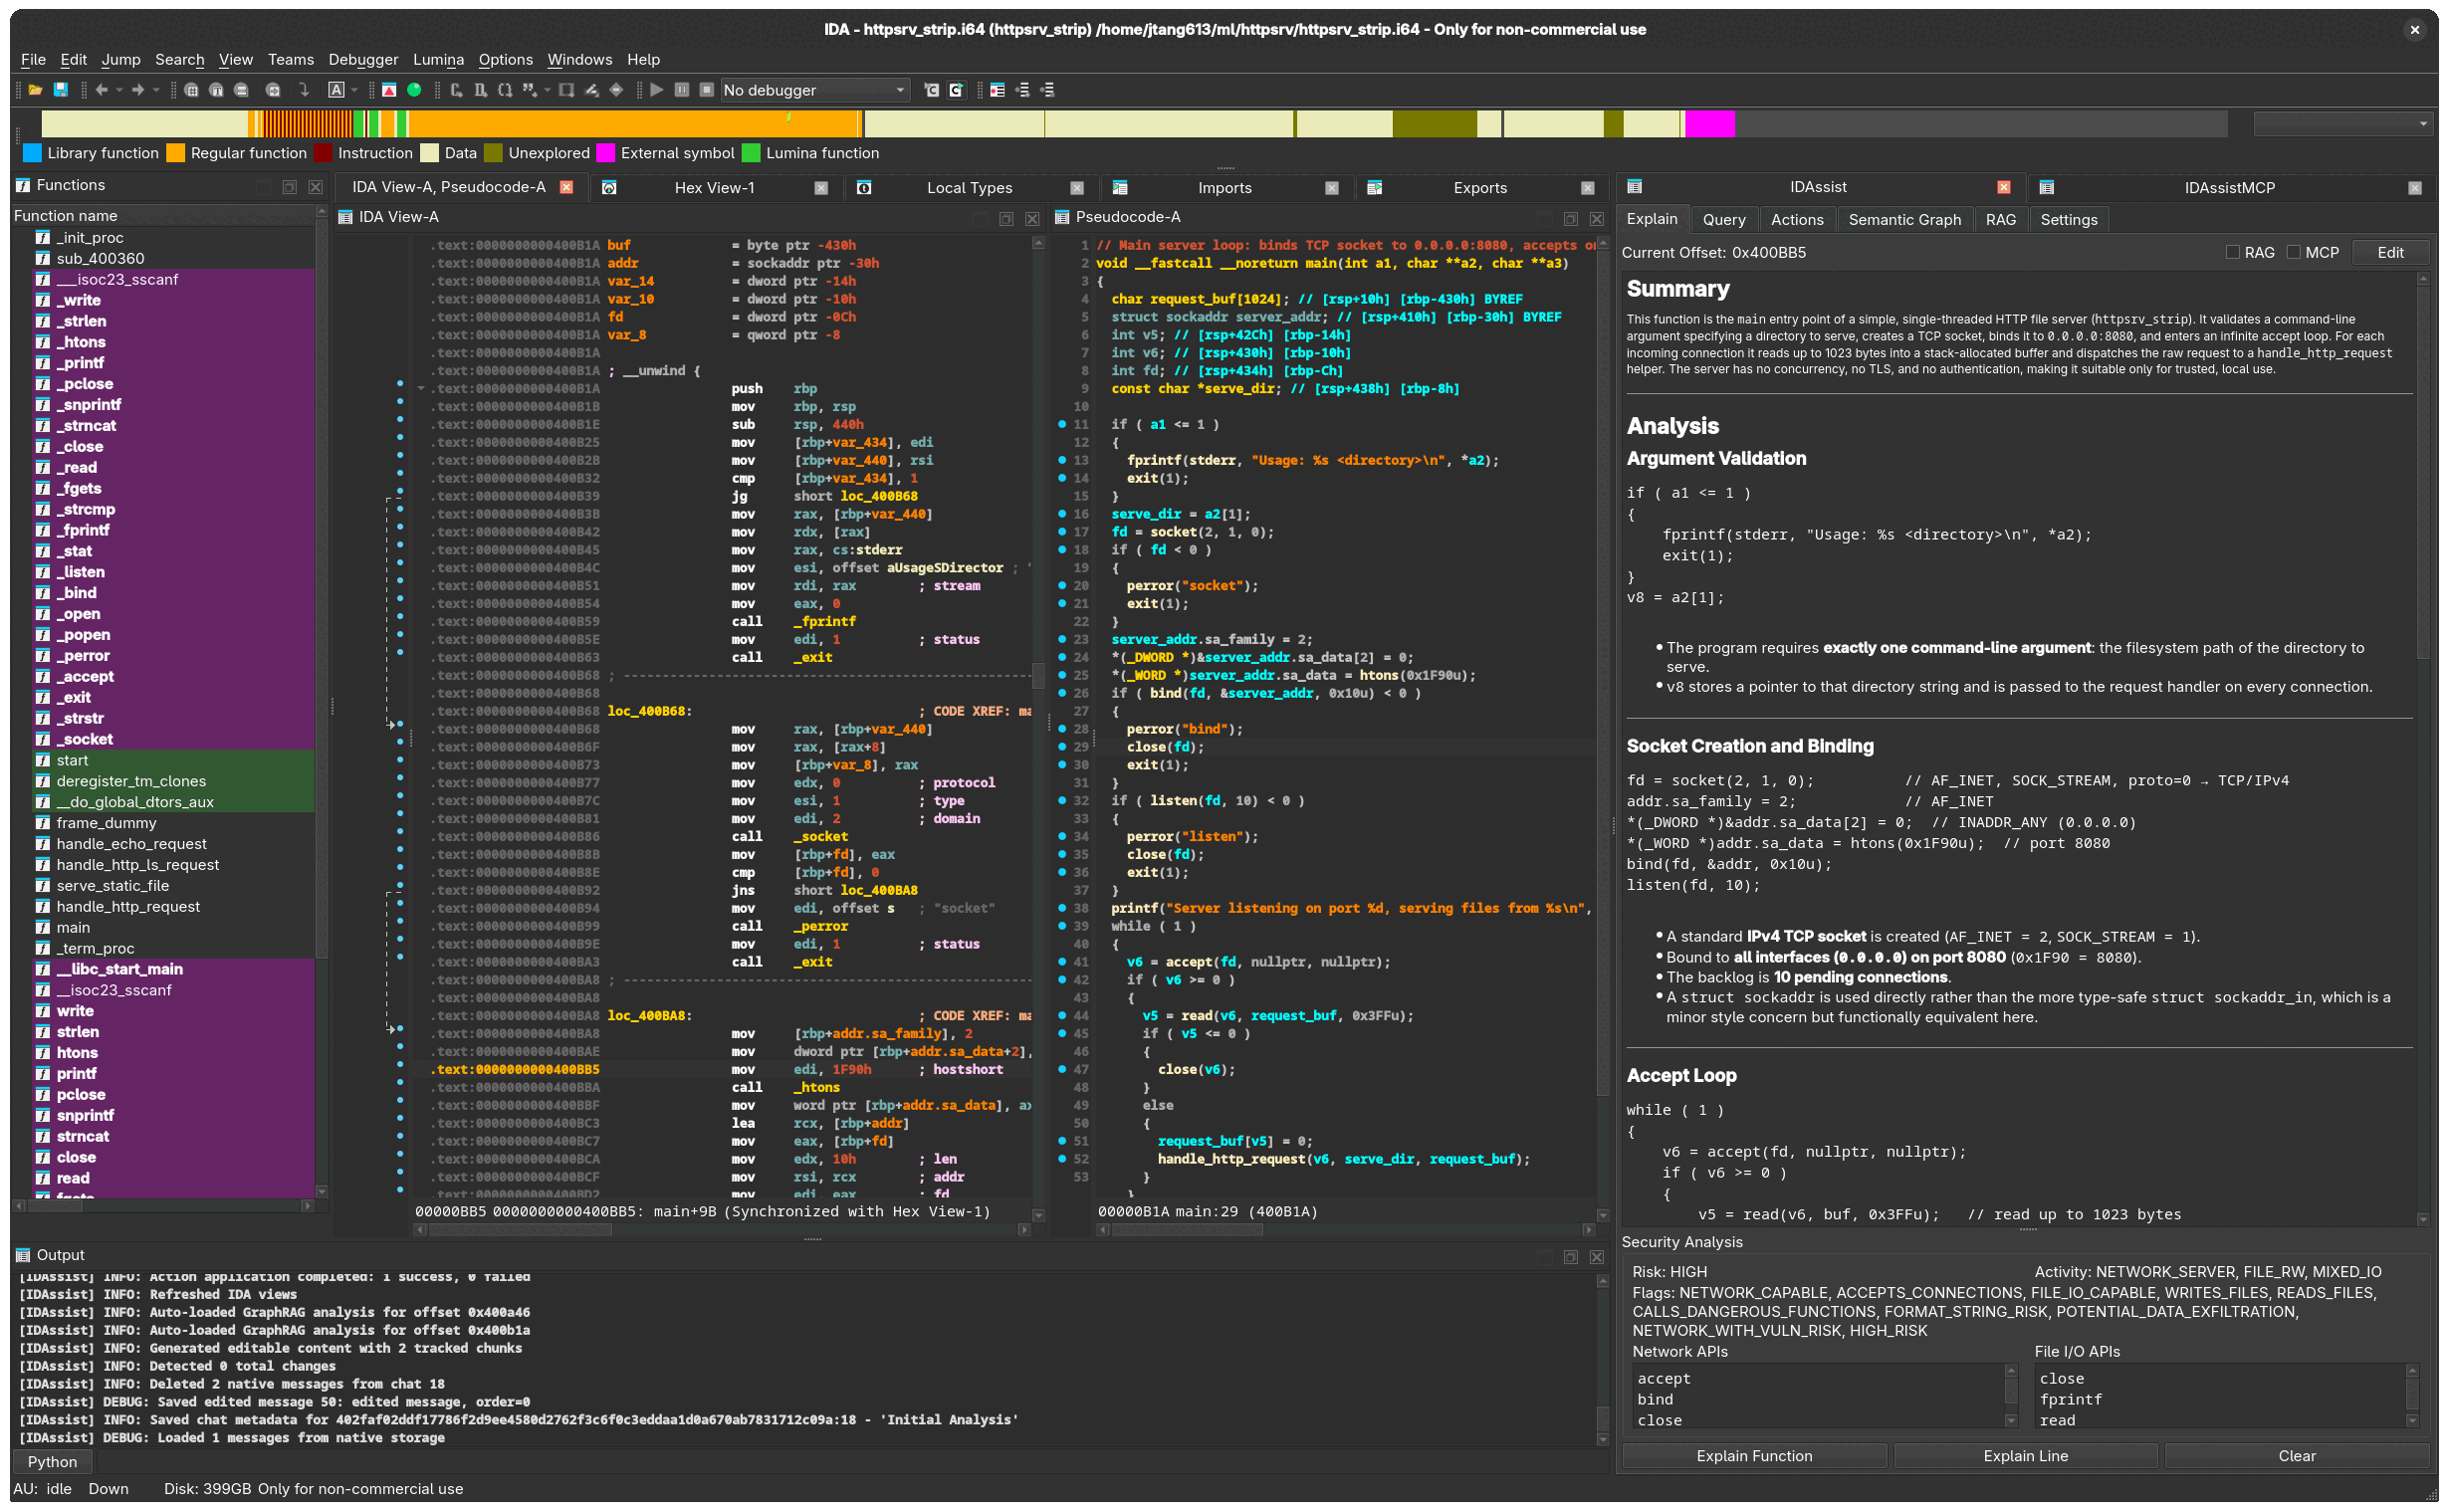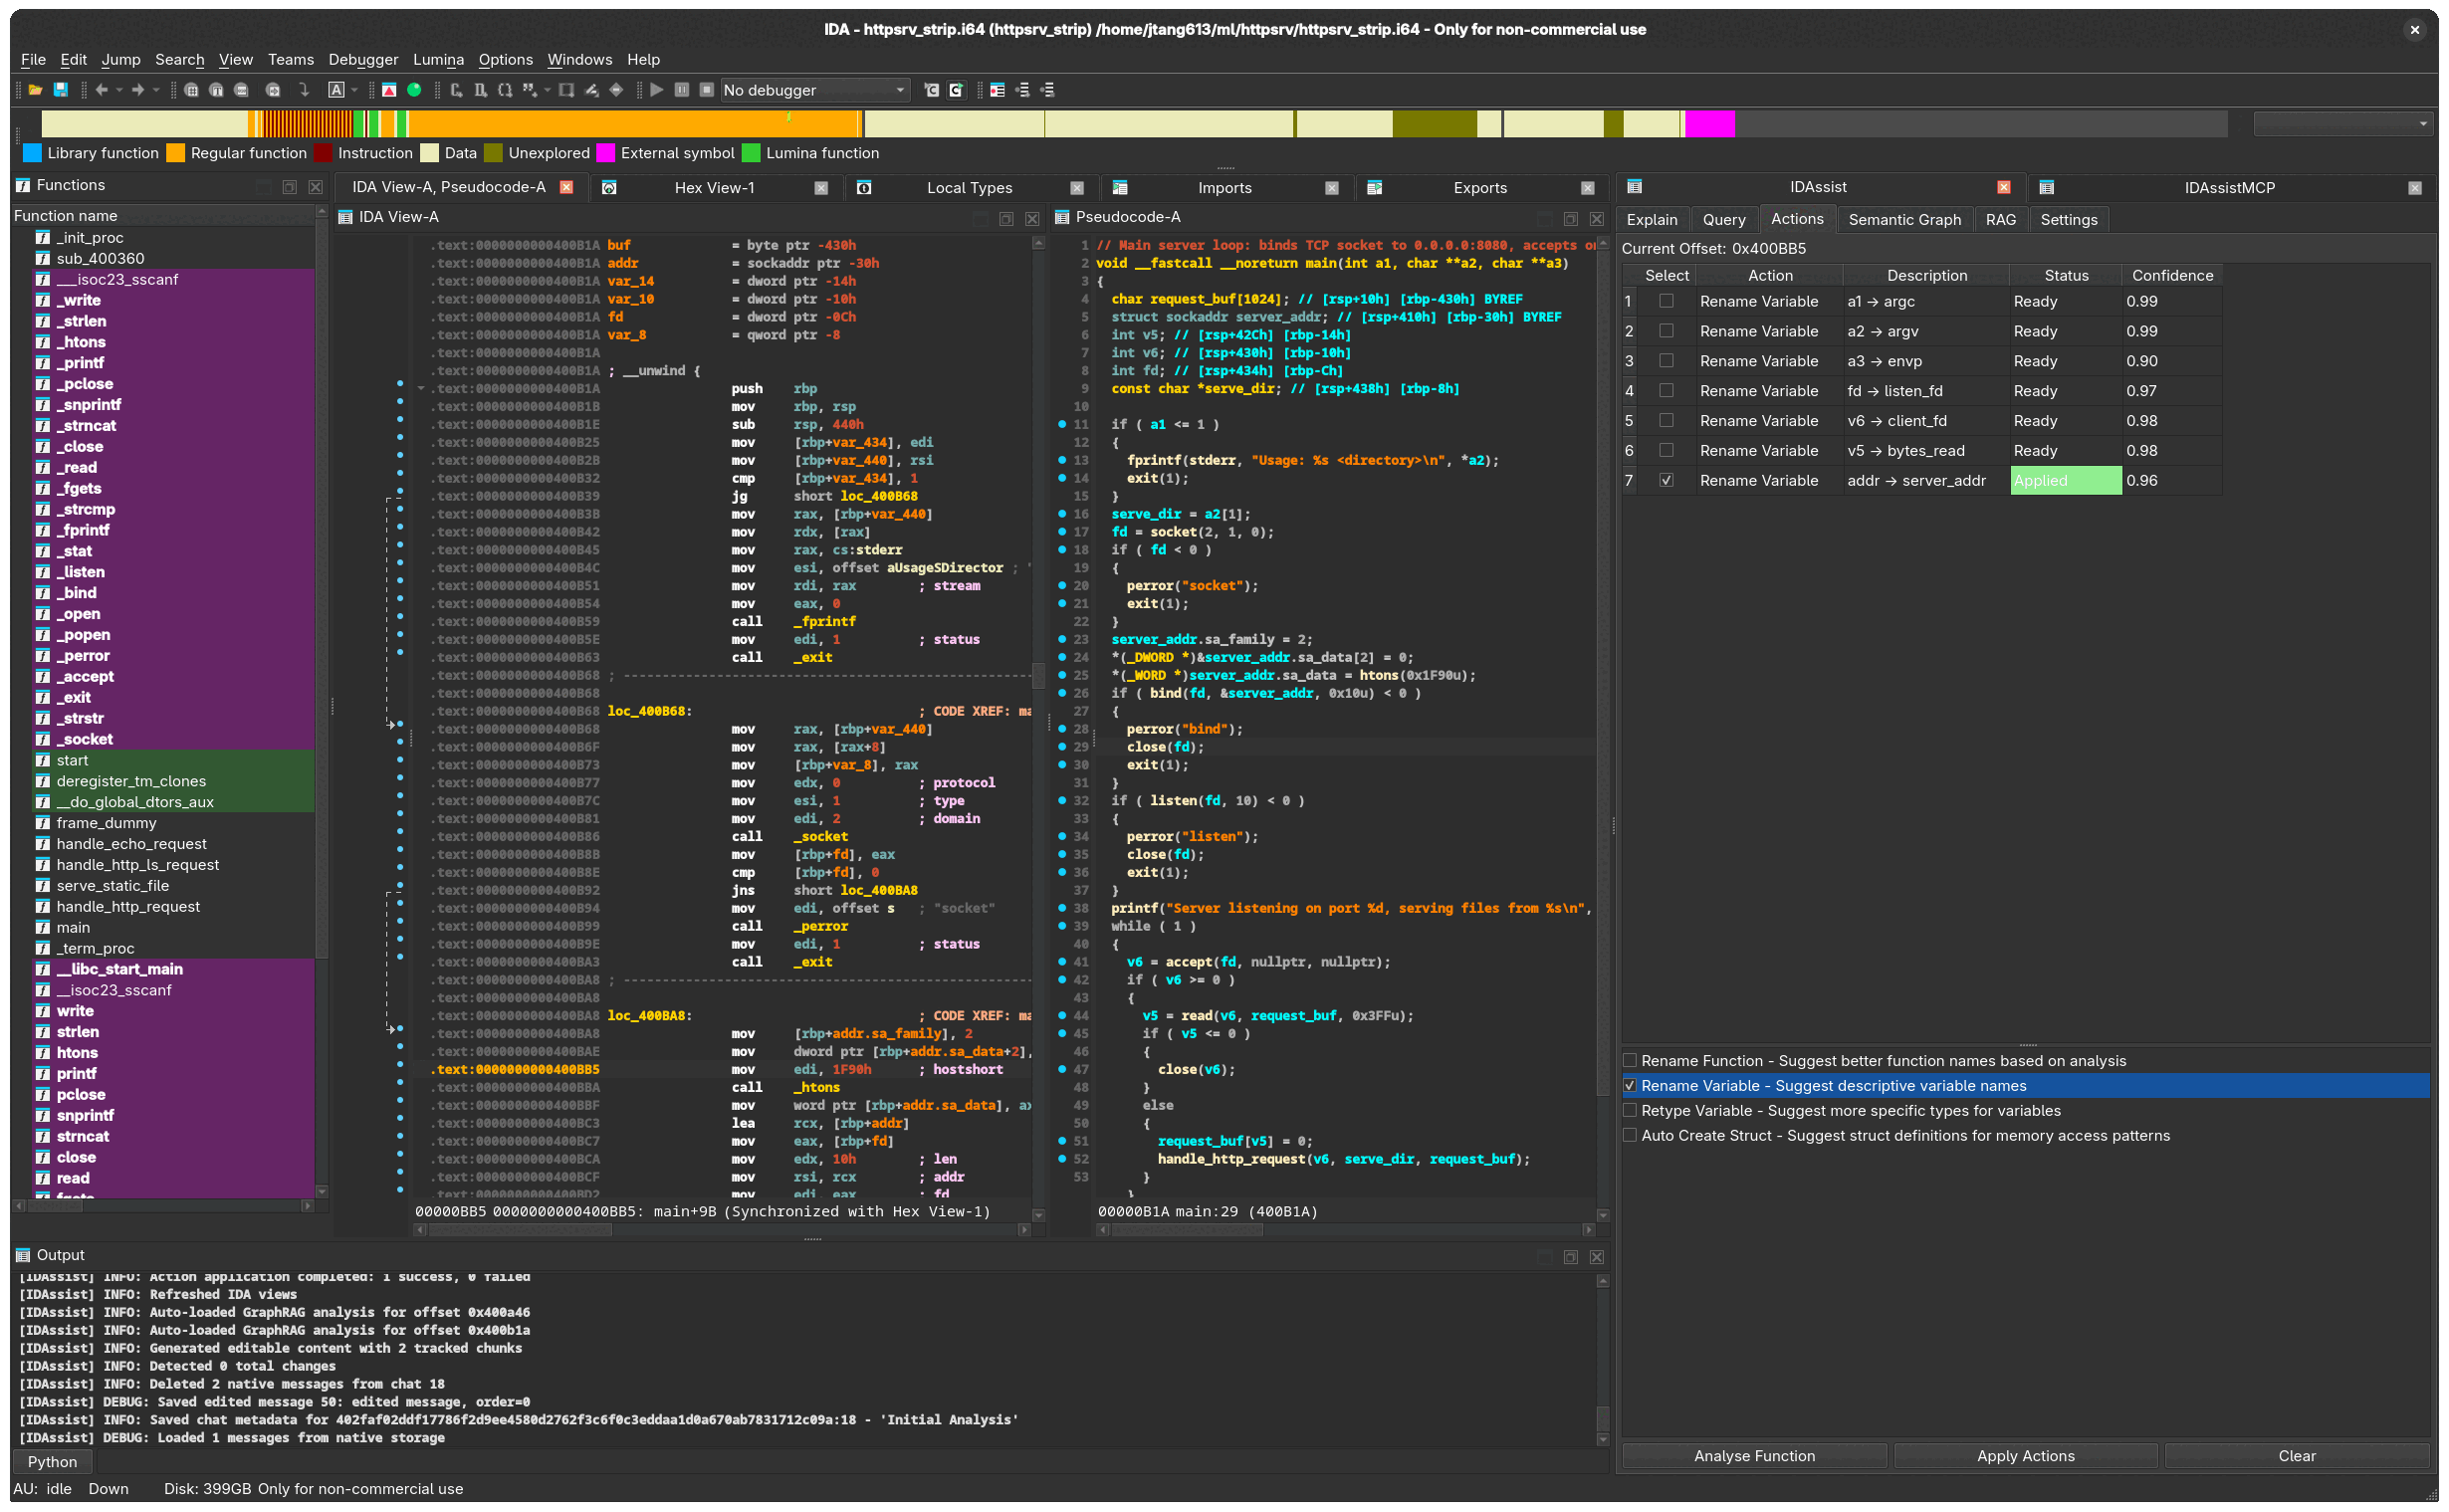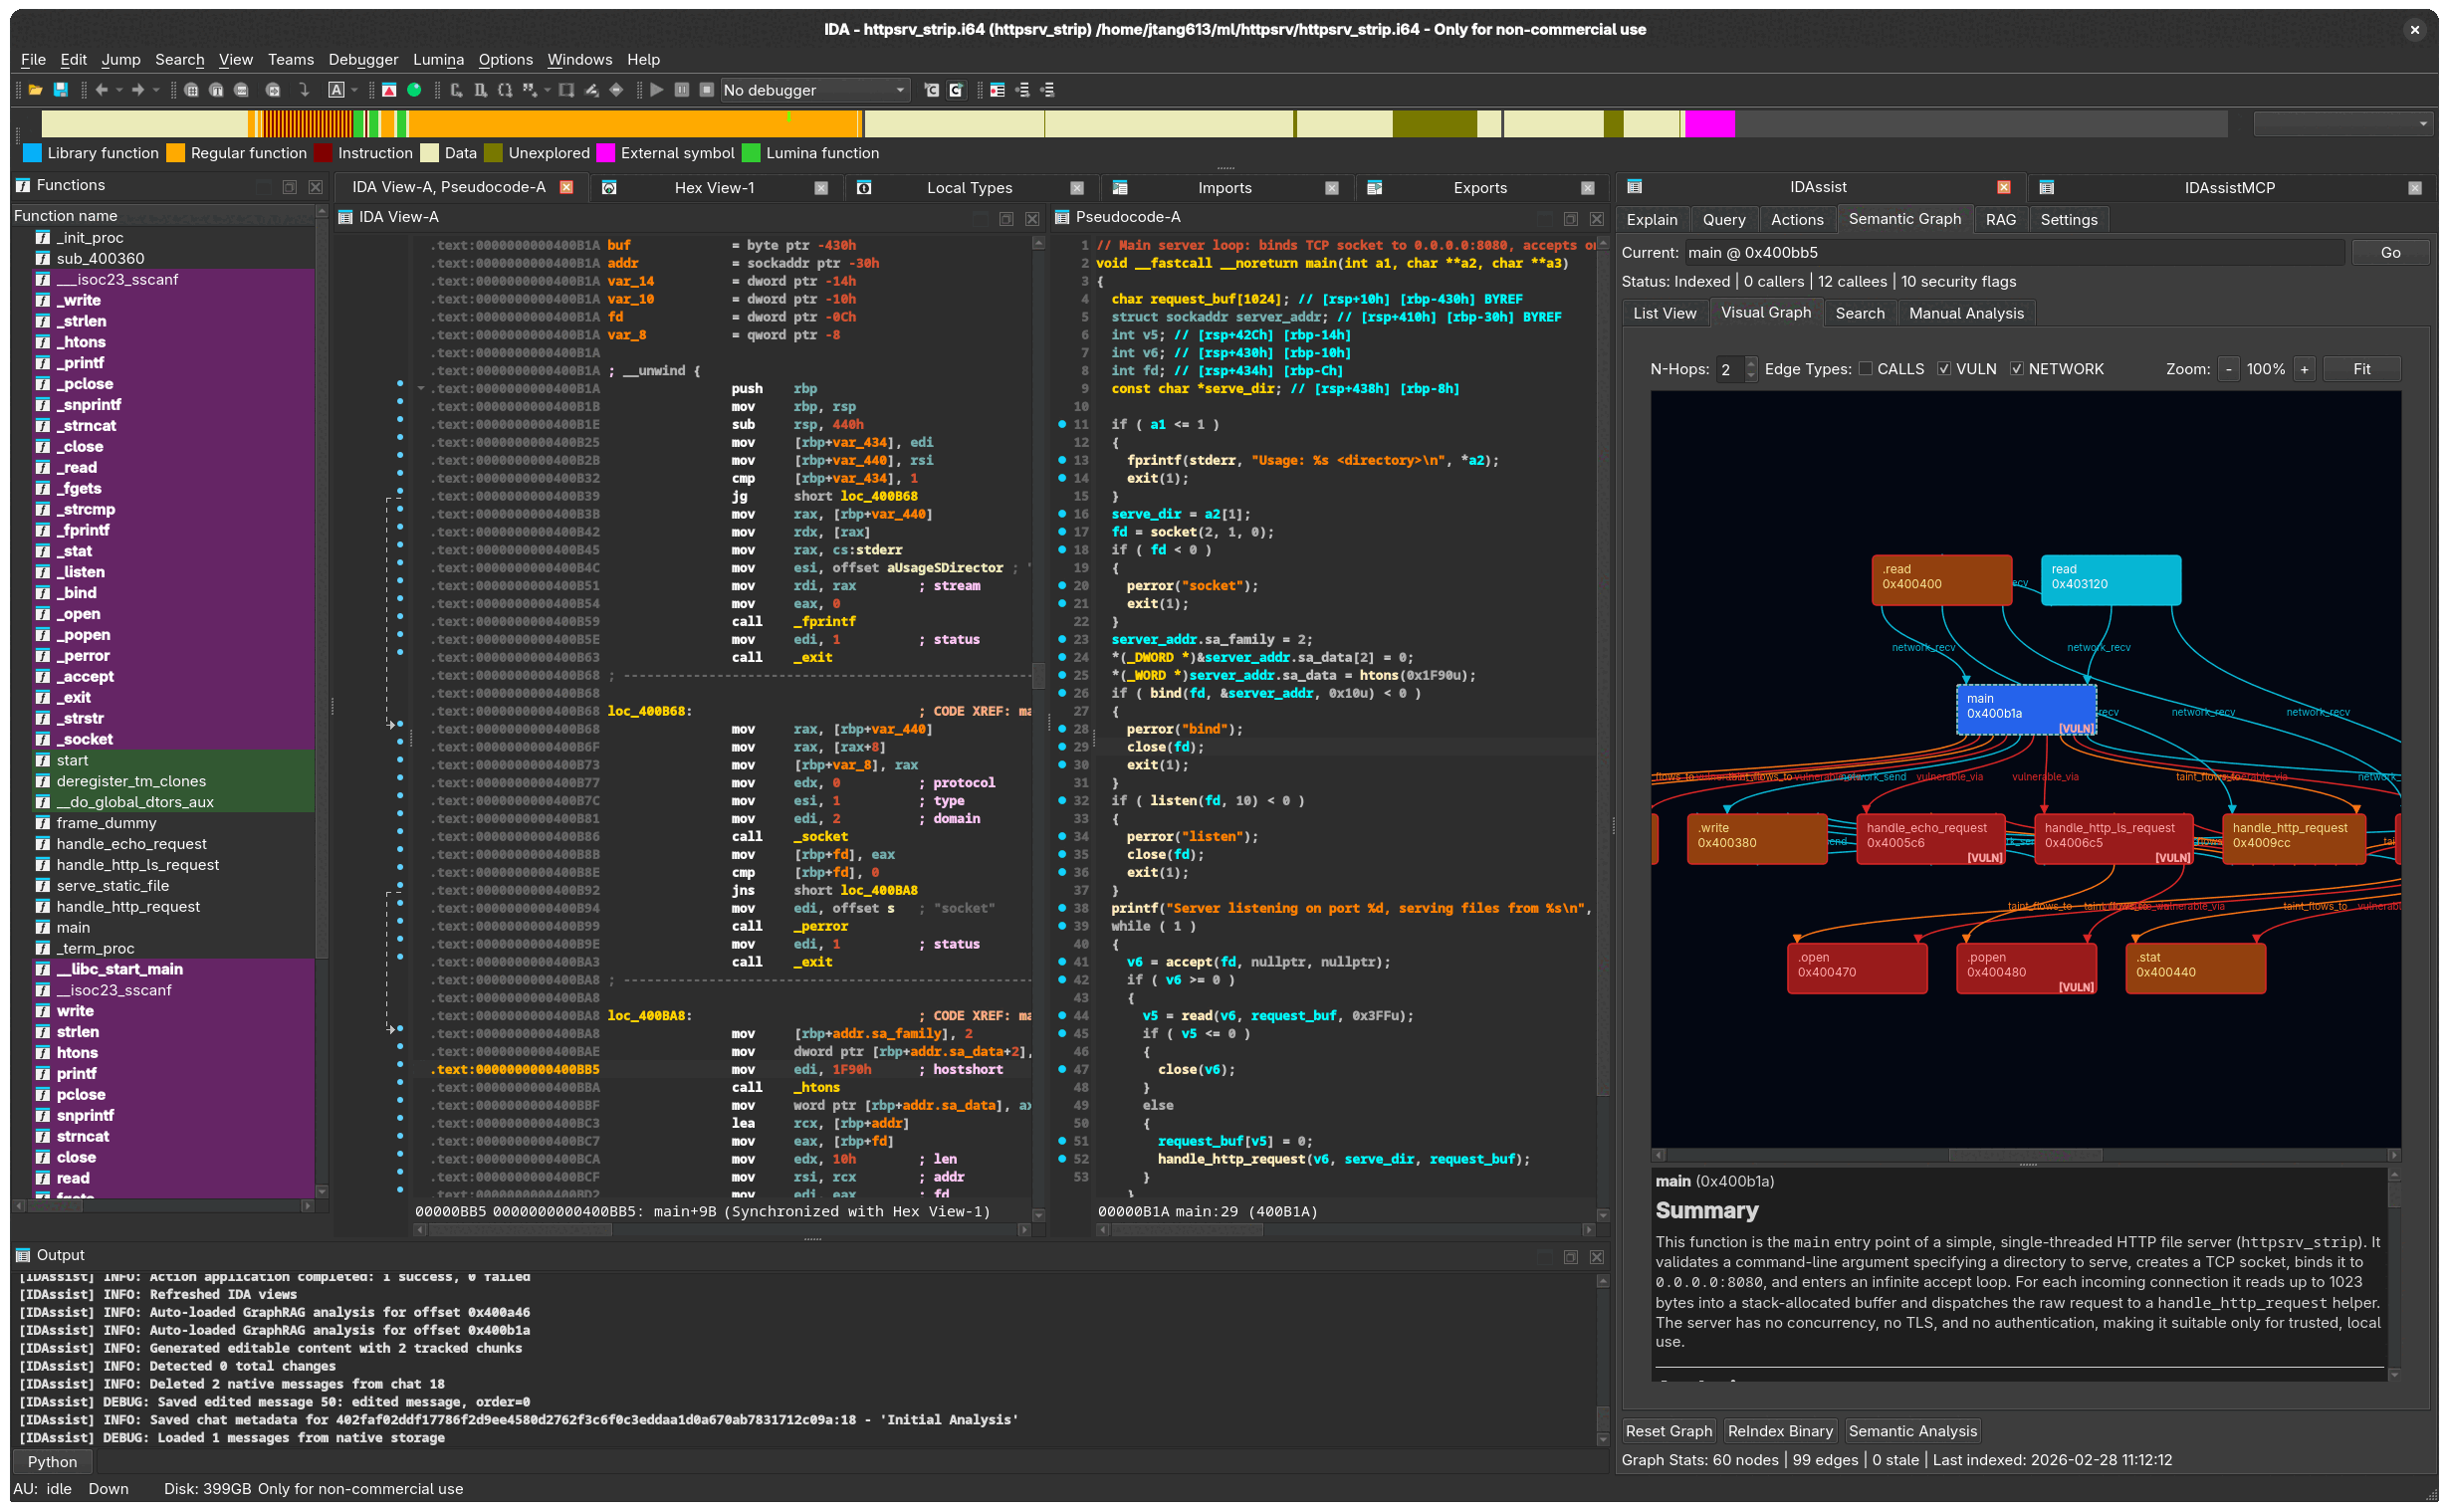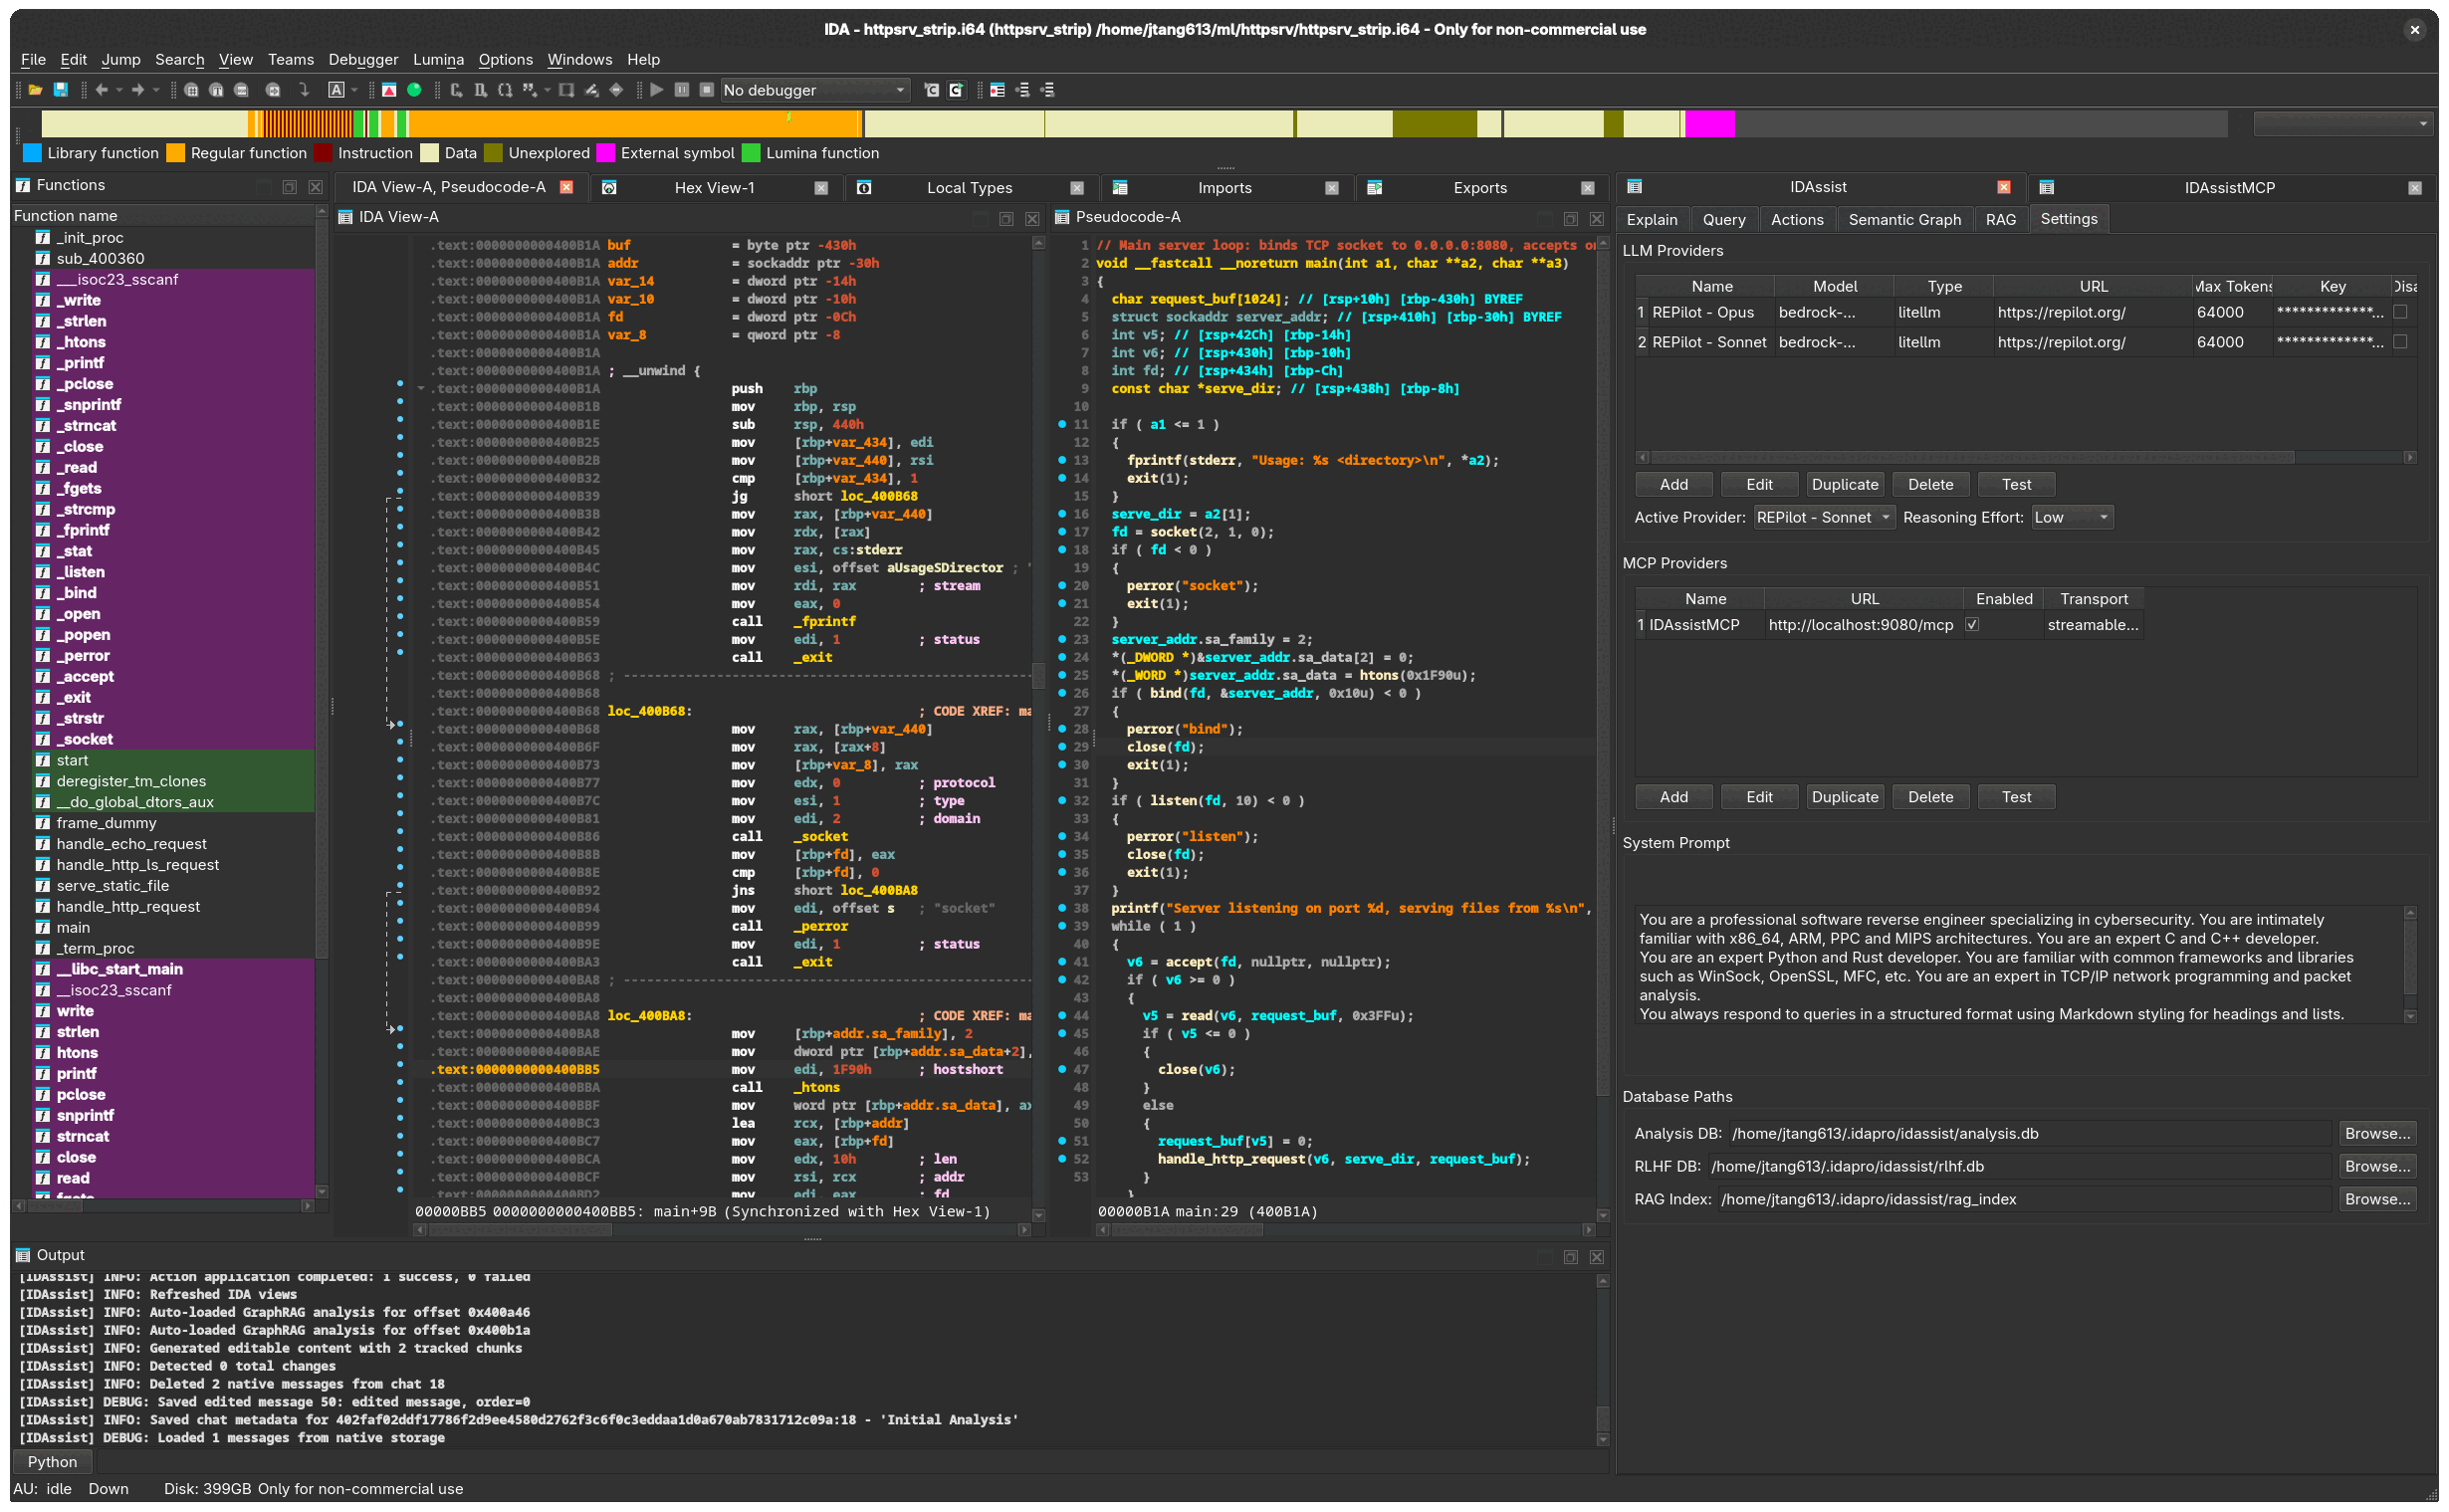 symgraph/idassist
AI-Powered Reverse Engineering Plugin for IDA Pro
 recurse-labs/recurse
Agentic reverse engineering IDE with a pure-Rust multi-architecture disassembler, native decompiler, debugger, and LLM agent for binary analysis and…
 seekbytes/ipa
GUI analyzer for deep-diving into PDF files. Detect malicious payloads, understand object relationships, and extract key information for threat…
 nmatt0/moria
IoT firmware identification and extraction
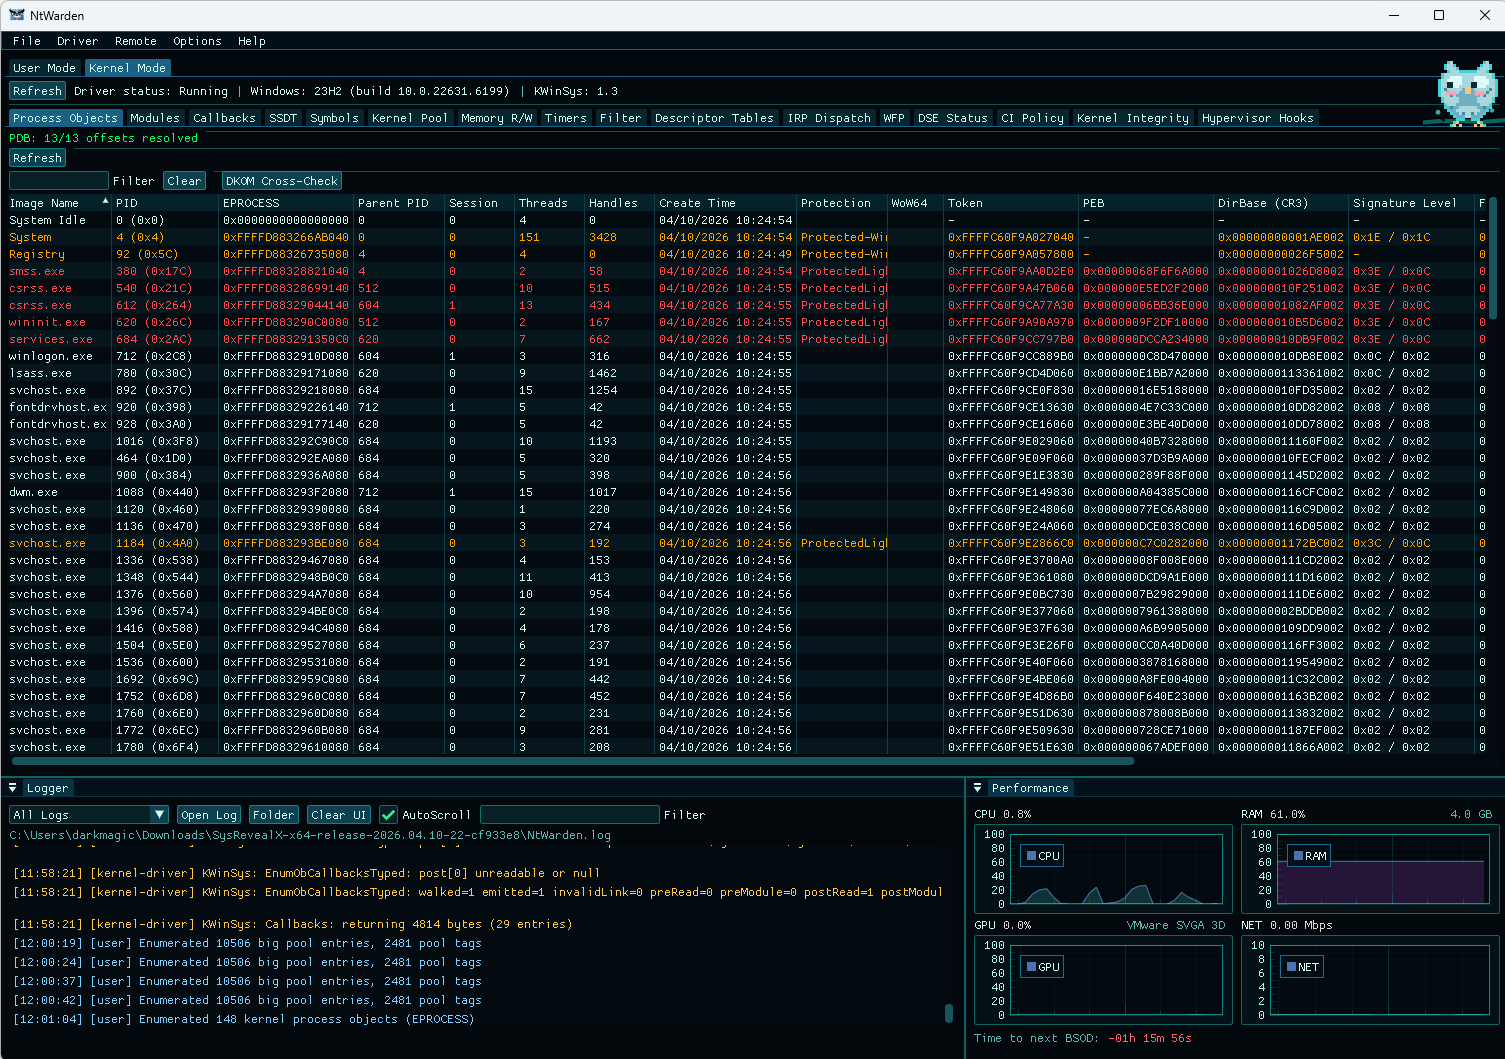 mrt4ntr4/ntwarden
Windows Analysis and Research Toolkit
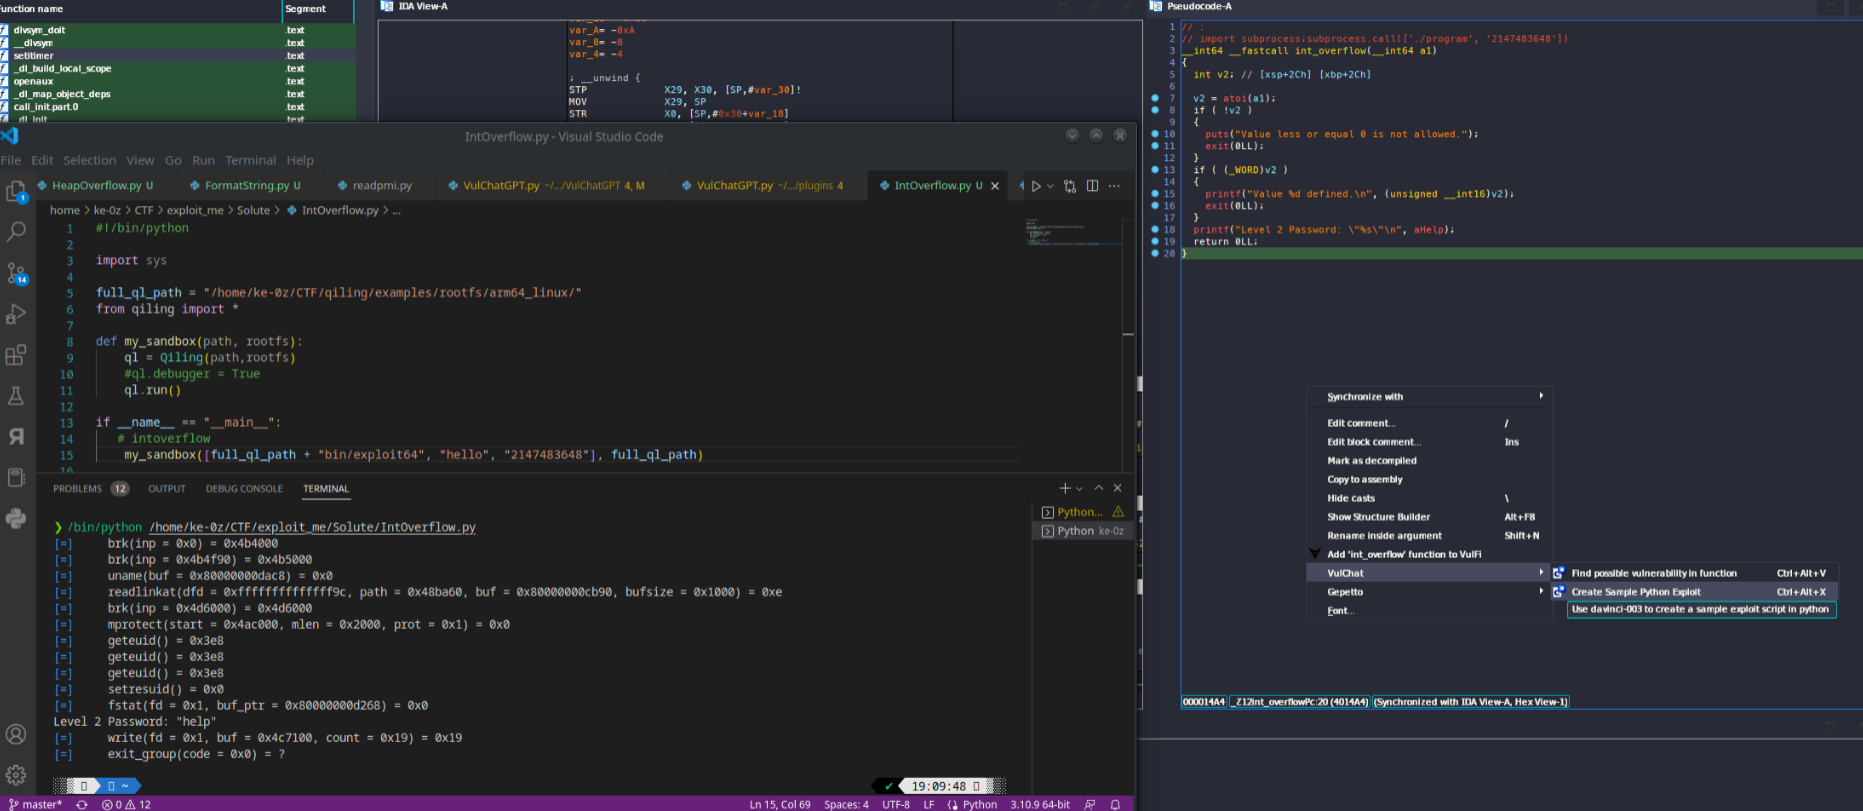 ke0z/binaivulhunter
Use IDA PRO HexRays decompiler with OpenAI(ChatGPT) to find possible vulnerabilities in binaries
 mrphrazer/obfuscation_analysis
Binary Ninja plugin to analyze and simplify obfuscated code
 allthingsida/allthingsida
Repository for the code snippets from the AllThingsIDA video channel
 squalr/squalr
A generic game/software hacking tool written from the ground up in Rust.
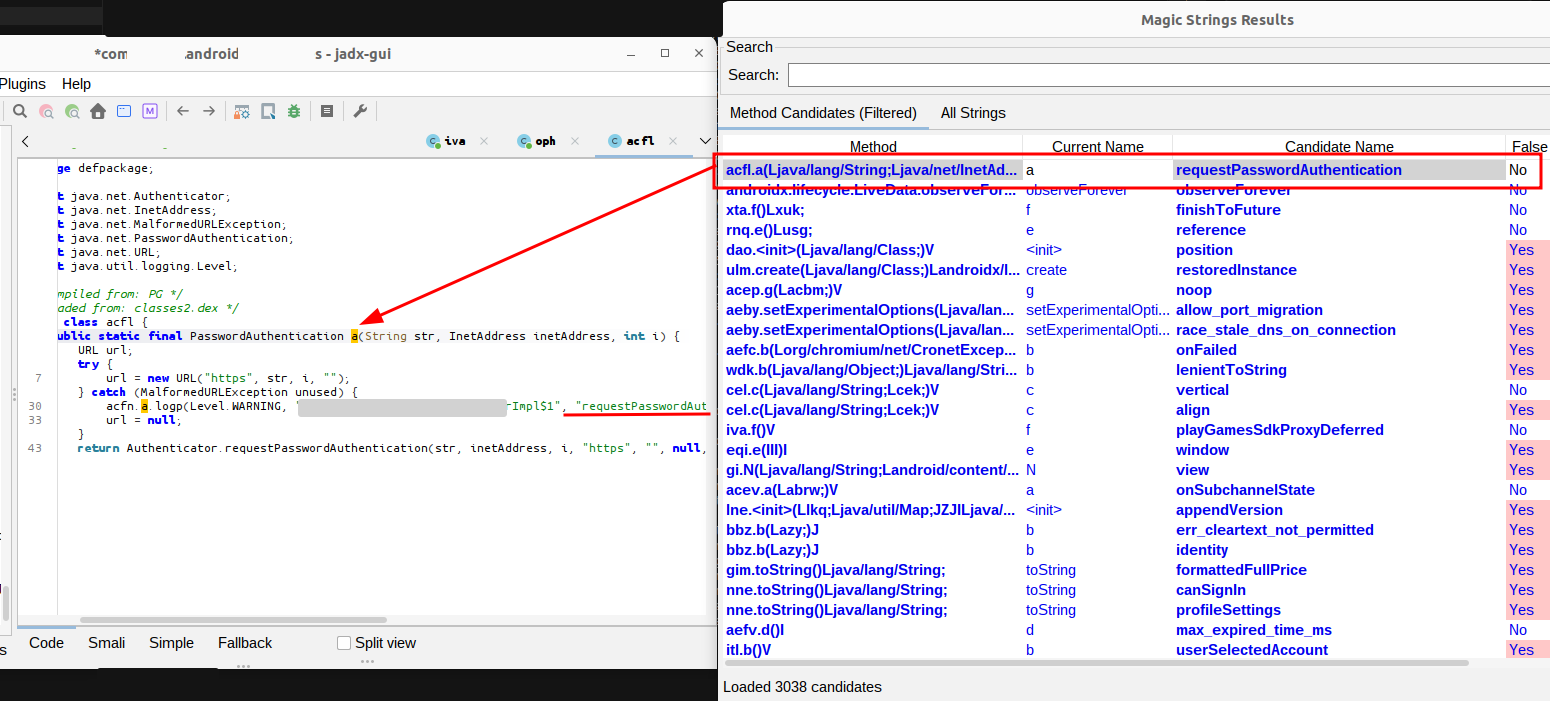 0rshemesh/jadx-magic-strings
JADX plugin that extracts method names, class references, and source file paths from string constants found in DEX files and decompiled Android code.
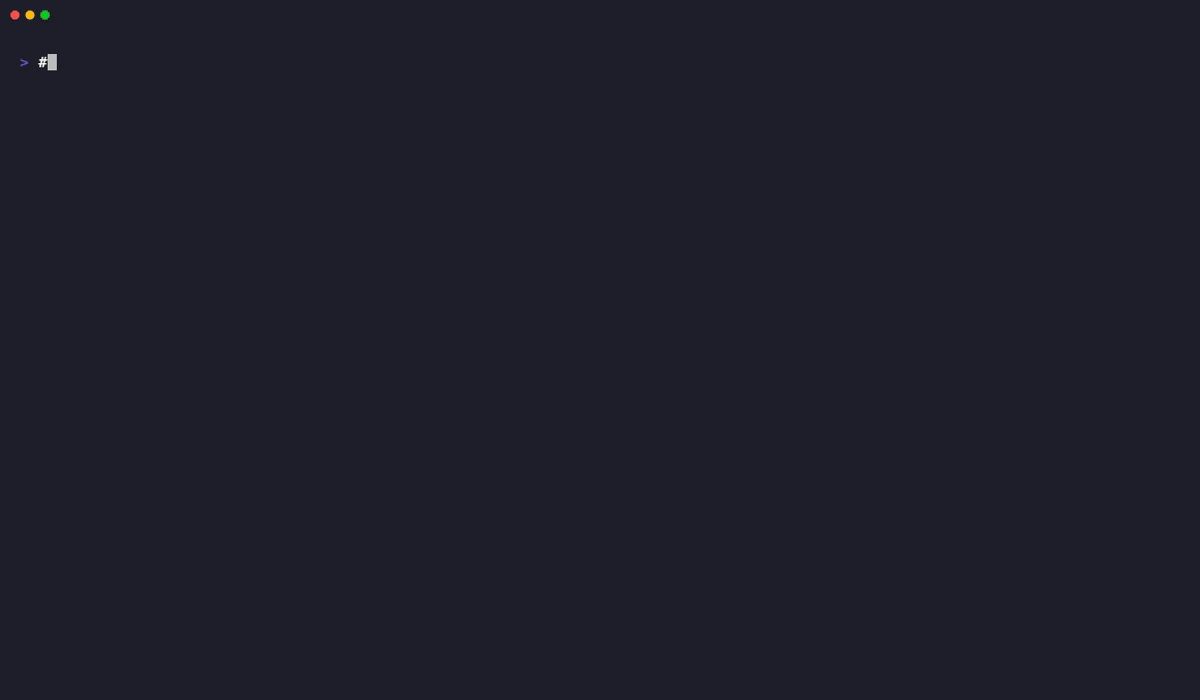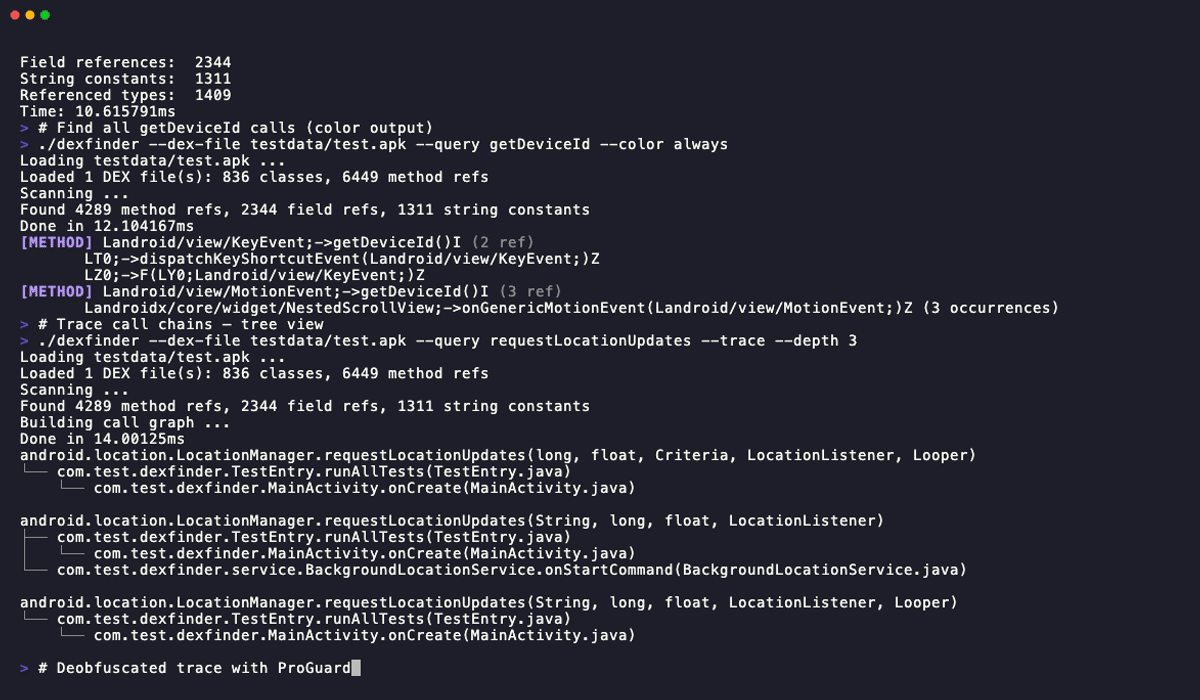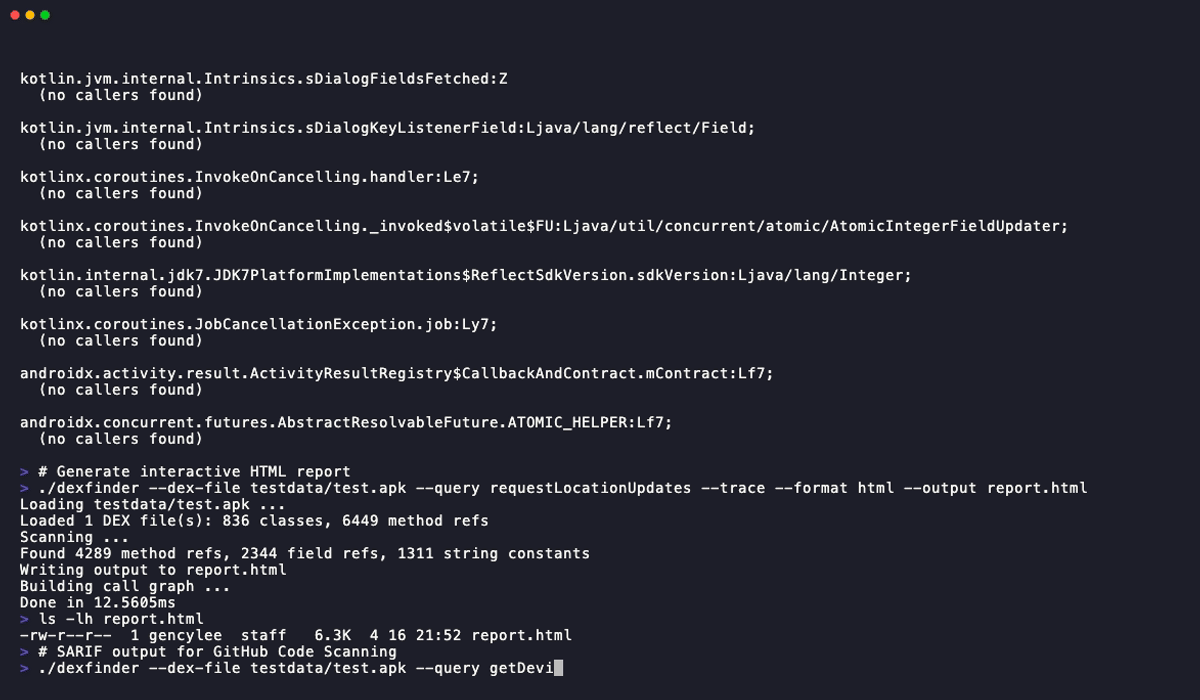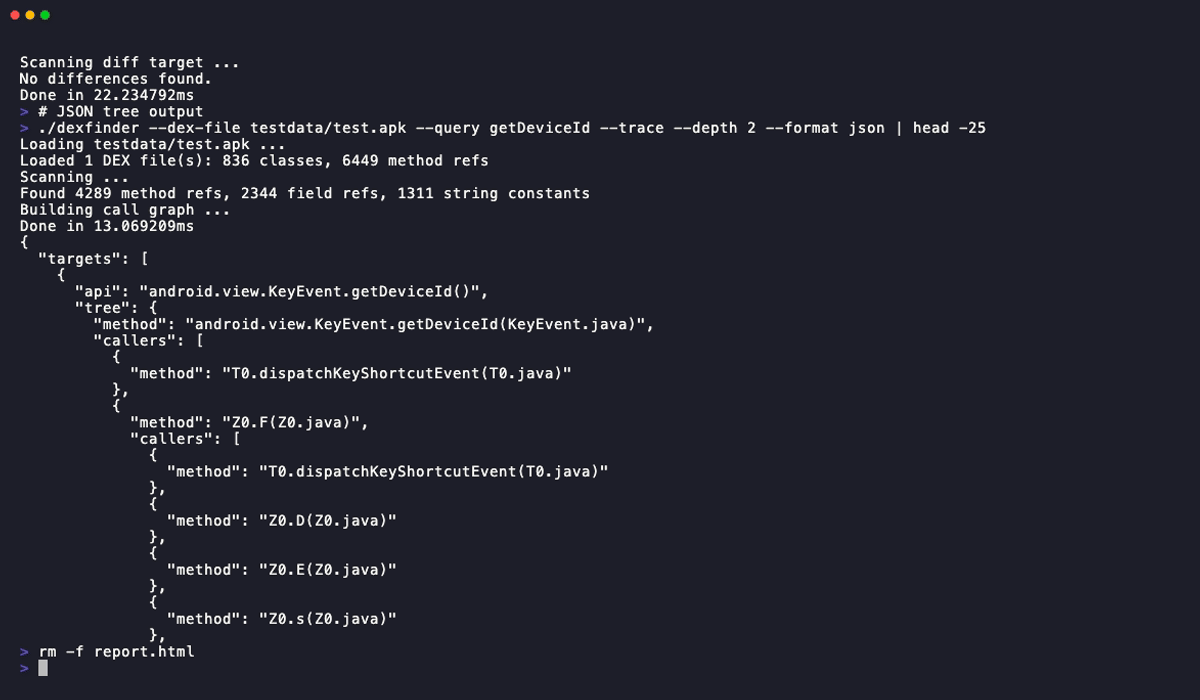 junelegency/dexfinder
Cross-platform APK/DEX method finder with call chain tracing, ProGuard deobfuscation, and hidden API detection